About Us Contact Blog
Governance DocsGovernance Docs
Which Toolkit?SoA GeneratorFree TemplatesSample ReportsFind the Right AssessmentRecords of Processing (ROPA)Data Privacy Impact AssessmentLegitimate Interests AssessmentTransfer Impact AssessmentPrivacy Risk AssessmentGDPR Gap AssessmentUK GDPR Gap AssessmentCCPA/CPRA Gap AssessmentISO 27701 Gap AssessmentHIPAA Gap AssessmentISO 27001 Risk AssessmentThird-Party Risk AssessmentSoA GeneratorISO 27001 Assessment Tool (Excel)ISO 27001 Gap AssessmentSOC 2 Gap AssessmentNIST CSF 2.0 Gap AssessmentNIST SP 800-53 Gap AssessmentNIST RMF Gap AssessmentCIS Controls Gap AssessmentPCI DSS 4.0 Gap AssessmentNIS2 Gap AssessmentCMMC 2.0 Gap AssessmentNIST SP 800-171 Gap AssessmentFedRAMP Gap AssessmentBSI C5 Gap AssessmentIEC 62443 Gap AssessmentSAMA CSF Gap AssessmentNCA ECC Gap AssessmentISO 20000 Gap AssessmentAI Risk AssessmentAI Impact AssessmentISO 42001 Gap AssessmentEU AI Act Gap AssessmentBusiness Impact AnalysisContinuity Risk AssessmentISO 22301 Assessment Tool (Excel)ISO 22301 Gap AssessmentDORA Gap AssessmentISO 9001 Gap AssessmentISO 13485 Gap AssessmentIATF 16949 Gap AssessmentISO 14001 Gap AssessmentISO 45001 Gap AssessmentISO 45001 Assessment Tool (Excel)HACCP Gap AssessmentEnterprise Risk AssessmentISO 31000 Gap AssessmentData Governance Gap AssessmentProject Management Gap AssessmentAll Gap AssessmentsAboutBlogContactMy AccountCart
FOX v.2.4.9
Browse Toolkits
Governance Docs
  • Browse All Toolkits
  • Information Security & Cybersecurity
  • Data Privacy & Protection
  • Governance, Risk & Compliance
  • Quality Management
  • Health, Safety & Environment
  • AI Governance

My Account

CART

No products in the cart.

Category: Articles

ISO 42001 Statement of Applicability explained

ISO 42001 Statement of Applicability: A Clear 2026 Guide

Governance Docs13th September 2026

The ISO 42001 Statement of Applicability under clause 6.1.3: all 38 Annex A controls, the 5 columns that…
Read More
ISO 42001 internal audit explained

ISO 42001 Internal Audit: A Clear 2026 Guide to Clause 9.2

Governance Docs13th September 2026

An ISO 42001 internal audit under clause 9.2: the 6 things it must show, how it differs from…
Read More
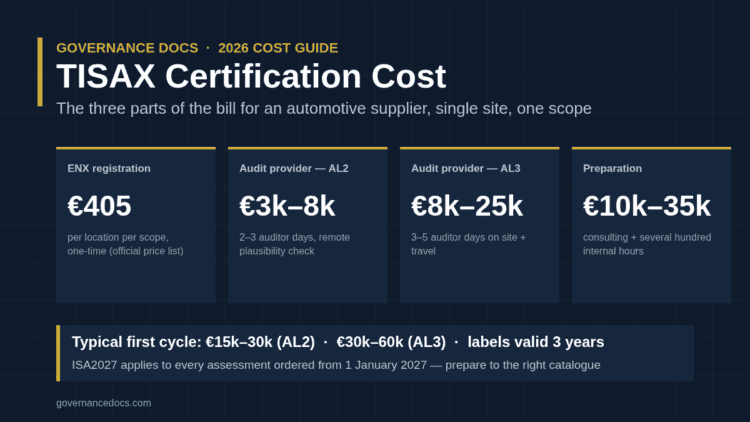
TISAX certification cost 2026 infographic: ENX fee €405, AL2 and AL3 audit provider ranges, preparation cost

TISAX Certification Cost in 2026: The Complete Breakdown

Governance Docs13th September 2026

TISAX certification cost in 2026: the €405 ENX fee, AL2 vs AL3 audit provider fees, preparation ranges, hidden…
Read More
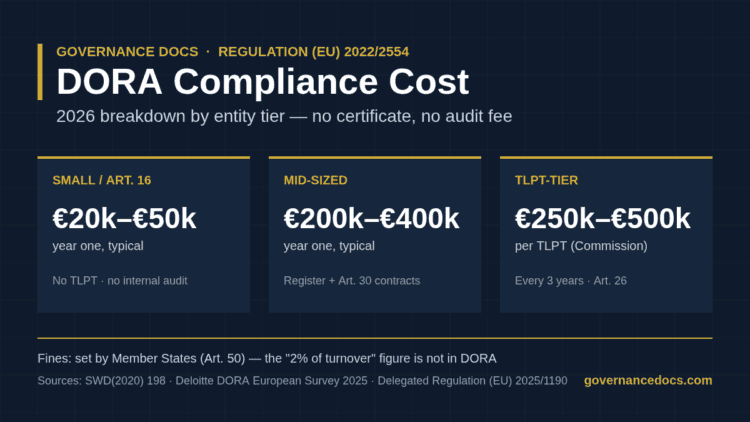
DORA compliance cost 2026 breakdown by entity tier: small Article 16 entities, mid-sized firms and TLPT-tier institutions

DORA Compliance Cost in 2026: The Complete Breakdown

Governance Docs12th September 2026

DORA compliance cost in 2026: why 64% of institutions budget €2–5 million, what a €250,000–€500,000 TLPT covers, and…
Read More
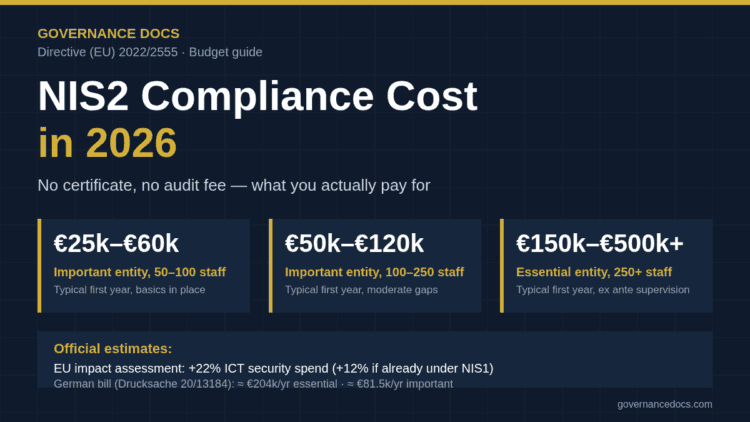
NIS2 compliance cost in 2026: typical first-year ranges for important and essential entities and the official EU and German estimates

NIS2 Compliance Cost in 2026: The Complete Breakdown

Governance Docs12th September 2026

NIS2 compliance cost in 2026 runs €25,000 to €120,000 in year one for most important entities, more for…
Read More
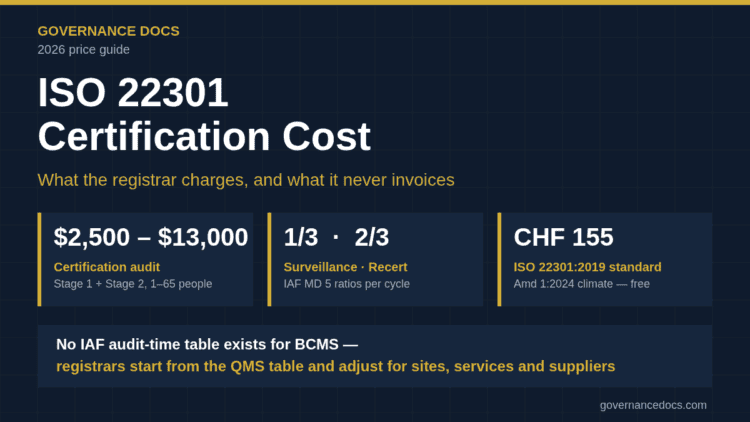
ISO 22301 certification cost 2026 infographic: audit fee ranges, IAF MD 5 surveillance and recertification ratios, and the CHF 155 standard price

ISO 22301 Certification Cost: A Complete 2026 Breakdown

Governance Docs11th September 2026

ISO 22301 certification cost runs about $2,500-$13,000 for a small or mid-sized company in 2026. Audit-day math, hidden…
Read More
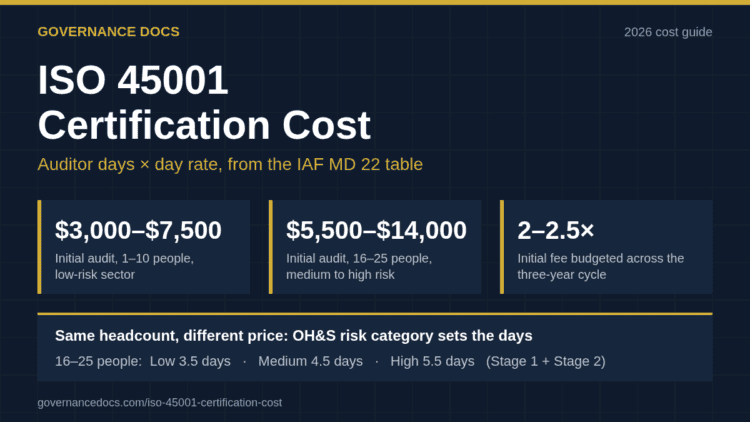
ISO 45001 certification cost 2026 infographic: typical audit fees by company size and OH&S risk category

ISO 45001 Certification Cost: A Complete 2026 Breakdown

Governance Docs11th September 2026

ISO 45001 certification cost runs about $3,000-$14,000 for a small company in 2026. Audit-day math from IAF MD…
Read More
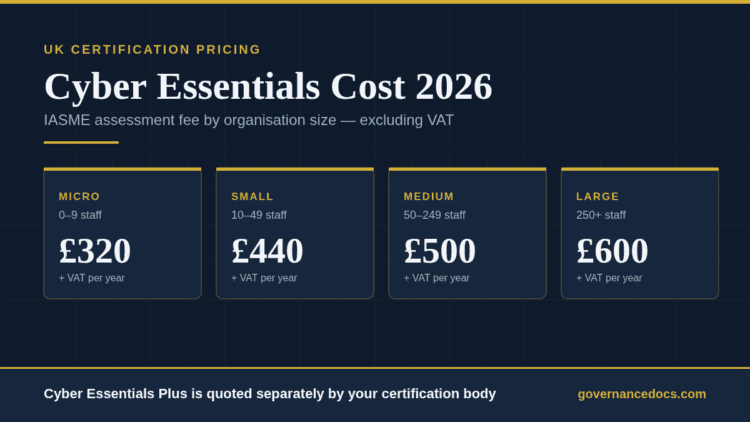
Cyber Essentials cost 2026 by organisation size: micro £320, small £440, medium £500, large £600 plus VAT

Cyber Essentials Cost 2026: The Complete UK Price Guide

Governance Docs10th September 2026

Cyber Essentials cost in 2026 runs £320 to £600 plus VAT by headcount, with Plus quoted separately from…
Read More
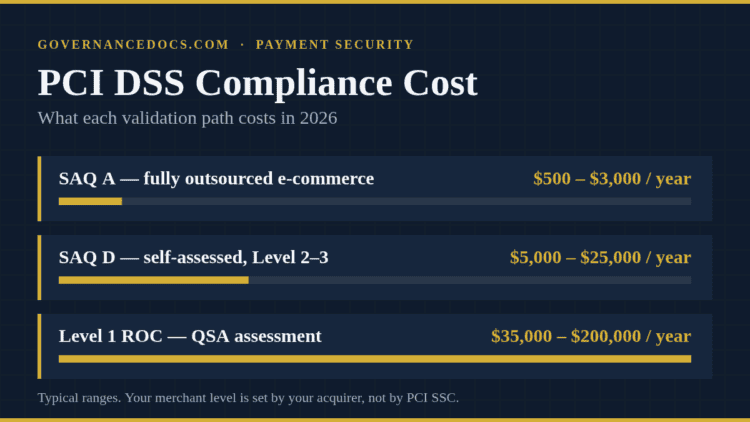
PCI DSS compliance cost by validation path in 2026, from SAQ A to a Level 1 ROC

PCI DSS Compliance Cost: A Clear 2026 Price Breakdown

Governance Docs10th September 2026

PCI DSS compliance cost in 2026 runs from about $500 a year on SAQ A to over $200,000…
Read More
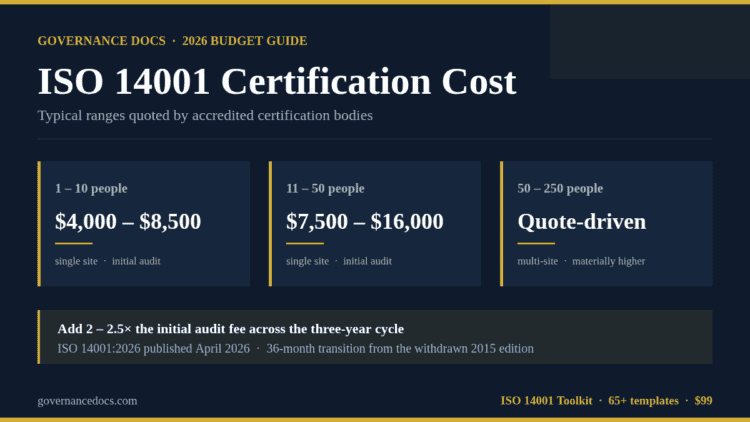
ISO 14001 certification cost ranges for 2026 by company size, with three-year cycle and 2026 transition notes

ISO 14001 Certification Cost: A Complete 2026 Breakdown

Governance Docs09th September 2026

ISO 14001 certification cost runs about $4,000-$16,000 for a small company in 2026. Full breakdown of audit fees,…
Read More
ISO 27001 vs ISO 27701 — ISO 27001 vs ISO 27701: The Complete 2026 Decision Guide

ISO 27001 vs ISO 27701: The Complete 2026 Decision Guide

Governance Docs09th September 2026

ISO 27001 vs ISO 27701: since the 2025 edition a privacy system can be certified alone. Which you…
Read More
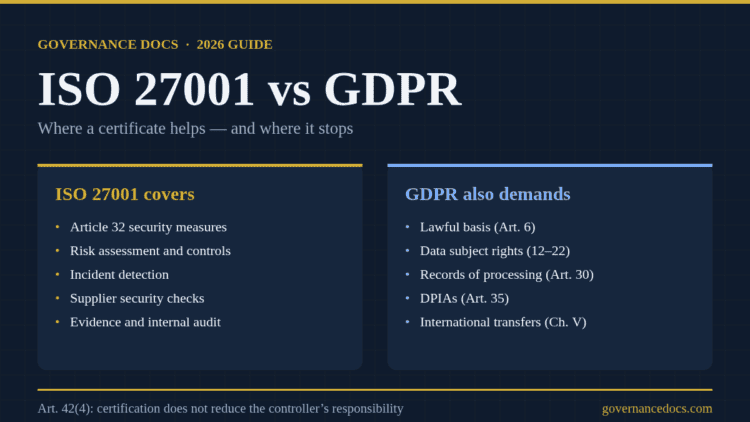
ISO 27001 vs GDPR — what ISO 27001 covers and what GDPR still demands

ISO 27001 vs GDPR: The Complete 2026 Compliance Guide

Governance Docs08th September 2026

ISO 27001 vs GDPR: certification proves you secure data, but GDPR asks whether you should hold it at…
Read More

    ←
  • 1
  • …
  • 59
  • 60
  • 61
  • 62
  • 63
  • …
  • 100
  • →

Recent Posts

iso 30301 — ISO 30301 vs ISO 15489: Which Records Standard Do You Need?
ISO 30301 vs ISO 15489: Which Records Standard Do You Need?

October 12, 2026

legal hold — Legal Hold: How to Suspend Records Destruction Properly (2026)
Legal Hold: How to Suspend Records Destruction Properly (2026)

October 12, 2026

records retention schedule — Records Retention Schedule: How to Build One in 2026
Records Retention Schedule: How to Build One in 2026

October 12, 2026

iso 15489 — ISO 15489 Explained: The Records Management Standard in 2026
ISO 15489 Explained: The Records Management Standard in 2026

October 12, 2026

records management metadata — Records Management Metadata: What to Capture and Why (2026)
Records Management Metadata: What to Capture and Why (2026)

October 12, 2026

Categories

  • Articles
  • DORA
  • GDPR
  • HIPAA
  • ISO 27001
  • ISO 42001 & AI governance
  • ISO 9001
  • Management systems
  • NIS2
  • Security frameworks
  • SOC 2
Governance DocsGovernance Docs

Reliable ISO & compliance documentation toolkits that help your business meet regulatory standards with ease.

Governance Docs LLC
1209 Mountain Road Pl NE, Suite R
Albuquerque, NM 87110, USA
info@governancedocs.com
+1 505 289 2455

Toolkits

  • ISO 27001:2022
  • GDPR
  • SOC 2
  • PCI-DSS v4.0
  • HIPAA
  • ISO 42001
  • All toolkits →

Company

  • About Us
  • Blog
  • Contact
  • FAQ
  • Which toolkit do I need?
  • Free templates
  • SoA generator
  • Assessments
  • Sample reports
  • RSS feeds

Policies

  • Privacy Policy
  • Terms & Conditions
  • Refund & Return Policy
  • Delivery Policy
  • Manage cookies
Browse by topicISO 27001ISO 42001 & AI governanceGDPRSOC 2HIPAANIS2DORAISO 9001Management systemsSecurity frameworks
© 2026 Governance Docs LLC. All rights reserved.
Secure checkoutstripeVISA