Description
At a glance: the PCI DSS Toolkit is an editable Microsoft Office documentation set for PCI DSS v4.0.1. It covers the PCI scope inventory and cardholder data policy, targeted risk analysis and the customized approach, cryptographic key management, vulnerability management and incident response. One-time price $99, instant download, licensed for internal use by one organisation. Implementing for several clients? The Consultant Package covers unlimited client engagements.
About the PCI-DSS Toolkit
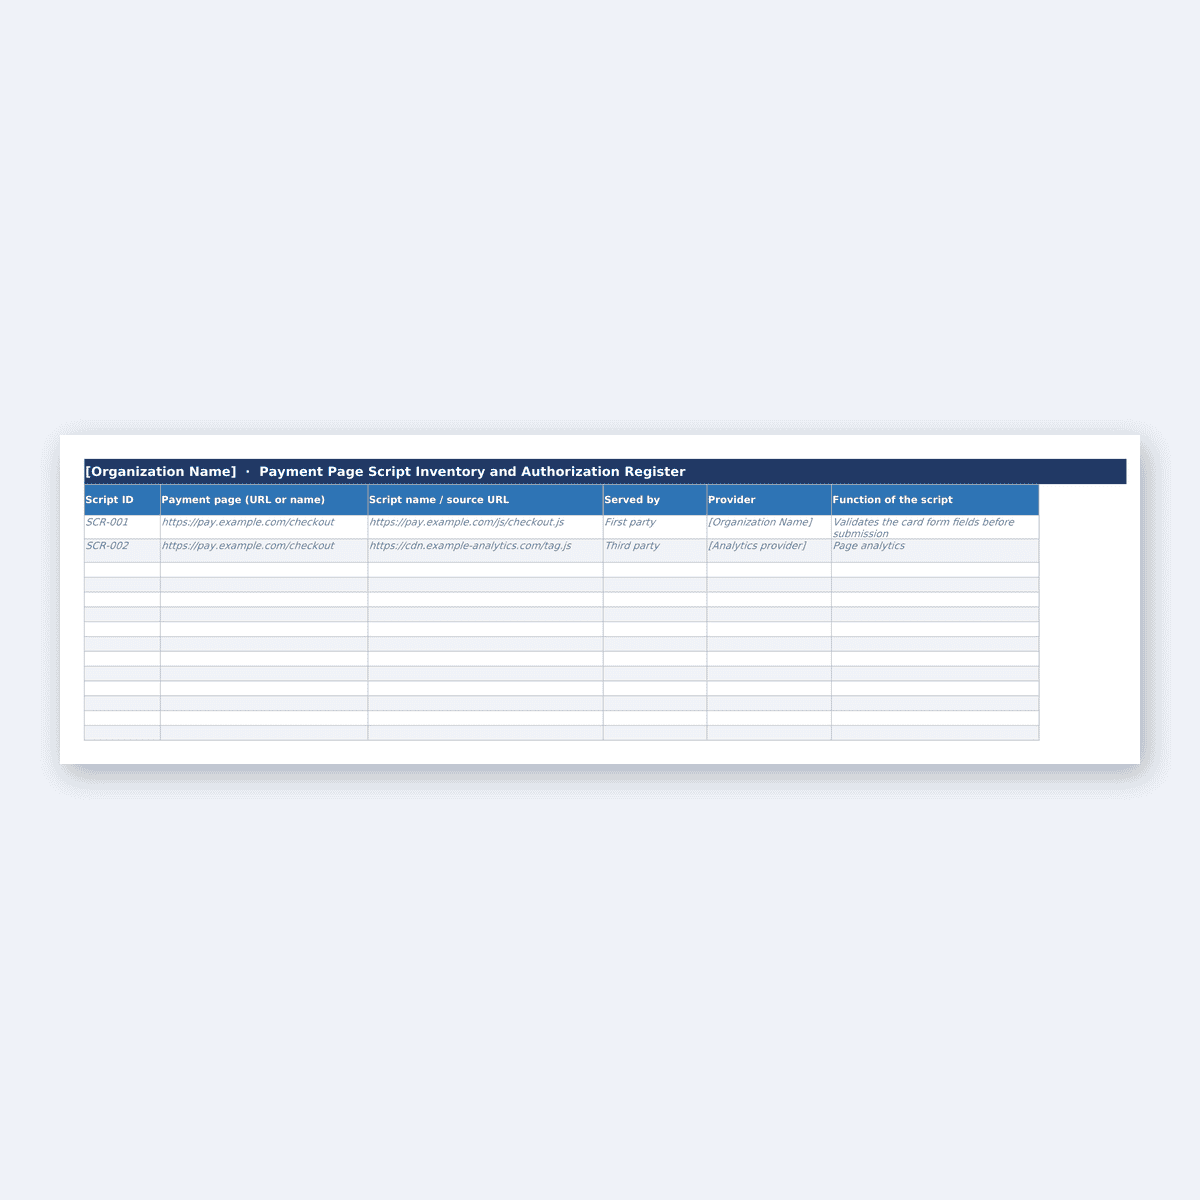
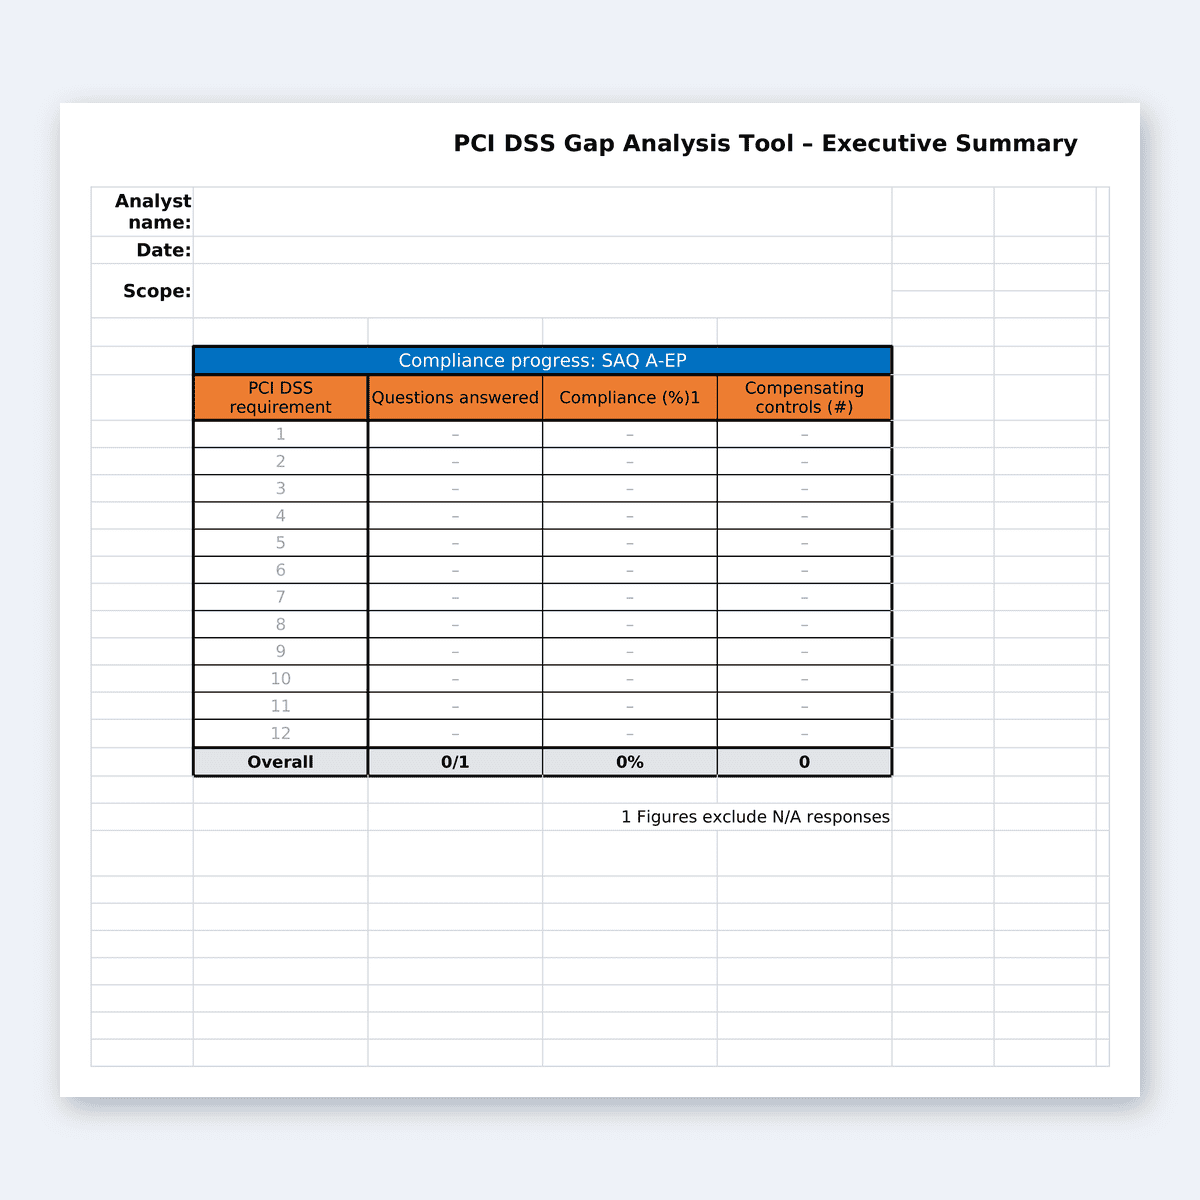
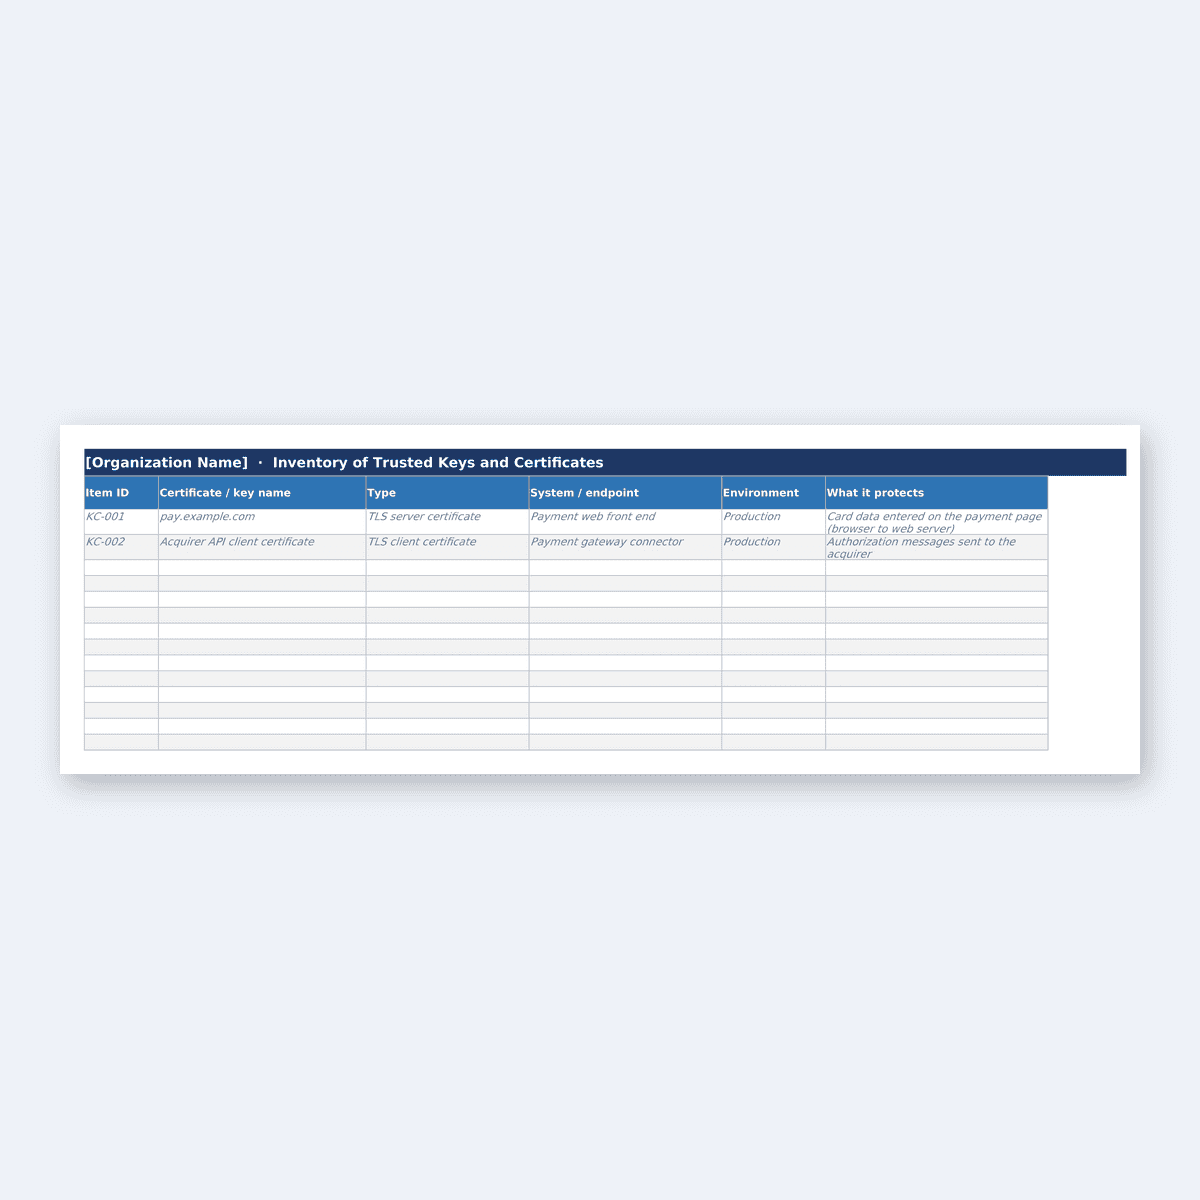
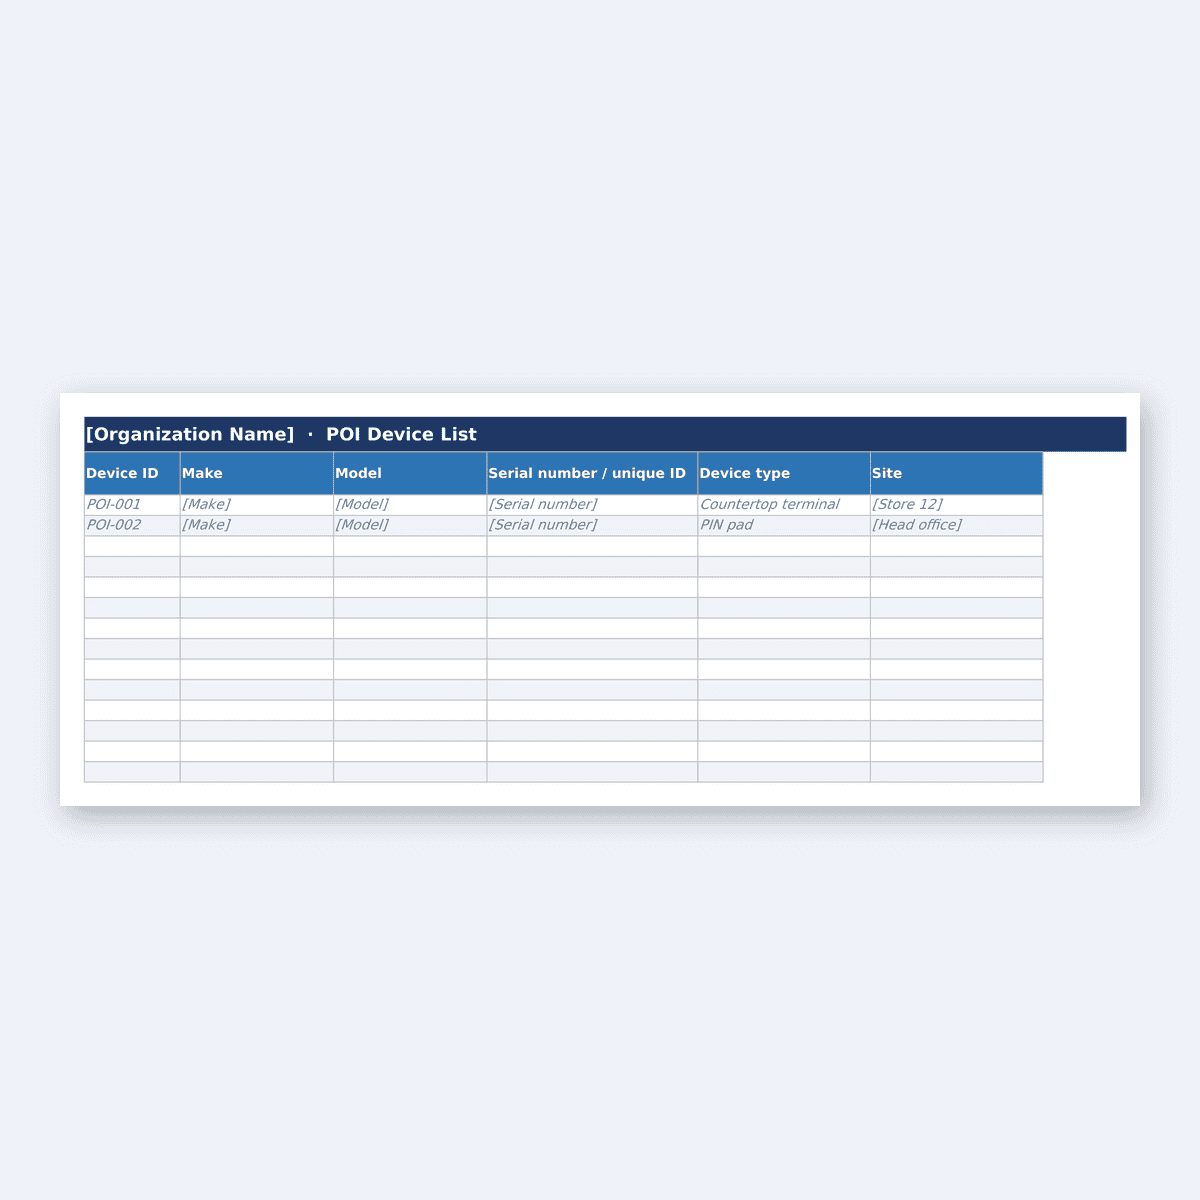
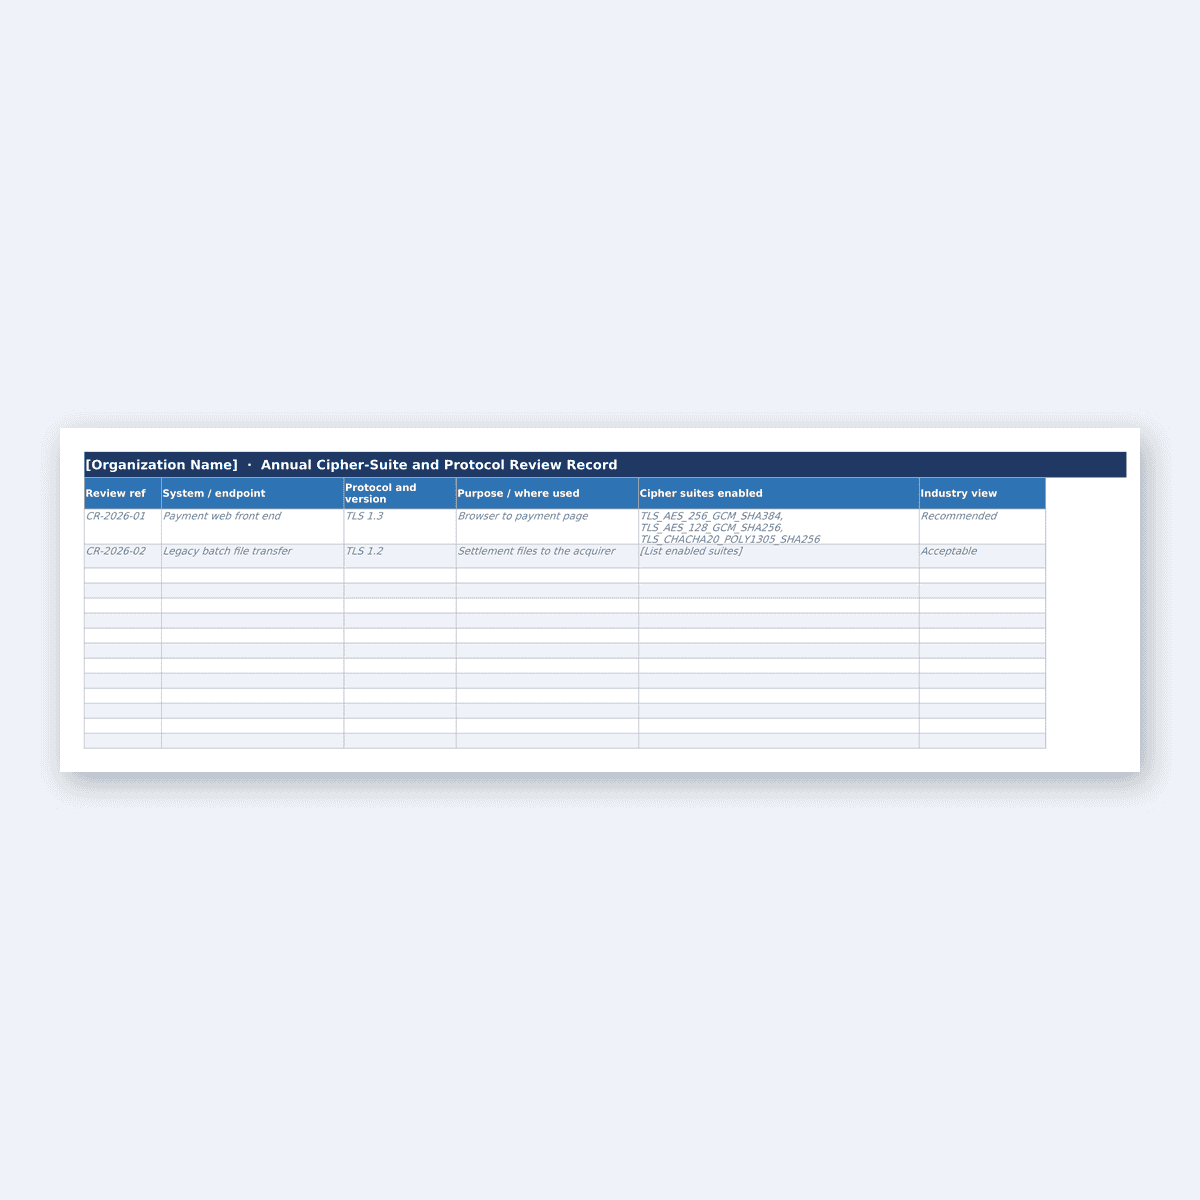
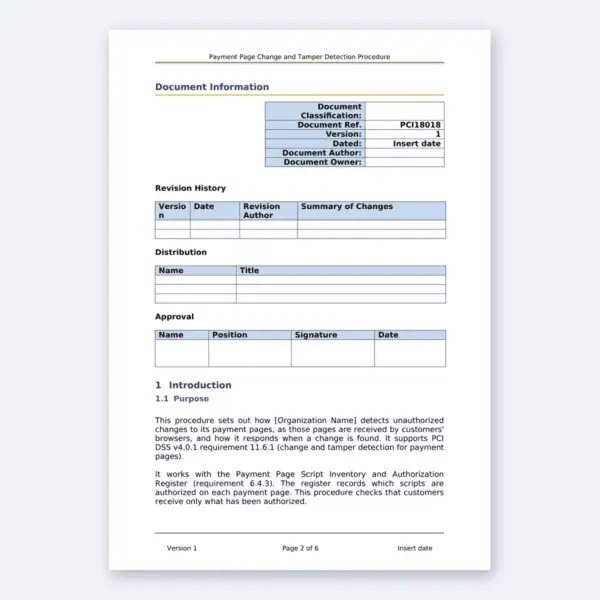
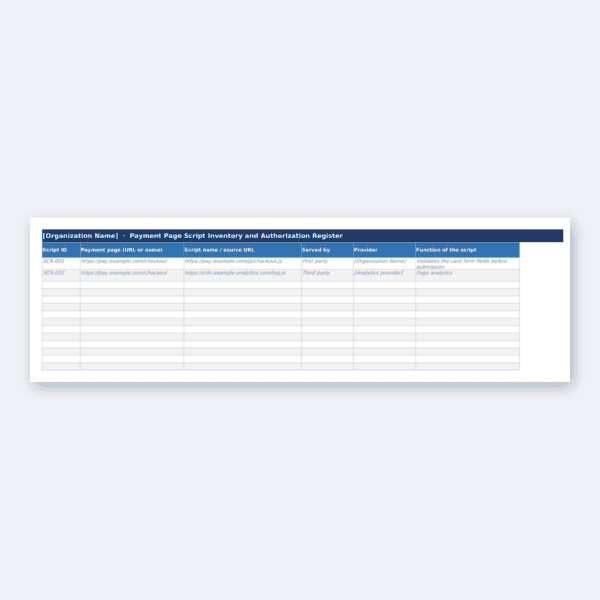
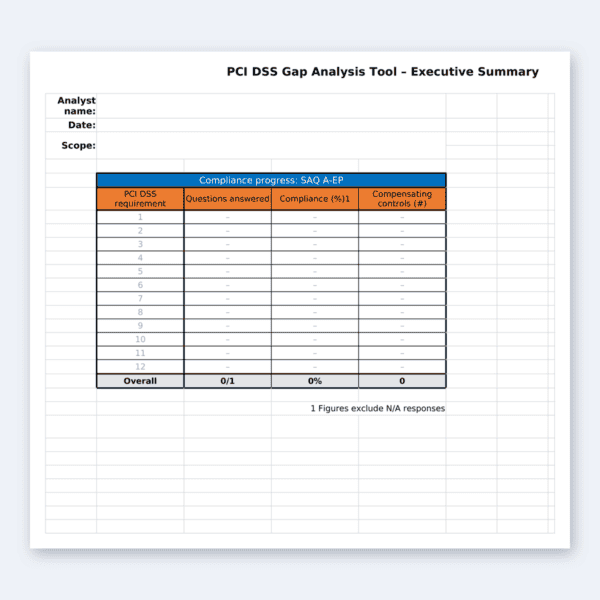
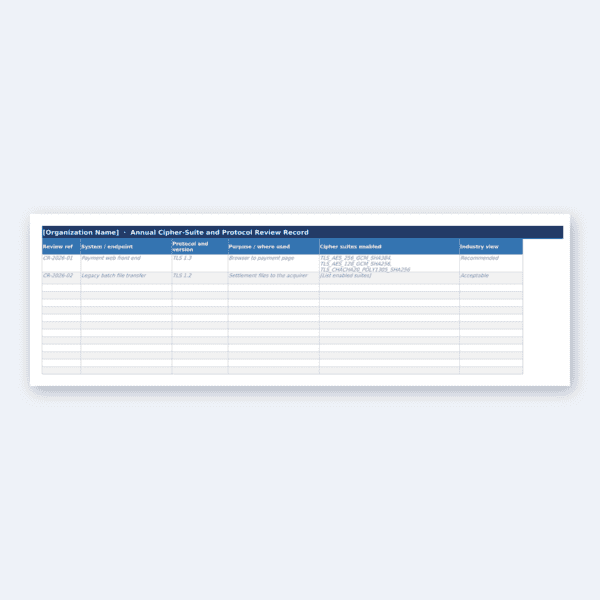
Last updated 3 November 2026. Version 2: every Word document now opens with a branded full-page cover and every Excel workbook with a cover sheet, in one consistent house style, and the remaining legacy .doc/.xls files are now .docx/.xlsx. This release also adds six templates for the newer PCI DSS v4.0.1 requirements: a payment-page script inventory and authorization register (6.4.3), a payment-page change and tamper-detection procedure (11.6.1), inventories of trusted keys and certificates (4.2.1.1), bespoke software and components (6.3.2) and POI devices (9.5.1.1), and an annual cipher-suite and protocol review record (12.3.3). The Gap Analysis Tool’s SAQ A list now follows the January 2025 SAQ A revision.
This is the most comprehensive PCI-DSS toolkit currently available.
The documents are created in Microsoft Office format and are ready to be tailored to your organization’s specific needs. Along with standard format and contents, the PCI-DSS template documents include example text that is clearly highlighted to illustrate the type of information that needs to be provided regarding your organization. Full example documents are also included to assist you with your implementation.
Published by Governance Docs, the toolkit presents the documents a PCI-DSS v4.0.1 programme needs in an easy-to-implement format.
The toolkit covers the documents an organization needs to achieve PCI-DSS v4.0.1 compliance and then to keep improving its information security management.
This pack has been created by Governance Docs to comply with the PCI-DSS v4.0.1 standard, the version in force since v4.0 was retired on 31 December 2024.
Not sure which documents an assessor will actually ask for? Our checklist of the PCI DSS documentation you must hold walks through the requirement areas, the targeted risk analyses and the evidence to retain.
What is included with in the PCI-DSS toolkit?
- 180+ template documents – including policies, procedures, controls, checklists, tools and other useful documentation.
- Available as an instant download after purchase
180+ Templates
Payment Card Industry Data Security Standard
A full and comprehensive documentation pack to help clients, consultants and service providers achieve PCI-DSS v4.0.1 successfully.
List of all documents:
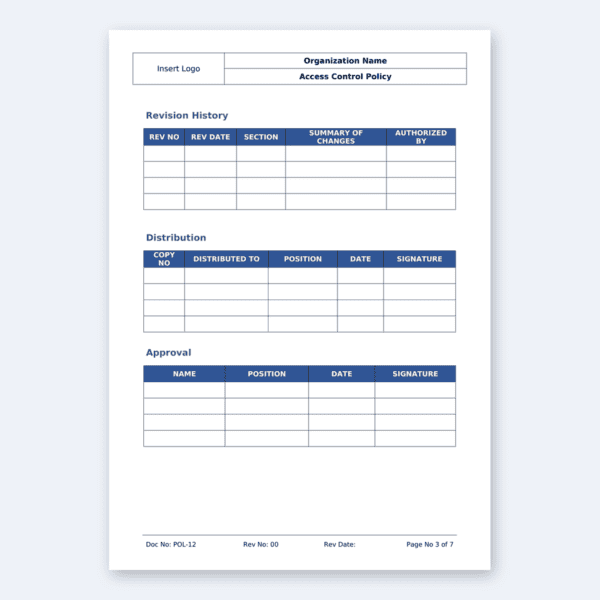
- Access Control Policy v1
- Access Control Policy v2
- Access Review Procedure
- Anti Malware Policy v1
- Anti Malware Policy v2
- Application and System Development Software Policy
- Asset Handling Procedure
- Authorised and Unauthorised Software Policy
- Availability Management Plan
- Backup Policy
- Bespoke Software and Component Inventory
- Bring Your Own Device Policy
- Business Continuity Exercising and Testing Schedule
- Business Continuity Plan
- Business Continuity Test Plan
- Business Continuity Test Report
- Business Impact Analysis Process
- Business Requirements Specification
- Capacity Management Process
- Capacity Plan
- Card Reader Policy
- Cardholder Data Policy Statement
- Change Management Policy v1
- Change Management Policy v2
- Change Management Process
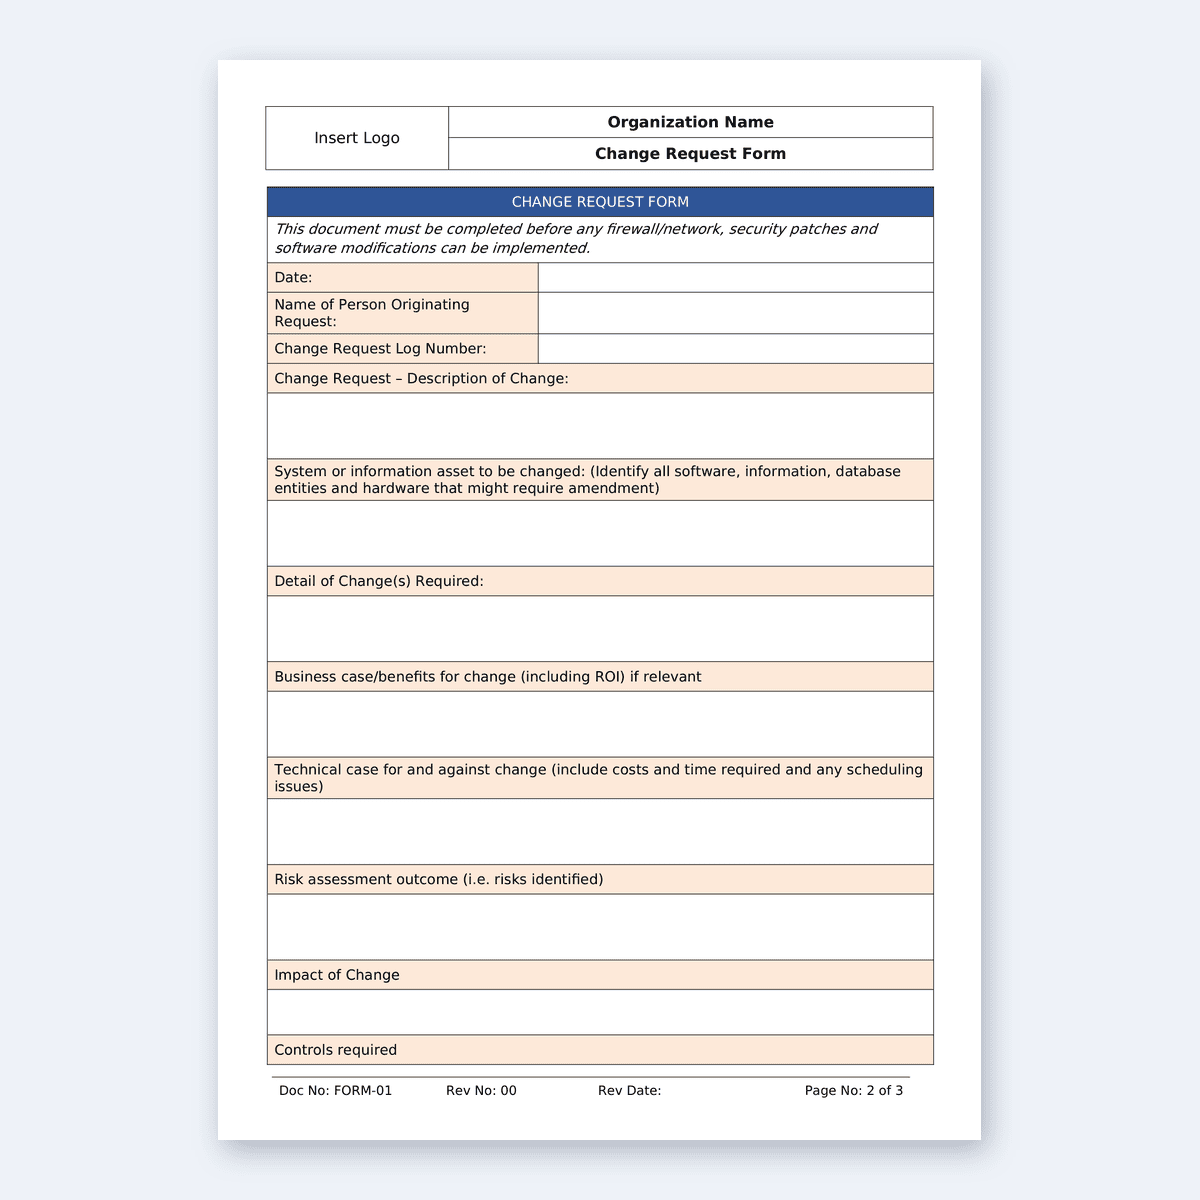
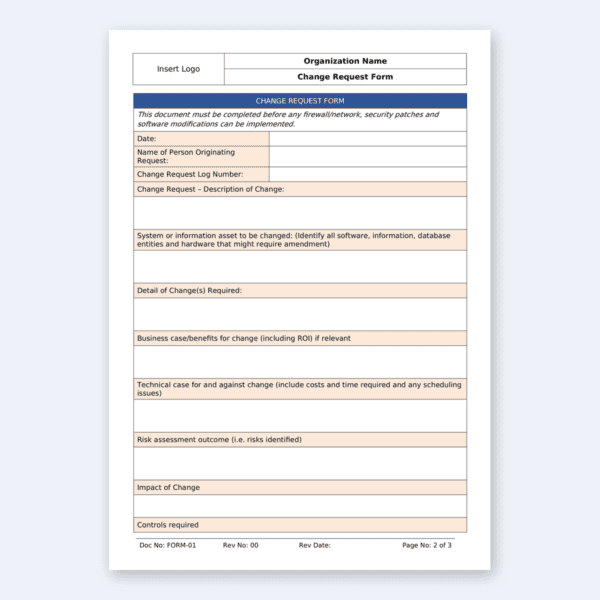
- Change Request Form v1
- Change Request Form v2
- Cipher Suite and Protocol Review Record
- Configuration Management Procedure
- Configuration Management Process
- Continual Improvement Monitoring Log
- Control of Records
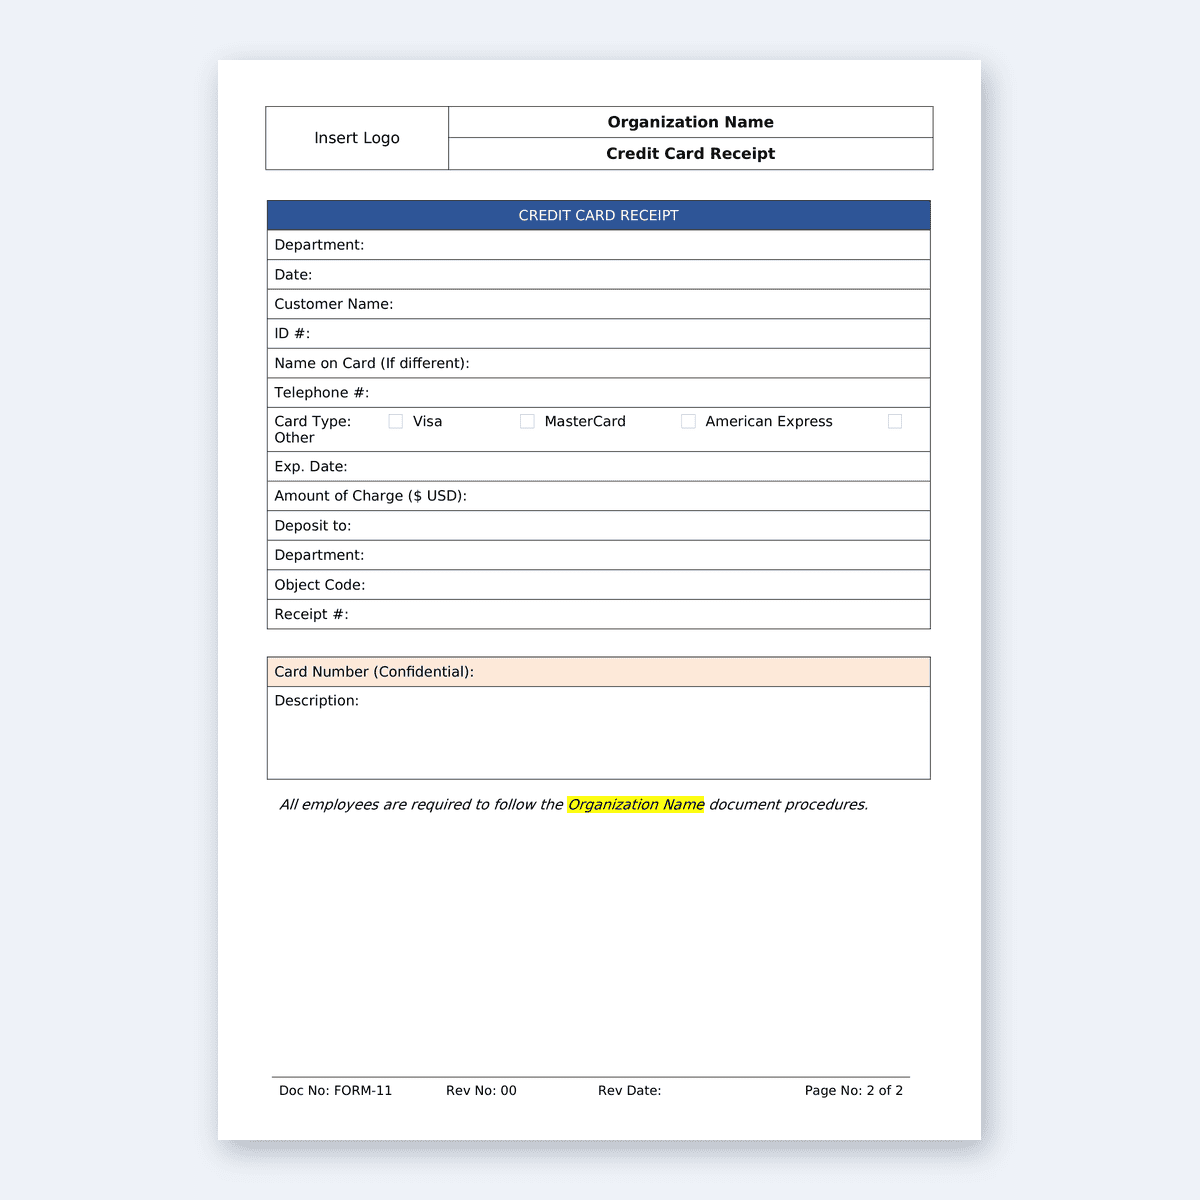
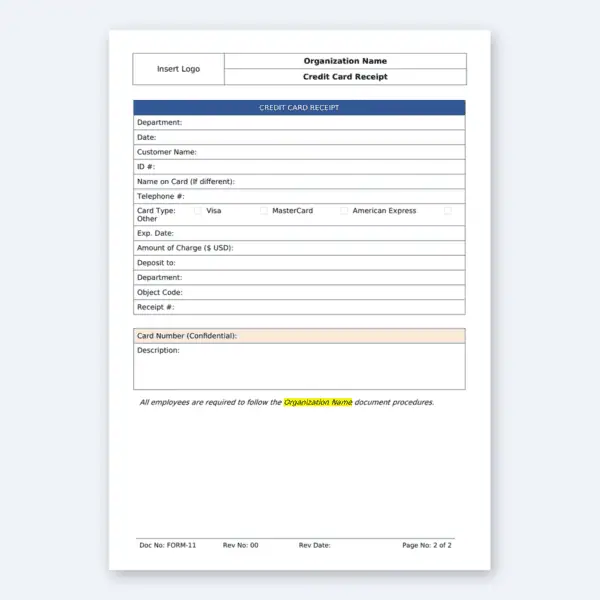
- Credit Card Receipt
- Cryptographic Key Custodian Acceptance Form
- Cryptographic Key Management Policy
- Cryptographic Policy
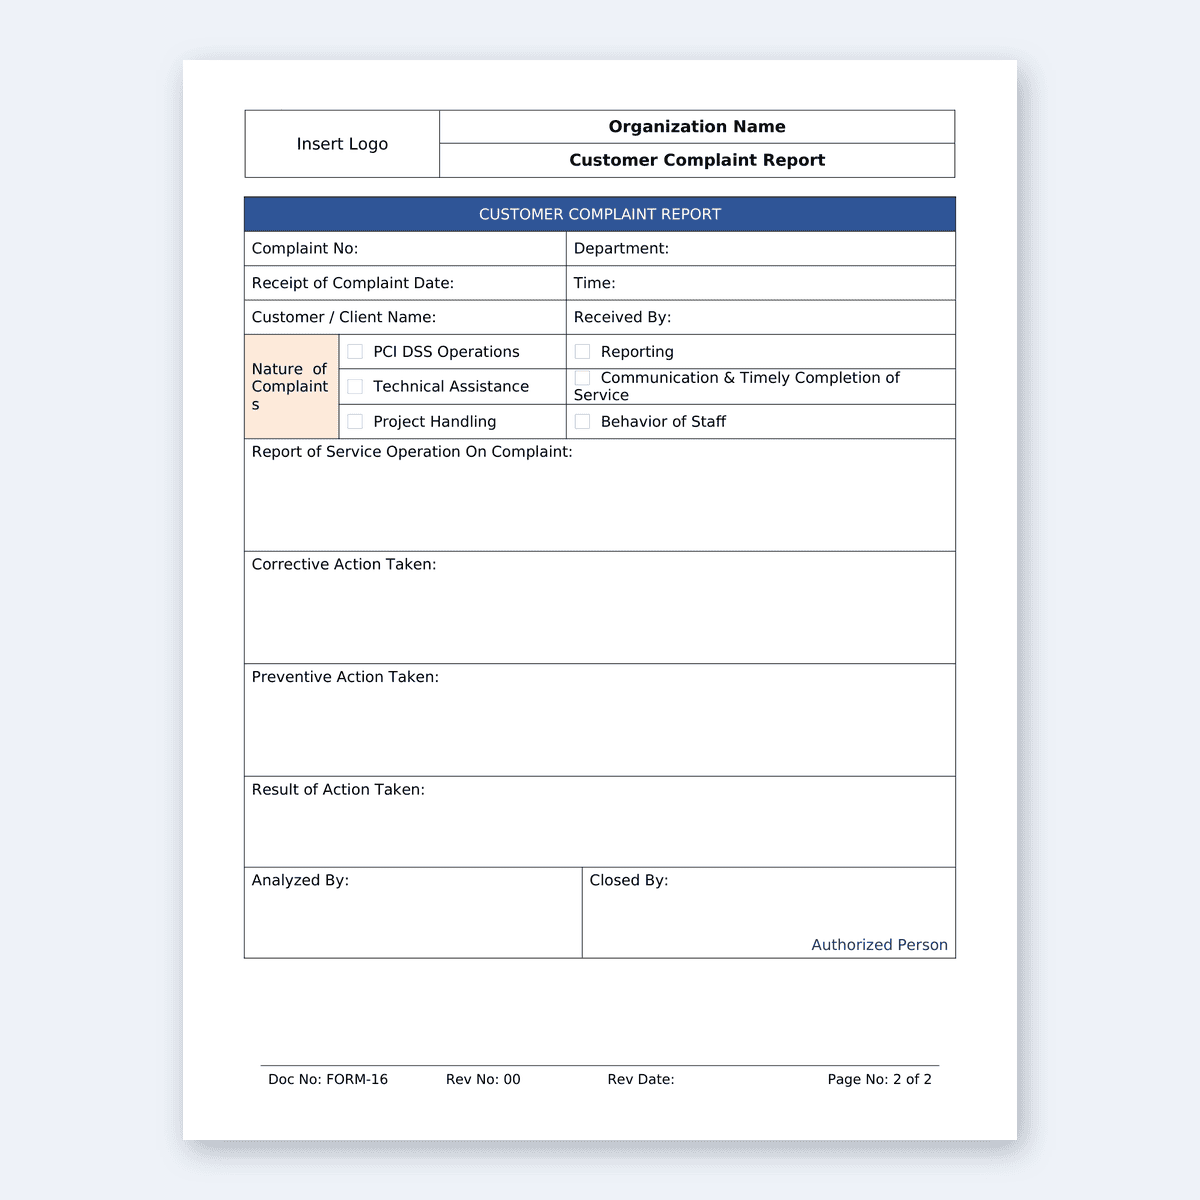
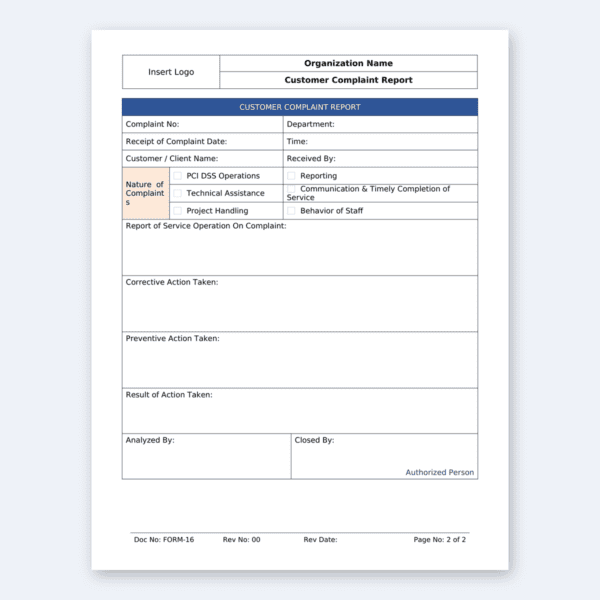
- Customer Complaint Report
- Customized Approach Matrix
- Customized Approach Targeted Risk Analysis
- Data Centre Access
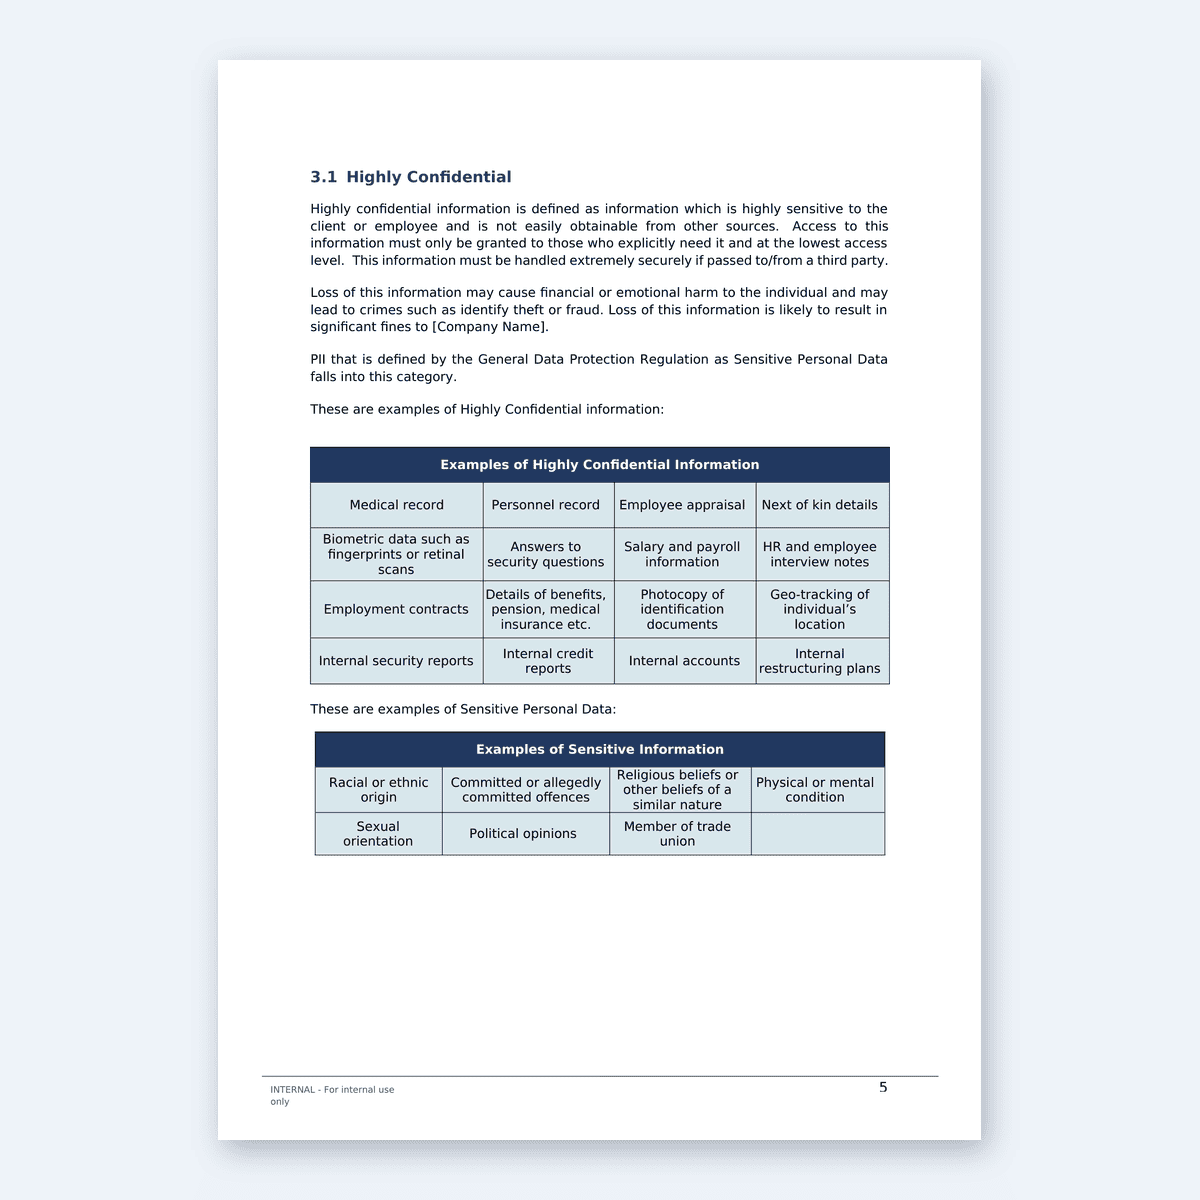
- Data Classification Reference Guidelines
- Data Leakage Prevention Policy
- Data Masking Policy
- Data Retention and Disposal Policy
- Design and Transition of New or Changed Services Process
- Disposal of Media
- Document Control
- Documentation Analysis Tool
- Email Policy
- Employee Disciplinary Process
- Employee Recruitment and New Starter Checklist
- Employee Screening Checklist
- Employee Termination and Change of Employment Checklist
- Encryption Key Management Guidance
- Event Logging and Monitoring Policy
- Firewall and Router Policy
- Gap Analysis Tool Version 3.2.1 — superseded, retained for historical reference only (PCI DSS v3.2.1 was retired on 31 March 2024)
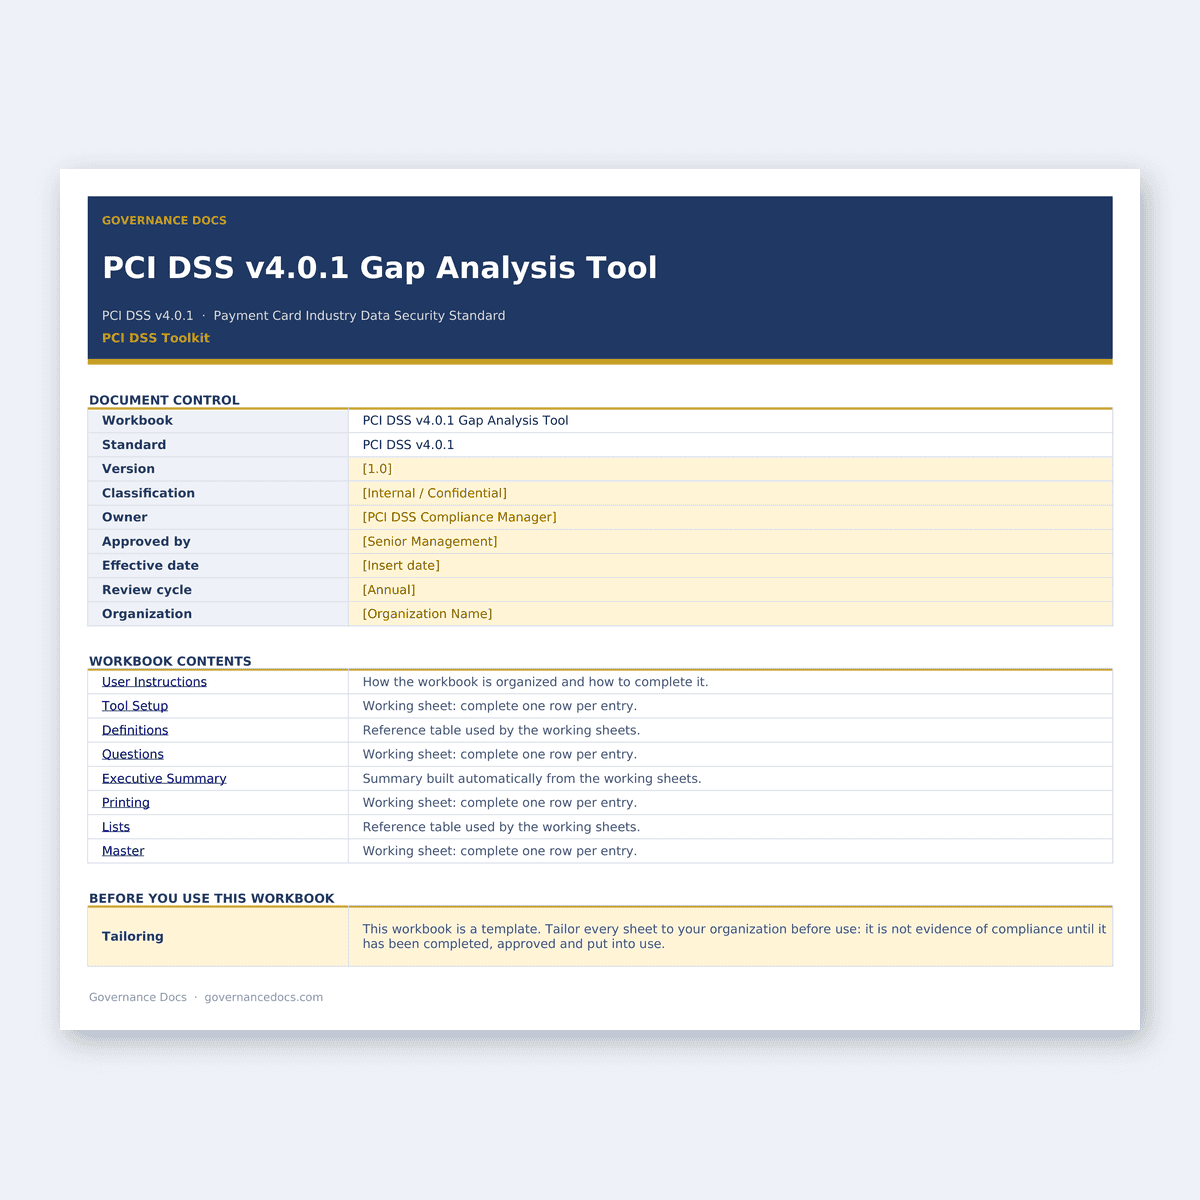
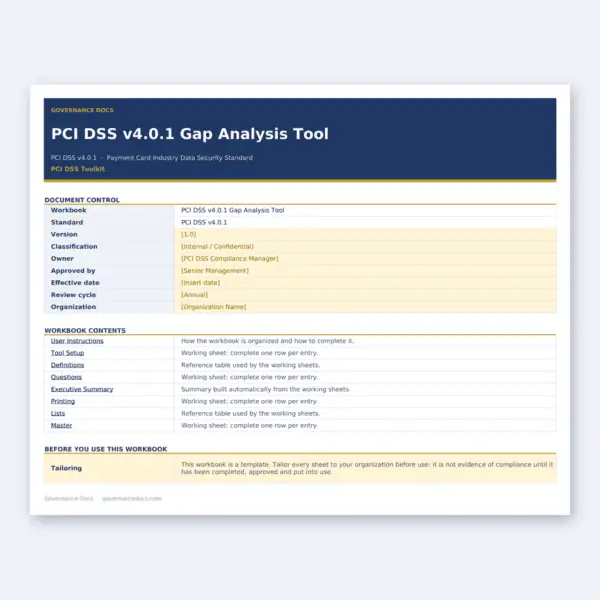
- Gap Analysis Tool Version 4.0
- Guidelines for Inclusion in Employment Contracts
- Guidelines for Working in Secure Areas
- Handling of Virus Attacks
- Incident Management Process
- Incident Response Procedure
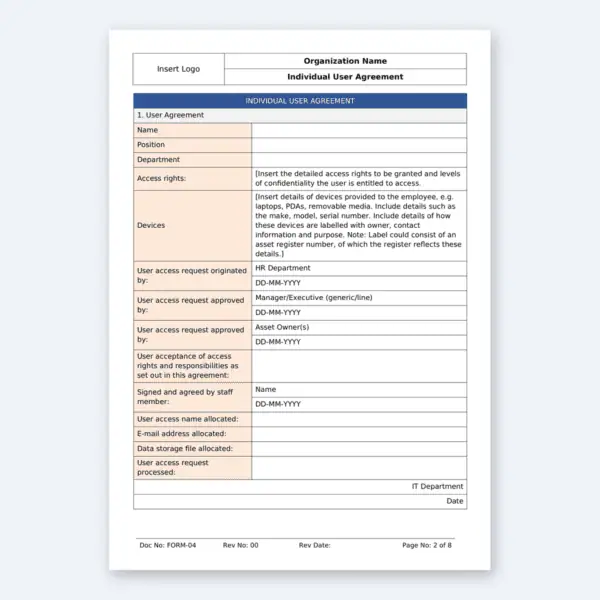
- Individual User Agreement
- Information and System Classification Standard
- Information Security Classification Guidelines v1
- Information Security Classification Guidelines v2
- Information Security Communication Plan
- Information Security Guidelines for Project Management
- Information Security Incident Management
- Information Security Incident Management Procedure
- Information Security Labelling Procedure
- Information Security Policy v1
- Information Security Policy v2
- Information Security Policy for the Use of Cloud Services
- Information Security Responsibilities Policy Statement
- Information Security Risk Assessment Report
- Information Security Risk Treatment Plan
- Information Security Skills and Training Needs Assessment
- Information Systems Audit Plan
- Information Transfer Agreement
- Information Transfer Procedure
- Internal Audit Action Plan
- Internet Acceptable Use Policy v1
- Internet Acceptable Use Policy v2
- Inventory and Ownership of Assets
- Inventory Template
- IT Segregation of Duties Policy
- Leavers Letter
- Legal and Regulatory Requirements Procedure
- Legal Responsibilities Policy
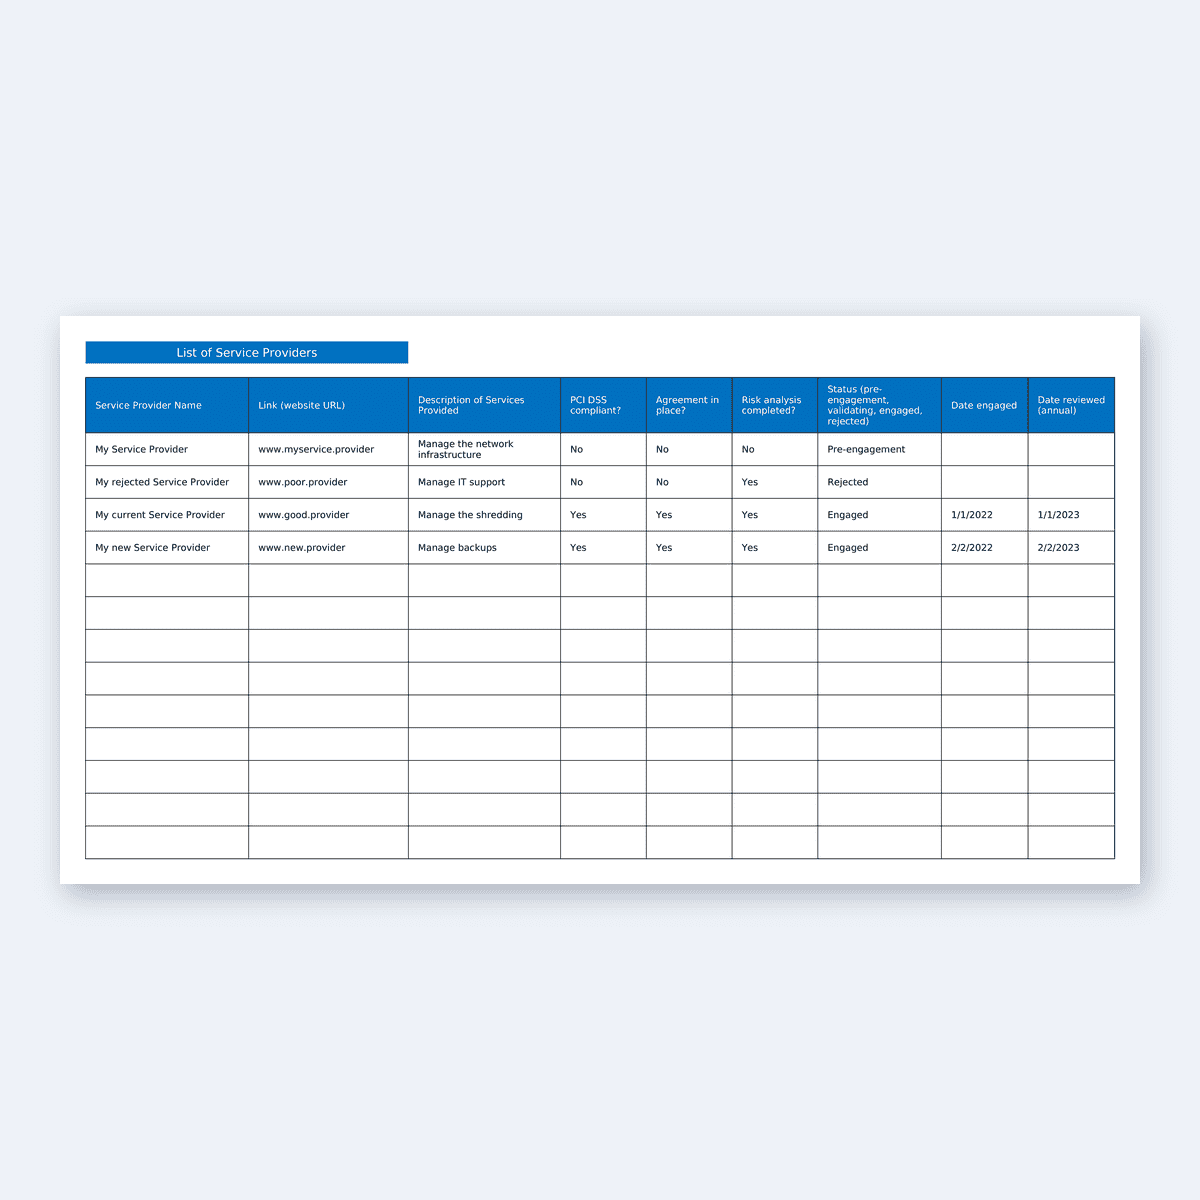
- List of Service Providers
- Major Incident Management Process
- Managing Service Providers
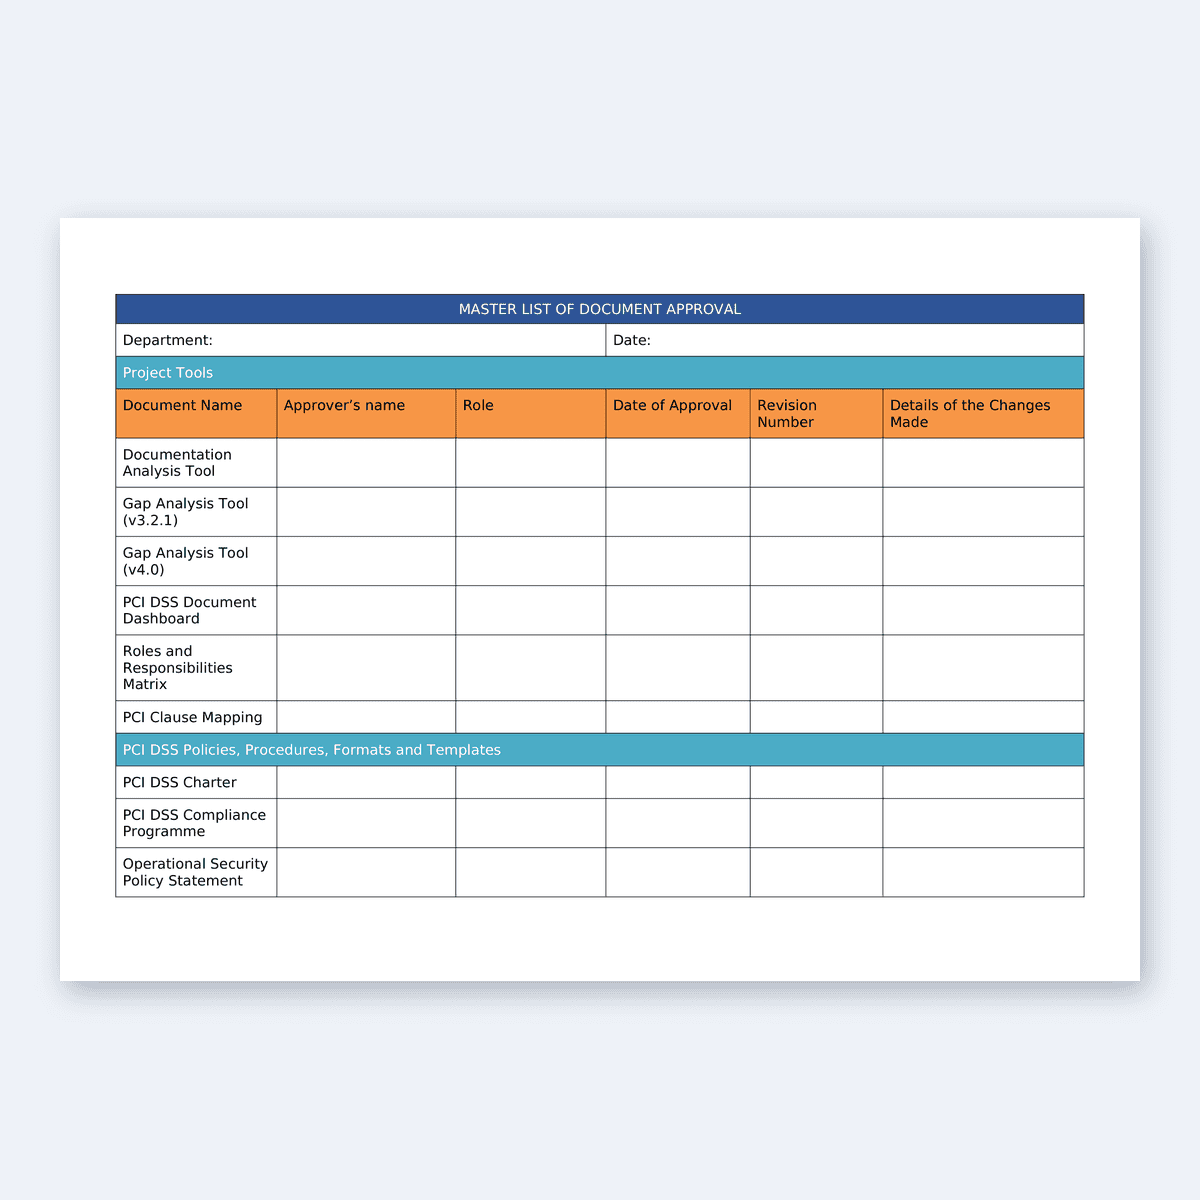
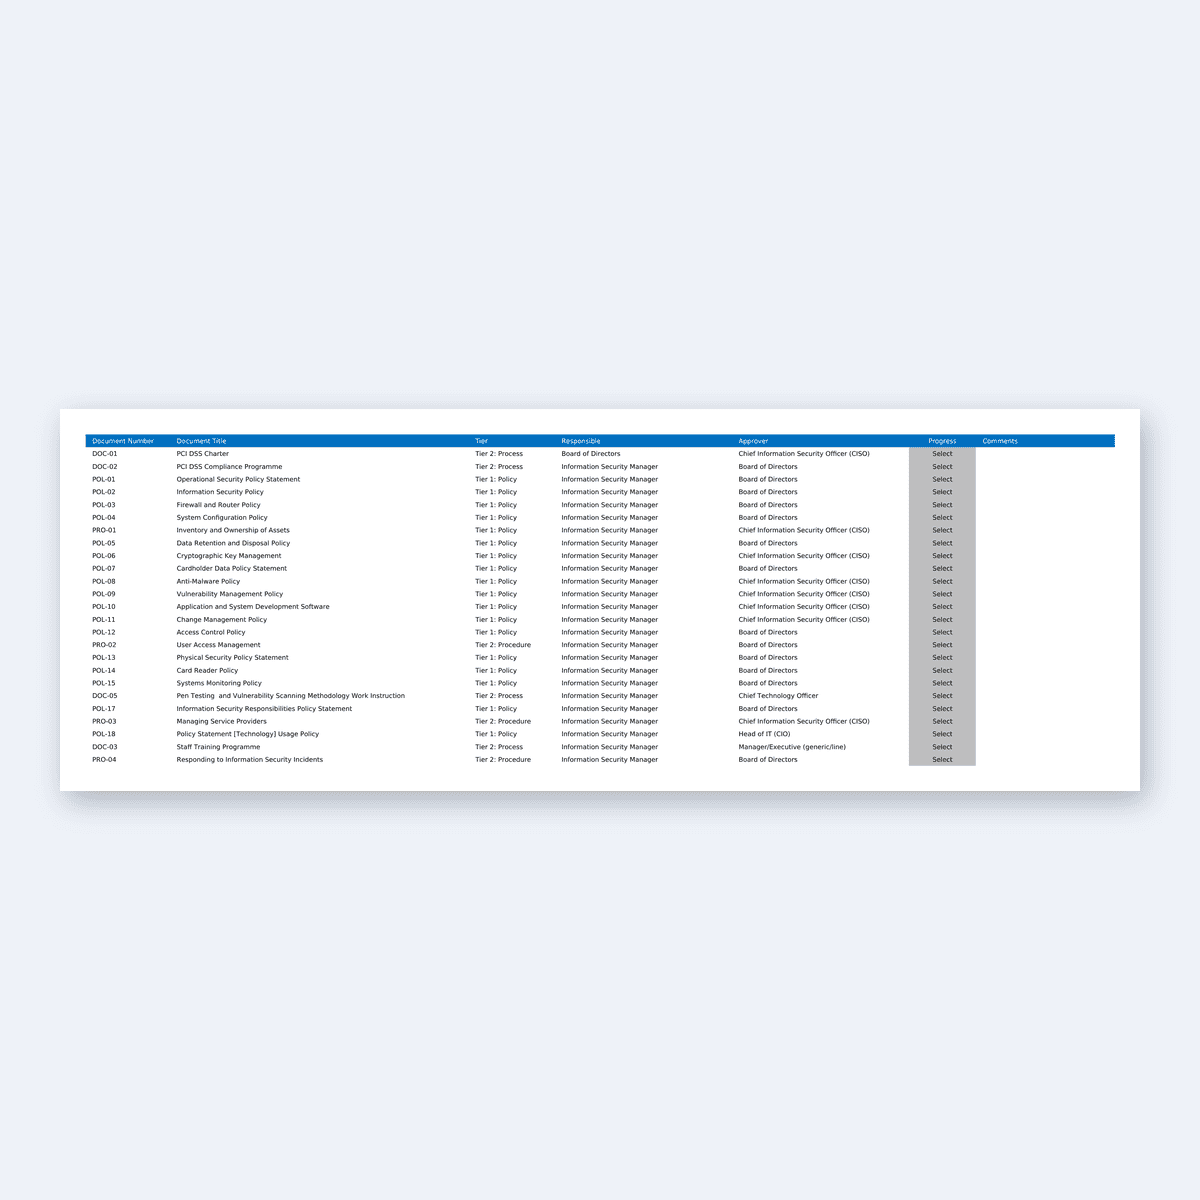
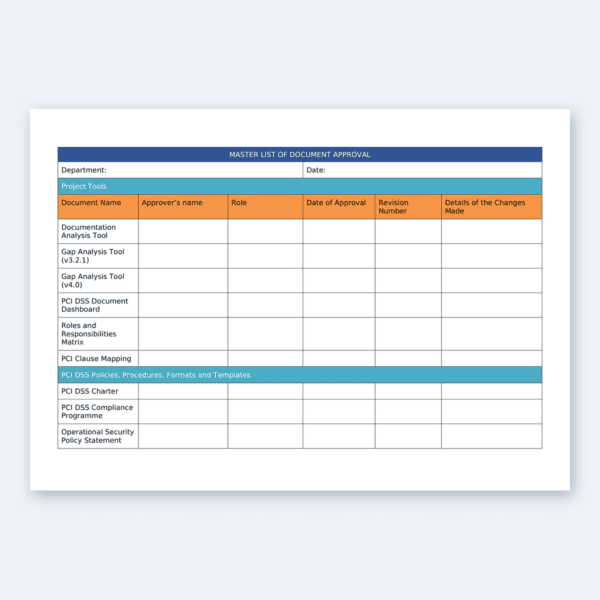
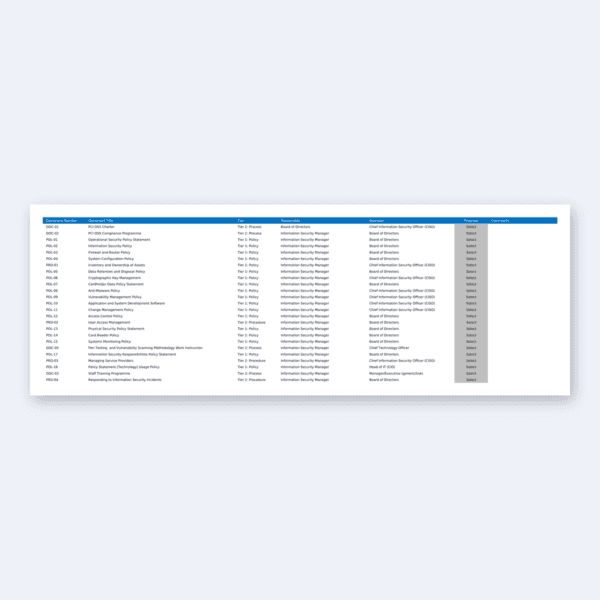
- Master List of Document Approvals
- Master List of Records
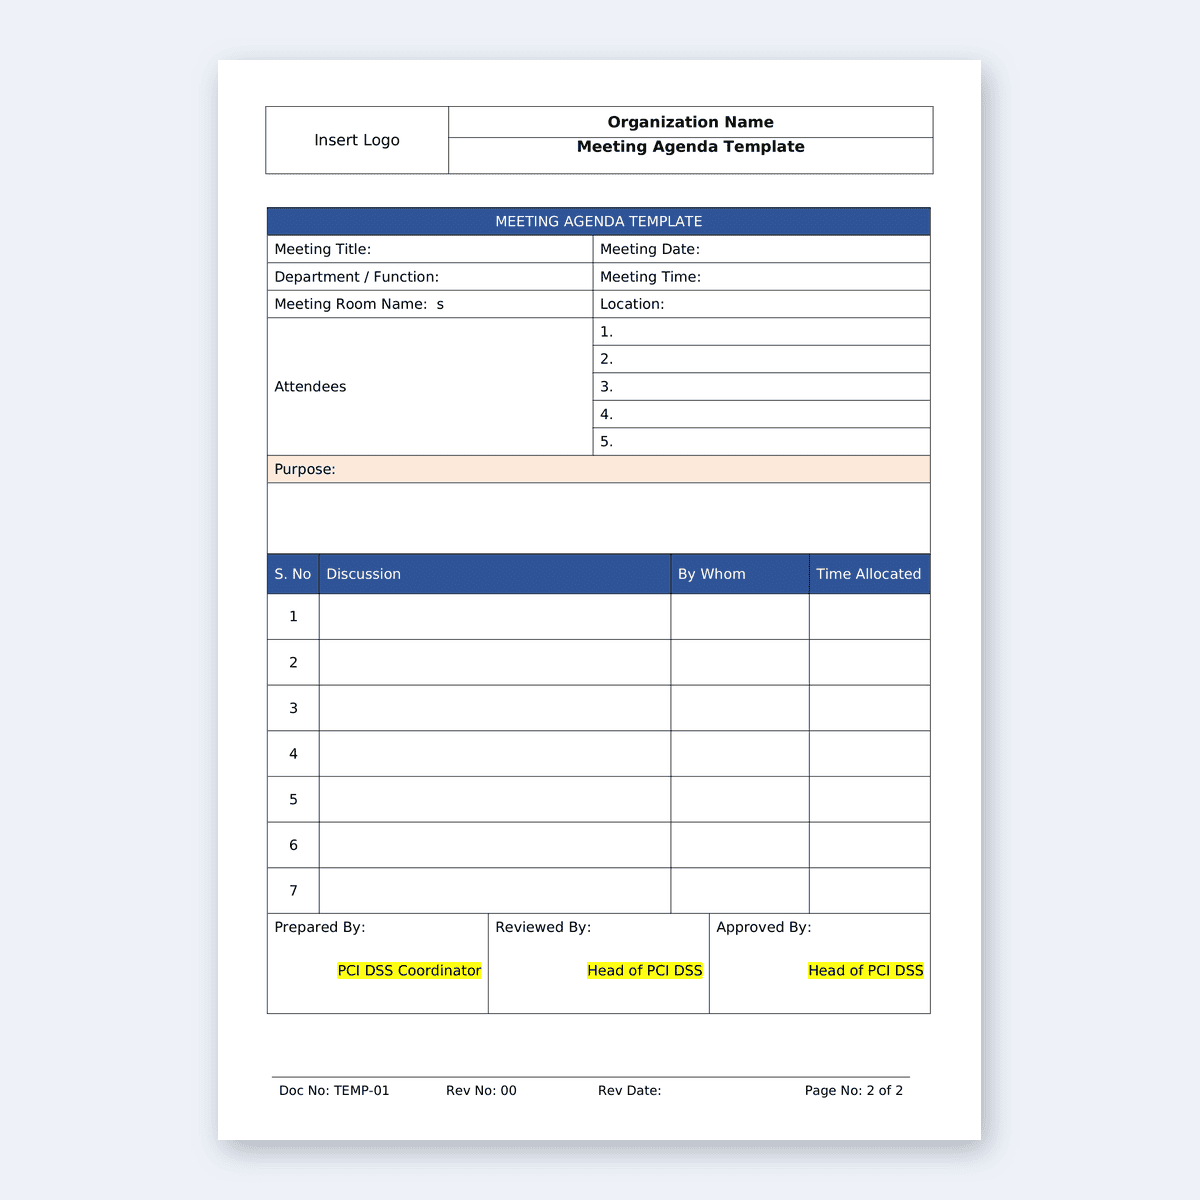
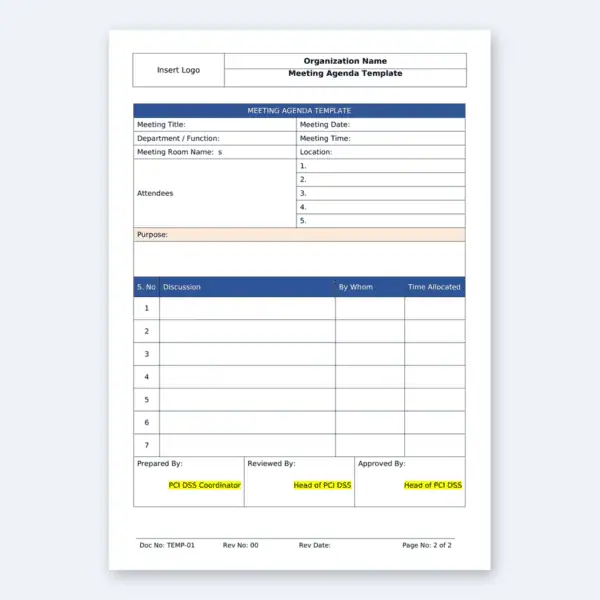
- Meeting Agenda Template
- Meeting Minutes Template v1
- Meeting Minutes Template v2
- Mobile Computing Policy
- Network Access Control Policy
- Network Security Policy
- Network Services Agreement
- Non Disclosure Agreement
- Operating Procedure
- Operational Security Policy Statement
- Outsourced Services Details
- Password Policy Statement
- Payment Page Change and Tamper Detection Procedure
- Payment Page Script Inventory and Authorization Register
- PCI DSS Audit Programme Schedule
- PCI DSS Charter
- PCI DSS Compliance Programme
- PCI DSS Compliance Review Meeting Agenda
- PCI DSS Document Dashboard Version 4.0
- PCI DSS Guidelines and Implementation
- PCI DSS ISO 27001 Clause Mapping — maps PCI DSS v4.0.1 to ISO/IEC 27001:2022 Annex A
- PCI DSS Operational Security Programme
- PCI DSS Recertification Audit Plan
- PCI Scope Inventory
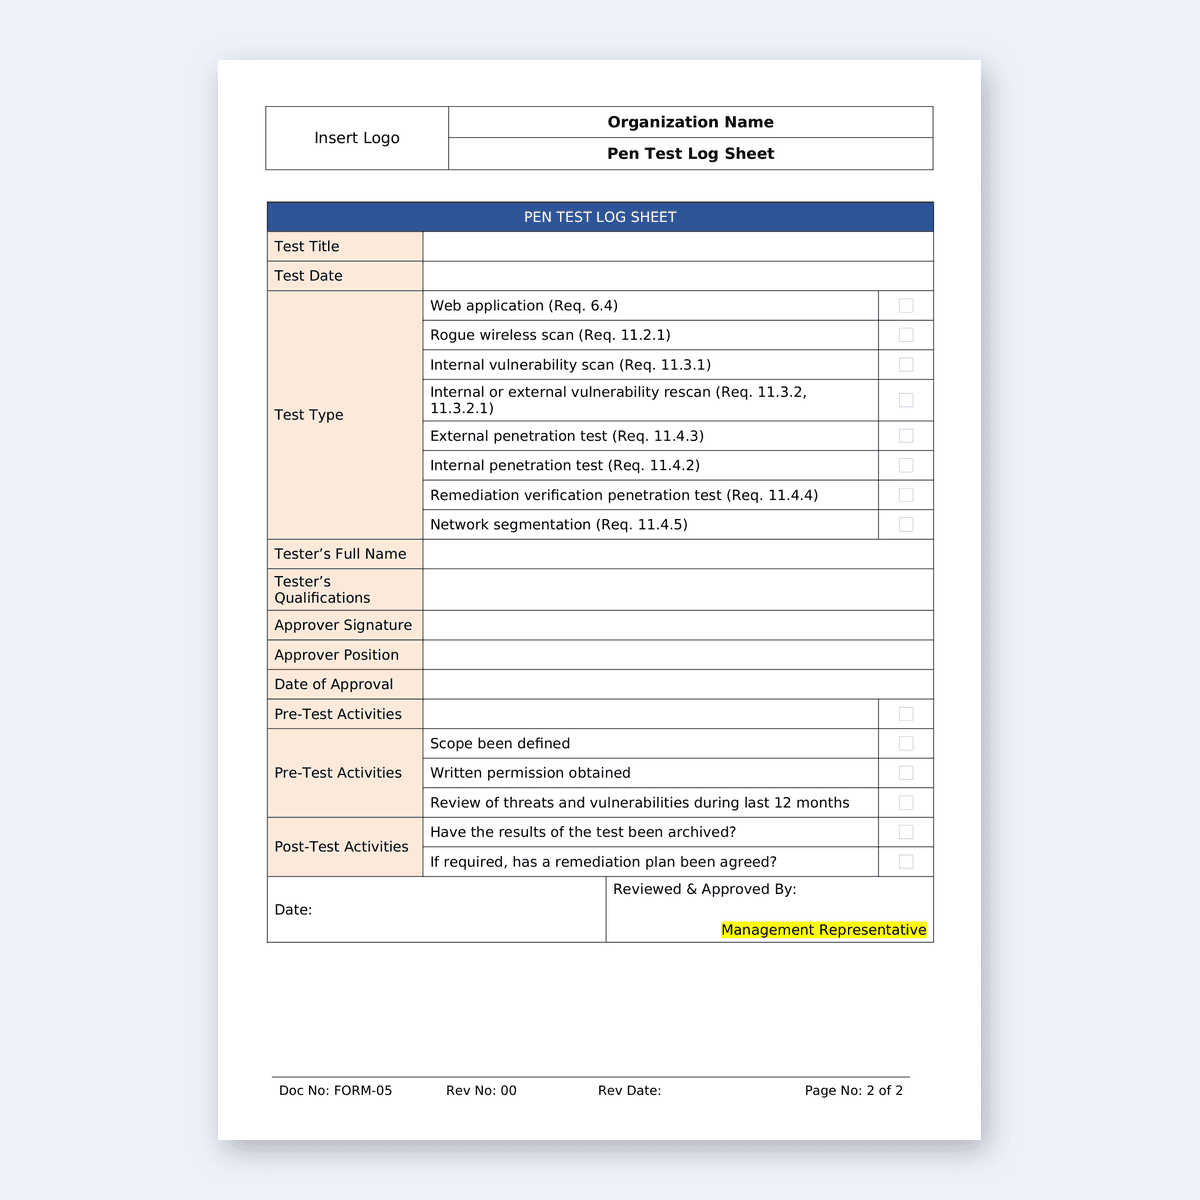
- Penetration Test Log Sheet
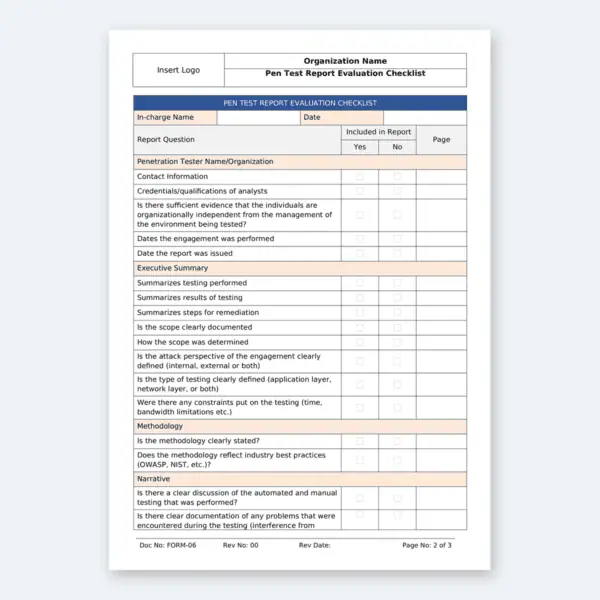
- Penetration Test Report Evaluation Checklist
- Penetration Testing Methodology
- Personal Security
- Physical Media Transfer Procedure
- Physical Security Design Standards
- Physical Security Policy
- Physical Security Policy Statement
- POI Device List
- Policy Statement Technology Usage Policy
- Post Incident Report Template
- Principles for Engineering Secure Systems
- Procedure for Disposal of Media
- Procedure for Management of Removable Media
- Procedure for Monitoring the Use of IT Systems
- Procedure for PCI DSS Audits
- Procedure for Remote Supplier Access to Systems
- Procedure for Reset of User Passwords
- Procedure for Taking Assets Offsite
- Process for Monitoring Measurement Analysis and Evaluation
- Project Highlight Report
- Project Initiation Document
- Project Post Implementation Review
- Records Retention and Protection Policy
- Release and Deployment Management Plan
- Release and Deployment Management Policy
- Release and Deployment Management Process
- Removable Media Assessment Guidelines
- Responding to Information Security Incidents
- Risk Assessment and Treatment Process
- Risk Treatment Plan
- Roles and Responsibilities Matrix
- Rules for Use of Email
- Safe Browsing and Web Filtering Policy
- Secure Coding Policy
- Secure Development Environment Guidelines
- Secure Development Policy
- Secure Information Deletion Policy
- Security Incident Investigation Form
- Segregation of Duties Guidelines
- Service Acceptance Checklist
- Service Level Agreement
- Service Level Agreement Template
- Shared Responsibility Matrix Version 3.2.1 — superseded, retained for historical reference only
- Shared Responsibility Matrix Version 4.0
- Software Policy
- Staff Training Programme
- Supplier Information Security Agreement
- Supplier Information Security Evaluation Process
- Supplier Management Policy
- System Configuration Policy
- System Hardening and Baseline Configuration Procedure
- Systems Monitoring Policy
- Targeted Risk Analysis
- Technical Vulnerability Assessment Procedure
- Technical Vulnerability Management Policy
- Testing Systems and Processes Policy
- Threat Intelligence Policy
- Top Management Communication Programme
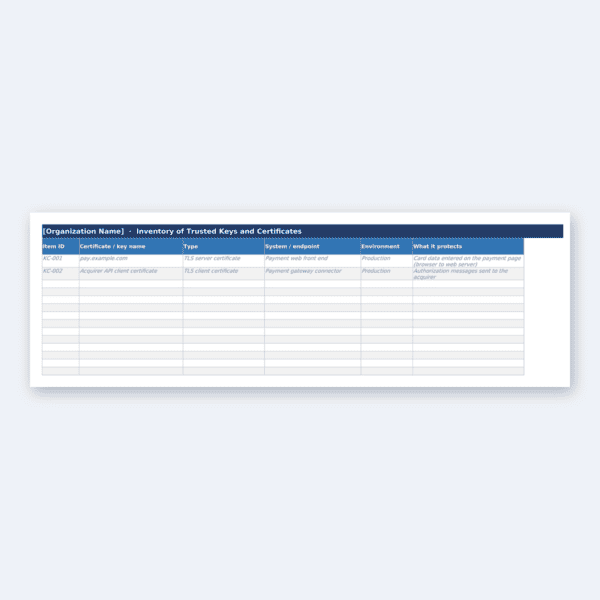
- Trusted Keys and Certificates Inventory
- User Access Management
- User Access Management Process
- Username Administration
- Vulnerability Management Policy
- Warehouse Security
- Web and Mobile Applications Security Standard
- Work Instruction Template
All documents of this toolkit are developed based on PCI-DSS Standard.
Frequently Asked Questions (FAQ)
What is included in the PCI-DSS Toolkit?
The PCI-DSS Toolkit includes 180+ fully editable Microsoft Office templates covering policies, procedures, security standards, checklists, audit plans, agreements, and more. It’s designed to help you implement and maintain PCI-DSS v4.0.1 compliance with practical documents you can customize quickly.
Is this toolkit aligned with PCI-DSS v4.0.1?
The policy, procedure and standard documents are written to PCI-DSS v4.0.1, the current version of the standard; the pack also keeps a legacy v3.2.1 documentation-analysis tool for organisations still tracking the older numbering. PCI DSS v4.0.1 was published in June 2024 and v4.0 was retired on 31 December 2024. It ensures your organization can demonstrate full compliance with modern data security guidelines for handling cardholder information.
Who should use the PCI-DSS documentation toolkit?
This toolkit is ideal for merchants, service providers, IT managers, auditors, cybersecurity professionals, and consultants. Whether you’re building a PCI-compliant environment or preparing for a recertification audit, this pack simplifies every step of the process.
Can I customize the PCI-DSS documents for my company?
Absolutely. All documents are provided in editable Microsoft Word and Excel formats. Example text is clearly highlighted to show where you need to insert your company name, policies, or specific procedures. You can also add your logo and branding for professional presentation.
How does this toolkit help with PCI compliance audits?
The toolkit includes everything needed to prepare for PCI-DSS compliance audits — from access control and incident management policies to risk assessments and audit checklists. These ready-to-use documents save time and help you confidently meet auditor expectations.
Does the toolkit cover technical and physical security controls?
Yes, the toolkit covers a wide range of security controls including technical (e.g., secure coding, vulnerability management, data masking) and physical (e.g., physical security policies, offsite asset procedures). This makes it a complete resource for PCI-DSS scope management.
How do I access the documents after purchase?
Once your payment is complete, you’ll receive an instant download link. All 180+ documents are neatly organized into folders, making it easy to find and start customizing the files relevant to your PCI-DSS implementation or audit process.
Is this toolkit created by qualified experts?
The PCI-DSS toolkit is published by Governance Docs and checked against the PCI DSS v4.0.1 requirement numbering; each document is written to be practical to adopt. You remain responsible for validating it against your own scope and your assessor’s expectations.
Find More Products:
Implementing for clients? The Consultant Package bundles 89 toolkits — 8,100+ editable templates — under one firm-wide licence that covers unlimited client engagements. $1,399 one-time.
Guides for the PCI-DSS Toolkit
Free articles that explain the requirements this toolkit covers.


 PCI-DSS Toolkit - Comprehensive 180+ Templates$99.00












Really useful collection of templates that made handling PCI compliance much easier and saved me plenty of time.