

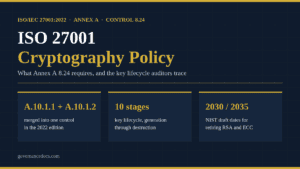
ISO 27001 Cryptography Policy: The Complete 2026 Guide
An ISO 27001 cryptography policy satisfies Annex A 8.24, which merged two 2013 controls into one. The 10…
CART
An ISO 27001 cryptography policy satisfies Annex A 8.24, which merged two 2013 controls into one. The 10…
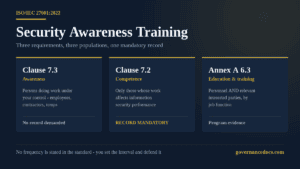
ISO 27001 security awareness training is 3 requirements, not 1: clause 7.3, clause 7.2 and Annex A 6.3.…
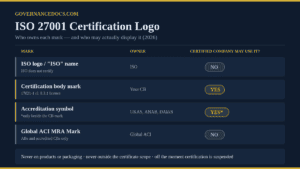
ISO 27001 certification logo rules for 2026: ISO bans its own logo outright, and ISO/IEC 17021-1 clause 8.3…
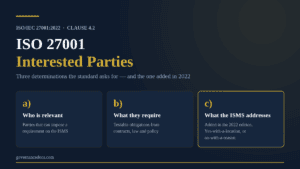
ISO 27001 interested parties under clause 4.2 – how to build a register that answers all 3 requirements,…
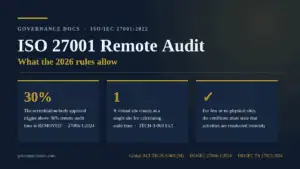
ISO 27001 remote audit rules changed in 2024: the 30% approval cap is gone, but your certificate must…
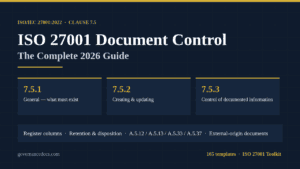
ISO 27001 document control explained: what clause 7.5 really requires, the 10 register columns auditors sample, and the…
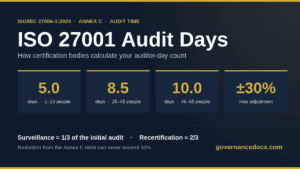
ISO 27001 audit days come from ISO/IEC 27006-1 Annex C, not your budget. Typical counts run 5 to…
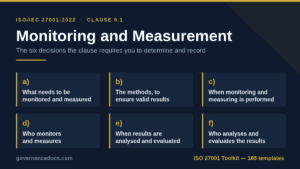
ISO 27001 monitoring and measurement explained: the six decisions clause 9.1 requires, 14 worked measures, and the 5…
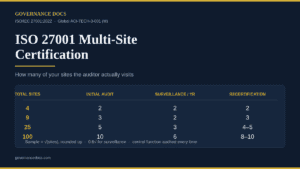
ISO 27001 multi-site certification explained: the square-root sampling rule, the six eligibility tests, and why 25 sites means…
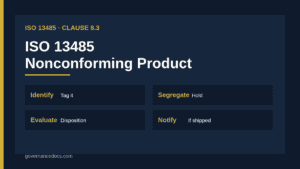
How to control ISO 13485 nonconforming product under clause 8.3: identification, segregation, concessions, rework, advisory notices and the…
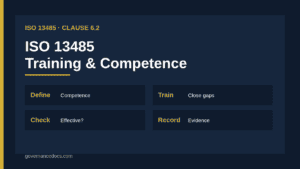
How to meet ISO 13485 training and competence requirements under clause 6.2, with a training matrix, effectiveness checks…
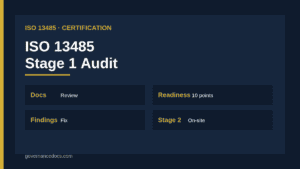
What happens in an ISO 13485 stage 1 audit, what the auditor reviews, a ten-point readiness checklist and…
October 8, 2026
October 7, 2026
October 7, 2026
October 6, 2026
October 6, 2026