CART
No products in the cart.
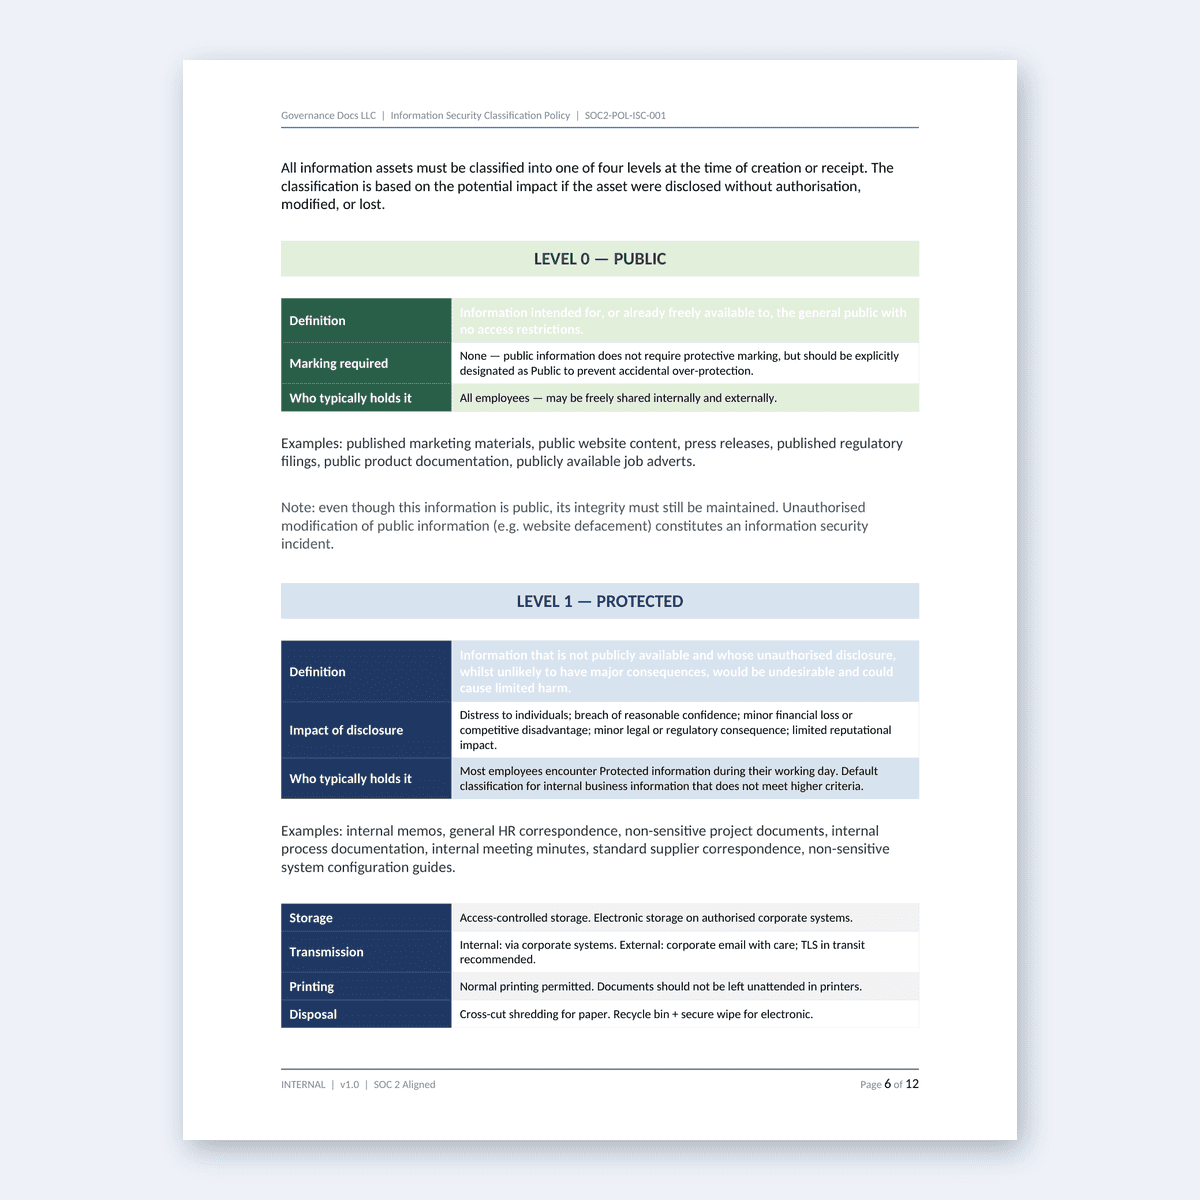
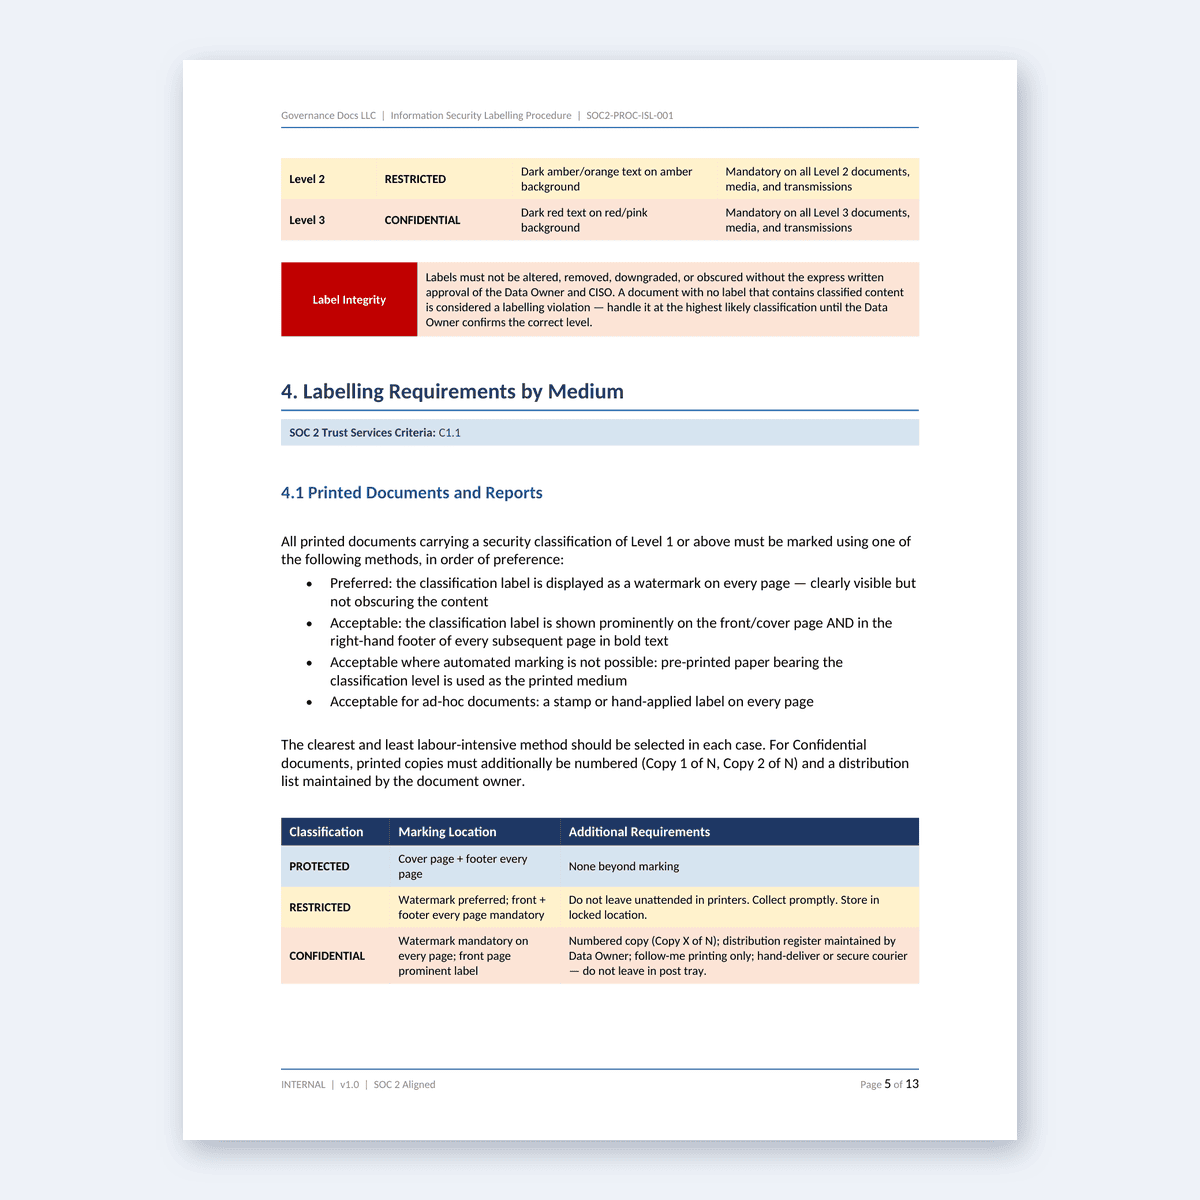
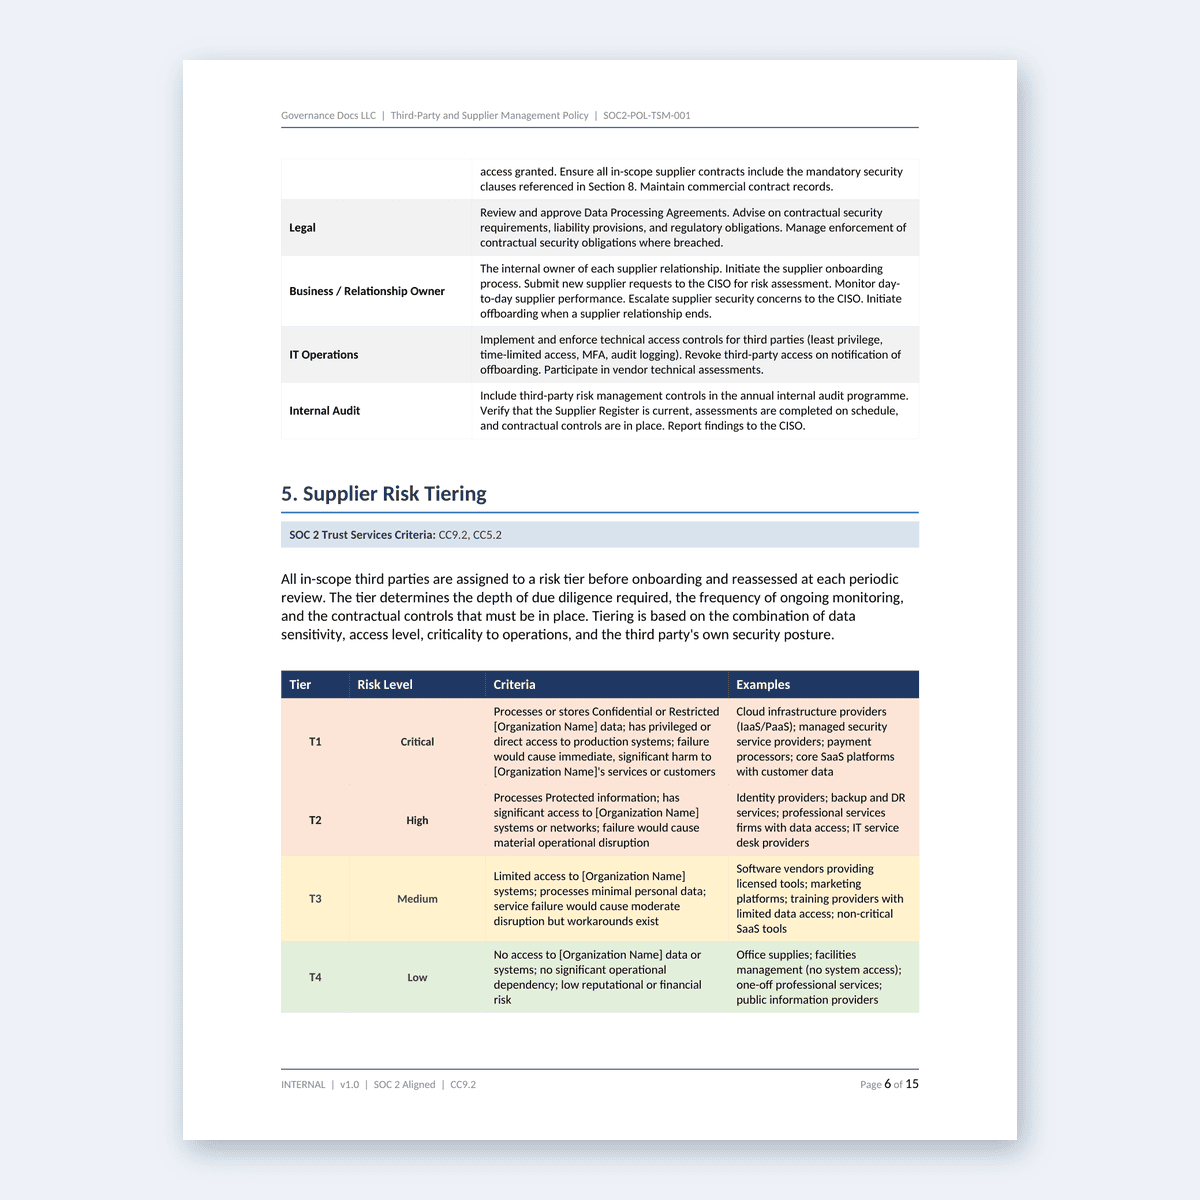
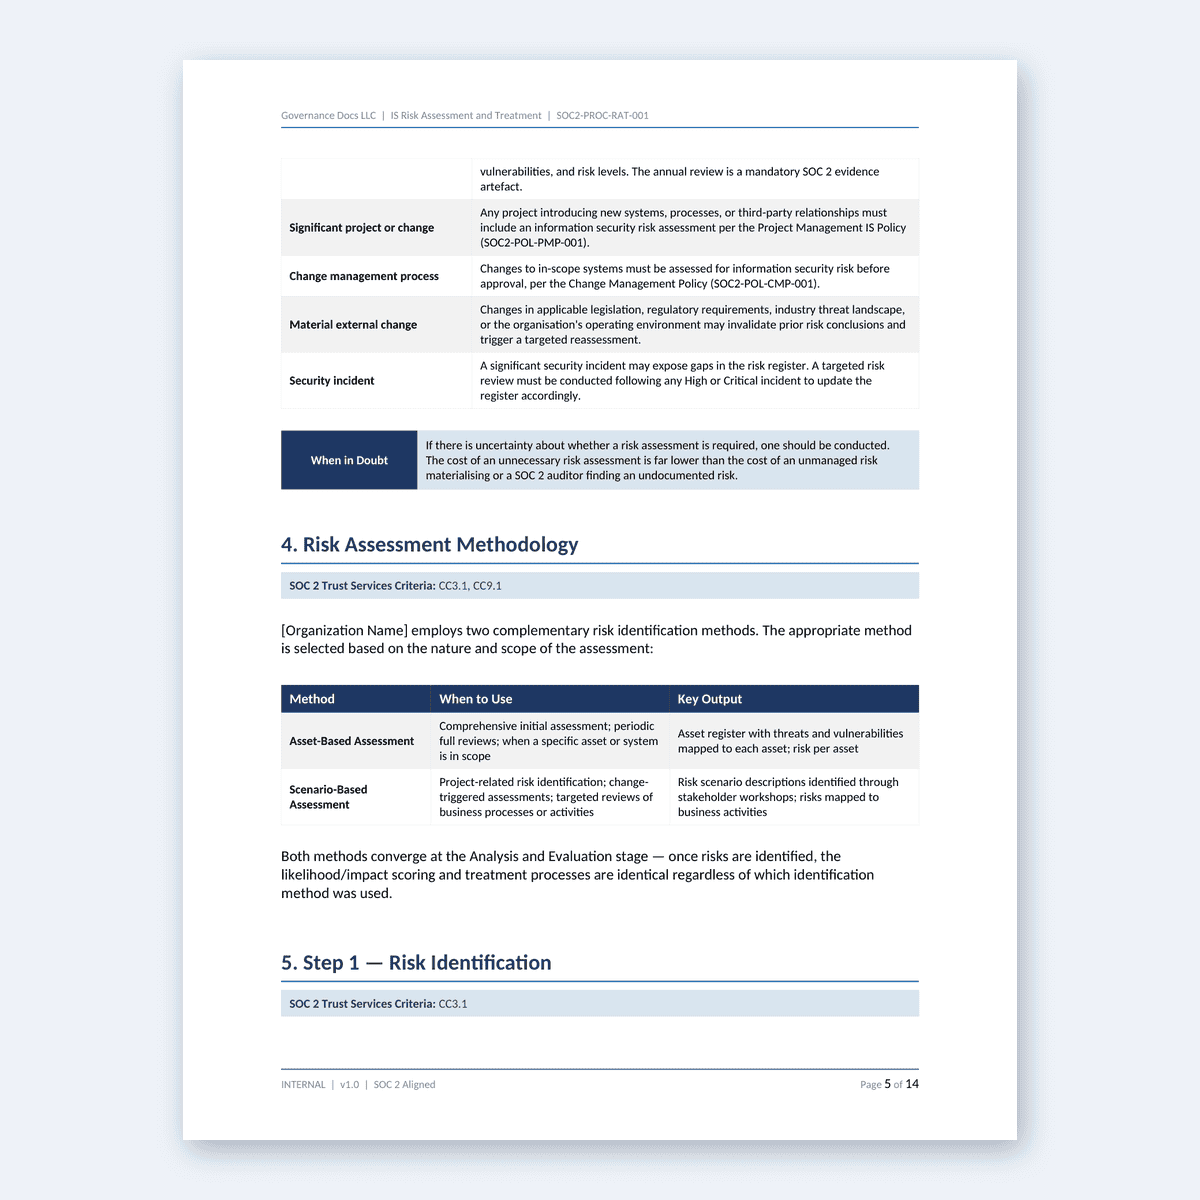
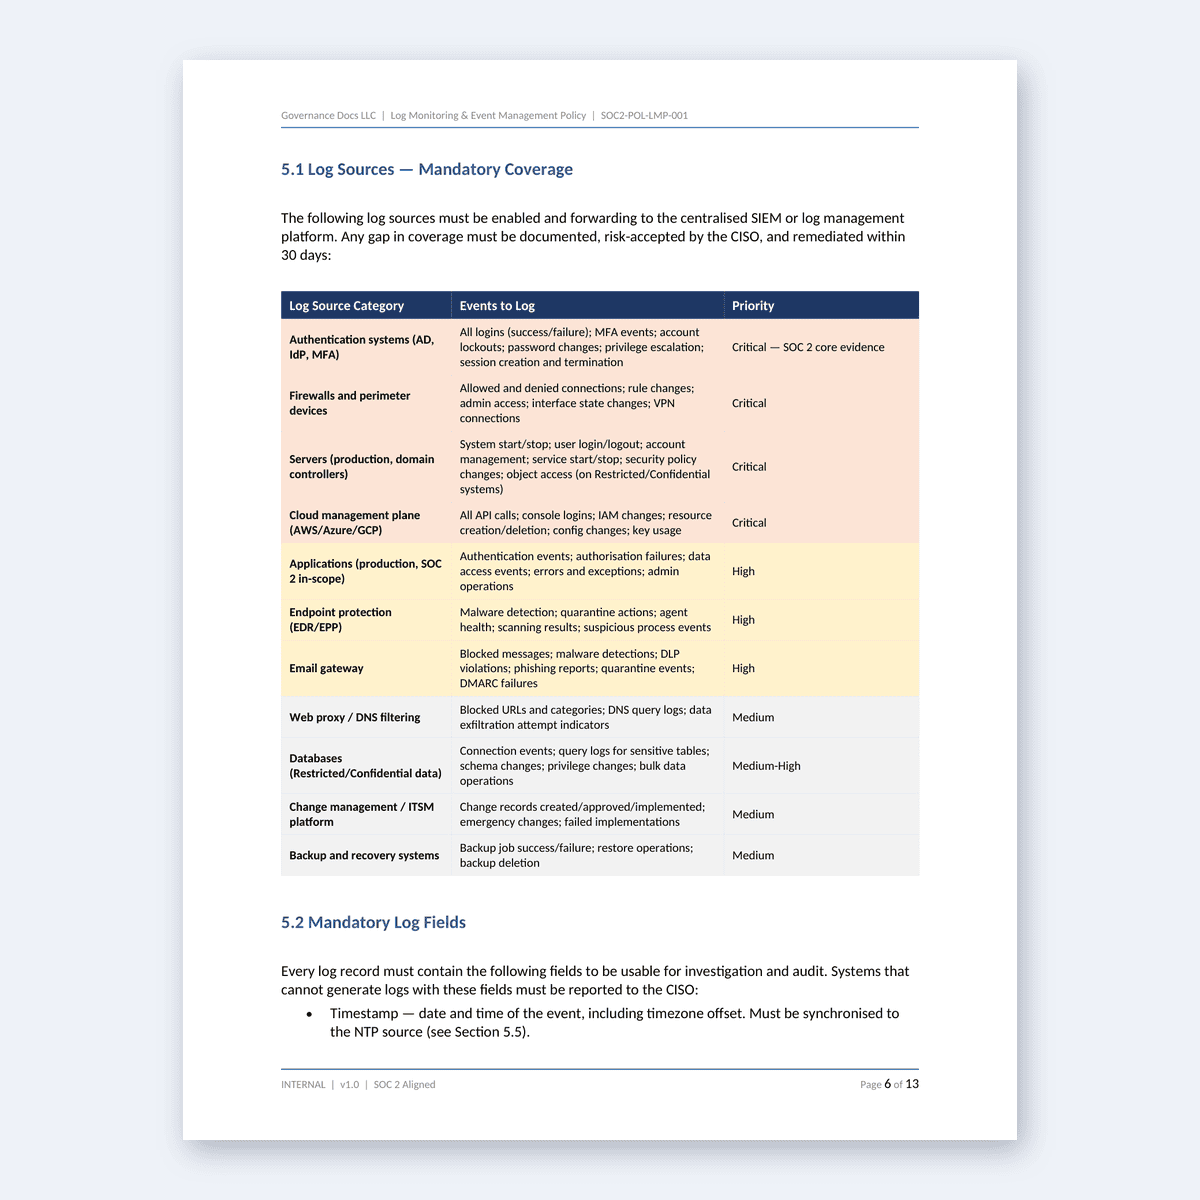
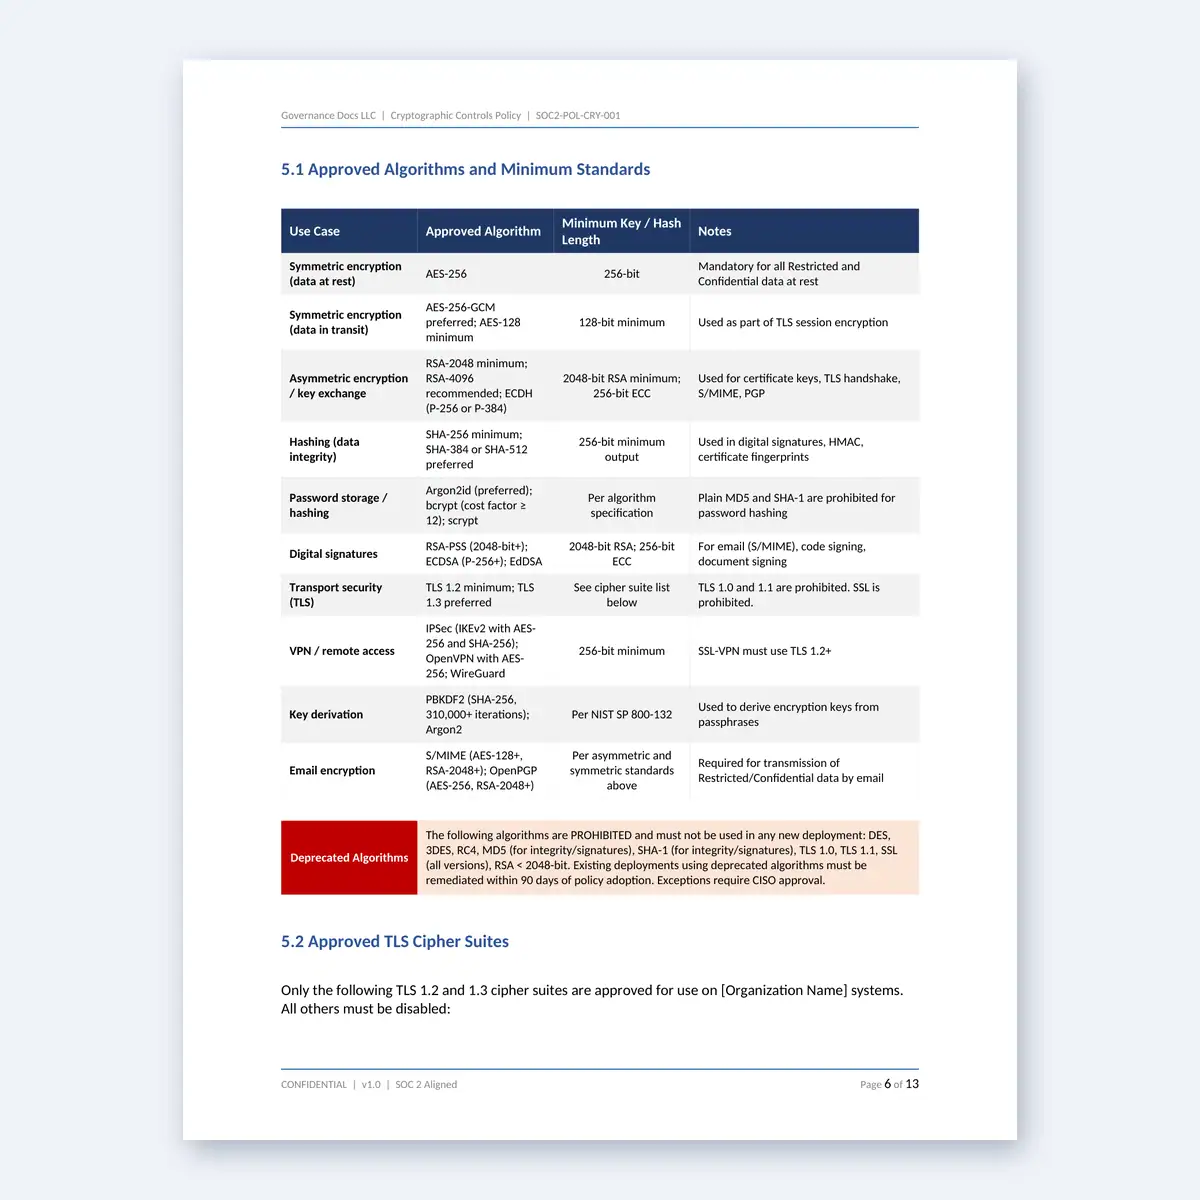
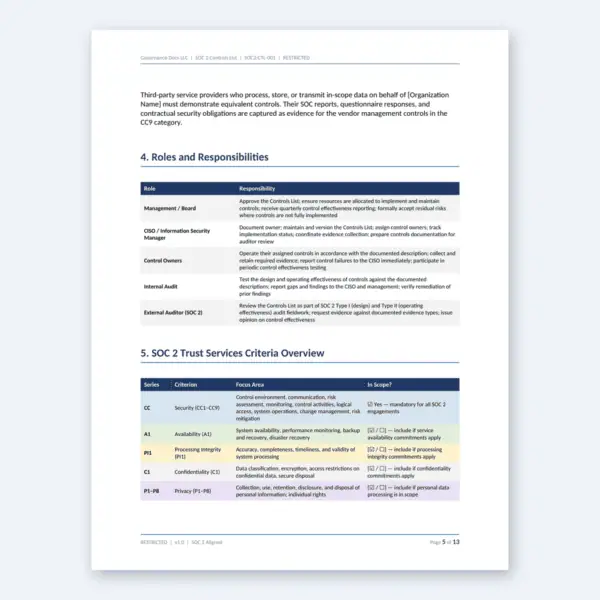
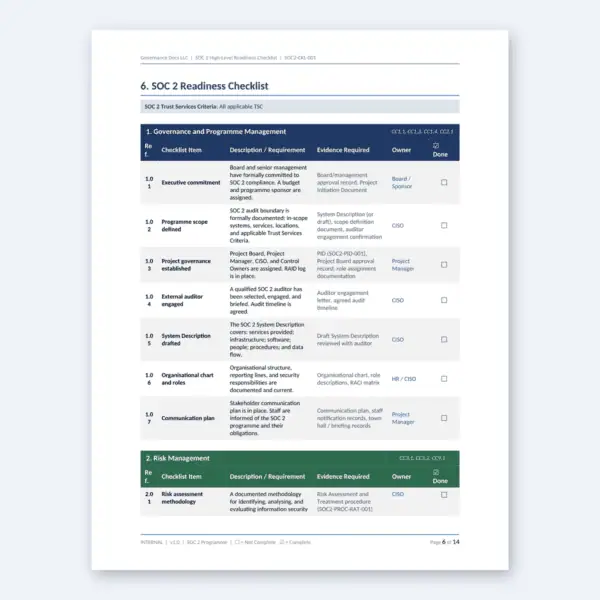
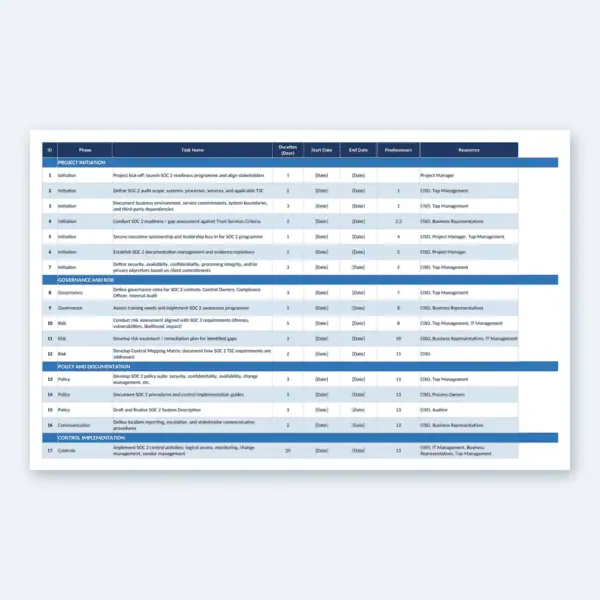
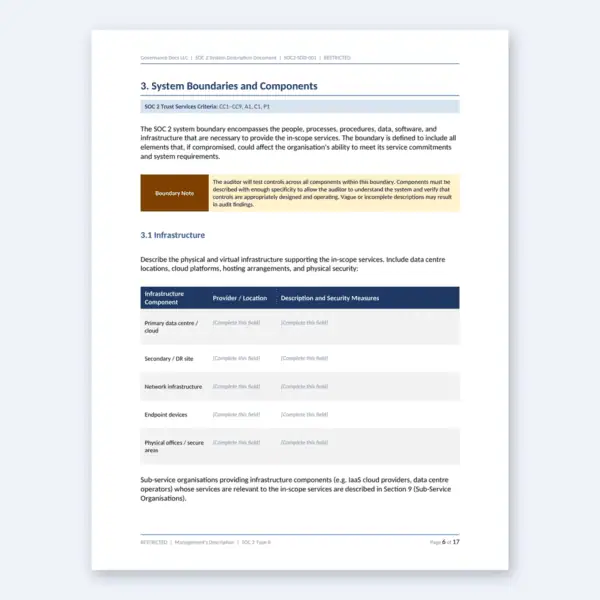
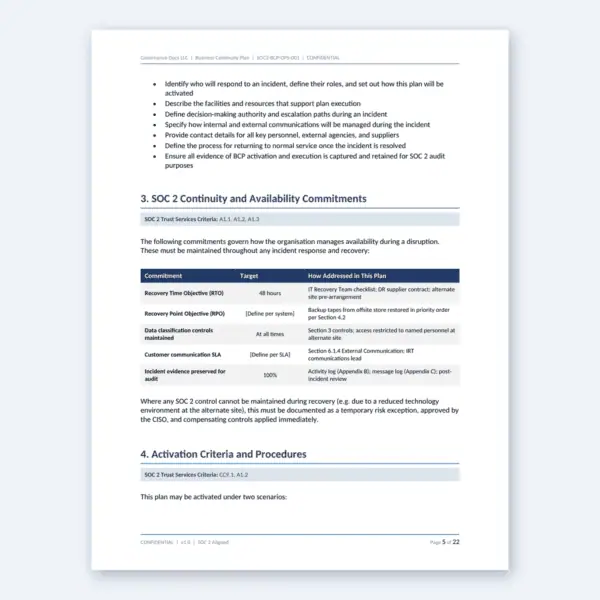
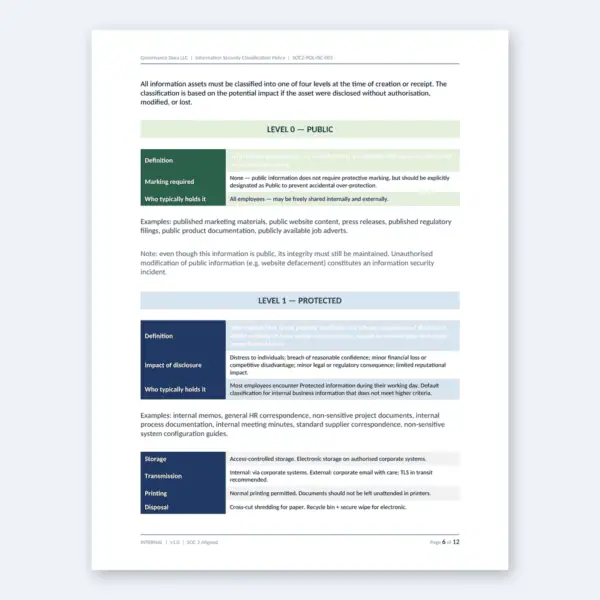
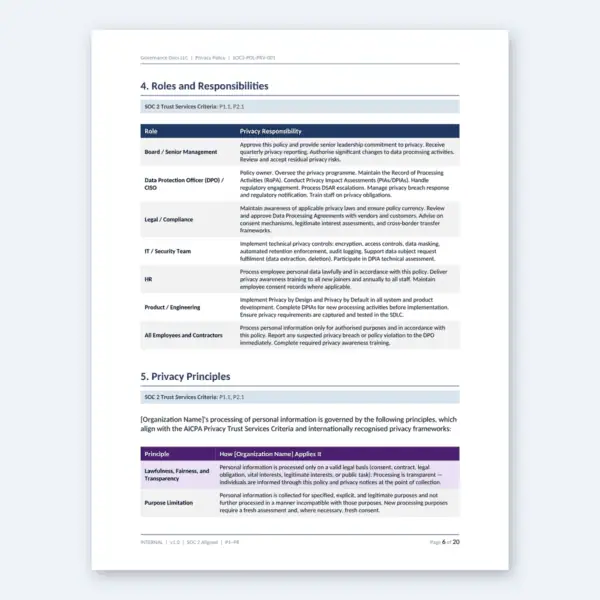
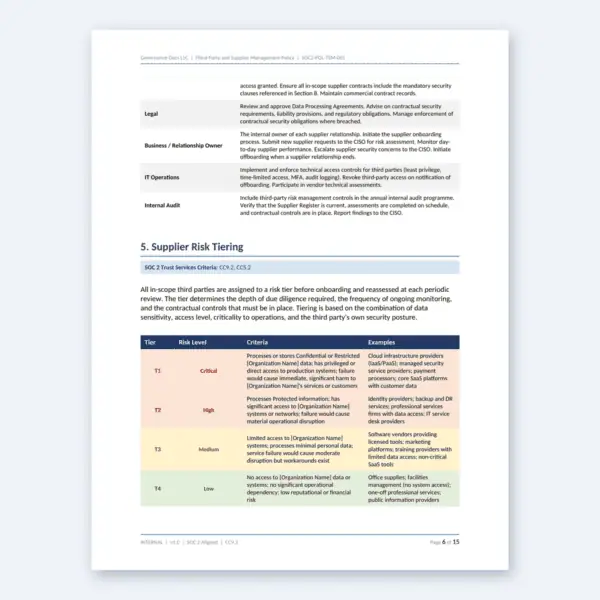
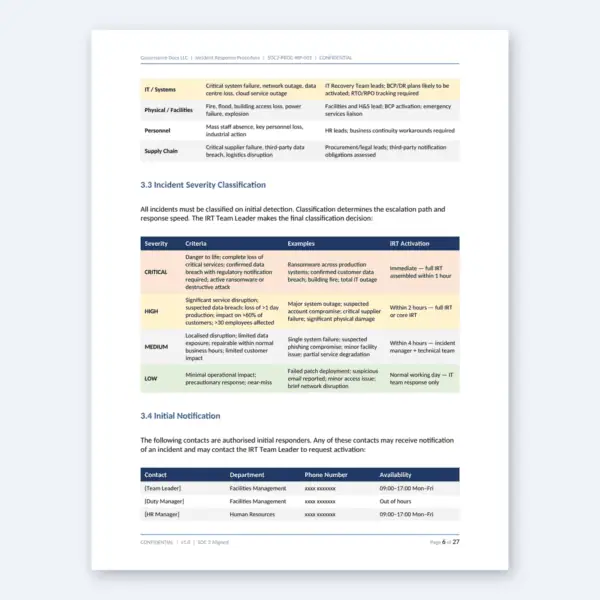
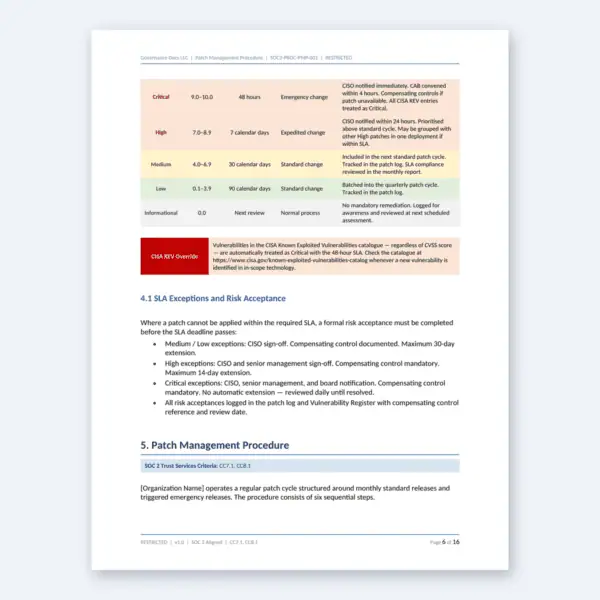
Safeguard your business and ensure compliance with our SOC 2 Toolkit. Designed specifically for service organizations that process customer data, this comprehensive toolkit equips you with the essential resources to navigate the complexities of SOC 2 Trust Services Criteria and audit requirements.
Version 2 (November 2026): all templates are professionally formatted, with branded full-page cover pages and consistent styling across every Word document and workbook.
$99.00
✓ In stock — instant download after checkout
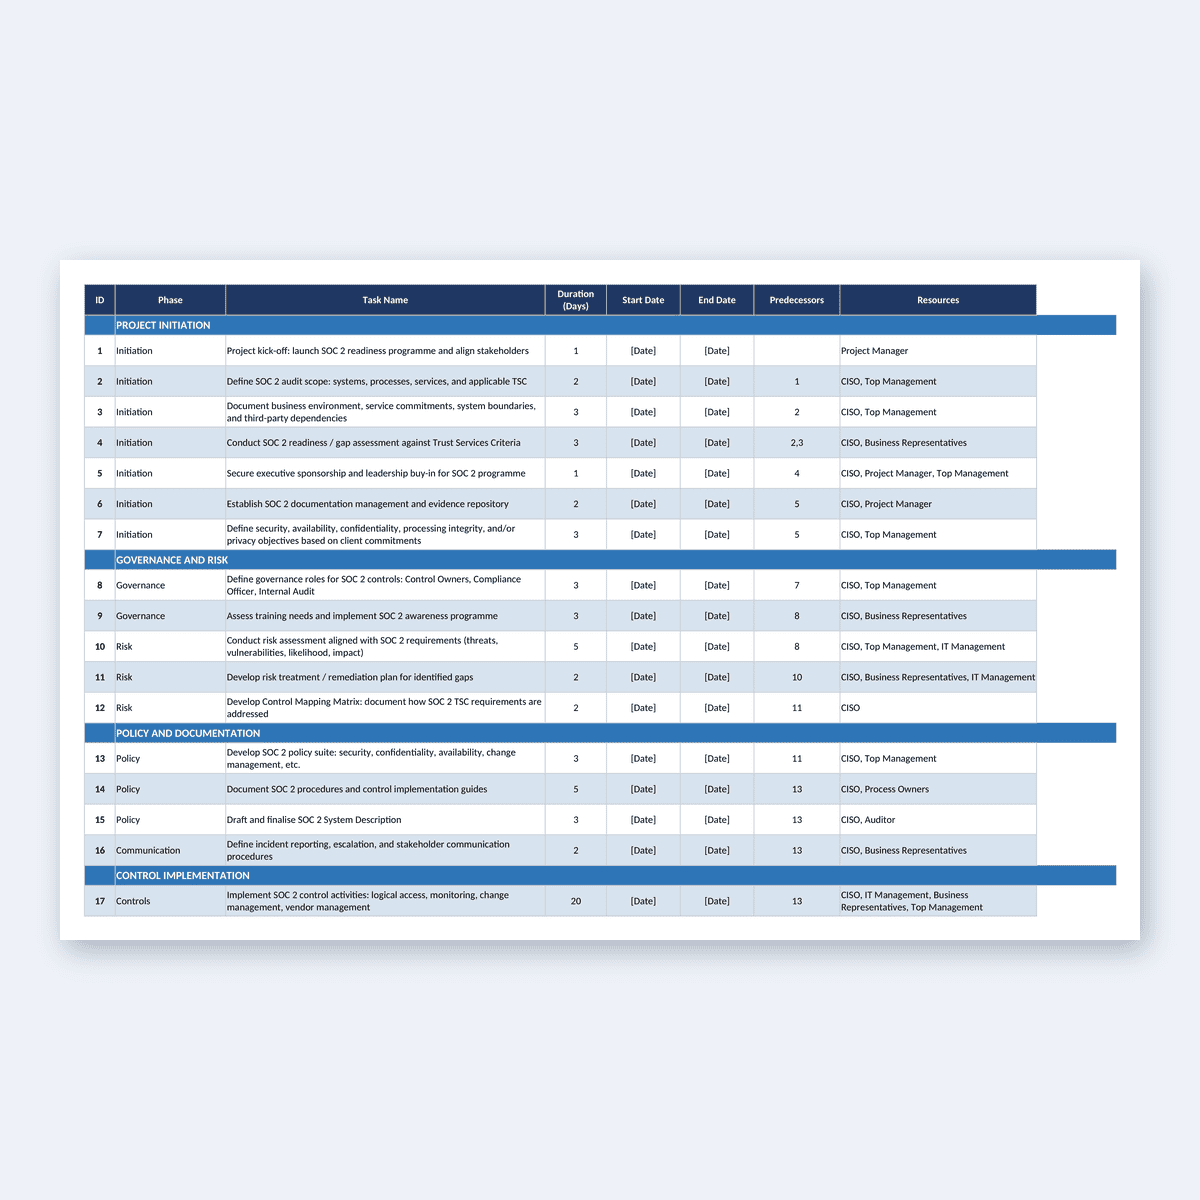
At a glance: the SOC 2 Toolkit is an editable Microsoft Word and Excel documentation set for SOC 2 readiness against the AICPA Trust Services Criteria. It is mainly a policy set (access control, change management, backup and recovery, cryptography, data retention, acceptable use and more) plus incident and vendor management documents. One-time price $99, instant download, licensed for internal use by one organisation. Implementing for several clients? The Consultant Package covers unlimited client engagements.
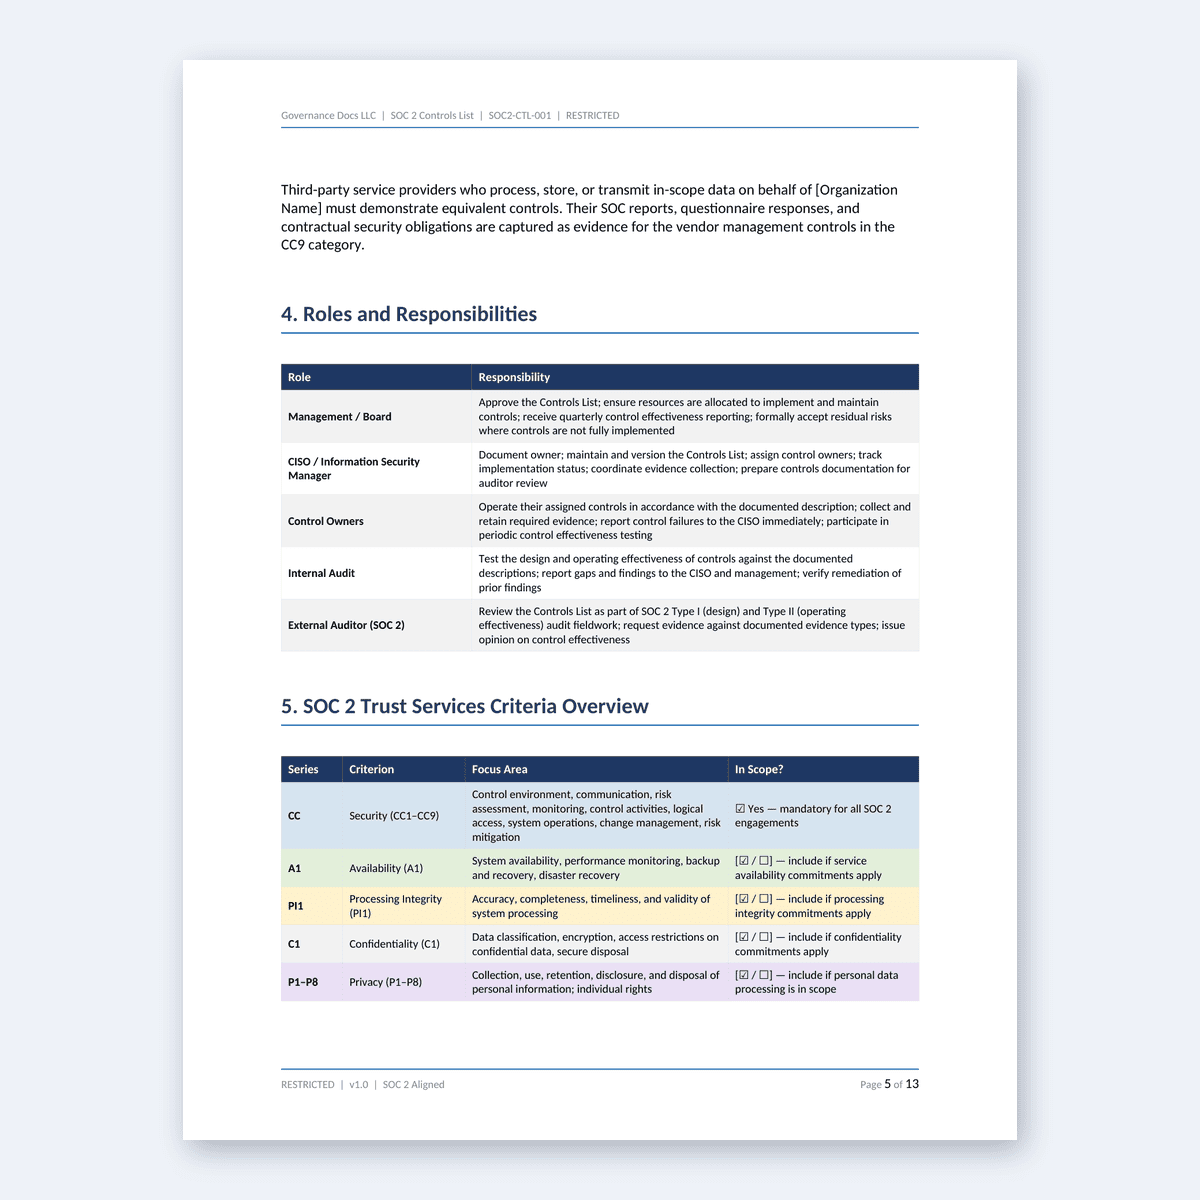
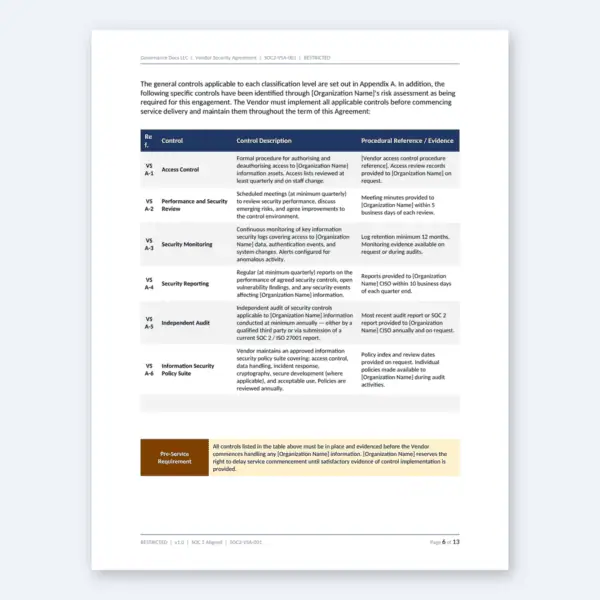
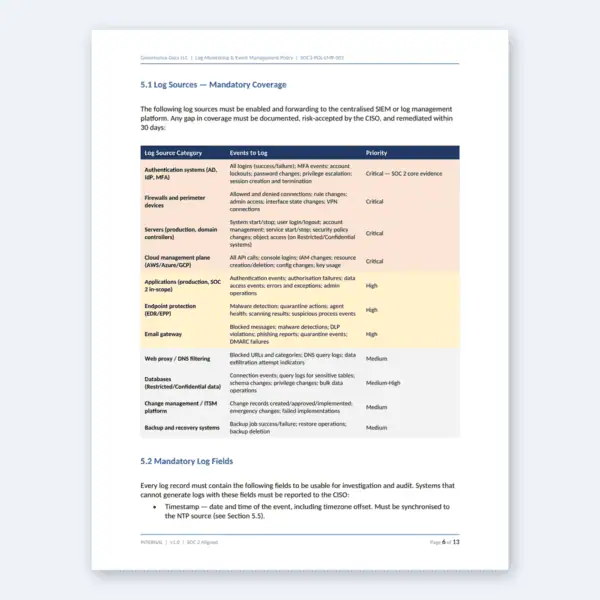
Last updated 3 November 2026. Version 2: all 71 Word documents now open with a branded full-page cover showing the document code, type and classification, followed by a Document Information page that keeps each document’s Trust Services Criteria scope, and both workbooks gain a cover sheet. This release also removes statements implying SOC 2 sets retention periods, resets the controls list status column to blank for you to complete, labels the BCP exercise report as a worked example, uses SOC 2 report (attestation) wording throughout, and updates the incident notification guidance. It also corrects the Trust Services Criteria references throughout and adds 13 new documents: an evidence (PBC) request list, an internal audit and monitoring plan, a code of conduct, a board oversight charter, a whistleblower procedure, a fraud risk assessment, registers for information assets, suppliers, security incidents and training, a user access review record, a management assertion template and a bridge letter template with SOC 3 guidance.
SOC2 Toolkit is used to help organizations strengthen information security, enhance customer trust, and ensure compliance with the SOC 2 framework.
This toolkit is specifically designed for service organizations that need to demonstrate adherence to the AICPA Trust Services Criteria (TSC) across Security, Availability, Processing Integrity, Confidentiality, and Privacy. The SOC 2 Toolkit equips you with the essential documentation and processes to meet SOC 2’s stringent audit and assurance requirements.
SOC2 Toolkit provides an all-encompassing package of meticulously crafted documents covering every critical element of SOC 2 compliance. From developing security policies and incident response procedures to managing vendor risk and evidence collection for audits, this Assured Toolkit ensures your organization is prepared for both auditor scrutiny and client expectations.
Each document is published by Governance Docs and drafted against the AICPA Trust Services Criteria; you review the finished documents against your own control environment before an audit. The templates are fully customizable, making it simple to adapt them to your organization’s unique structure and operations, saving you valuable time and resources.
Ensure audit readiness, mitigate compliance risks, and build trust with clients and stakeholders. Invest in this Premium Toolkit today and create a robust framework for SOC 2 compliance that reinforces your organization’s credibility and reputation.
The SOC2 compliance framework requires service organizations to implement and maintain effective controls that safeguard data across the Trust Services Criteria (TSC): Security, Availability, Processing Integrity, Confidentiality, and Privacy. Compliance with SOC 2 is not just an audit requirement but a business imperative to protect sensitive data, ensure service reliability, and build trust with clients and stakeholders.
SOC2 compliance helps organizations demonstrate accountability and preparedness by showing that they have strong controls to prevent breaches, downtime, and data misuse. It mitigates financial, legal, and reputational risks associated with security incidents and provides assurance to customers that their data is handled with the highest level of integrity.
Adopting SOC 2-aligned practices enhances organizational governance, improves risk management, and positions businesses as leaders in secure and reliable service delivery. It also ensures that organizations are prepared to meet increasing client, partner, and regulatory expectations in a rapidly evolving digital environment.
Additionally, achieving SOC 2 compliance creates a competitive advantage, fostering stronger customer relationships and differentiating your organization as a trusted, security-conscious service provider in the global marketplace.
Simply add your organization’s name and logo to the documents and ensure the implementation of the documented policies and procedures within your operational framework.
All documents in this Toolkit are developed based on the AICPA’s SOC2 Trust Services Criteria (TSC), covering Security, Availability, Processing Integrity, Confidentiality, and Privacy. However, they are adaptable for use in other assurance or compliance frameworks with minimal adjustments, making them versatile and suitable for broader governance and regulatory environments.
Ready to strengthen your compliance posture and build client trust? Invest in the SOC2 Toolkit and take the first step towards achieving audit readiness, operational excellence, and sustained credibility.
Implementing for clients? The Consultant Package bundles 89 toolkits — 8,100+ editable templates — under one firm-wide licence that covers unlimited client engagements. $1,399 one-time.
Want to see the documents first? Five templates from this toolkit are free by email — get the SOC 2 samples.
Free articles that explain the requirements this toolkit covers.
Sorry, no reviews match your current selections
 SOC2 Toolkit - Premium Documentation Pack$99.00



















Really helpful documents that made SOC 2 preparation much easier and more organized.
A polished and practical documentation pack that makes audit preparation much smoother.