Description
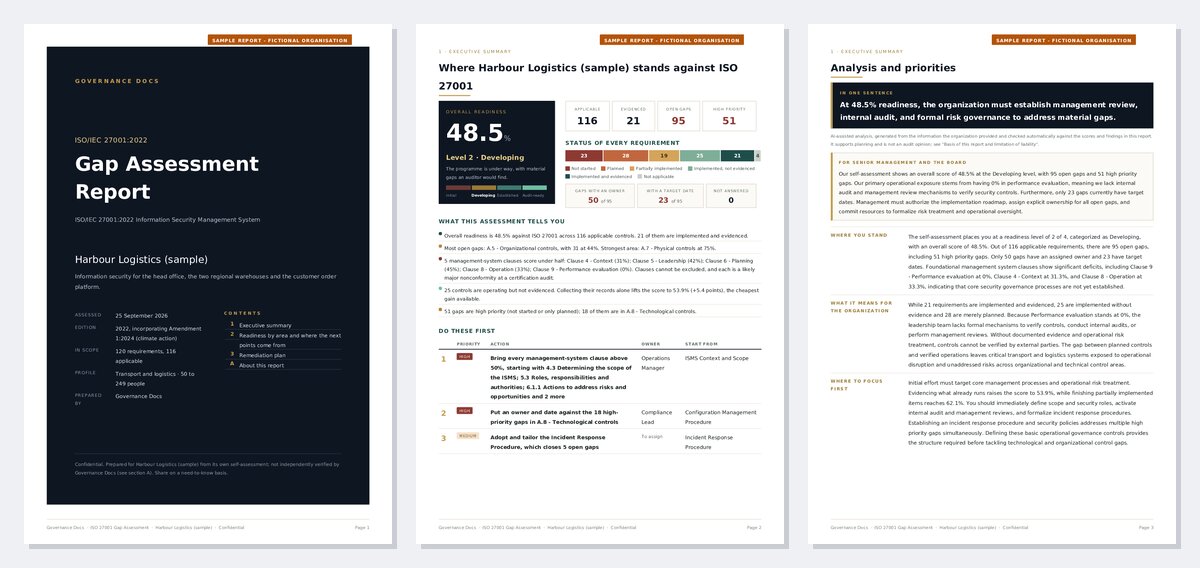
At a glance: the ISO 27001 Toolkit is an editable Microsoft Word and Excel documentation set for ISO/IEC 27001:2022 and its Annex A controls. It covers the ISMS scope, risk assessment and treatment, the Statement of Applicability, topic policies and procedures, internal audit and management review. One-time price $99, instant download, licensed for internal use by one organisation. Implementing for several clients? The Consultant Package covers unlimited client engagements.
Before you buy, you can draft your own Statement of Applicability free with our ISO SoA Generator, then use the toolkit to build the rest of the ISMS.
About the ISO 27001 Toolkit
Last updated 31 October 2026. Aligned to ISO/IEC 27001:2022 including Amendment 1:2024, which added the climate-action requirements to clauses 4.1 and 4.2. Purchase includes 12 months of free updates.
This ISO 27001 Toolkit is an editable documentation set for implementing an Information Security Management System (ISMS) in accordance with ISO/IEC 27001:2022.
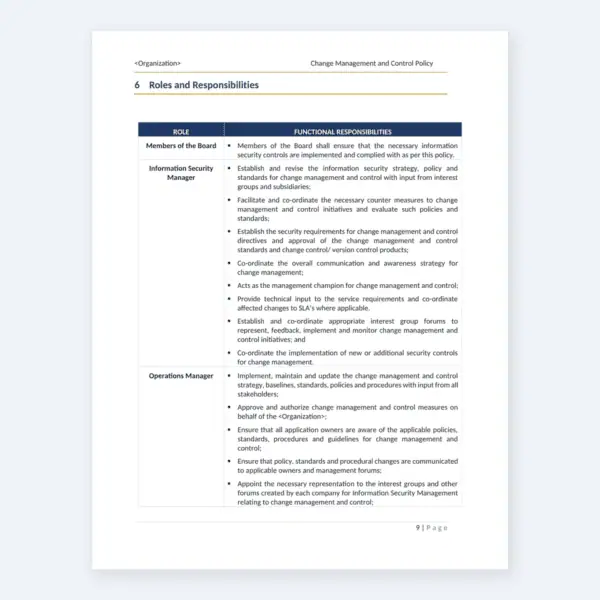
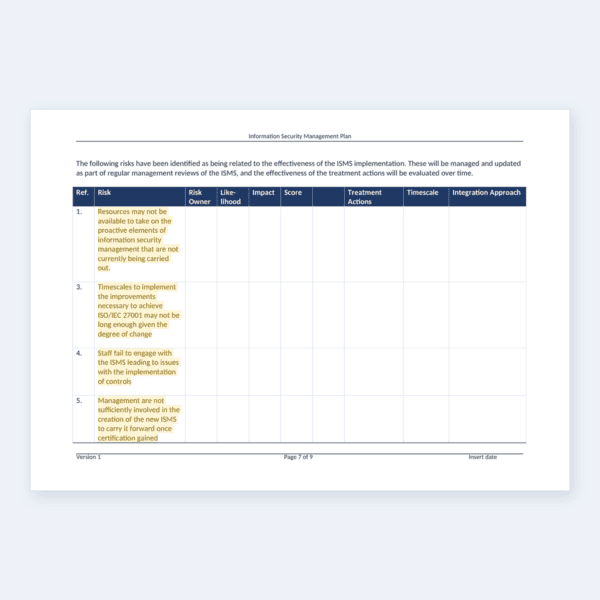
Developed in Microsoft Office format, the documents are fully customizable to address your organization’s unique requirements. Each template is structured with standard content and includes clearly highlighted example text to guide users in providing the necessary organization-specific details. Additionally, full example documents are included to support a smooth and effective implementation process.
This toolkit not only simplifies your ISO 27001 implementation but also serves as a vital resource for awareness and training in cybersecurity best practices. Designed for business leaders, compliance professionals, it provides structured guidance to streamline your journey toward certification. Whether you’re seeking to establish a solid ISMS foundation or enhance existing controls, this toolkit ensures you have the right resources and support for a seamless compliance process. Enhance Your ISO 27001 Implementation with Expert Support and Training.
About the publisher
Published by Governance Docs, this ISO 27001 toolkit is drafted against the text of ISO/IEC 27001:2022 and supplied in a user-friendly, ready-to-use format.
Governance Docs have created this pack to comply with ISO IEC 27001:2022 standard and ISO 27002:2022
What is included in the toolkit?
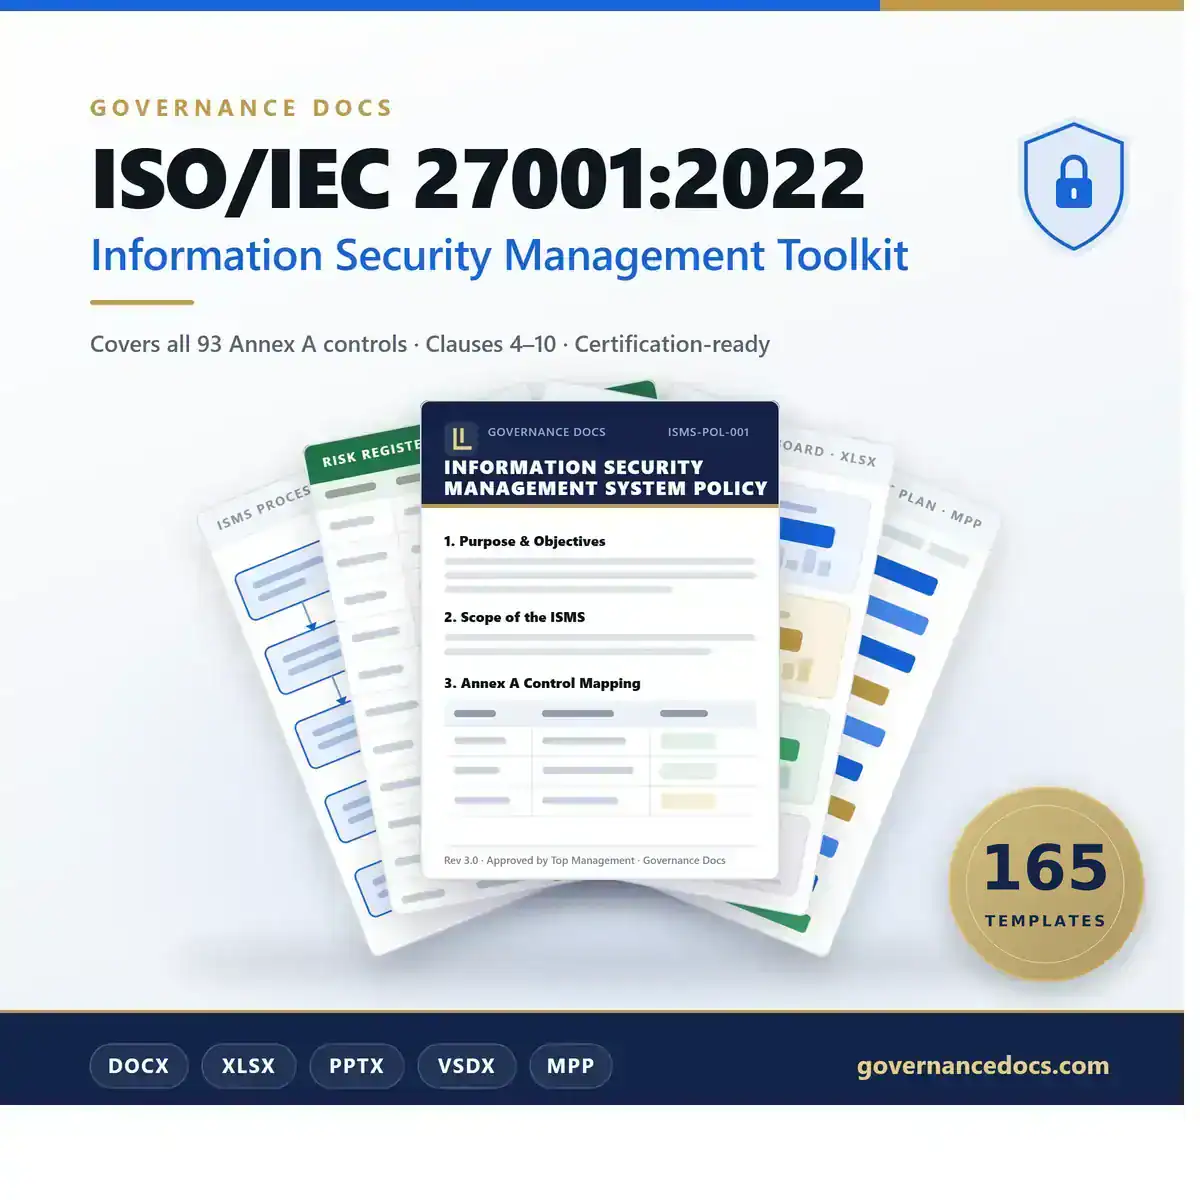
- 165 ISO 27001 Documentation Templates – including policies, procedures, controls, checklists, tools, presentations, and other helpful documentation
- Available as an instant download after purchase
- Organised into 13 numbered folders that follow the ISMS lifecycle, from framework and leadership through risk, the Annex A control areas, audit and improvement, so every document is easy to find (full folder list below)
- Professionally formatted: every Word document has a branded cover page, consistent navy headings, styled tables and highlighted fill-in fields; the Excel workbooks keep their formulas, macros and dashboards
- Updated for ISO/IEC 27001:2022 Amendment 1:2024 — the internal audit checklist covers the climate-action requirements added to clauses 4.1 and 4.2 in February 2024, which certification bodies now assess at every audit
- Three Excel workbooks with live dashboards — a 77-question internal audit checklist covering every sub-clause of Clauses 4–10 and all 93 Annex A controls, cross-referenced in both directions; a risk treatment plan with inherent and residual scoring and heat maps; and a documented information register that tracks version, review and approval dates automatically
165 ISO 27001 Document Templates
Information Security Management System (ISMS) Documentation pack
A complete and comprehensive documentation package designed to assist clients, consultants, and service providers in successfully achieving compliance with ISO 27001:2022.
ISO 27001 Toolkit folder structure
The download is organised into 13 numbered folders that follow the order of an ISO 27001 implementation: framework and leadership first, then risk and the Statement of Applicability, support, the Annex A control areas, performance evaluation, improvement and the implementation project. It contains 180 files in total: 165 editable templates (136 Word, 21 Excel, 2 PowerPoint, 5 Visio and 1 MS Project), 12 process diagram images, an introduction email template, a read-me note on the Excel templates and the licence. Expand a folder to see every file.
01 ISMS Framework and Leadership (15 files)
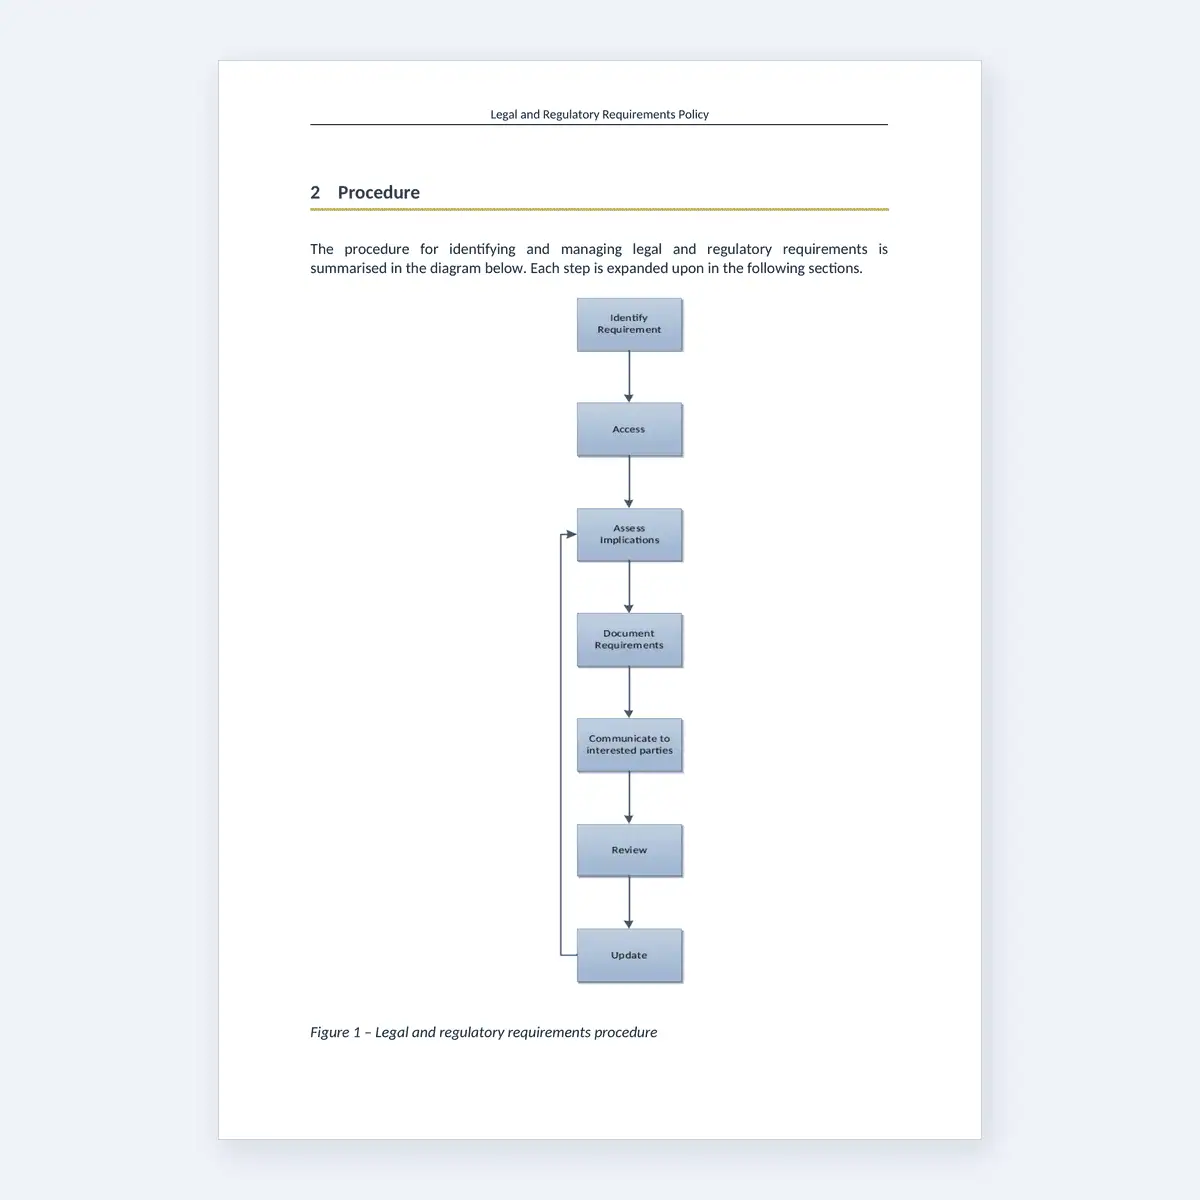
Clauses 4–5: context and scope, the ISMS and information security policies, roles, legal and regulatory requirements, and the management support letter.
- Copyright Compliance Policy (Word)
- Information Security Policy (Word)
- ISM organization chart data (Excel)
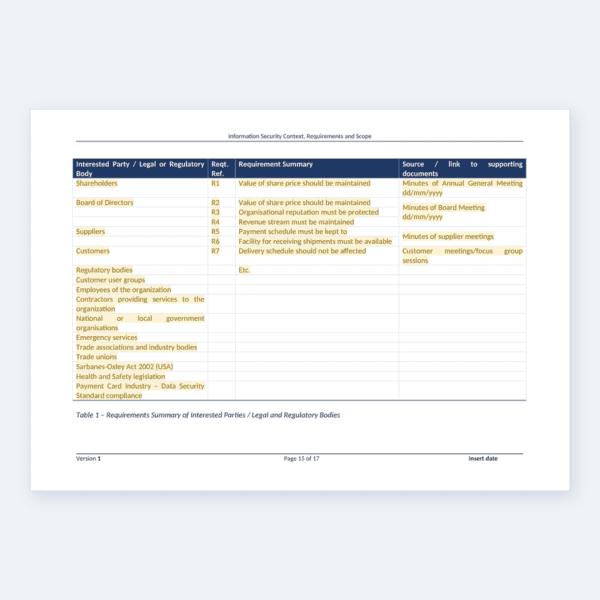
- ISMS Context and Scope (Word)
- ISMS Management Plan (Word)
- ISMS Operating Procedure (Word)
- ISMS Policy (Word)
- ISMS Roles Responsibilities (Word)
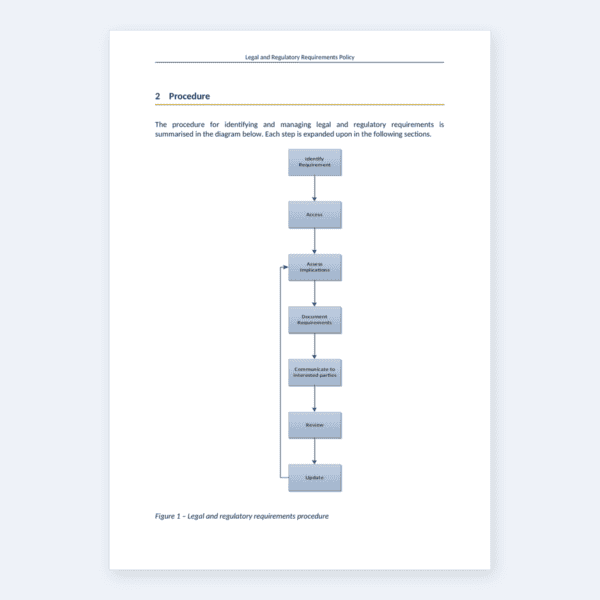
- Legal and Regulatory Requirements Policy (Word)
- Legal Responsibilities Policy (Word)
- Management Support Letter (Word)
- Model Policy on Information Security (Word)
- Organization of Information Security (Word)
- Segregation of Duties Policy (Word)
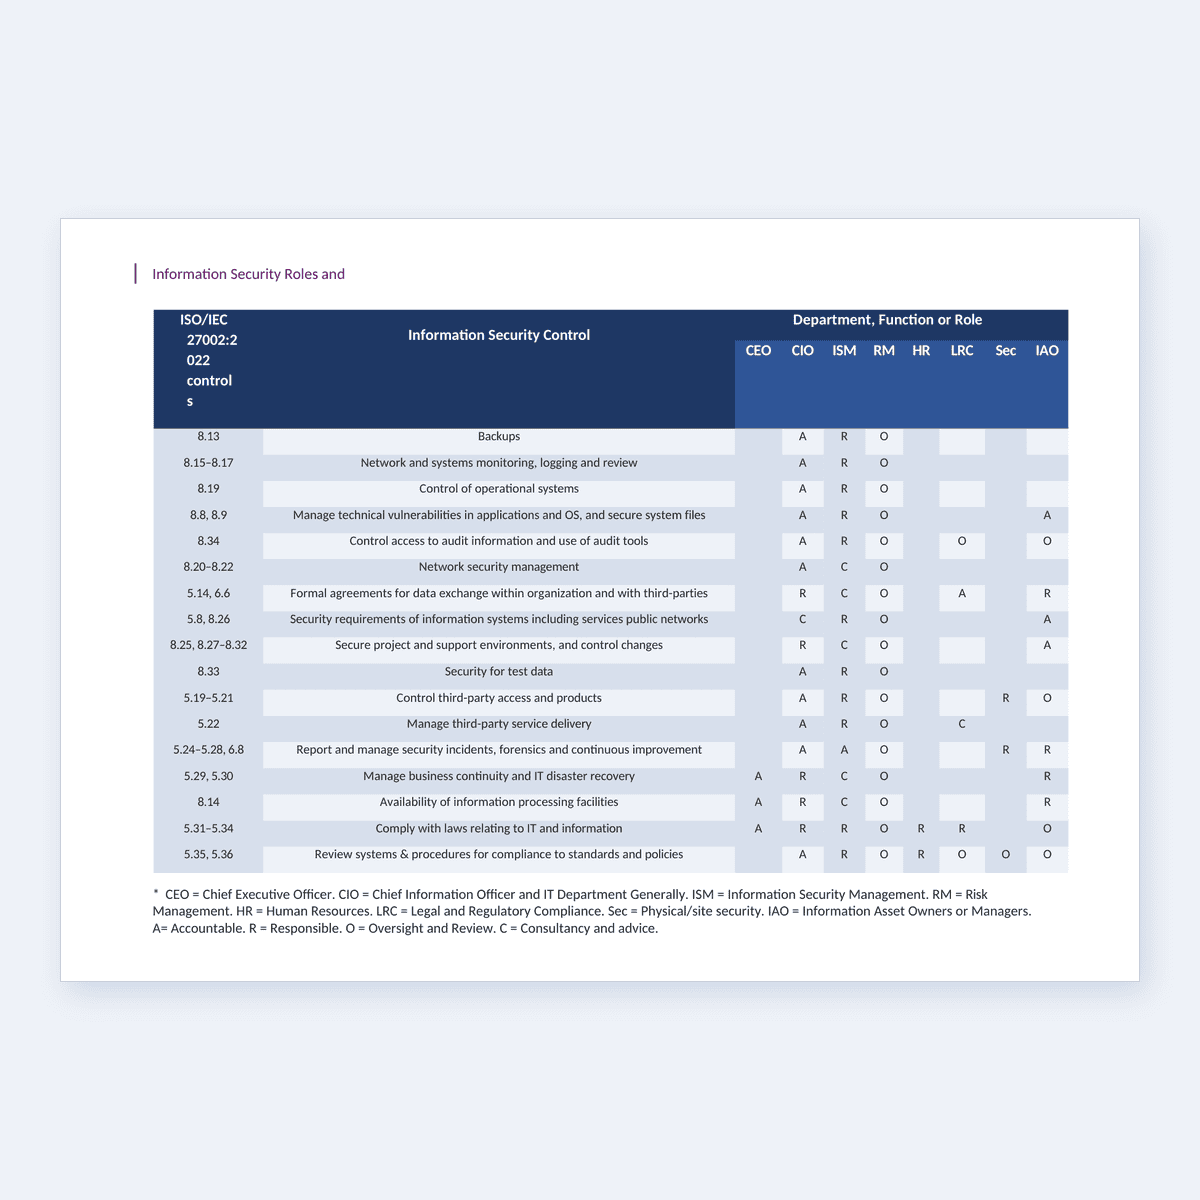
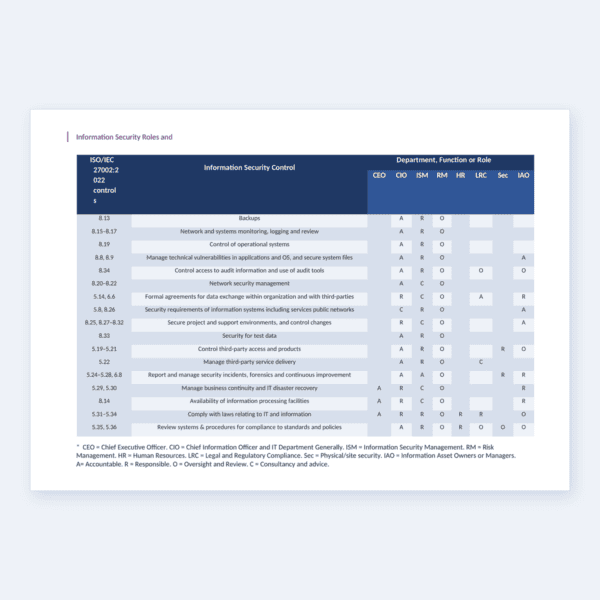
- Technical Briefing on Security Roles and Responsibilities Matrix (Word)
02 Risk Management and Statement of Applicability (15 files)
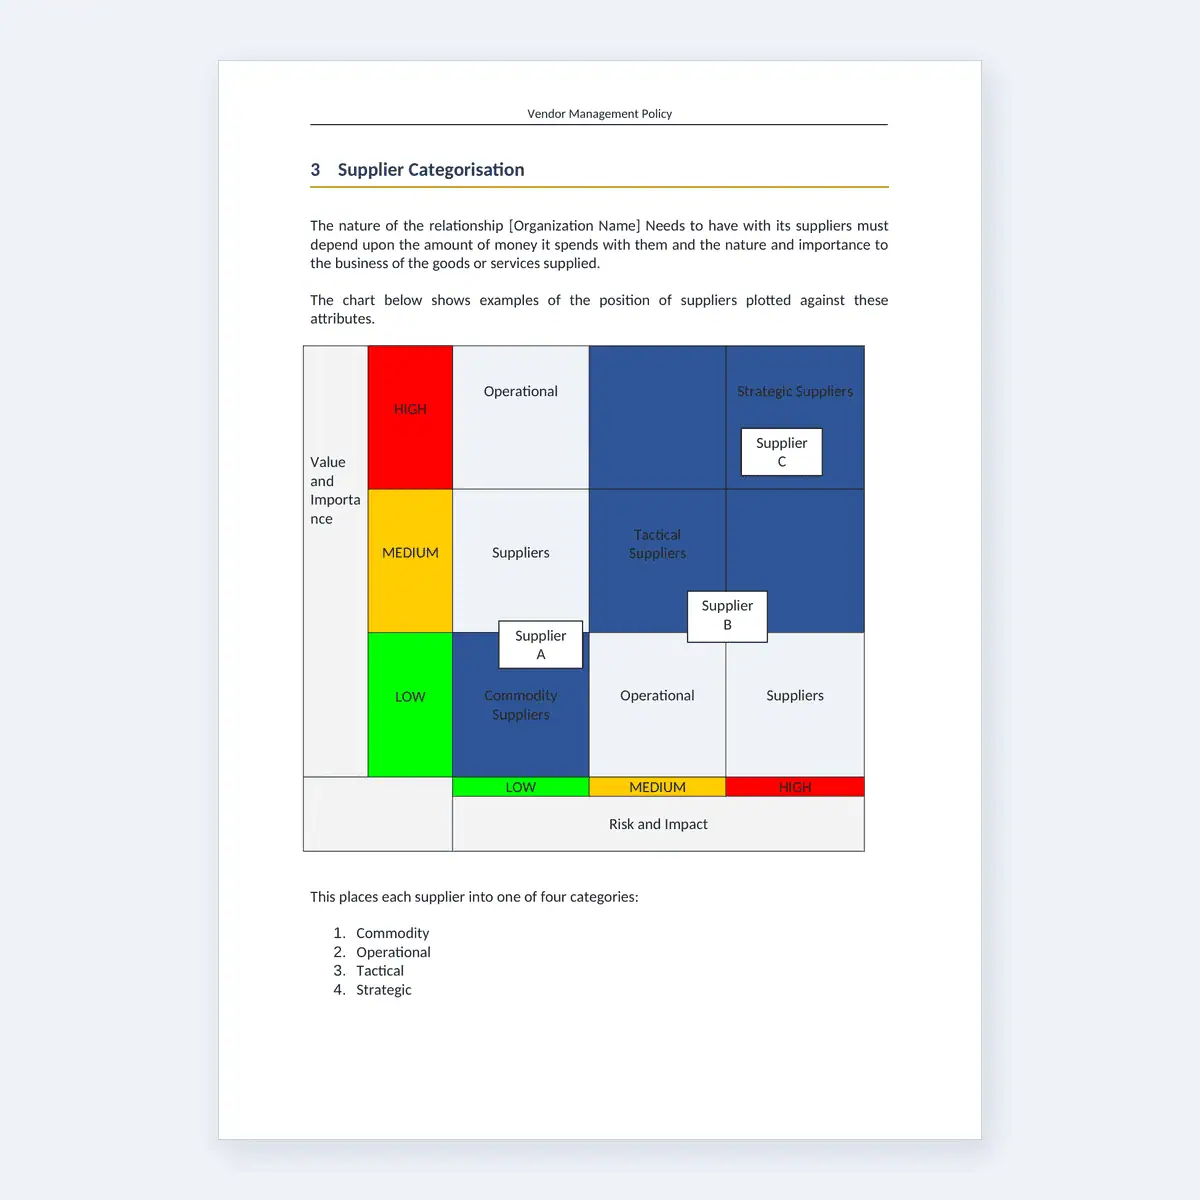
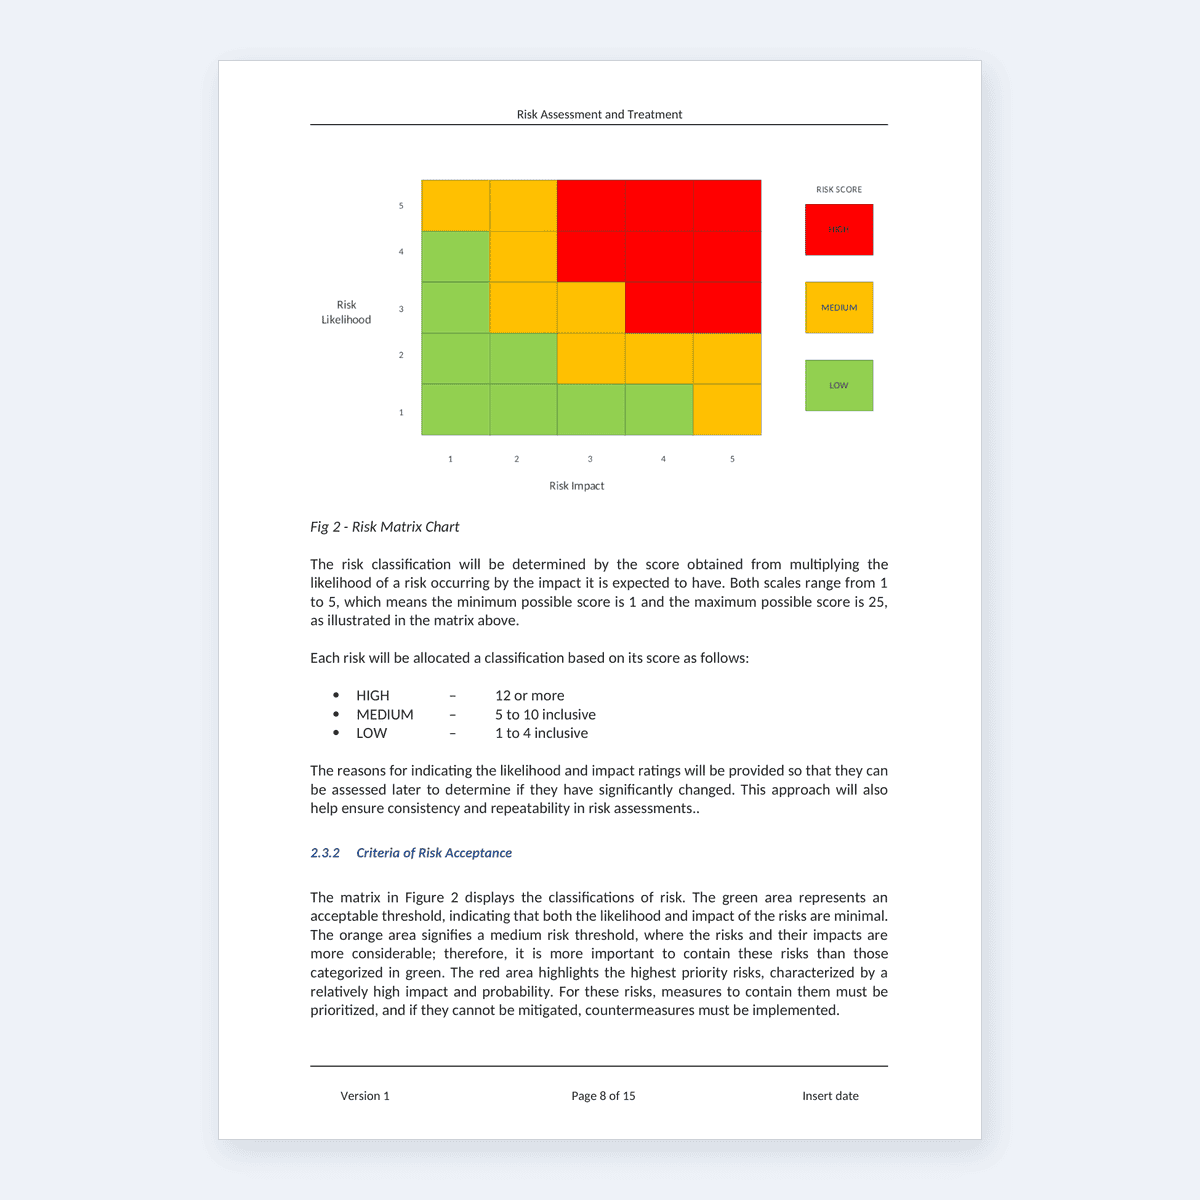
Clauses 6 and 8: risk assessment and treatment method, risk register, assessment worksheet, treatment plan, FMEA, asset valuation and the Statement of Applicability for all 93 Annex A controls.
- FMEA Spreadsheet (Excel)
- Guideline on Information Asset Valuation (Word)
- ISMS Information Risk Management Process v1-Basic RM Process Flowchart (image)
- ISMS Information Risk Management Process v1-Detailed Process Flowchart (image)
- ISMS Information Risk Management Process v1 (Visio)
- ISMS Information Risk Register (Excel, macro-enabled)
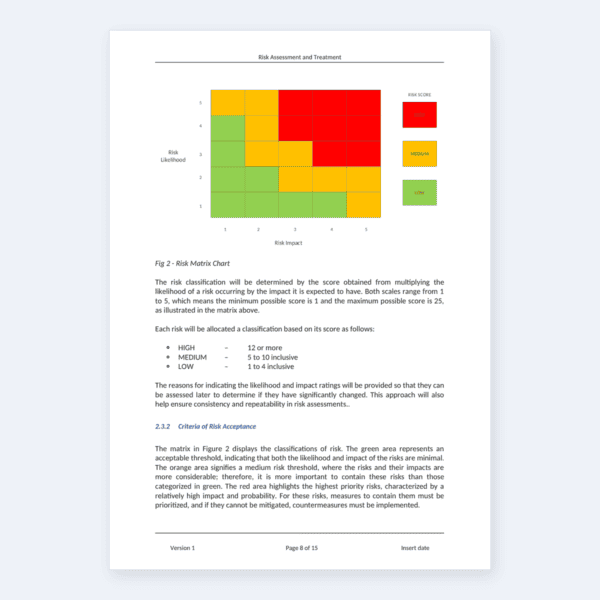
- ISMS Risk Assessment and Treatment (Word)
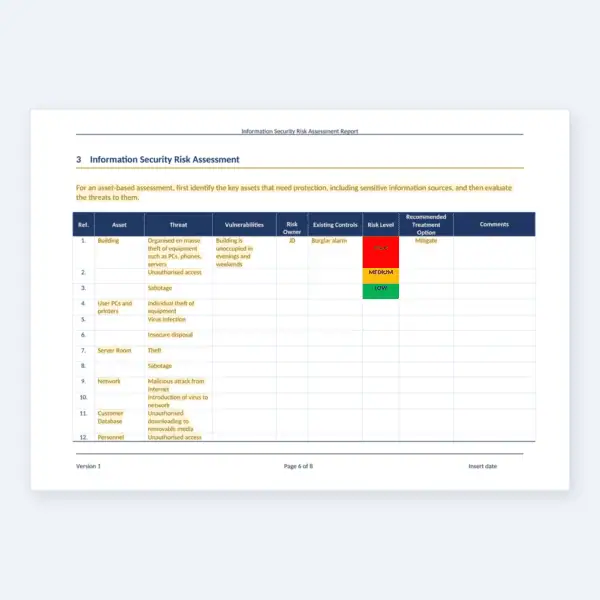
- ISMS Risk Assessment Report (Word)
- ISMS Risk Assessment Worksheet (Excel)
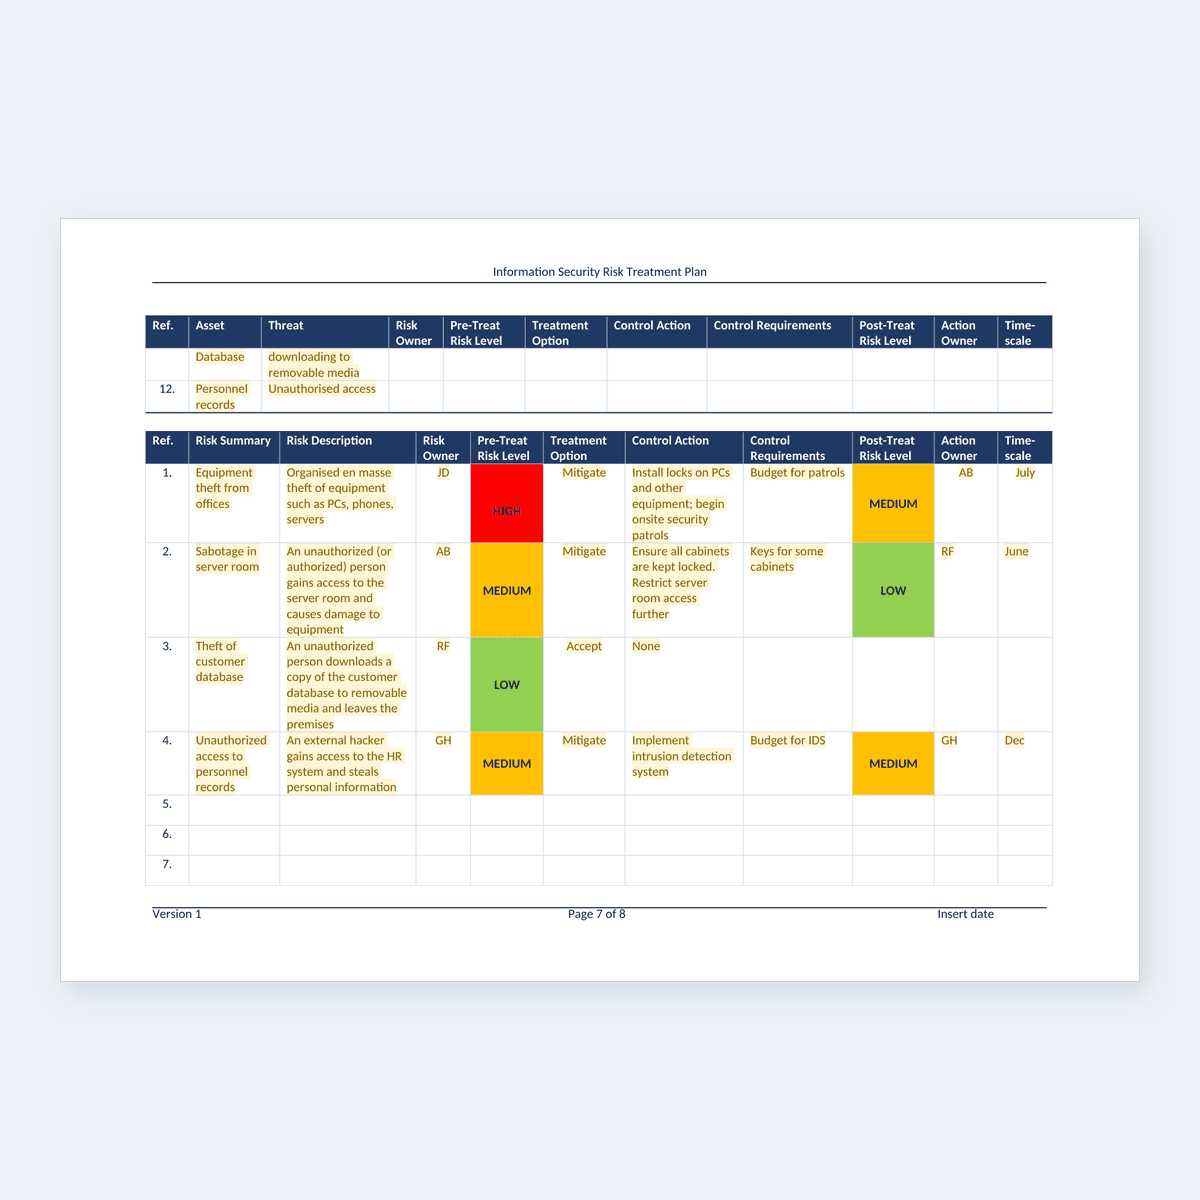
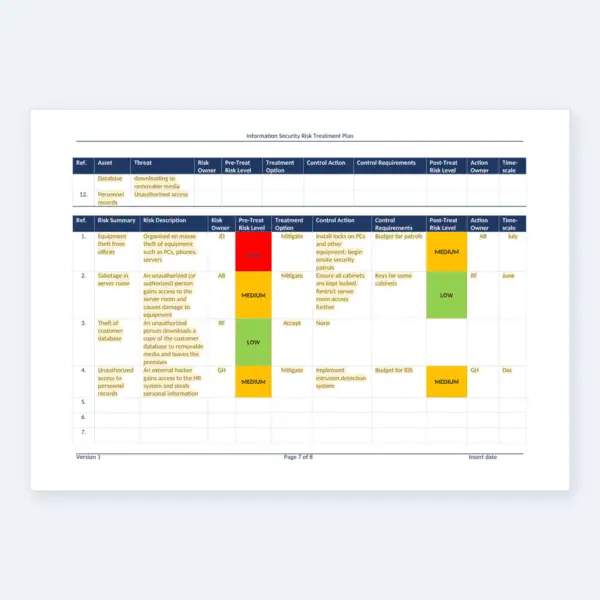
- ISMS Risk Treatment Plan (Word)
- ISMS Risk Treatment Plan (Excel)
- ISO27001-2022 Statement of Applicability (Excel)
- SGSI 6.1 SoA 2022 Espanol 2022 (Excel)
- SGSI 6.1 SoA 2022 Portugues (Excel)
- Threat Intelligence Policy (Word)
03 Support – Documents, Communication and Awareness (6 files)
Clause 7: documented information and records control, communication plan, awareness presentation and training policy.
- Awareness Presentation (PowerPoint)
- Control of Records Procedure (Word)
- Documented Information Control Procedure (Word)
- ISMS Communication Plan (Word)
- ISMS Documented Information and Procedures Register (Excel)
- Model Policy on Security Awareness and Training (Word)
04 Asset Management and Information Handling (18 files)
Annex A 5.9–5.14, 7.10, 8.10–8.12: asset inventories, acceptable use, classification, labelling, transfer, retention, masking, DLP and secure disposal.
- Acceptable Use Policy (Word)
- Asset Handling Policy (Word)
- Asset inventory (Excel, macro-enabled)
- Asset Register (Excel)
- Data Masking Policy (Word)
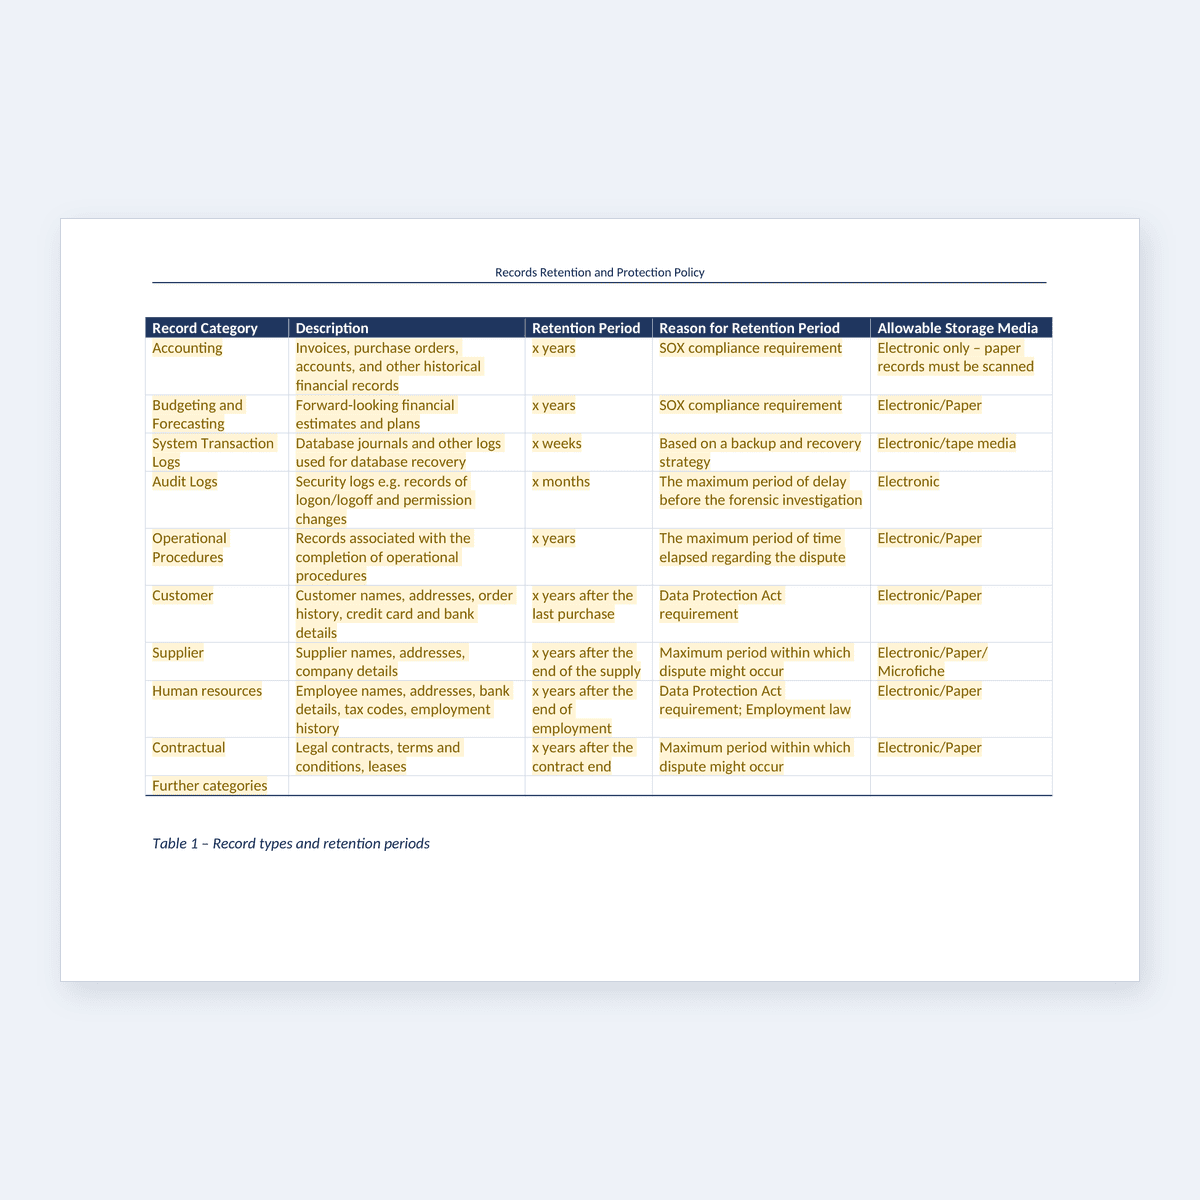
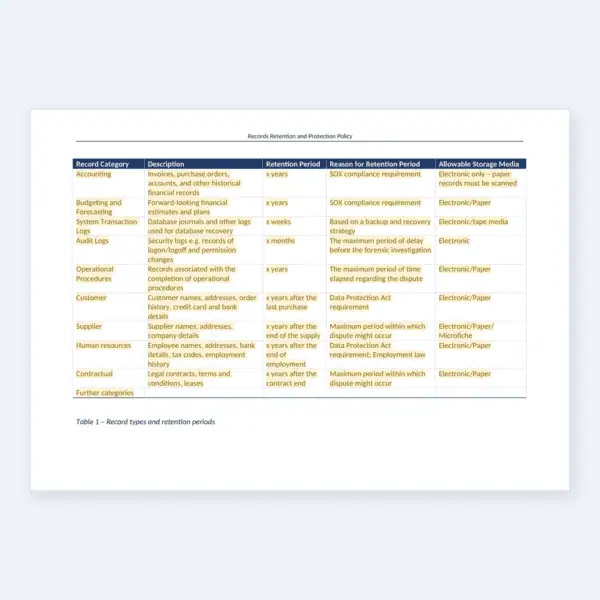
- Data Retention Policy (Word)
- DLP Policy (Word)
- Information Classification Matrix (Excel)
- Information Security Classification Policy (Word)
- Information Security Labelling Procedure (Word)
- Information Transfer Procedure (Word)
- ISMS Information Asset Inventory (Excel)
- Media Disposal Procedure (Word)
- Model Policy on Information Classification (Word)
- Offsite Assets Procedure (Word)
- Physical Media Transfer Procedure (Word)
- Removable Media Management Procedure (Word)
- Secure Data Disposal Policy (Word)
05 Access Control and Technical Security (21 files)
Annex A 5.15–5.18, 8.1–8.24: access control, cryptography, network security, malware, backup, logging and monitoring, vulnerability management, cloud, remote working and BYOD.
- Access Control Policy (Word)
- Anti-Malware Policy (Word)
- Backup Policy (Word)
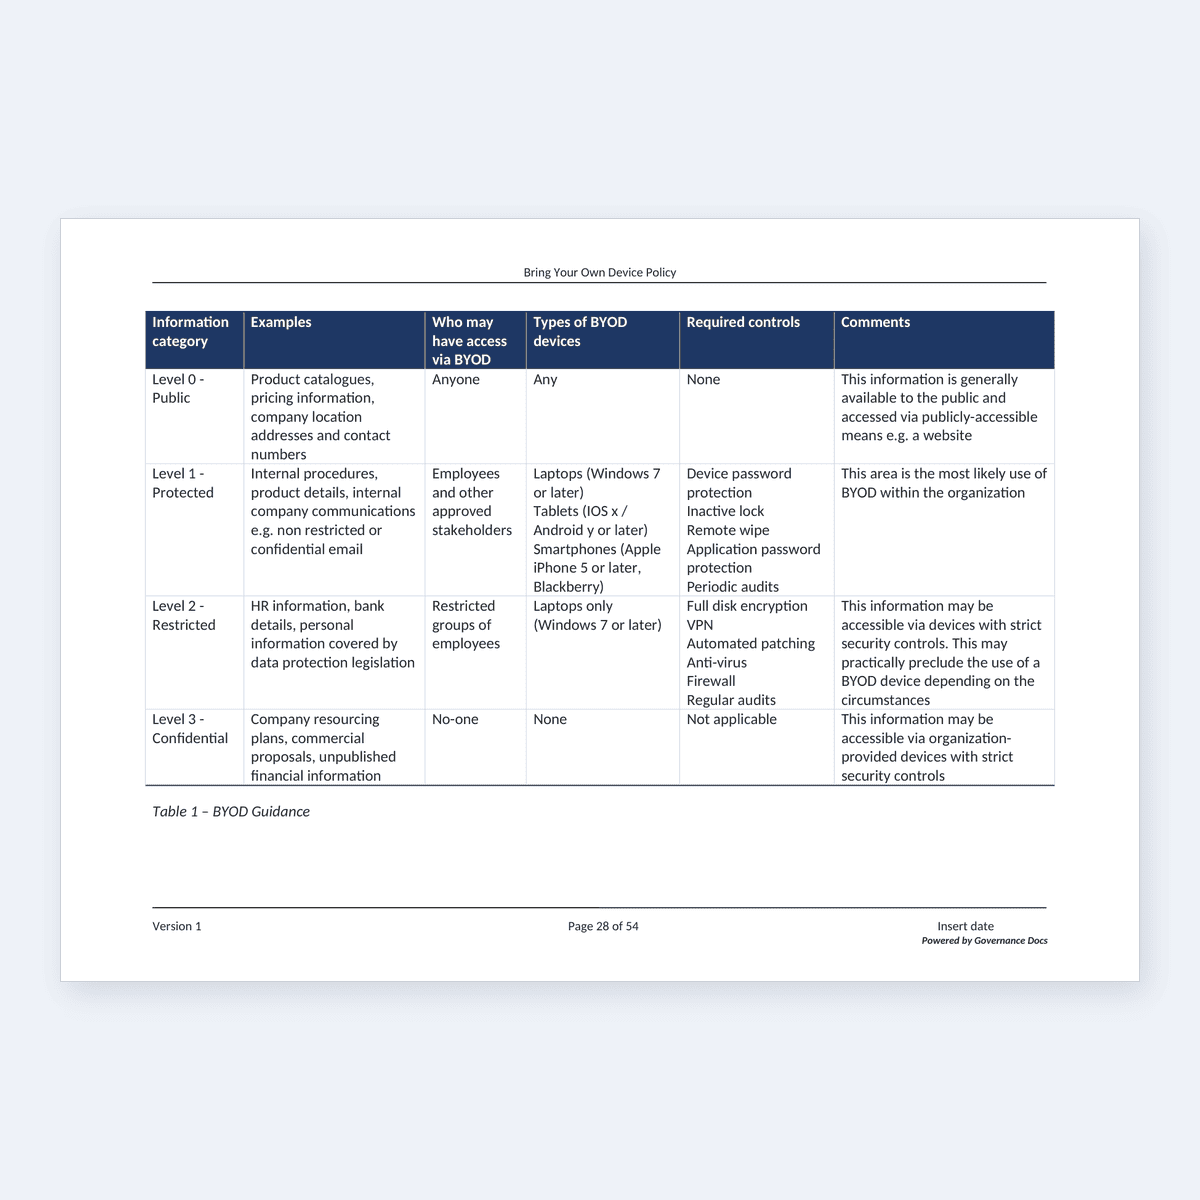
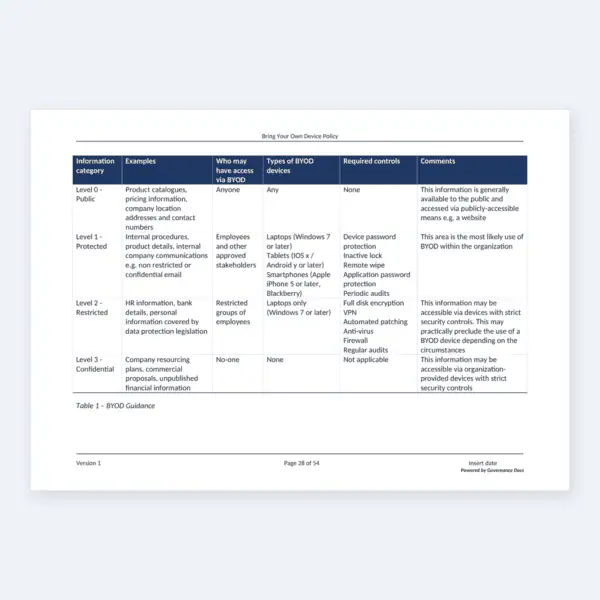
- BYOD Policy (Word)
- Cloud Services Security Policy (Word)
- Configuration Management Procedure (Word)
- Cryptographic Policy (Word)
- Data Restoration Form (Word)
- Email Usage Policy (Word)
- Internet Acceptable Use Policy (Word)
- IT Systems Monitoring Procedure (Word)
- Log Monitoring Policy (Word)
- Mobile Computing Policy (Word)
- Model Policy on Malware (Word)
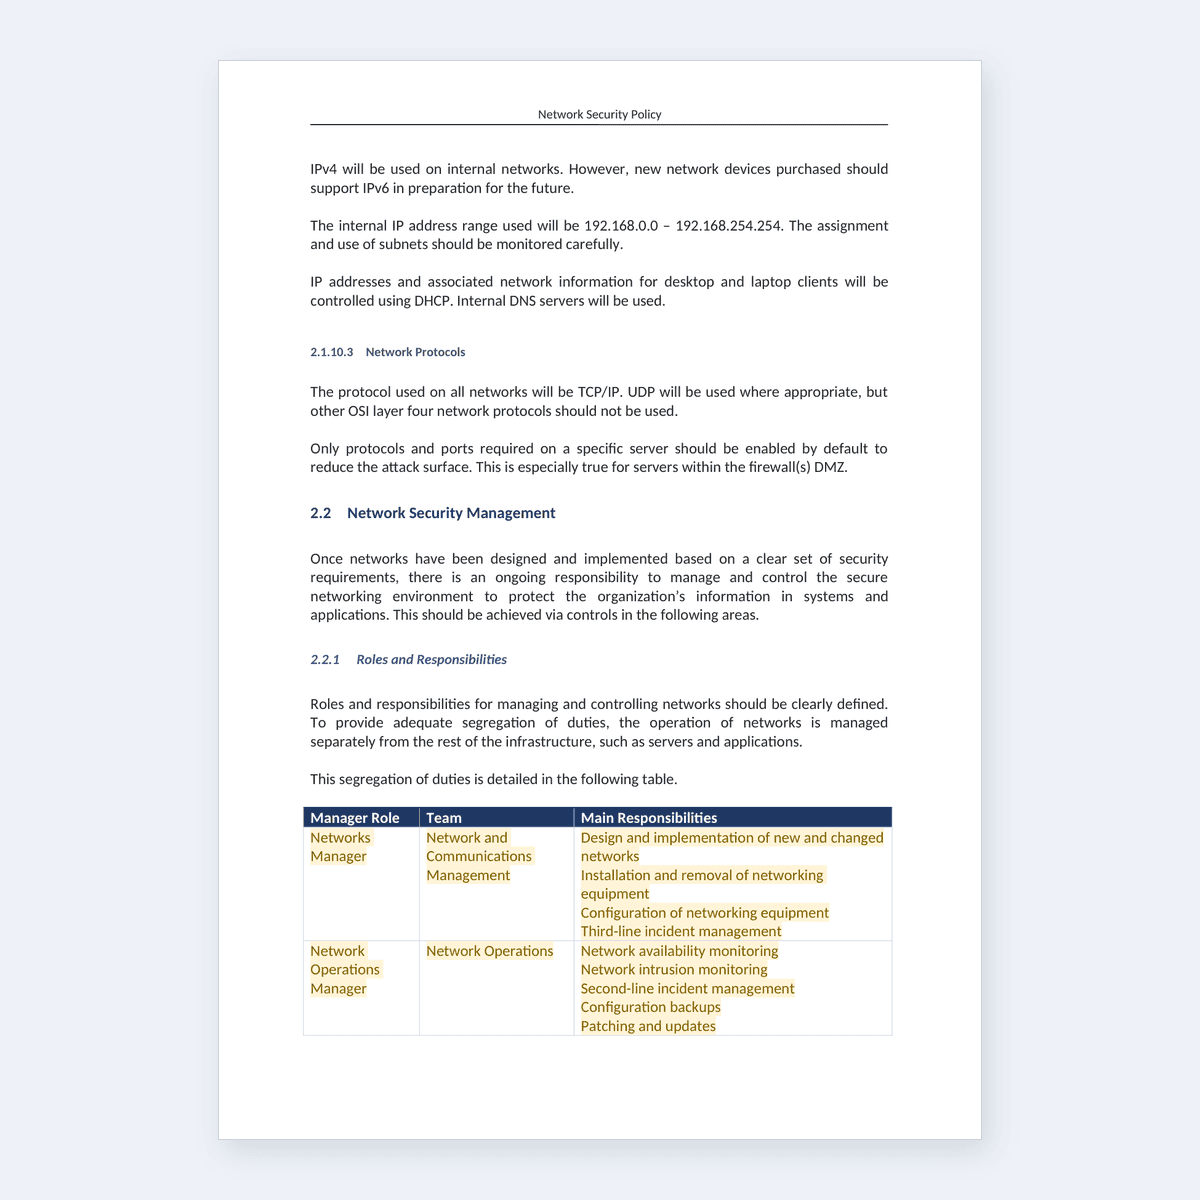
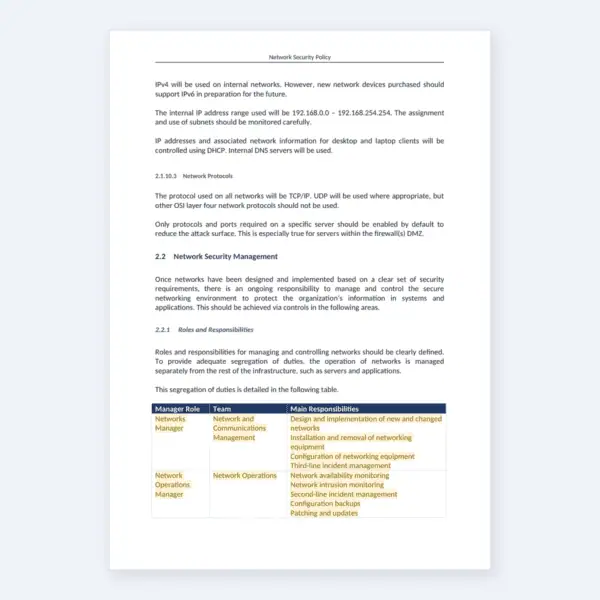
- Network Security Policy (Word)
- Passwords Reset Procedure (Word)
- Remote Working Policy (Word)
- Software Policy (Word)
- Vulnerability Assessment Procedure (Word)
- Vulnerability Management Policy (Word)
- Web Filtering Policy (Word)
06 Secure Development and Change Management (9 files)
Annex A 8.25–8.33: secure development and coding, environments, change and release management, and security in projects.
- Business Requirements Specification Procedure (Word)
- Change Management Policy (Word)
- Development Environment Policy (Word)
- Model Policy on Change Management and Control (Word)
- Project Management Security Policy (Word)
- Release Management Policy (Word)
- Secure Coding Policy (Word)
- Secure Development Policy (Word)
- Secure Systems Engineering Policy (Word)
07 People Security and Job Descriptions (35 files)
Annex A 6.1–6.6: screening, contracts, joiners and leavers, disciplinary process, plus 30 security job descriptions.
- Employee Disciplinary Process (Word)
- Employee Movement and Termination Checklist (Word)
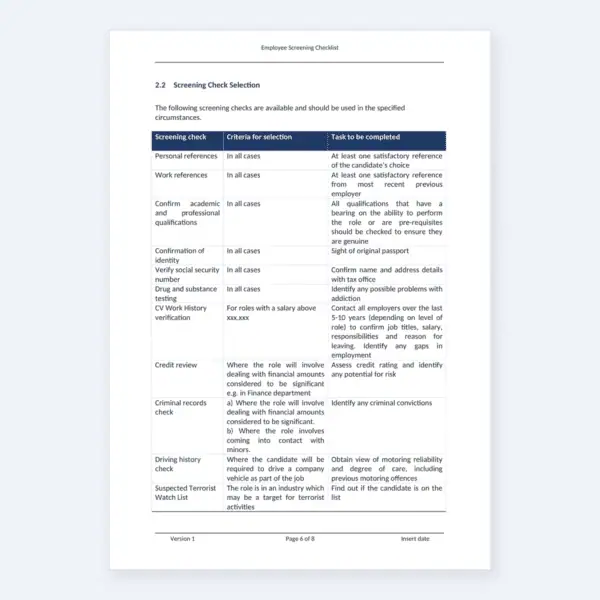
- Employee Screening Checklist (Word)
- Employment Contracts Clauses (Word)
- Recruitment and New Joiner Checklist (Word)
- Job Descriptions / Business Continuity Manager JD (Word)
- Job Descriptions / BYOD Security Manager JD (Word)
- Job Descriptions / Chief Information Security Officer JD (Word)
- Job Descriptions / Compliance Manager JD (Word)
- Job Descriptions / Counterespionage Manager JD (Word)
- Job Descriptions / Database Security Manager JD (Word)
- Job Descriptions / Fraud Manager JD (Word)
- Job Descriptions / Industrial Information Risk and Security Manager JD (Word)
- Job Descriptions / Information Risk and Security Manager JD (Word)
- Job Descriptions / Information Security Incident Manager JD (Word)
- Job Descriptions / Intellectual Property Manager JD (Word)
- Job Descriptions / Internet Risk and Security Manager JD (Word)
- Job Descriptions / IoT and BYOD Security Manager JD (Word)
- Job Descriptions / IT Audit Manager JD (Word)
- Job Descriptions / IT Auditor JD (Word)
- Job Descriptions / Malware Analyst JD (Word)
- Job Descriptions / Network Risk Analyst JD (Word)
- Job Descriptions / Network Risk Manager JD (Word)
- Job Descriptions / Permissions Manager JD (Word)
- Job Descriptions / Physical Security Manager JD (Word)
- Job Descriptions / Privacy Officer JD (Word)
- Job Descriptions / Security Administration Team Leader JD (Word)
- Job Descriptions / Security Administrator JD (Word)
- Job Descriptions / Security Awareness Contact JD (Word)
- Job Descriptions / Security Awareness Manager JD (Word)
- Job Descriptions / Security Awareness Officer JD (Word)
- Job Descriptions / Technology Risk Manager JD (Word)
- Job Descriptions / Whistleblowers' Hotline Case Handler JD (Word)
- Job Descriptions / Whistleblowers’ Hotline Manager JD (Word)
- Job Descriptions / Workplace Information Security Representative JD (Word)
08 Physical Security (3 files)
Annex A 7.1–7.14: physical security, secure areas and physical security design.
- Physical Security Design Policy (Word)
- Physical Security Policy (Word)
- Secure Areas Policy (Word)
09 Supplier and Third-Party Security (7 files)
Annex A 5.19–5.23: vendor management, evaluation, access and security agreements, NDA and SLA.
- Model Policy on Outsourcing (Word)
- Standard NDA (Word)
- Standard SLA (Word)
- Vendor Access Procedure (Word)
- Vendor Evaluation Process (Word)
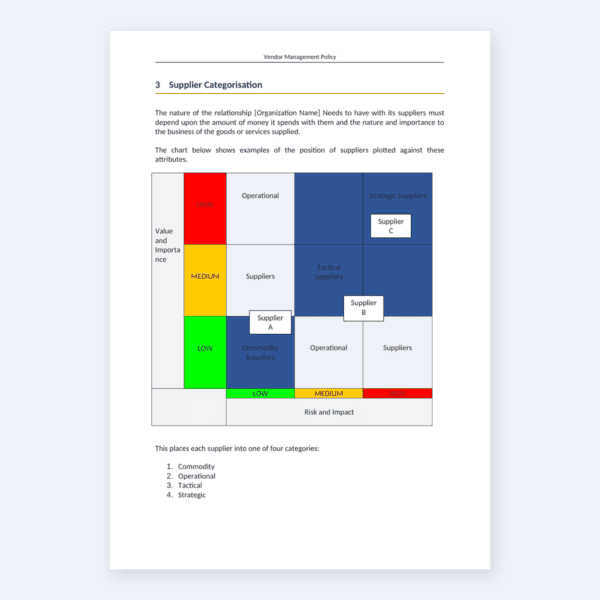
- Vendor Management Policy (Word)
- Vendor Security Agreement (Word)
10 Incident Management and Business Continuity (7 files)
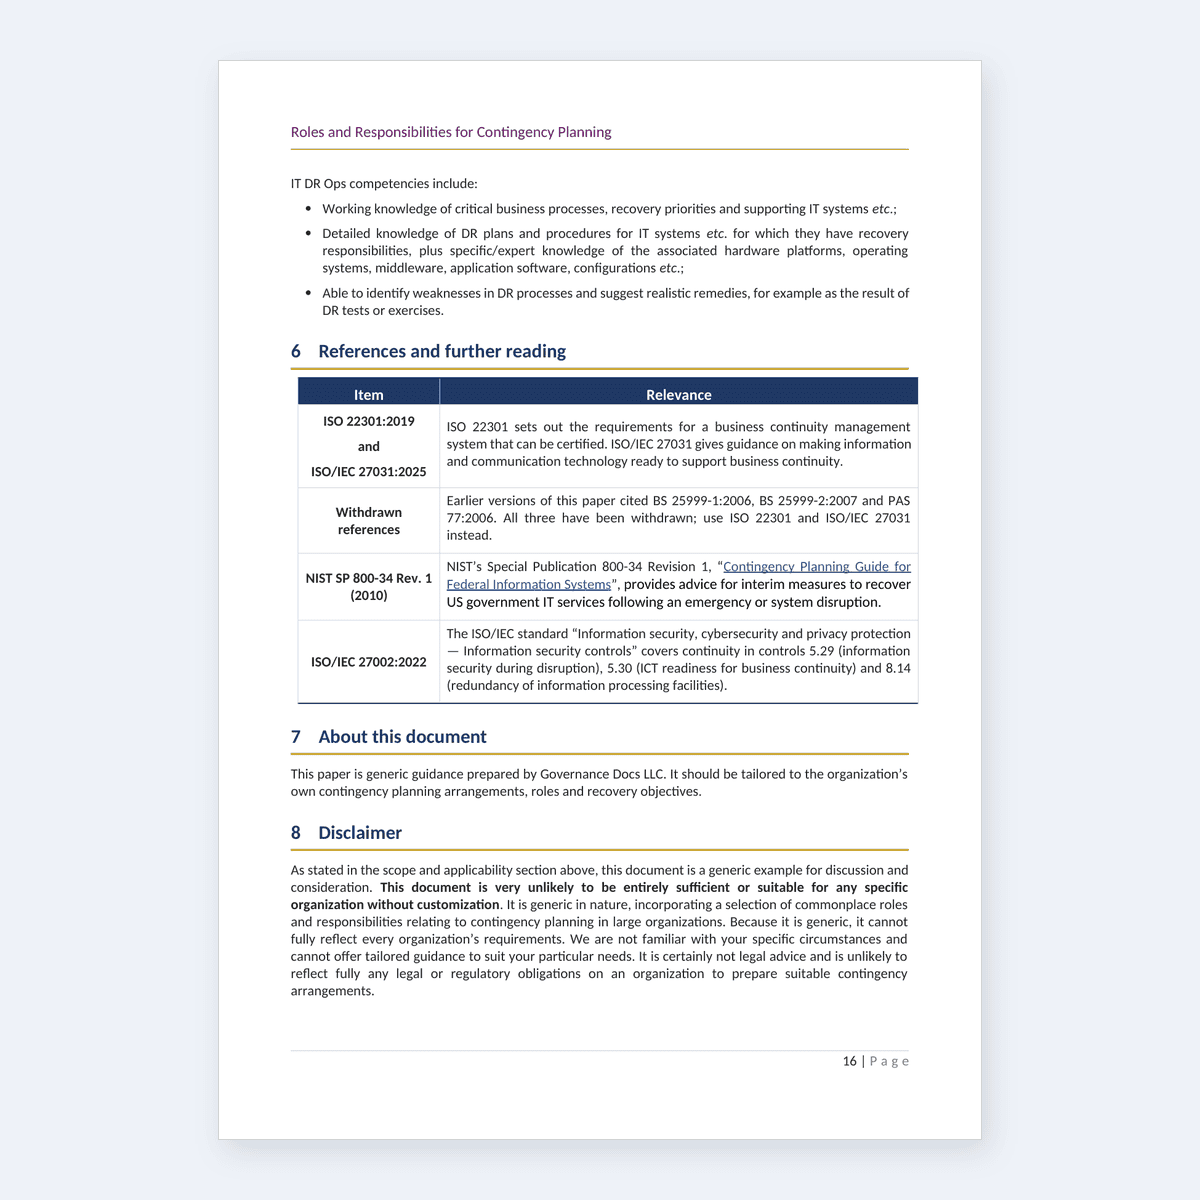
Annex A 5.24–5.30: incident response, business impact analysis, business continuity plan, test plan and test report.
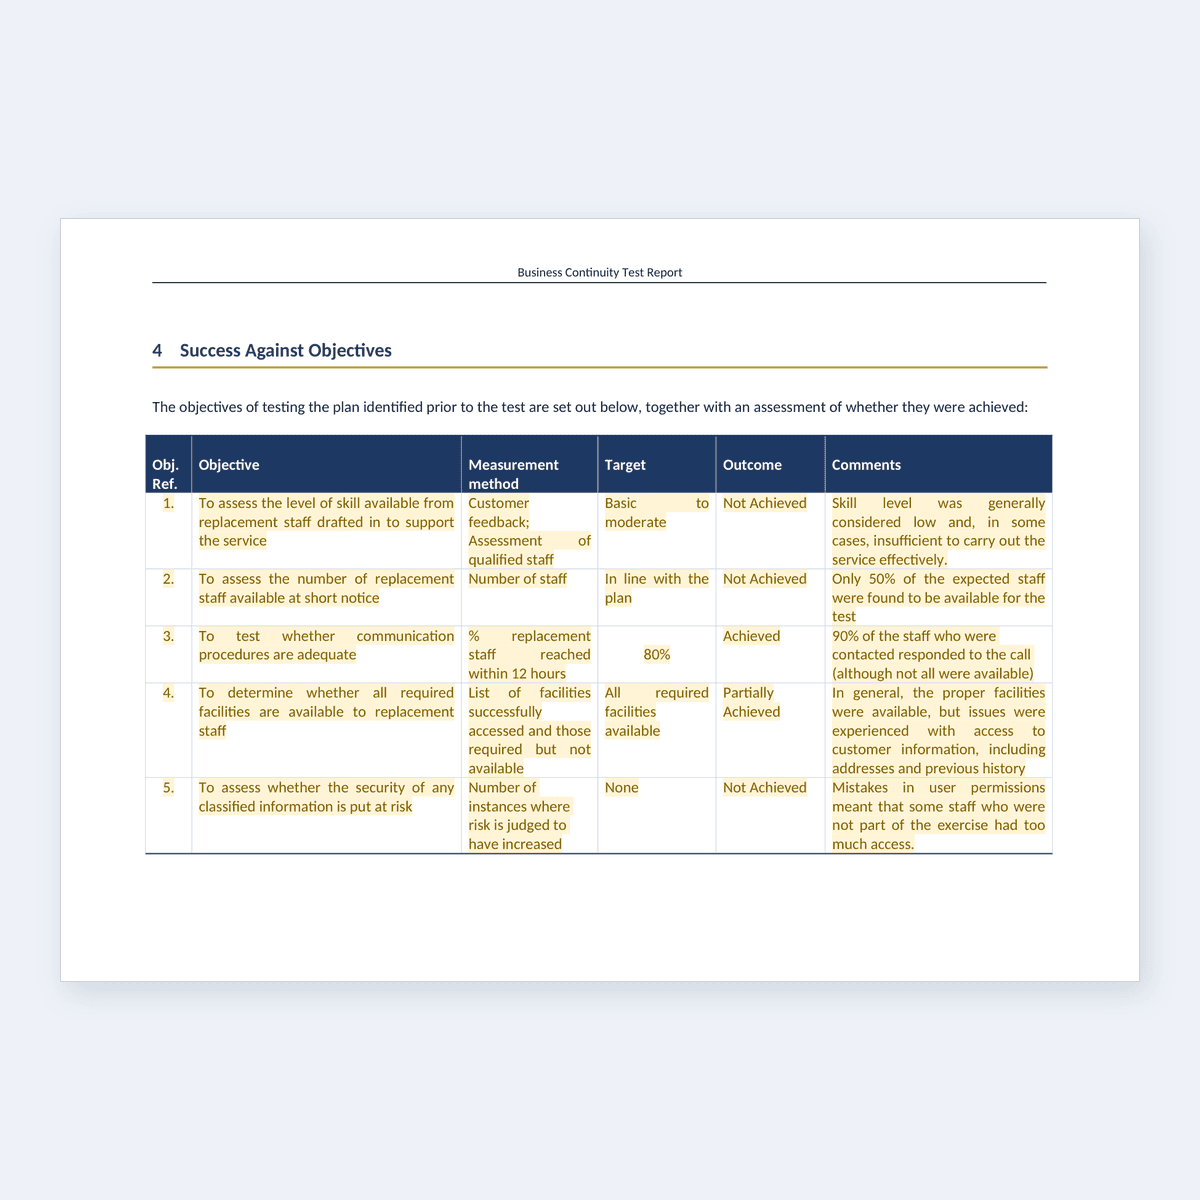
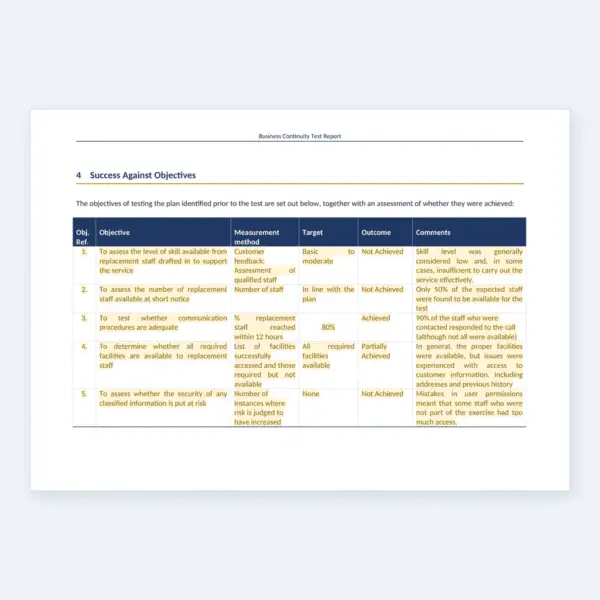
- BCP Test Report (Word)
- Business Continuity Plan (Word)
- Business Continuity Test Plan (Word)
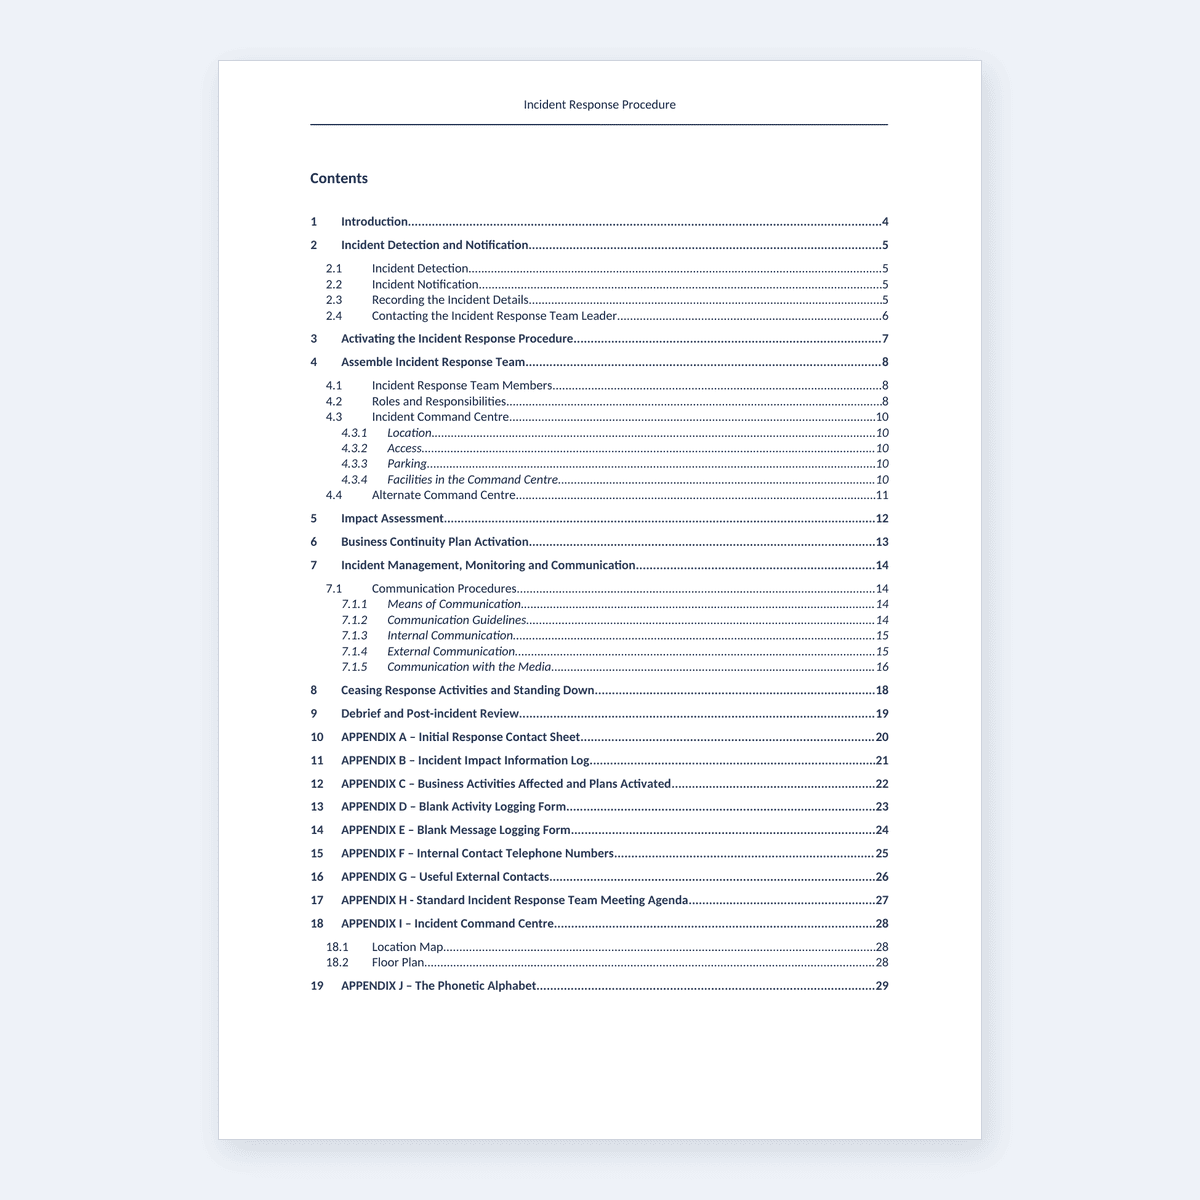
- Incident Response Procedure (Word)
- ISMS BIA Procedure (Word)
- Roles and Responsibilities for Contingency Planning (Word)
- Security Incident Procedure (Word)
11 Performance Evaluation and Audit (14 files)
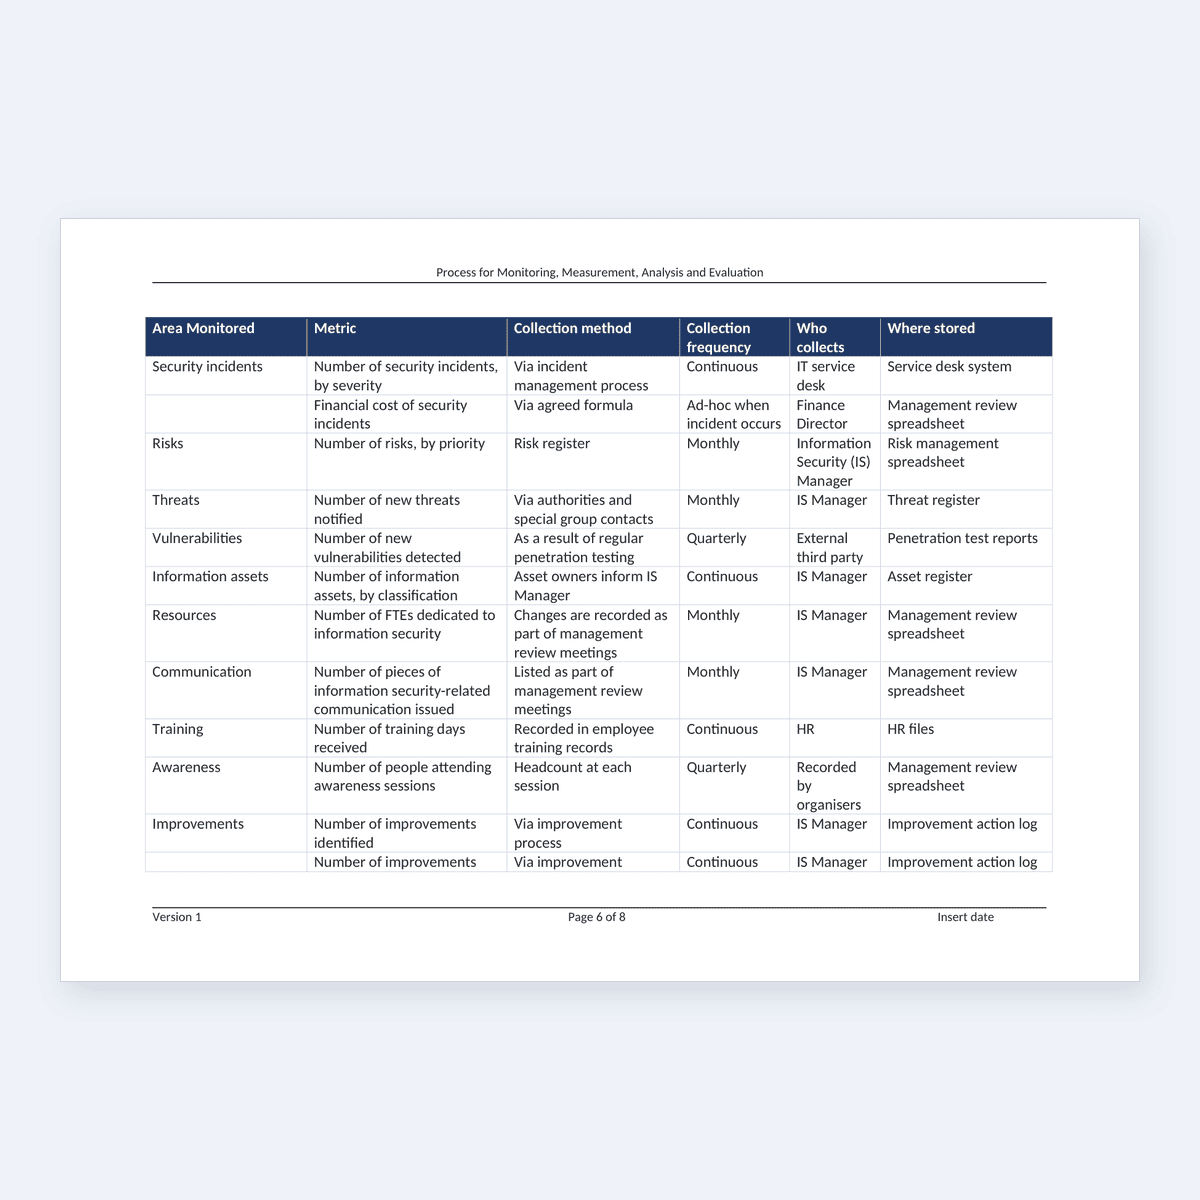
Clause 9: monitoring and evaluation, audit procedures, plans, schedules, checklists with dashboards, assessment tools and management review agendas.
- Information security program maturity assessment tool (Excel)
- ISMS Audit Plan (Word)
- ISMS Audit Schedule (Word)
- ISMS Auditing Guideline (Word)
- ISMS Audits Procedure (Word)
- ISMS Internal Audit Plan (Word)
- ISMS Internal Audit Procedure (Word)
- ISMS Management Review Meeting Agenda (Word)
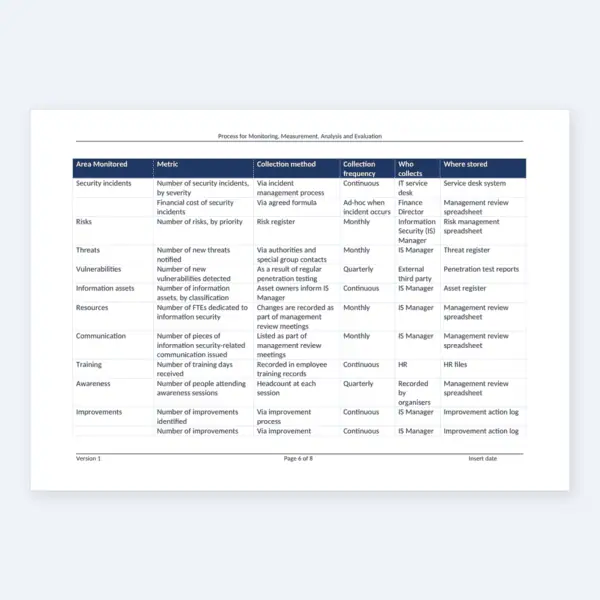
- ISMS Monitoring and Evaluation (Word)
- ISMS MRM Agenda (Word)
- ISO 27001 Audit Checklist (Excel)
- ISO 27001 Internal Audit Checklist with Dashboard (Excel)
- ISO 27001 Internal Audit Checklist (Excel)
- ISO 27001-2022 Assessment Tool (Excel)
12 Improvement (5 files)
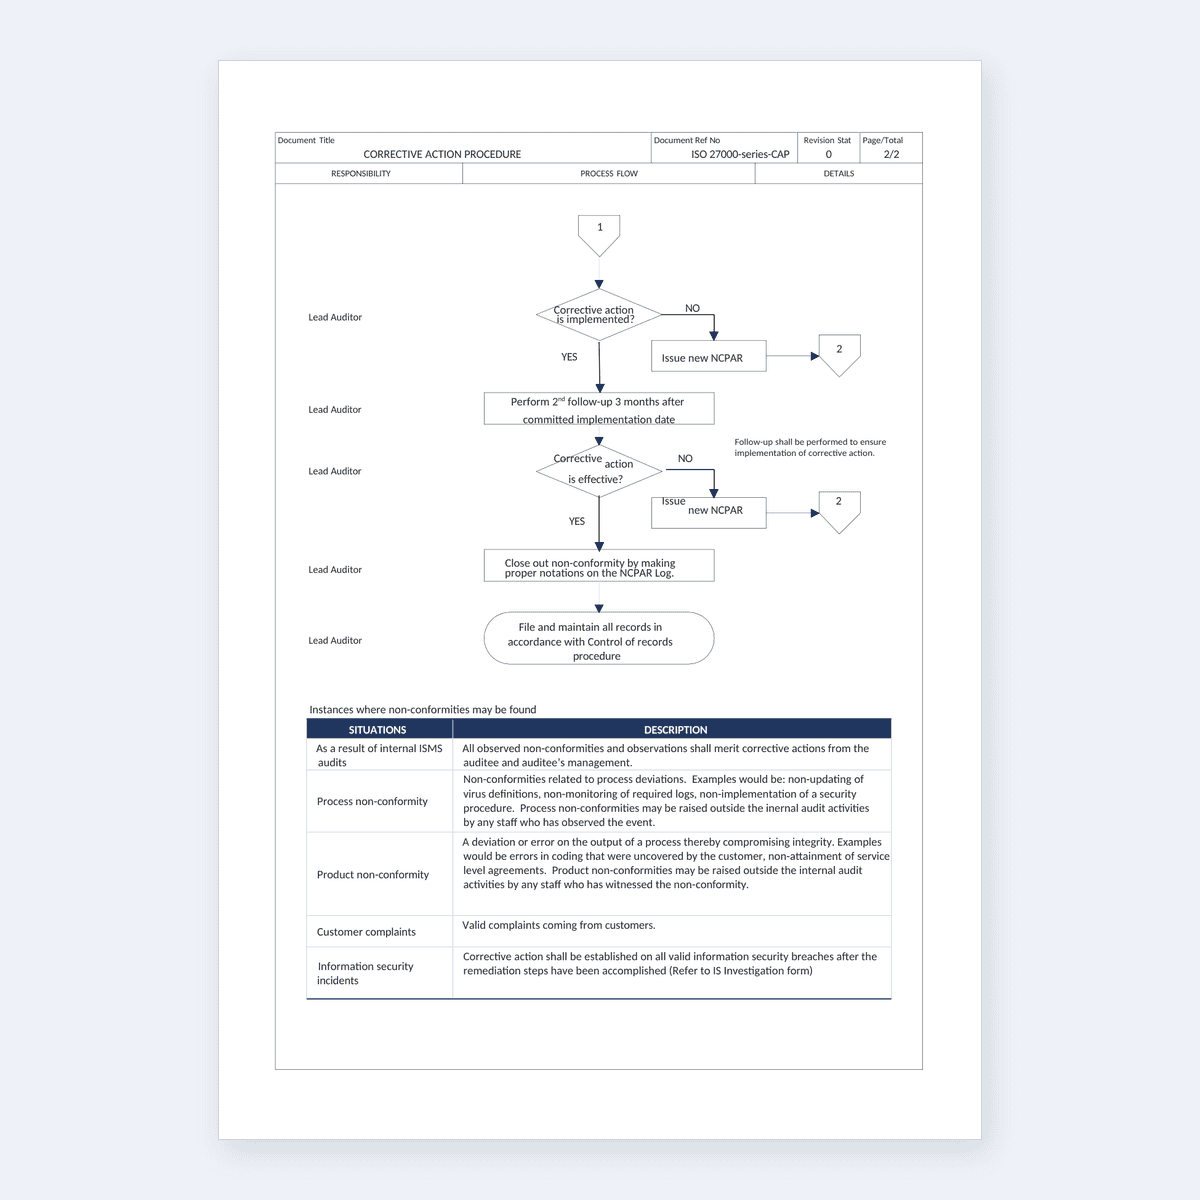
Clause 10: nonconformity, corrective and preventive action, continuous improvement procedure and log.
- Continuous Improvement Procedure (Word)
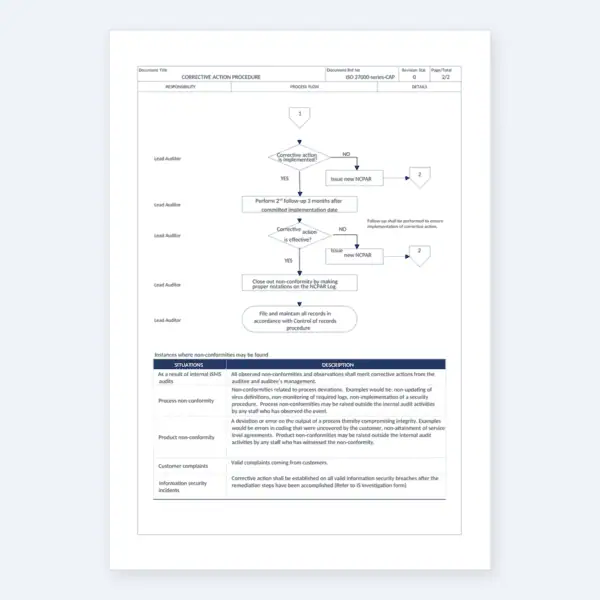
- Corrective Action Procedure (Word)
- ISMS Continuous Improvement Log (Excel)
- ISMS Nonconformity Management Procedure (Word)
- Preventive Action Procedure (Word)
13 Implementation Project and Business Case (23 files)
Project initiation, plan (Excel and MS Project), estimator, business case, case study, certification overview deck and process diagrams (with translations).
- Business case template for ISO IEC 27001 ISMS (Word)
- Business Value of ISO 27001 Case Study (Word)
- Intro and Gap Analysis email Template (text)
- ISMS Implementation and Certification Overview (PowerPoint)
- ISMS implementation project estimator (Excel)
- ISMS Project Highlight Report (Word)
- ISMS Project Initiation Document (Word)
- ISMS Project plan (MS Project)
- ISMS Project Plan (Excel)
- Process Diagrams / ISMS Implementation and Certification Process 4v1 Basic Process (image)
- Process Diagrams / ISMS Implementation and Certification Process 4v1 Procedures and Documents (image)
- Process Diagrams / ISMS Implementation and Certification Process 4v1 (Visio)
- Process Diagrams / ISMS Implementation and Certification Process v3 (Visio)
- Process Diagrams/Translations / ISMS Implementation and Certification Basic Process Croatian (image)
- Process Diagrams/Translations / ISMS Implementation and Certification Basic Process Italian (image)
- Process Diagrams/Translations / ISMS Implementation and Certification Basic Process Polish (image)
- Process Diagrams/Translations / ISMS Implementation and Certification Basic Process Spanish (image)
- Process Diagrams/Translations / ISMS Implementation and Certification Detailed Process Croatian (image)
- Process Diagrams/Translations / ISMS Implementation and Certification Detailed Process Italian (image)
- Process Diagrams/Translations / ISMS Implementation and Certification Detailed Process Polish (image)
- Process Diagrams/Translations / ISMS Implementation and Certification Detailed Process Spanish (image)
- Process Diagrams/Translations / ISMS Implementation and Certification Process 4v1 French (Visio)
- Process Diagrams/Translations / ISMS Implementation and Certification Process 4v1 German (Visio)
Root folder: LICENCE.txt
ISO Compliance
All documents of this Toolkit are developed based on ISO 27001:2022 Standard
Frequently Asked Questions (FAQ)
What is included in the ISO 27001 Toolkit?
The ISO 27001 Toolkit includes 165 customizable templates such as policies, procedures, checklists, risk assessments, audit plans, and business continuity documents. All templates are in Microsoft Office format, organised into 13 numbered folders, and come with example content, making them easy to tailor to your organization’s needs.
Is this ISO 27001 documentation toolkit compliant with the 2022 version of the standard?
Yes, this toolkit is fully aligned with ISO/IEC 27001:2022 and ISO 27002:2022 standards. It includes updated templates that reflect the latest clauses and Annex A controls, ensuring you’re working with documentation that matches current certification requirements.
Who can benefit from this ISO 27001 Toolkit?
This toolkit is ideal for businesses aiming for ISO 27001 certification, including IT managers, security officers, compliance teams, consultants, and auditors. It’s especially useful for organizations that need a ready-to-use solution to save time and effort during ISMS implementation.
How do I use the ISO 27001 templates after purchase?
All 165 templates download instantly. Open each in Microsoft Office, tailor the ISMS policies, Statement of Applicability and Annex A controls to your scope, and the risk assessment, procedures and records are ready to operate. The structure follows ISO 27001:2022 so your documentation lines up with how a certification audit is run.
Is technical support or training included with the ISO 27001 Toolkit?
The toolkit is designed for easy use without needing outside help. However, if you require expert guidance or training for implementation, support packages are available separately. The included documents already offer structured examples to support a smooth setup.
Can I use this ISO 27001 toolkit for multiple clients or projects?
Within your own organisation, yes: reuse it across business units, sites and projects. Each external client needs its own licence. If you implement for several clients, the
Consultant Package covers unlimited client engagements under one firm-wide licence for $1,399.
How long will it take to implement ISO 27001 using this toolkit?
Most organisations reach certification readiness in four to eight months: a few weeks to set the ISMS scope, policies and risk assessment, then embedding the Annex A controls and running the ISMS long enough to evidence it before the stage-2 audit. Organisations with existing security controls move faster.
What makes your ISO 27001 toolkit different from others online?
This toolkit is published by Governance Docs and drafted against the text of ISO/IEC 27001:2022. Unlike basic templates, it’s structured, complete, and based on real-world compliance projects—making it one of the most trusted toolkits available today.
Find More Products:
Implementing for clients? The Consultant Package bundles 89 toolkits — 8,100+ editable templates — under one firm-wide licence that covers unlimited client engagements. $1,399 one-time.
Moving from CertiKit? CertiKit closes on 18 December 2026 and its ISO 27001 toolkit, which sold for £595, is no longer being updated. This one is $99 with twelve months of free updates. See how the two toolkits compare.
Guides for the ISO 27001 Toolkit
Free articles that explain the requirements this toolkit covers.

 ISO 27001 Toolkit - 165 Comprehensive Templates$99.00







I have not got a chance to use it yet but once I do, I will be glade to comment on it. Regards
I am extremely pleased with the exceptional service provided by the Government Docs Team. From start to finish, their professionalism, expertise, and dedication to meeting my needs exceeded all expectations.
The team demonstrated remarkable attention to detail while assisting with all of my ISO-related requirements, ensuring that every aspect of my projects was handled accurately, efficiently, and in full compliance with the necessary standards. Their commitment to quality and thoroughness gave me complete confidence throughout the entire process.
What truly sets the Government Docs Team apart is their willingness to go beyond the minimum requirements. They took the time to understand my goals, provided valuable guidance, and consistently delivered solutions that helped move my projects forward successfully. Their responsiveness, clear communication, and customer-focused approach made what could have been a complex process feel seamless and stress-free.
I highly recommend the Government Docs Team to anyone seeking reliable, knowledgeable, and detail-oriented professionals. Their outstanding support, dedication, and commitment to excellence have been instrumental in helping me accomplish my projects and exceed my ISO compliance objectives.
Thank you for your exceptional service and for continually going above and beyond to support your clients’ success.
Useful pack with a great variety of templates. Made my work much quicker and easier.