Description
Independent ISO 42001 Internal Audit, Delivered Remotely
ISO/IEC 42001 Clause 9.2 requires an internal audit of your AI management system (AIMS) before certification and every year after. The auditor must be competent and must not audit their own work. In most organisations adopting ISO 42001, the people who understand the AI systems well enough to audit them are the same people who built and govern them.
Governance Docs performs that audit for you. A Lead Auditor with no role in your AIMS audits it against ISO/IEC 42001:2023 and your own AI policy and procedures, then gives you the full Clause 9.2 evidence trail your certification body expects to see. Because ISO 42001 is new and accredited auditors are scarce, a well-documented internal audit matters more than usual: it is often the first thing the certification body reads.
Packages
| Package |
Best for |
Effort |
Price (USD) |
| Essentials |
Up to 50 people in scope, up to 3 AI systems, one site plus cloud |
About 2 auditor days |
$2,750 |
| Standard |
51 to 250 people in scope, up to 8 AI systems, or two sites |
About 3 auditor days |
$4,250 |
| Annual Programme |
Two Essentials audits about 12 months apart, same Lead Auditor: covers your pre-certification and first surveillance-year audits |
2 audit cycles |
$4,950 per year |
Rush delivery (start within 5 business days, report within 2 business days of the closing meeting) adds 20% to the audit fee. Need more than your package covers? Add an additional site ($750) or a corrective-action verification ($650). Larger scopes, or a combined ISO 42001 and ISO 27001 audit, are quoted on request.
What You Receive
- Audit plan: objectives, scope, criteria, sampling approach and session schedule, agreed before fieldwork.
- Remote audit sessions: four half-day sessions on screen-share, plus opening and closing meetings.
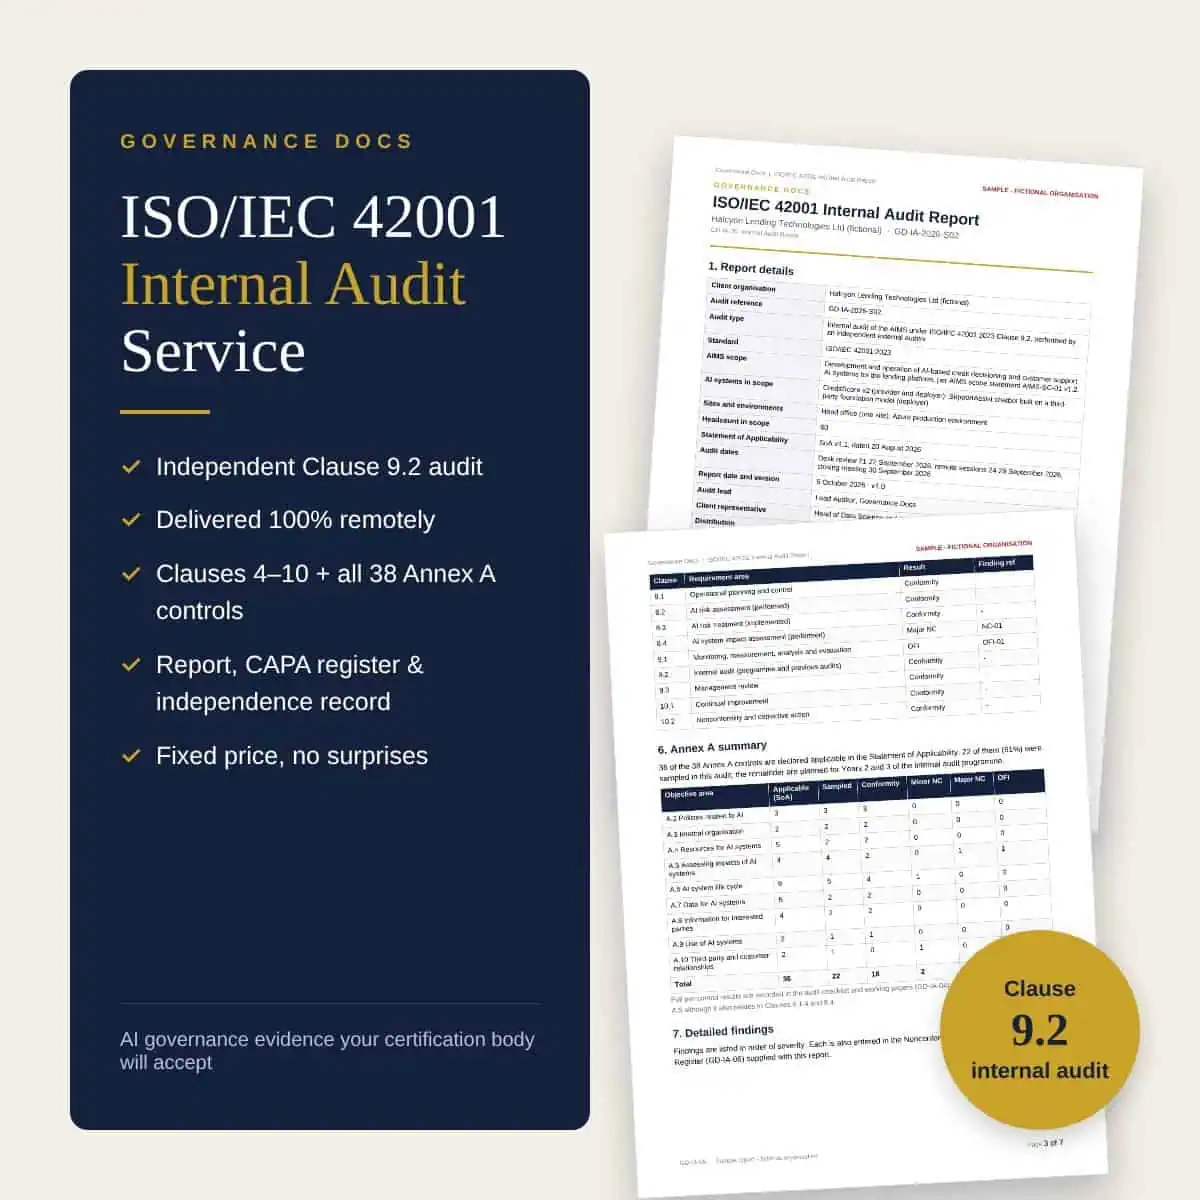
- Internal audit report: findings graded as major nonconformity, minor nonconformity or opportunity for improvement, each with objective evidence. Ready to take to management review.
- Nonconformity & corrective action register: every finding pre-loaded so you can record correction, root cause and corrective action (Clause 10.2).
- Checklist summary: results for every requirement in Clauses 4–10 and for all 38 Annex A controls.
- Auditor competence and independence record: a signed record, issued to you privately, that you can show your certification body on request.
- Internal audit programme template: a three-year, risk-based programme, if you do not have one yet.
Download a sample report (PDF). It uses a fictional organisation, so you can see exactly what you will get.
What the Audit Covers
- Clauses 4–10 in full: context and your AI roles, AI policy, AI risk assessment and treatment, AI system impact assessment, objectives, competence, operational control, monitoring, management review and corrective action.
- Annex A: all applicable controls across the nine objective areas, from AI policies and internal organisation to the AI system life cycle, data, information for interested parties, responsible use and third parties.
- Sampled AI systems: for two or three systems we follow the evidence from requirements and design through verification, deployment and operation.
How It Works
- Order and intake. After checkout, complete the intake form (about 10 minutes). We confirm your start date within one business day.
- Scoping call and plan. A 30-minute call to confirm scope and the AI systems in it. We then send the audit plan and a document request list.
- Desk review. We review your scope, AI policy, AI risk assessment, impact assessments, Statement of Applicability and key records.
- Remote sessions. We interview your team and review evidence on screen-share, including model documentation, evaluation results and monitoring.
- Closing meeting. We walk you through every finding before anything is written down.
- Report. The final report, register and independence record arrive within 5 business days of the closing meeting.
Typical elapsed time from intake to report is about three weeks. Sessions are scheduled to suit GCC, European and US time zones.
Is This Right for You?
This service fits best when your AIMS is already operating. Before ordering, check that you have:
- a defined and approved AIMS scope with an inventory of the AI systems in it;
- a completed AI risk assessment;
- at least one completed AI system impact assessment;
- an approved Statement of Applicability;
- an approved AI policy.
Still building these? Start with the free ISO 42001 gap assessment, the AI impact assessment tool and the ISO 42001 Toolkit, then book your internal audit once the AIMS has been running for a few weeks.
Independence, Taken Seriously
An internal audit only counts if it is objective. We therefore do not audit an AIMS, or AI systems, that Governance Docs has helped implement through consultancy in the last 24 months, and we do not sell implementation services to fix the findings we raise. Buying one of our documentation toolkits is not consultancy, so toolkit customers are welcome. The purchase is simply disclosed in the independence record.
Our Lead Auditor holds recognised information security and audit credentials and has more than 18 years of experience in information security and GRC in regulated financial services, with AI governance work for regulated clients. The record of the auditor’s competence and independence is issued privately to each client.
Limited Monthly Capacity
We take on a maximum of five audits each month across our services, so that every audit gets senior attention. Your start date is confirmed within one business day of receiving your intake form.
Frequently Asked Questions
Is an internal audit mandatory for ISO 42001 certification?
Yes. Clause 9.2 of ISO/IEC 42001 requires internal audits at planned intervals. Certification bodies expect to see at least one completed internal audit, with its programme, report and follow-up, before the Stage 2 certification audit, and an internal audit every year after that.
Can we use an external company for our internal audit?
Yes. The internal audit remains your organisation’s responsibility, but the standard allows you to use any auditor who is competent and objective. Outsourcing is the most common way organisations meet the independence requirement, especially for a new standard where few people have audit experience.
Is this a certification audit?
No. Governance Docs is not a certification body and does not issue certificates. This is the internal audit that Clause 9.2 requires you to perform. It prepares you for the certification audit, but it cannot guarantee its outcome.
Do you test our models for bias or security?
No. We audit whether your AIMS requires such testing, whether it was done and whether the results were acted on. Technical testing of models, red-teaming and penetration testing are separate engagements.
We use a third-party foundation model. Is that in scope?
Yes, if the AI system built on it is in your AIMS scope. ISO 42001 treats you as a deployer, so we audit your supplier controls, impact assessment, intended-use rules and monitoring for that system, not the provider’s internal processes.
We bought your ISO 42001 Toolkit. Can you still audit us?
Yes. A documentation toolkit is not consultancy, and your team adapted and implemented it. We disclose the purchase in the independence record. We cannot audit an AIMS that Governance Docs implemented for you through consultancy in the previous 24 months.
Can you audit ISO 42001 and ISO 27001 together?
Yes. The two standards share the same management-system clauses, so an integrated audit saves time. Contact us for a combined quote; the integrated audit is priced below two separate audits.
How do I pay and what if I need to cancel?
You pay at checkout, or by invoice by arrangement. You get a full refund if you cancel before the desk review starts, and 50% if you cancel after the desk review but before the first audit session. The full terms are in the ISO 42001 Internal Audit Service Terms.
By ordering you agree to the ISO 42001 Internal Audit Service Terms. Prices are in US dollars and exclude any applicable taxes.

 ISO 42001 Internal Audit Service$2,750.00 – $5,500.00Price range: $2,750.00 through $5,500.00



Reviews
There are no reviews yet