CART
NIST 800-171 Rev 3 is the current NIST publication for protecting Controlled Unclassified Information in nonfederal systems — final since May 2024, superseding Revision 2, which NIST withdrew on 14 May 2024 — and it is also the revision most defense contractors must not build to yet. The two facts sit together because two different authorities are involved: NIST decides what the current standard is, and the regulation that binds you decides which revision it incorporates.
CMMC and DFARS 252.204-7012 remain on Revision 2 through a DoD class deviation; contracts and agreements outside that regime may name Revision 3. This guide sets out what changed between Rev 2 and Rev 3 — 110 requirements in 14 families became 97 in 17, with organization-defined parameters, three new families and a rewritten assessment companion — which revision applies to whom, how to tell Rev 2 and Rev 3 content apart, and how to run a program that satisfies the one you owe while staying ready for the other.
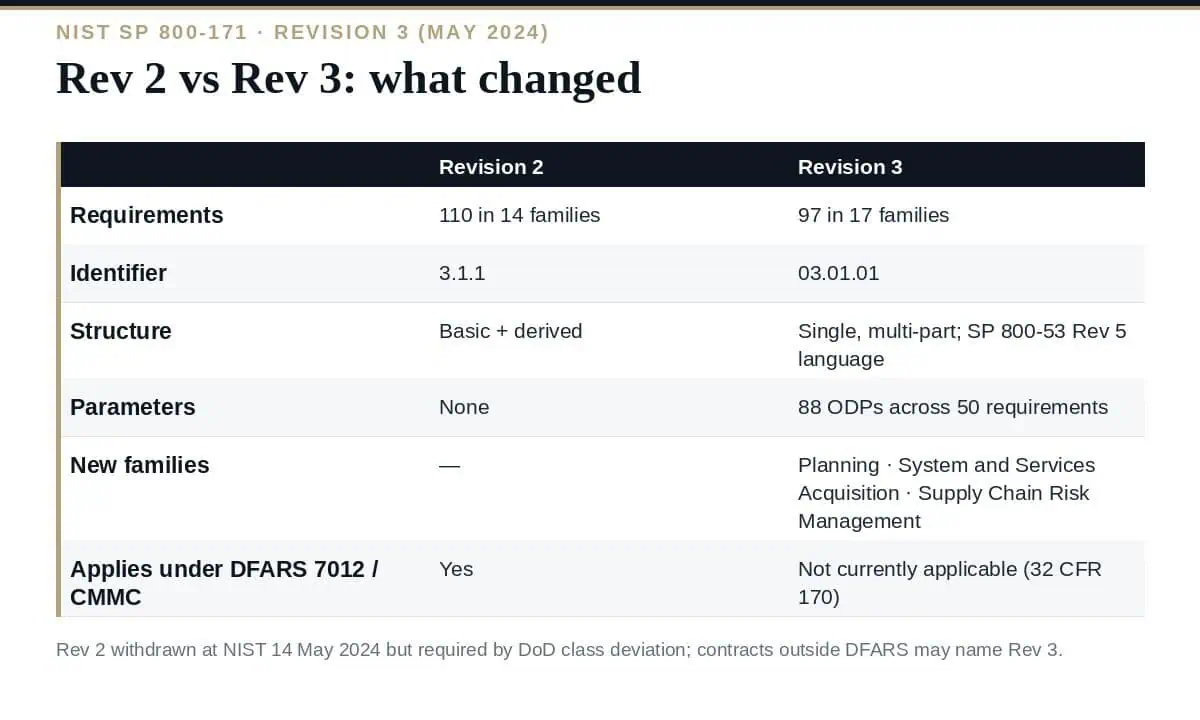
| Revision 2 (Feb 2020, updated Jan 2021) | Revision 3 (May 2024) | |
|---|---|---|
| Status at NIST | Withdrawn 14 May 2024 | Current; no Rev 4 |
| Security requirements | 110 across 14 families | 97 across 17 families (130 identifiers, 33 marked withdrawn) |
| Structure of a requirement | Basic requirements plus derived requirements | Single requirements, many multi-part, aligned to SP 800-53 Rev 5 control language |
| Identifier format | 3.1.1 | 03.01.01 (leading zeros, matching 800-171A) |
| Organization-defined parameters | None | 88 ODPs in 50 requirements; values set by the agency or, failing that, by the organization |
| Families added | — | Planning (PL), System and Services Acquisition (SA), Supply Chain Risk Management (SR); Security Assessment renamed Security Assessment and Monitoring (CA) |
| Tailoring categories | NCO, FED, NFO, CUI | NCO, FED, ORC, N/A, CUI — NFO eliminated |
| Source baseline | SP 800-53 Rev 4 moderate | SP 800-53 Rev 5 / SP 800-53B moderate, with a published CUI overlay |
| Assessment companion | SP 800-171A (June 2018), 320 objectives | SP 800-171A Rev 3 (May 2024), procedures restructured to SP 800-53A syntax |
| Applies under CMMC / DFARS 7012 | Yes — by class deviation and the CMMC rule | No — “not currently applicable” per 32 CFR Part 170 |
NIST’s own FAQ on the revision lists the significant differences. Five of them change what an implementer actually does.
| Family | Rev 3 identifier | Active requirements |
|---|---|---|
| Access Control | 03.01 | 16 |
| Awareness and Training | 03.02 | 2 |
| Audit and Accountability | 03.03 | 8 |
| Configuration Management | 03.04 | 10 |
| Identification and Authentication | 03.05 | 8 |
| Incident Response | 03.06 | 5 |
| Maintenance | 03.07 | 3 |
| Media Protection | 03.08 | 7 |
| Personnel Security | 03.09 | 2 |
| Physical Protection | 03.10 | 5 |
| Risk Assessment | 03.11 | 3 |
| Security Assessment and Monitoring | 03.12 | 4 |
| System and Communications Protection | 03.13 | 10 |
| System and Information Integrity | 03.14 | 5 |
| Planning (new) | 03.15 | 3 |
| System and Services Acquisition (new) | 03.16 | 3 |
| Supply Chain Risk Management (new) | 03.17 | 3 |
Counts are of active requirements after the 33 withdrawn identifiers are excluded; Access Control, for example, runs 03.01.01 to 03.01.22 but six of those are marked withdrawn and incorporated elsewhere. Our guide to NIST 800-53 control families covers the parent catalog the families are drawn from.
| Your obligation | Revision to implement | Why |
|---|---|---|
| DFARS 252.204-7012 covered defense information | Rev 2 | DoD’s May 2024 class deviation holds 7012 at Rev 2; the September 2025 DFARS rule cites SP 800-171 without moving the revision |
| CMMC Level 2 (self-assessment, or a voluntary C3PAO assessment) | Rev 2 | 32 CFR Part 170 assesses the 110 Rev 2 requirements and states Rev 3 is not currently applicable; Part 170 is unamended |
| SPRS score under the DoD Assessment Methodology | Rev 2 | The methodology scores 110 requirements from 110 down to −203 |
| A civilian-agency contract or agreement that names SP 800-171 | Whichever it names — increasingly Rev 3 | Outside DFARS there is no deviation; read the clause |
| A commercial customer flowing down ‘NIST 800-171’ | Ask | Many mean Rev 2 because their own obligation is DFARS; some mean the current NIST publication |
| No contractual driver; using 800-171 as a voluntary baseline | Rev 3 | It is the current standard and the direction every regime will eventually move |
The 13 July 2026 suspension of CMMC Phase 2 did not change any of this: DFARS 7012 and Phase 1 self-assessments continue, on Rev 2. Our guide to CMMC vs NIST 800-171 covers how the program layers on the standard.
Because the two revisions are both in circulation, templates, SSPs and vendor documents get mislabelled — including, in our own experience, a pack whose content was Rev 2 under labels that said Rev 3. Three tells settle it without reading a requirement:
Our guide to NIST 800-171 templates applies the same tests to document sets.
Is NIST 800-171 Rev 3 mandatory?
It is the current NIST publication, but whether it binds you depends on the regulation or contract that incorporates SP 800-171. DFARS 252.204-7012 and CMMC remain on Rev 2 by DoD class deviation; other agreements may name Rev 3.
How many requirements are in Rev 3?
97 security requirements across 17 families, down from 110 in 14 families in Rev 2. The catalog has 130 identifiers, 33 of which are marked withdrawn and incorporated into other requirements.
What are organization-defined parameters?
Values the requirement leaves open — a number, a frequency, a time period — that the federal agency may set and that the organization must set if the agency does not. Rev 3 has 88 of them across 50 requirements, consolidated in Appendix D.
Is Rev 2 still available?
NIST withdrew it on 14 May 2024 but it remains published as a superseded document, and DoD requires it: the CMMC rule assesses Rev 2 and Part 170 has not been amended.
When will CMMC move to Rev 3?
No date has been set; the CMMC final rule states Rev 3 is not currently applicable, and the July 2026 suspension of Phase 2 has not changed the revision. Track the Federal Register for an amendment to 32 CFR Part 170 or a new DFARS deviation.
Treat NIST 800-171 Rev 3 as the destination and Rev 2 as the obligation: implement and score the 110 Rev 2 requirements for anything that runs through DFARS or CMMC, keep a crosswalk to the 97 Rev 3 requirements, set the 88 parameter values in policy now, and read every contract clause for the revision it actually names.
The System Security Plan, the POA&M, the control-family policies and procedures and the CUI scoping workbook — built to Revision 2 because that is what DFARS and CMMC assess — are in the NIST SP 800-171 CUI Protection Toolkit, or start with the free templates.


September 21, 2026

September 21, 2026

September 20, 2026

September 20, 2026

September 19, 2026

