Cyber Risk Quantification: A Clear Guide to FAIR Indicators Governance Docs17th September 2026 Cyber risk quantification with FAIR: the factors from threat event frequency to loss magnitude, the 5 indicators it… Read More
NIST SP 800-55: A Clear Guide to Security Measurement Indicators Governance Docs17th September 2026 NIST SP 800-55 (December 2024, two volumes): the 4 measure types, the 10 documentation fields, what makes a… Read More
MTTD vs MTTR: A Clear Guide to the 4 Cyber Response Indicators Governance Docs17th September 2026 MTTD vs MTTR explained as 4 clocks on one incident timeline — detect, acknowledge, contain, recover — with… Read More
Board Cybersecurity Reporting: A Clear Guide to the 6 Indicators Governance Docs17th September 2026 Board cybersecurity reporting built on 6 indicators — exposure, control coverage, detection and response speed, incident impact, third-party… Read More
ISO 27001 Assessment Report: A Clear Guide to the 6 Sections Governance Docs17th September 2026 The ISO 27001 assessment report in 6 sections — summary, method, clause results, Annex A results, findings, action… Read More
Supplier Security Assessment: A Clear ISO 27001 Guide for 2026 Governance Docs17th September 2026 A supplier security assessment under ISO 27001 controls A.5.19–A.5.22: tier suppliers, what to ask, what evidence to accept,… Read More
ISO 27001 Control Assessment: A Clear Annex A Scoring Guide Governance Docs17th September 2026 The ISO 27001 control assessment: scoring all 93 Annex A controls for applicability, implementation and evidence, with the… Read More
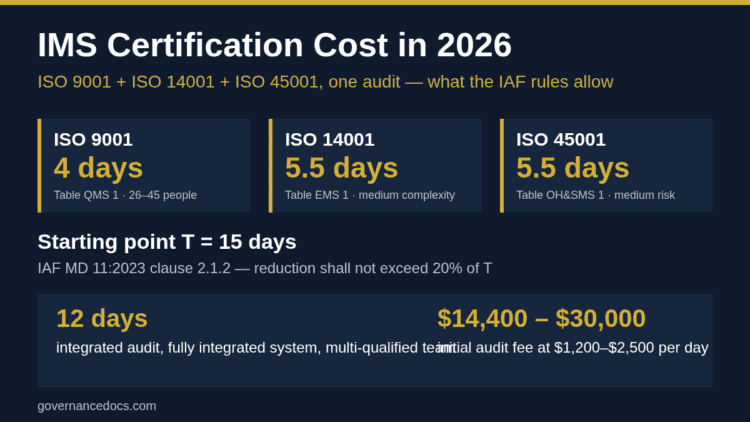
IMS Certification Cost in 2026: The Complete Breakdown Governance Docs17th September 2026 IMS certification cost runs about $14,400-$30,000 in registrar fees for a 40-person company in 2026. How IAF MD… Read More
ISO 27001 Gap Assessment: A Clear Guide to the 4 Outputs Governance Docs17th September 2026 An ISO 27001 gap assessment delivers 4 outputs: a gap register, a prioritized remediation plan, a draft SoA… Read More
ISO 27001 Self-Assessment: A Clear Guide to Scoring All 93 Controls Governance Docs17th September 2026 An ISO 27001 self-assessment scores clauses 4–10 and all 93 Annex A controls on a 5-point scale with… Read More
CMMC Phase 2 Suspended: A Clear Guide to What Still Applies in 2026 Governance Docs17th September 2026 CMMC Phase 2 was due 10 November 2026 and was suspended on 13 July 2026. What stopped, what… Read More
CMMC Scoping: A Clear Guide to the 5 Asset Categories Governance Docs17th September 2026 CMMC scoping under 32 CFR 170.19: the 5 Level 2 asset categories and how each is assessed, the… Read More