

Every assessment here asks the same kind of question, clause by clause: is this actually in place, and could you prove it? You answer, it scores you, and you find out where you stand before a customer, an auditor or a regulator tells you.
How it works
- Pick a standard and work through it. Nothing to install and nothing to download. Your answers save as you go, so you can stop, gather evidence and come back.
- Score yourself honestly. Every requirement uses the same five-point scale, from nothing in place through to implemented and evidenced. Anything you can justify as out of scope is excluded from the result rather than counted against you.
- See where you stand. A free account gets you your overall readiness score. The optional full report adds your score for every domain, every open gap in priority order, a remediation plan naming the document that closes each one, and your answers as a live Excel workbook.
Premium report
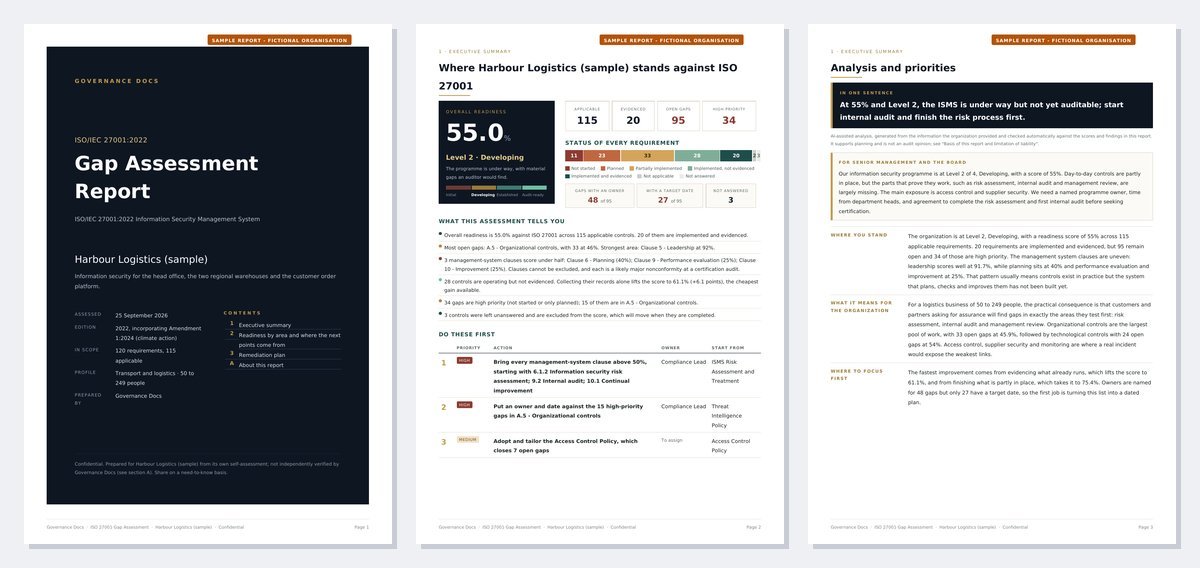
See what the premium gap assessment report looks like
A worked sample for a fictional organization: readiness by area, every open gap in a remediation plan, an AI-assisted analysis with priorities and a 30/60/90-day roadmap, plus the live Excel workbook.
Not sure which one applies to you?
Four questions. Nothing is stored, and you can start any assessment without answering them.
Information security and cyber
Certifiable management standards and the control catalogues customers and auditors ask for.
ISO 27001
Free assessmentISO/IEC 27001:2022 Information Security Management System
The certifiable information security management standard. Scores you against all seven management clauses and all 93 Annex A controls.
- 120 questions
- about 45 minutes
- saves as you go
SOC 2
Free assessmentSOC 2 Trust Services Criteria
The report North American customers ask for. Scope your categories, then score all 33 common criteria plus availability, confidentiality, processing integrity and privacy.
- 69 questions
- about 35 minutes
- saves as you go
NIST CSF 2.0
Free assessmentNIST Cybersecurity Framework (CSF) 2.0
Govern, Identify, Protect, Detect, Respond, Recover. All 106 subcategories scored, so you can show a board where the programme actually stands.
- 106 questions
- about 45 minutes
- saves as you go
CIS Controls
Free assessmentCIS Critical Security Controls Version 8.1
The prioritised control set, scored the way CIS structures it. Implementation Group 1 is treated as the floor every organisation should clear, so you find out whether you have essential cyber hygiene before you worry about the rest.
- 66 questions
- about 40 minutes
- saves as you go
PCI DSS 4.0
Free assessmentPCI DSS v4.0.1 Payment Card Industry Data Security Standard
All twelve requirements at sub-requirement level, scoped to how you actually take payments, with the requirements that became mandatory in March 2025 called out.
- 73 questions
- about 40 minutes
- saves as you go
BSI C5
Free assessmentBSI Cloud Computing Compliance Criteria Catalogue C5:2026
The German cloud attestation catalogue at its 2026 edition, including what is new: container management, confidential computing, tenant separation and post-quantum readiness. Covers the system description and customer responsibility boundary, which is where C5 engagements usually go wrong.
- 73 questions
- about 45 minutes
- saves as you go
NIS2
Free assessmentEU NIS2 Directive (Directive (EU) 2022/2555) cybersecurity risk-management measures
Scope, the ten Article 21 measures, the 24-hour and 72-hour reporting clocks, and the management-body duties that carry personal liability.
- 60 questions
- about 30 minutes
- saves as you go
CMMC 2.0
Free assessmentCMMC 2.0 Level 2 / NIST SP 800-171 Rev 2
All 110 Level 2 practices, plus the scoping, POA&M eligibility and affirmation duties a defence supplier has to evidence before an SPRS score means anything.
- 123 questions
- about 50 minutes
- saves as you go
IEC 62443
Free assessmentIEC 62443-2-1:2024 IACS Security Programme for Asset Owners
The asset owner security programme as the 2024 edition restructured it - eight programme elements, not the old management system clauses - with zones, conduits and target security levels scored alongside.
- 61 questions
- about 40 minutes
- saves as you go
NIST RMF
Free assessmentNIST Risk Management Framework for Information Systems and Organizations
The seven-step authorisation lifecycle, task by task. Prepare is split into its organisation-level and system-level halves the way NIST splits it, so the organisation-level answers carry over to every system you assess after the first.
- 53 questions
- about 40 minutes
- saves as you go
NIST SP 800-53
Free assessmentNIST SP 800-53 Security and Privacy Controls for Information Systems and Organizations
The federal control catalogue at the level you can actually assess: all twenty families, anchored on the controls that carry the most weight, plus the categorisation, baseline and parameter decisions that everything below them depends on.
- 66 questions
- about 45 minutes
- saves as you go
FedRAMP
Free assessmentFedRAMP Certification under the Consolidated Rules for 2026
Written to the 2026 rules, not the old ones. Key Security Indicators, the Security Decision Record that replaced the SSP, Accepted Weaknesses in place of POA&Ms, and the notification clocks on significant change that catch most providers out.
- 60 questions
- about 45 minutes
- saves as you go
AI governance
Governance over the AI systems you build, buy or put in front of customers.
ISO 42001
Free assessmentISO/IEC 42001:2023 Artificial Intelligence Management System
The certifiable AI management standard, and the fastest route to evidencing EU AI Act governance. All seven clauses plus the 38 Annex A controls.
- 67 questions
- about 30 minutes
- saves as you go
EU AI Act
Free assessmentEU Artificial Intelligence Act (Regulation (EU) 2024/1689)
Classify your systems, then score what already applies - prohibitions, AI literacy, transparency and GPAI - separately from the high-risk duties that now land in 2027 and 2028.
- 65 questions
- about 35 minutes
- saves as you go
Privacy and data protection
What you owe the people whose data you hold, wherever they are.
GDPR
Free assessmentEU General Data Protection Regulation (Regulation (EU) 2016/679)
Lawful basis, records of processing, data subject rights, transfers and breach readiness, article by article, the way a supervisory authority would ask for them.
- 88 questions
- about 40 minutes
- saves as you go
HIPAA
Free assessmentHIPAA Security, Privacy and Breach Notification Rules (45 CFR Parts 160 and 164)
Administrative, physical and technical safeguards, the privacy and breach rules, and the addressable-versus-required decisions an OCR investigator will ask you to justify.
- 96 questions
- about 45 minutes
- saves as you go
ISO 27701
Free assessmentISO/IEC 27701:2025 Privacy Information Management System
The standalone privacy management system, not the old extension to ISO 27001. Clauses 4 to 10 plus the controller, processor and security control sets, with privacy risk scored as risk to the individual.
- 48 questions
- about 40 minutes
- saves as you go
Continuity and operational resilience
Staying available, and proving you would survive the day it goes wrong.
DORA
Free assessmentEU Digital Operational Resilience Act (Regulation (EU) 2022/2554)
All five pillars, from the ICT risk framework to the register of information, with the incident clocks and the third-party contract terms a supervisor will actually test.
- 78 questions
- about 40 minutes
- saves as you go
ISO 22301
Free assessmentISO 22301:2019 Business Continuity Management System
The certifiable business continuity standard. Every clause from context to improvement, with the business impact analysis and plan requirements broken out the way an auditor reads them.
- 64 questions
- about 30 minutes
- saves as you go
Risk, data and delivery
The disciplines that sit underneath everything else: how risk is governed, how data is managed, and how projects actually get delivered.
ISO 31000
Free assessmentISO 31000:2018 Risk management - Guidelines
A maturity assessment, not a conformity one, because ISO 31000 is guidance and nobody can be certified against it. Scores how far risk management is actually embedded in decisions, against the eight principles, the framework and the process.
- 53 questions
- about 35 minutes
- saves as you go
Data governance
Free assessmentData Governance and Data Management Maturity Assessment, anchored on DAMA-DMBOK2
All eleven DAMA knowledge areas, plus the ethics, AI and organisational change chapters that sit off the wheel. Scored as maturity rather than conformity, because a body of knowledge is not something an organisation can be certified against.
- 60 questions
- about 40 minutes
- saves as you go
Project management
Free assessmentProject Management Maturity Assessment, anchored on ISO 21502:2020
Vendor-neutral and delivery-approach agnostic, so predictive, agile and hybrid teams are scored on the same basis. Anchored on ISO 21502 rather than any one institute's method, and framed as maturity because no organisation can be certified against these standards.
- 56 questions
- about 40 minutes
- saves as you go
Quality and product assurance
The certifiable quality standards customers and regulators audit you against, from general manufacturing to medical devices.
ISO 9001
Free assessmentISO 9001:2026 Quality Management System
The new edition, scored as it now reads. Risks and opportunities split apart, quality culture and ethical behaviour as real requirements, and the clause 10 renumbering that breaks every converted 2015 checklist.
- 61 questions
- about 40 minutes
- saves as you go
IATF 16949
Free assessmentIATF 16949:2016 Automotive Quality Management System
Only the automotive supplemental requirements, because the ISO 9001 base is assessed separately. Covers customer-specific requirements, product safety, the control plan and the core tools, and flags the clauses IATF has named as priorities for the second edition.
- 66 questions
- about 45 minutes
- saves as you go
ISO 13485
Free assessmentISO 13485:2016 Medical Devices Quality Management System
Clauses 4 to 8 as the standard actually reads, with the named mandatory procedures, the Medical Device File, and the FDA QMSR and EU MDR duties scored separately so you can see what is the standard and what is the regulator.
- 89 questions
- about 45 minutes
- saves as you go
Health, safety and environment
Keeping people safe at work, and proving the system that does it actually runs.
ISO 45001
Free assessmentISO 45001:2018 Occupational Health and Safety Management System
The certifiable occupational health and safety standard. Every clause, with worker consultation, the hierarchy of controls and incident investigation scored the way an auditor tests them.
- 54 questions
- about 35 minutes
- saves as you go
ISO 14001
Free assessmentISO 14001:2026 Environmental Management System
The new edition, scored as it now reads. Risks and opportunities promoted to their own clause, planning of changes added, clause 10 cut to two - and the renumbering that breaks every 2015 checklist.
- 46 questions
- about 35 minutes
- saves as you go
Food safety
Hazard control and food hygiene, from the Codex text through to the certification schemes built on top of it.
HACCP
Free assessmentHACCP and Good Hygiene Practices under Codex Alimentarius CXC 1-1969
The whole of CXC 1-1969, not just the seven principles. Good Hygiene Practices carry roughly forty per cent of the questions because that is where most real failures sit, with the twelve application steps and the US and EU overlays on top.
- 61 questions
- about 40 minutes
- saves as you go
IT service management
Running services to agreed levels, and proving the management system behind them works.
ISO 20000
Free assessmentISO/IEC 20000-1:2018 Service Management System
The certifiable IT service management standard, where clause 8 is most of the standard. Every service management process, plus the service management plan, service reporting and knowledge requirements that generic checklists miss.
- 48 questions
- about 40 minutes
- saves as you go
Gulf regulatory
The regulator-issued frameworks that apply to licensed entities across the Gulf.
SAMA CSF
Free assessmentSaudi Central Bank (SAMA) Cyber Security Framework
All 32 sub-domains across the four SAMA domains, so you can see where the programme stands before you translate it into the maturity level SAMA expects.
- 41 questions
- about 25 minutes
- saves as you go
NCA ECC
Free assessmentSaudi National Cybersecurity Authority Essential Cybersecurity Controls (ECC-2:2024)
All 28 subdomains of ECC-2:2024, plus the scoping, other-control-set and reporting questions that decide what the NCA actually assesses you against.
- 44 questions
- about 25 minutes
- saves as you go
Risk and resilience assessments
Not a gap assessment against one standard, but the analysis a standard asks you to carry out. Free, and each saves as you go.
Business impact analysis
ISO 22301Which activities come back first after a disruption, how long each can be down, and what they depend on.
Information Security Risk Assessment
ISO 27001Set your criteria, pick from 61 information security scenarios, rate them and plan treatment against Annex A.
Privacy Risk Assessment
ISO 27701Privacy risks to the people whose data you hold and to you, treated with ISO 27701 Annex A controls, with GDPR in mind.
Business Continuity Risk Assessment
ISO 22301The events that could stop your prioritized activities, rated and matched to continuity measures.
Enterprise Risk Assessment
ISO 31000Strategic, financial, operational, legal and reputational risks against your own appetite.
AI Risk Assessment
ISO 42001Risks from the AI you build, buy or use, rated for the people affected and treated with ISO 42001 Annex A controls.
Data Protection Impact Assessment
GDPRA GDPR Article 35 DPIA for one processing operation: screening, necessity, risks to individuals, measures and sign-off.
Transfer Impact Assessment
GDPRA transfer impact assessment for one transfer out of the EEA or UK: screening, the destination's laws, transfer risks, supplementary measures and sign-off.
AI System Impact Assessment
ISO 42005An ISO/IEC 42005 impact assessment for one AI system: screening, the system, safeguards, impacts on people and society, measures and decision.
Legitimate Interests Assessment
GDPRA legitimate interests assessment for one processing activity: screening, the purpose, necessity and balancing tests, impact on people, safeguards and conclusion.
Third-Party Risk Assessment
ISO 27001A third-party risk assessment for one vendor: tiering, profile, due diligence, risks, controls referenced to ISO 27001, NIST and DORA, and the decision.
Questions people ask first
- Is the gap assessment really free?
- Yes. Working through every clause and control, and seeing your overall readiness score, costs nothing. The paid report is optional: it adds your score for each domain, every open gap in priority order, a remediation plan naming the document that closes each one, and your answers as a live Excel workbook.
- Do I need an account?
- You can start answering straight away without one. You need a free account to see your score, because the score and the report are tied to your organisation's record rather than to a browser.
- How long does it take?
- Between about thirty minutes and an hour, depending on the standard and how much you already know off the top of your head. Your answers save as you go, so you can stop, gather evidence and come back.
- Is this a certification, or an audit?
- No. It is a self-assessment: you score yourself, so the result is only as honest as the answers. It is designed to tell you where to start and what to fix before a certification body or a regulator looks at you, not to replace either.
- Can I reuse the assessment later?
- Yes. Come back whenever you like, update the answers you have moved on, and your score updates with them. If you have bought the report for an assessment, you can regenerate it free every time you change your answers.
- Which standard should I start with?
- If nobody has told you which one you need, ISO 27001 is the usual starting point: it is the information security management standard most customers, tenders and regulators recognise, and much of what you build for it is reused by every other framework. The chooser on this page narrows it down if your situation is more specific.