About Us Contact Blog
Governance DocsGovernance Docs
Which Toolkit?SoA GeneratorFree TemplatesSample ReportsFind the Right AssessmentRecords of Processing (ROPA)Data Privacy Impact AssessmentLegitimate Interests AssessmentTransfer Impact AssessmentPrivacy Risk AssessmentGDPR Gap AssessmentUK GDPR Gap AssessmentCCPA/CPRA Gap AssessmentISO 27701 Gap AssessmentHIPAA Gap AssessmentISO 27001 Risk AssessmentThird-Party Risk AssessmentSoA GeneratorISO 27001 Assessment Tool (Excel)ISO 27001 Gap AssessmentSOC 2 Gap AssessmentNIST CSF 2.0 Gap AssessmentNIST SP 800-53 Gap AssessmentNIST RMF Gap AssessmentCIS Controls Gap AssessmentPCI DSS 4.0 Gap AssessmentNIS2 Gap AssessmentCMMC 2.0 Gap AssessmentNIST SP 800-171 Gap AssessmentFedRAMP Gap AssessmentBSI C5 Gap AssessmentIEC 62443 Gap AssessmentSAMA CSF Gap AssessmentNCA ECC Gap AssessmentISO 20000 Gap AssessmentAI Risk AssessmentAI Impact AssessmentISO 42001 Gap AssessmentEU AI Act Gap AssessmentBusiness Impact AnalysisContinuity Risk AssessmentISO 22301 Assessment Tool (Excel)ISO 22301 Gap AssessmentDORA Gap AssessmentISO 9001 Gap AssessmentISO 13485 Gap AssessmentIATF 16949 Gap AssessmentISO 14001 Gap AssessmentISO 45001 Gap AssessmentISO 45001 Assessment Tool (Excel)HACCP Gap AssessmentEnterprise Risk AssessmentISO 31000 Gap AssessmentData Governance Gap AssessmentProject Management Gap AssessmentAll Gap AssessmentsAboutBlogContactMy AccountCart
FOX v.2.4.9
Browse Toolkits
Governance Docs
  • Browse All Toolkits
  • Information Security & Cybersecurity
  • Data Privacy & Protection
  • Governance, Risk & Compliance
  • Quality Management
  • Health, Safety & Environment
  • AI Governance

My Account

CART

No products in the cart.

Category: Articles

remote key distribution — PCI PIN Remote Key Distribution: Normative Annex A Explained

PCI PIN Remote Key Distribution: Normative Annex A Explained

Governance Docs08th September 2026

Remote key distribution under PCI PIN Annex A: the two sub-annexes, the design assurance requirement, the three barrier…
Read More
key injection facility — PCI PIN Key Injection Facilities: Normative Annex B Explained

PCI PIN Key Injection Facility: Normative Annex B Explained

Governance Docs08th September 2026

Key injection facility requirements under PCI PIN Annex B: the secure room, the clear-text injection dates and their…
Read More
Qualified PIN Assessor — Qualified PIN Assessor: What a PCI PIN Assessment Involves

Qualified PIN Assessor: What a PCI PIN Assessment Involves

Governance Docs08th September 2026

Qualified PIN Assessor explained: no self-assessment route, observation-led testing, the two-year listing clock that starts at signature, and…
Read More
dual control and split knowledge — Dual Control and Split Knowledge: The Difference That Fails Audits

Dual Control and Split Knowledge: The Difference That Fails Audits

Governance Docs08th September 2026

Dual control and split knowledge are two separate controls, not one. What each requires, the arrangements that look…
Read More
PCI PIN scope — PCI PIN Scope: Which of the 145 Requirements Apply to You

PCI PIN Scope: Which of the 145 Requirements Apply to You

Governance Docs08th September 2026

PCI PIN scope explained: the four requirement columns, why 96 + 85 + 105 + 94 does not…
Read More
PCI PIN key blocks — PCI PIN Key Blocks: The 3 Phases and What Phase 3 Did Not Require

PCI PIN Key Blocks: The 3 Phases and What Phase 3 Did Not Require

Governance Docs08th September 2026

PCI PIN key blocks explained: the three phases, why Phase 3 never required existing POI deployments to convert,…
Read More
PCI PIN vs PCI DSS — PCI PIN vs PCI DSS: Which One Applies to You in 2026

PCI PIN vs PCI DSS: Which One Applies to You in 2026

Governance Docs08th September 2026

PCI PIN vs PCI DSS explained: different assessors, no self-assessment route for PIN, a two-year cycle, and scope…
Read More
PCI PIN Security Requirements — PCI PIN Security Requirements: A Complete Guide to v3.1 in 2026

PCI PIN Security Requirements: A Complete Guide to v3.1 in 2026

Governance Docs08th September 2026

PCI PIN Security Requirements v3.1 explained: 7 control objectives, 33 requirements, 145 sub-requirements, the four scope columns and…
Read More
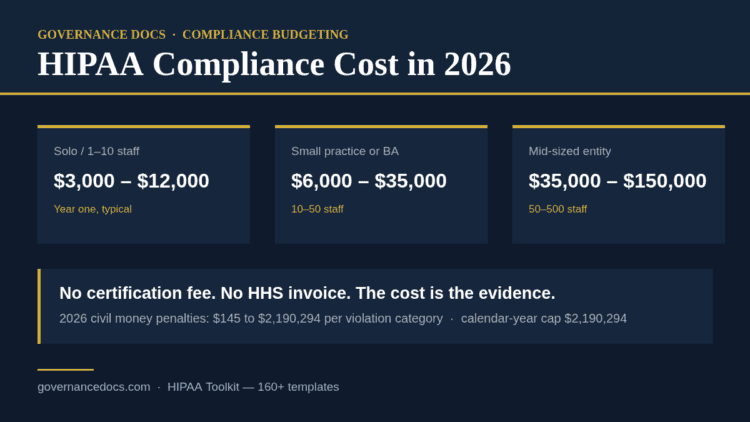
HIPAA compliance cost in 2026 broken down by organization size, with 2026 civil money penalty figures

HIPAA Compliance Cost in 2026: The Complete Breakdown

Governance Docs08th September 2026

HIPAA compliance cost in 2026 runs $3,000 to $35,000 in year one for most small organizations. A full…
Read More
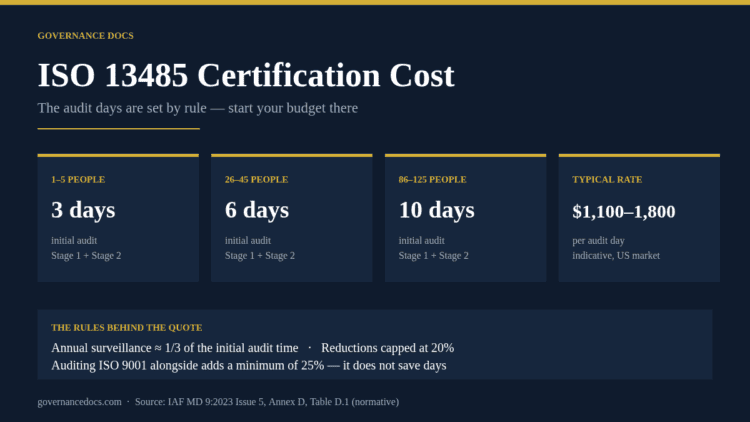
ISO 13485 certification cost breakdown showing IAF MD 9 audit days of 3, 6 and 10 for different company sizes and an indicative $1,100 to $1,800 per audit day rate

ISO 13485 Certification Cost: A Clear 2026 Breakdown

Governance Docs07th September 2026

ISO 13485 certification cost, broken down: the normative IAF audit-day table that sets your fee, indicative $1,100-$1,800 day…
Read More
AMLA direct supervision — AMLA Direct Supervision: Who Is Actually Selected in 2027

AMLA Direct Supervision: Who Is Actually Selected in 2027

Governance Docs07th September 2026

AMLA direct supervision reaches about 40 cross-border financial groups, not the whole market. The three gates, the timetable,…
Read More
suspicious transaction report — Suspicious Transaction Report Deadline: The Complete AMLR Guide

Suspicious Transaction Report Deadline: The Complete AMLR Guide

Governance Docs07th September 2026

A suspicious transaction report under AMLR has no fixed filing period. The clocks that do run, the two…
Read More

    ←
  • 1
  • …
  • 60
  • 61
  • 62
  • 63
  • 64
  • …
  • 100
  • →

Recent Posts

iso 30301 — ISO 30301 vs ISO 15489: Which Records Standard Do You Need?
ISO 30301 vs ISO 15489: Which Records Standard Do You Need?

October 12, 2026

legal hold — Legal Hold: How to Suspend Records Destruction Properly (2026)
Legal Hold: How to Suspend Records Destruction Properly (2026)

October 12, 2026

records retention schedule — Records Retention Schedule: How to Build One in 2026
Records Retention Schedule: How to Build One in 2026

October 12, 2026

iso 15489 — ISO 15489 Explained: The Records Management Standard in 2026
ISO 15489 Explained: The Records Management Standard in 2026

October 12, 2026

records management metadata — Records Management Metadata: What to Capture and Why (2026)
Records Management Metadata: What to Capture and Why (2026)

October 12, 2026

Categories

  • Articles
  • DORA
  • GDPR
  • HIPAA
  • ISO 27001
  • ISO 42001 & AI governance
  • ISO 9001
  • Management systems
  • NIS2
  • Security frameworks
  • SOC 2
Governance DocsGovernance Docs

Reliable ISO & compliance documentation toolkits that help your business meet regulatory standards with ease.

Governance Docs LLC
1209 Mountain Road Pl NE, Suite R
Albuquerque, NM 87110, USA
info@governancedocs.com
+1 505 289 2455

Toolkits

  • ISO 27001:2022
  • GDPR
  • SOC 2
  • PCI-DSS v4.0
  • HIPAA
  • ISO 42001
  • All toolkits →

Company

  • About Us
  • Blog
  • Contact
  • FAQ
  • Which toolkit do I need?
  • Free templates
  • SoA generator
  • Assessments
  • Sample reports
  • RSS feeds

Policies

  • Privacy Policy
  • Terms & Conditions
  • Refund & Return Policy
  • Delivery Policy
  • Manage cookies
Browse by topicISO 27001ISO 42001 & AI governanceGDPRSOC 2HIPAANIS2DORAISO 9001Management systemsSecurity frameworks
© 2026 Governance Docs LLC. All rights reserved.
Secure checkoutstripeVISA