About Us Contact Blog
Governance DocsGovernance Docs
Which Toolkit?SoA GeneratorFree TemplatesSample ReportsFind the Right AssessmentRecords of Processing (ROPA)Data Privacy Impact AssessmentLegitimate Interests AssessmentTransfer Impact AssessmentPrivacy Risk AssessmentGDPR Gap AssessmentUK GDPR Gap AssessmentCCPA/CPRA Gap AssessmentISO 27701 Gap AssessmentHIPAA Gap AssessmentISO 27001 Risk AssessmentThird-Party Risk AssessmentSoA GeneratorISO 27001 Assessment Tool (Excel)ISO 27001 Gap AssessmentSOC 2 Gap AssessmentNIST CSF 2.0 Gap AssessmentNIST SP 800-53 Gap AssessmentNIST RMF Gap AssessmentCIS Controls Gap AssessmentPCI DSS 4.0 Gap AssessmentNIS2 Gap AssessmentCMMC 2.0 Gap AssessmentNIST SP 800-171 Gap AssessmentFedRAMP Gap AssessmentBSI C5 Gap AssessmentIEC 62443 Gap AssessmentSAMA CSF Gap AssessmentNCA ECC Gap AssessmentISO 20000 Gap AssessmentAI Risk AssessmentAI Impact AssessmentISO 42001 Gap AssessmentEU AI Act Gap AssessmentBusiness Impact AnalysisContinuity Risk AssessmentISO 22301 Assessment Tool (Excel)ISO 22301 Gap AssessmentDORA Gap AssessmentISO 9001 Gap AssessmentISO 13485 Gap AssessmentIATF 16949 Gap AssessmentISO 14001 Gap AssessmentISO 45001 Gap AssessmentISO 45001 Assessment Tool (Excel)HACCP Gap AssessmentEnterprise Risk AssessmentISO 31000 Gap AssessmentData Governance Gap AssessmentProject Management Gap AssessmentAll Gap AssessmentsAboutBlogContactMy AccountCart
FOX v.2.4.9
Browse Toolkits
Governance Docs
  • Browse All Toolkits
  • Information Security & Cybersecurity
  • Data Privacy & Protection
  • Governance, Risk & Compliance
  • Quality Management
  • Health, Safety & Environment
  • AI Governance

My Account

CART

No products in the cart.

Category: Articles

SWIFT CSP non-compliance consequences and recovery plan

SWIFT CSP Non-Compliance: Consequences and Recovery 2026

Governance Docs29th September 2026

SWIFT CSP non-compliance is visible to supervisors and counterparties. Learn the categories, consequences and a practical recovery plan.
Read More
SOX for newly public companies IPO compliance timeline

SOX for Newly Public Companies: IPO Timeline 2026

Governance Docs29th September 2026

A practical guide to SOX after an IPO: what applies immediately, what the SEC transition period defers and…
Read More
SOC 1 subservice organization carve-out vs inclusive method

SOC 1 Subservice Organization: Carve-Out vs Inclusive 2026

Governance Docs29th September 2026

Understand how SOC 1 treats subservice organizations: carve-out versus inclusive, CSOCs and the monitoring evidence auditors expect.
Read More
Saudi PDPL privacy policy Article 12 checklist

Saudi PDPL Privacy Policy: What Article 12 Requires in 2026

Governance Docs29th September 2026

Article 12 of the Saudi PDPL requires a privacy policy before collection. See the eight required elements, timing…
Read More
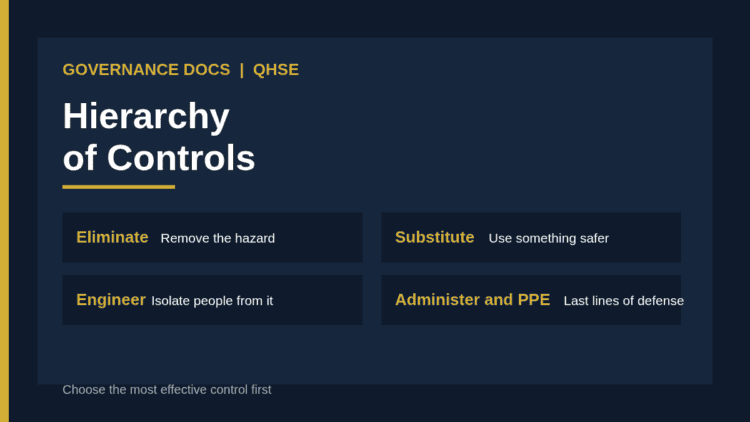
Hierarchy of controls: elimination, substitution, engineering controls, administrative controls and PPE

Hierarchy of Controls: The Essential 2026 Guide to Choosing Safer Risk Controls

Governance Docs29th September 2026

How to use the hierarchy of controls: the five levels from elimination to PPE, how ISO 45001 applies…
Read More
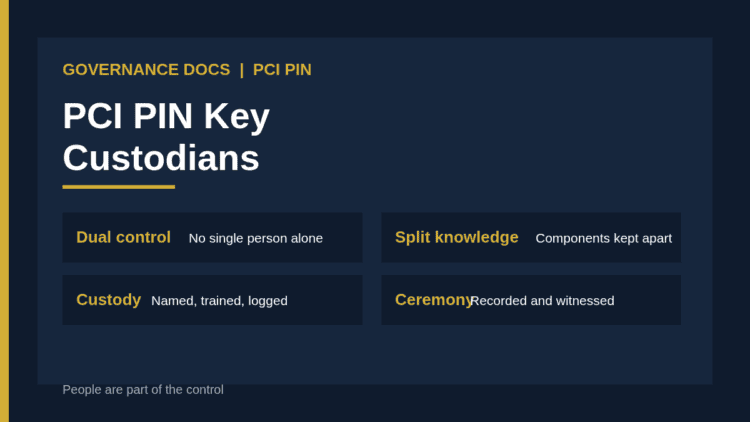
PCI PIN key custodians applying dual control and split knowledge to key components and shares

PCI PIN Key Custodians: The Essential 2026 Guide to Dual Control and Split Knowledge

Governance Docs29th September 2026

A guide to PCI PIN key custodians: their role, dual control and split knowledge in key components, key…
Read More
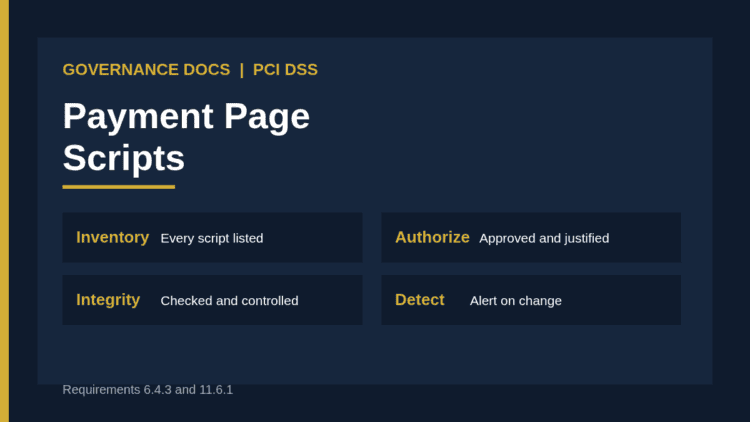
PCI DSS payment page scripts: inventory, authorization, integrity and change detection under requirements 6.4.3 and 11.6.1

PCI DSS Payment Page Scripts: The Essential 2026 Guide to Requirements 6.4.3 and 11.6.1

Governance Docs29th September 2026

How to meet PCI DSS payment page script requirements 6.4.3 and 11.6.1: script inventory, authorization, integrity, change detection,…
Read More
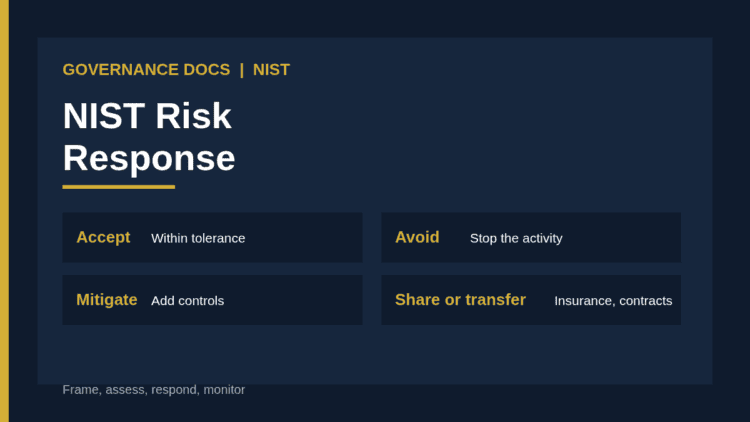
NIST risk response options: accept, avoid, mitigate, share and transfer, chosen against risk tolerance

NIST Risk Response: The Essential 2026 Guide to Accept, Avoid, Mitigate, Share or Transfer

Governance Docs29th September 2026

How NIST risk response works: the five response options in SP 800-39, how to choose between them using…
Read More
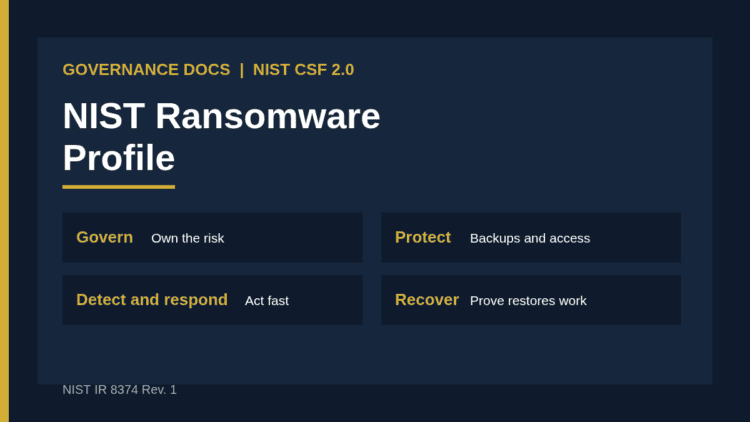
NIST ransomware profile mapping CSF 2.0 functions govern, identify, protect, detect, respond and recover to ransomware

NIST Ransomware Profile: The Essential 2026 Guide to NIST IR 8374 Rev. 1

Governance Docs29th September 2026

A practical guide to the NIST ransomware profile (IR 8374 Rev. 1): how it maps CSF 2.0 to…
Read More
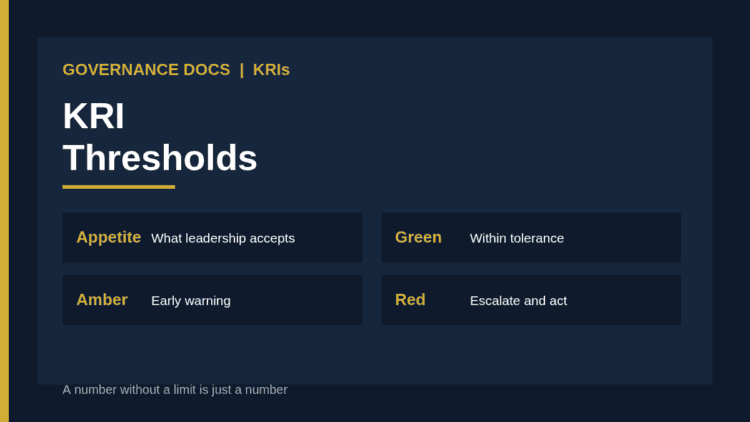
KRI thresholds: green, amber and red limits derived from risk appetite with escalation rules

KRI Thresholds: The Essential 2026 Guide to Setting Amber and Red Limits for Cyber Risk

Governance Docs29th September 2026

How to set KRI thresholds for IT and cybersecurity indicators: translating risk appetite into amber and red limits,…
Read More
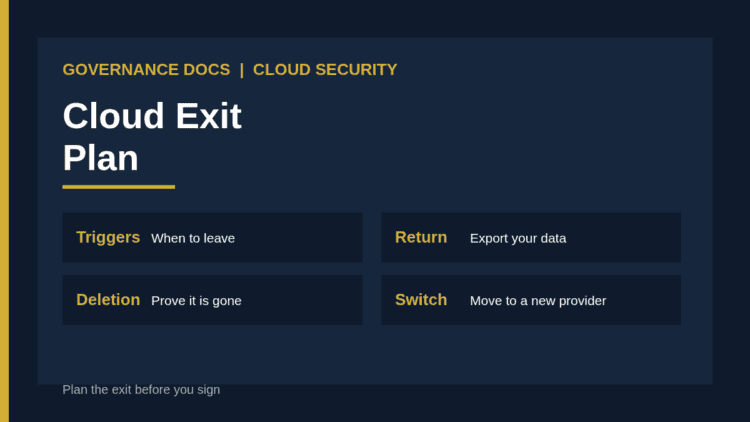
Cloud exit plan: termination triggers, data export, deletion evidence and migration to a new provider

Cloud Exit Plan: The Essential 2026 Guide to Termination, Data Return and Deletion

Governance Docs29th September 2026

How to write a cloud exit plan: termination triggers, data return and deletion, portability, EU Data Act switching…
Read More
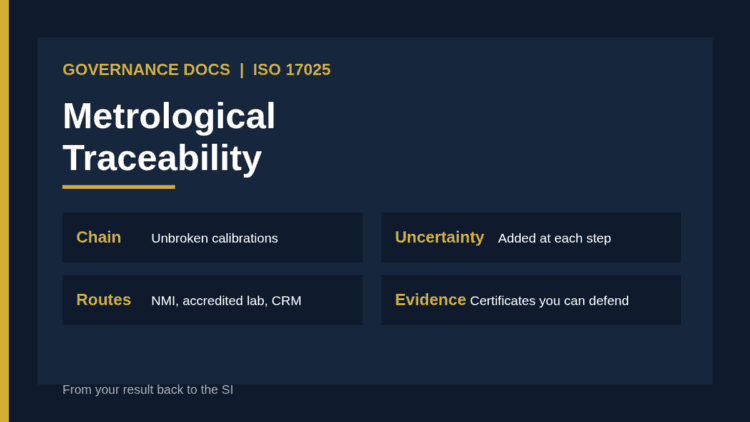
ISO 17025 metrological traceability: unbroken chain of calibrations from laboratory measurement to SI units

ISO 17025 Metrological Traceability: The Essential 2026 Guide to Clause 6.5

Governance Docs29th September 2026

How to meet ISO 17025 metrological traceability: the clause 6.5 requirements, ILAC P10 traceability routes, calibration certificate checks…
Read More

    ←
  • 1
  • …
  • 25
  • 26
  • 27
  • 28
  • 29
  • …
  • 100
  • →

Recent Posts

ISO 27001 remote working Annex A 6.7 diagram showing the four evidence sets: authorisation, provisioning, enforcement and attestation
ISO 27001 Remote Working: Complete A.6.7 Guide 2026

October 12, 2026

ISO 27001 configuration management requirements under Annex A 8.9 - established, documented, implemented, monitored, reviewed
ISO 27001 Configuration Management: Complete 2026 Guide

October 11, 2026

internal audit findings rating scale — Internal Audit Findings Rating Scale: Examples and Template
Internal Audit Findings Rating Scale: Examples and Template

October 11, 2026

third party topical requirement — Third Party Topical Requirement: The 2026 Audit Guide
Third Party Topical Requirement: The 2026 Audit Guide

October 11, 2026

cybersecurity topical requirement — Cybersecurity Topical Requirement: How to Audit It in 2026
Cybersecurity Topical Requirement: How to Audit It in 2026

October 11, 2026

Categories

  • Articles
  • DORA
  • GDPR
  • HIPAA
  • ISO 27001
  • ISO 42001 & AI governance
  • ISO 9001
  • Management systems
  • NIS2
  • Security frameworks
  • SOC 2
Governance DocsGovernance Docs

Reliable ISO & compliance documentation toolkits that help your business meet regulatory standards with ease.

Governance Docs LLC
1209 Mountain Road Pl NE, Suite R
Albuquerque, NM 87110, USA
info@governancedocs.com
+1 505 289 2455

Toolkits

  • ISO 27001:2022
  • GDPR
  • SOC 2
  • PCI-DSS v4.0
  • HIPAA
  • ISO 42001
  • All toolkits →

Company

  • About Us
  • Blog
  • Contact
  • FAQ
  • Which toolkit do I need?
  • Free templates
  • SoA generator
  • Assessments
  • Sample reports
  • RSS feeds

Policies

  • Privacy Policy
  • Terms & Conditions
  • Refund & Return Policy
  • Delivery Policy
  • Manage cookies
Browse by topicISO 27001ISO 42001 & AI governanceGDPRSOC 2HIPAANIS2DORAISO 9001Management systemsSecurity frameworks
© 2026 Governance Docs LLC. All rights reserved.
Secure checkoutstripeVISA