About Us Contact Blog
Governance DocsGovernance Docs
Which Toolkit?SoA GeneratorFree TemplatesSample ReportsFind the Right AssessmentRecords of Processing (ROPA)Data Privacy Impact AssessmentLegitimate Interests AssessmentTransfer Impact AssessmentPrivacy Risk AssessmentGDPR Gap AssessmentUK GDPR Gap AssessmentCCPA/CPRA Gap AssessmentISO 27701 Gap AssessmentHIPAA Gap AssessmentISO 27001 Risk AssessmentThird-Party Risk AssessmentSoA GeneratorISO 27001 Assessment Tool (Excel)ISO 27001 Gap AssessmentSOC 2 Gap AssessmentNIST CSF 2.0 Gap AssessmentNIST SP 800-53 Gap AssessmentNIST RMF Gap AssessmentCIS Controls Gap AssessmentPCI DSS 4.0 Gap AssessmentNIS2 Gap AssessmentCMMC 2.0 Gap AssessmentNIST SP 800-171 Gap AssessmentFedRAMP Gap AssessmentBSI C5 Gap AssessmentIEC 62443 Gap AssessmentSAMA CSF Gap AssessmentNCA ECC Gap AssessmentISO 20000 Gap AssessmentAI Risk AssessmentAI Impact AssessmentISO 42001 Gap AssessmentEU AI Act Gap AssessmentBusiness Impact AnalysisContinuity Risk AssessmentISO 22301 Assessment Tool (Excel)ISO 22301 Gap AssessmentDORA Gap AssessmentISO 9001 Gap AssessmentISO 13485 Gap AssessmentIATF 16949 Gap AssessmentISO 14001 Gap AssessmentISO 45001 Gap AssessmentISO 45001 Assessment Tool (Excel)HACCP Gap AssessmentEnterprise Risk AssessmentISO 31000 Gap AssessmentData Governance Gap AssessmentProject Management Gap AssessmentAll Gap AssessmentsISO 27001 Internal AuditISO 42001 Internal AuditAboutBlogContactMy AccountCart
Browse Toolkits
Governance Docs
  • Browse All Toolkits
  • Information Security & Cybersecurity
  • Data Privacy & Protection
  • Governance, Risk & Compliance
  • Quality Management
  • Health, Safety & Environment
  • AI Governance

My Account

CART

No products in the cart.

Category: Articles

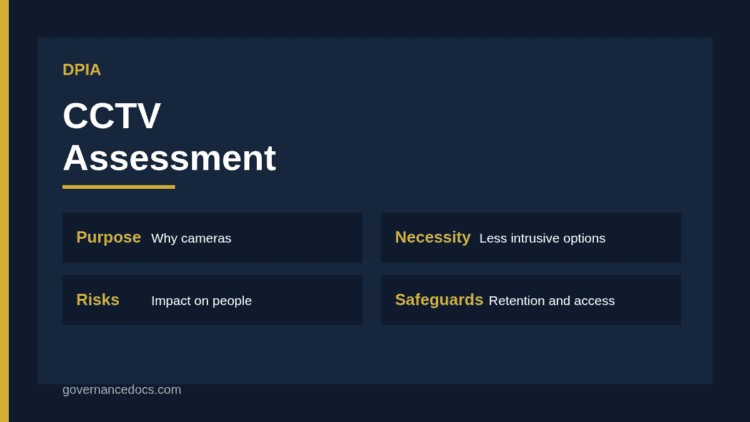
DPIA for CCTV steps from purpose and necessity to risks, safeguards and sign-off

DPIA for CCTV Guide 2026: When and How to Assess

Governance Docs30th September 2026

When a DPIA for CCTV is required, what to include, how to judge necessity, retention, signage, access and…
Read More
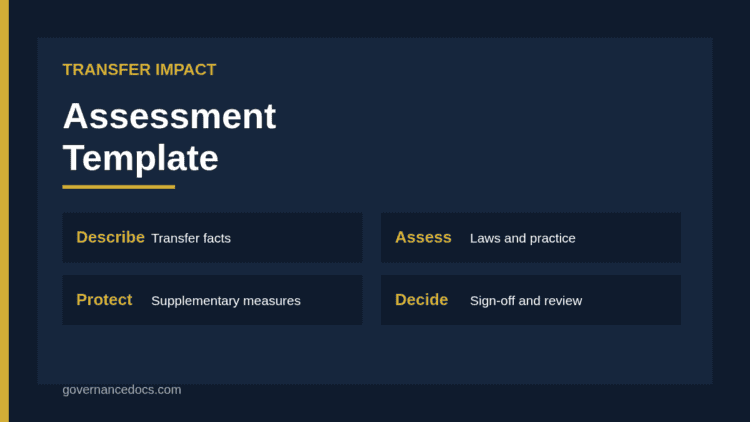
Transfer impact assessment template sections from transfer description to conclusion and review

Transfer Impact Assessment Template Guide 2026

Governance Docs30th September 2026

What a transfer impact assessment template should contain: transfer description, transfer tool, third-country law analysis, supplementary measures, sign-off…
Read More
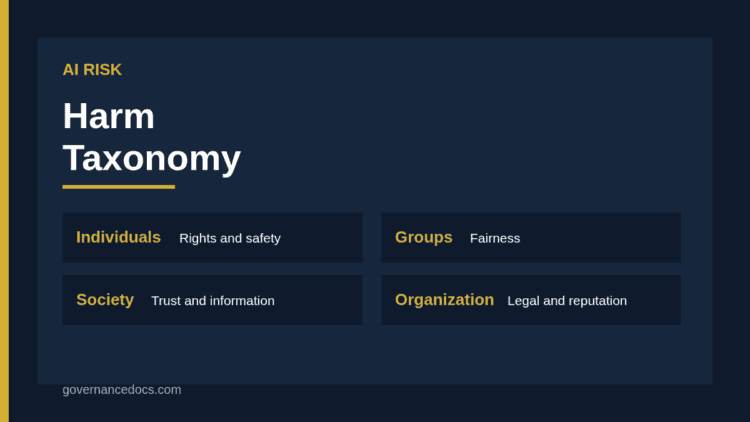
AI harm taxonomy chart grouping harms to individuals, groups, organizations and society

AI Harm Taxonomy Guide 2026: Categories and Use

Governance Docs30th September 2026

What an AI harm taxonomy is, which categories to include, how it links to AI risk assessment, scoring…
Read More
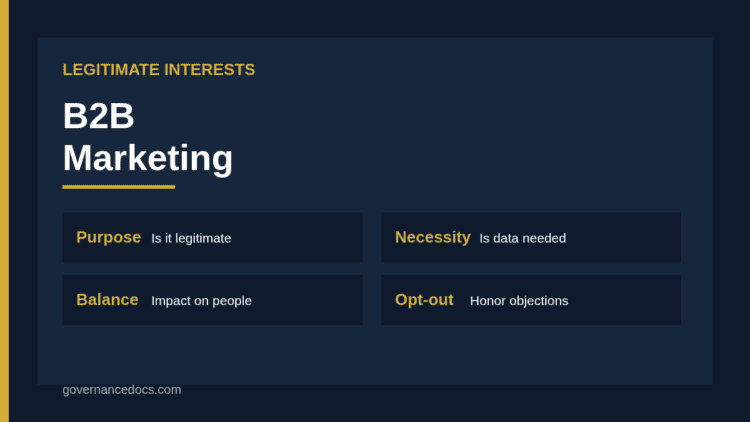
Legitimate interests for B2B marketing three-part test of purpose necessity and balancing

Legitimate Interests for B2B Marketing Guide 2026

Governance Docs30th September 2026

When legitimate interests for B2B marketing works under GDPR: the three-part test, ePrivacy limits, sole traders, objections, notices…
Read More
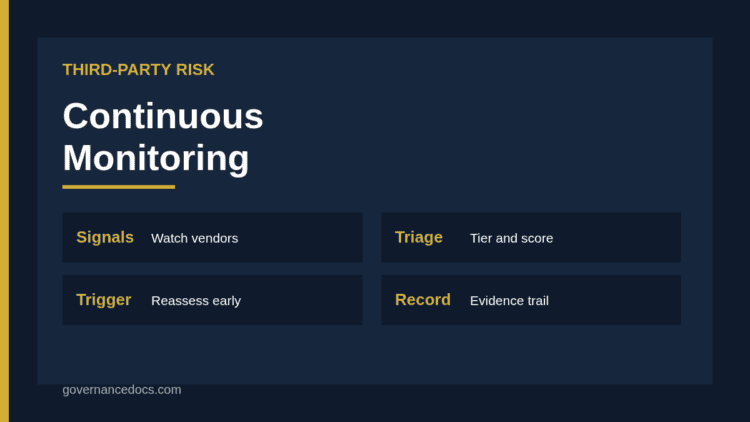
Third-party continuous monitoring dashboard showing vendor risk signals, triggers and reassessment actions

Third-Party Continuous Monitoring Guide 2026

Governance Docs30th September 2026

How to set up third-party continuous monitoring: which signals to watch, how to tier vendors, when to trigger…
Read More
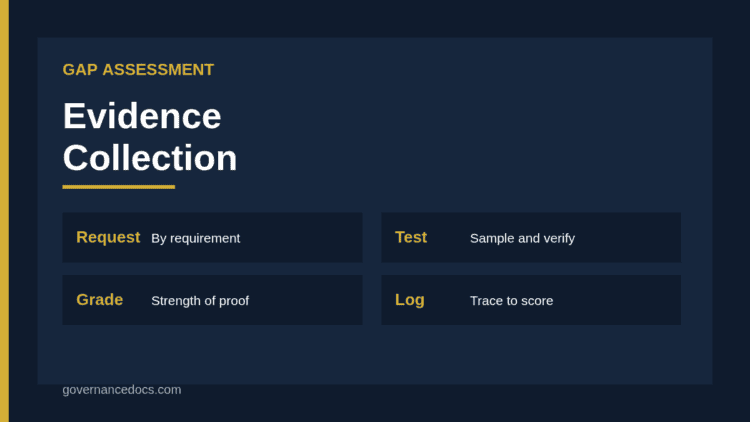
Gap assessment evidence log linking requirements to documents interviews and system samples

Gap Assessment Evidence Guide 2026: What to Collect

Governance Docs30th September 2026

What gap assessment evidence to collect, how to test it, how to grade its strength and how to…
Read More
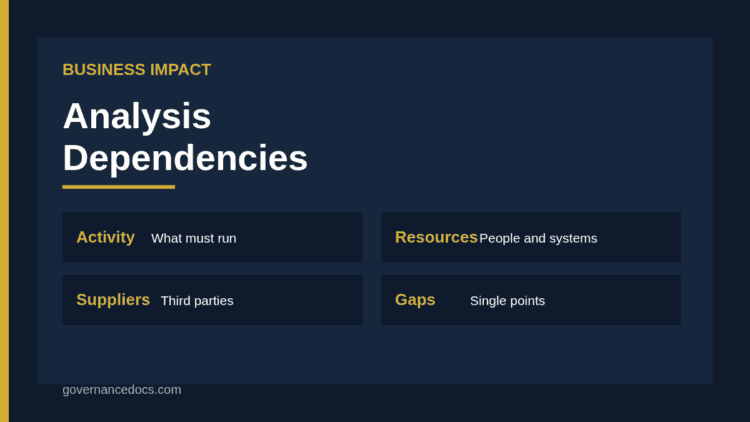
Business impact analysis dependencies map linking a critical activity to people systems suppliers and sites

Business Impact Analysis Dependencies Guide 2026

Governance Docs30th September 2026

How to identify and map business impact analysis dependencies: people, technology, suppliers, data and facilities, with a worked…
Read More
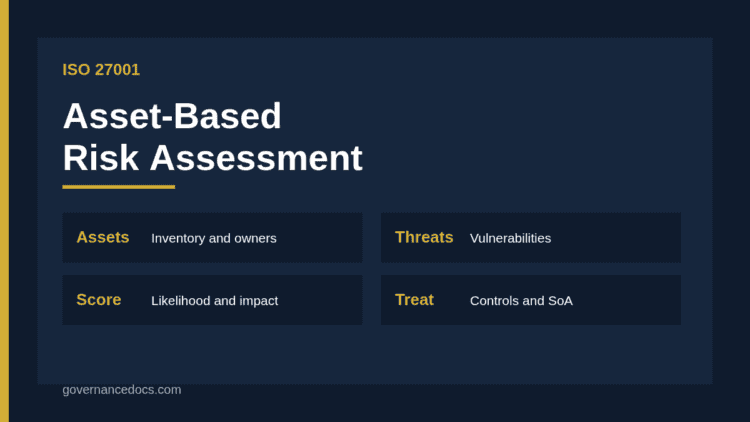
ISO 27001 asset-based risk assessment showing assets, threats and vulnerabilities feeding a risk score

ISO 27001 Asset-Based Risk Assessment Guide 2026

Governance Docs30th September 2026

How to run an ISO 27001 asset-based risk assessment: asset inventory, owners, threats, vulnerabilities, scoring, treatment and audit…
Read More
Privacy risk assessment methodology flow from data flows to scored risks and treatment

Privacy Risk Assessment Methodology Guide 2026

Governance Docs30th September 2026

How to build a privacy risk assessment methodology: scope, harm categories, likelihood and impact scales, scoring, treatment and…
Read More
Business continuity threat assessment matrix of natural technological and human threats

Business Continuity Threat Assessment Guide 2026

Governance Docs30th September 2026

How to run a business continuity threat assessment: threat categories, sources, likelihood and impact rating, scenario selection and…
Read More
Emerging risk identification funnel from horizon scanning to risk register

Emerging Risk Identification: A Practical Process 2026

Governance Docs30th September 2026

How to run emerging risk identification: horizon scanning, sources, triage criteria, scenario analysis, ownership and how to report…
Read More
AI model drift risk chart showing performance decaying over time against thresholds

AI Model Drift Risk: Monitoring and Response 2026

Governance Docs30th September 2026

How to assess and manage AI model drift risk: data drift, concept drift and performance decay, monitoring metrics,…
Read More

    ←
  • 1
  • …
  • 24
  • 25
  • 26
  • 27
  • 28
  • …
  • 106
  • →

Recent Posts

ISO 14001 surveillance audit infographic showing the cycle years, audit time, eight review areas and the 2029 transition deadline
ISO 14001 Surveillance Audit: The Complete 2026 Guide

November 3, 2026

ISO 27001 toolkit contents shown as three layers: clause 4 to 10 records, 93 Annex A controls and supporting registers
ISO 27001 Toolkit: What a Complete One Contains (2026)

November 2, 2026

ISO 9001 recertification audit three-year cycle showing surveillance in years 1 and 2 and recertification in year 3
ISO 9001 Recertification Audit: The Complete 2026 Guide

November 1, 2026

ISO 9001 surveillance audit: eight required review areas, the 12-month window and the 2029 transition deadline
ISO 9001 Surveillance Audit: The Complete 2026 Guide

October 31, 2026

ISO 27001 software installation under Annex A 8.19: production systems and end-user endpoints
ISO 27001 Software Installation: Essential A.8.19 Guide 2026

October 31, 2026

Categories

  • Articles
  • DORA
  • GDPR
  • HIPAA
  • ISO 27001
  • ISO 42001 & AI governance
  • ISO 9001
  • Management systems
  • NIS2
  • Security frameworks
  • SOC 2
Governance DocsGovernance Docs

Reliable ISO & compliance documentation toolkits that help your business meet regulatory standards with ease.

Governance Docs LLC
1209 Mountain Road Pl NE, Suite R
Albuquerque, NM 87110, USA
[email protected]
+1 505 289 2455

Toolkits

  • ISO 27001:2022
  • GDPR
  • SOC 2
  • PCI-DSS v4.0
  • HIPAA
  • ISO 42001
  • All toolkits →

Company

  • About Us
  • Blog
  • Contact
  • FAQ
  • Which toolkit do I need?
  • Request a custom toolkit
  • Free templates
  • SoA generator
  • Assessments
  • Sample reports
  • RSS feeds

Policies

  • Privacy Policy
  • Terms & Conditions
  • Refund & Return Policy
  • Delivery Policy
  • Manage cookies
Browse by topicISO 27001ISO 42001 & AI governanceGDPRSOC 2HIPAANIS2DORAISO 9001Management systemsSecurity frameworks
© 2026 Governance Docs LLC. All rights reserved.
Secure checkoutstripeVISA