About Us Contact Blog
Governance DocsGovernance Docs
Which Toolkit?SoA GeneratorFree TemplatesSample ReportsFind the Right AssessmentRecords of Processing (ROPA)Data Privacy Impact AssessmentLegitimate Interests AssessmentTransfer Impact AssessmentPrivacy Risk AssessmentGDPR Gap AssessmentUK GDPR Gap AssessmentCCPA/CPRA Gap AssessmentISO 27701 Gap AssessmentHIPAA Gap AssessmentISO 27001 Risk AssessmentThird-Party Risk AssessmentSoA GeneratorISO 27001 Assessment Tool (Excel)ISO 27001 Gap AssessmentSOC 2 Gap AssessmentNIST CSF 2.0 Gap AssessmentNIST SP 800-53 Gap AssessmentNIST RMF Gap AssessmentCIS Controls Gap AssessmentPCI DSS 4.0 Gap AssessmentNIS2 Gap AssessmentCMMC 2.0 Gap AssessmentNIST SP 800-171 Gap AssessmentFedRAMP Gap AssessmentBSI C5 Gap AssessmentIEC 62443 Gap AssessmentSAMA CSF Gap AssessmentNCA ECC Gap AssessmentISO 20000 Gap AssessmentAI Risk AssessmentAI Impact AssessmentISO 42001 Gap AssessmentEU AI Act Gap AssessmentBusiness Impact AnalysisContinuity Risk AssessmentISO 22301 Assessment Tool (Excel)ISO 22301 Gap AssessmentDORA Gap AssessmentISO 9001 Gap AssessmentISO 13485 Gap AssessmentIATF 16949 Gap AssessmentISO 14001 Gap AssessmentISO 45001 Gap AssessmentISO 45001 Assessment Tool (Excel)HACCP Gap AssessmentEnterprise Risk AssessmentISO 31000 Gap AssessmentData Governance Gap AssessmentProject Management Gap AssessmentAll Gap AssessmentsISO 27001 Internal AuditISO 42001 Internal AuditAboutBlogContactMy AccountCart
Browse Toolkits
Governance Docs
  • Browse All Toolkits
  • Information Security & Cybersecurity
  • Data Privacy & Protection
  • Governance, Risk & Compliance
  • Quality Management
  • Health, Safety & Environment
  • AI Governance

My Account

CART

No products in the cart.

Category: Articles

Third-party risk reporting dashboard with vendor tiers, open findings, overdue assessments and concentration

Third-Party Risk Reporting Guide 2026

Governance Docs30th September 2026

How to design third-party risk reporting: audiences, key metrics, tiering views, concentration, findings, exceptions and how to present…
Read More
AI bias testing workflow from defining groups to metrics, thresholds, remediation and monitoring

AI Bias Testing Guide 2026: Methods and Records

Governance Docs30th September 2026

How to run AI bias testing: define groups and outcomes, choose metrics, build test data, set thresholds, investigate…
Read More
Risk culture assessment showing leadership, communication, accountability and incentives around a risk management program

Risk Culture Guide 2026: Assess and Improve It

Governance Docs30th September 2026

What risk culture is, why it decides whether enterprise risk management works, how to assess it with surveys…
Read More
RoPA joint controllers diagram of two organizations sharing purposes and means with an Article 26 arrangement

RoPA and Joint Controllers Guide 2026

Governance Docs30th September 2026

How to handle RoPA joint controllers: when controllership is joint, what Article 26 requires, what to record in…
Read More
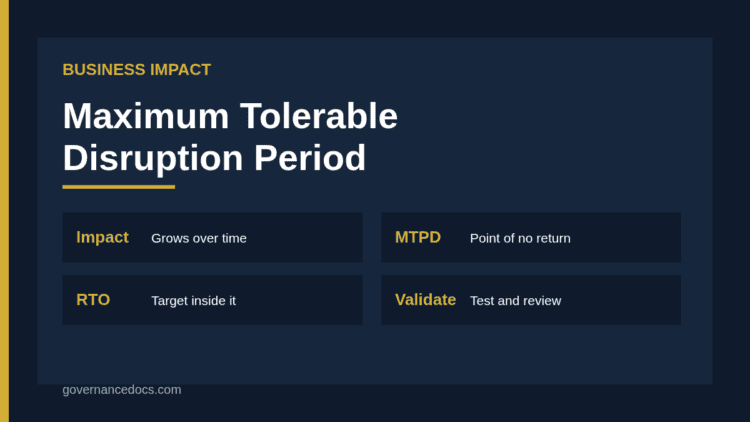
Maximum tolerable period of disruption timeline showing impact growth, RTO and MTPD for a critical activity

Maximum Tolerable Period of Disruption Guide 2026

Governance Docs30th September 2026

What the maximum tolerable period of disruption is, how it differs from RTO and RPO, how to set…
Read More
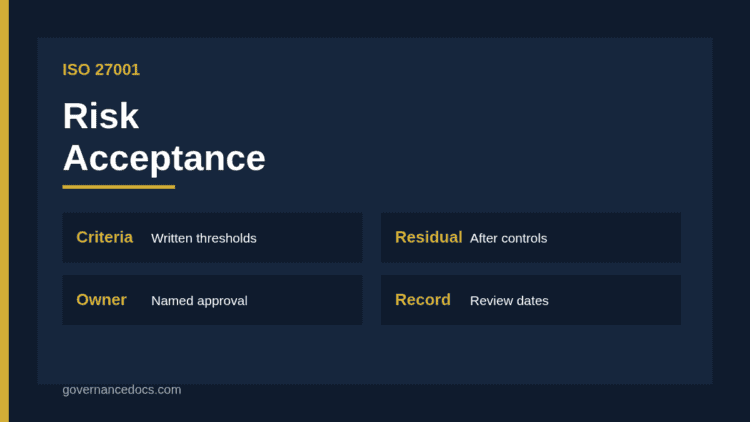
ISO 27001 risk acceptance flow from residual risk rating through criteria check to owner approval and record

ISO 27001 Risk Acceptance Criteria Guide 2026

Governance Docs30th September 2026

How ISO 27001 risk acceptance works: criteria under clause 6.1.2, owner approval under 6.1.3, thresholds, exceptions, records, review…
Read More
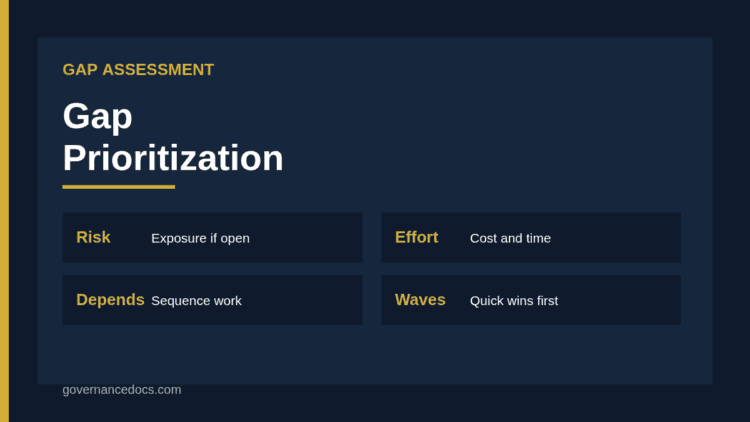
Gap assessment prioritization matrix comparing risk reduction against effort with quick wins and major projects

Gap Assessment Prioritization Guide 2026

Governance Docs30th September 2026

How to prioritize gaps after an assessment: risk, regulatory exposure, effort, dependencies, quick wins, scoring, sequencing into waves…
Read More
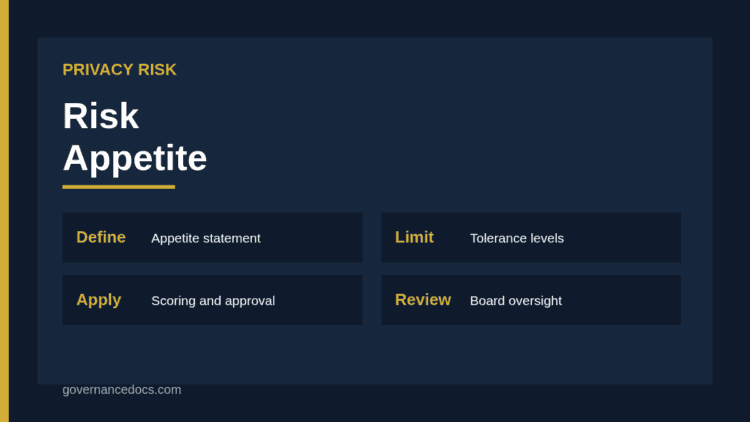
Privacy risk appetite scale with acceptable, tolerable and unacceptable levels for privacy risks

Privacy Risk Appetite Guide 2026: Setting Limits

Governance Docs30th September 2026

How to set privacy risk appetite: appetite versus tolerance, choosing categories, writing statements, linking to scoring and approvals,…
Read More
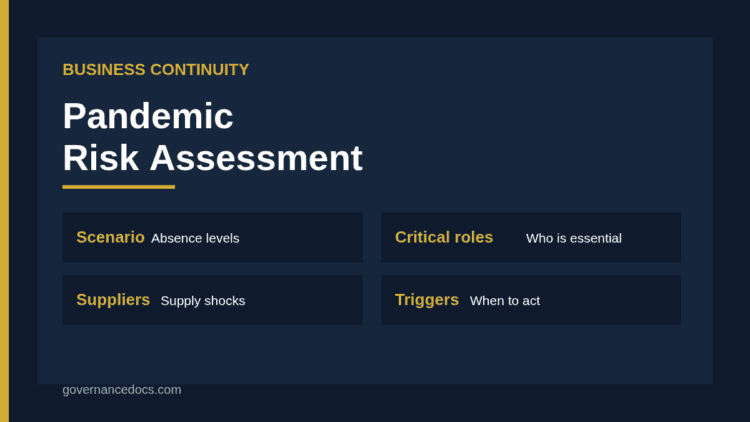
Pandemic risk assessment scenario table showing absence levels supplier disruption and response triggers

Pandemic Risk Assessment Guide 2026 for Business Continuity

Governance Docs30th September 2026

How to run a pandemic risk assessment for business continuity: scenarios, absence assumptions, critical roles, suppliers, remote work,…
Read More
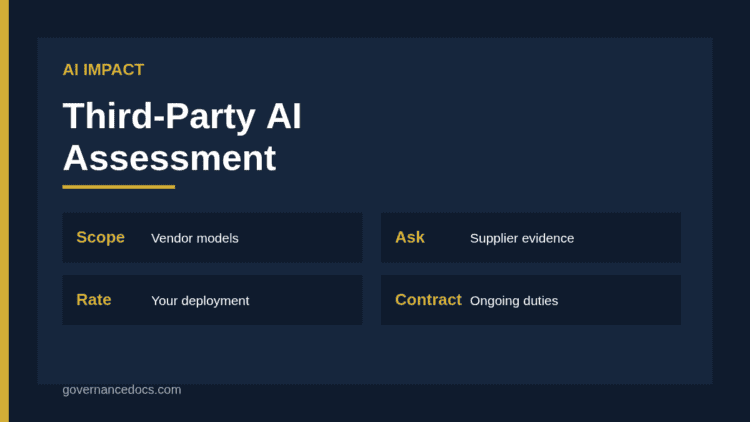
Third-party AI impact assessment showing vendor documentation, deployment context, impact rating and contract controls

Third-Party AI Impact Assessment Guide 2026

Governance Docs30th September 2026

How to run a third-party AI impact assessment for vendor models: scoping, supplier questions, evidence gaps, contract terms,…
Read More
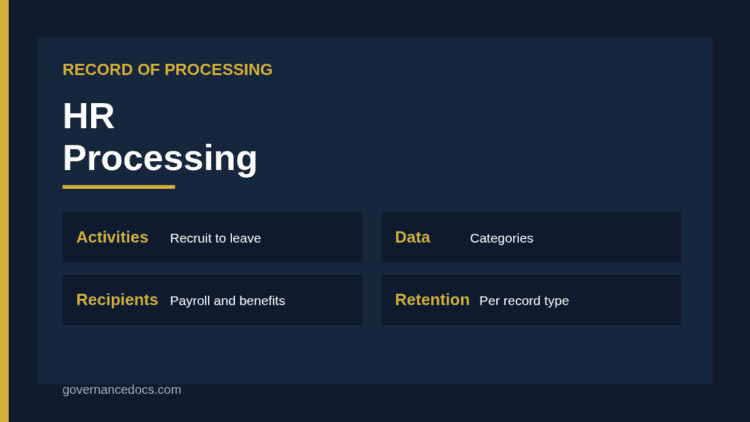
RoPA for HR processing table of recruitment payroll benefits and absence with purposes and retention

RoPA for HR Processing Guide 2026

Governance Docs30th September 2026

How to build a RoPA for HR processing: recruitment, payroll, benefits, absence, monitoring, special category data, retention, recipients…
Read More
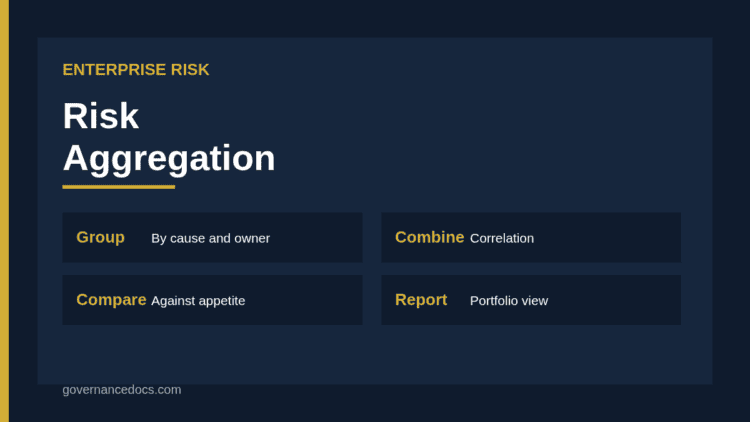
Risk aggregation diagram combining individual risks by category, cause and business unit into a portfolio view

Risk Aggregation Guide 2026: Portfolio View of Risk

Governance Docs30th September 2026

How risk aggregation works in enterprise risk management: grouping methods, common causes, correlation, simple scoring and quantitative options,…
Read More

    ←
  • 1
  • …
  • 23
  • 24
  • 25
  • 26
  • 27
  • …
  • 106
  • →

Recent Posts

ISO 14001 surveillance audit infographic showing the cycle years, audit time, eight review areas and the 2029 transition deadline
ISO 14001 Surveillance Audit: The Complete 2026 Guide

November 3, 2026

ISO 27001 toolkit contents shown as three layers: clause 4 to 10 records, 93 Annex A controls and supporting registers
ISO 27001 Toolkit: What a Complete One Contains (2026)

November 2, 2026

ISO 9001 recertification audit three-year cycle showing surveillance in years 1 and 2 and recertification in year 3
ISO 9001 Recertification Audit: The Complete 2026 Guide

November 1, 2026

ISO 9001 surveillance audit: eight required review areas, the 12-month window and the 2029 transition deadline
ISO 9001 Surveillance Audit: The Complete 2026 Guide

October 31, 2026

ISO 27001 software installation under Annex A 8.19: production systems and end-user endpoints
ISO 27001 Software Installation: Essential A.8.19 Guide 2026

October 31, 2026

Categories

  • Articles
  • DORA
  • GDPR
  • HIPAA
  • ISO 27001
  • ISO 42001 & AI governance
  • ISO 9001
  • Management systems
  • NIS2
  • Security frameworks
  • SOC 2
Governance DocsGovernance Docs

Reliable ISO & compliance documentation toolkits that help your business meet regulatory standards with ease.

Governance Docs LLC
1209 Mountain Road Pl NE, Suite R
Albuquerque, NM 87110, USA
[email protected]
+1 505 289 2455

Toolkits

  • ISO 27001:2022
  • GDPR
  • SOC 2
  • PCI-DSS v4.0
  • HIPAA
  • ISO 42001
  • All toolkits →

Company

  • About Us
  • Blog
  • Contact
  • FAQ
  • Which toolkit do I need?
  • Request a custom toolkit
  • Free templates
  • SoA generator
  • Assessments
  • Sample reports
  • RSS feeds

Policies

  • Privacy Policy
  • Terms & Conditions
  • Refund & Return Policy
  • Delivery Policy
  • Manage cookies
Browse by topicISO 27001ISO 42001 & AI governanceGDPRSOC 2HIPAANIS2DORAISO 9001Management systemsSecurity frameworks
© 2026 Governance Docs LLC. All rights reserved.
Secure checkoutstripeVISA