About Us Contact Blog
Governance DocsGovernance Docs
Which Toolkit?SoA GeneratorFree TemplatesSample ReportsFind the Right AssessmentRecords of Processing (ROPA)Data Privacy Impact AssessmentLegitimate Interests AssessmentTransfer Impact AssessmentPrivacy Risk AssessmentGDPR Gap AssessmentUK GDPR Gap AssessmentCCPA/CPRA Gap AssessmentISO 27701 Gap AssessmentHIPAA Gap AssessmentISO 27001 Risk AssessmentThird-Party Risk AssessmentSoA GeneratorISO 27001 Assessment Tool (Excel)ISO 27001 Gap AssessmentSOC 2 Gap AssessmentNIST CSF 2.0 Gap AssessmentNIST SP 800-53 Gap AssessmentNIST RMF Gap AssessmentCIS Controls Gap AssessmentPCI DSS 4.0 Gap AssessmentNIS2 Gap AssessmentCMMC 2.0 Gap AssessmentNIST SP 800-171 Gap AssessmentFedRAMP Gap AssessmentBSI C5 Gap AssessmentIEC 62443 Gap AssessmentSAMA CSF Gap AssessmentNCA ECC Gap AssessmentISO 20000 Gap AssessmentAI Risk AssessmentAI Impact AssessmentISO 42001 Gap AssessmentEU AI Act Gap AssessmentBusiness Impact AnalysisContinuity Risk AssessmentISO 22301 Assessment Tool (Excel)ISO 22301 Gap AssessmentDORA Gap AssessmentISO 9001 Gap AssessmentISO 13485 Gap AssessmentIATF 16949 Gap AssessmentISO 14001 Gap AssessmentISO 45001 Gap AssessmentISO 45001 Assessment Tool (Excel)HACCP Gap AssessmentEnterprise Risk AssessmentISO 31000 Gap AssessmentData Governance Gap AssessmentProject Management Gap AssessmentAll Gap AssessmentsISO 27001 Internal AuditISO 42001 Internal AuditAboutBlogContactMy AccountCart
FOX v.2.4.9
Browse Toolkits
Governance Docs
  • Browse All Toolkits
  • Information Security & Cybersecurity
  • Data Privacy & Protection
  • Governance, Risk & Compliance
  • Quality Management
  • Health, Safety & Environment
  • AI Governance

My Account

CART

No products in the cart.

Day: September 30, 2026

AMLR business-wide risk assessment infographic

AMLR Business-Wide Risk Assessment: The Essential 2026 Guide Under Article 10

Governance Docs30th September 2026

How to prepare an AMLR business-wide risk assessment under Article 10 of Regulation (EU) 2024/1624, with inputs, structure,…
Read More
NIST CSF profile template infographic

NIST CSF Profile Template: The Essential 2026 Guide to Current and Target Profiles

Governance Docs30th September 2026

Build a NIST CSF profile template for 2026: columns, scoring, current and target profiles across the six functions,…
Read More
QMSR management review infographic

QMSR Management Review: The Essential 2026 Guide to Records FDA Can Now Inspect

Governance Docs30th September 2026

QMSR management review for 2026: inputs, outputs, records and how to prepare now that management review, internal audit…
Read More
Compliance consulting proposal template infographic

Compliance Consulting Proposal Template: The Essential 2026 Guide to Winning Fixed-Scope Work

Governance Docs30th September 2026

A compliance consulting proposal template for 2026: ten sections from objectives and scope to fees and change control,…
Read More
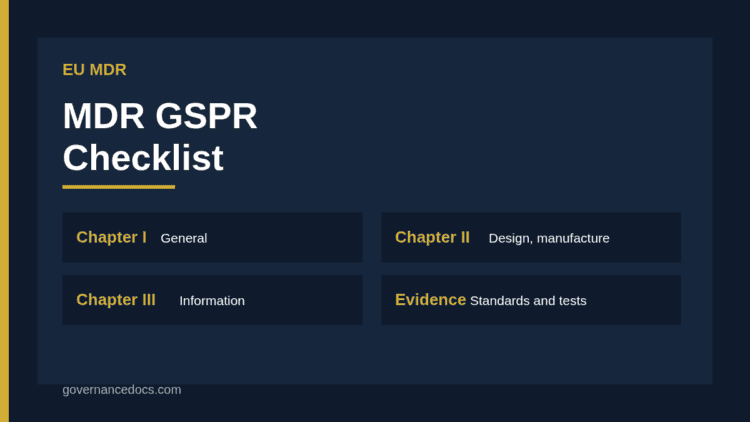
MDR GSPR checklist infographic

MDR GSPR Checklist: The Essential 2026 Guide to Annex I Safety and Performance Requirements

Governance Docs30th September 2026

Build an MDR GSPR checklist in 2026: the structure of Annex I, what to record for each requirement,…
Read More
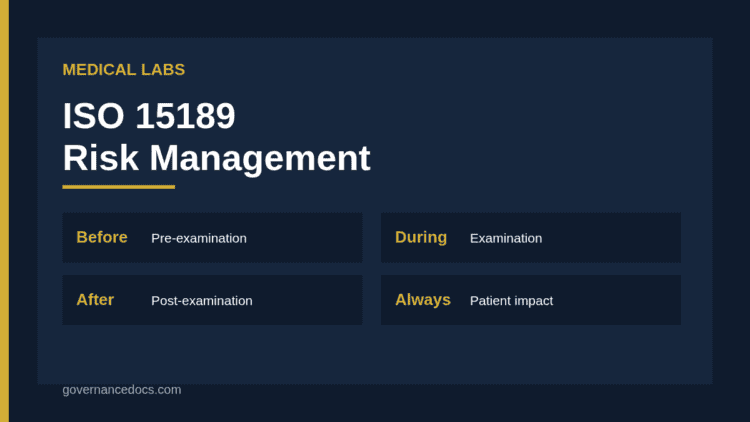
ISO 15189 risk management infographic

ISO 15189 Risk Management: The Essential 2026 Guide for Medical Laboratories

Governance Docs30th September 2026

ISO 15189 risk management explained for 2026: patient-focused risk assessment across pre-examination, examination and post-examination, with a worked…
Read More
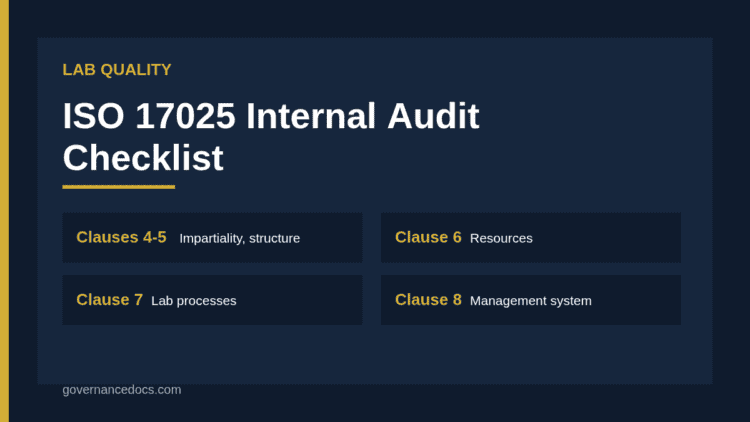
ISO 17025 internal audit checklist infographic

ISO 17025 Internal Audit Checklist: The Essential 2026 Guide for Testing and Calibration Labs

Governance Docs30th September 2026

An ISO 17025 internal audit checklist for 2026, organized by clauses 4 to 8 with evidence to sample,…
Read More
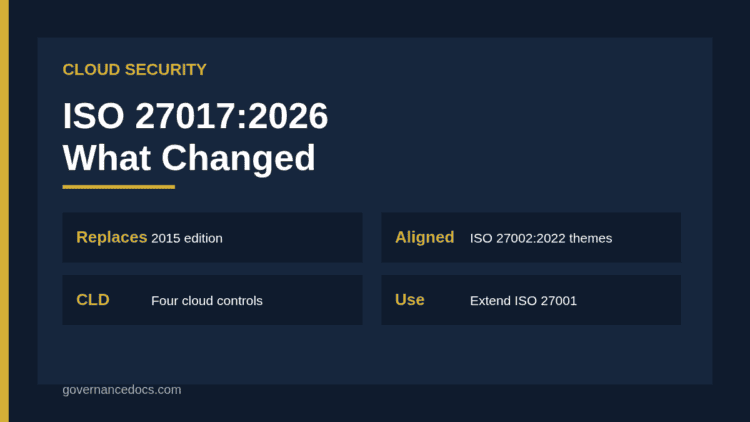
ISO 27017:2026 changes infographic

ISO 27017:2026 Changes: The Essential Guide to the New Cloud Security Standard

Governance Docs30th September 2026

ISO 27017:2026 was published in July 2026 and replaces the 2015 edition. What changed, the four CLD controls…
Read More
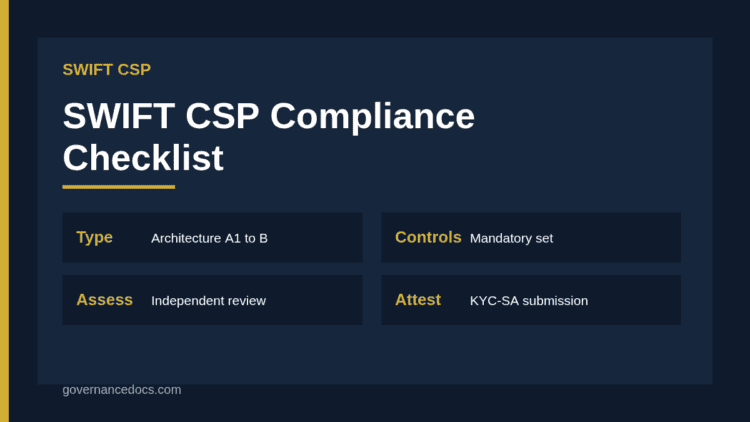
SWIFT CSP compliance checklist infographic

SWIFT CSP Compliance Checklist: The Essential 2026 Guide to CSCF v2026 Controls

Governance Docs30th September 2026

A SWIFT CSP compliance checklist for 2026: confirm your architecture type, apply mandatory CSCF v2026 controls, collect evidence…
Read More
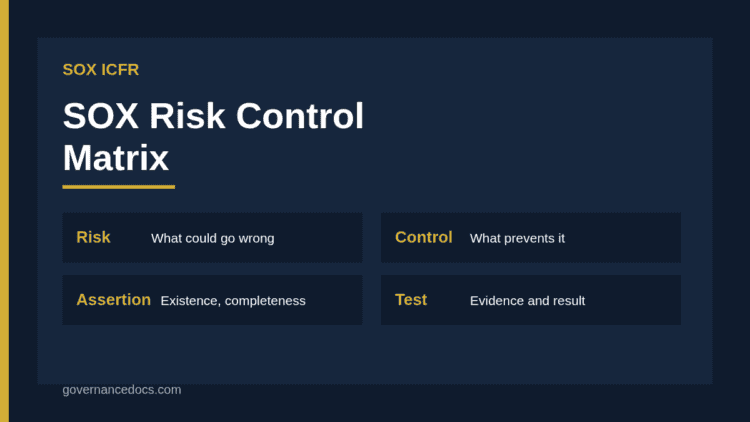
SOX risk control matrix infographic

SOX Risk Control Matrix: The Essential 2026 Guide to Building an RCM Auditors Accept

Governance Docs30th September 2026

Build a SOX risk control matrix in 2026: required columns, risk and control wording, key control selection, assertions…
Read More
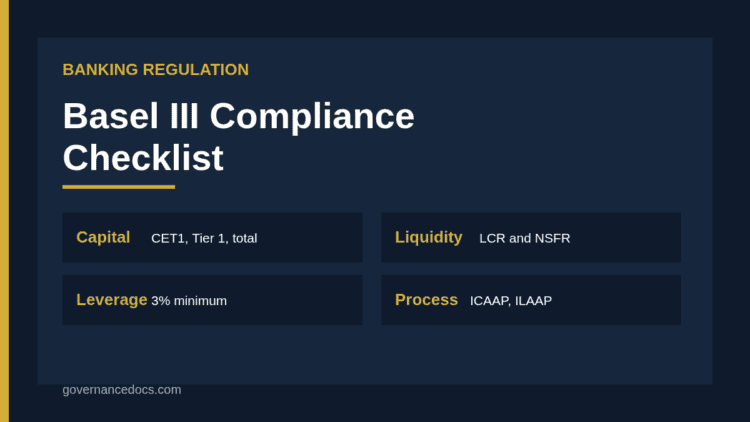
Basel III compliance checklist infographic

Basel III Compliance Checklist: The Essential 2026 Guide to Capital, Liquidity and Leverage

Governance Docs30th September 2026

A Basel III compliance checklist for 2026 covering capital ratios, buffers, leverage, LCR, NSFR, ICAAP, ILAAP, disclosure and…
Read More
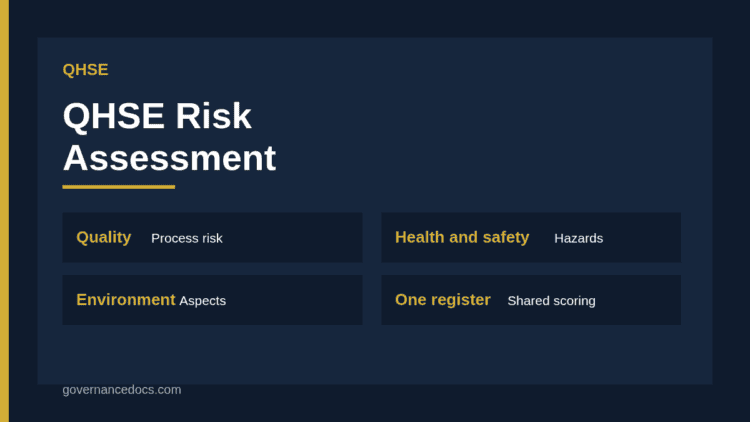
QHSE risk assessment infographic

QHSE Risk Assessment: The Essential 2026 Guide to One Method for Quality, Safety and Environment

Governance Docs30th September 2026

A QHSE risk assessment method for 2026: one process and register covering quality risks, workplace hazards and environmental…
Read More

  • 1
  • 2
  • 3
  • …
  • 12
  • →

Recent Posts

ISO 27001 password policy requirements under Annex A 5.17 and A.8.5, with NIST, PCI DSS and Cyber Essentials length baselines compared
ISO 27001 Password Policy: Complete 2026 Requirements Guide

October 20, 2026

ISO 27001 intellectual property rights: the six categories in Annex A control 5.32
ISO 27001 Intellectual Property Rights: Complete 2026 Guide

October 20, 2026

ISO 27001 independent review under Annex A 5.35 compared with the clause 9.2 internal audit and clause 9.3 management review
ISO 27001 Independent Review: Complete A.5.35 Guide 2026

October 19, 2026

ISO 27001 acceptable use policy requirements under Annex A control A.5.10
ISO 27001 Acceptable Use Policy: Complete 2026 Guide

October 19, 2026

ISO 27001 network security controls A.8.20, A.8.21 and A.8.22 compared
ISO 27001 Network Security: Complete A.8.20–8.22 Guide 2026

October 18, 2026

Categories

  • Articles
  • DORA
  • GDPR
  • HIPAA
  • ISO 27001
  • ISO 42001 & AI governance
  • ISO 9001
  • Management systems
  • NIS2
  • Security frameworks
  • SOC 2
Governance DocsGovernance Docs

Reliable ISO & compliance documentation toolkits that help your business meet regulatory standards with ease.

Governance Docs LLC
1209 Mountain Road Pl NE, Suite R
Albuquerque, NM 87110, USA
[email protected]
+1 505 289 2455

Toolkits

  • ISO 27001:2022
  • GDPR
  • SOC 2
  • PCI-DSS v4.0
  • HIPAA
  • ISO 42001
  • All toolkits →

Company

  • About Us
  • Blog
  • Contact
  • FAQ
  • Which toolkit do I need?
  • Free templates
  • SoA generator
  • Assessments
  • Sample reports
  • RSS feeds

Policies

  • Privacy Policy
  • Terms & Conditions
  • Refund & Return Policy
  • Delivery Policy
  • Manage cookies
Browse by topicISO 27001ISO 42001 & AI governanceGDPRSOC 2HIPAANIS2DORAISO 9001Management systemsSecurity frameworks
© 2026 Governance Docs LLC. All rights reserved.
Secure checkoutstripeVISA