

Business Classification Scheme: A Practical 2026 Guide
How to build a business classification scheme: functions, activities and transactions, file plans, and linking classes to access…
CART
How to build a business classification scheme: functions, activities and transactions, file plans, and linking classes to access…
What a records management policy should contain under ISO 15489-1 clause 6.2: scope, mandates, responsibilities, approval, review and…
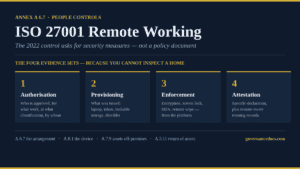
ISO 27001 remote working (Annex A 6.7) explained: why the 2022 control no longer names a policy, plus…
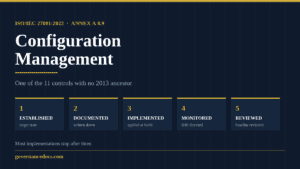
ISO 27001 configuration management (Annex A 8.9) is new in the 2022 edition. The five verbs auditors test,…
An internal audit findings rating scale that meets Standard 14.3: likelihood and impact, rating bands, priorities and engagement…
The IIA Third Party Topical Requirement explained: effective 15 September 2026, its 17 items across the third-party life…
The IIA Cybersecurity Topical Requirement explained: effective 5 February 2026, its 17 items, what to test and how…
Quality assurance and improvement program for internal audit: ongoing monitoring, self-assessment, the five-yearly external assessment and reporting.
Build a risk based internal audit plan under Standard 9.4: audit universe, annual risk assessment, required coverage areas…
Internal audit charter requirements under the 2024 IIA Standards: minimum contents, mandate, reporting lines, independence and the board’s…
IIA Topical Requirements explained: all four issued requirements, effective dates, item counts, the applicability rule and how to…
Global Internal Audit Standards explained: 5 domains, 15 principles, 52 standards, what changed from the 2017 IPPF and…
October 18, 2026
October 18, 2026
October 15, 2026
October 15, 2026
October 14, 2026