

IEC 62443-3-3: Complete 2026 Guide to 51 System Requirements
IEC 62443-3-3 in practice: the 7 foundational requirements, the 51 system requirements counted by FR, how SL-C and…
CART
IEC 62443-3-3 in practice: the 7 foundational requirements, the 51 system requirements counted by FR, how SL-C and…
A practical guide to IEC 62443-2-4 for asset owners and OT service providers: who it covers, the 2023…
What IEC 62443-2-1:2024 asks of asset owners, what changed from the 2010 edition, the evidence auditors typically expect…
What a cybersecurity requirements specification (CRS) is under IEC 62443-3-2 ZCR 6.1, what it must contain, a section-by-section…
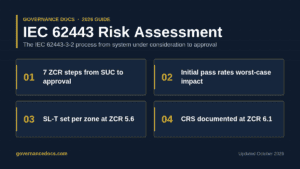
A practical guide to the IEC 62443-3-2 risk assessment: inputs, tolerable risk, the seven ZCR steps and their…
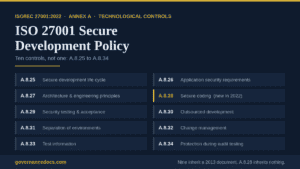
An ISO 27001 secure development policy covers ten Annex A controls, not one. What A.8.25 to A.8.34 require,…
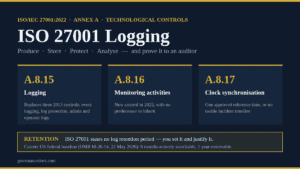
ISO 27001 logging sits in Annex A 8.15, 8.16 and 8.17. What to log, how long to keep…
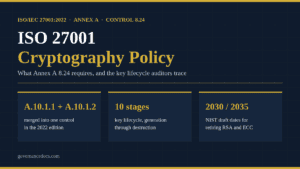
An ISO 27001 cryptography policy satisfies Annex A 8.24, which merged two 2013 controls into one. The 10…
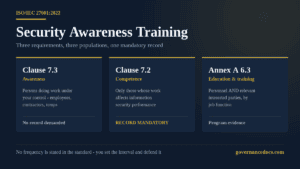
ISO 27001 security awareness training is 3 requirements, not 1: clause 7.3, clause 7.2 and Annex A 6.3.…
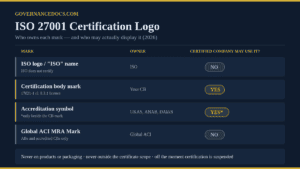
ISO 27001 certification logo rules for 2026: ISO bans its own logo outright, and ISO/IEC 17021-1 clause 8.3…
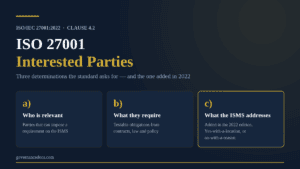
ISO 27001 interested parties under clause 4.2 – how to build a register that answers all 3 requirements,…
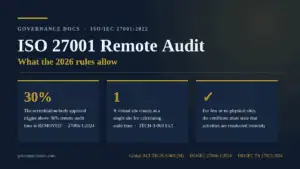
ISO 27001 remote audit rules changed in 2024: the 30% approval cap is gone, but your certificate must…
October 18, 2026
October 18, 2026
October 15, 2026
October 15, 2026
October 14, 2026