Description
At a glance: the Information Security Package is an editable Microsoft Office documentation set that brings together all 30 Governance Docs information security toolkits in one purchase. One-time price $699, instant download, licensed for internal use by one organisation. Implementing for several clients? The Consultant Package covers unlimited client engagements.
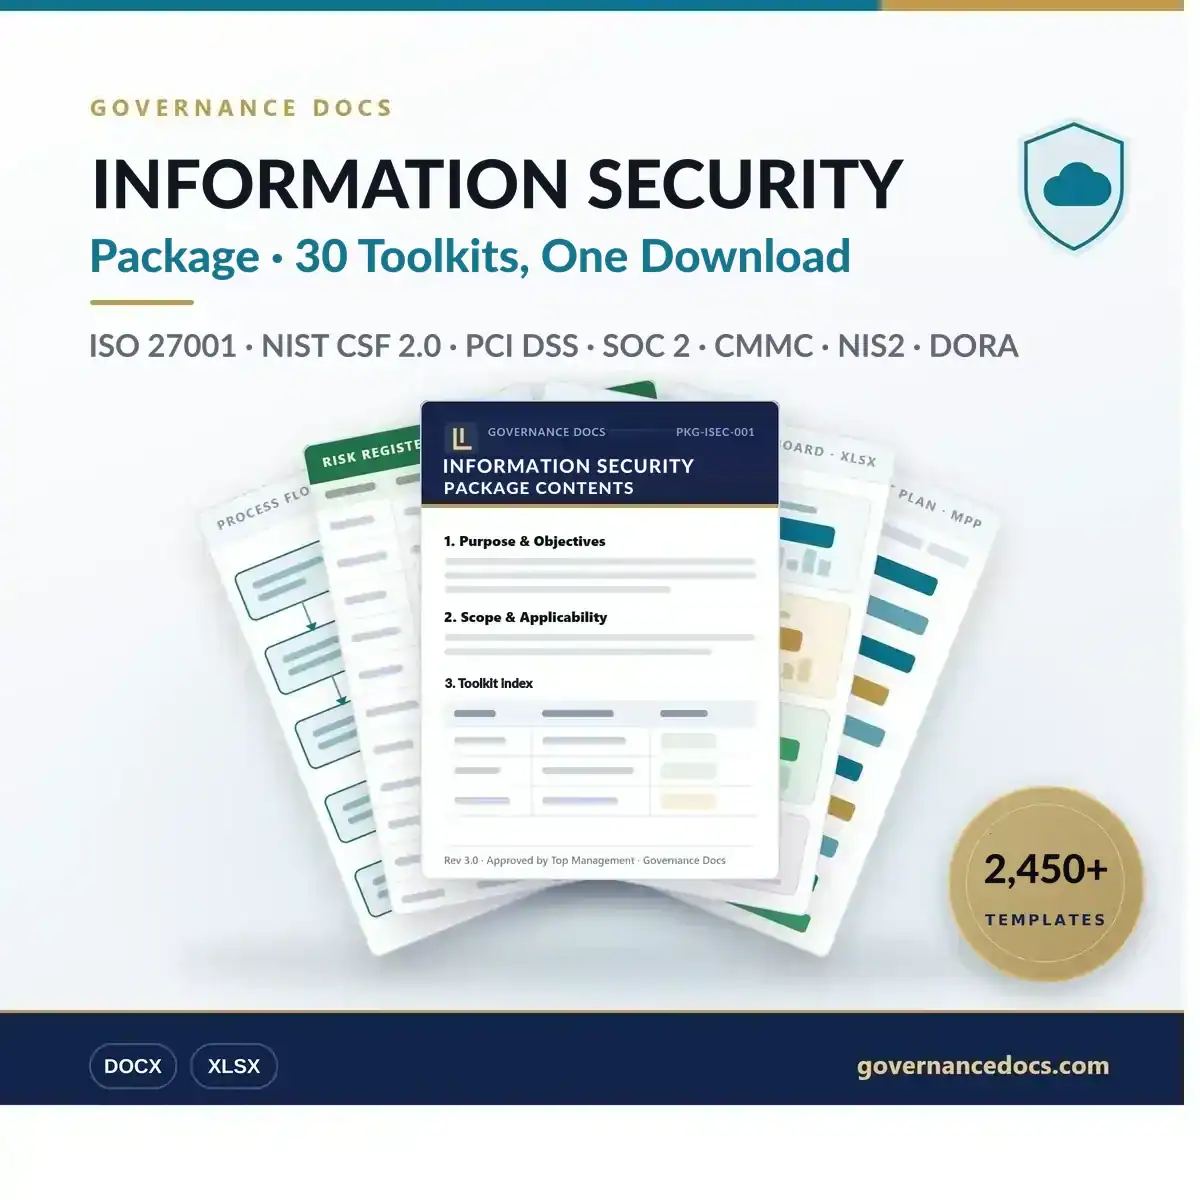
The Information Security Package gives you every Information Security toolkit we publish — 30 toolkits and 2,475 editable documents — in one purchase. Each toolkit arrives as its own download, exactly as it does when bought on its own, so you open only the one a project needs.
Bought separately, these 30 toolkits list at $2,960. The Information Security Package is $699, one time.
Who the Information Security Package is for
Security leaders who answer to several frameworks at once — an ISO 27001 certificate, a SOC 2 report, a customer questionnaire built on NIST CSF, a PCI DSS assessment — and who would rather work from one consistent document set than buy each framework as the auditor asks for it. It suits CISOs, security and compliance managers, and in-house GRC teams in a single organisation.
What the Information Security Package covers
Core security management
The foundation most programmes start from: an ISO/IEC 27001 information security management system, the NIST Cybersecurity Framework 2.0, NIST SP 800-30 risk management, the CIS Controls v8.1 safeguards, an incident response plan and playbooks built on NIST SP 800-61, and a security KPI set for board reporting.
Payments and financial-sector security
Card and payment security under PCI DSS and PCI PIN, the SWIFT Customer Security Programme for institutions on the SWIFT network, and DORA for ICT risk management, incident reporting and resilience testing in EU financial entities.
Cloud security and assurance
For cloud and SaaS providers that are asked to prove their controls: SOC 2, ISO/IEC 27017 and 27018 for cloud services and cloud privacy, CSA STAR, and the German BSI C5 criteria.
US government and defence
For contractors and cloud providers serving US agencies: CMMC, NIST SP 800-171 for controlled unclassified information, the NIST SP 800-53 control catalogue, FedRAMP, and GovRAMP (formerly StateRAMP) with TX-RAMP.
OT, critical infrastructure and product security
IEC 62443 for industrial automation and control systems, NERC CIP for the North American bulk electric system, the EU NIS2 Directive for essential and important entities, and the EU Cyber Resilience Act for products with digital elements.
Regional and sector frameworks
The Saudi NCA Essential Cybersecurity Controls and the SAMA Cyber Security Framework, UK Cyber Essentials, TISAX for the automotive supply chain, HITRUST CSF, HIPAA for US healthcare, and a Written Information Security Plan (WISP) for the FTC Safeguards Rule.
For the framework itself, see NIST Cybersecurity Framework.
Every toolkit in the Information Security Package
Click any toolkit to see its full document list on its own product page.
How the Information Security Package downloads work
- 30 separate downloads, one per toolkit, available in your account straight after checkout.
- The same files as the individual toolkits. Each download is the current version of that toolkit, so when we update a toolkit, your download delivers the update.
- Download links do not expire.
- Editable Microsoft Office files, with nothing locked or watermarked.
Information Security Package licence
The Information Security Package carries the same licence as each toolkit: you may use and adapt the documents for internal use within one organisation. The full terms are in our Terms and Conditions. If you deliver information security work for clients, the Consultant Package licenses every toolkit in the catalogue for unlimited client engagements across your firm.
Frequently asked questions
Is the Information Security Package different from buying the toolkits one by one?
The documents are identical. You get the same 30 toolkit downloads you would get by buying each one separately, for $699 instead of $2,960.
Do I get updates?
Yes. Each download serves the current version of its toolkit, so when we revise a toolkit — for a new edition of a standard, for example — the next download from your account is the updated file.
Can I use it for more than one organisation?
No. The Information Security Package is licensed to one organisation. Consultants who implement for clients need the Consultant Package.
Guides for the Information Security Package
Free articles that explain the requirements this toolkit covers.


















Reviews
There are no reviews yet