CART
No products in the cart.
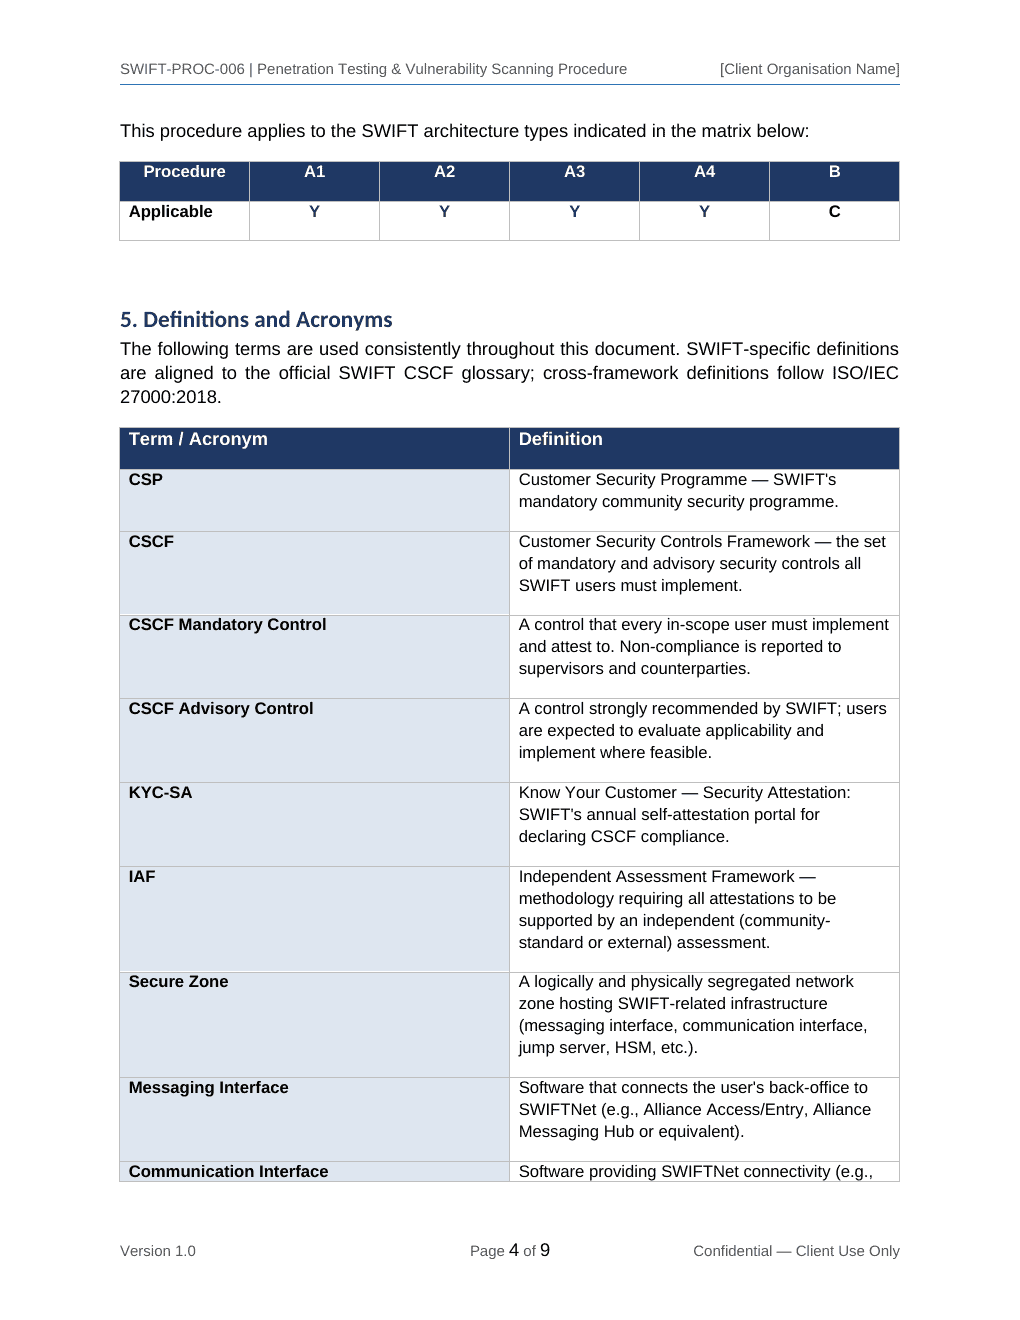
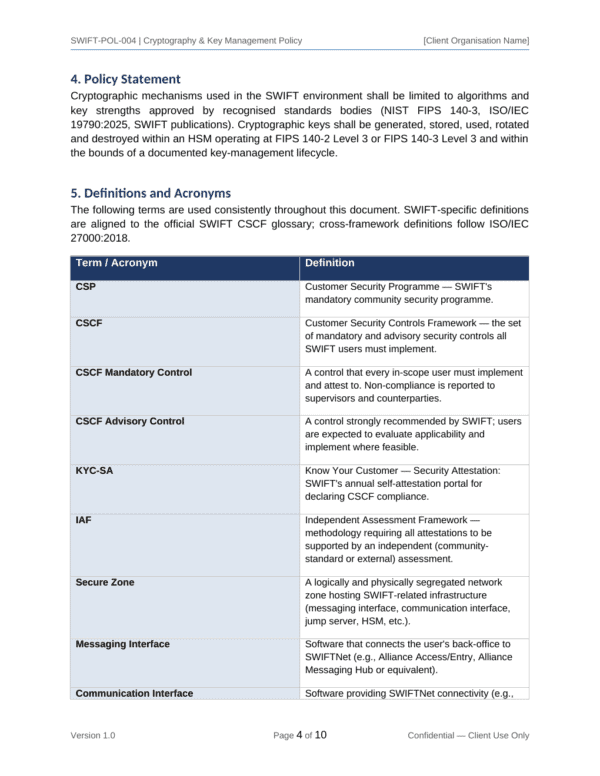
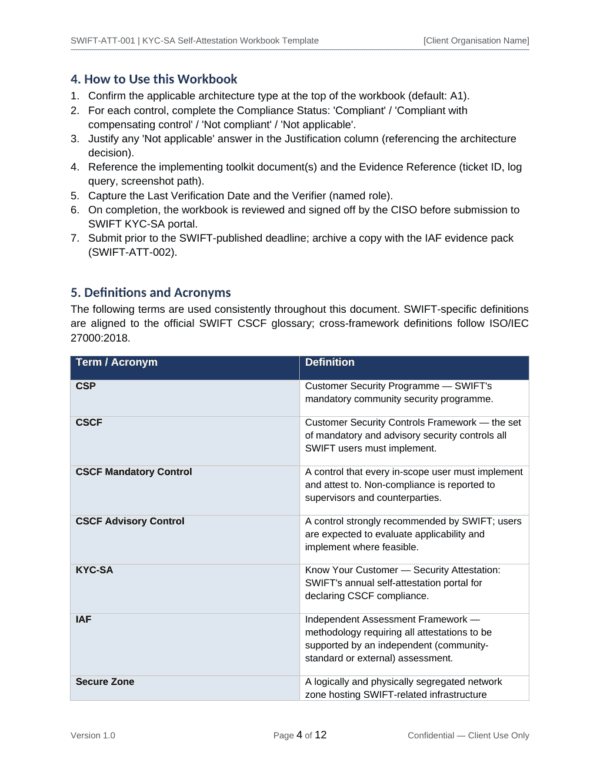
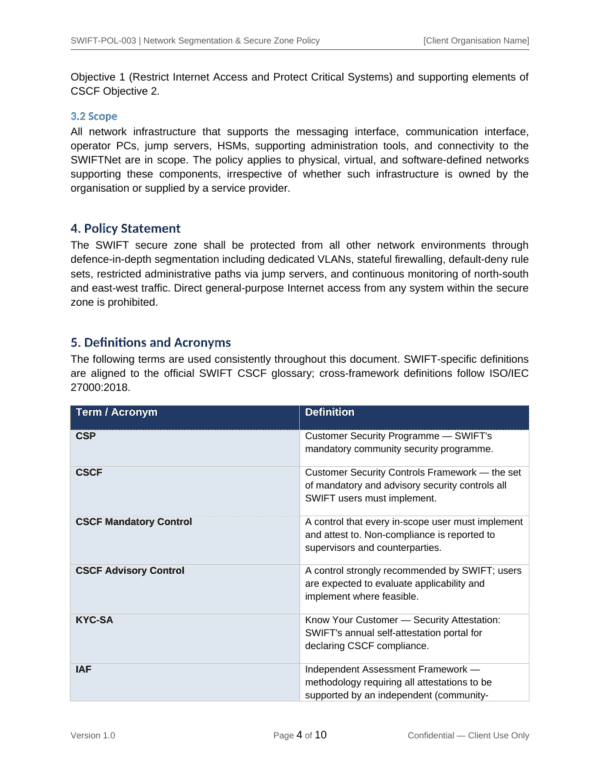
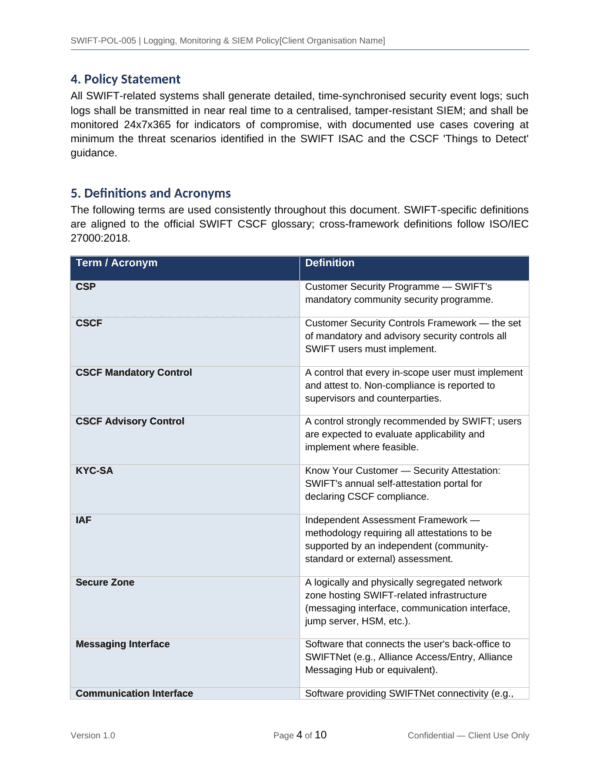
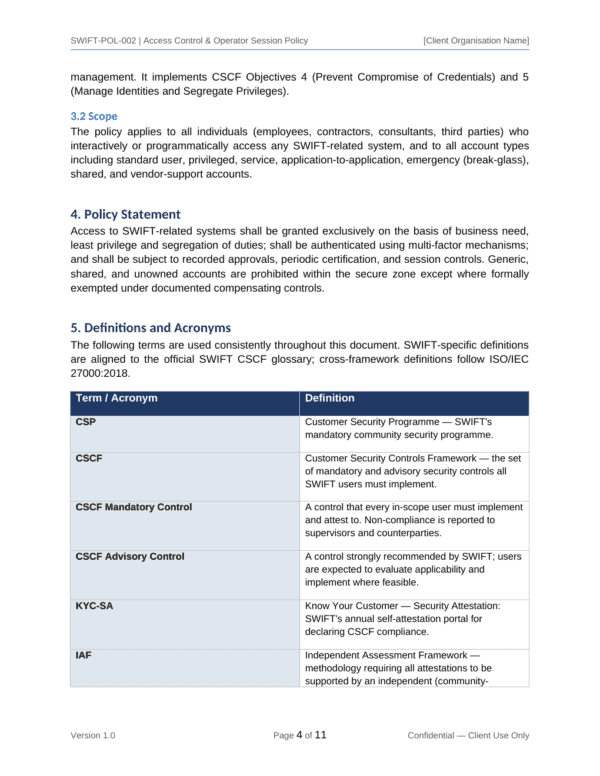
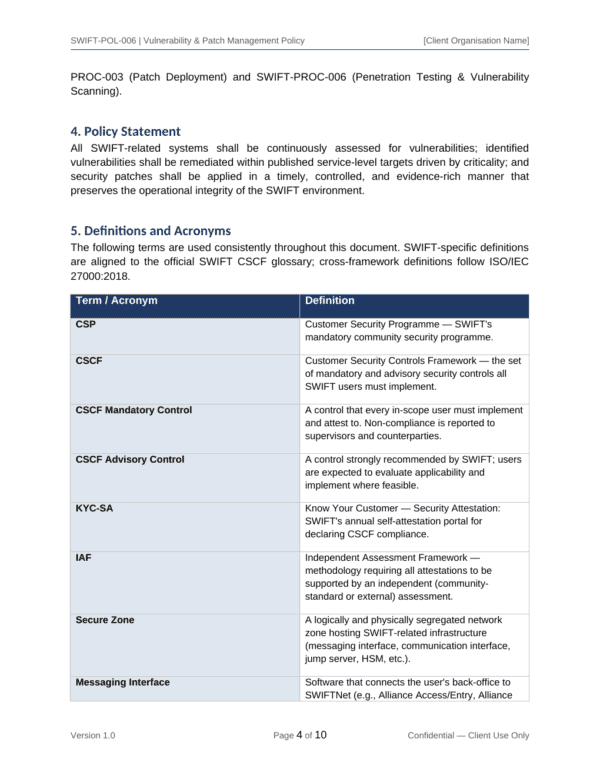
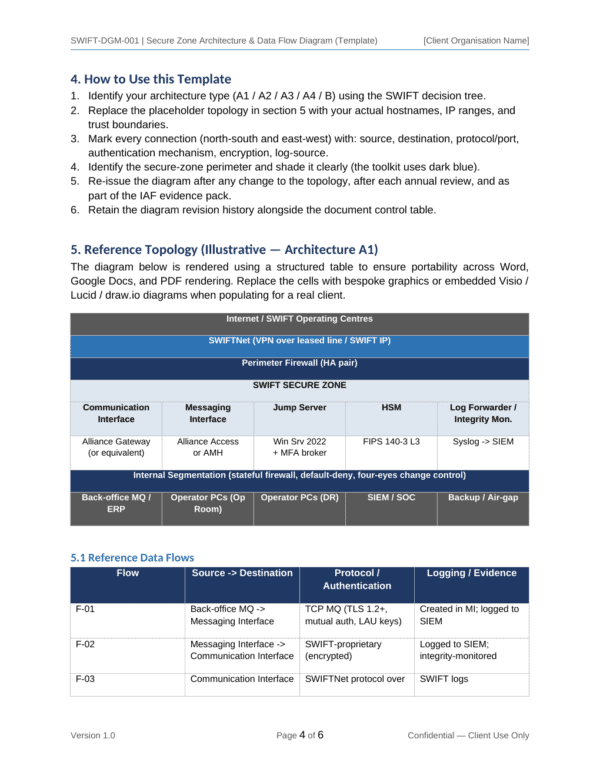
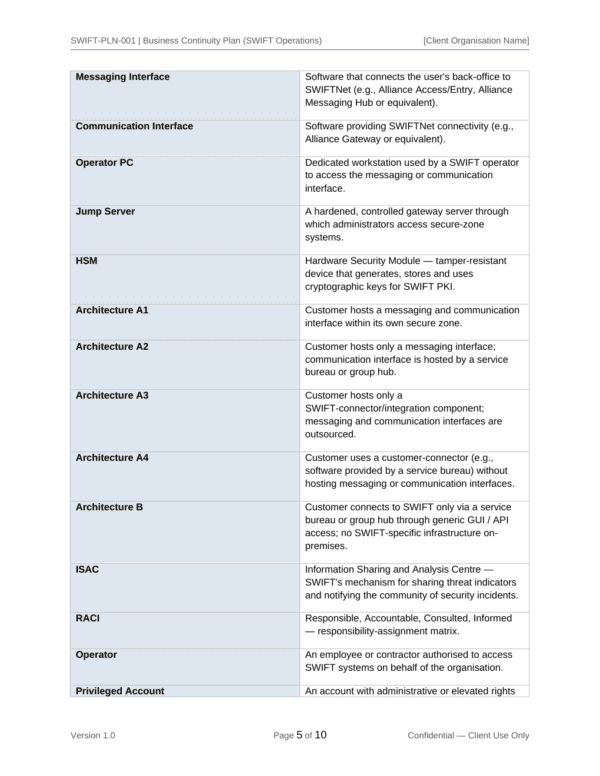
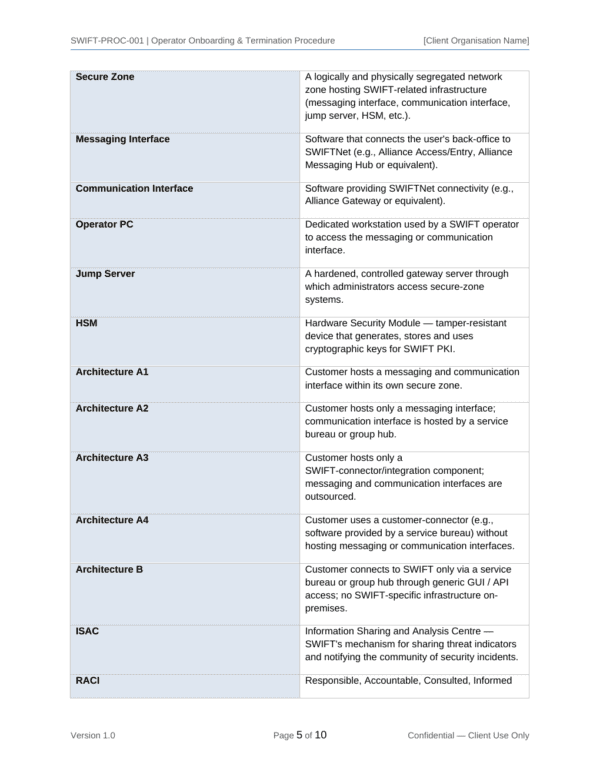
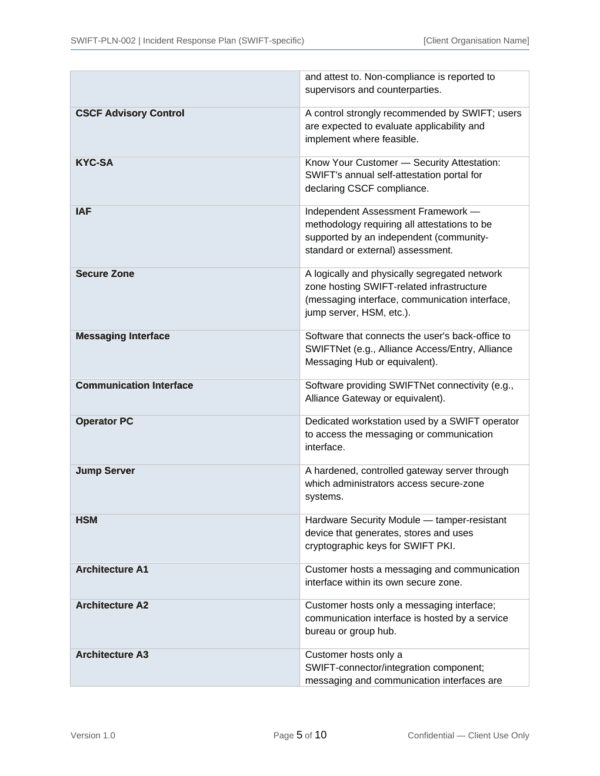
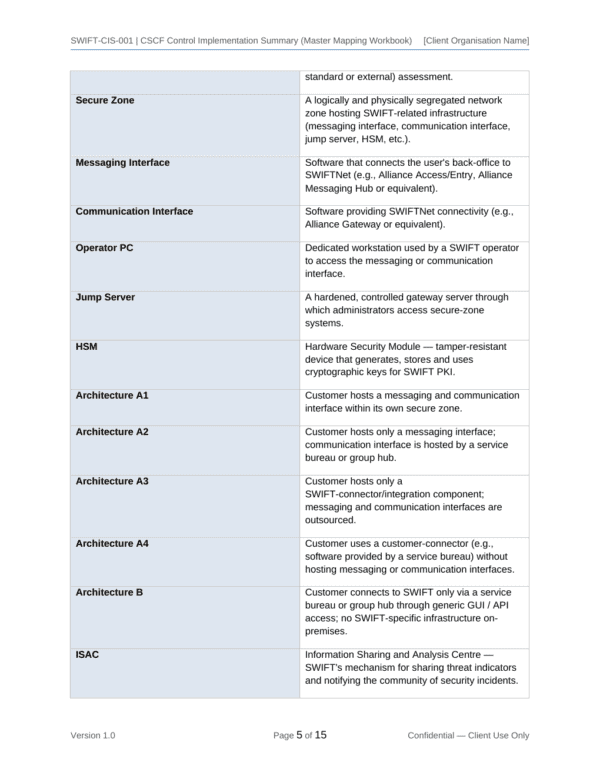
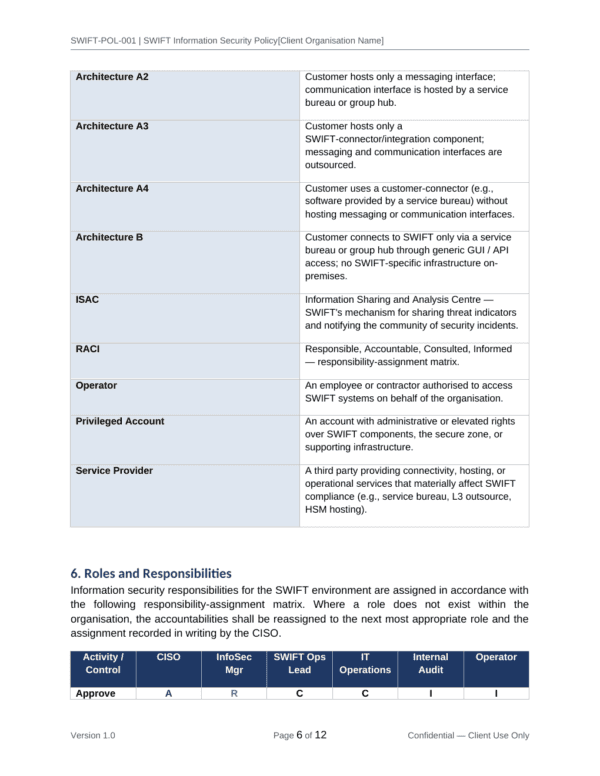
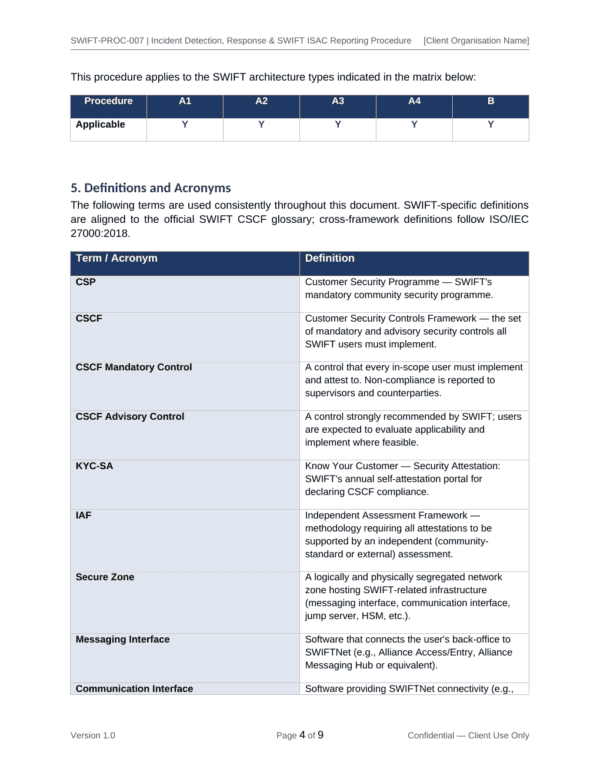
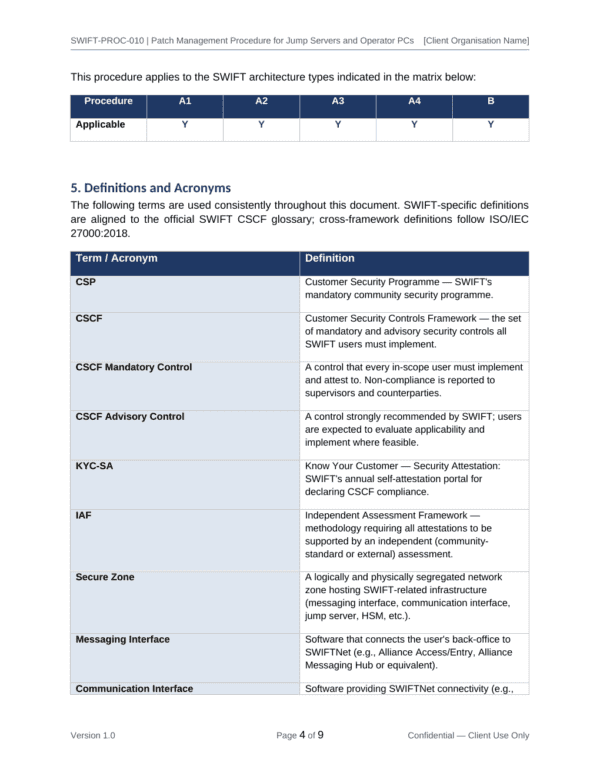
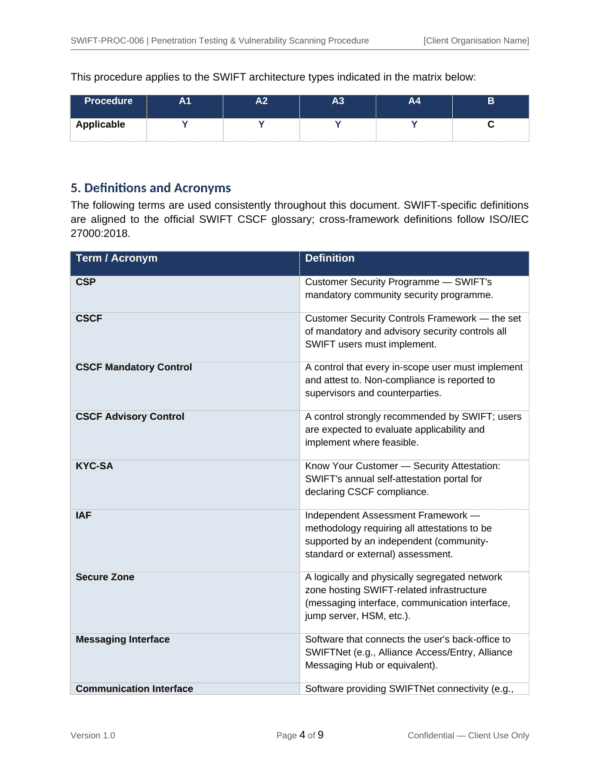
SWIFT CSP Toolkit delivers 32 ready-to-use Microsoft Office templates aligned to CSCF v2026 covering secure zone architecture, access control and operator session management, network segmentation, cryptography and key management, logging and SIEM, vulnerability and patch management, operator acceptable use, third-party security, incident response, business continuity, and continuous monitoring. Accelerate your SWIFT CSP compliance programme with a complete, audit-ready SWIFT CSP compliance documentation foundation built for swift-connected financial institutions and beyond.
$99.00
✓ In stock — instant download after checkout
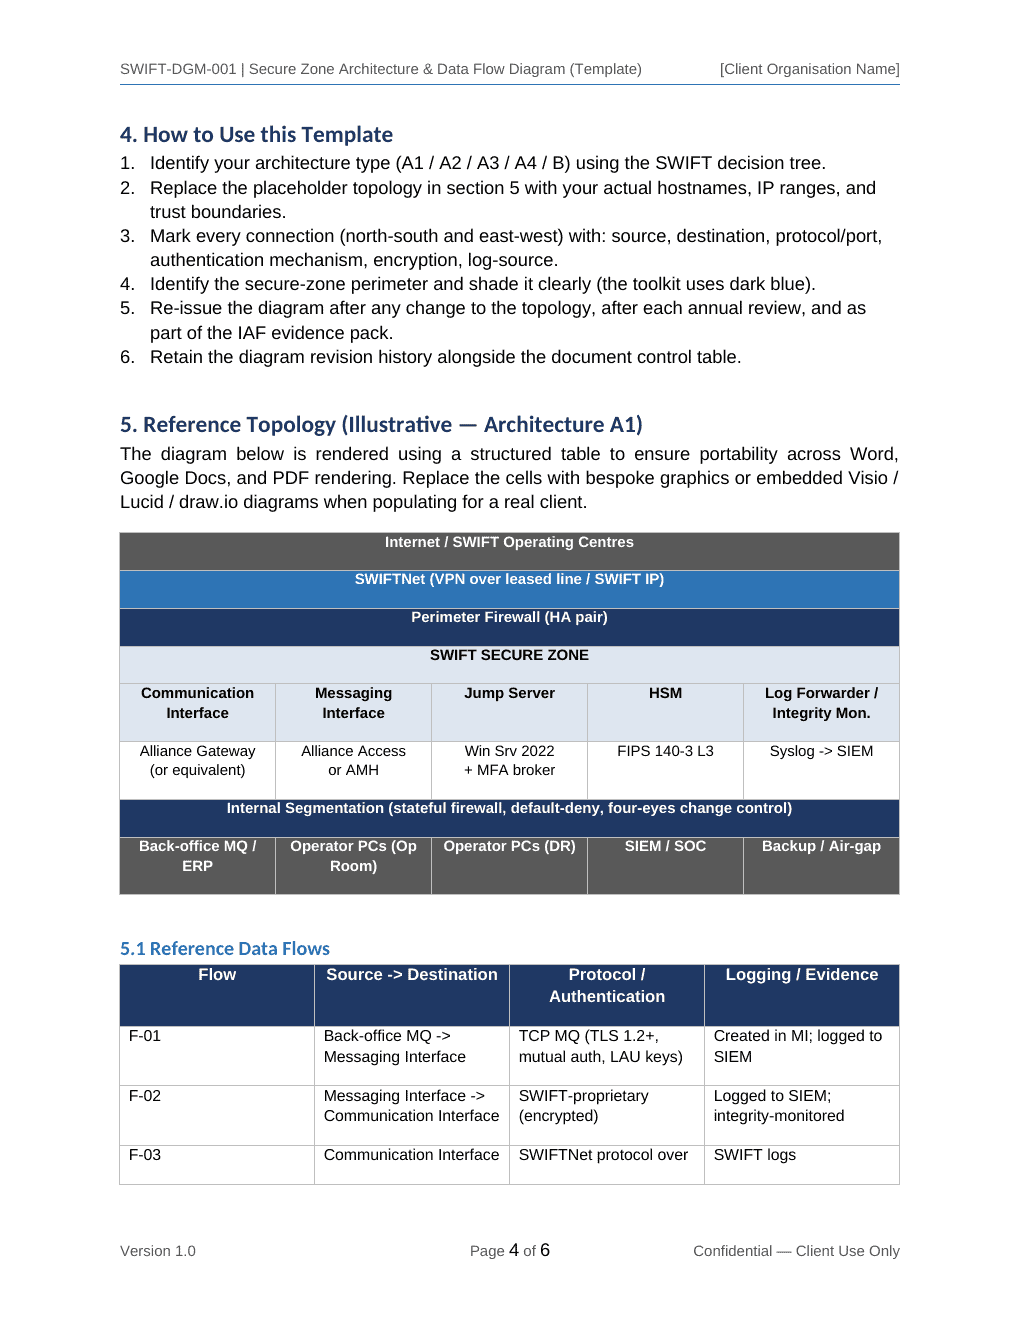
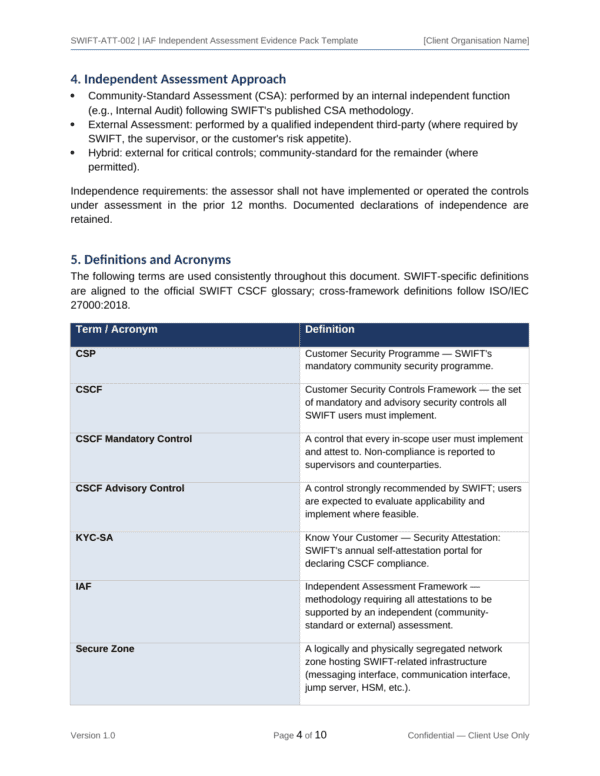
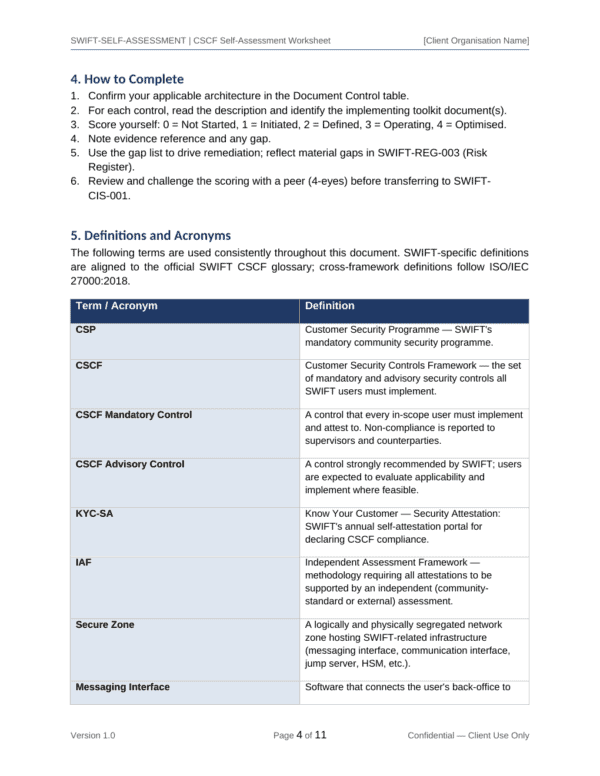
The SWIFT Customer Security Programme is not optional for institutions on the network: every member must attest annually against the Customer Security Controls Framework, and that attestation has to be backed by evidence. This SWIFT CSP Toolkit provides 32 templates covering the mandatory and advisory CSCF controls, the local and remote environment security policies, access and credential management, logging and detection, and the attestation and independent-assessment records SWIFT expects. Each document is written around the CSCF control objectives so your attestation reflects controls that are genuinely operating. All files are editable in Microsoft Office and ready to reflect your SWIFT architecture type.
Authored by a CISSP-certified GRC consultant with extensive experience in governance, risk and compliance, this toolkit encapsulates decades of practical expertise in a user-friendly, ready-to-use format. The templates reflect how SWIFT CSP attestations are prepared and independently assessed against the CSCF, not just the framework wording.
Governance Docs have created this pack to comply with the SWIFT Customer Security Programme (CSP) and the SWIFT Customer Security Control Framework (CSCF) v2026 — the version you must attest against by 31 December 2026. A dedicated transition guide covers the changes introduced by CSCF v2027, which applies to attestations in the second half of 2027.
A complete and comprehensive documentation package designed to assist clients, consultants, and service providers in successfully achieving compliance with SWIFT Customer Security Programme (CSP).
This toolkit has been developed in alignment with the SWIFT Customer Security Programme (CSP) and the SWIFT Customer Security Control Framework (CSCF) v2026, and includes a CSCF v2027 transition guide so you can plan ahead of the 2027 attestation cycle. Cross-mapping to ISO/IEC 27001:2022, NIST CSF 2.0, PCI DSS v4.0.1, and CBB Rulebook Module RM-9 is also provided where applicable.
Implementing for clients? The Consultant Package bundles 70 toolkits — 6,100+ editable templates — under one firm-wide licence that covers unlimited client engagements. $1,399 one-time.
Free articles that explain the requirements this toolkit covers.
 Comprehensive SWIFT CSP Compliance Toolkit – 32 Templates$99.00




Reviews
There are no reviews yet