Description
About the CMMC Documentation Toolkit
Last updated 2 November 2026. Version 2: every Word document now opens with a branded full-page cover showing its title, document ID and type, and every Excel workbook has a matching cover sheet and consistent table styling. The FAQ and reference guide also now reflect the 13 July 2026 suspension of CMMC Phase 2.
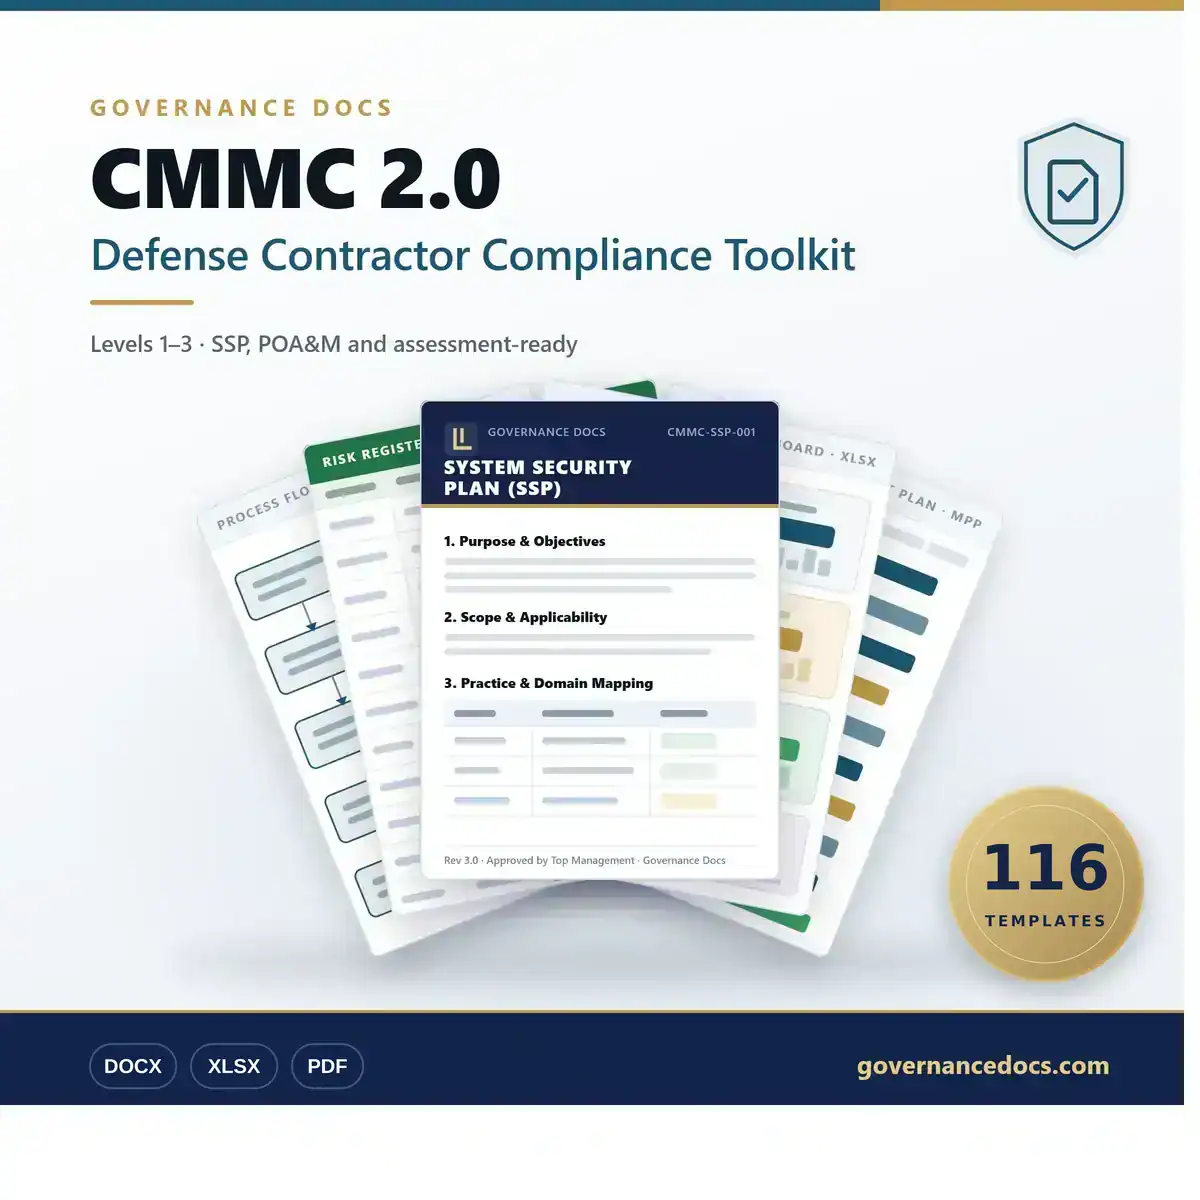
CMMC turns NIST SP 800-171 from a self-attestation into a certified requirement: defense contractors handling Federal Contract Information or Controlled Unclassified Information must reach the level their contracts demand, verified by assessment. This CMMC Toolkit provides 116 templates spanning CMMC Levels 1 to 2 — covering the System Security Plan, the practice-level policies and procedures across all 14 domains, the POA&M, and the incident-response, access-control and configuration records a C3PAO assessment examines. Each document is written so you can evidence each practice and trace it to implementation, which is the difference between passing and failing an assessment. The 113 Word and Excel files are editable in Microsoft Office.
The Cybersecurity Maturity Model Certification (CMMC) is a unified cybersecurity framework established by the U.S. Department of Defense (DoD) to protect Controlled Unclassified Information (CUI) across the Defence Industrial Base (DIB). CMMC 2.0 consolidates the 110 security practices of NIST SP 800-171 into a tiered certification model. Level 2 — the primary certification target for most defence contractors handling CUI — requires comprehensive, auditable documentation across 14 practice families. Organisations that fail to demonstrate this documentation during a third-party assessment risk losing DoD contract eligibility.
What is included in the toolkit?
- 107 Word documentation templates covering policies, procedures, standards, registers, plans, checklists, matrices, and programme governance documents aligned to all 14 NIST SP 800-171 practice families
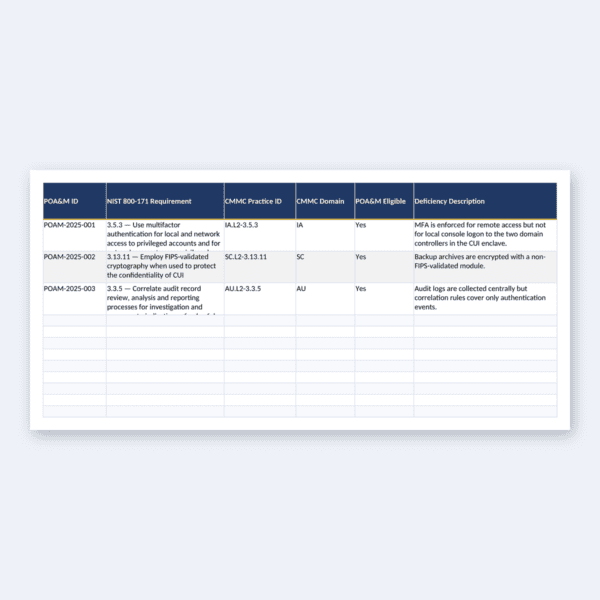
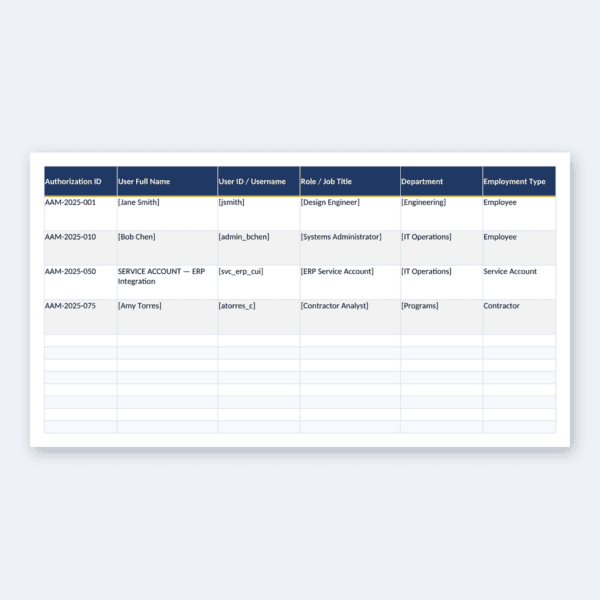
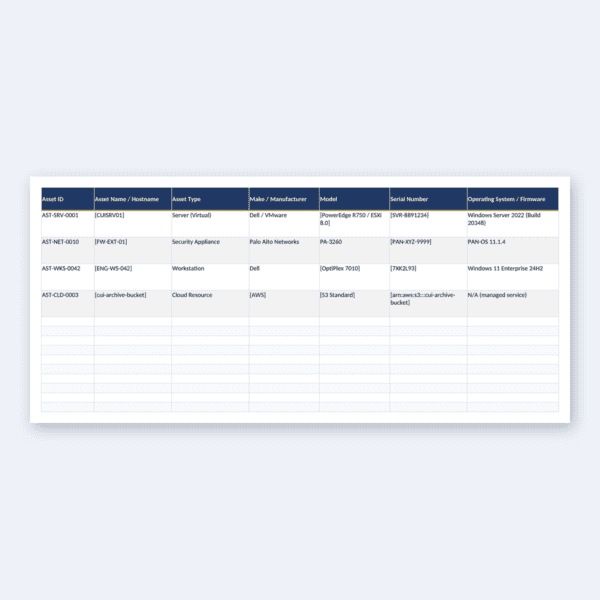
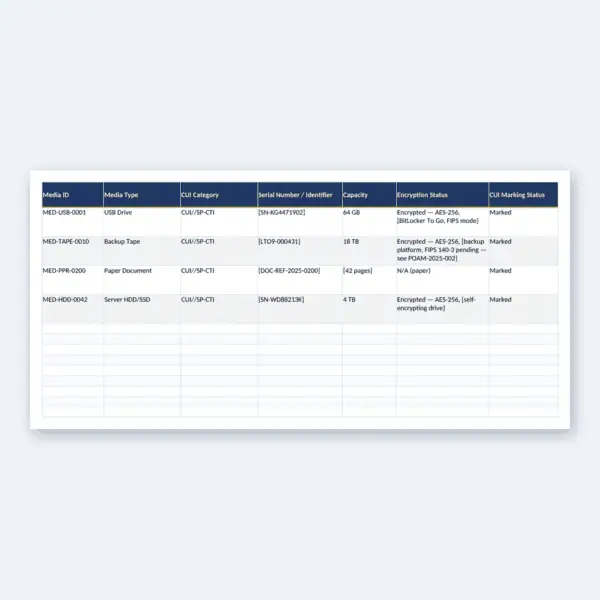
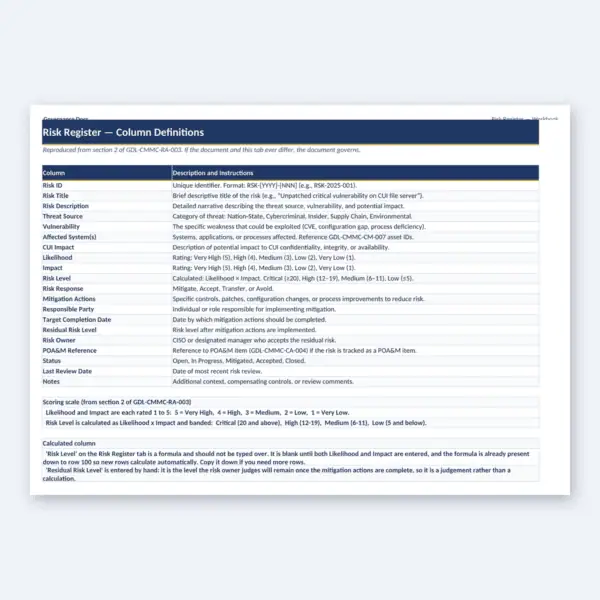
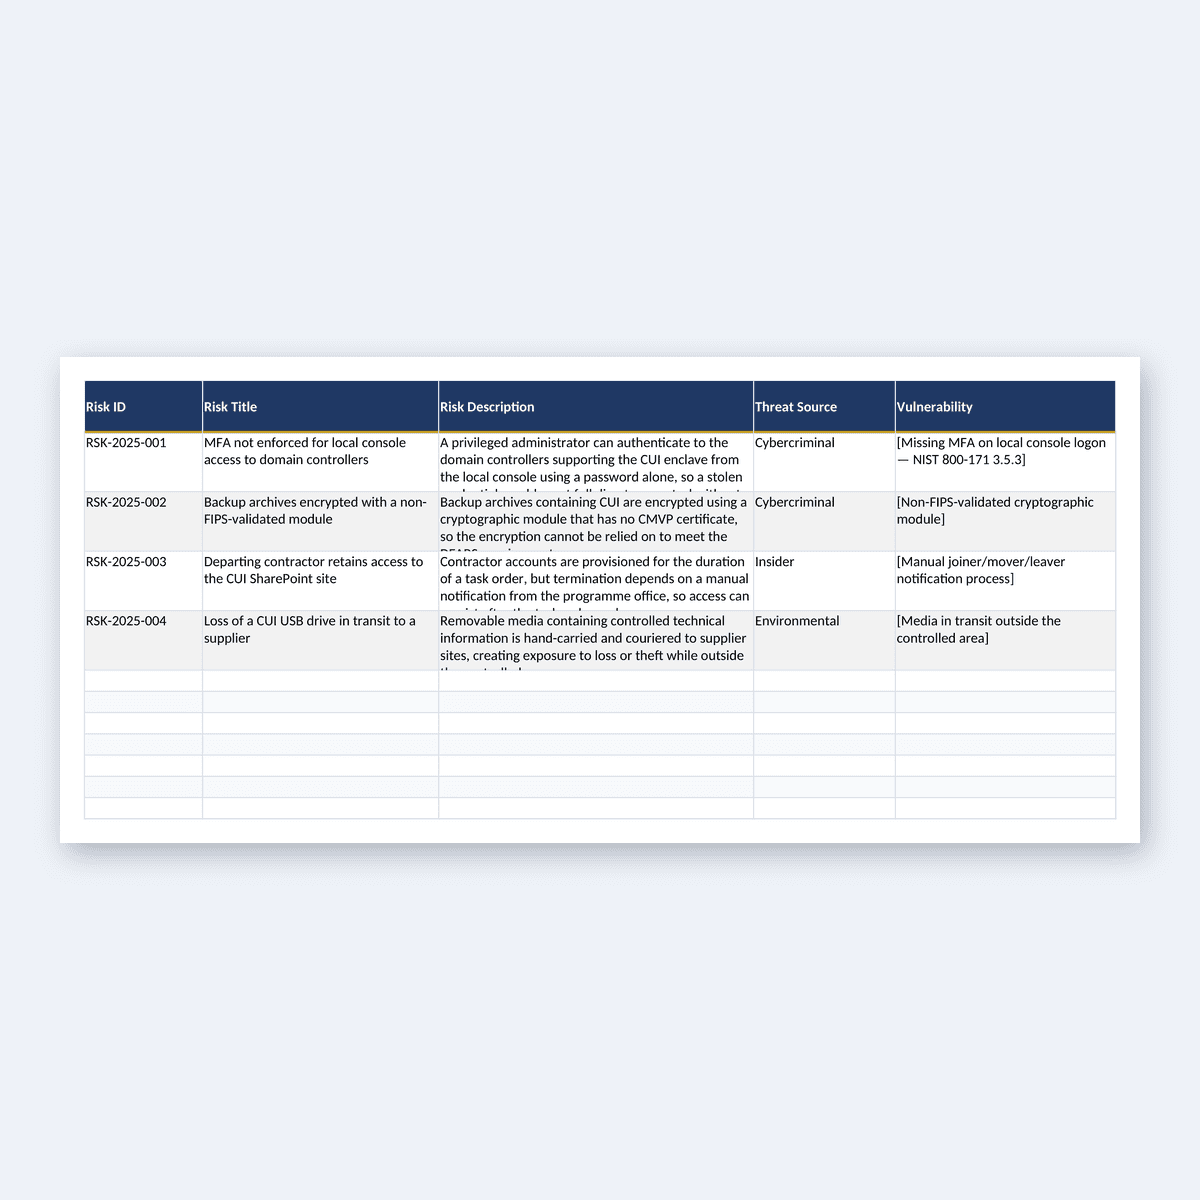
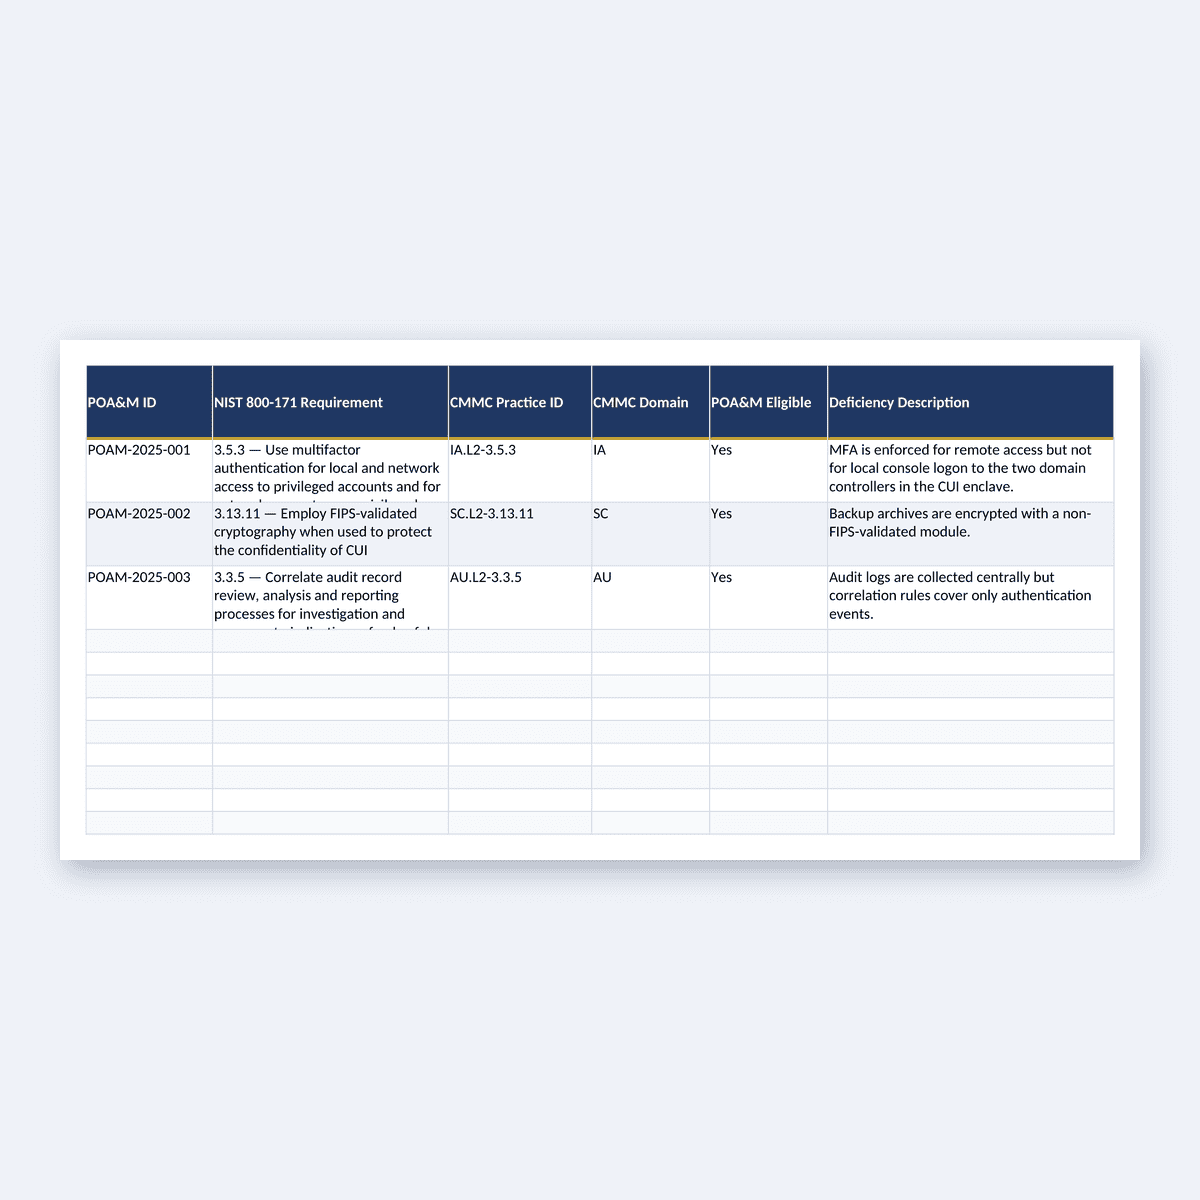
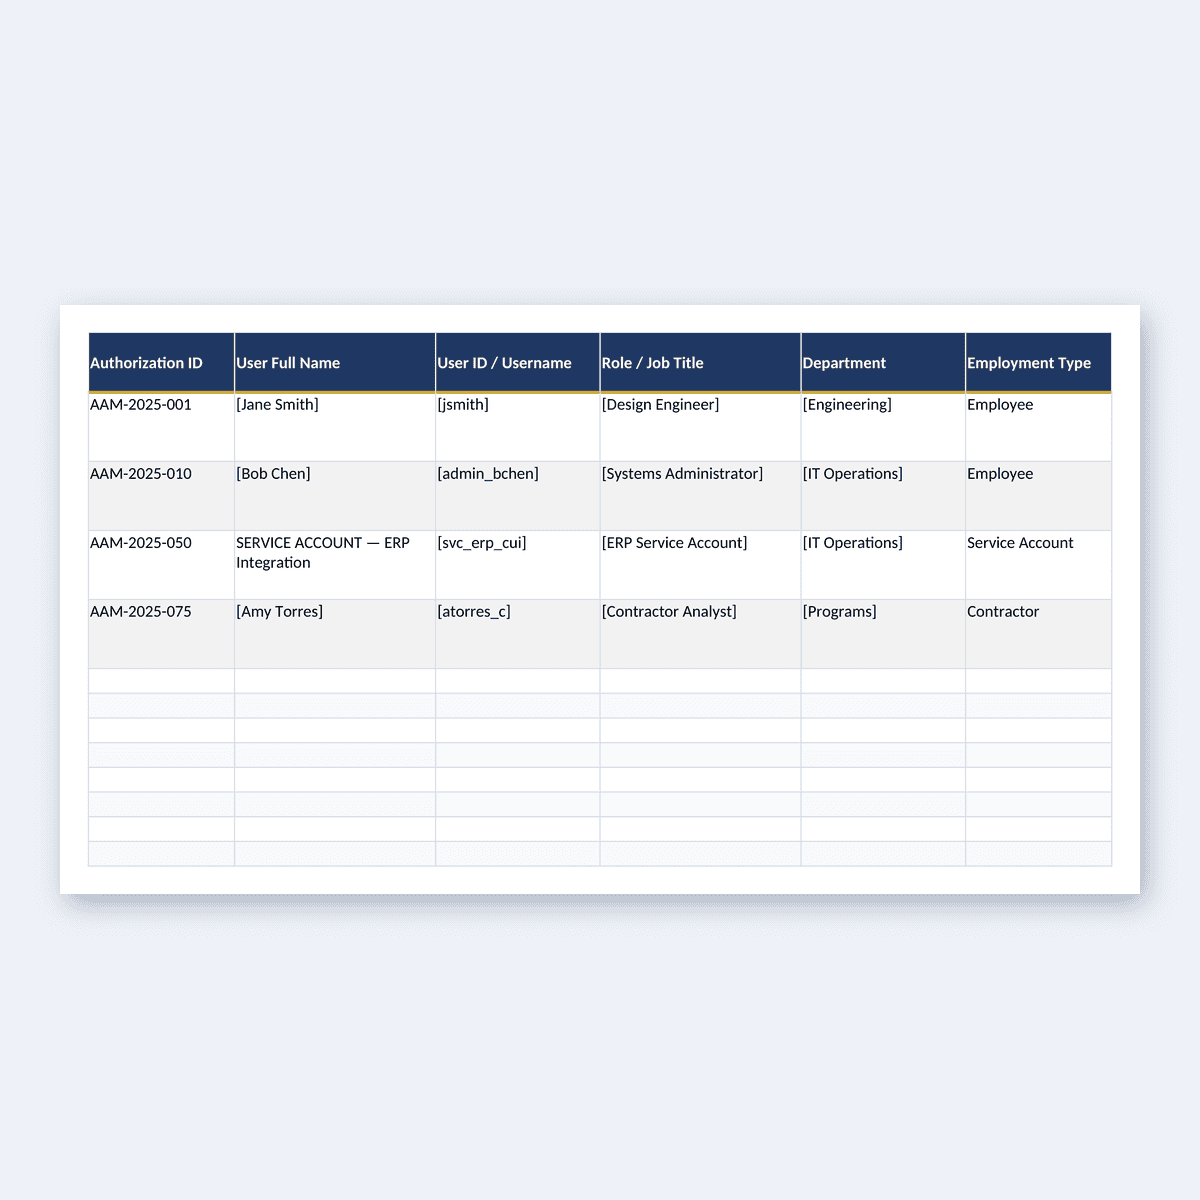
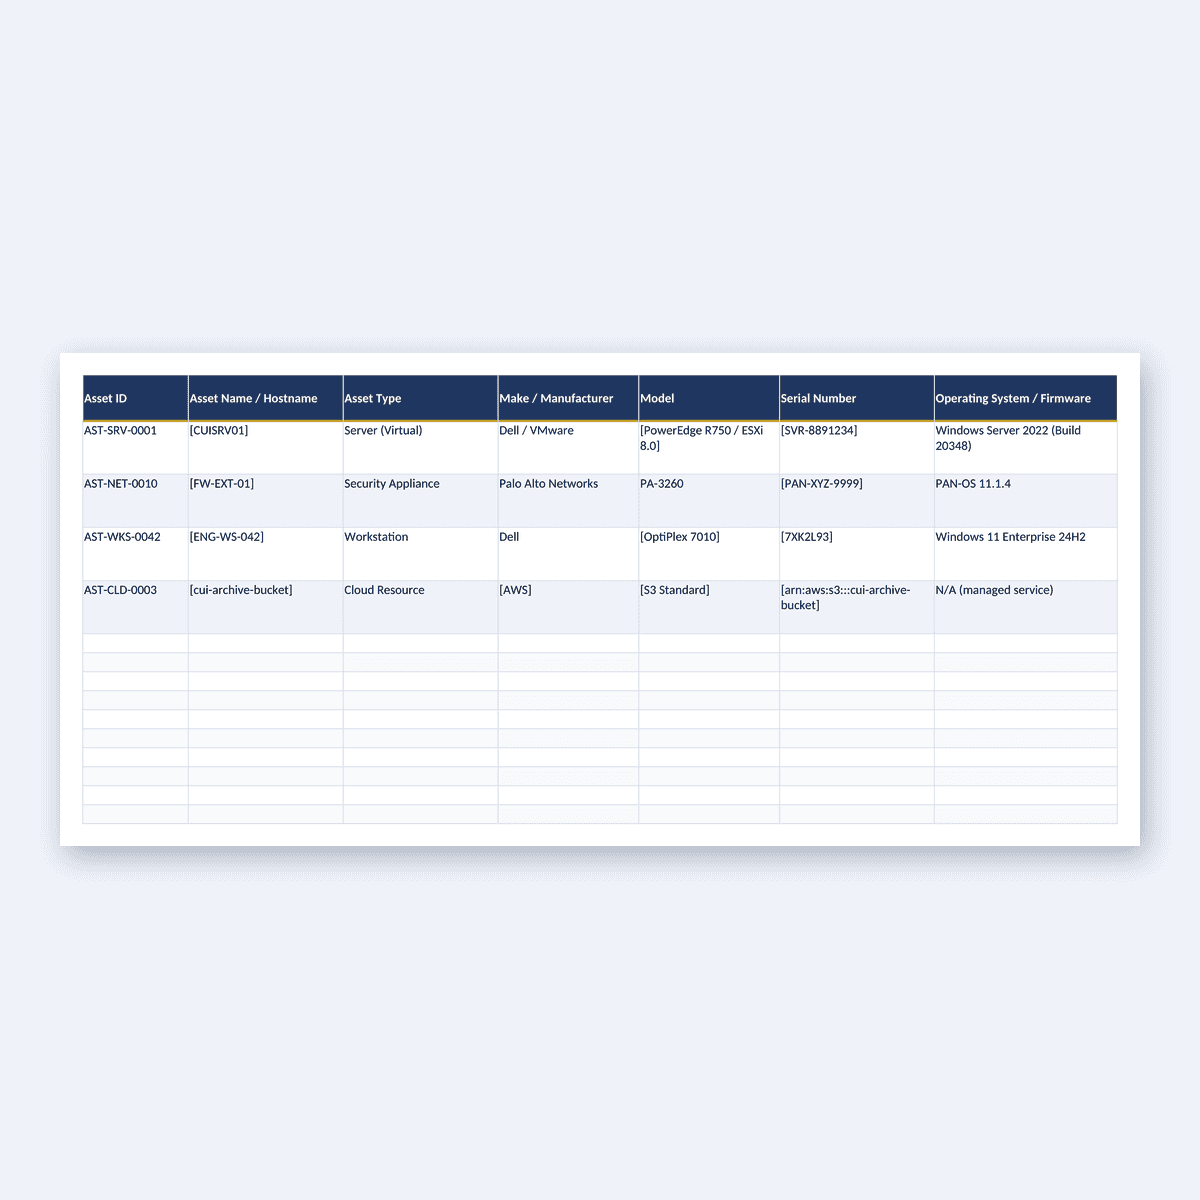
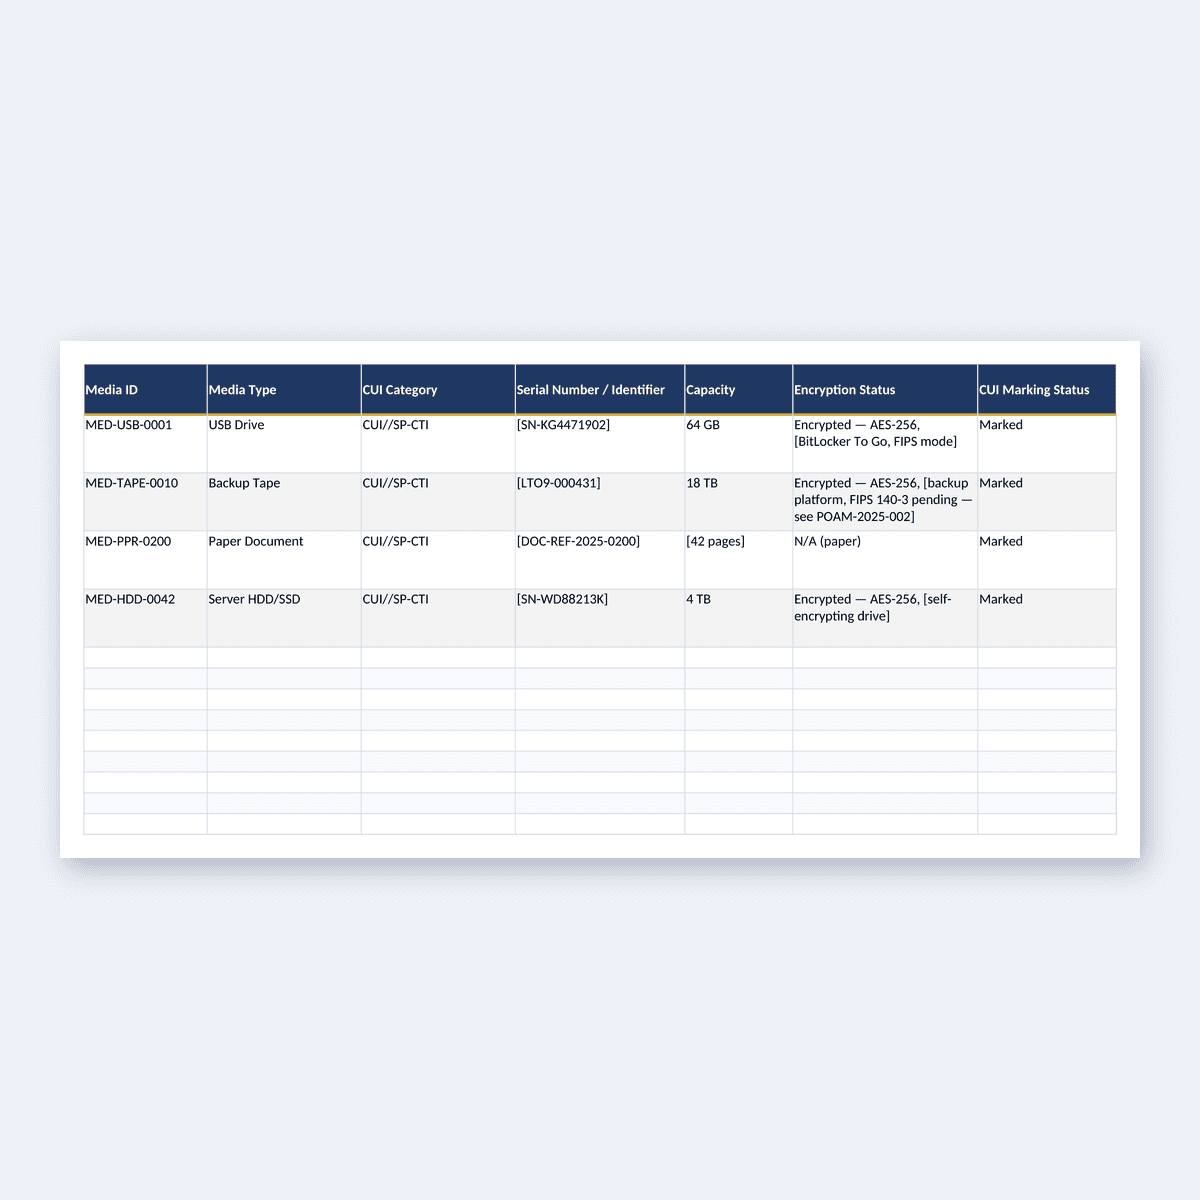
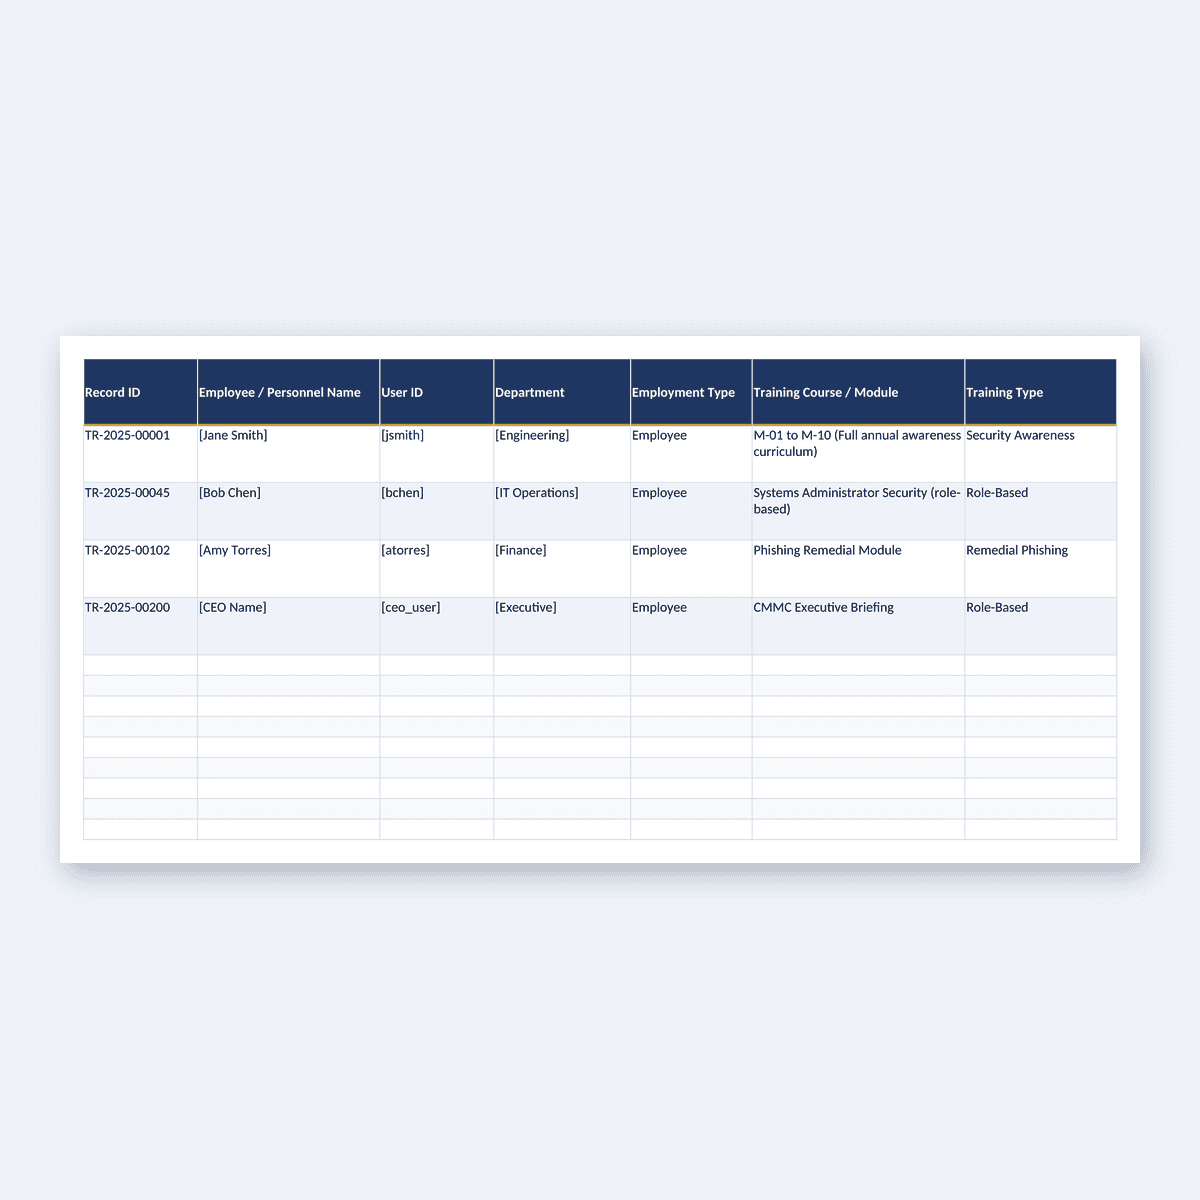
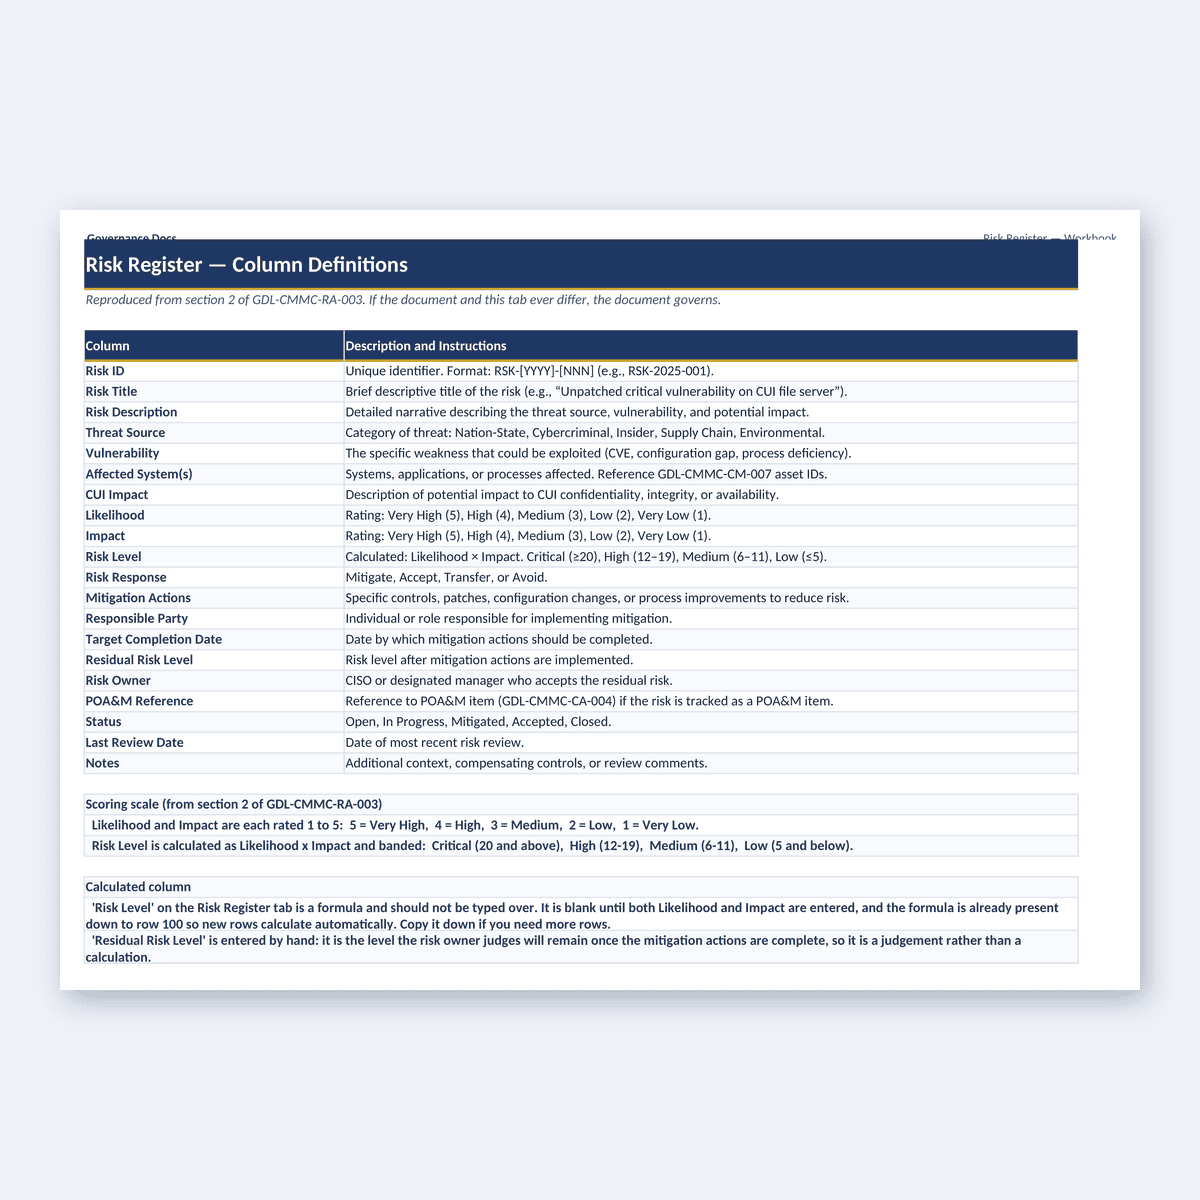
- Six registers ship with a companion Excel workbook — the Risk Register, POA&M Register, System Component Inventory, CUI Access Authorization Matrix, CUI Media Accountability Register and Training Attendance and Competency Register each include a ready-to-use .xlsx with dropdown lists, worked sample entries and the column definitions built in, so you can start populating the register immediately instead of building the spreadsheet yourself
- All templates provided in Microsoft Office format (.docx, .xlsx), plus 3 PDF guides (FAQ, how-to-use and reference) — fully editable and customisable to your organisation’s environment
- Instant download available immediately after purchase — no waiting, no shipping
116 CMMC Documentation Templates
This CMMC Toolkit delivers full coverage of every practice family required for CMMC Level 2 certification, including 10 cross-domain governance documents addressing CUI scoping, SPRS scoring, gap analysis, and continual improvement. Each template is structured for practical use, with clear headings, editable placeholder fields, and direct alignment to the specific practices and assessment objectives defined in the CMMC framework.
Toolkit Structure
The toolkit is organised into the following document categories:
- Access Control & Identity Management — 17 documents
- Awareness & Training — 5 documents
- Audit & Accountability — 7 documents
- Configuration Management — 8 documents
- Incident Response — 9 documents
- Maintenance & Media Protection — 11 documents
- Personnel & Physical Security — 11 documents
- Risk Assessment & Security Assessment — 13 documents
- System & Communications Protection — 9 documents
- System & Information Integrity — 7 documents
- Cross-Domain & Program Governance — 10 documents
List of Documentation Toolkit:
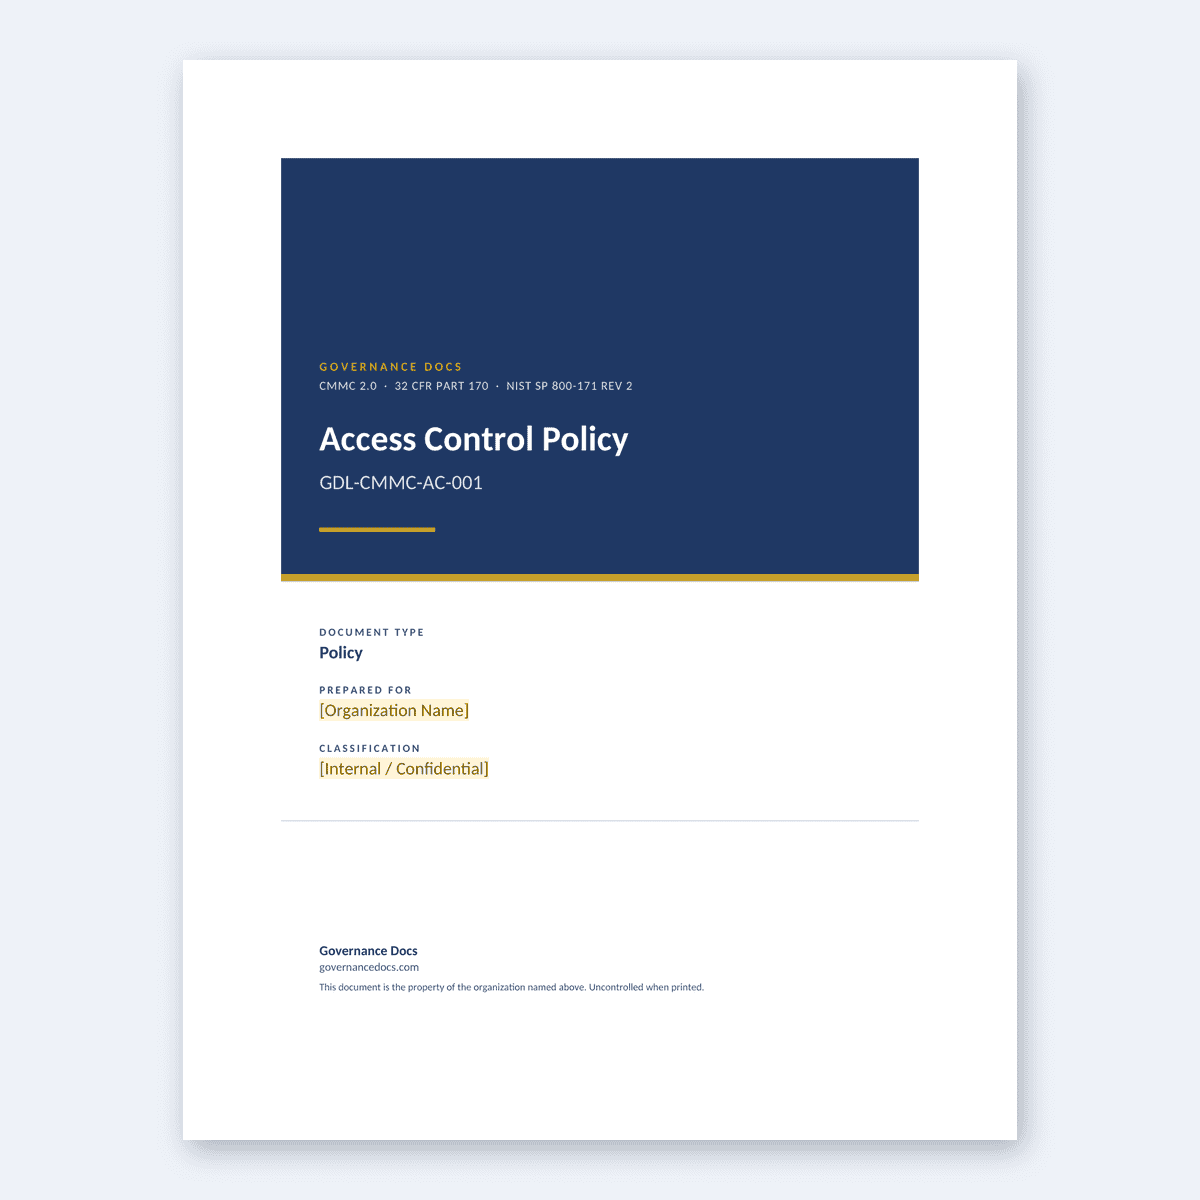
- Access Control Policy
- Account Management Procedure
- Access Enforcement and Information Flow Procedure
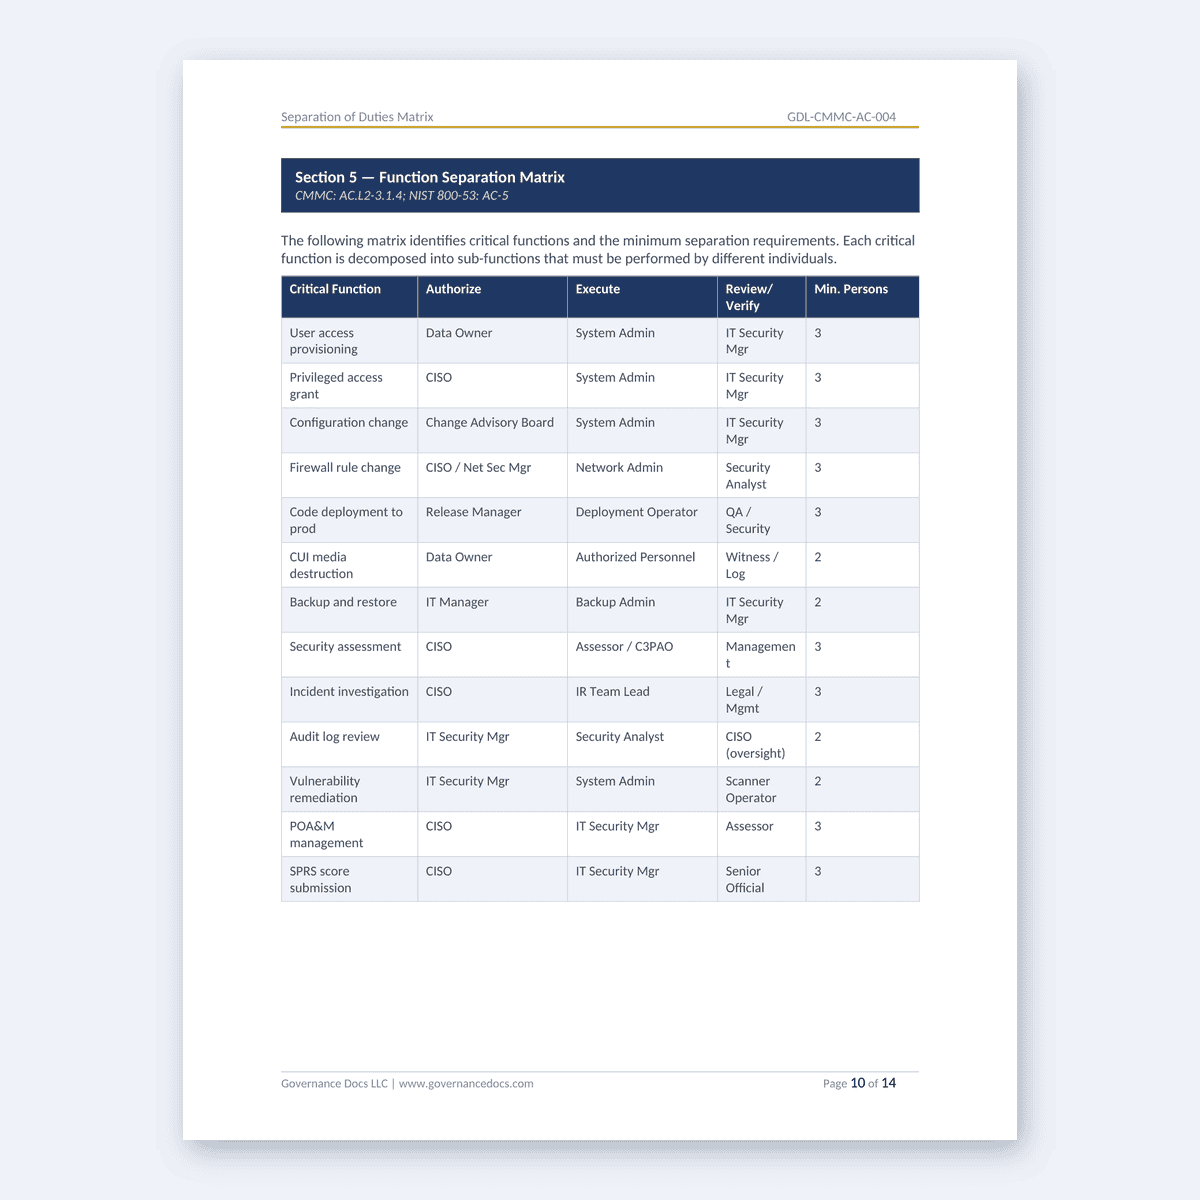
- Separation of Duties Matrix
- Least Privilege Implementation Procedure
- Remote Access Management Procedure
- Wireless Access Control Procedure
- Mobile Device Management Procedure
- External System Connection Procedure
- CUI Access Authorization Matrix
- Identification and Authentication Policy
- Multi-Factor Authentication Standard
- Authenticator Management Procedure
- Password Policy and Complexity Standard
- Device Identification and Authentication Procedure
- Cryptographic Authentication Standard
- Identifier Management Procedure
- Security Awareness and Training Policy
- Security Awareness Training Program
- Role-Based Security Training Procedure
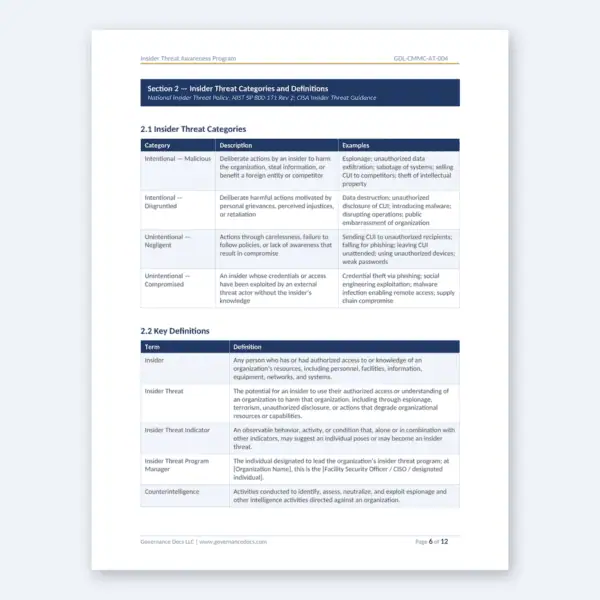
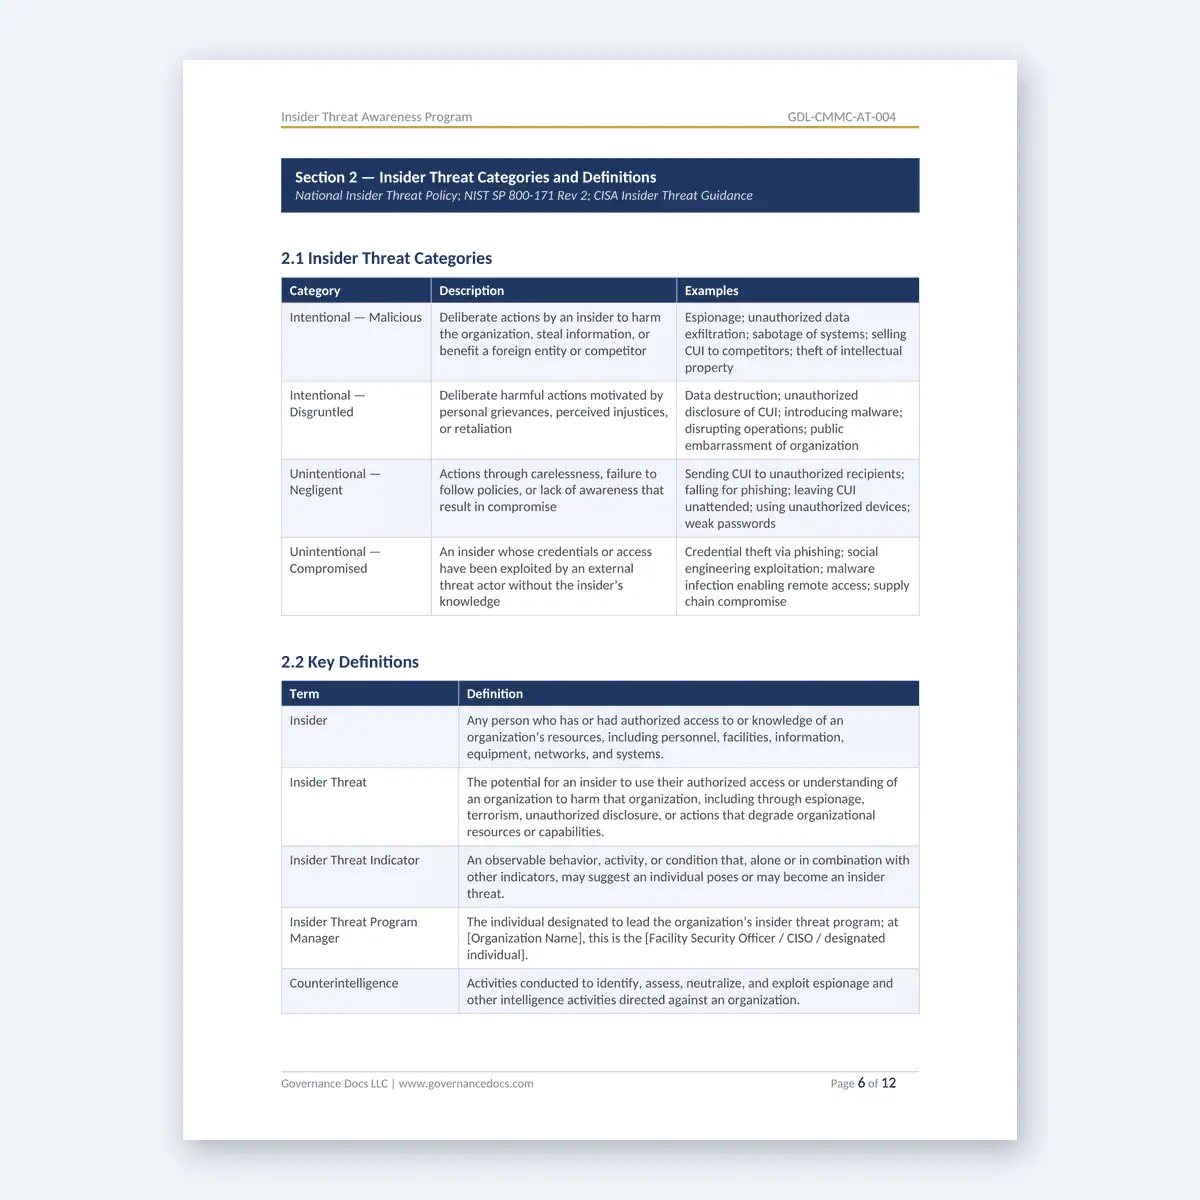
- Insider Threat Awareness Program
- Training Attendance and Competency Register
- Audit and Accountability Policy
- Audit Logging Configuration Standard
- Audit Log Review and Analysis Procedure
- Audit Record Content and Format Standard
- Audit Storage and Log Protection Procedure
- Audit Reduction and Report Generation Procedure
- Time Synchronization Standard
- Configuration Management Policy
- Baseline Configuration Standard
- Configuration Change Control Procedure
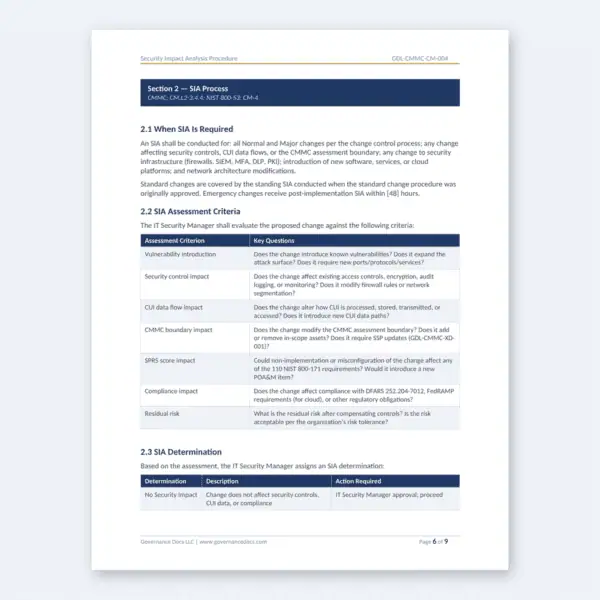
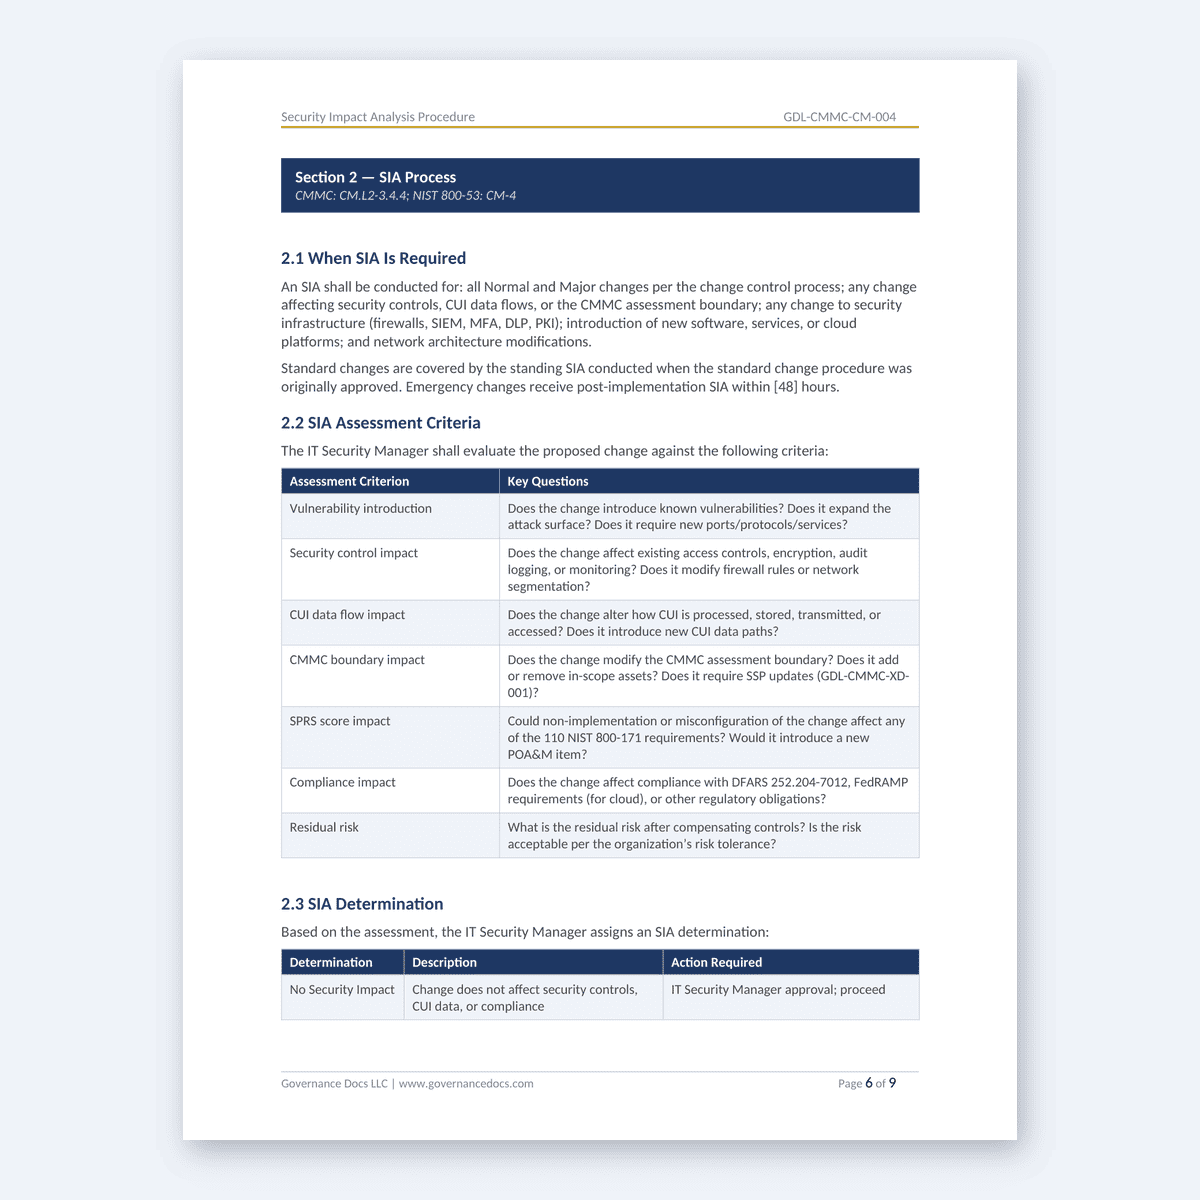
- Security Impact Analysis Procedure
- Access Restrictions for Change Procedure
- Least Functionality and Software Restriction Standard
- System Component Inventory Register
- Configuration Management Plan Template
- Incident Response Policy
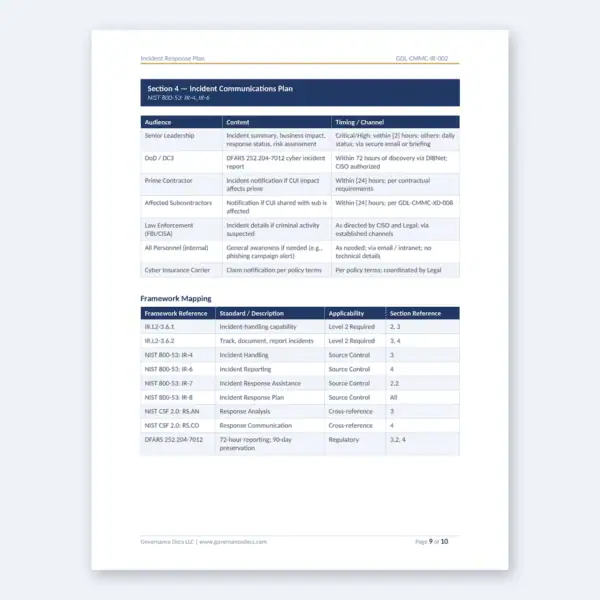
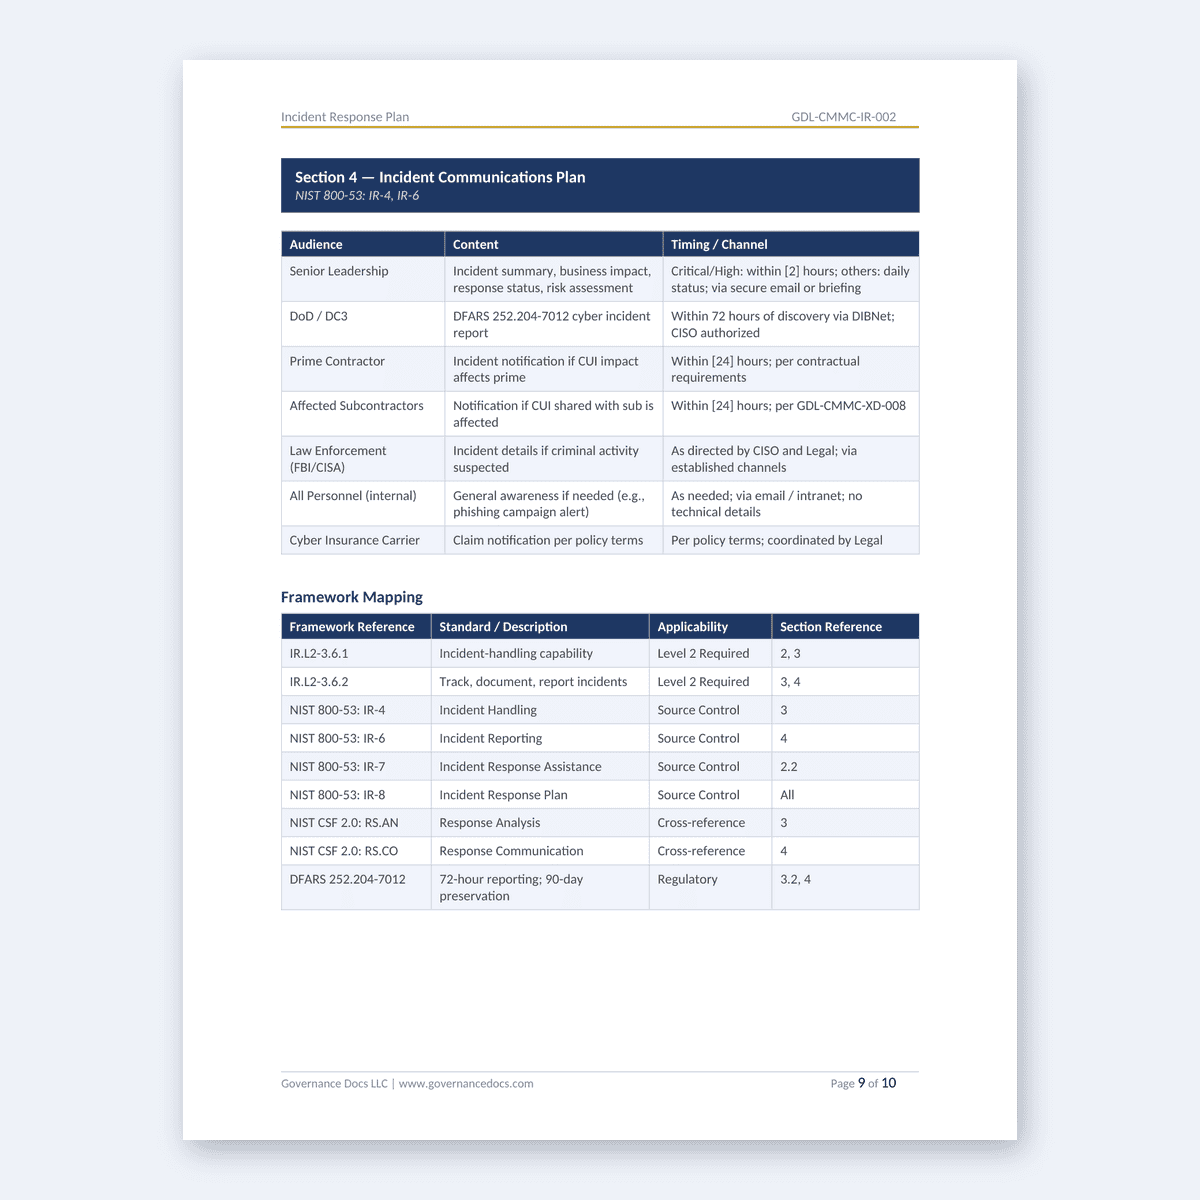
- Incident Response Plan
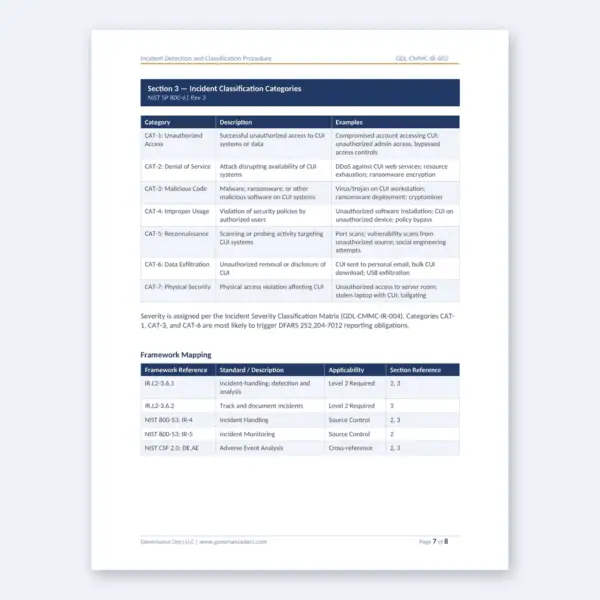
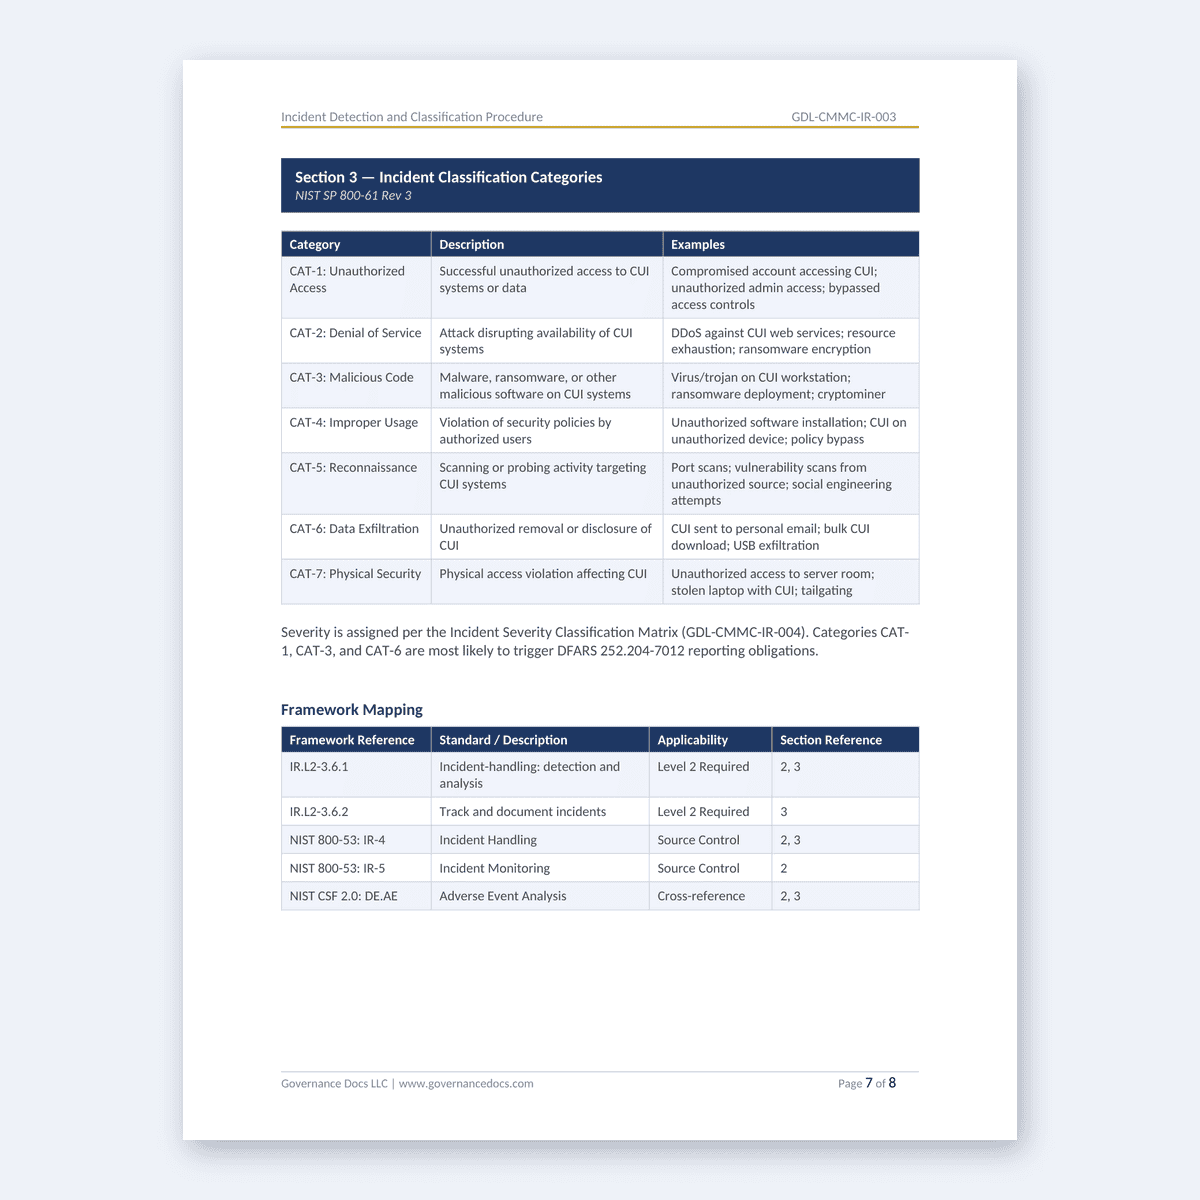
- Incident Detection and Classification Procedure
- Incident Severity Classification Matrix
- DoD Cyber Incident Reporting Procedure (72-Hour Notification)
- Incident Response Testing and Exercise Procedure
- Post-Incident Review and Lessons Learned Template
- Incident Register
- Digital Forensics and Evidence Preservation Procedure
- System Maintenance Policy
- Controlled Maintenance Procedure
- Maintenance Tools Control Procedure
- Nonlocal Maintenance Procedure
- Maintenance Personnel Oversight Procedure
- Media Protection Policy
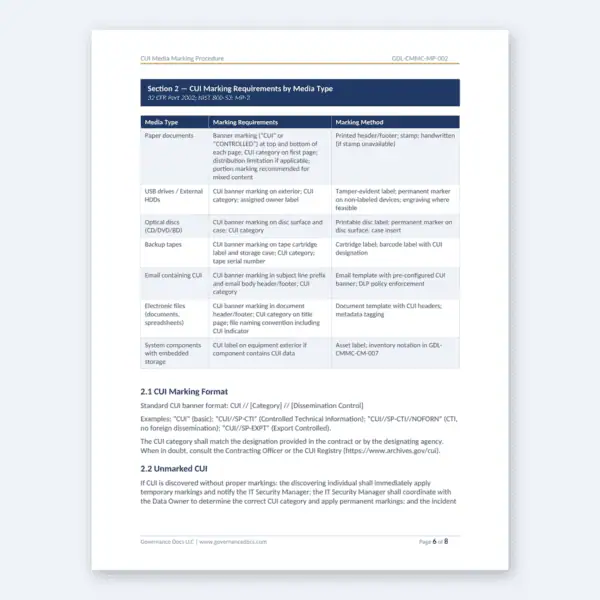
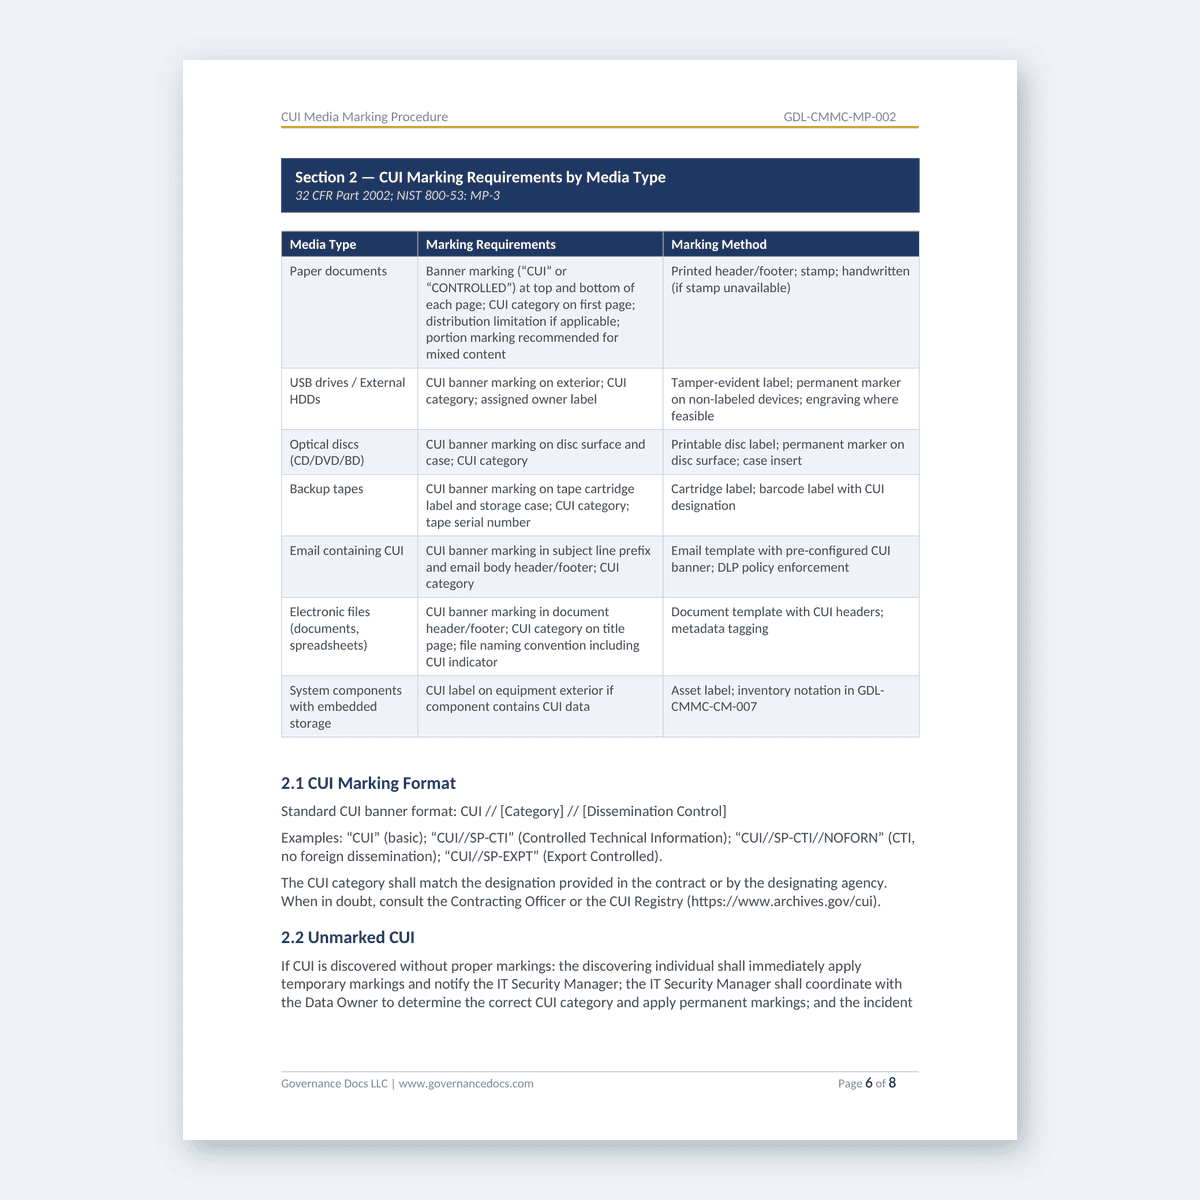
- CUI Media Marking Procedure
- Media Storage and Access Control Procedure
- Media Transport Protection Procedure
- Media Sanitization and Disposal Procedure
- CUI Media Accountability Register
- Personnel Security Policy
- Personnel Screening Procedure
- Personnel Termination and Transfer Security Procedure
- Nondisclosure Agreement (NDA) Template
- Physical Protection Policy
- Physical Access Authorization Procedure
- Facility Physical Access Monitoring Procedure
- Visitor Management Procedure
- Physical Access Log Template
- Alternate Work Site Security Procedure
- Equipment and Delivery Protection Procedure
- Risk Assessment Policy
- Risk Assessment Procedure
- Risk Register
- Vulnerability Scanning Procedure
- Vulnerability Remediation Procedure
- Risk Assessment Report Template
- Security Assessment Policy
- Security Assessment Procedure
- Plan of Action and Milestones (POA&M) Procedure
- POA&M Register Template
- Continuous Monitoring Strategy and Plan
- System Connection Authorization Procedure
- CMMC Assessment Readiness Checklist
- System and Communications Protection Policy
- Boundary Protection and Network Architecture Standard
- Network Segmentation and CUI Enclave Procedure
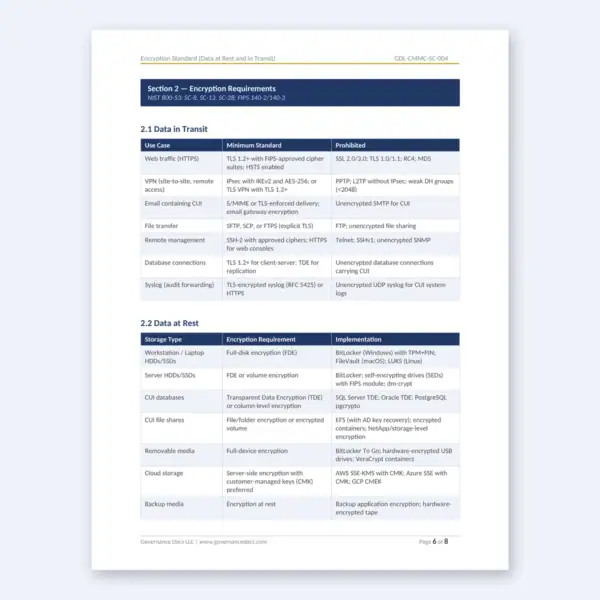
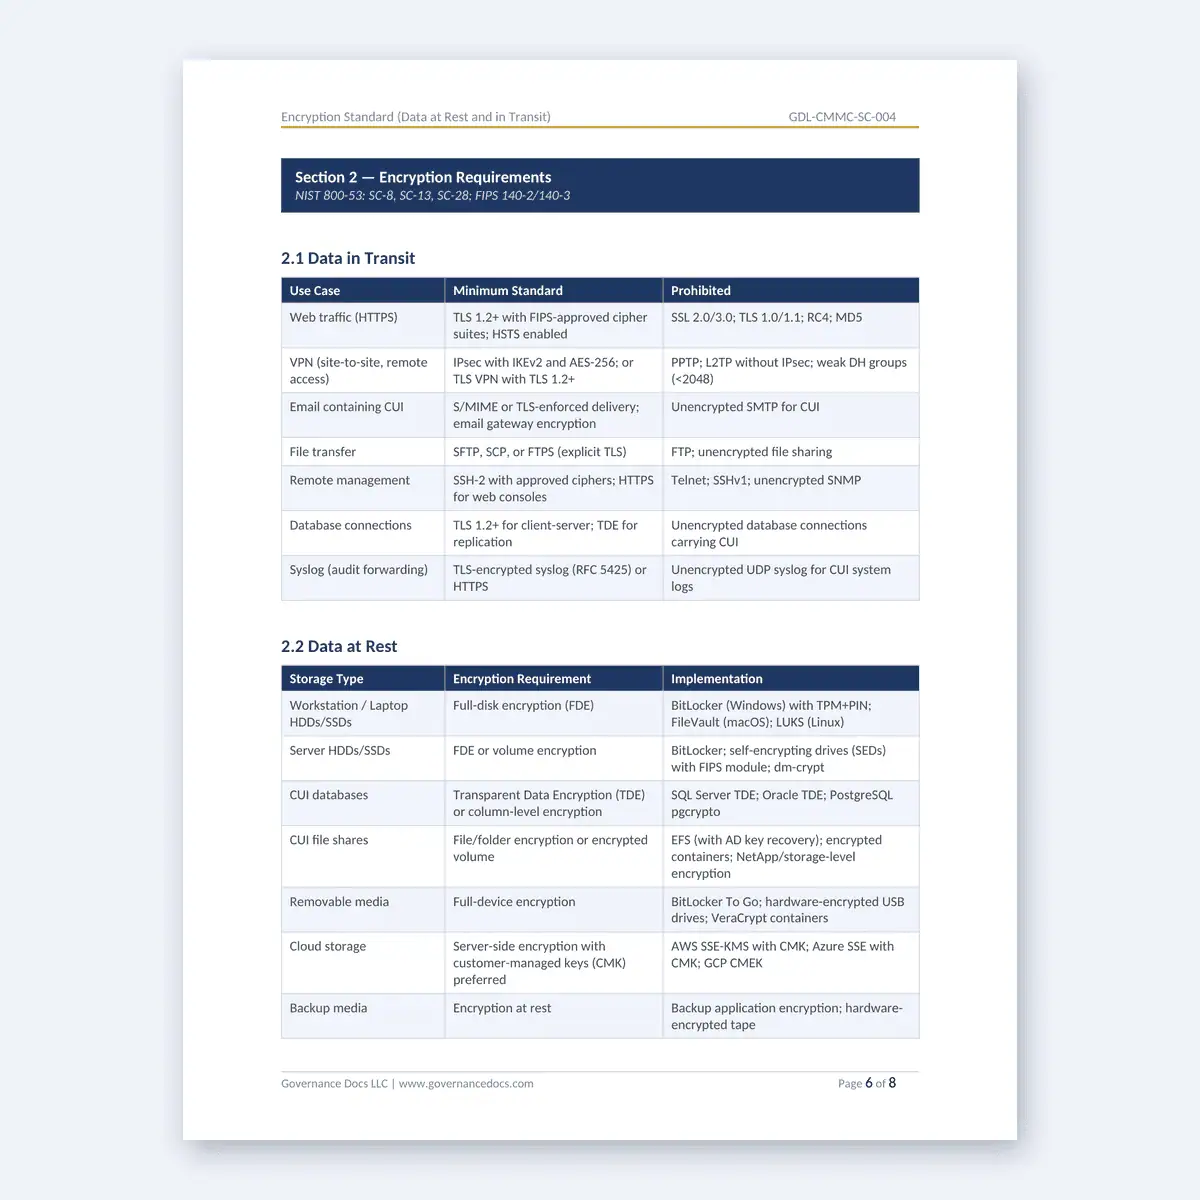
- Encryption Standard (Data at Rest and in Transit)
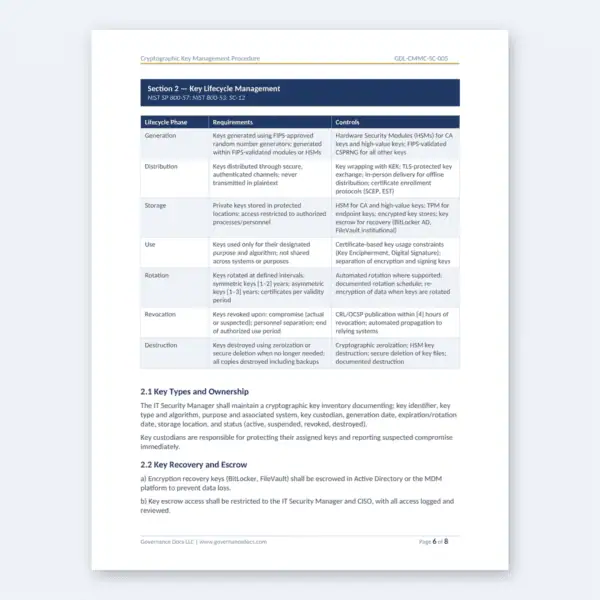
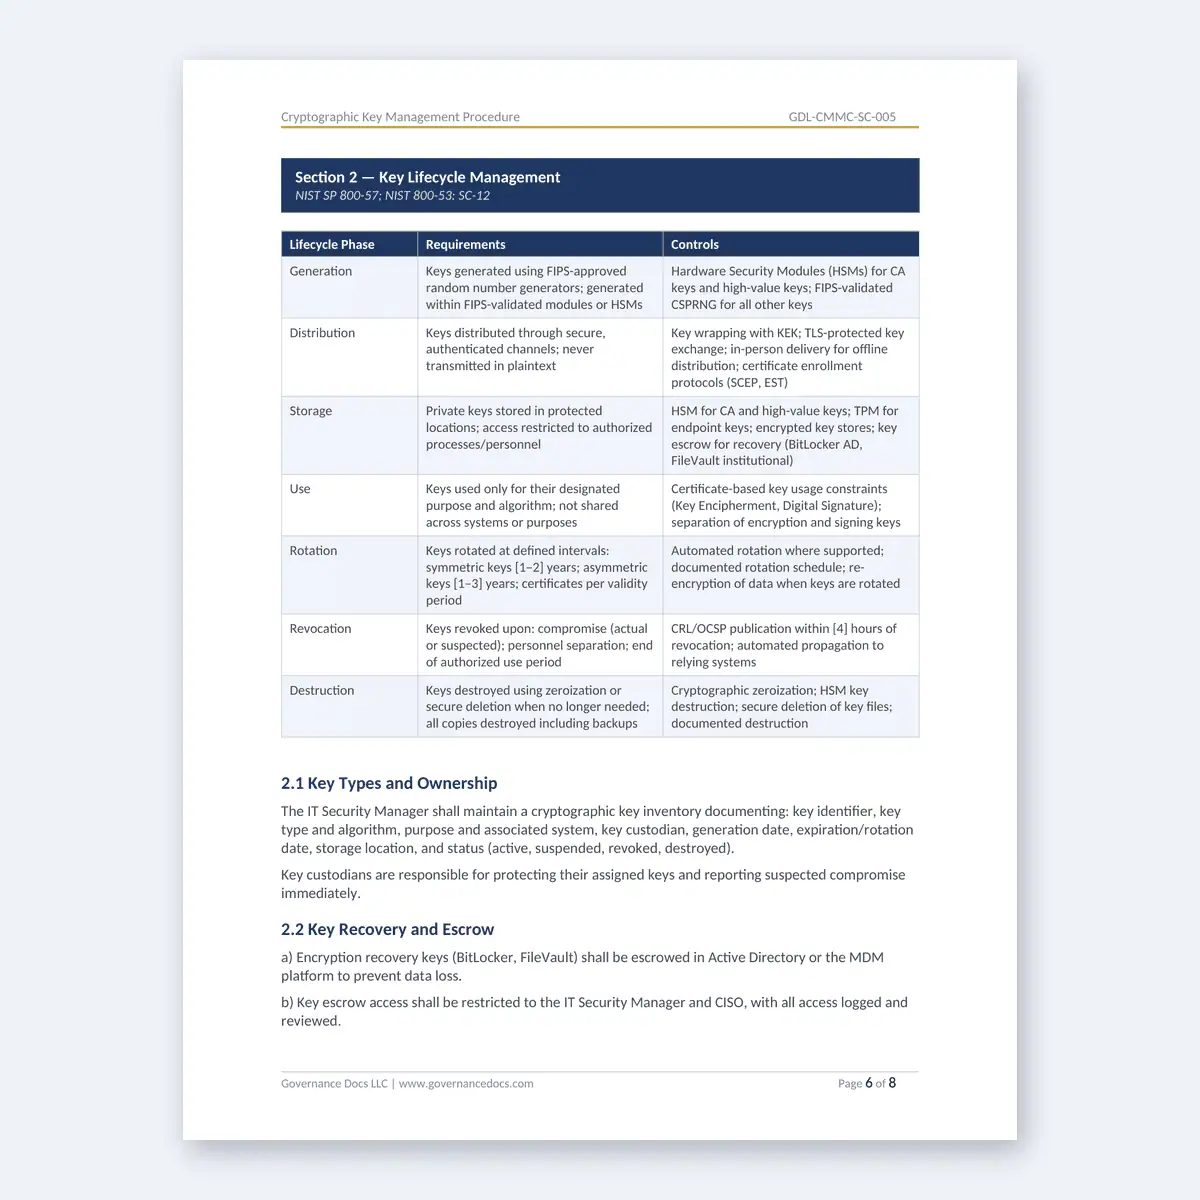
- Cryptographic Key Management Procedure
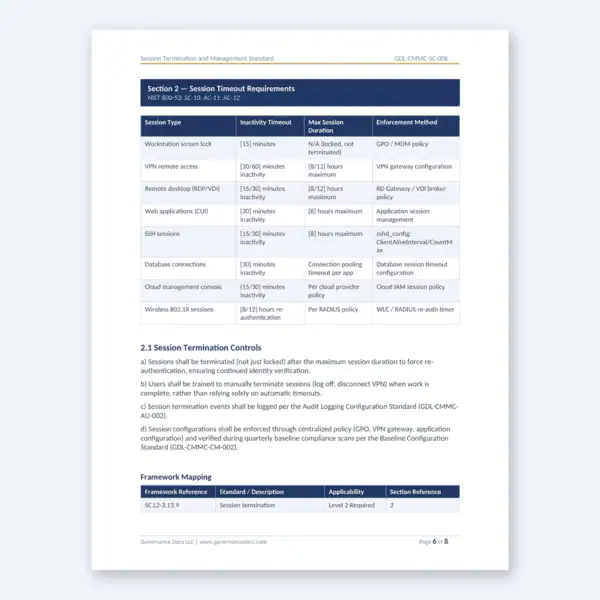
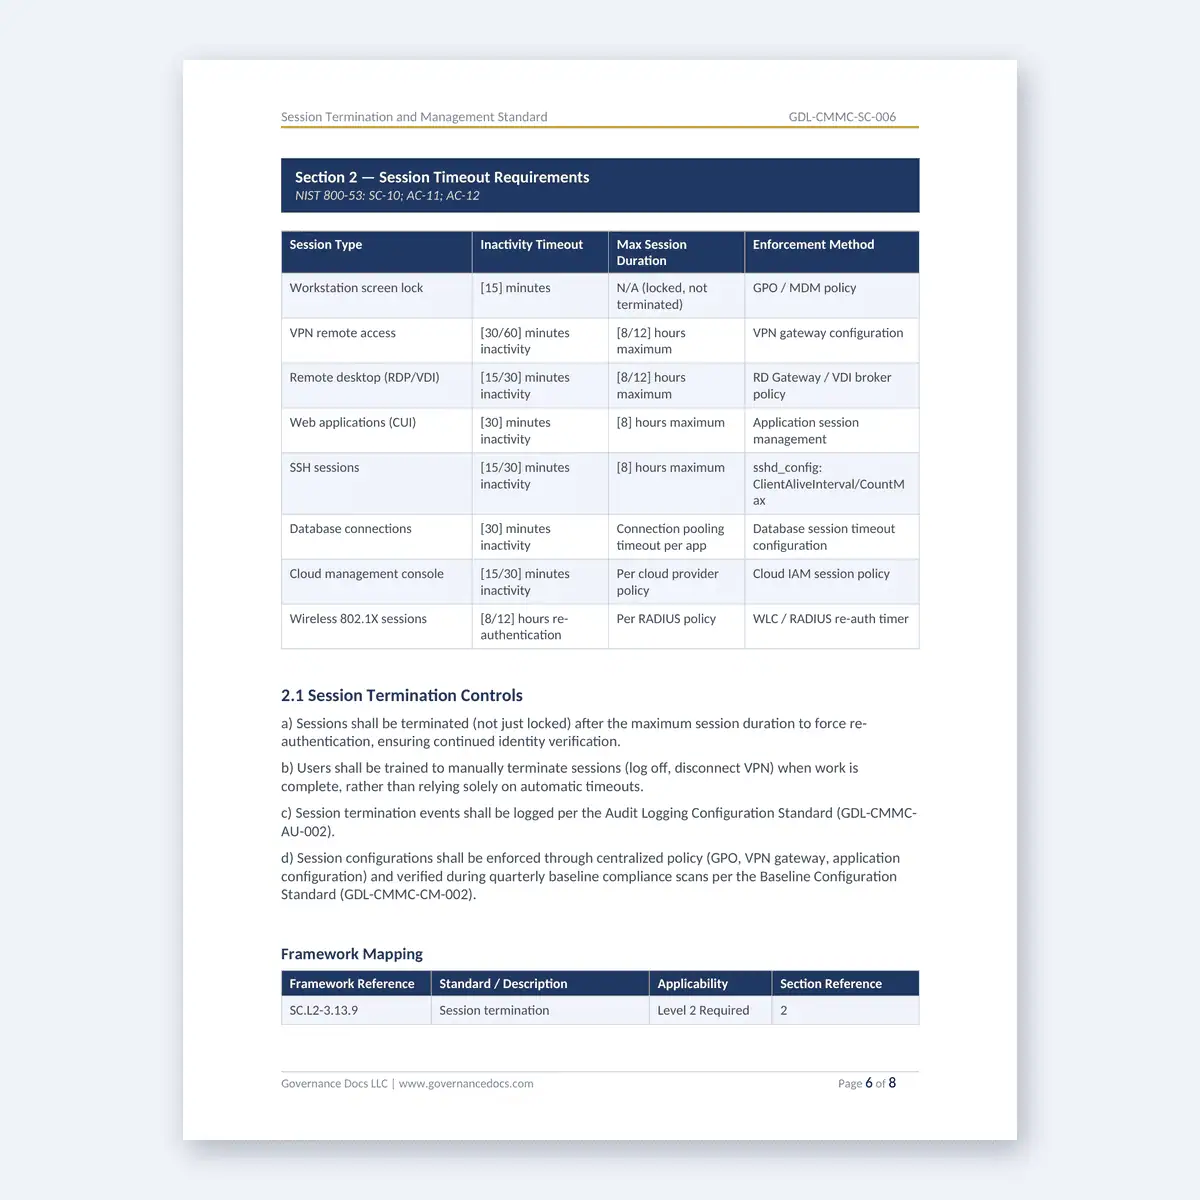
- Session Termination and Management Standard
- Public-Access System Separation Procedure
- DNS and Communications Integrity Standard
- Collaborative Computing and VoIP Security Procedure
- System and Information Integrity Policy
- Flaw Remediation and Patch Management Procedure
- Malicious Code Protection Procedure
- Security Alert and Advisory Monitoring Procedure
- System Monitoring and Intrusion Detection Procedure
- Inbound/Outbound Communications Analysis Procedure
- Software and Information Integrity Verification Procedure
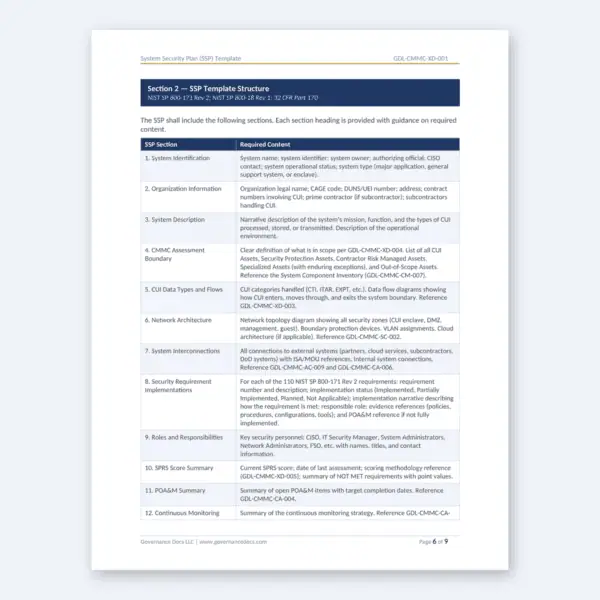
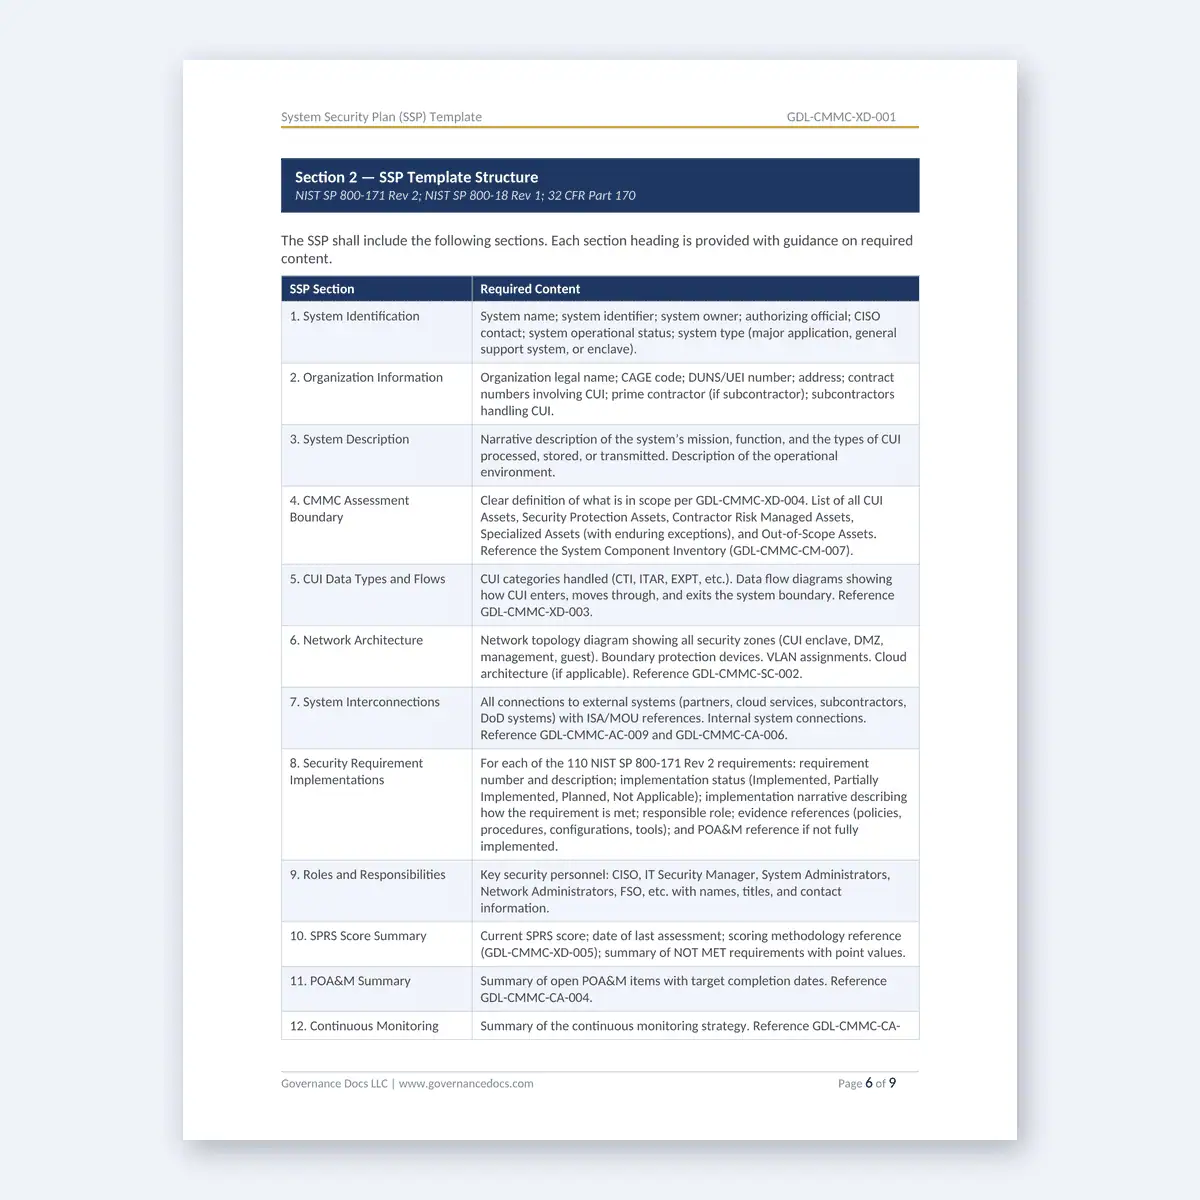
- System Security Plan (SSP) Template
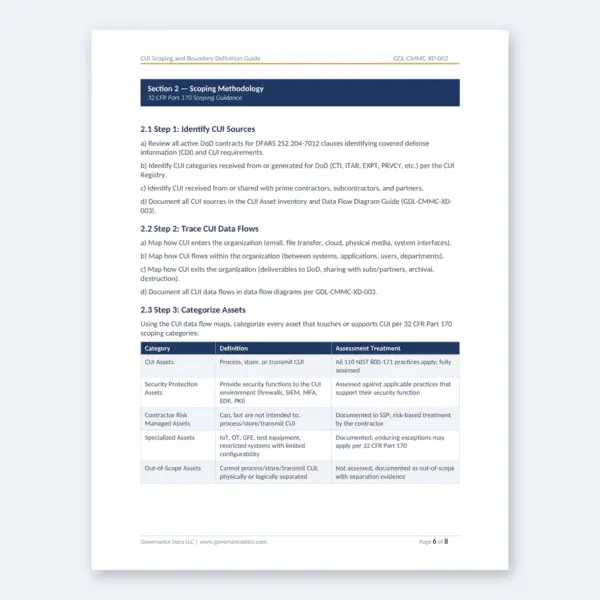
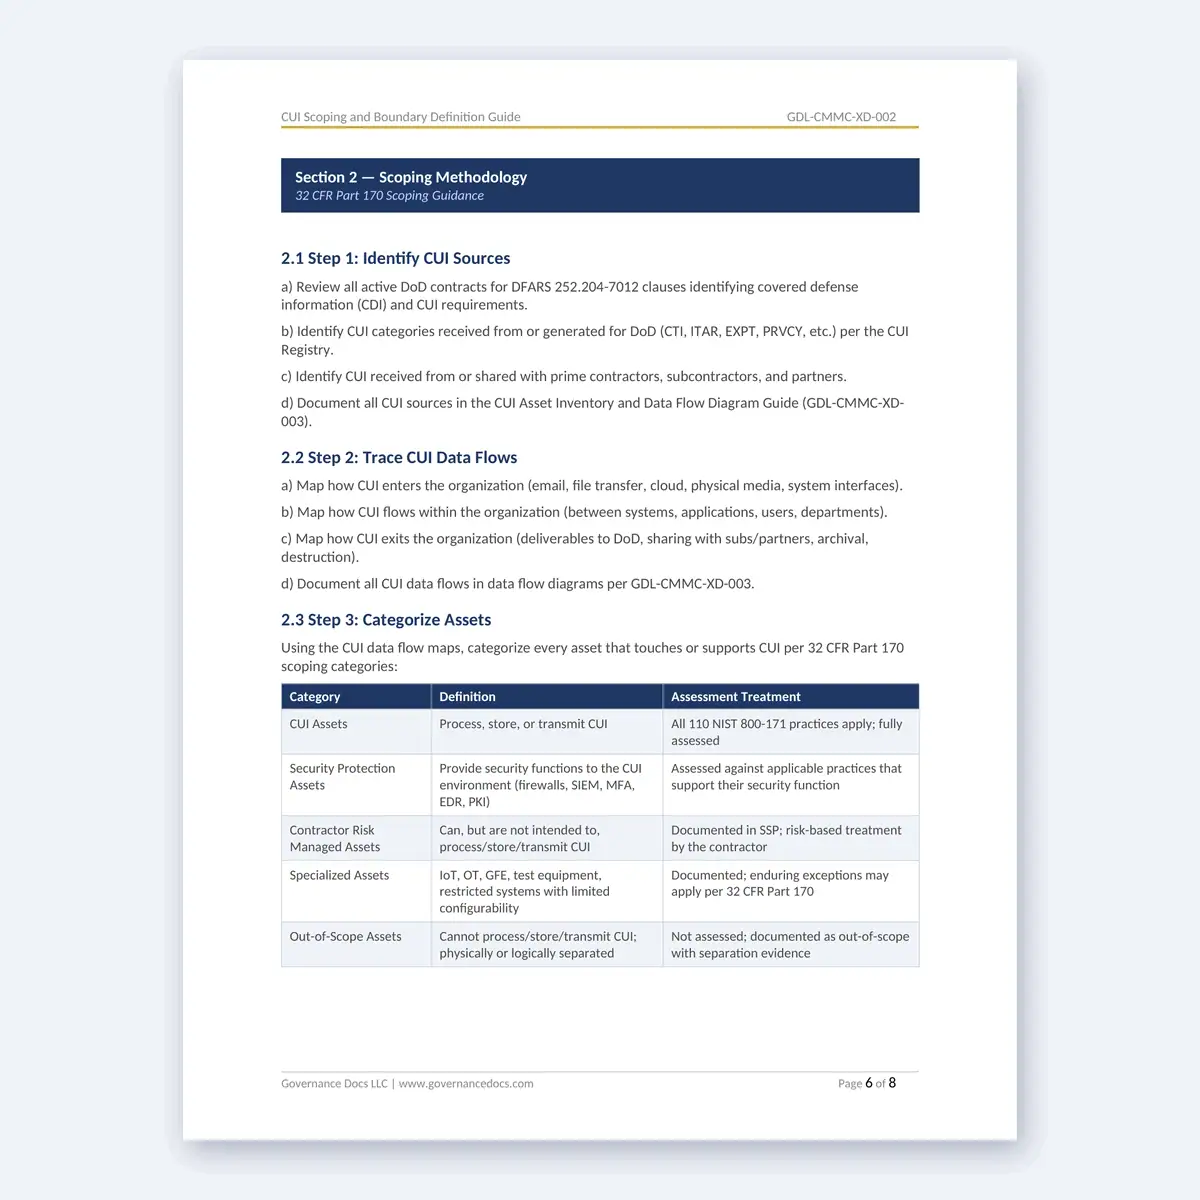
- CUI Scoping and Boundary Definition Guide
- CUI Asset Inventory and Data Flow Diagram Guide
- CMMC Assessment Scope Determination Procedure
- SPRS Score Calculation Workbook Guide
- CMMC Gap Analysis Workbook Template
- CMMC Governance and Oversight Framework
- Subcontractor Flow-Down Requirements Procedure
- Cloud Service Provider (CSP) Security Requirements Guide
- CMMC Continual Improvement and Reassessment Procedure
CMMC Compliance
This toolkit has been developed in alignment with the CMMC Official Framework, as established by the U.S. Department of Defense, and references the security practice requirements of NIST SP 800-171 Rev 2.
Frequently Asked Questions
What is included in the CMMC Documentation Toolkit?
The toolkit includes 116 professionally developed templates (107 Word, 6 Excel, 3 PDF guides) covering all 14 NIST SP 800-171 practice families required for CMMC Level 2 certification, including 10 cross-domain governance documents. Templates span policies, procedures, standards, registers, plans, checklists, matrices, and programme governance tools — provided as editable Microsoft Office (.docx, .xlsx) files for immediate use, plus 3 PDF guides. Six of the registers — the Risk Register, POA&M Register, System Component Inventory, CUI Access Authorization Matrix, CUI Media Accountability Register and Training Attendance and Competency Register — also ship with a companion Excel workbook carrying that register’s column definitions, dropdown lists and worked sample entries, so you receive 113 editable files, plus the 3 PDF guides.
Is this toolkit aligned with the latest version of CMMC?
Yes. This toolkit is aligned with the CMMC Program as codified at 32 CFR Part 170, the rule that governs CMMC and took effect on 16 December 2024. (You will still see the programme called “CMMC 2.0” across the market — that was the name of the 2021 restructuring proposal, and the final rule simply calls it the Cybersecurity Maturity Model Certification Program.) The documentation reflects the 110 security practices of NIST SP 800-171 Rev 2, which underpin CMMC Level 2 requirements, and includes cross-domain documents addressing the System Security Plan (SSP), SPRS scoring, and POA&M management.
Who can benefit from this CMMC toolkit?
This toolkit is designed for defence contractors, subcontractors, and organisations within the Defence Industrial Base (DIB) that handle Controlled Unclassified Information (CUI) under DFARS obligations. It is equally valuable for cybersecurity consultants, C3PAOs, and GRC professionals supporting multiple clients pursuing CMMC Level 2 certification. Compliance managers, IT security teams, and programme security officers will all find practical value in the templates.
How do I use the templates after purchase?
All 116 templates download instantly. Open the Word and Excel files in Microsoft Office, complete the SSP and domain documents for your CUI environment, and the POA&M and supporting records are ready to finalise. The structure maps to the CMMC domains and practices, so your documentation aligns with how the assessment is run.
Can I use this toolkit for multiple clients or projects?
Within your own organisation, yes: reuse it across business units, sites and projects. Each external client needs its own licence. If you implement for several clients, the
Consultant Package covers unlimited client engagements under one firm-wide licence for $1,399.
How long will it take to implement using this toolkit?
A defensible SSP and POA&M can be in place within weeks; closing the technical practice gaps and preparing for the C3PAO assessment drives most of the timeline. Contractors already running a compliant enclave such as Microsoft 365 GCC High reach readiness fastest.
Does this toolkit cover all CMMC Level 2 practice families?
Yes. The toolkit provides documentation templates mapped to all 14 NIST SP 800-171 practice families that form the basis of CMMC Level 2 — including Access Control, Configuration Management, Incident Response, Risk Assessment, System and Communications Protection, and System and Information Integrity, among others. The cross-domain documents additionally address CUI scoping, SSP development, SPRS scoring, gap analysis, and ongoing assessment readiness.
What is the difference between CMMC Level 1, Level 2, and Level 3?
CMMC 2.0 comprises three maturity levels. Level 1 (Foundational) covers 15 basic safeguarding requirements for organisations handling Federal Contract Information (FCI) only. Level 2 (Advanced) covers 110 practices aligned to NIST SP 800-171 and applies to organisations handling CUI — this is the primary focus of this toolkit. Level 3 (Expert) incorporates additional practices from NIST SP 800-172 for organisations supporting critical or high-priority DoD programmes.
What is a System Security Plan (SSP) and is it included?
A System Security Plan (SSP) is the central document required by CMMC Level 2 that describes how your organisation implements each of the 110 NIST SP 800-171 practices within your specific system boundary. This toolkit includes a comprehensive SSP Template along with supporting documents such as the CUI Scoping and Boundary Definition Guide and the CMMC Assessment Scope Determination Procedure to help you build a complete, assessment-ready SSP.
Implementing for clients? The Consultant Package bundles 91 toolkits — 8,400+ editable templates — under one firm-wide licence that covers unlimited client engagements. $1,399 one-time.
Want to see the documents first? Five templates from this toolkit are free by email — get the CMMC samples.
Guides for the CMMC Documentation Toolkit
Free articles that explain the requirements this toolkit covers.
 Comprehensive CMMC Documentation Toolkit – 116 Compliance Templates$99.00











A highly useful set of resources that simplifies CMMC compliance and keeps documentation organized. The templates are detailed, practical, and easy to adapt to specific requirements.