
CART
No products in the cart.
The Incident Response Toolkit is 93 editable templates aligned to NIST SP 800-61 Rev. 3 (April 2025): an incident response plan, 13 scenario playbooks including ransomware and business email compromise, 6 tabletop exercise scenarios with a briefing deck, and the procedures, forms and registers to run them — 75 Word documents, 17 Excel workbooks and 1 PowerPoint deck. It covers all 114 Rev. 3 recommendations and considerations, with NIST’s wording reproduced in every document.
$99.00
✓ In stock — instant download after checkout
The Incident Response Toolkit is a complete, editable incident response programme aligned to NIST SP 800-61 Revision 3. It is 93 templates — 75 Word documents, 17 Excel workbooks and 1 PowerPoint deck — covering the plan, the playbooks, the exercises and the records an incident actually needs.
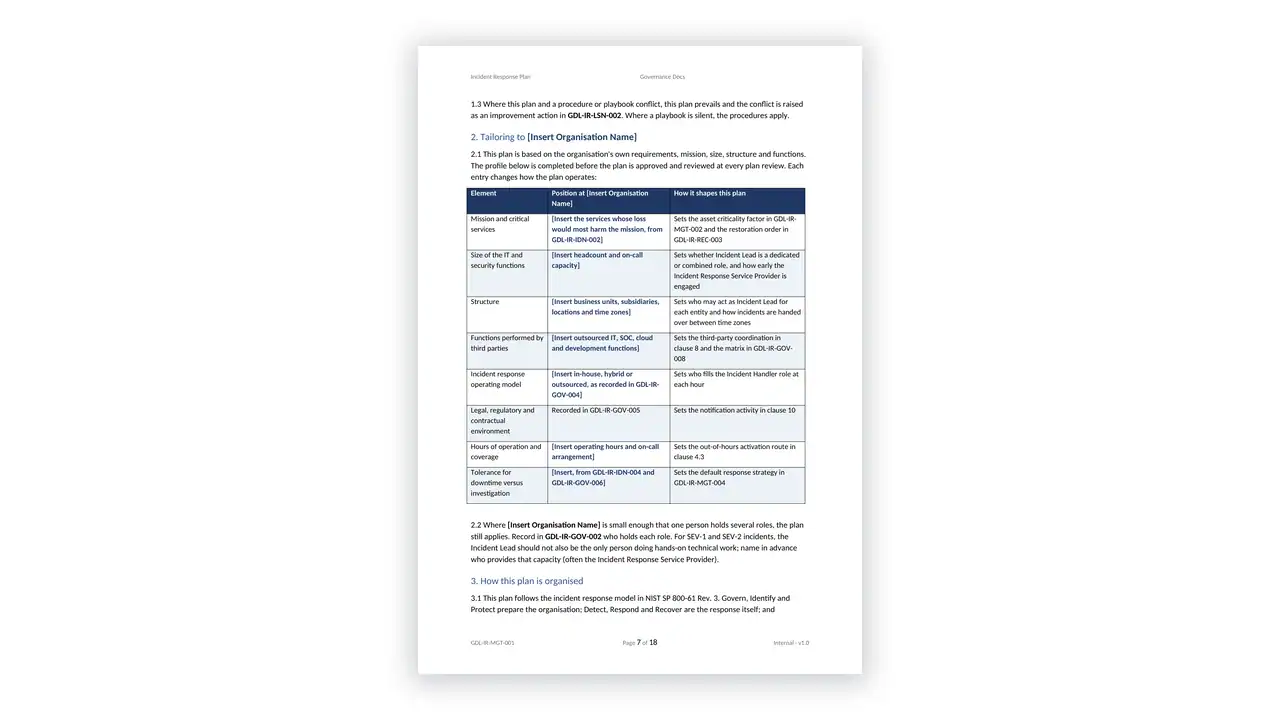
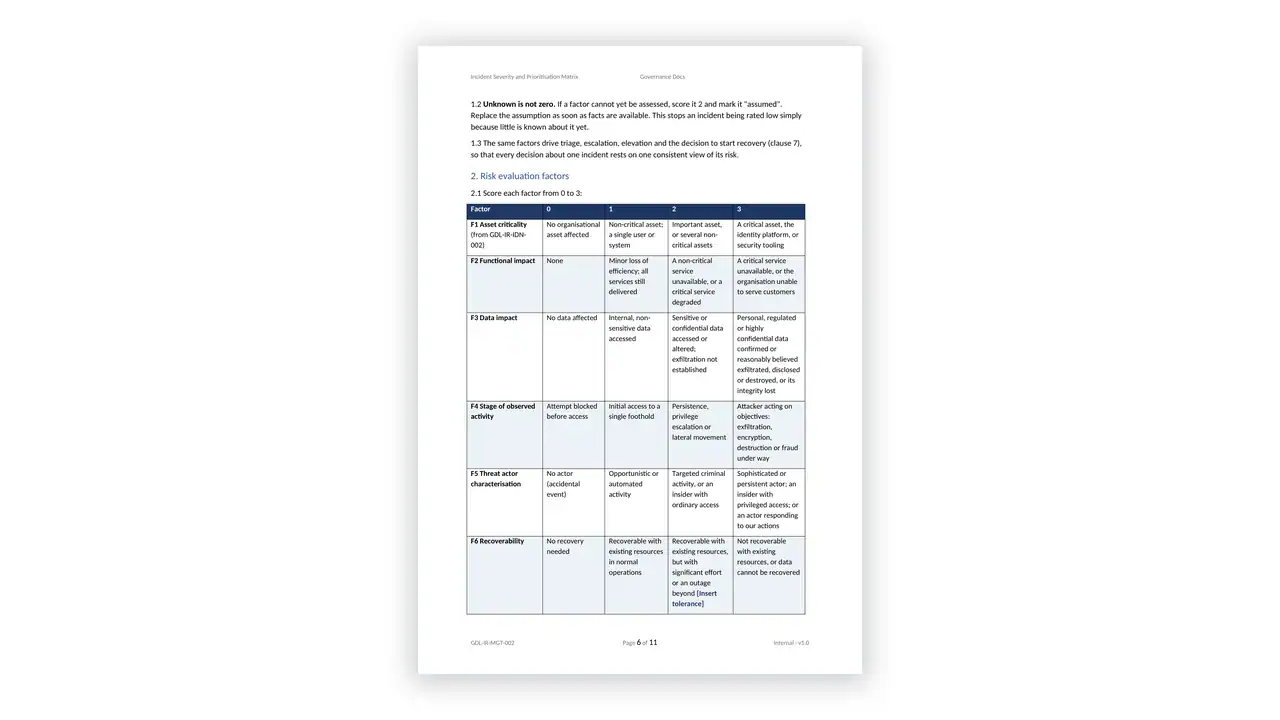
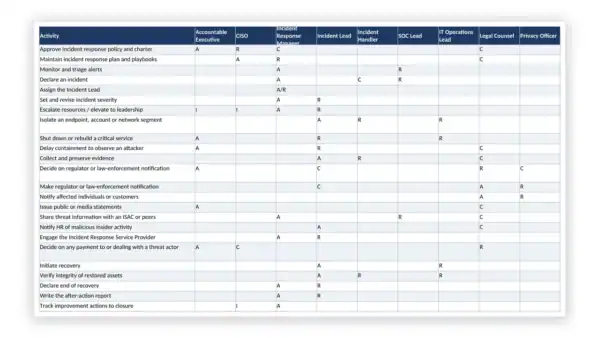
At the centre of the Incident Response Toolkit is an incident response plan template you can adopt, surrounded by 13 scenario playbooks, 6 tabletop exercise scenarios and the procedures that make the plan work under pressure: severity criteria, declaration criteria, escalation, containment authority, evidence handling, notification and recovery.
NIST published SP 800-61 Revision 3 as a final document on 3 April 2025. It supersedes Revision 2, the Computer Security Incident Handling Guide of 2012.
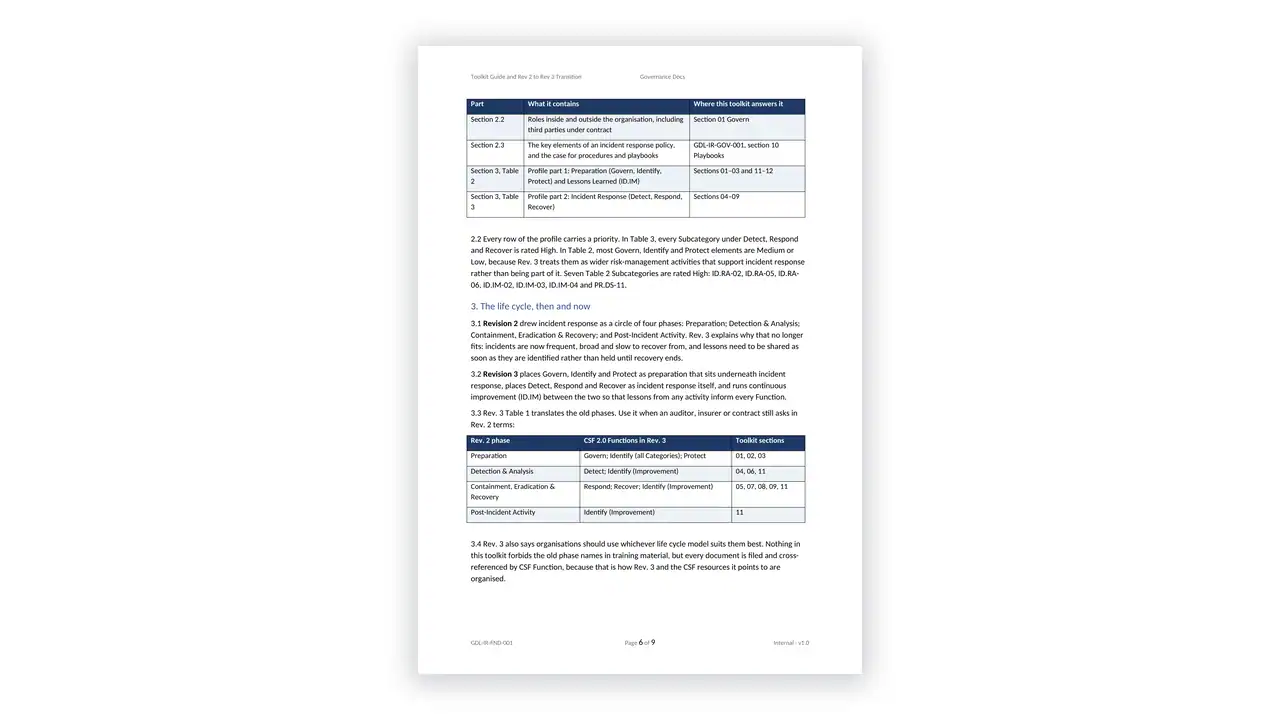
The change is structural. Revision 2 drew incident response as a four-phase circle: Preparation; Detection & Analysis; Containment, Eradication & Recovery; Post-Incident Activity. Revision 3 retired that model. It is published as a CSF 2.0 Community Profile: incident response is organised around the six CSF 2.0 Functions, and lessons learned are fed into improvement continuously rather than saved for the end.
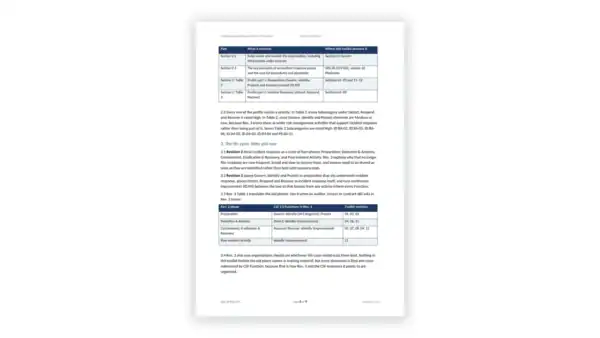
If a template you are looking at is organised around those four phases and cites “NIST 800-61”, it was built on the 2012 revision. This Incident Response Toolkit is built on Revision 3’s own structure, and its guide translates the old phases using Rev. 3’s Table 1 for anyone who still asks in the old terms.
SP 800-61 is guidance. There is no certificate, no accredited assessor and no such thing as being “800-61 compliant”. The accurate phrase is aligned to NIST SP 800-61 Rev. 3. What you can do is run a capability that meets Rev. 3’s recommendations and produce the evidence that it works — which is what the Incident Response Toolkit is for.
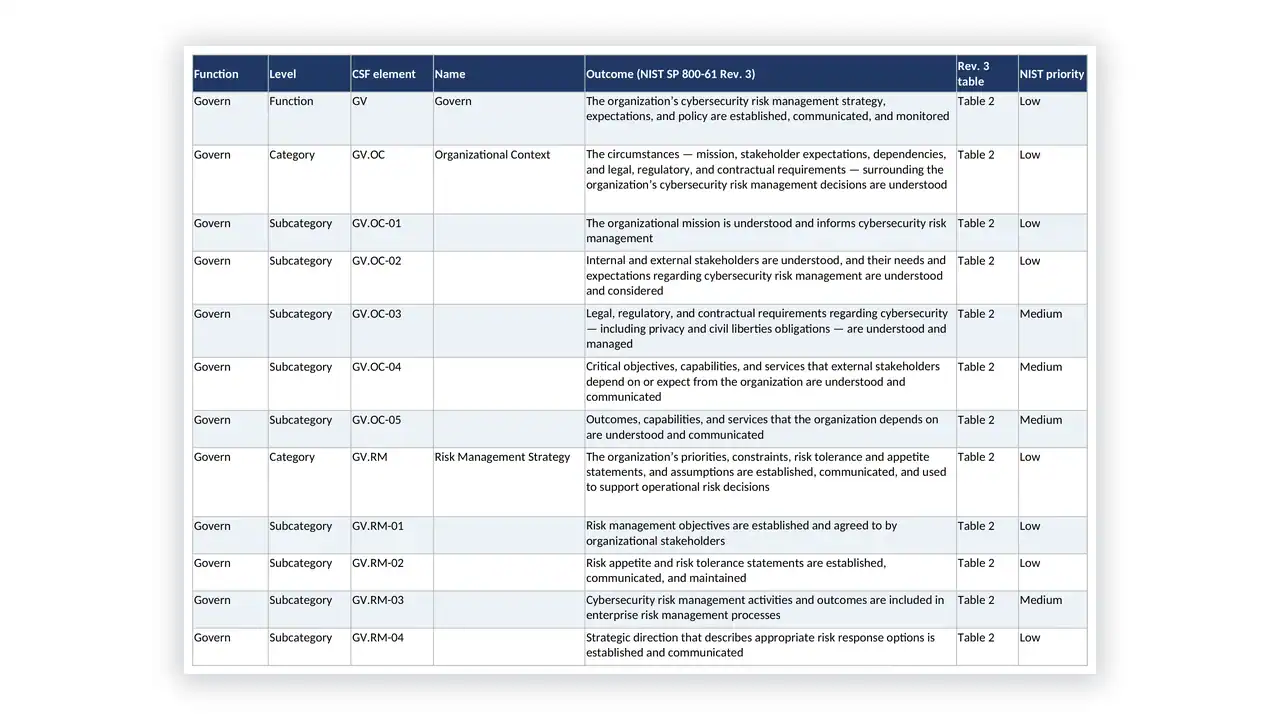
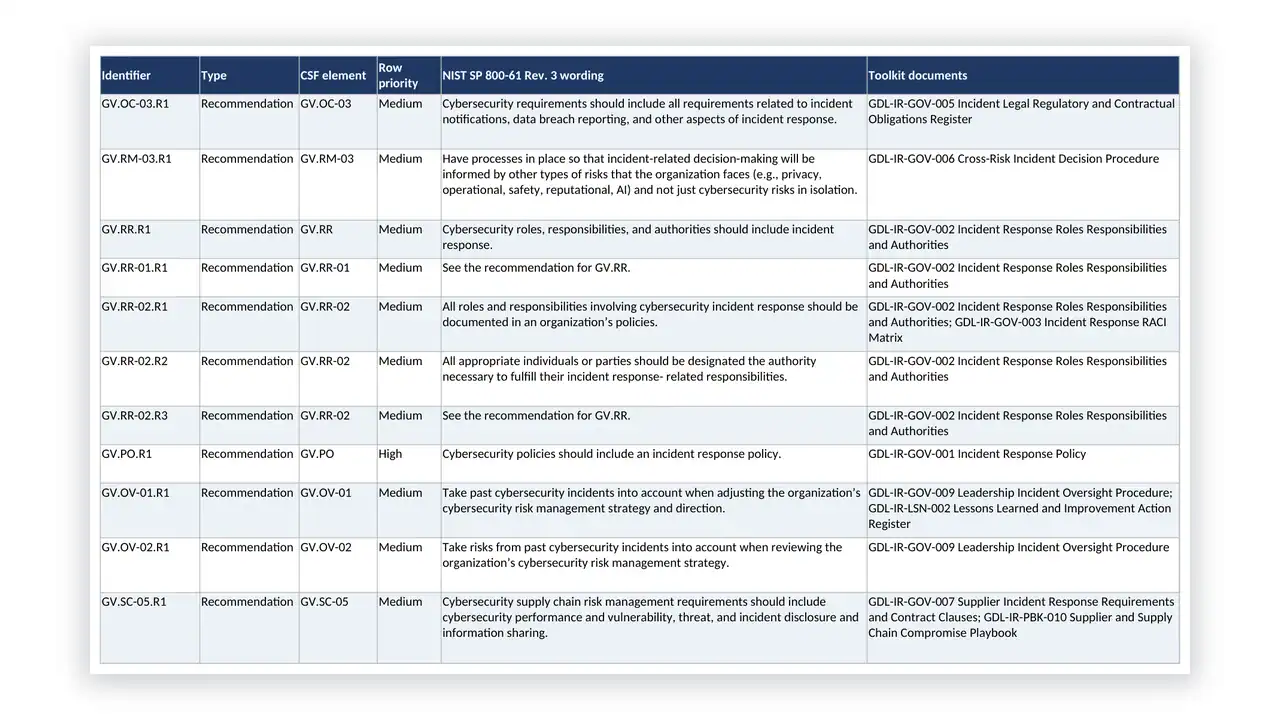
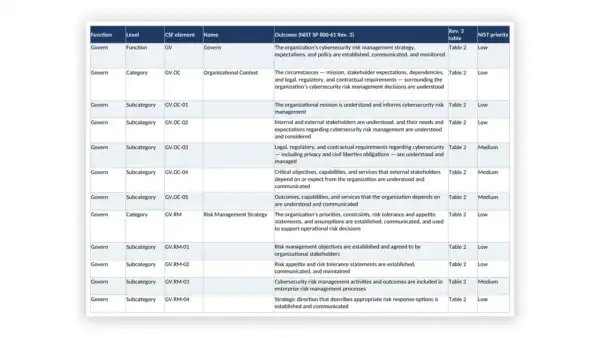
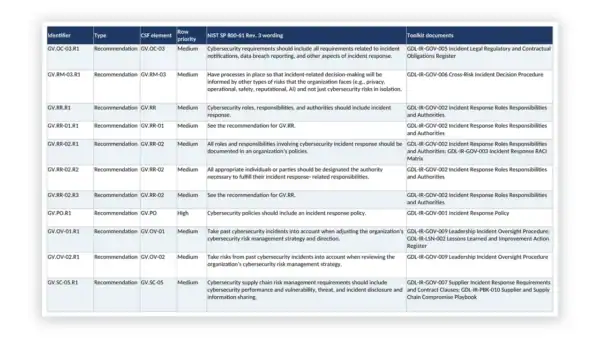
Rev. 3’s profile has 134 rows — 6 Functions, 22 Categories and 106 Subcategories — each rated High, Medium or Low for incident response, and carries 106 Recommendations and 8 Considerations. Every Detect, Respond and Recover Subcategory is rated High.
Incident Response Toolkit document, and so is every one of the 51 High-priority rows. The build fails if one is left without a home — a check we run, not a claim we make.
answers and the clause that answers it. NIST Technical Series publications are works of the United States Government (17 U.S.C. 105) and NIST permits reprinting with attribution, so you get the text, not a paraphrase.
priority beside a column for yours, because Rev. 3 tells organisations to customise the priorities.
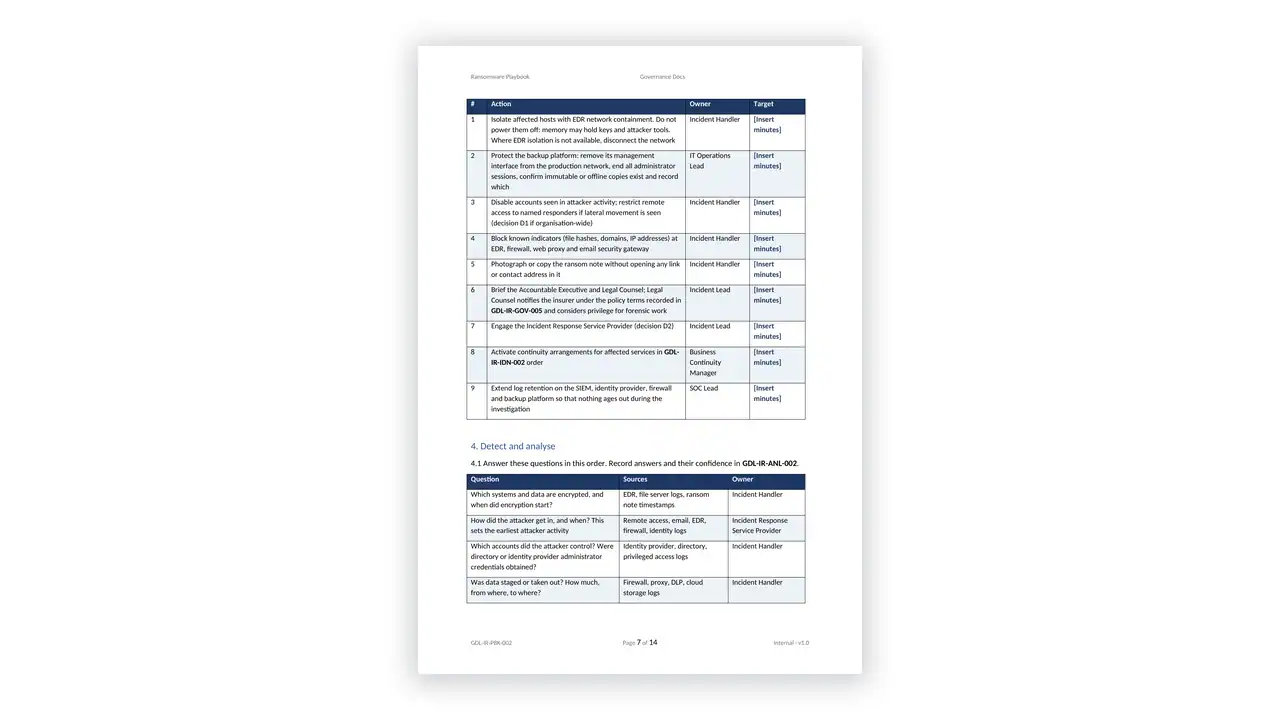
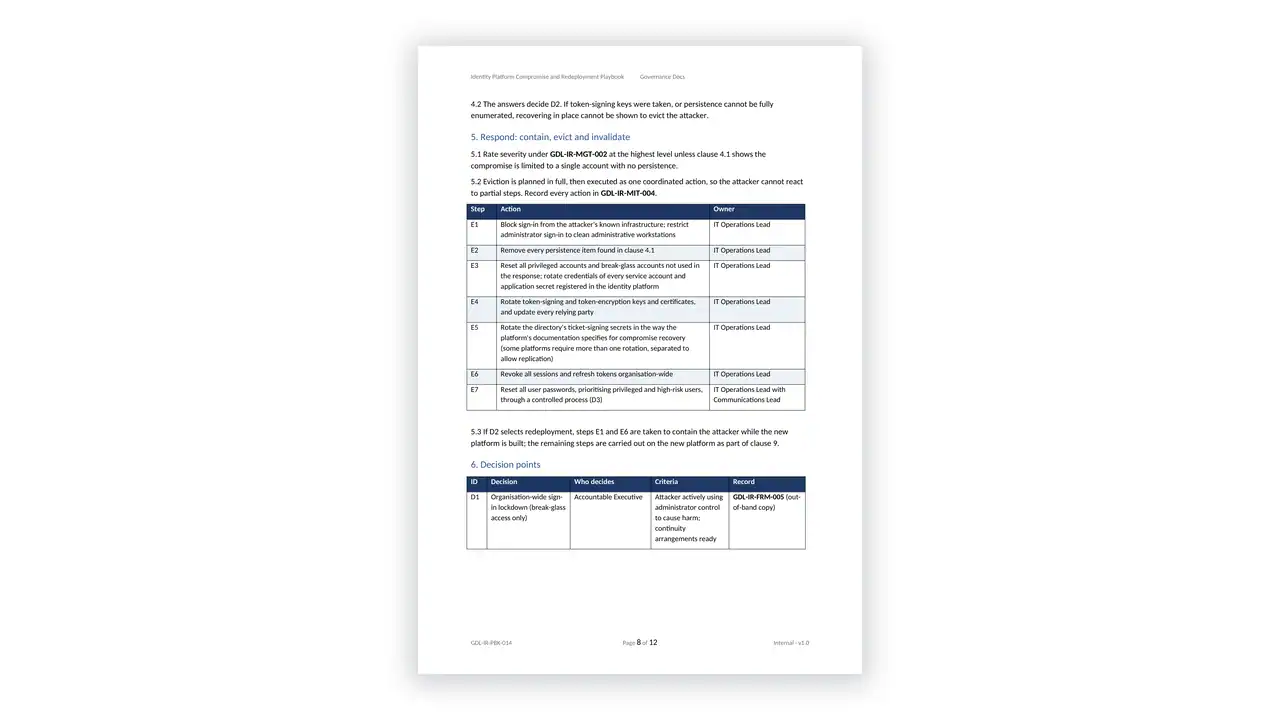
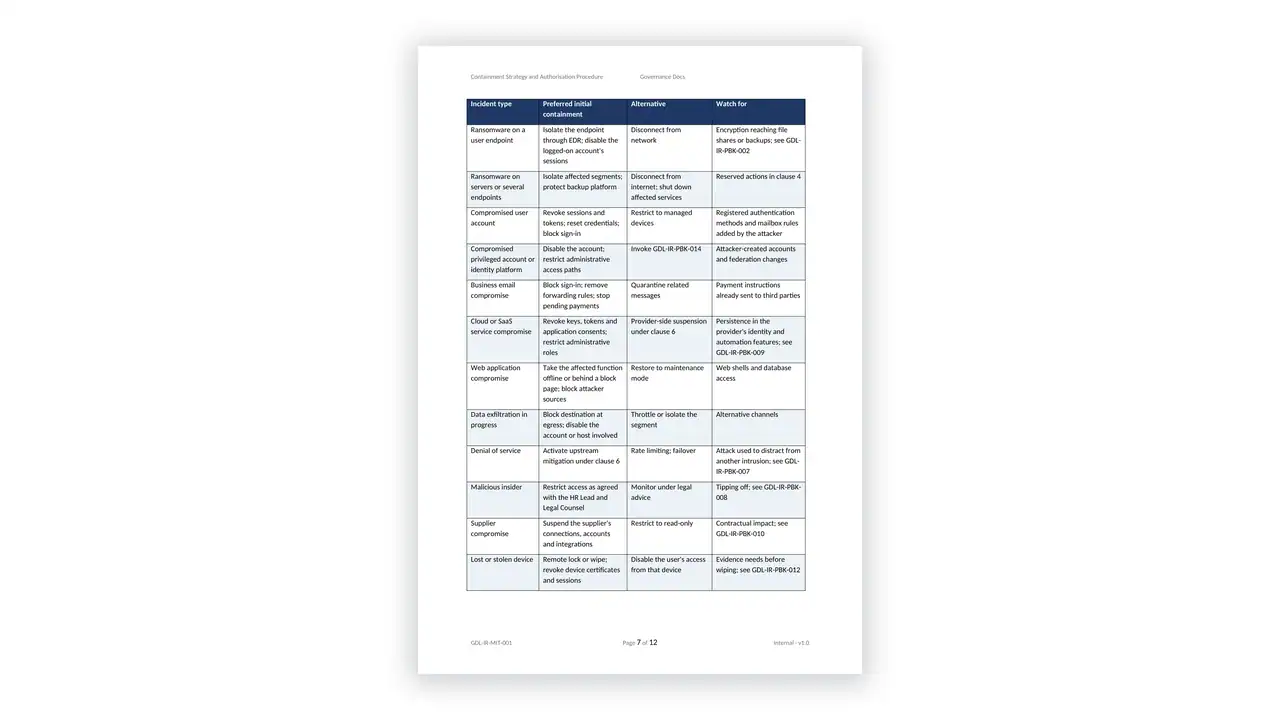
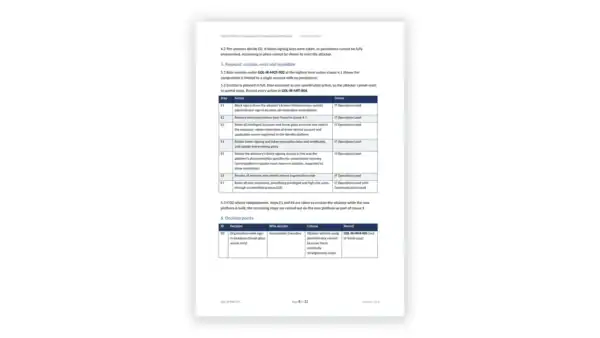
Rev. 3 recommends documenting procedures for the incident types you are most likely to face, and for processes needed urgently in an emergency; the Incident Response Toolkit does exactly that. Every playbook follows one incident response playbook template (supplied blank for your own scenarios), with first-hour actions and owners, decision points with criteria, evidence to preserve, notification triggers, recovery checks and a one-page checklist:
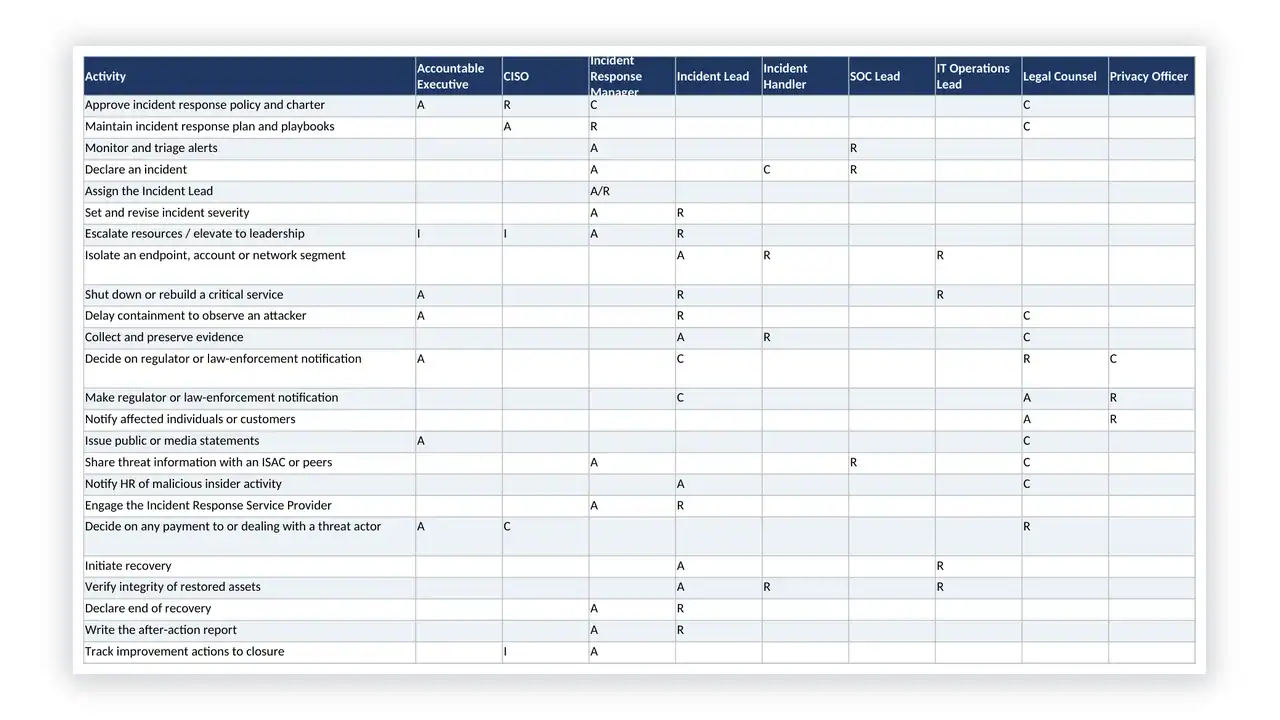
The last one exists because Rev. 3 names redeploying the primary authentication platform as its example of an urgently needed procedure. Any decision to pay or deal with a threat actor is reserved to the accountable executive with legal counsel, in every playbook that could raise it.
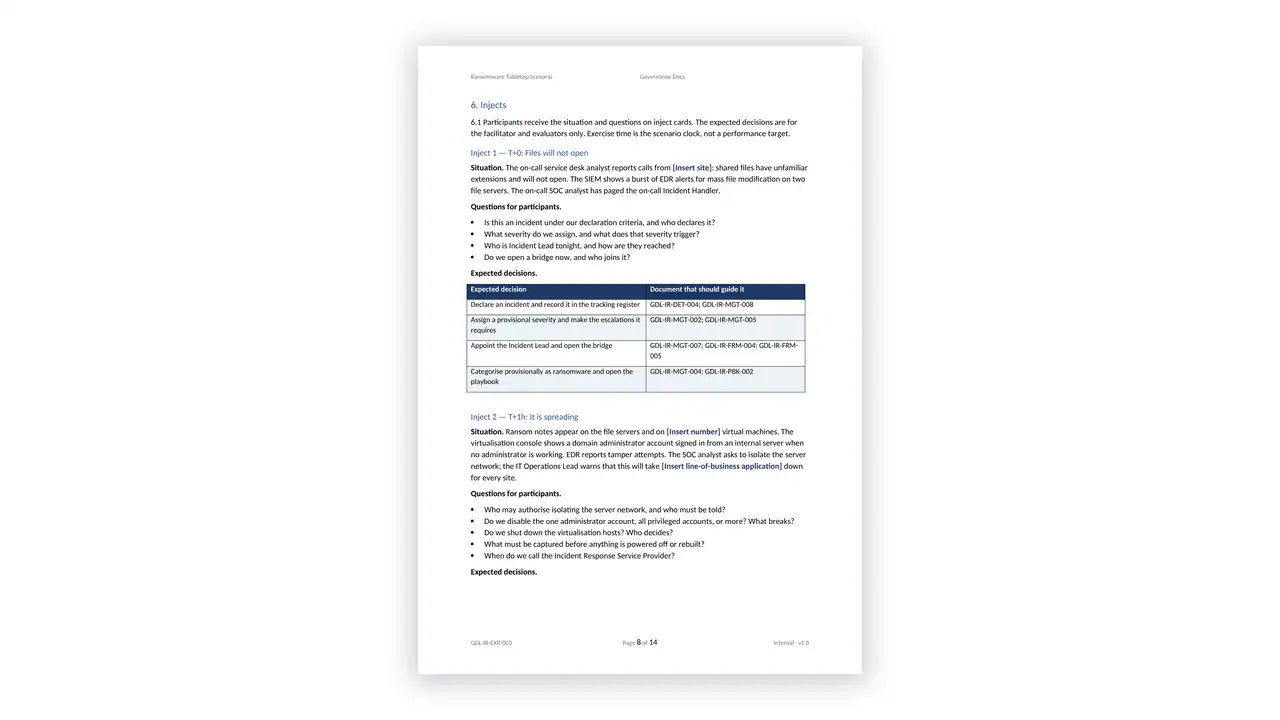
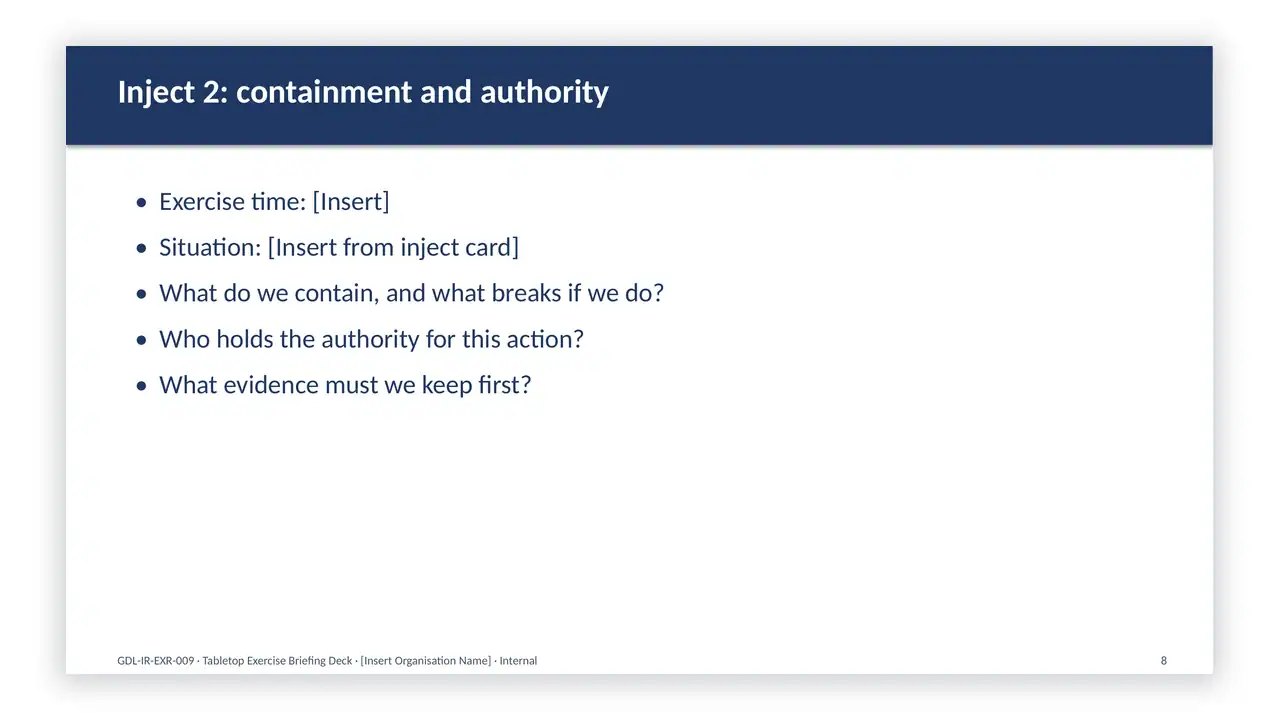
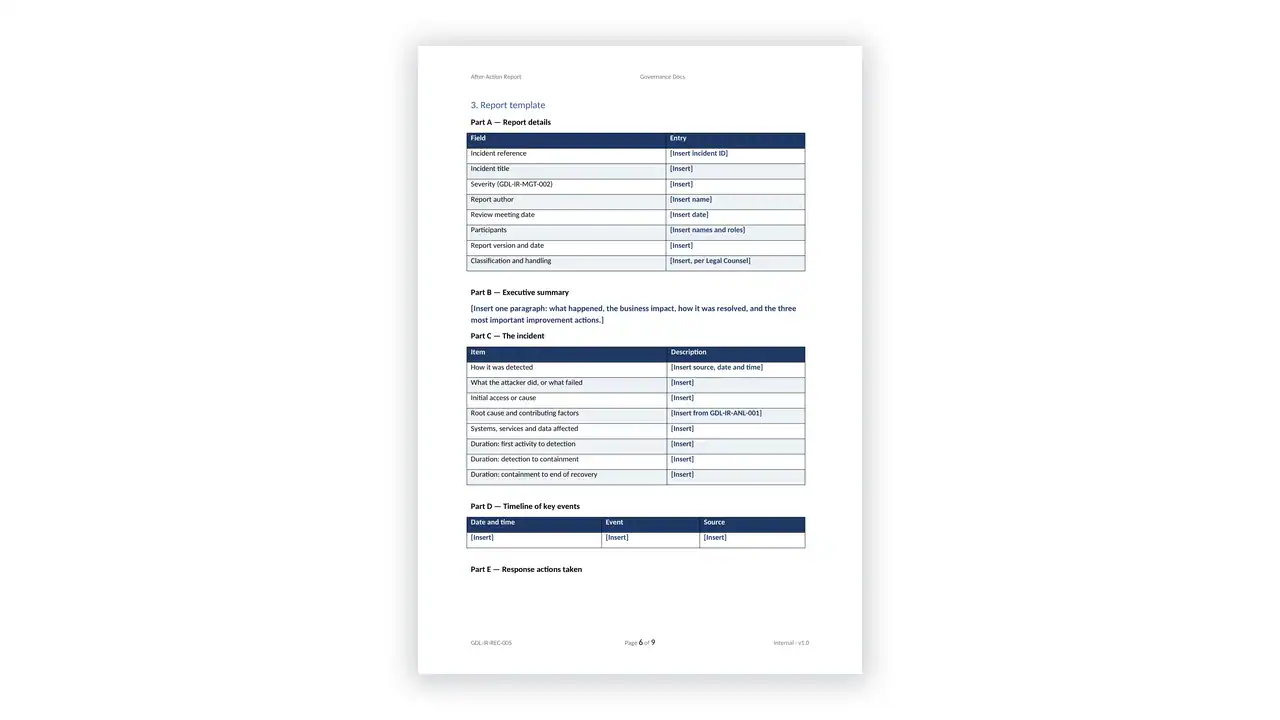
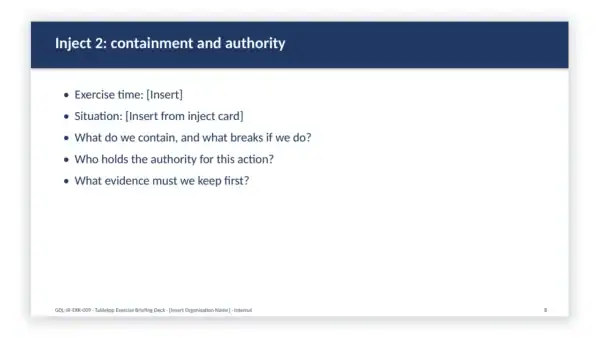
Rev. 3 rates improvements identified from tests and exercises as High priority. The Incident Response Toolkit includes an exercise programme, a facilitator guide, an evaluation and improvement plan, a tabletop exercise template briefing deck in PowerPoint with speaker notes, and 6 ready-to-run scenarios — Ransomware, Business Email Compromise, Cloud Data Breach, Malicious Insider, Supplier Compromise, Executive Crisis Decision — each with timed injects, the decisions participants should reach and the document that should guide them.
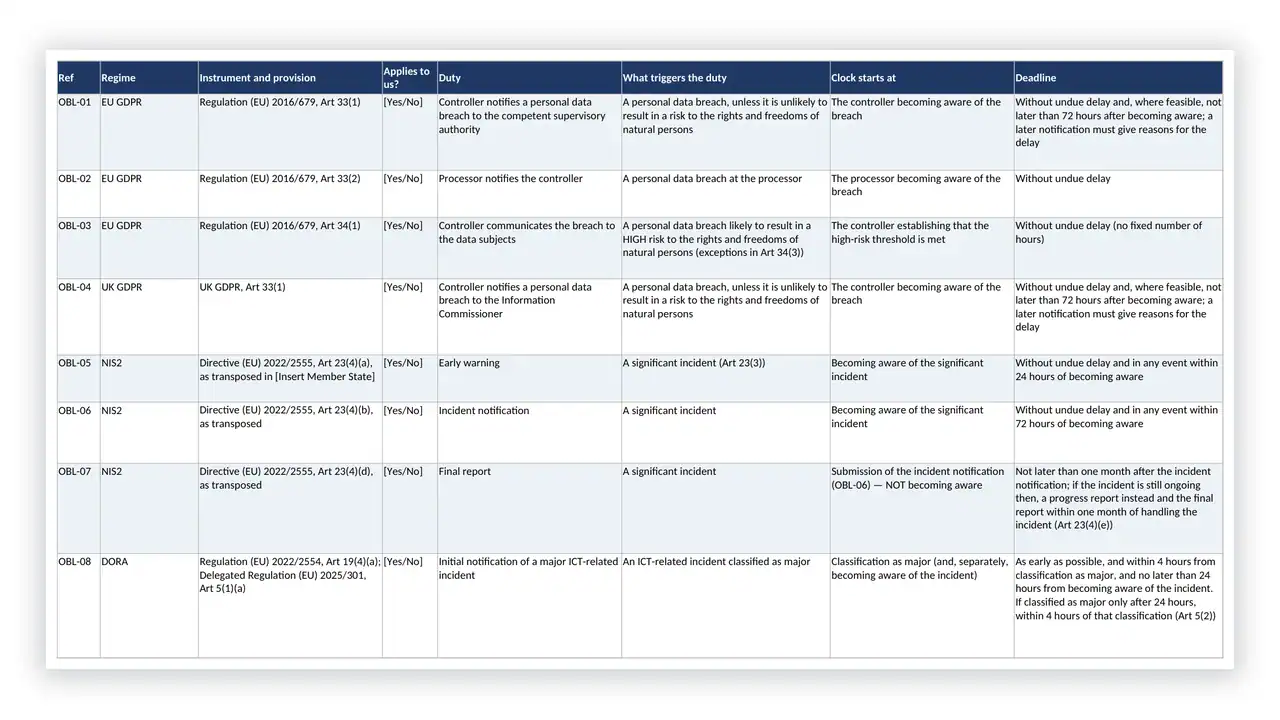
Incident notification clocks do not all start from the same event. One runs from becoming aware, another from classifying the incident, another from determining materiality, and some count business days. A procedure that says “notify within N hours of the incident” cannot be right for all of them.
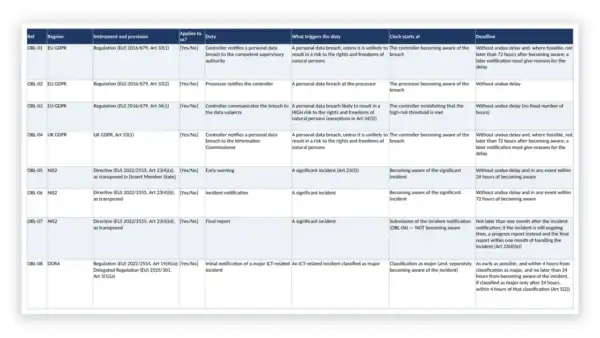
So no procedure in the Incident Response Toolkit states a statutory deadline. They all point to one obligations register that records the trigger, the event the clock starts from and the deadline in separate columns. It ships with 17 worked examples — EU GDPR, UK GDPR, NIS2, DORA, US SEC (public companies), US HIPAA, US FTC Safeguards Rule — each read against the primary legal text on 22 October 2026 and cited to the provision. They are examples, not legal advice: your legal counsel confirms which apply and adds your contracts, insurer and state laws.
Rev. 3 cites NIST IR 8286 from 2020 for risk responses; NIST superseded it with IR 8286 Revision 1 in December 2025, and the Incident Response Toolkit cites the current one. It also treats SP 800-92 Revision 1, Rev. 3’s logging reference, as what it still is: an initial public draft.
Free guides that explain the standard behind the Incident Response Toolkit:
| # | Section | Documents |
|---|---|---|
| 00 | Programme Foundation | 4 |
| 01 | Govern | 9 |
| 02 | Identify | 4 |
| 03 | Protect | 5 |
| 04 | Detect | 5 |
| 05 | Respond – Incident Management | 8 |
| 06 | Respond – Incident Analysis | 6 |
| 07 | Respond – Communication | 8 |
| 08 | Respond – Mitigation | 4 |
| 09 | Recover | 6 |
| 10 | Incident Playbooks | 14 |
| 11 | Lessons Learned and Improvement | 5 |
| 12 | Exercises and Tabletops | 10 |
| 13 | Forms and Logs | 5 |
| Total | 93 |
locked PDFs and no macros.
wording reproduced.
section 2.3 lists, and an incident response plan built on Rev. 3’s model.
indefinitely.
00 — Programme Foundation (4 documents)
01 — Govern (9 documents)
02 — Identify (4 documents)
03 — Protect (5 documents)
04 — Detect (5 documents)
05 — Respond – Incident Management (8 documents)
06 — Respond – Incident Analysis (6 documents)
07 — Respond – Communication (8 documents)
08 — Respond – Mitigation (4 documents)
09 — Recover (6 documents)
10 — Incident Playbooks (14 documents)
11 — Lessons Learned and Improvement (5 documents)
12 — Exercises and Tabletops (10 documents)
13 — Forms and Logs (5 documents)
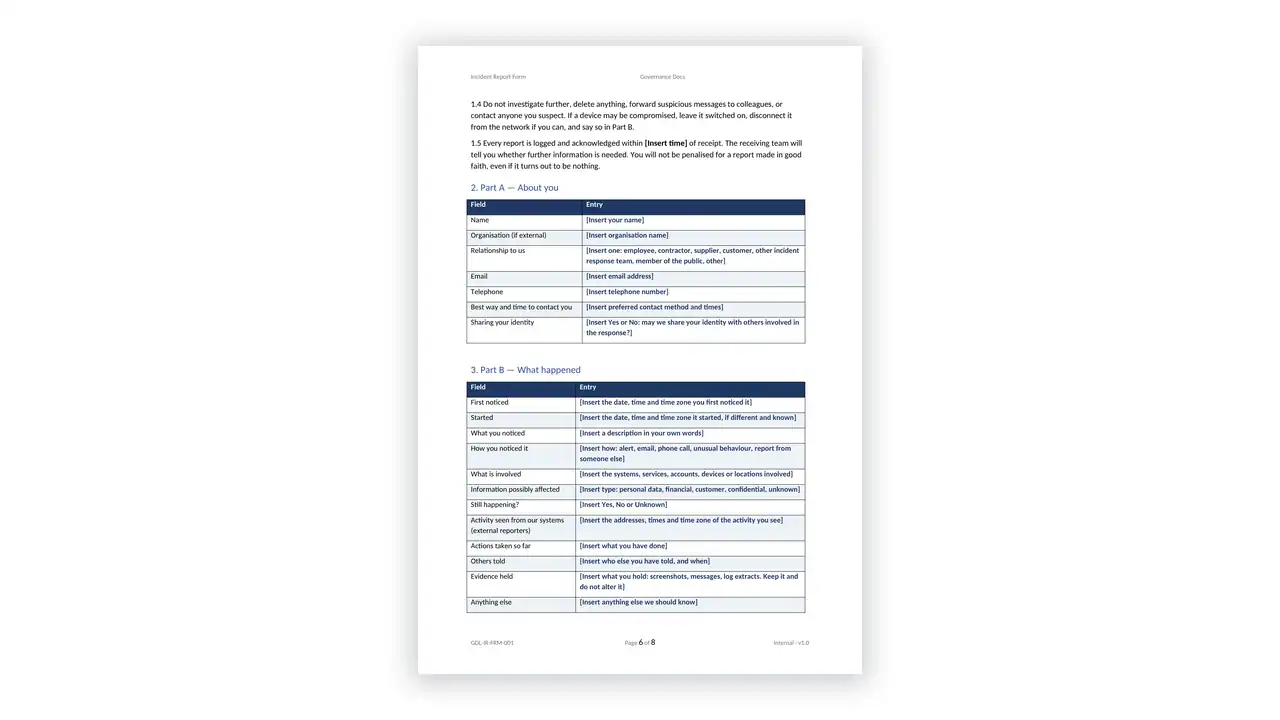
The Incident Response Toolkit is 93 editable templates for running a cybersecurity incident response capability aligned to NIST SP 800-61 Rev. 3: an incident response policy and plan, 13 scenario playbooks, 6 tabletop exercise scenarios with a briefing deck, the procedures for detection, triage, analysis, containment, communication and recovery, and the forms, logs and registers that record what happened.
Revision 3, published 3 April 2025, which superseded Revision 2. The Incident Response Toolkit follows Rev. 3’s CSF 2.0 structure rather than the four-phase model of 2012, and its guide maps the old phases onto the new structure for anyone who still asks in Rev. 2 terms.
No. SP 800-61 is NIST guidance and there is no certification against it. The accurate description is aligned to NIST SP 800-61 Rev. 3. The Incident Response Toolkit gives you the documents and the evidence trail — decisions, logs, exercise results and improvement actions — that a customer, insurer or regulator can examine.
No. SP 800-61 Rev. 3 is free from NIST. The wording of every Rev. 3 Recommendation and Consideration is also reproduced inside the Incident Response Toolkit, with attribution.
Partly, and we would rather say so. The NIST CSF Toolkit includes an incident response plan, an incident response policy and response and recovery procedures written to the CSF outcomes. The Incident Response Toolkit is the operational layer underneath: the scenario playbooks, tabletop exercises, severity and declaration criteria, forms, logs and the notification register, written to Rev. 3’s incident response recommendations. If you hold the CSF toolkit and need playbooks and exercises, this is the addition; if you need one pack for the whole Cybersecurity Framework, that is the CSF toolkit.
It gives you the incident response documents those programmes expect to see, and the obligations register includes worked examples for NIS2 and DORA reporting. It is not a substitute for a framework-specific toolkit: it does not map itself to ISO 27001 Annex A or the SOC 2 criteria.
No. The Incident Response Toolkit’s obligations register ships with worked examples read against the primary legal text on 22 October 2026, each citing its provision, so your legal counsel starts from a checked draft rather than a blank page. Counsel confirms which apply to you, adds national, state and contractual duties, and keeps the register current.
Microsoft Word (.docx), Excel (.xlsx) and PowerPoint (.pptx). Everything is editable.
You get the updated Incident Response Toolkit free for 12 months from purchase. Revision 3 is the current final version.
Free articles that explain the requirements this toolkit covers.
 Incident Response Toolkit – NIST SP 800-61 Rev 3 Plan, Playbook and Tabletop Templates$99.00



Reviews
There are no reviews yet