About Us Contact Blog
Governance DocsGovernance Docs
Which Toolkit?SoA GeneratorFree TemplatesSample ReportsFind the Right AssessmentRecords of Processing (ROPA)Data Privacy Impact AssessmentLegitimate Interests AssessmentTransfer Impact AssessmentPrivacy Risk AssessmentGDPR Gap AssessmentUK GDPR Gap AssessmentCCPA/CPRA Gap AssessmentISO 27701 Gap AssessmentHIPAA Gap AssessmentISO 27001 Risk AssessmentThird-Party Risk AssessmentSoA GeneratorISO 27001 Assessment Tool (Excel)ISO 27001 Gap AssessmentSOC 2 Gap AssessmentNIST CSF 2.0 Gap AssessmentNIST SP 800-53 Gap AssessmentNIST RMF Gap AssessmentCIS Controls Gap AssessmentPCI DSS 4.0 Gap AssessmentNIS2 Gap AssessmentCMMC 2.0 Gap AssessmentNIST SP 800-171 Gap AssessmentFedRAMP Gap AssessmentBSI C5 Gap AssessmentIEC 62443 Gap AssessmentSAMA CSF Gap AssessmentNCA ECC Gap AssessmentISO 20000 Gap AssessmentAI Risk AssessmentAI Impact AssessmentISO 42001 Gap AssessmentEU AI Act Gap AssessmentBusiness Impact AnalysisContinuity Risk AssessmentISO 22301 Assessment Tool (Excel)ISO 22301 Gap AssessmentDORA Gap AssessmentISO 9001 Gap AssessmentISO 13485 Gap AssessmentIATF 16949 Gap AssessmentISO 14001 Gap AssessmentISO 45001 Gap AssessmentISO 45001 Assessment Tool (Excel)HACCP Gap AssessmentEnterprise Risk AssessmentISO 31000 Gap AssessmentData Governance Gap AssessmentProject Management Gap AssessmentAll Gap AssessmentsISO 27001 Internal AuditISO 42001 Internal AuditAboutBlogContactMy AccountCart
Browse Toolkits
Governance Docs
  • Browse All Toolkits
  • Information Security & Cybersecurity
  • Data Privacy & Protection
  • Governance, Risk & Compliance
  • Quality Management
  • Health, Safety & Environment
  • AI Governance

My Account

CART

No products in the cart.

Category: Articles

Sub-processor transfer assessment showing exporter, processor and chain of sub-processors with onward transfers

Sub-Processor Transfer Assessment Guide 2026

Governance Docs30th September 2026

How to run a sub-processor transfer assessment: SCC sub-processor clauses, mapping the chain, onward transfers, questions for processors,…
Read More
Vendor risk scoring model combining inherent risk factors and control ratings into a residual score and tier

Vendor Risk Scoring Guide 2026: Methods and Examples

Governance Docs30th September 2026

How to build vendor risk scoring: inherent risk factors, control assessment, residual scores, weights, thresholds, overrides, calibration and…
Read More
ERM maturity model showing five levels from ad hoc to leading across governance, process, culture and technology

ERM Maturity Model Guide 2026: Levels and Assessment

Governance Docs30th September 2026

What an ERM maturity model is, typical levels, attributes to assess, how to run an assessment, how to…
Read More
AI impact assessment for recruitment across sourcing, screening, interviews and selection with candidate harms

AI Impact Assessment for Recruitment Guide 2026

Governance Docs30th September 2026

How to run an AI impact assessment for recruitment: legal context, mapping the hiring funnel, harms to candidates,…
Read More
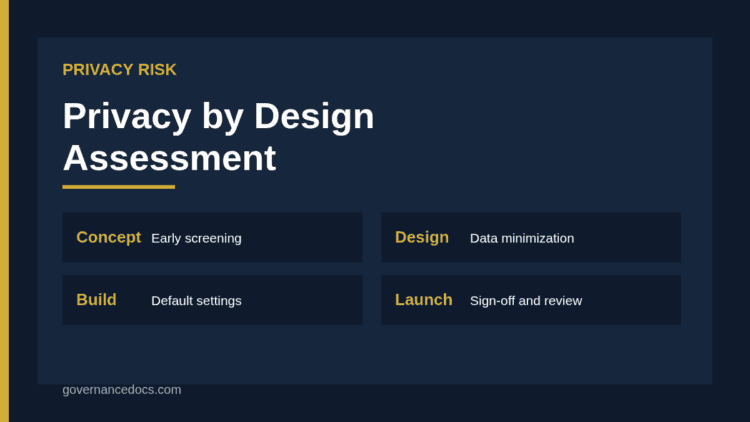
Privacy by design risk assessment mapped across product stages from concept to launch and review

Privacy by Design Risk Assessment Guide 2026

Governance Docs30th September 2026

How to run a privacy by design risk assessment: Article 25 duties, when to assess in the product…
Read More
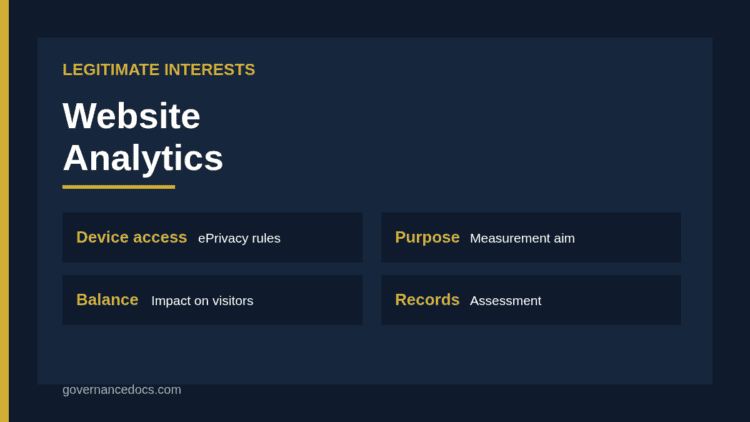
Legitimate interests for website analytics decision path from data type to cookie rules and balancing test

Legitimate Interests for Website Analytics Guide 2026

Governance Docs30th September 2026

When legitimate interests for website analytics can be used: GDPR test, ePrivacy consent rules for cookies, server-side and…
Read More
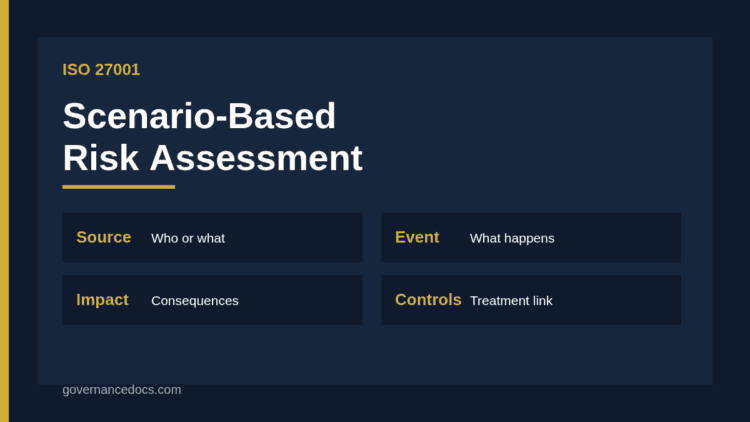
ISO 27001 scenario-based risk assessment flow from threat source and event to consequence and control

ISO 27001 Scenario-Based Risk Assessment Guide 2026

Governance Docs30th September 2026

How an ISO 27001 scenario-based risk assessment works: what a scenario contains, how to build a library, rate…
Read More
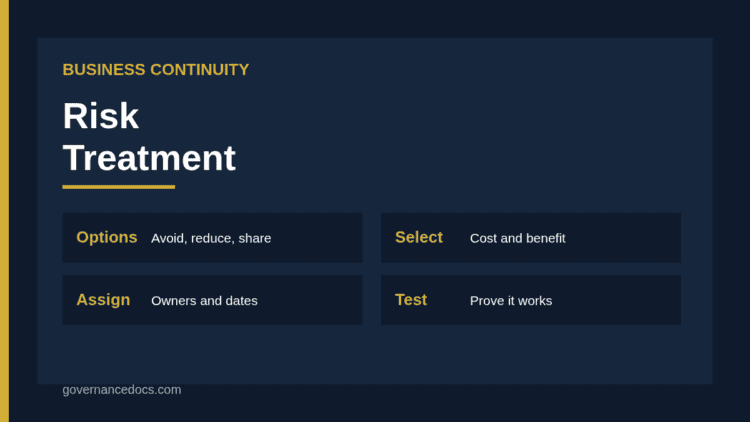
Business continuity risk treatment options linking assessed risks to prevention, protection and recovery measures

Business Continuity Risk Treatment Guide 2026

Governance Docs30th September 2026

How business continuity risk treatment works: options to avoid, reduce, transfer or accept, choosing strategies, costing, ownership, plans…
Read More
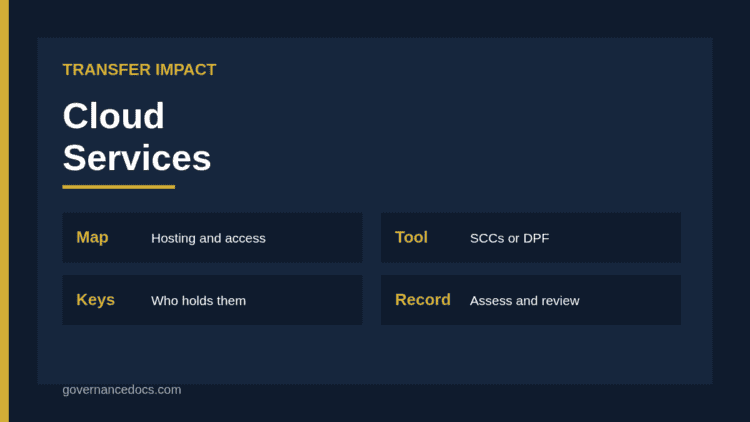
Transfer impact assessment for cloud services showing hosting region, support access, encryption keys and legal review

Transfer Impact Assessment for Cloud Services Guide 2026

Governance Docs30th September 2026

How to run a transfer impact assessment for cloud services: mapping hosting and support access, transfer tool, encryption…
Read More
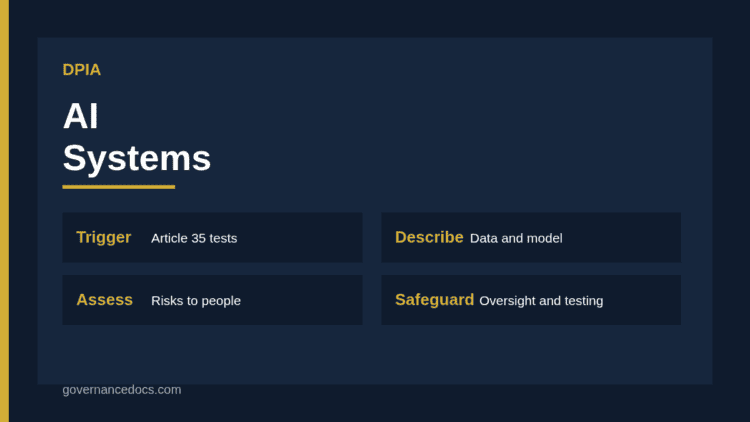
DPIA for AI showing model description, data flows, risks to individuals, safeguards and sign-off

DPIA for AI Systems Guide 2026

Governance Docs30th September 2026

When and how to complete a DPIA for AI: triggers under Article 35, describing models and data, necessity,…
Read More
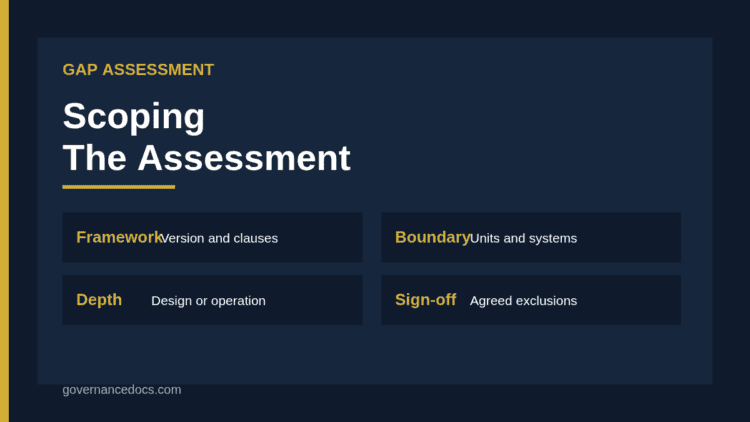
Gap assessment scoping diagram showing framework, organizational boundary, systems, sites and exclusions

Gap Assessment Scoping Guide 2026

Governance Docs30th September 2026

How to scope a gap assessment: choosing the framework and version, setting organizational and system boundaries, applicability, depth,…
Read More
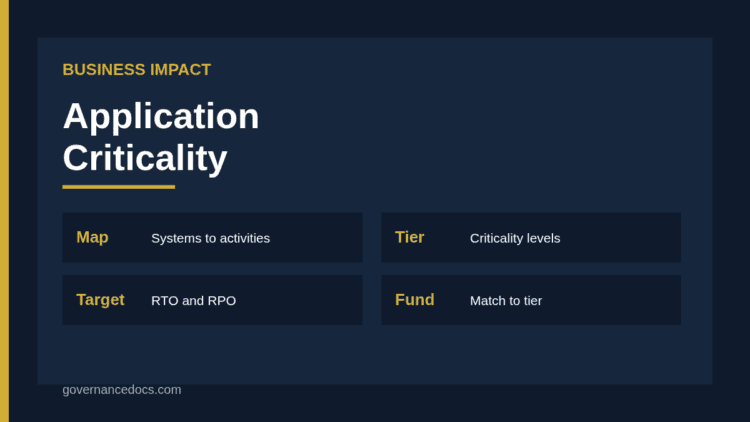
Application criticality tiers derived from business impact analysis with recovery time targets per tier

Application Criticality from a BIA Guide 2026

Governance Docs30th September 2026

How to rate application criticality from a business impact analysis: mapping systems to activities, deriving tiers, setting recovery…
Read More

    ←
  • 1
  • …
  • 22
  • 23
  • 24
  • 25
  • 26
  • …
  • 106
  • →

Recent Posts

ISO 14001 surveillance audit infographic showing the cycle years, audit time, eight review areas and the 2029 transition deadline
ISO 14001 Surveillance Audit: The Complete 2026 Guide

November 3, 2026

ISO 27001 toolkit contents shown as three layers: clause 4 to 10 records, 93 Annex A controls and supporting registers
ISO 27001 Toolkit: What a Complete One Contains (2026)

November 2, 2026

ISO 9001 recertification audit three-year cycle showing surveillance in years 1 and 2 and recertification in year 3
ISO 9001 Recertification Audit: The Complete 2026 Guide

November 1, 2026

ISO 9001 surveillance audit: eight required review areas, the 12-month window and the 2029 transition deadline
ISO 9001 Surveillance Audit: The Complete 2026 Guide

October 31, 2026

ISO 27001 software installation under Annex A 8.19: production systems and end-user endpoints
ISO 27001 Software Installation: Essential A.8.19 Guide 2026

October 31, 2026

Categories

  • Articles
  • DORA
  • GDPR
  • HIPAA
  • ISO 27001
  • ISO 42001 & AI governance
  • ISO 9001
  • Management systems
  • NIS2
  • Security frameworks
  • SOC 2
Governance DocsGovernance Docs

Reliable ISO & compliance documentation toolkits that help your business meet regulatory standards with ease.

Governance Docs LLC
1209 Mountain Road Pl NE, Suite R
Albuquerque, NM 87110, USA
[email protected]
+1 505 289 2455

Toolkits

  • ISO 27001:2022
  • GDPR
  • SOC 2
  • PCI-DSS v4.0
  • HIPAA
  • ISO 42001
  • All toolkits →

Company

  • About Us
  • Blog
  • Contact
  • FAQ
  • Which toolkit do I need?
  • Request a custom toolkit
  • Free templates
  • SoA generator
  • Assessments
  • Sample reports
  • RSS feeds

Policies

  • Privacy Policy
  • Terms & Conditions
  • Refund & Return Policy
  • Delivery Policy
  • Manage cookies
Browse by topicISO 27001ISO 42001 & AI governanceGDPRSOC 2HIPAANIS2DORAISO 9001Management systemsSecurity frameworks
© 2026 Governance Docs LLC. All rights reserved.
Secure checkoutstripeVISA