

ITIL 5 Explained: The Complete 2026 Guide
ITIL 5 changed the value chain, the practice categories and added AI governance. Here is what actually changed…
CART
ITIL 5 changed the value chain, the practice categories and added AI governance. Here is what actually changed…
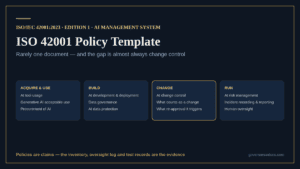
An ISO 42001 policy template is rarely one document. The 7 policies an AI management system needs, the…
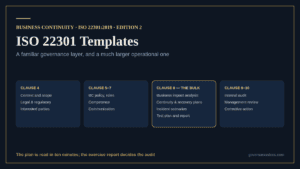
ISO 22301 templates split into a familiar governance layer and a much larger operational one. What clause 8…
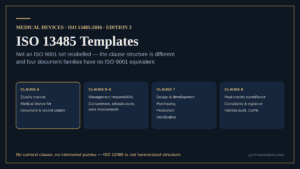
ISO 13485 templates are not an ISO 9001 set relabelled. The clause structure, the 4 documents unique to…
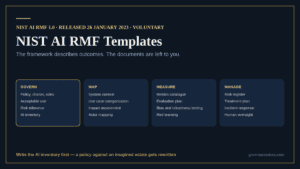
NIST AI RMF templates are the question the framework will not answer. What Govern, Map, Measure and Manage…
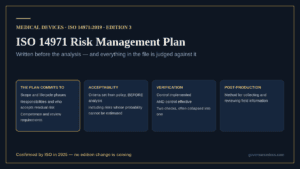
The ISO 14971 risk management plan is written before the analysis and judged against everything after it. What…
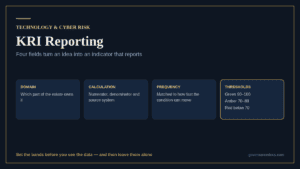
KRI reporting fails when indicators are picked for easy data. The 4 fields every KRI needs, RAG thresholds…
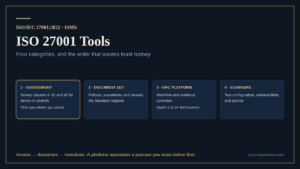
ISO 27001 tools range from a spreadsheet to a GRC platform. The 4 categories, what an assessment tool…
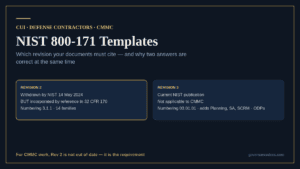
NIST 800-171 templates must cite the right revision. Why CMMC still requires Rev 2 though NIST withdrew it,…
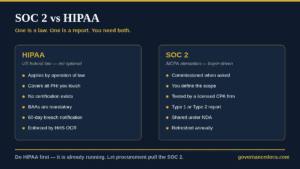
SOC 2 vs HIPAA compared: HIPAA is US federal law, SOC 2 is an AICPA attestation. See what…
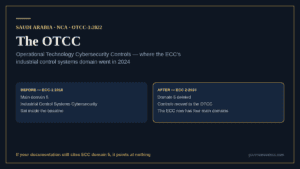
The OTCC absorbed the ECC’s industrial control systems domain in 2024. What it covers, how it differs from…
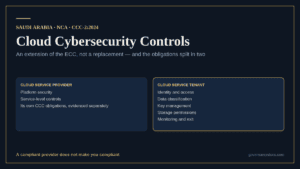
The Cloud Cybersecurity Controls split obligations between provider and tenant. CCC-2:2024, the 6 responsibility areas, and what changed…
October 23, 2026
October 23, 2026

October 22, 2026

October 22, 2026
October 22, 2026