About Us Contact Blog
Governance DocsGovernance Docs
Which Toolkit?SoA GeneratorFree TemplatesSample ReportsFind the Right AssessmentRecords of Processing (ROPA)Data Privacy Impact AssessmentLegitimate Interests AssessmentTransfer Impact AssessmentPrivacy Risk AssessmentGDPR Gap AssessmentUK GDPR Gap AssessmentCCPA/CPRA Gap AssessmentISO 27701 Gap AssessmentHIPAA Gap AssessmentISO 27001 Risk AssessmentThird-Party Risk AssessmentSoA GeneratorISO 27001 Assessment Tool (Excel)ISO 27001 Gap AssessmentSOC 2 Gap AssessmentNIST CSF 2.0 Gap AssessmentNIST SP 800-53 Gap AssessmentNIST RMF Gap AssessmentCIS Controls Gap AssessmentPCI DSS 4.0 Gap AssessmentNIS2 Gap AssessmentCMMC 2.0 Gap AssessmentNIST SP 800-171 Gap AssessmentFedRAMP Gap AssessmentBSI C5 Gap AssessmentIEC 62443 Gap AssessmentSAMA CSF Gap AssessmentNCA ECC Gap AssessmentISO 20000 Gap AssessmentAI Risk AssessmentAI Impact AssessmentISO 42001 Gap AssessmentEU AI Act Gap AssessmentBusiness Impact AnalysisContinuity Risk AssessmentISO 22301 Assessment Tool (Excel)ISO 22301 Gap AssessmentDORA Gap AssessmentISO 9001 Gap AssessmentISO 13485 Gap AssessmentIATF 16949 Gap AssessmentISO 14001 Gap AssessmentISO 45001 Gap AssessmentISO 45001 Assessment Tool (Excel)HACCP Gap AssessmentEnterprise Risk AssessmentISO 31000 Gap AssessmentData Governance Gap AssessmentProject Management Gap AssessmentAll Gap AssessmentsAboutBlogContactMy AccountCart
FOX v.2.4.9
Browse Toolkits
Governance Docs
  • Browse All Toolkits
  • Information Security & Cybersecurity
  • Data Privacy & Protection
  • Governance, Risk & Compliance
  • Quality Management
  • Health, Safety & Environment
  • AI Governance

My Account

CART

No products in the cart.

Category: Articles

NIST CSF to 800-53 mapping — NIST CSF to 800-53 Mapping: A Clear Guide to All 106

NIST CSF to 800-53 Mapping: A Clear Guide to All 106

Governance Docs06th September 2026

NIST maps all 106 CSF 2.0 outcomes to SP 800-53 Rev 5 with 740 control references. How to…
Read More
NIST CSF 2.0 vs 1.1 — NIST CSF 2.0 vs 1.1: The 79 Subcategories That Changed

NIST CSF 2.0 vs 1.1: The 79 Subcategories That Changed

Governance Docs06th September 2026

CSF 2.0 withdrew 79 Subcategories and removed 12 Categories. The full mapping, the 16 outcomes with no predecessor,…
Read More
NIST CSF GOVERN function — The NIST CSF GOVERN Function: All 31 Outcomes Explained

The NIST CSF GOVERN Function: All 31 Outcomes Explained

Governance Docs06th September 2026

The GOVERN function is 31 of the 106 CSF 2.0 outcomes across six Categories, ten of them supply…
Read More
NIST CSF Tiers — NIST CSF Tiers: A Clear Guide to the 4 Implementation Tiers

NIST CSF Tiers: A Clear Guide to the 4 Implementation Tiers

Governance Docs06th September 2026

The 4 NIST CSF Tiers explained, including the two axes CSWP 29 scores them on and why Tier…
Read More
Is ISO 45001 a legal requirement: voluntary standard versus mandatory law

Is ISO 45001 a Legal Requirement? The Clear Answer for 2026

Governance Docs06th September 2026

Is ISO 45001 a legal requirement? No, in any country. But the OH&S law underneath it is mandatory.…
Read More
ISO climate change amendment to clauses 4.1 and 4.2

ISO Climate Change Amendment: 2 Sentences, 31 Standards, 1 Trap

Governance Docs06th September 2026

The ISO climate change amendment added 2 sentences to clauses 4.1 and 4.2 across 31 standards. What auditors…
Read More
Annex SL harmonized structure: the ten ISO management system clauses

Annex SL Explained: The Best Guide to 10 ISO Clauses

Governance Docs06th September 2026

Annex SL is the harmonized structure behind ISO 9001, 14001, 27001 and 45001. The 10 clauses explained, the…
Read More
CertiKit alternative: comparison of CertiKit and Governance Docs toolkit pricing

CertiKit Alternative: The Best Options Before It Closes in 2026

Governance Docs06th September 2026

CertiKit closes on 18 December 2026. A CertiKit alternative covering all nine of their frameworks plus 66 more,…
Read More
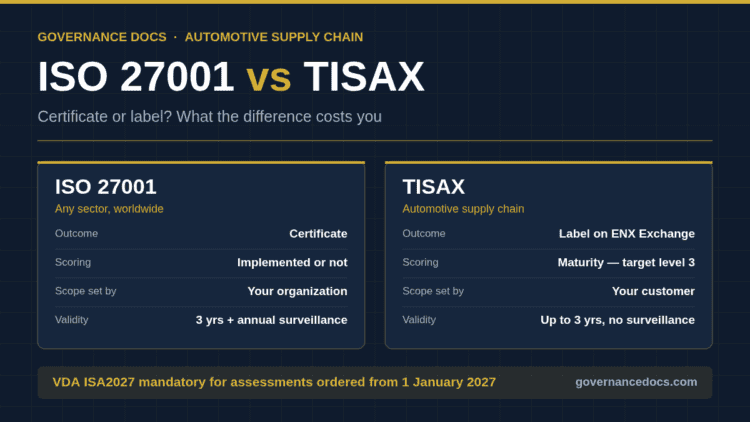
ISO 27001 vs TISAX comparison showing certificate versus ENX label, scoring and validity

ISO 27001 vs TISAX: The Complete 2026 Supplier Guide

Governance Docs06th September 2026

ISO 27001 vs TISAX compared for automotive suppliers: certificate versus ENX label, maturity level 3 scoring, AL2 vs…
Read More
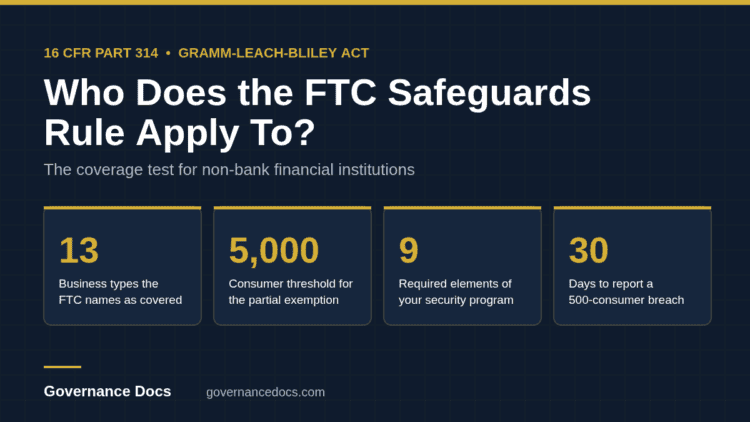
Infographic explaining who does the FTC Safeguards Rule apply to under 16 CFR Part 314

Who Does the FTC Safeguards Rule Apply To? The Complete 2026 Guide

Governance Docs05th September 2026

The FTC Safeguards Rule covers 13 types of non-bank financial institution, not just banks. Here is the two-part…
Read More
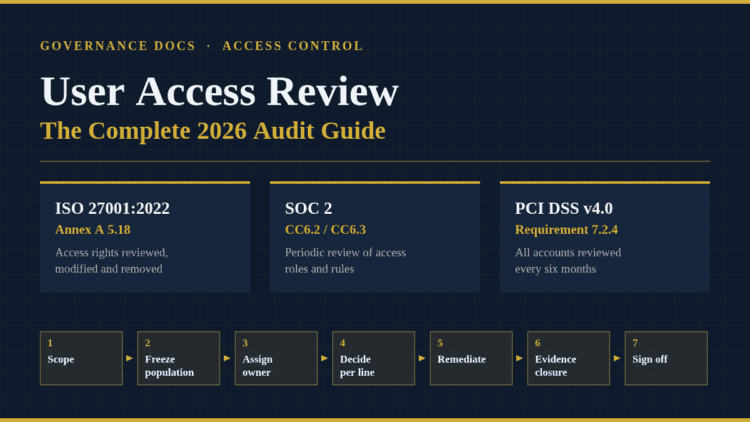
User access review process mapped to ISO 27001 Annex A 5.18, SOC 2 CC6.3 and PCI DSS 7.2.4

User Access Review: A Complete 2026 Guide for ISO 27001 and SOC 2

Governance Docs04th September 2026

A user access review is the control auditors test hardest. Here is the seven-step process, the ISO 27001…
Read More
NIST Privacy Framework data map — NIST Privacy Framework Data Map: How to Build One (ID.IM-P8)

NIST Privacy Framework Data Map: How to Build One (ID.IM-P8)

Governance Docs03rd September 2026

A NIST Privacy Framework data map shows every data action, store and party. What to include, how much…
Read More

    ←
  • 1
  • …
  • 62
  • 63
  • 64
  • 65
  • 66
  • …
  • 100
  • →

Recent Posts

iso 30301 — ISO 30301 vs ISO 15489: Which Records Standard Do You Need?
ISO 30301 vs ISO 15489: Which Records Standard Do You Need?

October 12, 2026

legal hold — Legal Hold: How to Suspend Records Destruction Properly (2026)
Legal Hold: How to Suspend Records Destruction Properly (2026)

October 12, 2026

records retention schedule — Records Retention Schedule: How to Build One in 2026
Records Retention Schedule: How to Build One in 2026

October 12, 2026

iso 15489 — ISO 15489 Explained: The Records Management Standard in 2026
ISO 15489 Explained: The Records Management Standard in 2026

October 12, 2026

records management metadata — Records Management Metadata: What to Capture and Why (2026)
Records Management Metadata: What to Capture and Why (2026)

October 12, 2026

Categories

  • Articles
  • DORA
  • GDPR
  • HIPAA
  • ISO 27001
  • ISO 42001 & AI governance
  • ISO 9001
  • Management systems
  • NIS2
  • Security frameworks
  • SOC 2
Governance DocsGovernance Docs

Reliable ISO & compliance documentation toolkits that help your business meet regulatory standards with ease.

Governance Docs LLC
1209 Mountain Road Pl NE, Suite R
Albuquerque, NM 87110, USA
info@governancedocs.com
+1 505 289 2455

Toolkits

  • ISO 27001:2022
  • GDPR
  • SOC 2
  • PCI-DSS v4.0
  • HIPAA
  • ISO 42001
  • All toolkits →

Company

  • About Us
  • Blog
  • Contact
  • FAQ
  • Which toolkit do I need?
  • Free templates
  • SoA generator
  • Assessments
  • Sample reports
  • RSS feeds

Policies

  • Privacy Policy
  • Terms & Conditions
  • Refund & Return Policy
  • Delivery Policy
  • Manage cookies
Browse by topicISO 27001ISO 42001 & AI governanceGDPRSOC 2HIPAANIS2DORAISO 9001Management systemsSecurity frameworks
© 2026 Governance Docs LLC. All rights reserved.
Secure checkoutstripeVISA