Gap Analysis Remediation Plan: The Essential 2026 Guide to Closing Findings Governance Docs29th September 2026 How to turn gap assessment findings into a remediation plan: the ten fields, prioritization by severity and effort,… Read More
Privacy Risk Register: The Essential 2026 Guide with 12 Fields for Harm to Individuals Governance Docs29th September 2026 How to build a privacy risk register: 12 fields, scoring harm to individuals using GDPR Recital 75, links… Read More
Supplementary Measures for Data Transfers: The Essential 2026 Guide to the EDPB Six Steps Governance Docs29th September 2026 When a transfer tool is not enough, supplementary measures may be needed. The EDPB six steps, the three… Read More
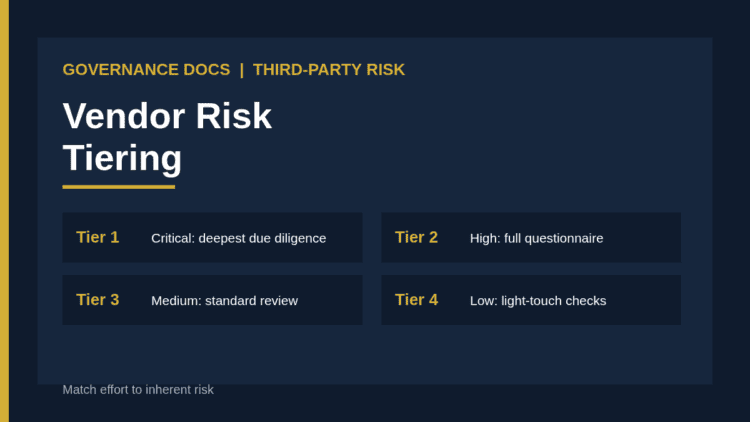
Vendor Risk Tiering: The Essential 2026 Guide to 4 Tiers, Criteria and Review Cycles Governance Docs29th September 2026 How to tier vendors by risk: four tiers, weighted scoring criteria, override rules and how each tier drives… Read More
ROPA Exemption: The Essential 2026 Guide to GDPR Article 30(5) for Small Organizations Governance Docs29th September 2026 Does a small organization need a record of processing activities? The ROPA exemption in GDPR Article 30(5), the… Read More
Legitimate Interests Right to Object: The Essential 2026 Guide to GDPR Article 21 Governance Docs29th September 2026 What happens when someone objects to processing based on legitimate interests: the Article 21 test, the absolute marketing… Read More
ISO 27001 Risk Assessment Methodology: The Essential 2026 Guide to Choosing an Approach Governance Docs29th September 2026 How to define an ISO 27001 risk assessment methodology: what clause 6.1.2 requires, asset-based versus event-based approaches and… Read More
Risk Heat Map: The Essential 2026 Guide to Building a 5×5 Matrix Executives Trust Governance Docs29th September 2026 How to build a risk heat map: define 5x5 likelihood and impact scales, set colour bands from risk… Read More
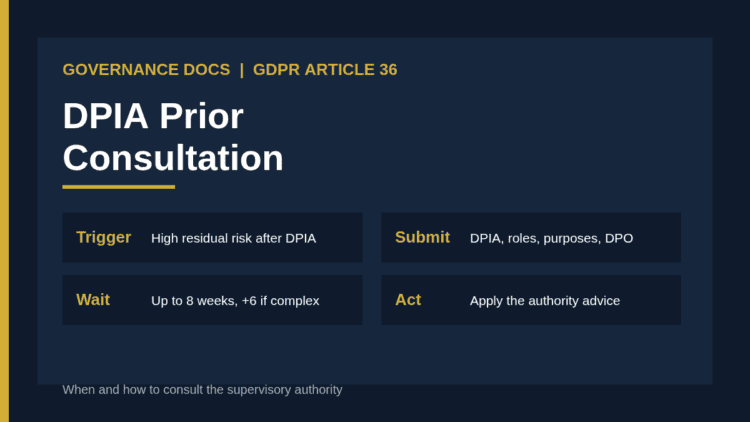
DPIA Prior Consultation: The Essential 2026 Guide to GDPR Article 36 Governance Docs29th September 2026 When a DPIA leaves high residual risk, GDPR Article 36 requires prior consultation. Learn the trigger, the submission… Read More
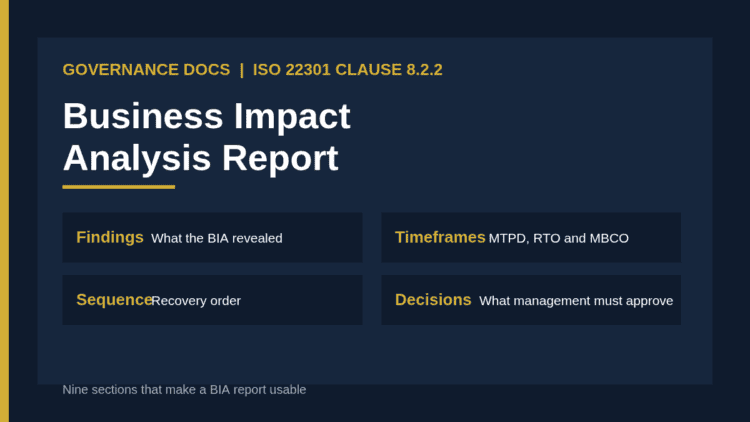
Business Impact Analysis Report: The Essential 2026 Guide to Structure and Findings Governance Docs29th September 2026 How to structure a business impact analysis report for ISO 22301: nine sections, clear findings, the recovery sequence… Read More
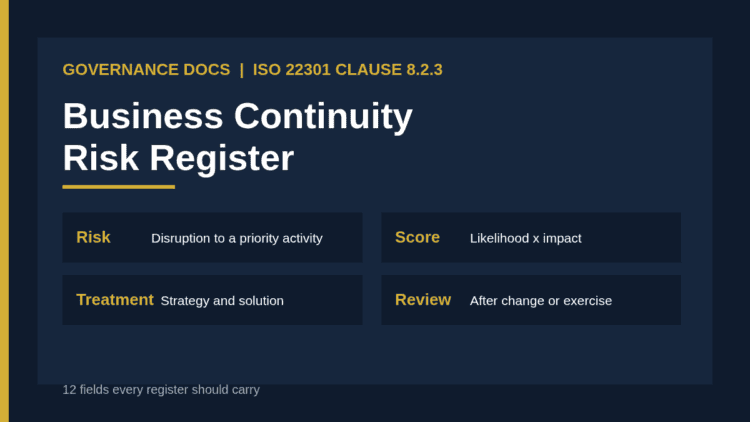
Business Continuity Risk Register: The Essential 2026 Guide with 12 Fields Governance Docs29th September 2026 A practical guide to building a business continuity risk register for ISO 22301: the 12 fields, BIA-linked scoring,… Read More
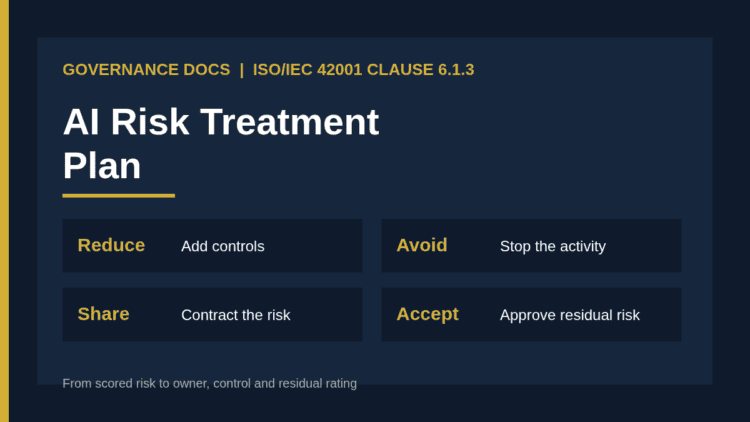
AI Risk Treatment Plan: The Essential 2026 Guide to ISO 42001 Clause 6.1.3 Governance Docs29th September 2026 How to build an AI risk treatment plan under ISO 42001 clause 6.1.3: options, columns, Annex A links… Read More