NIST CSF Supply Chain Risk Management: GV.SC Guide 2026 Governance Docs29th September 2026 A practical guide to NIST CSF supply chain risk management under the GV.SC category, from supplier criticality to… Read More
AMLR Politically Exposed Persons: EDD Steps 2026 Governance Docs29th September 2026 How to handle AMLR politically exposed persons: approval, source of wealth, monitoring and the 12-month post-office rule. Read More
PCI PIN Key Destruction and Compromise Response 2026 Governance Docs29th September 2026 How PCI PIN key destruction and compromise procedures work: retirement, witnessed destruction, key logs, backups and replacement. Read More
GENIUS Act State Qualified Issuers: The $10 Billion Line 2026 Governance Docs29th September 2026 How GENIUS Act state qualified issuers work: the $10 billion cap, state regime certification and the path to… Read More
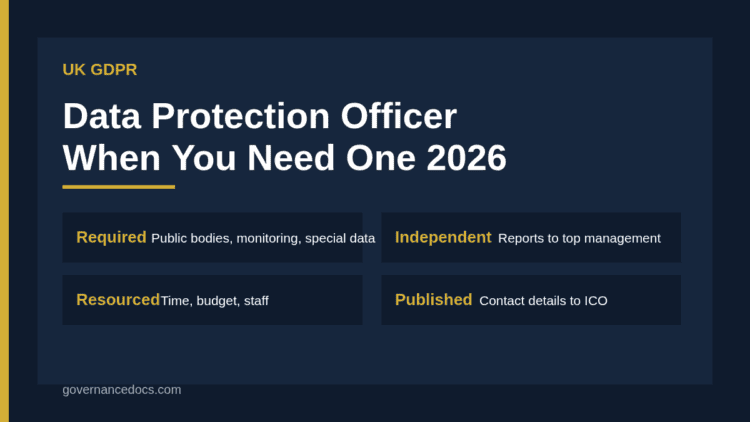
UK GDPR Data Protection Officer: When You Need One 2026 Governance Docs29th September 2026 When a UK GDPR data protection officer is required, what the role does, how to avoid conflicts of… Read More
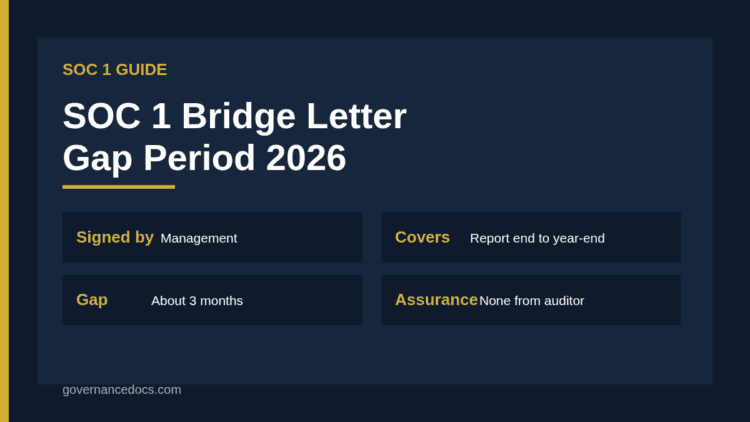
SOC 1 Bridge Letter: What It Covers and Its Limits 2026 Governance Docs29th September 2026 What a SOC 1 bridge letter is, what to include, who signs it and where its assurance stops. Read More
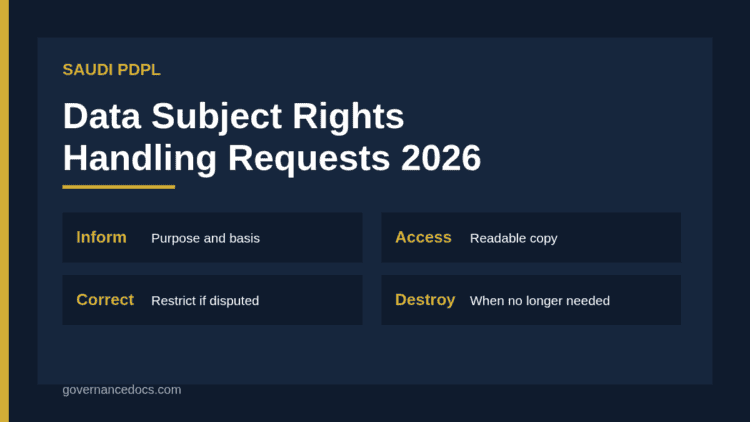
Saudi PDPL Data Subject Rights: Handling Requests 2026 Governance Docs29th September 2026 How to handle Saudi PDPL data subject rights: the five rights, response deadlines and a practical request-handling workflow. Read More
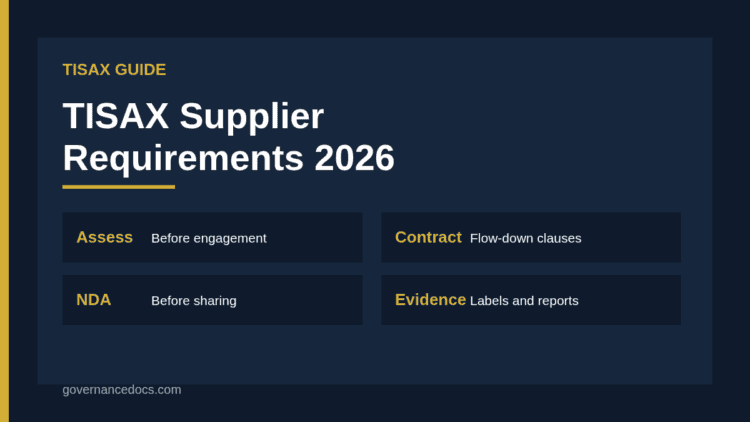
TISAX Supplier Requirements: Subcontractors and Flow-Down 2026 Governance Docs29th September 2026 How TISAX supplier requirements work: risk assessment before engagement, contract flow-down, NDAs and the evidence assessors ask for. Read More
GovRAMP Continuous Monitoring: Reports and Escalation 2026 Governance Docs29th September 2026 What providers must do after GovRAMP verification: reports, POA&M timelines, annual assessment, change notice and escalation. Read More
NQA-1 Supplier Evaluation: Requirement 7 Guide for 2026 Governance Docs29th September 2026 A practical guide to NQA-1 Requirement 7: how to evaluate suppliers, keep an approved supplier list and prepare… Read More
NIST 800-53 SR Family: Supply Chain Risk Controls 2026 Governance Docs29th September 2026 A guide to the twelve controls in the NIST 800-53 SR family, how to build a supply chain… Read More
NIST Privacy Framework Govern-P: Governance Guide 2026 Governance Docs29th September 2026 A guide to the Govern-P function of the NIST Privacy Framework, with its four categories, evidence and steps… Read More