About Us Contact Blog
Governance DocsGovernance Docs
Which Toolkit?SoA GeneratorFree TemplatesSample ReportsFind the Right AssessmentRecords of Processing (ROPA)Data Privacy Impact AssessmentLegitimate Interests AssessmentTransfer Impact AssessmentPrivacy Risk AssessmentGDPR Gap AssessmentUK GDPR Gap AssessmentCCPA/CPRA Gap AssessmentISO 27701 Gap AssessmentHIPAA Gap AssessmentISO 27001 Risk AssessmentThird-Party Risk AssessmentSoA GeneratorISO 27001 Assessment Tool (Excel)ISO 27001 Gap AssessmentSOC 2 Gap AssessmentNIST CSF 2.0 Gap AssessmentNIST SP 800-53 Gap AssessmentNIST RMF Gap AssessmentCIS Controls Gap AssessmentPCI DSS 4.0 Gap AssessmentNIS2 Gap AssessmentCMMC 2.0 Gap AssessmentNIST SP 800-171 Gap AssessmentFedRAMP Gap AssessmentBSI C5 Gap AssessmentIEC 62443 Gap AssessmentSAMA CSF Gap AssessmentNCA ECC Gap AssessmentISO 20000 Gap AssessmentAI Risk AssessmentAI Impact AssessmentISO 42001 Gap AssessmentEU AI Act Gap AssessmentBusiness Impact AnalysisContinuity Risk AssessmentISO 22301 Assessment Tool (Excel)ISO 22301 Gap AssessmentDORA Gap AssessmentISO 9001 Gap AssessmentISO 13485 Gap AssessmentIATF 16949 Gap AssessmentISO 14001 Gap AssessmentISO 45001 Gap AssessmentISO 45001 Assessment Tool (Excel)HACCP Gap AssessmentEnterprise Risk AssessmentISO 31000 Gap AssessmentData Governance Gap AssessmentProject Management Gap AssessmentAll Gap AssessmentsAboutBlogContactMy AccountCart
FOX v.2.4.9
Browse Toolkits
Governance Docs
  • Browse All Toolkits
  • Information Security & Cybersecurity
  • Data Privacy & Protection
  • Governance, Risk & Compliance
  • Quality Management
  • Health, Safety & Environment
  • AI Governance

My Account

CART

No products in the cart.

Category: Articles

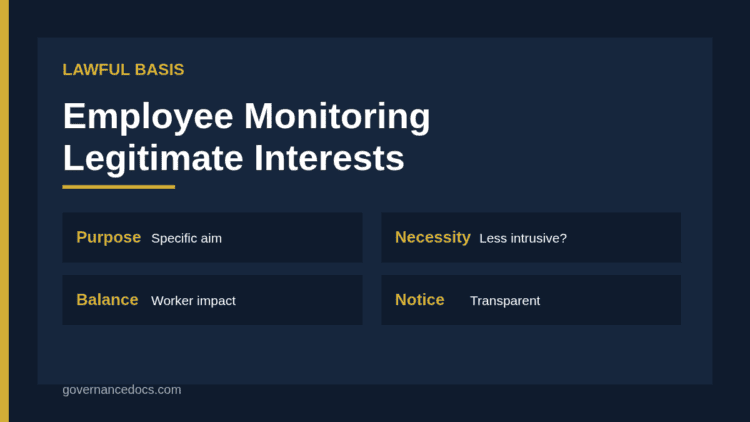
Employee monitoring legitimate interests assessment weighing employer and worker interests

Employee Monitoring and Legitimate Interests 2026

Governance Docs30th September 2026

Can you rely on legitimate interests to monitor employees? The three-part test, proportionality, transparency and when a DPIA…
Read More
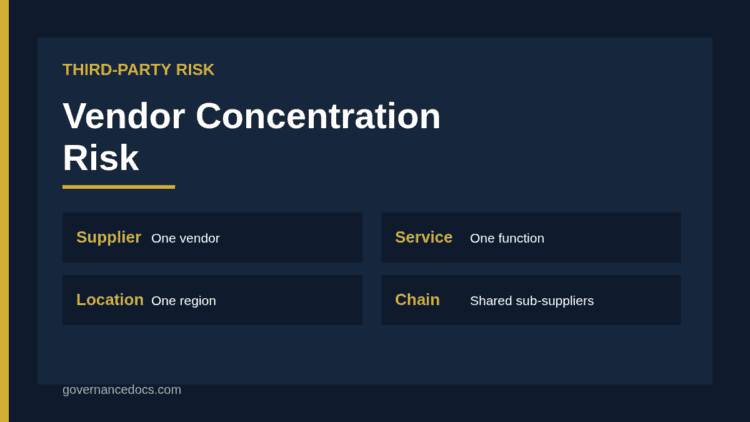
Vendor concentration risk chart showing dependence on a few critical suppliers

Vendor Concentration Risk: How to Assess It 2026

Governance Docs29th September 2026

How to assess vendor concentration risk: supplier, service, geographic and sub-supplier concentration, with measures, thresholds and mitigation options.
Read More
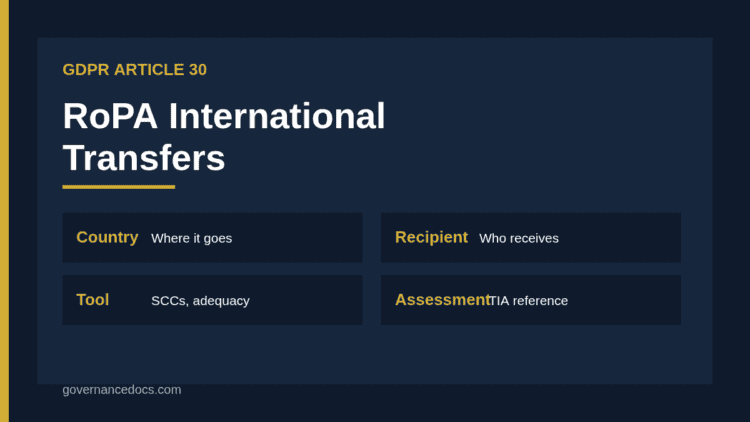
RoPA international transfers entry listing country recipient and safeguard

RoPA International Transfers: Recording Them Right 2026

Governance Docs29th September 2026

How to record international transfers in your RoPA under Article 30(1)(e): naming countries, transfer tools, derogations and links…
Read More
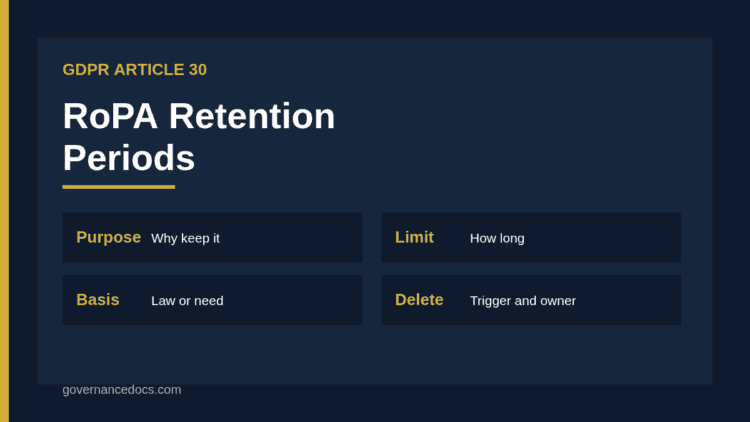
RoPA retention periods column linked to a retention schedule and deletion process

RoPA Retention Periods: Recording Erasure Limits 2026

Governance Docs29th September 2026

How to record RoPA retention periods under Article 30(1)(f): setting limits, citing legal bases, linking to a retention…
Read More
IMS context of the organization showing internal issues external issues and interested parties

IMS Context of the Organization: Practical Guide 2026

Governance Docs29th September 2026

How to handle the IMS context of the organization: identify internal and external issues, interested parties, scope and…
Read More
HACCP records including monitoring logs corrective actions and verification

HACCP Records: What to Keep and How 2026

Governance Docs29th September 2026

Which HACCP records to keep, how to complete and review them, how long to retain them and what…
Read More
IATF 16949 control plan covering prototype pre-launch and production phases

IATF 16949 Control Plan: Requirements Guide 2026

Governance Docs29th September 2026

What an IATF 16949 control plan must contain: three phases, required controls, reaction plans, review triggers and how…
Read More
NCA ECC defense domain subdomains from asset management to incident management

NCA ECC Defense Domain: Controls Explained 2026

Governance Docs29th September 2026

A guide to the NCA ECC defense domain: its subdomains from asset management to web application security, and…
Read More
Data governance metrics dashboard covering quality adoption and risk

Data Governance Metrics That Prove Value 2026

Governance Docs29th September 2026

Which data governance metrics to track: adoption, data quality, stewardship, policy compliance and business value, with definitions and…
Read More
IMS internal audit combining quality, environment and safety management systems

IMS Internal Audit: Combined Audit Guide 2026

Governance Docs29th September 2026

How to run an IMS internal audit that covers ISO 9001, 14001 and 45001 together: programme, planning, auditor…
Read More
Gap assessment scoring matrix ranking findings by risk and effort

Gap Assessment Scoring and Prioritisation 2026

Governance Docs29th September 2026

How to design gap assessment scoring: define compliance ratings, weight by risk and effort, and produce a prioritised…
Read More
Business impact analysis financial impact curve rising over time of disruption

Business Impact Analysis Financial Impact Guide 2026

Governance Docs29th September 2026

How to estimate the financial impact in a business impact analysis: direct and indirect costs, impact over time,…
Read More

    ←
  • 1
  • …
  • 19
  • 20
  • 21
  • 22
  • 23
  • …
  • 100
  • →

Recent Posts

ISO 27001 remote working Annex A 6.7 diagram showing the four evidence sets: authorisation, provisioning, enforcement and attestation
ISO 27001 Remote Working: Complete A.6.7 Guide 2026

October 12, 2026

ISO 27001 configuration management requirements under Annex A 8.9 - established, documented, implemented, monitored, reviewed
ISO 27001 Configuration Management: Complete 2026 Guide

October 11, 2026

internal audit findings rating scale — Internal Audit Findings Rating Scale: Examples and Template
Internal Audit Findings Rating Scale: Examples and Template

October 11, 2026

third party topical requirement — Third Party Topical Requirement: The 2026 Audit Guide
Third Party Topical Requirement: The 2026 Audit Guide

October 11, 2026

cybersecurity topical requirement — Cybersecurity Topical Requirement: How to Audit It in 2026
Cybersecurity Topical Requirement: How to Audit It in 2026

October 11, 2026

Categories

  • Articles
  • DORA
  • GDPR
  • HIPAA
  • ISO 27001
  • ISO 42001 & AI governance
  • ISO 9001
  • Management systems
  • NIS2
  • Security frameworks
  • SOC 2
Governance DocsGovernance Docs

Reliable ISO & compliance documentation toolkits that help your business meet regulatory standards with ease.

Governance Docs LLC
1209 Mountain Road Pl NE, Suite R
Albuquerque, NM 87110, USA
info@governancedocs.com
+1 505 289 2455

Toolkits

  • ISO 27001:2022
  • GDPR
  • SOC 2
  • PCI-DSS v4.0
  • HIPAA
  • ISO 42001
  • All toolkits →

Company

  • About Us
  • Blog
  • Contact
  • FAQ
  • Which toolkit do I need?
  • Free templates
  • SoA generator
  • Assessments
  • Sample reports
  • RSS feeds

Policies

  • Privacy Policy
  • Terms & Conditions
  • Refund & Return Policy
  • Delivery Policy
  • Manage cookies
Browse by topicISO 27001ISO 42001 & AI governanceGDPRSOC 2HIPAANIS2DORAISO 9001Management systemsSecurity frameworks
© 2026 Governance Docs LLC. All rights reserved.
Secure checkoutstripeVISA