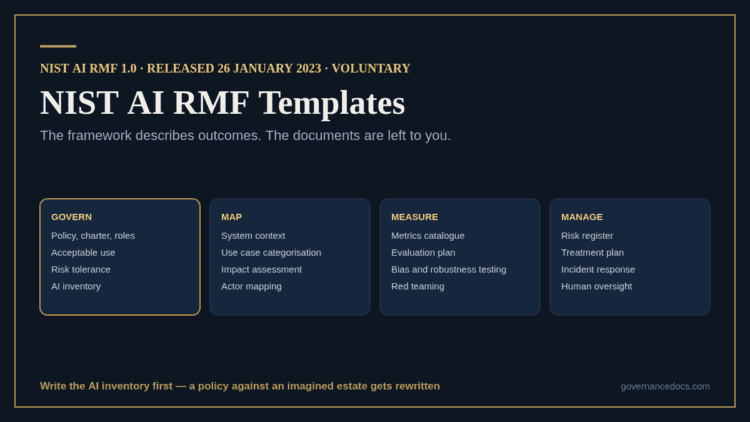
NIST AI RMF Templates: A Clear Guide to All 4 Functions Governance Docs31st August 2026 NIST AI RMF templates are the question the framework will not answer. What Govern, Map, Measure and Manage… Read More
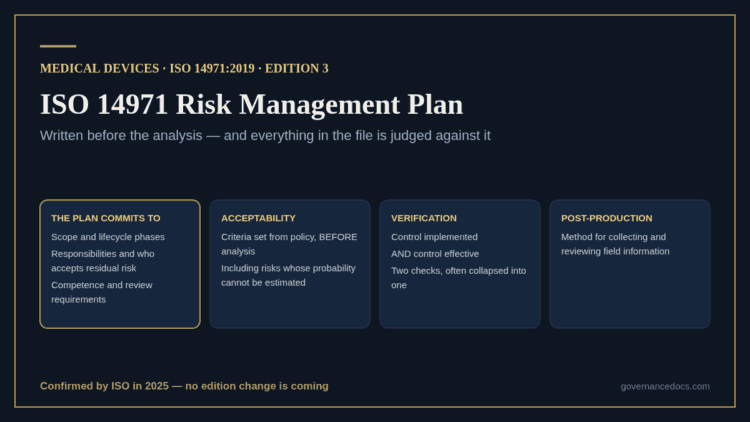
ISO 14971 Risk Management Plan: A Clear Guide to Its Content Governance Docs31st August 2026 The ISO 14971 risk management plan is written before the analysis and judged against everything after it. What… Read More
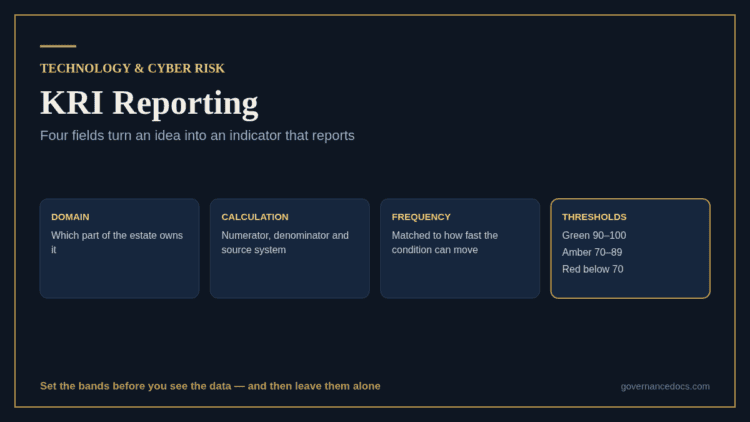
KRI Reporting: A Clear Guide to the 4 Core Fields Governance Docs31st August 2026 KRI reporting fails when indicators are picked for easy data. The 4 fields every KRI needs, RAG thresholds… Read More
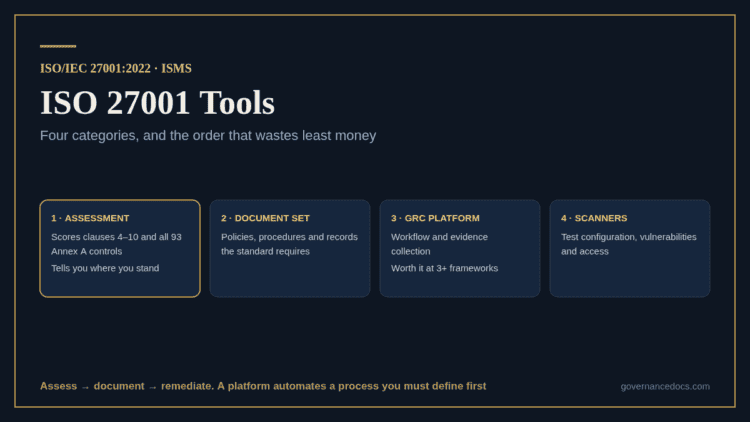
ISO 27001 Tools: Complete Guide to the 4 Categories Governance Docs31st August 2026 ISO 27001 tools range from a spreadsheet to a GRC platform. The 4 categories, what an assessment tool… Read More
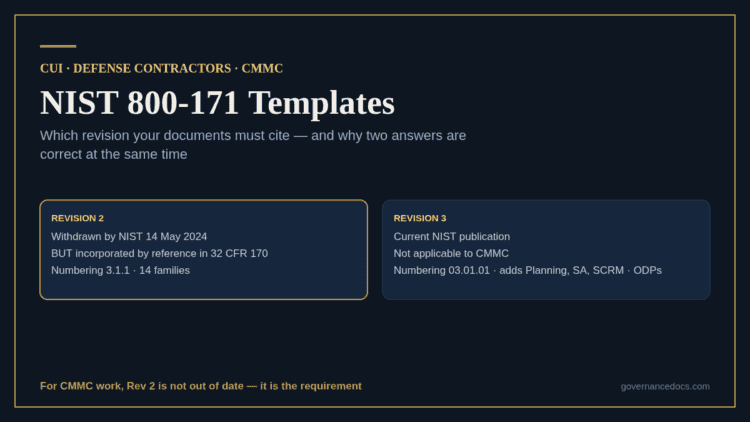
NIST 800-171 Templates: Complete Rev 2 Document Set Guide Governance Docs31st August 2026 NIST 800-171 templates must cite the right revision. Why CMMC still requires Rev 2 though NIST withdrew it,… Read More
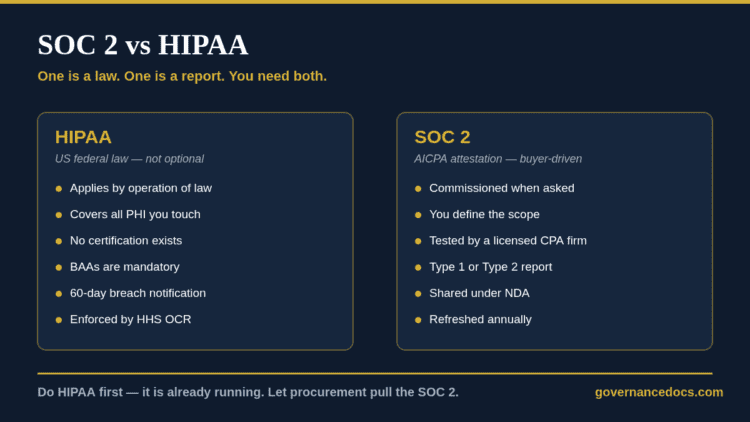
SOC 2 vs HIPAA: The Complete 2026 Compliance Guide Governance Docs31st August 2026 SOC 2 vs HIPAA compared: HIPAA is US federal law, SOC 2 is an AICPA attestation. See what… Read More
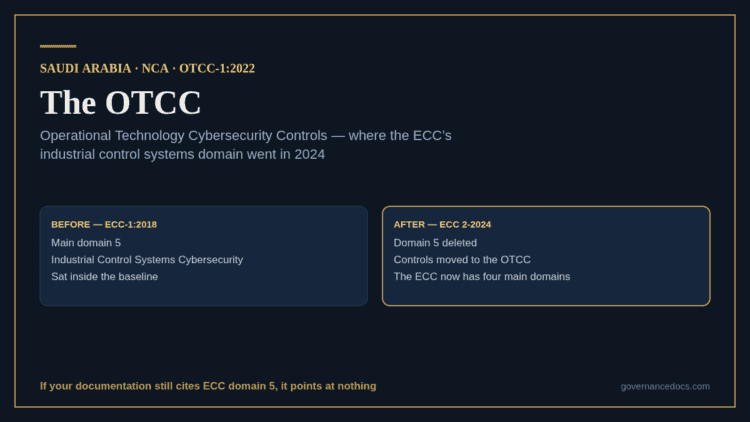
OTCC: A Clear Guide to Saudi OT Cybersecurity in 2026 Governance Docs30th August 2026 The OTCC absorbed the ECC's industrial control systems domain in 2024. What it covers, how it differs from… Read More
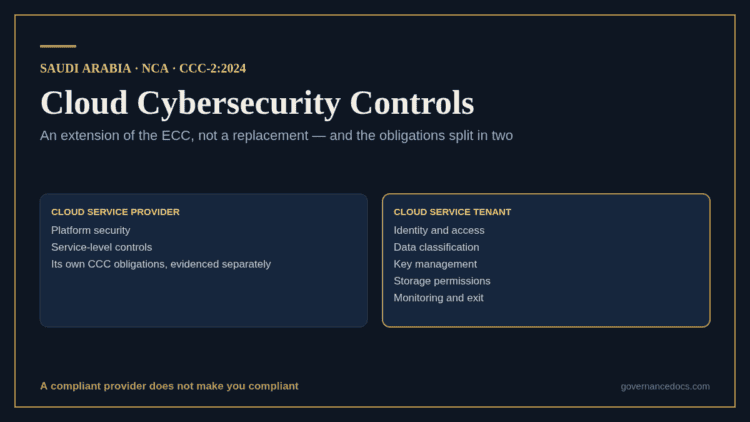
Cloud Cybersecurity Controls: A Clear CCC-2:2024 Guide Governance Docs30th August 2026 The Cloud Cybersecurity Controls split obligations between provider and tenant. CCC-2:2024, the 6 responsibility areas, and what changed… Read More
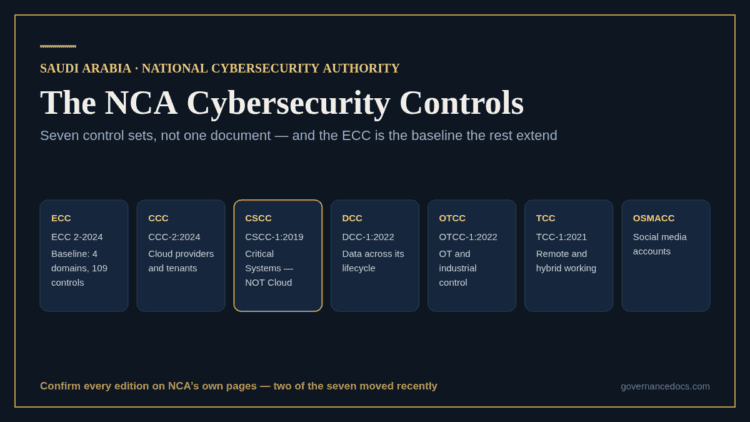
NCA Cybersecurity Controls: A Clear Guide to All 7 Sets Governance Docs30th August 2026 The 7 NCA cybersecurity controls sets and their current editions, which apply to you, and why CSCC is… Read More
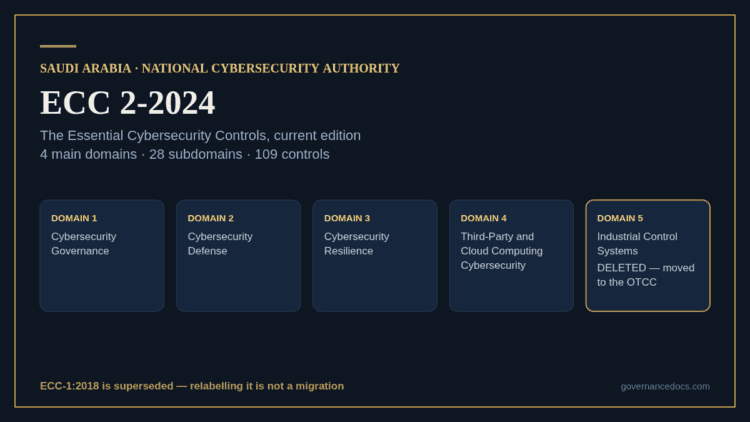
ECC 2-2024: A Clear Guide to All 4 Domains Governance Docs30th August 2026 ECC 2-2024 replaced ECC-1:2018 and deleted a whole domain. The 4 domains, 109 controls, where the ICS controls… Read More
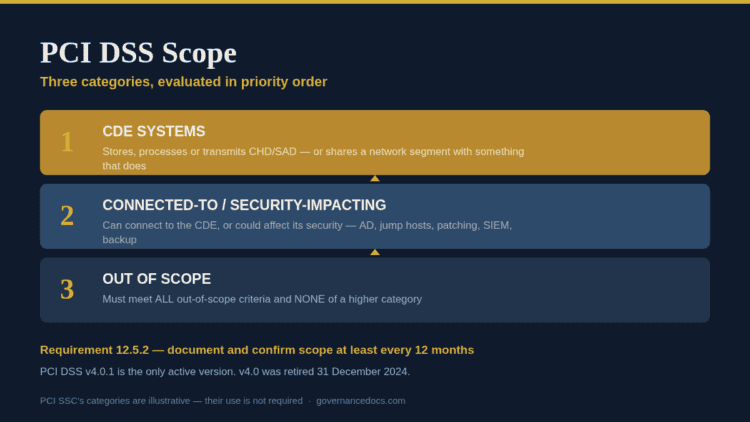
PCI DSS Scope: A Clear Guide to All 3 Categories Governance Docs30th August 2026 How PCI DSS scope is decided: the 3 system categories in priority order, the annual confirmation under Requirement… Read More
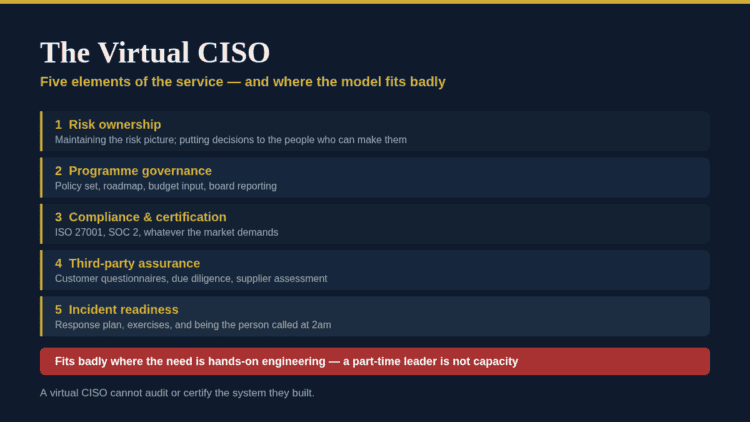
Virtual CISO: A Clear Guide to All 5 Service Elements Governance Docs30th August 2026 What a virtual CISO does, the 5 elements of the service, how to structure and price an engagement,… Read More