

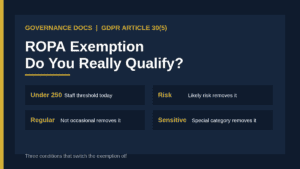
ROPA Exemption: The Essential 2026 Guide to GDPR Article 30(5) for Small Organizations
Does a small organization need a record of processing activities? The ROPA exemption in GDPR Article 30(5), the…
CART
Does a small organization need a record of processing activities? The ROPA exemption in GDPR Article 30(5), the…
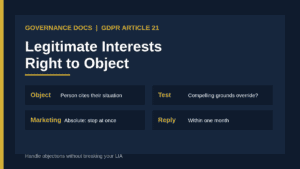
What happens when someone objects to processing based on legitimate interests: the Article 21 test, the absolute marketing…
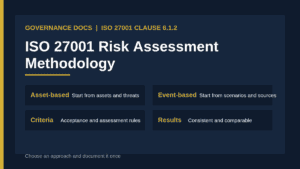
How to define an ISO 27001 risk assessment methodology: what clause 6.1.2 requires, asset-based versus event-based approaches and…
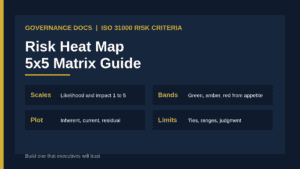
How to build a risk heat map: define 5×5 likelihood and impact scales, set colour bands from risk…
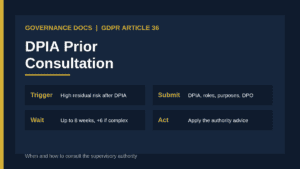
When a DPIA leaves high residual risk, GDPR Article 36 requires prior consultation. Learn the trigger, the submission…
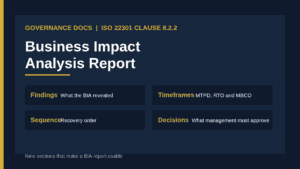
How to structure a business impact analysis report for ISO 22301: nine sections, clear findings, the recovery sequence…
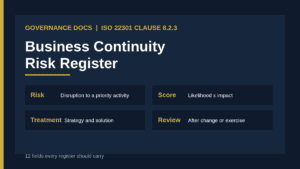
A practical guide to building a business continuity risk register for ISO 22301: the 12 fields, BIA-linked scoring,…
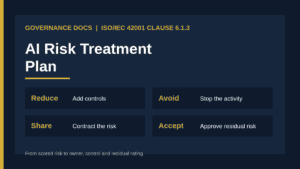
How to build an AI risk treatment plan under ISO 42001 clause 6.1.3: options, columns, Annex A links…
How the ISO 42001 impact assessment works: clause 6.1.4, clause 8.4, Annex A.5, and the evidence auditors ask…
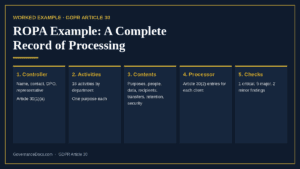
A ROPA example for a fictional 320-person delivery company: controller details, the exemption check, three activities in full,…
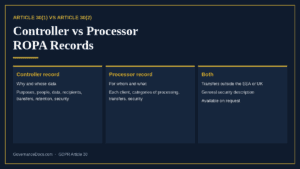
Controller vs processor ROPA: what Article 30(1) and 30(2) each require, a side-by-side comparison, which record an activity…
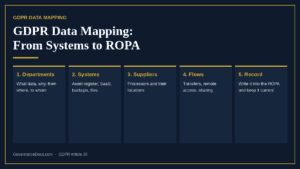
GDPR data mapping explained: what to capture, how a data map differs from the records of processing, a…
October 19, 2026
October 19, 2026
October 18, 2026
October 18, 2026
October 15, 2026