

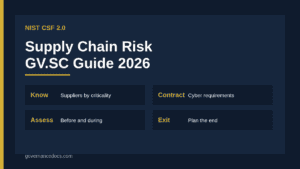
NIST CSF Supply Chain Risk Management: GV.SC Guide 2026
A practical guide to NIST CSF supply chain risk management under the GV.SC category, from supplier criticality to…
CART
A practical guide to NIST CSF supply chain risk management under the GV.SC category, from supplier criticality to…
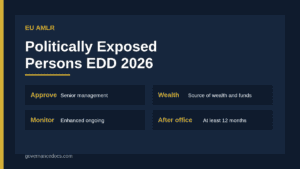
How to handle AMLR politically exposed persons: approval, source of wealth, monitoring and the 12-month post-office rule.
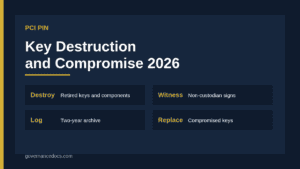
How PCI PIN key destruction and compromise procedures work: retirement, witnessed destruction, key logs, backups and replacement.
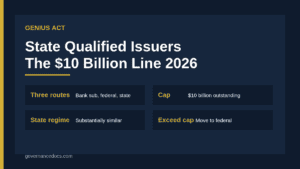
How GENIUS Act state qualified issuers work: the $10 billion cap, state regime certification and the path to…
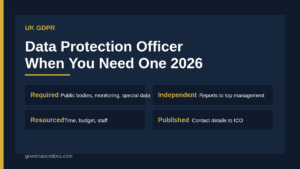
When a UK GDPR data protection officer is required, what the role does, how to avoid conflicts of…
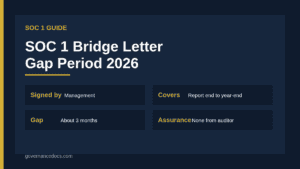
What a SOC 1 bridge letter is, what to include, who signs it and where its assurance stops.
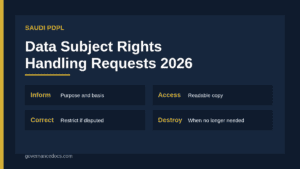
How to handle Saudi PDPL data subject rights: the five rights, response deadlines and a practical request-handling workflow.
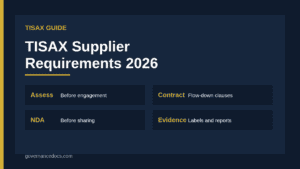
How TISAX supplier requirements work: risk assessment before engagement, contract flow-down, NDAs and the evidence assessors ask for.
What providers must do after GovRAMP verification: reports, POA&M timelines, annual assessment, change notice and escalation.
A practical guide to NQA-1 Requirement 7: how to evaluate suppliers, keep an approved supplier list and prepare…
A guide to the twelve controls in the NIST 800-53 SR family, how to build a supply chain…
A guide to the Govern-P function of the NIST Privacy Framework, with its four categories, evidence and steps…
October 19, 2026
October 19, 2026
October 18, 2026
October 18, 2026
October 15, 2026