About Us Contact Blog
Governance DocsGovernance Docs
Which Toolkit?SoA GeneratorFree TemplatesSample ReportsRecords of Processing (ROPA)Data Privacy Impact AssessmentLegitimate Interests AssessmentTransfer Impact AssessmentPrivacy Risk AssessmentGDPR Gap AssessmentISO 27701 Gap AssessmentHIPAA Gap AssessmentGap AssessmentsBusiness Impact AnalysisISO 27001 Risk AssessmentContinuity Risk AssessmentEnterprise Risk AssessmentAI Risk AssessmentAI Impact AssessmentThird-Party Risk AssessmentAboutBlogContactMy AccountCart
FOX v.2.4.9
Browse Toolkits
Governance Docs
  • Browse All Toolkits
  • Information Security & Cybersecurity
  • Data Privacy & Protection
  • Governance, Risk & Compliance
  • Quality Management
  • Health, Safety & Environment
  • AI Governance

My Account

CART

No products in the cart.

Day: September 29, 2026

COBIT 2019 governance system principles guide cover

COBIT 2019 Governance System Principles Explained 2026

Governance Docs29th September 2026

The six COBIT 2019 governance system principles, how they differ from COBIT 5 and how to apply them…
Read More
ISO 27017 virtual machine hardening guide cover

ISO 27017 Virtual Machine Hardening and Segregation 2026

Governance Docs29th September 2026

How to apply ISO 27017 virtual machine hardening and segregation controls, with practical steps and audit evidence.
Read More
ISO 17025 risks and opportunities guide cover

ISO 17025 Risks and Opportunities: Clause 8.5 Guide 2026

Governance Docs29th September 2026

What ISO 17025 clause 8.5 requires on risks and opportunities, and a simple way to show assessors you…
Read More
ISO 15189 method verification and validation guide cover

ISO 15189 Method Verification vs Validation Guide 2026

Governance Docs29th September 2026

When a laboratory verifies or validates examination procedures under ISO 15189, what to test and what records assessors…
Read More
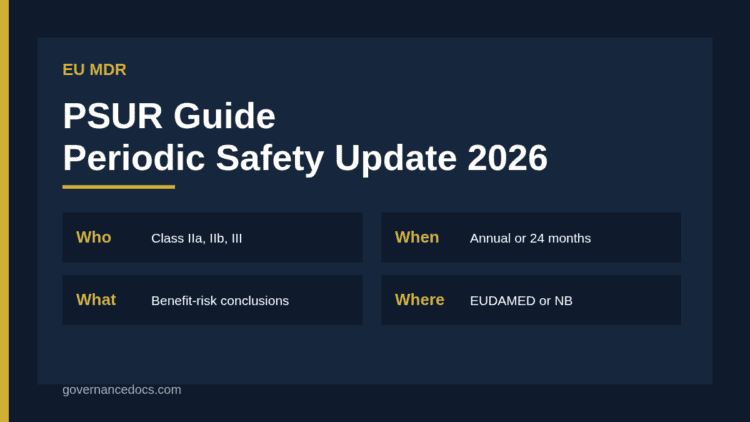
MDR PSUR periodic safety update report guide cover

MDR PSUR: Periodic Safety Update Report Guide 2026

Governance Docs29th September 2026

How an MDR PSUR works: which classes need one, update frequency, required content, EUDAMED submission and common mistakes.
Read More
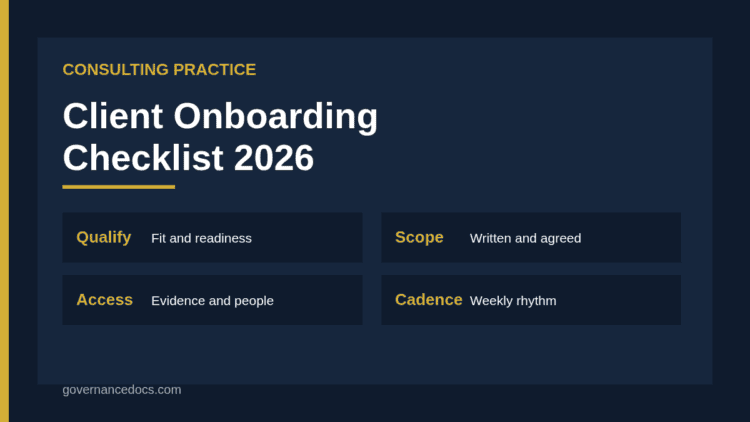
Compliance consulting client onboarding checklist cover

Compliance Consulting Client Onboarding: A 2026 Checklist

Governance Docs29th September 2026

A practical checklist for compliance consulting client onboarding, from qualification and scope to access, evidence and the first…
Read More
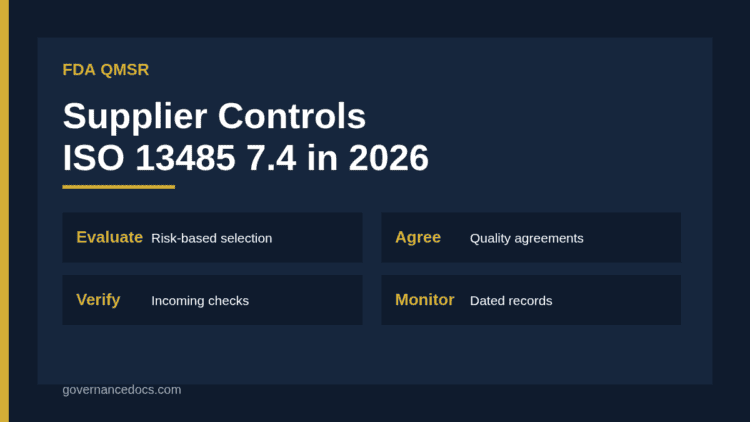
QMSR supplier controls guide cover

QMSR Supplier Controls: ISO 13485 Clause 7.4 for FDA 2026

Governance Docs29th September 2026

How QMSR supplier controls work under ISO 13485 clause 7.4: evaluation, agreements, verification, monitoring and inspection evidence.
Read More
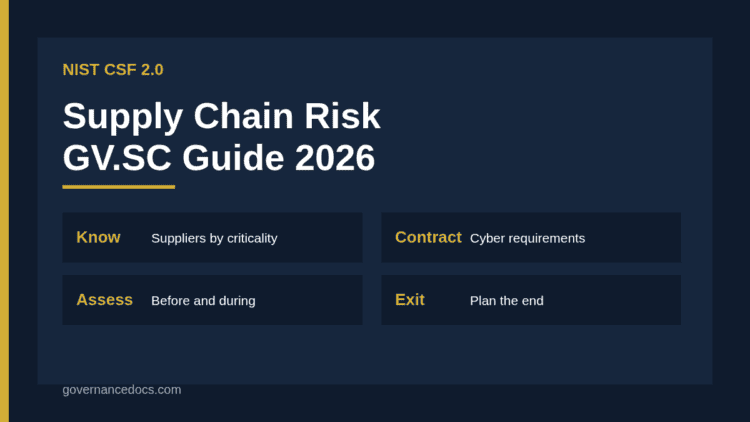
NIST CSF supply chain risk management guide cover

NIST CSF Supply Chain Risk Management: GV.SC Guide 2026

Governance Docs29th September 2026

A practical guide to NIST CSF supply chain risk management under the GV.SC category, from supplier criticality to…
Read More
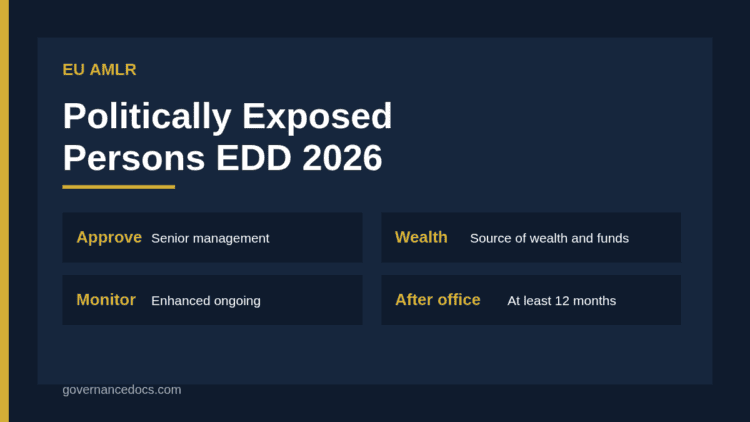
AMLR politically exposed persons guide cover

AMLR Politically Exposed Persons: EDD Steps 2026

Governance Docs29th September 2026

How to handle AMLR politically exposed persons: approval, source of wealth, monitoring and the 12-month post-office rule.
Read More
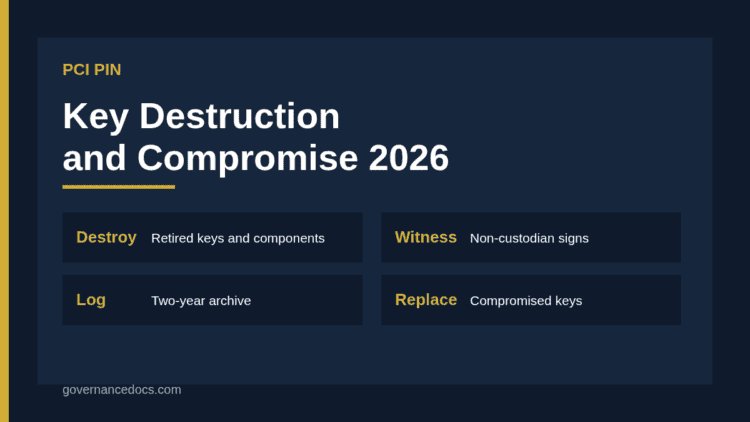
PCI PIN key destruction and compromise guide cover

PCI PIN Key Destruction and Compromise Response 2026

Governance Docs29th September 2026

How PCI PIN key destruction and compromise procedures work: retirement, witnessed destruction, key logs, backups and replacement.
Read More
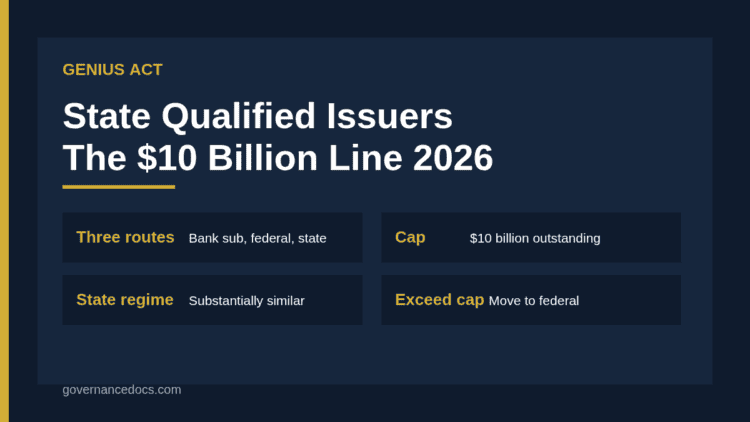
GENIUS Act state qualified issuers guide cover

GENIUS Act State Qualified Issuers: The $10 Billion Line 2026

Governance Docs29th September 2026

How GENIUS Act state qualified issuers work: the $10 billion cap, state regime certification and the path to…
Read More
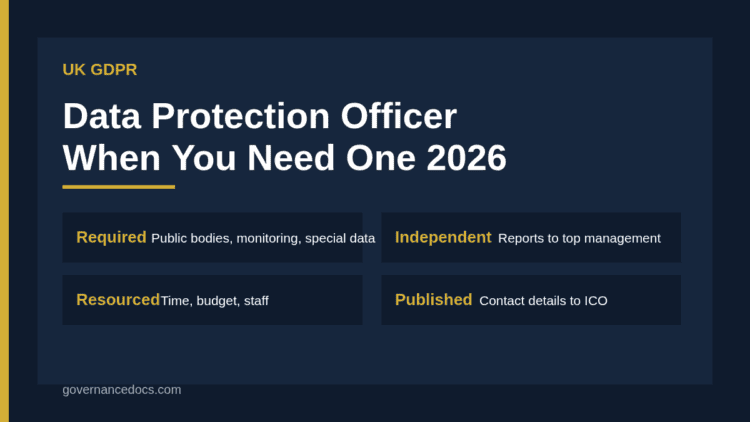
UK GDPR data protection officer guide cover

UK GDPR Data Protection Officer: When You Need One 2026

Governance Docs29th September 2026

When a UK GDPR data protection officer is required, what the role does, how to avoid conflicts of…
Read More

    ←
  • 1
  • 2
  • 3
  • 4
  • 5
  • 6
  • …
  • 10
  • →

Recent Posts

Gap assessment reassessment progress comparison diagram
Gap Assessment Reassessment: The Essential 2026 Guide to Measuring Progress

September 30, 2026

Business continuity supply chain risk map diagram
Business Continuity Supply Chain Risk: The Essential 2026 Guide to Resilient Suppliers

September 30, 2026

Business continuity risk appetite statement diagram
Business Continuity Risk Appetite: The Essential 2026 Guide to Setting Tolerance for Disruption

September 30, 2026

Business continuity risk monitoring indicators diagram
Business Continuity Risk Monitoring: The Essential 2026 Guide to Indicators and Reviews

September 30, 2026

Business continuity scenario planning steps diagram
Business Continuity Scenario Planning: The Essential 2026 Guide to Testing Your Plans

September 30, 2026

Categories

  • Articles
  • DORA
  • GDPR
  • HIPAA
  • ISO 27001
  • ISO 42001 & AI governance
  • ISO 9001
  • Management systems
  • NIS2
  • Security frameworks
  • SOC 2
Governance DocsGovernance Docs

Reliable ISO & compliance documentation toolkits that help your business meet regulatory standards with ease.

Governance Docs LLC
1209 Mountain Road Pl NE, Suite R
Albuquerque, NM 87110, USA
info@governancedocs.com
+1 812 227 5662

Toolkits

  • ISO 27001:2022
  • GDPR
  • SOC 2
  • PCI-DSS v4.0
  • HIPAA
  • ISO 42001
  • All toolkits →

Company

  • About Us
  • Blog
  • Contact
  • FAQ
  • Which toolkit do I need?
  • Free templates
  • SoA generator
  • Assessments
  • Sample reports
  • RSS feeds

Policies

  • Privacy Policy
  • Terms & Conditions
  • Refund & Return Policy
  • Delivery Policy
  • Manage cookies
Browse by topicISO 27001ISO 42001 & AI governanceGDPRSOC 2HIPAANIS2DORAISO 9001Management systemsSecurity frameworks
© 2026 Governance Docs LLC. All rights reserved.
Secure checkoutstripeVISA