About Us Contact Blog
Governance DocsGovernance Docs
Which Toolkit?SoA GeneratorFree TemplatesSample ReportsFind the Right AssessmentRecords of Processing (ROPA)Data Privacy Impact AssessmentLegitimate Interests AssessmentTransfer Impact AssessmentPrivacy Risk AssessmentGDPR Gap AssessmentUK GDPR Gap AssessmentCCPA/CPRA Gap AssessmentISO 27701 Gap AssessmentHIPAA Gap AssessmentISO 27001 Risk AssessmentThird-Party Risk AssessmentSoA GeneratorISO 27001 Assessment Tool (Excel)ISO 27001 Gap AssessmentSOC 2 Gap AssessmentNIST CSF 2.0 Gap AssessmentNIST SP 800-53 Gap AssessmentNIST RMF Gap AssessmentCIS Controls Gap AssessmentPCI DSS 4.0 Gap AssessmentNIS2 Gap AssessmentCMMC 2.0 Gap AssessmentNIST SP 800-171 Gap AssessmentFedRAMP Gap AssessmentBSI C5 Gap AssessmentIEC 62443 Gap AssessmentSAMA CSF Gap AssessmentNCA ECC Gap AssessmentISO 20000 Gap AssessmentAI Risk AssessmentAI Impact AssessmentISO 42001 Gap AssessmentEU AI Act Gap AssessmentBusiness Impact AnalysisContinuity Risk AssessmentISO 22301 Assessment Tool (Excel)ISO 22301 Gap AssessmentDORA Gap AssessmentISO 9001 Gap AssessmentISO 13485 Gap AssessmentIATF 16949 Gap AssessmentISO 14001 Gap AssessmentISO 45001 Gap AssessmentISO 45001 Assessment Tool (Excel)HACCP Gap AssessmentEnterprise Risk AssessmentISO 31000 Gap AssessmentData Governance Gap AssessmentProject Management Gap AssessmentAll Gap AssessmentsISO 27001 Internal AuditISO 42001 Internal AuditAboutBlogContactMy AccountCart
FOX v.2.4.9
Browse Toolkits
Governance Docs
  • Browse All Toolkits
  • Information Security & Cybersecurity
  • Data Privacy & Protection
  • Governance, Risk & Compliance
  • Quality Management
  • Health, Safety & Environment
  • AI Governance

My Account

CART

No products in the cart.

Day: September 29, 2026

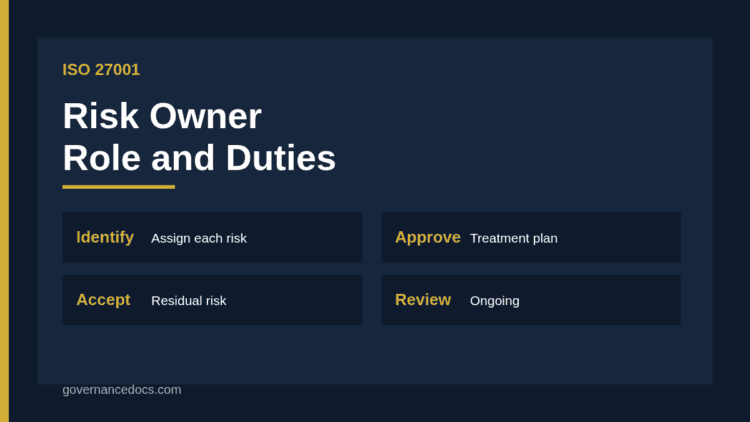
ISO 27001 risk owner approving treatment plan and residual risk acceptance

ISO 27001 Risk Owner: Role and Duties 2026

Governance Docs29th September 2026

What an ISO 27001 risk owner is, who should hold the role, and how owners approve treatment plans…
Read More
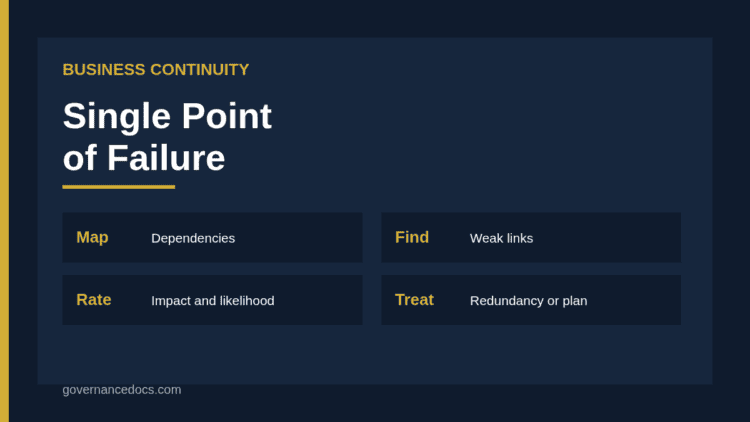
Single point of failure analysis mapping dependencies of a critical service

Single Point of Failure Analysis for Continuity 2026

Governance Docs29th September 2026

How to run single point of failure analysis for business continuity: map dependencies, find the weak links, rate…
Read More
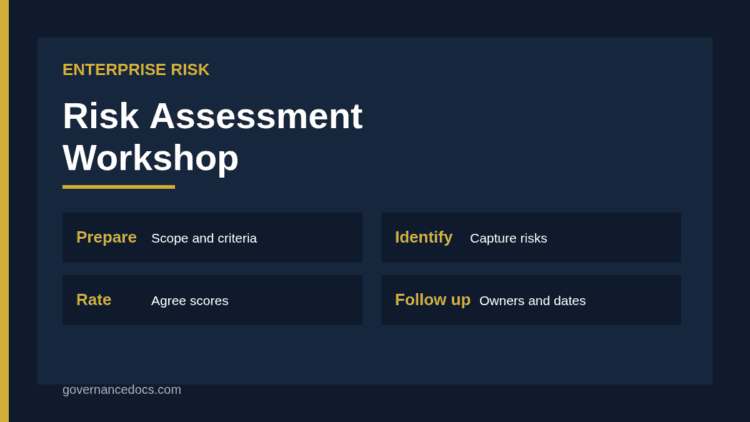
Risk assessment workshop with participants rating enterprise risks on a matrix

Risk Assessment Workshop: How to Run One 2026

Governance Docs29th September 2026

A step-by-step guide to running a risk assessment workshop: who to invite, how to prepare, how to facilitate…
Read More
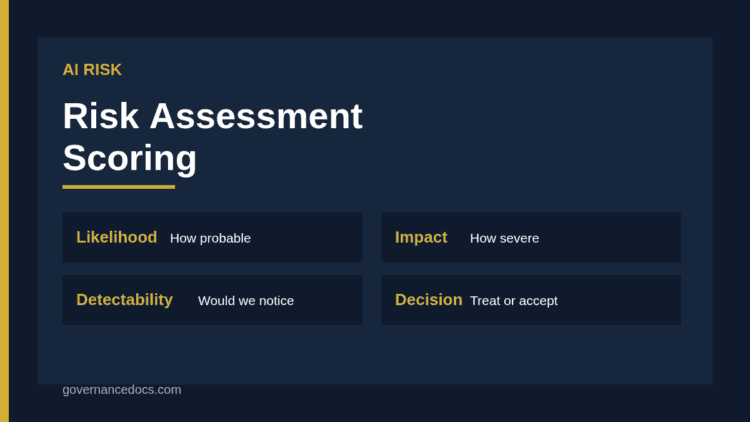
AI risk assessment scoring matrix with likelihood impact and detectability

AI Risk Assessment Scoring: A Practical Method 2026

Governance Docs29th September 2026

A practical approach to AI risk assessment scoring: define scales for likelihood, impact and detectability, calibrate them and…
Read More
DPIA residual risk rating after mitigation measures

DPIA Residual Risk: Rating Risk After Controls 2026

Governance Docs29th September 2026

How to assess DPIA residual risk: rate risk before and after measures, decide who accepts it and know…
Read More
Transfer impact assessment third country laws review against European Essential Guarantees

Transfer Impact Assessment: Third Country Laws 2026

Governance Docs29th September 2026

How to assess a destination country's laws and practice in a transfer impact assessment, using the EDPB roadmap…
Read More
AI impact assessment screening funnel from AI inventory to full assessment

AI Impact Assessment Screening: Who Needs One 2026

Governance Docs29th September 2026

How AI impact assessment screening works: the questions to ask, how to set thresholds, and how to record…
Read More
Legitimate interests balancing test weighing organisation and individual interests

Legitimate Interests Balancing Test Explained 2026

Governance Docs29th September 2026

How to run the legitimate interests balancing test: data sensitivity, reasonable expectations, likely impact and safeguards, with a…
Read More
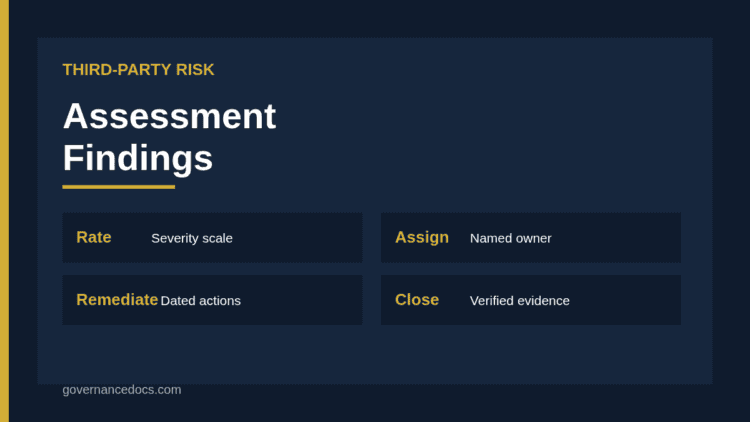
Third party risk assessment findings workflow from rating to closure

Third Party Risk Assessment Findings and Remediation 2026

Governance Docs29th September 2026

How to record, rate and close third party risk assessment findings so vendor assessments lead to real remediation,…
Read More
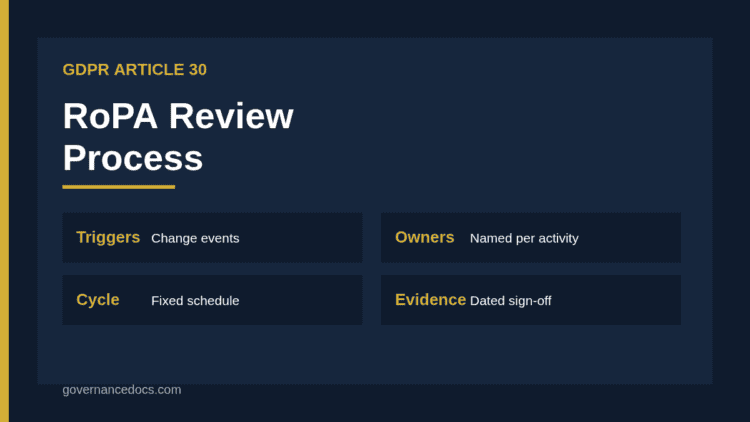
RoPA review process cycle for Article 30 records of processing

RoPA Review Process: Keep Your Records Current 2026

Governance Docs29th September 2026

A practical RoPA review process for Article 30 records: what to check, who owns it, how often to…
Read More
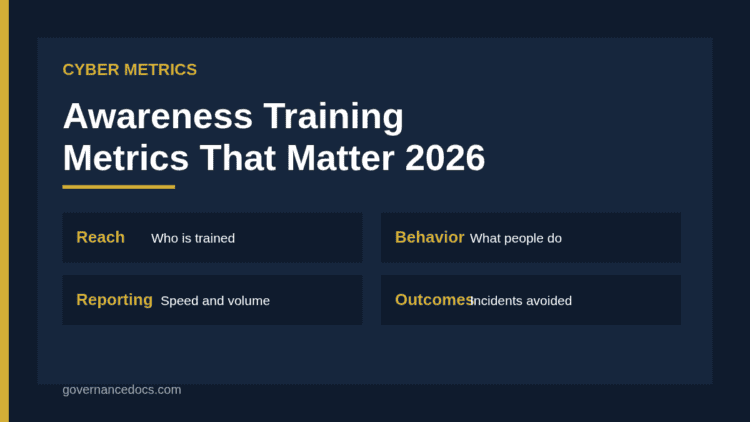
Security awareness training metrics guide cover

Security Awareness Training Metrics That Show Real Change 2026

Governance Docs29th September 2026

Which security awareness training metrics prove behavior change: reporting rates, phishing outcomes, incident data and program health.
Read More
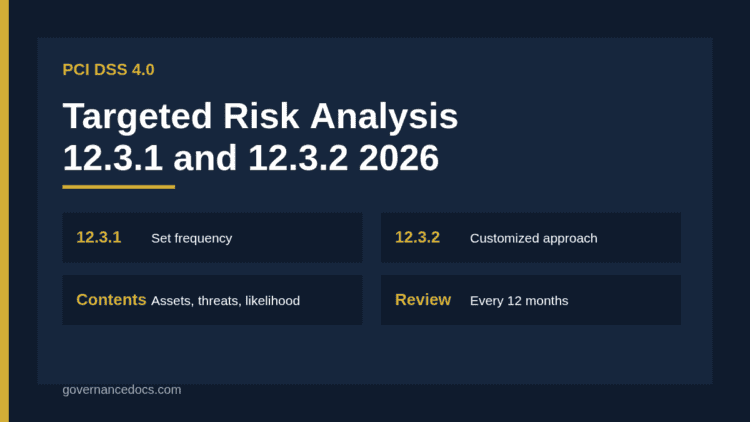
PCI DSS targeted risk analysis guide cover

PCI DSS Targeted Risk Analysis: 12.3.1 and 12.3.2 Guide 2026

Governance Docs29th September 2026

How to write a PCI DSS targeted risk analysis for flexible-frequency requirements and the customized approach, with content…
Read More

    ←
  • 1
  • 2
  • 3
  • 4
  • …
  • 10
  • →

Recent Posts

ISO 27001 password policy requirements under Annex A 5.17 and A.8.5, with NIST, PCI DSS and Cyber Essentials length baselines compared
ISO 27001 Password Policy: Complete 2026 Requirements Guide

October 20, 2026

ISO 27001 intellectual property rights: the six categories in Annex A control 5.32
ISO 27001 Intellectual Property Rights: Complete 2026 Guide

October 20, 2026

ISO 27001 independent review under Annex A 5.35 compared with the clause 9.2 internal audit and clause 9.3 management review
ISO 27001 Independent Review: Complete A.5.35 Guide 2026

October 19, 2026

ISO 27001 acceptable use policy requirements under Annex A control A.5.10
ISO 27001 Acceptable Use Policy: Complete 2026 Guide

October 19, 2026

ISO 27001 network security controls A.8.20, A.8.21 and A.8.22 compared
ISO 27001 Network Security: Complete A.8.20–8.22 Guide 2026

October 18, 2026

Categories

  • Articles
  • DORA
  • GDPR
  • HIPAA
  • ISO 27001
  • ISO 42001 & AI governance
  • ISO 9001
  • Management systems
  • NIS2
  • Security frameworks
  • SOC 2
Governance DocsGovernance Docs

Reliable ISO & compliance documentation toolkits that help your business meet regulatory standards with ease.

Governance Docs LLC
1209 Mountain Road Pl NE, Suite R
Albuquerque, NM 87110, USA
[email protected]
+1 505 289 2455

Toolkits

  • ISO 27001:2022
  • GDPR
  • SOC 2
  • PCI-DSS v4.0
  • HIPAA
  • ISO 42001
  • All toolkits →

Company

  • About Us
  • Blog
  • Contact
  • FAQ
  • Which toolkit do I need?
  • Free templates
  • SoA generator
  • Assessments
  • Sample reports
  • RSS feeds

Policies

  • Privacy Policy
  • Terms & Conditions
  • Refund & Return Policy
  • Delivery Policy
  • Manage cookies
Browse by topicISO 27001ISO 42001 & AI governanceGDPRSOC 2HIPAANIS2DORAISO 9001Management systemsSecurity frameworks
© 2026 Governance Docs LLC. All rights reserved.
Secure checkoutstripeVISA