About Us Contact Blog
Governance DocsGovernance Docs
Which Toolkit?SoA GeneratorFree TemplatesSample ReportsFind the Right AssessmentRecords of Processing (ROPA)Data Privacy Impact AssessmentLegitimate Interests AssessmentTransfer Impact AssessmentPrivacy Risk AssessmentGDPR Gap AssessmentUK GDPR Gap AssessmentCCPA/CPRA Gap AssessmentISO 27701 Gap AssessmentHIPAA Gap AssessmentISO 27001 Risk AssessmentThird-Party Risk AssessmentSoA GeneratorISO 27001 Assessment Tool (Excel)ISO 27001 Gap AssessmentSOC 2 Gap AssessmentNIST CSF 2.0 Gap AssessmentNIST SP 800-53 Gap AssessmentNIST RMF Gap AssessmentCIS Controls Gap AssessmentPCI DSS 4.0 Gap AssessmentNIS2 Gap AssessmentCMMC 2.0 Gap AssessmentNIST SP 800-171 Gap AssessmentFedRAMP Gap AssessmentBSI C5 Gap AssessmentIEC 62443 Gap AssessmentSAMA CSF Gap AssessmentNCA ECC Gap AssessmentISO 20000 Gap AssessmentAI Risk AssessmentAI Impact AssessmentISO 42001 Gap AssessmentEU AI Act Gap AssessmentBusiness Impact AnalysisContinuity Risk AssessmentISO 22301 Assessment Tool (Excel)ISO 22301 Gap AssessmentDORA Gap AssessmentISO 9001 Gap AssessmentISO 13485 Gap AssessmentIATF 16949 Gap AssessmentISO 14001 Gap AssessmentISO 45001 Gap AssessmentISO 45001 Assessment Tool (Excel)HACCP Gap AssessmentEnterprise Risk AssessmentISO 31000 Gap AssessmentData Governance Gap AssessmentProject Management Gap AssessmentAll Gap AssessmentsISO 27001 Internal AuditISO 42001 Internal AuditAboutBlogContactMy AccountCart
FOX v.2.4.9
Browse Toolkits
Governance Docs
  • Browse All Toolkits
  • Information Security & Cybersecurity
  • Data Privacy & Protection
  • Governance, Risk & Compliance
  • Quality Management
  • Health, Safety & Environment
  • AI Governance

My Account

CART

No products in the cart.

Day: September 29, 2026

NIST RMF system categorization FIPS 199 guide cover

NIST RMF System Categorization with FIPS 199 in 2026

Governance Docs29th September 2026

How NIST RMF system categorization works with FIPS 199: impact levels, information types, the high water mark and…
Read More
ESG data quality controls guide cover

ESG Data Quality: Controls for Reliable Reporting 2026

Governance Docs29th September 2026

How to improve ESG data quality using the five GHG Protocol principles, data owners, controls and an audit…
Read More
HACCP monitoring procedures guide cover

HACCP Monitoring Procedures: Critical Control Points 2026

Governance Docs29th September 2026

How to set HACCP monitoring procedures for critical control points: methods, frequency, who monitors and record review.
Read More
NCA ECC third-party cybersecurity guide cover

NCA ECC Third-Party Cybersecurity Requirements 2026

Governance Docs29th September 2026

What NCA ECC third-party cybersecurity controls require for contracts, outsourcing and managed services in Saudi Arabia.
Read More
FTC Safeguards Rule encryption and MFA guide cover

FTC Safeguards Rule Encryption and MFA Requirements 2026

Governance Docs29th September 2026

What the FTC Safeguards Rule requires for encryption and multi-factor authentication, plus logging, disposal and testing.
Read More
Integrated management system risk register guide cover

Integrated Management System Risk Register: One Register 2026

Governance Docs29th September 2026

How to build one integrated management system risk register that covers quality, environmental and safety risks and opportunities.
Read More
SAMA CSF incident management 3.3.15 response plan

SAMA CSF Incident Management: 3.3.15 Guide for 2026

Governance Docs29th September 2026

A guide to SAMA CSF section 3.3.15: define, approve and test an incident management process and prepare evidence…
Read More
SAMA CSF maturity levels guide cover

SAMA CSF Maturity Levels: What Level 3 Means in 2026

Governance Docs29th September 2026

What the SAMA CSF maturity levels mean, why level 3 matters and how to prepare evidence for a…
Read More
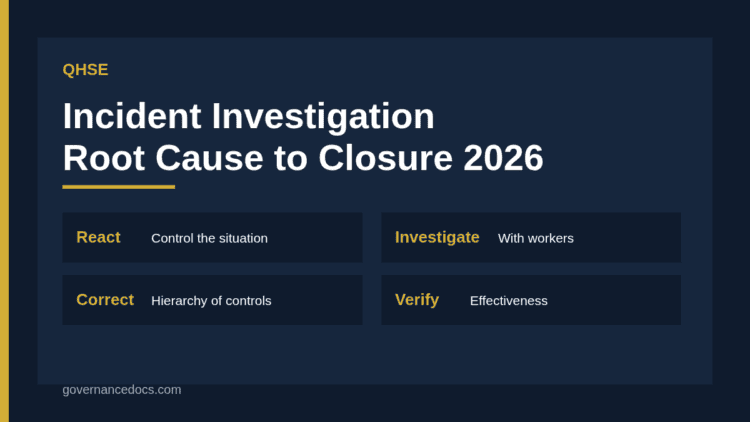
QHSE incident investigation guide cover

QHSE Incident Investigation: Root Cause to Closure 2026

Governance Docs29th September 2026

A practical QHSE incident investigation process: immediate response, root cause analysis with workers, corrective action and effectiveness review.
Read More
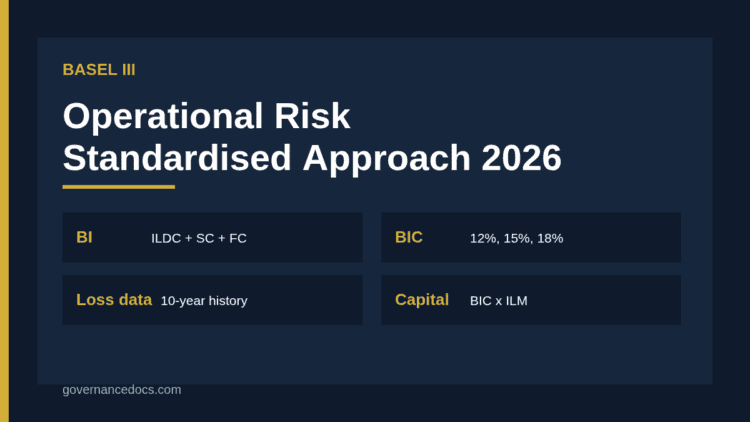
Basel III operational risk standardised approach guide cover

Basel III Operational Risk Standardised Approach Guide 2026

Governance Docs29th September 2026

How the Basel III operational risk standardised approach works: business indicator, coefficients, loss component and data needs.
Read More
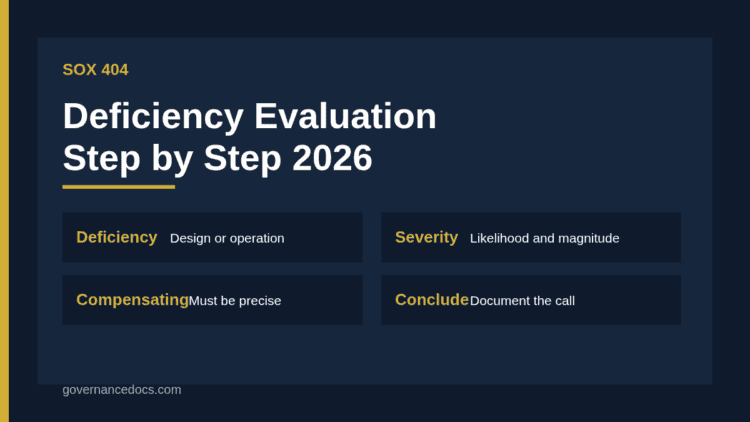
SOX control deficiency evaluation guide cover

SOX Control Deficiency Evaluation: A Step-by-Step Guide 2026

Governance Docs29th September 2026

How to evaluate a SOX control deficiency: severity, magnitude, compensating controls, material weakness indicators and documentation.
Read More
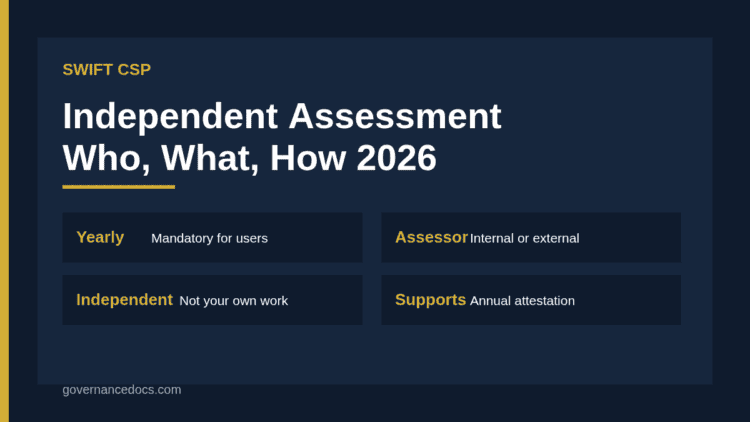
SWIFT CSP independent assessment guide cover

SWIFT CSP Independent Assessment: Who, What and How 2026

Governance Docs29th September 2026

Who can perform a SWIFT CSP independent assessment, what must be reviewed and how findings support the annual…
Read More

    ←
  • 1
  • 2
  • 3
  • 4
  • 5
  • …
  • 10
  • →

Recent Posts

ISO 27001 password policy requirements under Annex A 5.17 and A.8.5, with NIST, PCI DSS and Cyber Essentials length baselines compared
ISO 27001 Password Policy: Complete 2026 Requirements Guide

October 20, 2026

ISO 27001 intellectual property rights: the six categories in Annex A control 5.32
ISO 27001 Intellectual Property Rights: Complete 2026 Guide

October 20, 2026

ISO 27001 independent review under Annex A 5.35 compared with the clause 9.2 internal audit and clause 9.3 management review
ISO 27001 Independent Review: Complete A.5.35 Guide 2026

October 19, 2026

ISO 27001 acceptable use policy requirements under Annex A control A.5.10
ISO 27001 Acceptable Use Policy: Complete 2026 Guide

October 19, 2026

ISO 27001 network security controls A.8.20, A.8.21 and A.8.22 compared
ISO 27001 Network Security: Complete A.8.20–8.22 Guide 2026

October 18, 2026

Categories

  • Articles
  • DORA
  • GDPR
  • HIPAA
  • ISO 27001
  • ISO 42001 & AI governance
  • ISO 9001
  • Management systems
  • NIS2
  • Security frameworks
  • SOC 2
Governance DocsGovernance Docs

Reliable ISO & compliance documentation toolkits that help your business meet regulatory standards with ease.

Governance Docs LLC
1209 Mountain Road Pl NE, Suite R
Albuquerque, NM 87110, USA
[email protected]
+1 505 289 2455

Toolkits

  • ISO 27001:2022
  • GDPR
  • SOC 2
  • PCI-DSS v4.0
  • HIPAA
  • ISO 42001
  • All toolkits →

Company

  • About Us
  • Blog
  • Contact
  • FAQ
  • Which toolkit do I need?
  • Free templates
  • SoA generator
  • Assessments
  • Sample reports
  • RSS feeds

Policies

  • Privacy Policy
  • Terms & Conditions
  • Refund & Return Policy
  • Delivery Policy
  • Manage cookies
Browse by topicISO 27001ISO 42001 & AI governanceGDPRSOC 2HIPAANIS2DORAISO 9001Management systemsSecurity frameworks
© 2026 Governance Docs LLC. All rights reserved.
Secure checkoutstripeVISA