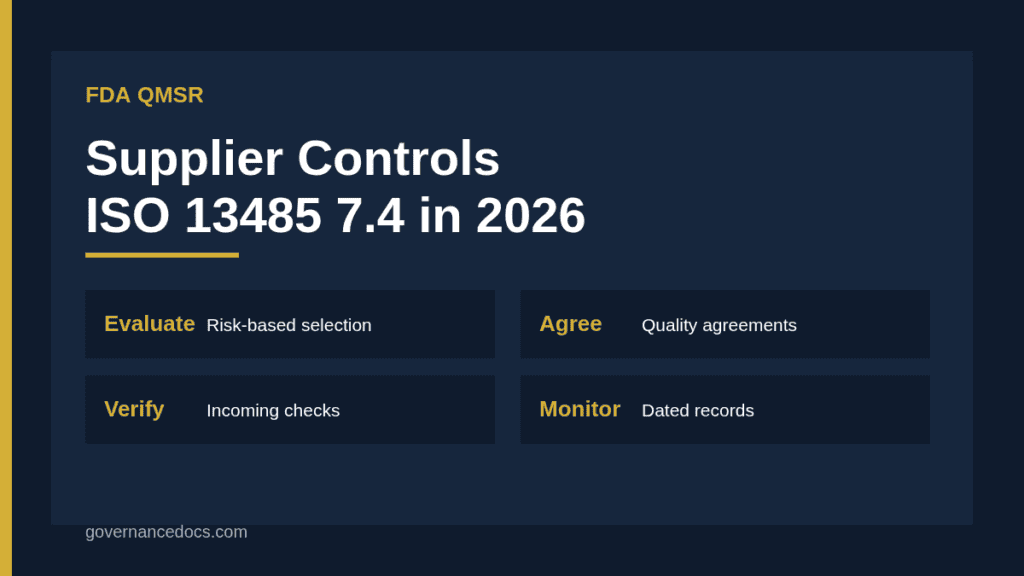
QMSR supplier controls are the purchasing and supplier rules that medical device manufacturers must follow now that the FDA’s Quality Management System Regulation applies. The regulation took effect on 2 February 2026 and incorporates ISO 13485:2016 by reference, so the detail on suppliers now comes from clause 7.4 of that standard instead of the old 21 CFR 820.50 wording. This guide explains what to expect, what evidence inspectors are likely to ask for and how to organise a supplier programme that stands up to review.
The FDA’s own page describes the change and the new inspection process. For background on how the two documents fit together, see our guides to QMSR versus ISO 13485 and the QSR to QMSR transition. The standard’s text is licensed, so this article paraphrases it and you should read your own copy.
Free gap assessment
How much of ISO 13485 could you evidence today?
Score clauses 4 to 8, free, with the FDA QMSR and EU MDR duties kept separate so you can see what is the standard and what is the regulator.
A practitioner guide to the regulation groups the supplier duties under ISO 13485 clause 7.4 into four areas. Treat the table as a working checklist, and verify it against your licensed copy of the standard.
Area
What it means
Typical evidence
Evaluation and selection
Assess suppliers in proportion to the risk their product poses to device safety and performance
Criteria, risk ratings, approved supplier list
Purchasing information and agreements
Define and agree quality requirements before purchase
Purchase specifications, signed quality agreements
Verification of purchased product
Confirm that what you receive meets requirements
Incoming inspection or certificates of conformance
These areas apply to purchased products and services that affect the conformity of your device, from raw materials and components to sterilisation services and calibration labs. Anything that touches product quality belongs in scope.
How QMSR supplier controls differ from the old QSR
The old rule handled purchasing in a short section, and many companies met it with an approved supplier list and a periodic review. One practitioner guide argues that the new approach makes ongoing monitoring explicit and expects dated evidence, so that a supplier approved years ago with no activity since becomes a weak point in inspection. Treat this as a helpful warning rather than a quote from the regulation, and check how your own quality system handles re-evaluation.
The FDA has also moved to a new inspection process. According to its QMSR page, Compliance Program 7382.850 took effect on 2 February 2026 and replaced the earlier approach. Read the current programme and our note on QMSR inspections to see what investigators are now asked to review.
Step 1: Build a risk-based approved supplier list
Start with an inventory of every external provider that affects product quality. Classify each by risk: a supplier of a sterile barrier or a software component in a life-critical device is higher risk than a supplier of office supplies or packaging that never touches the device. The classification decides how much control you apply.
Critical: supplier failure could harm patients or cause a recall. Expect audits, quality agreements and tight monitoring.
Significant: supplier affects performance but with less severe consequences. Expect questionnaires, certificate review and periodic scorecards.
Low: minimal effect on the device. Expect basic purchasing checks.
Record the reasoning for each rating. Inspectors want to see why a supplier was treated the way it was, and a written rationale answers that question.
Step 2: Set quality agreements
A quality agreement turns your expectations into a contract. It should cover specifications, change notification, the right to audit, record retention, handling of nonconforming product, complaint cooperation and subcontracting. Change notification is the most important clause for critical suppliers. Without it, a supplier can change a process or material and you learn about it from a field failure. Have each agreement signed by both sides and store it with the supplier file.
Step 3: Verify what you receive
Verification can take several forms: incoming inspection, testing a sample, review of a certificate of conformance or reliance on the supplier’s own controls, if you have validated them. Match the method to the risk. Record the results, and connect nonconformances to your corrective action process, as described in our guide to QMSR CAPA.
Step 4: Monitor and re-evaluate
Monitoring is where many programmes fall short. Define performance measures such as on-time delivery, rejection rate, complaint linkage and audit findings. Review them at a set frequency, for example quarterly for critical suppliers and annually for lower tiers. When performance drops, act: request a corrective action, increase inspection, audit or, if needed, disqualify the supplier.
Supplier audits give the deepest insight, and audits of your own quality system are covered by a separate process, as our QMSR internal audit guide explains. Coordinate the two so that supplier findings feed management review.
Handling supplier nonconformances
When a supplier delivers nonconforming product, quarantine it, record the nonconformance, notify the supplier and decide on disposition. Then ask whether the problem is isolated or systemic. A repeated defect calls for a formal supplier corrective action request with a due date, and a check that the fix works. Feed trends into management review so leaders see which suppliers create the most quality cost and risk.
Records to keep for inspection
The approved supplier list with the risk rating and rationale.
Signed quality agreements and specifications.
Incoming verification records.
Dated monitoring records and scorecards.
Audit reports and corrective action closure evidence.
Records of disqualification decisions.
Keep them accessible in one supplier file per critical supplier, so an inspector can follow the relationship from selection to the latest review.
Managing suppliers of software and services under QMSR supplier controls
Software components, cloud services and contract engineering teams need the same discipline as physical parts. If your device uses third-party software, treat the vendor as a supplier: evaluate it, agree change notification, verify releases before you adopt them and monitor for security advisories. For cloud services that store or process quality records, confirm how data is protected, backed up and retrieved, and keep the evidence with the supplier file. The requirements of the 21 CFR Part 820 framework still expect records to be controlled and retrievable, so an outage at a supplier should never leave you unable to produce them.
Working with critical suppliers over time
For critical suppliers, treat the relationship as continuous. Hold regular review meetings, share complaint trends that involve their parts and involve them in root cause work. Ask about planned changes in ownership, sites and processes, and record the answers. Sharing forecasts helps them plan, and clear communication makes it easier to act when something goes wrong. Together these habits are what turn QMSR supplier controls from a filing exercise into a working quality process.
Metrics that show the programme works
Choose a handful of measures and track them each quarter: percentage of critical suppliers with a current agreement, percentage re-evaluated on schedule, supplier lot rejection rate, number of supplier corrective actions open past due and number of unplanned supplier changes discovered late. Present them at management review. If a measure worsens, look for the cause in resourcing, communication or the supplier’s own capacity.
Also review how you onboard emergency or one-time suppliers. A rushed purchase during a shortage is exactly when quality shortcuts appear, so give buyers a short, fast route that still records the risk rating, the agreement and the verification plan.
A hypothetical example
A hypothetical maker of infusion pump components buys a molded housing from a contract manufacturer. It rates the supplier as critical, signs a quality agreement that requires notice of any tooling change, inspects a sample from every lot and reviews rejection rates each quarter. When the supplier moves a mold to a new plant without notice, the incoming inspection catches dimensional drift, the manufacturer opens a corrective action and audits the new site. Inspection records and the audit report show the whole story. The example is invented for illustration.
Common findings on QMSR supplier controls
Approved supplier list with no risk rationale.
Quality agreements missing or unsigned.
No dated evidence of ongoing monitoring after initial approval.
Supplier nonconformances not linked to corrective action.
Outsourced processes, such as sterilisation, treated as out of scope.
Use the FDA QMSR page as your primary source for the regulation and inspection programme.
Templates for QMSR supplier controls
To avoid building supplier evaluation forms, quality agreements and monitoring logs from scratch, the FDA QMSR Toolkit provides documents you can adapt. Have your regulatory affairs lead confirm them against your licensed copy of ISO 13485.
QMSR supplier controls FAQ
Where do supplier requirements come from under QMSR?
From ISO 13485:2016, which the regulation incorporates by reference. Clause 7.4 covers purchasing.
Is a certificate of conformance enough?
It can be, when justified by risk and supported by supplier evaluation. For critical items, add sampling, testing or audit.
How often should suppliers be re-evaluated?
Set the frequency by risk and record it. Many companies review critical suppliers at least annually, though the standard does not fix an interval.
Do outsourced processes count?
Yes. Services that affect product conformity, such as sterilisation or calibration, fall under supplier controls.
What do inspectors look for?
They look for documented risk-based selection, signed agreements, verification records and dated monitoring, as well as follow-up on problems.