About Us Contact Blog
Governance DocsGovernance Docs
Which Toolkit?SoA GeneratorFree TemplatesSample ReportsFind the Right AssessmentRecords of Processing (ROPA)Data Privacy Impact AssessmentLegitimate Interests AssessmentTransfer Impact AssessmentPrivacy Risk AssessmentGDPR Gap AssessmentUK GDPR Gap AssessmentCCPA/CPRA Gap AssessmentISO 27701 Gap AssessmentHIPAA Gap AssessmentISO 27001 Risk AssessmentThird-Party Risk AssessmentSoA GeneratorISO 27001 Assessment Tool (Excel)ISO 27001 Gap AssessmentSOC 2 Gap AssessmentNIST CSF 2.0 Gap AssessmentNIST SP 800-53 Gap AssessmentNIST RMF Gap AssessmentCIS Controls Gap AssessmentPCI DSS 4.0 Gap AssessmentNIS2 Gap AssessmentCMMC 2.0 Gap AssessmentNIST SP 800-171 Gap AssessmentFedRAMP Gap AssessmentBSI C5 Gap AssessmentIEC 62443 Gap AssessmentSAMA CSF Gap AssessmentNCA ECC Gap AssessmentISO 20000 Gap AssessmentAI Risk AssessmentAI Impact AssessmentISO 42001 Gap AssessmentEU AI Act Gap AssessmentBusiness Impact AnalysisContinuity Risk AssessmentISO 22301 Assessment Tool (Excel)ISO 22301 Gap AssessmentDORA Gap AssessmentISO 9001 Gap AssessmentISO 13485 Gap AssessmentIATF 16949 Gap AssessmentISO 14001 Gap AssessmentISO 45001 Gap AssessmentISO 45001 Assessment Tool (Excel)HACCP Gap AssessmentEnterprise Risk AssessmentISO 31000 Gap AssessmentData Governance Gap AssessmentProject Management Gap AssessmentAll Gap AssessmentsAboutBlogContactMy AccountCart
FOX v.2.4.9
Browse Toolkits
Governance Docs
  • Browse All Toolkits
  • Information Security & Cybersecurity
  • Data Privacy & Protection
  • Governance, Risk & Compliance
  • Quality Management
  • Health, Safety & Environment
  • AI Governance

My Account

CART

No products in the cart.

Day: September 19, 2026

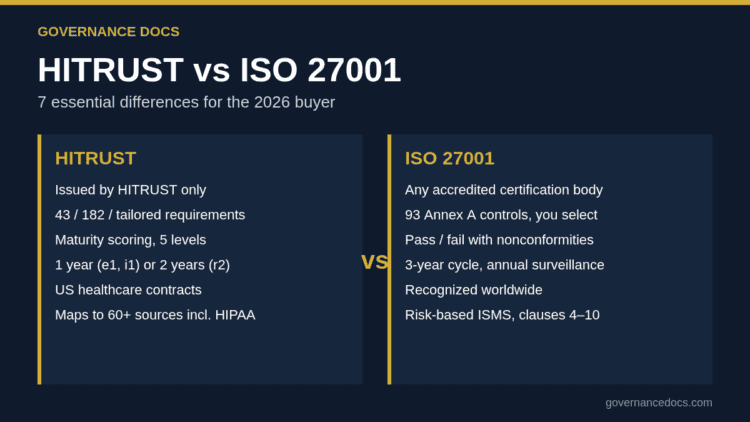
HITRUST vs ISO 27001 comparison: issuer, controls, scoring, validity and recognition side by side

HITRUST vs ISO 27001: 7 Essential Differences Explained (2026)

Governance Docs19th September 2026

HITRUST vs ISO 27001 compared on issuer, controls (43/182/tailored vs 93), scoring, validity (1–2 vs 3 years), cost…
Read More
compliance consultant certifications explained

Compliance Consultant Certifications: 6 Essential Credentials

Governance Docs19th September 2026

Compliance consultant certifications: Lead Auditor, CISA, CISSP, CISM/CRISC, CCEP, CIPP/E — what each proves, the issuers' prerequisites, and…
Read More
fixed fee vs time and materials explained

Fixed Fee vs Time and Materials: A Clear Guide for Consultants

Governance Docs19th September 2026

Fixed fee vs time and materials for compliance consultants: the 6 differences, which engagements suit each, the hybrids,…
Read More
compliance consulting rates explained

Compliance Consulting Rates in 2026: The Complete Breakdown

Governance Docs19th September 2026

Compliance consulting rates in 2026: day rates by seniority and market, fixed-fee ranges for ISO 27001, SOC 2,…
Read More
facility condition assessment explained

Facility Condition Assessment: A Complete Guide to the FCI (2026)

Governance Docs19th September 2026

Facility condition assessment and the FCI: what is surveyed, ASTM E2018 as the baseline, FCI = deferred maintenance…
Read More
ISO 41001 mandatory documents explained

ISO 41001 Mandatory Documents: The Complete Clause-by-Clause List

Governance Docs19th September 2026

ISO 41001 mandatory documents under the 2018 edition: 14 clause requirements, the 6 FM-specific ones (7.6, 8.2, 8.3,…
Read More
hard FM vs soft FM explained

Hard FM vs Soft FM: 6 Essential Differences Explained (2026)

Governance Docs19th September 2026

Hard FM vs soft FM: what belongs in each, the 6 differences that change how you manage them,…
Read More
facility management strategy explained

Facility Management Strategy: The Complete ISO 41001 Guide (2026)

Governance Docs19th September 2026

Facility management strategy per ISO 41011 and ISO 41014: the inputs, the 6 sections, how it differs from…
Read More
ISO 41001 certification cost explained

ISO 41001 Certification Cost in 2026: The Complete Breakdown

Governance Docs19th September 2026

ISO 41001 certification cost: audit fees over 3 years, FM system build, consultancy, staff time — $12,000 to…
Read More
ISO 39001 vs ISO 45001 explained

ISO 39001 vs ISO 45001: 5 Clear Differences for Fleets (2026)

Governance Docs19th September 2026

ISO 39001 vs ISO 45001: who is in scope, Safe System against the hierarchy of controls, worker participation,…
Read More
road traffic safety objectives explained

Road Traffic Safety Objectives: A Complete ISO 39001 Guide (2026)

Governance Docs19th September 2026

Road traffic safety objectives under ISO 39001 clause 6.4: derive them from the performance factors, worked objectives per…
Read More
fleet safety policy explained

Fleet Safety Policy: The Complete Guide to the 7 Sections (2026)

Governance Docs19th September 2026

Fleet safety policy under ISO 39001 clause 5.2: the 7 sections and the rules in each — drivers,…
Read More
  • 1
  • 2
  • 3
  • …
  • 8
  • →

Recent Posts

ISO 27001 configuration management requirements under Annex A 8.9 - established, documented, implemented, monitored, reviewed
ISO 27001 Configuration Management: Complete 2026 Guide

October 11, 2026

internal audit findings rating scale — Internal Audit Findings Rating Scale: Examples and Template
Internal Audit Findings Rating Scale: Examples and Template

October 11, 2026

third party topical requirement — Third Party Topical Requirement: The 2026 Audit Guide
Third Party Topical Requirement: The 2026 Audit Guide

October 11, 2026

cybersecurity topical requirement — Cybersecurity Topical Requirement: How to Audit It in 2026
Cybersecurity Topical Requirement: How to Audit It in 2026

October 11, 2026

quality assurance and improvement program — Quality Assurance and Improvement Program (QAIP): 2026 Guide
Quality Assurance and Improvement Program (QAIP): 2026 Guide

October 11, 2026

Categories

  • Articles
  • DORA
  • GDPR
  • HIPAA
  • ISO 27001
  • ISO 42001 & AI governance
  • ISO 9001
  • Management systems
  • NIS2
  • Security frameworks
  • SOC 2
Governance DocsGovernance Docs

Reliable ISO & compliance documentation toolkits that help your business meet regulatory standards with ease.

Governance Docs LLC
1209 Mountain Road Pl NE, Suite R
Albuquerque, NM 87110, USA
info@governancedocs.com
+1 505 289 2455

Toolkits

  • ISO 27001:2022
  • GDPR
  • SOC 2
  • PCI-DSS v4.0
  • HIPAA
  • ISO 42001
  • All toolkits →

Company

  • About Us
  • Blog
  • Contact
  • FAQ
  • Which toolkit do I need?
  • Free templates
  • SoA generator
  • Assessments
  • Sample reports
  • RSS feeds

Policies

  • Privacy Policy
  • Terms & Conditions
  • Refund & Return Policy
  • Delivery Policy
  • Manage cookies
Browse by topicISO 27001ISO 42001 & AI governanceGDPRSOC 2HIPAANIS2DORAISO 9001Management systemsSecurity frameworks
© 2026 Governance Docs LLC. All rights reserved.
Secure checkoutstripeVISA