An ISO 27001 gap assessment delivers 4 outputs: a gap register, a prioritized remediation plan, a draft SoA and a readiness estimate. How to run or buy one.
An ISO 27001 self-assessment scores clauses 4–10 and all 93 Annex A controls on a 5-point scale with evidence: how to run it, and 5 ways it flatters authors.
PCI DSS vs ISO 27001 on 5 differences — scope, enforcement, prescription, assessment cadence, output — with all 12 PCI requirements mapped to Annex A controls.
ISO 27001 vs ISO 27701: since the 2025 edition a privacy system can be certified alone. Which you need, what overlaps, and the 31 October 2028 deadline.
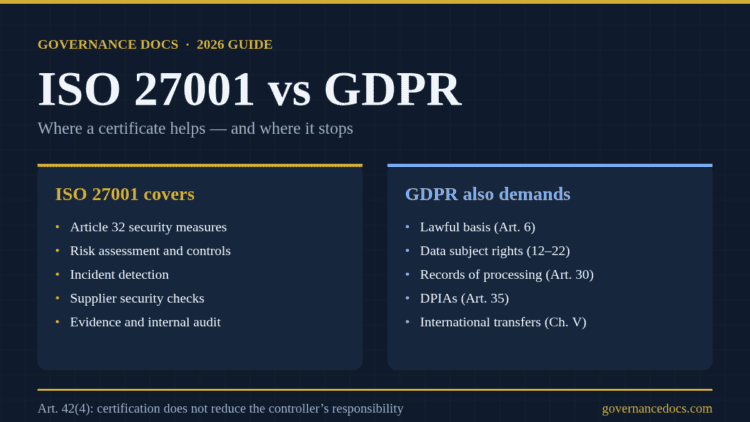
ISO 27001 vs GDPR: certification proves you secure data, but GDPR asks whether you should hold it at all. The overlaps, the five gaps, and what to build first.
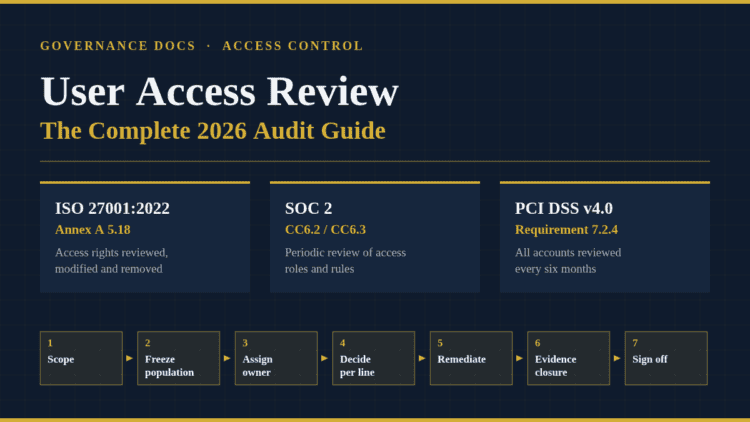
A user access review is the control auditors test hardest. Here is the seven-step process, the ISO 27001 A.5.18, SOC 2 CC6.3 and PCI DSS 7.2.4 mapping, the right cadence...
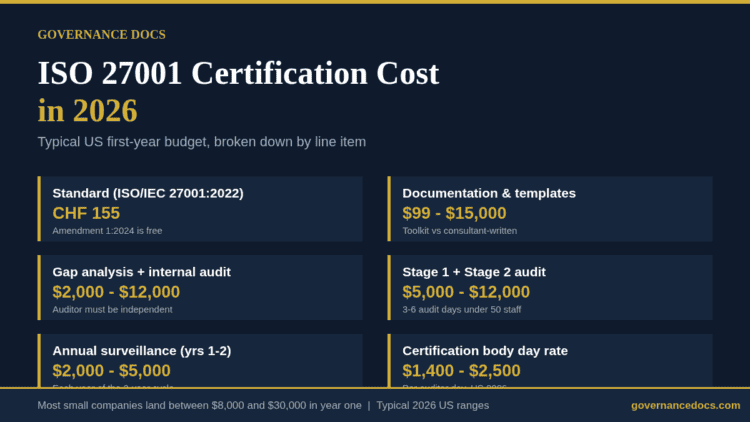
ISO 27001 certification cost in 2026 runs $8,000 to $30,000 for most small US companies. A full line-item breakdown of audit fees, day rates and ongoing costs.
An ISO 27001 maturity assessment scores how well a control works, not whether it exists. The 6 levels, what to score, and where the exercise loses credibility.