Threat intelligence under ISO 27001 control 5.7: the 3 levels, the 5 artefacts that make it auditable, and why a subscription nobody reads fails the control.
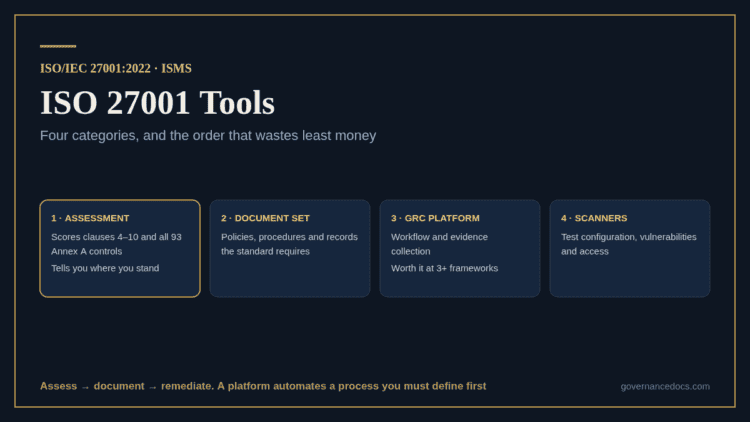
ISO 27001 tools range from a spreadsheet to a GRC platform. The 4 categories, what an assessment tool must cover, and how to choose in the right order.
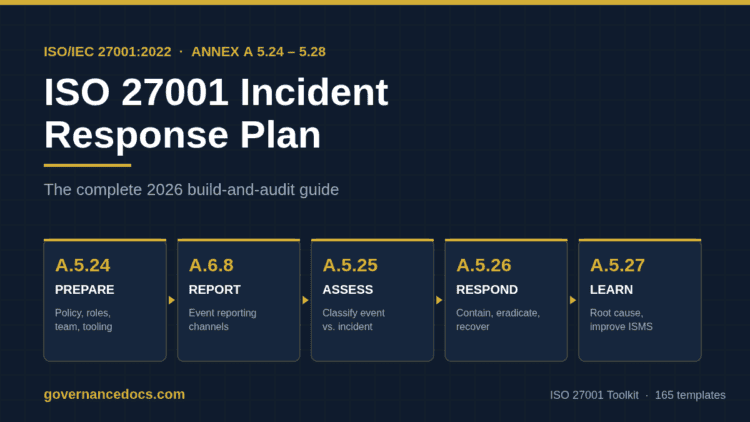
What an ISO 27001 incident response plan must contain, the Annex A 5.24 to 5.28 controls behind it, a seven-step build, the 24 and 72 hour reporting clocks, and the...
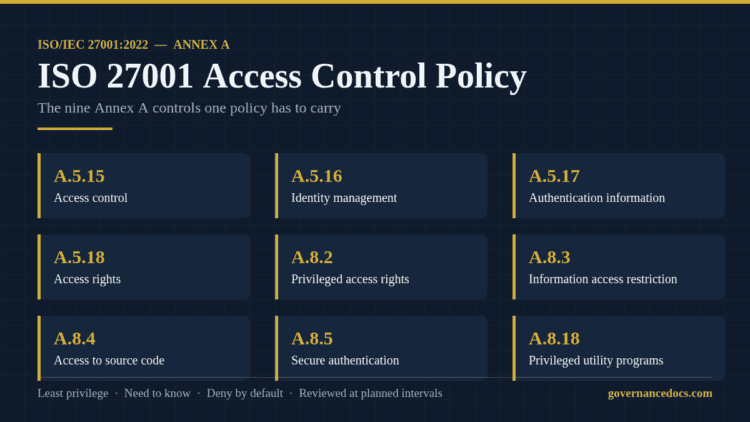
What an ISO 27001 access control policy must contain in 2026 — the nine Annex A controls it carries, a ten-section outline, review cadence, audit evidence and the five mistakes...
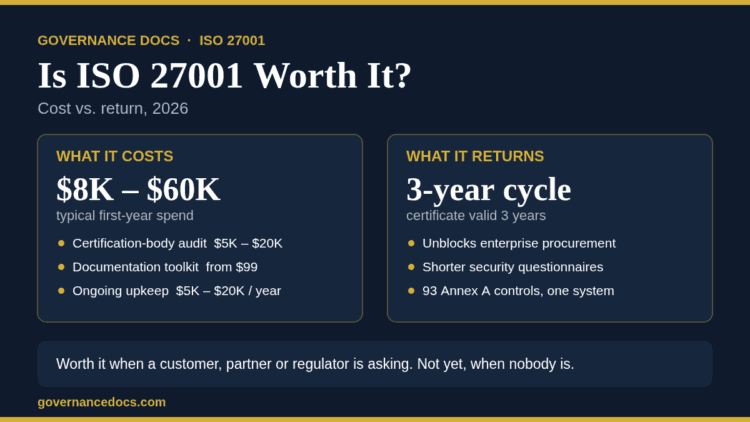
Is ISO 27001 worth it in 2026? A straight cost-versus-return breakdown: typical $8,000-$60,000 first-year spend, what certification actually unblocks, and when to skip it.
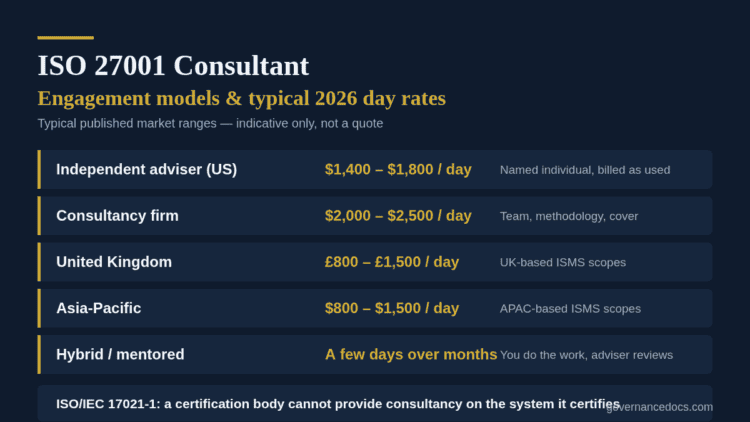
What an ISO 27001 consultant does, what day rates look like in 2026, the impartiality rule that stops your adviser certifying you, and how consultant, toolkit and platform routes compare.
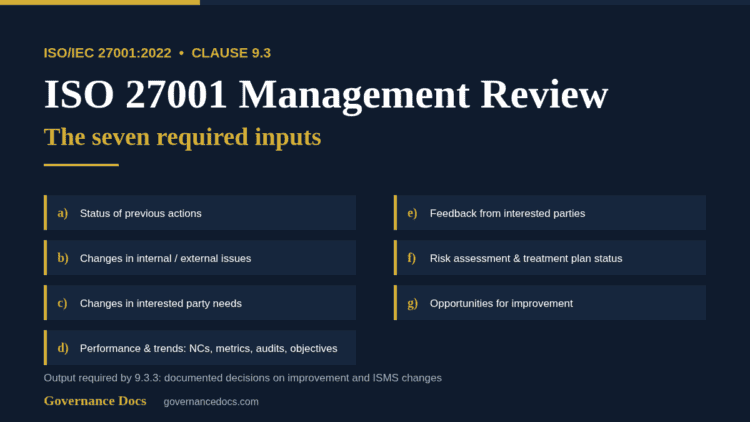
What ISO 27001 clause 9.3 requires: the seven management review inputs, how often to meet, what to minute, and the mistakes that cause nonconformities.
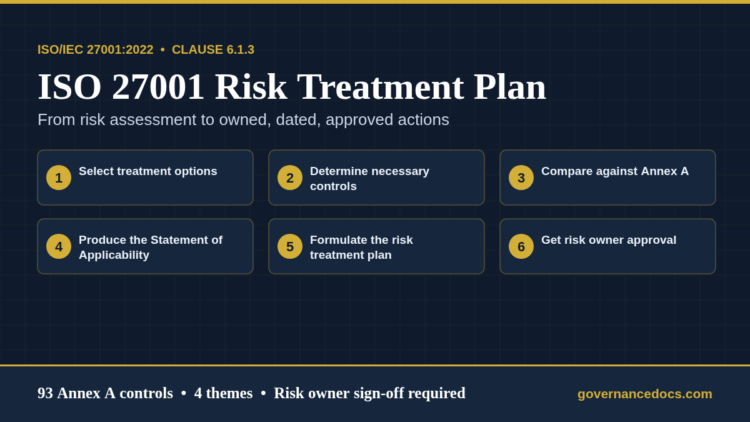
An ISO 27001 risk treatment plan is required by clause 6.1.3. Here are the fields it needs, the four treatment options, and the mistakes that become audit findings.