About Us Contact Blog
Governance DocsGovernance Docs
Which Toolkit?SoA GeneratorFree TemplatesGap AssessmentsBusiness Impact AnalysisISO 27001 Risk AssessmentPrivacy Risk AssessmentContinuity Risk AssessmentEnterprise Risk AssessmentAI Risk AssessmentDPIA TemplateTransfer Impact AssessmentAI Impact AssessmentLIA TemplateThird-Party Risk AssessmentSample ReportsAboutBlogContactMy AccountCart
FOX v.2.4.9
Browse Toolkits
Governance Docs
  • Browse All Toolkits
  • Information Security & Cybersecurity
  • Data Privacy & Protection
  • Governance, Risk & Compliance
  • Quality Management
  • Health, Safety & Environment
  • AI Governance

My Account

CART

No products in the cart.

Day: September 8, 2026

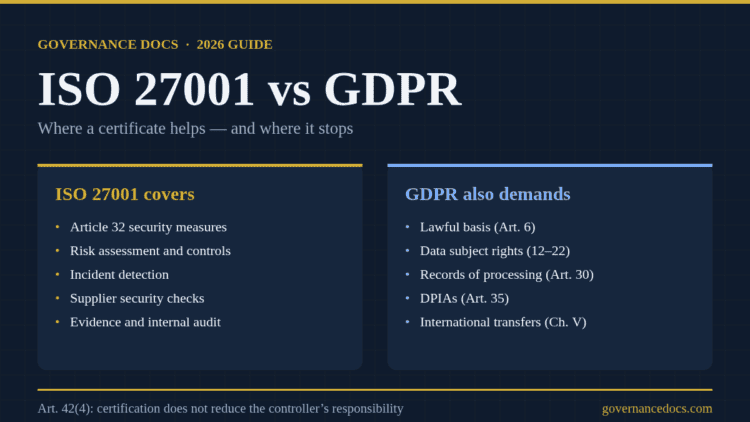
ISO 27001 vs GDPR — what ISO 27001 covers and what GDPR still demands

ISO 27001 vs GDPR: The Complete 2026 Compliance Guide

Governance Docs08th September 2026

ISO 27001 vs GDPR: certification proves you secure data, but GDPR asks whether you should hold it at…
Read More
remote key distribution — PCI PIN Remote Key Distribution: Normative Annex A Explained

PCI PIN Remote Key Distribution: Normative Annex A Explained

Governance Docs08th September 2026

Remote key distribution under PCI PIN Annex A: the two sub-annexes, the design assurance requirement, the three barrier…
Read More
key injection facility — PCI PIN Key Injection Facilities: Normative Annex B Explained

PCI PIN Key Injection Facility: Normative Annex B Explained

Governance Docs08th September 2026

Key injection facility requirements under PCI PIN Annex B: the secure room, the clear-text injection dates and their…
Read More
Qualified PIN Assessor — Qualified PIN Assessor: What a PCI PIN Assessment Involves

Qualified PIN Assessor: What a PCI PIN Assessment Involves

Governance Docs08th September 2026

Qualified PIN Assessor explained: no self-assessment route, observation-led testing, the two-year listing clock that starts at signature, and…
Read More
dual control and split knowledge — Dual Control and Split Knowledge: The Difference That Fails Audits

Dual Control and Split Knowledge: The Difference That Fails Audits

Governance Docs08th September 2026

Dual control and split knowledge are two separate controls, not one. What each requires, the arrangements that look…
Read More
PCI PIN scope — PCI PIN Scope: Which of the 145 Requirements Apply to You

PCI PIN Scope: Which of the 145 Requirements Apply to You

Governance Docs08th September 2026

PCI PIN scope explained: the four requirement columns, why 96 + 85 + 105 + 94 does not…
Read More
PCI PIN key blocks — PCI PIN Key Blocks: The 3 Phases and What Phase 3 Did Not Require

PCI PIN Key Blocks: The 3 Phases and What Phase 3 Did Not Require

Governance Docs08th September 2026

PCI PIN key blocks explained: the three phases, why Phase 3 never required existing POI deployments to convert,…
Read More
PCI PIN vs PCI DSS — PCI PIN vs PCI DSS: Which One Applies to You in 2026

PCI PIN vs PCI DSS: Which One Applies to You in 2026

Governance Docs08th September 2026

PCI PIN vs PCI DSS explained: different assessors, no self-assessment route for PIN, a two-year cycle, and scope…
Read More
PCI PIN Security Requirements — PCI PIN Security Requirements: A Complete Guide to v3.1 in 2026

PCI PIN Security Requirements: A Complete Guide to v3.1 in 2026

Governance Docs08th September 2026

PCI PIN Security Requirements v3.1 explained: 7 control objectives, 33 requirements, 145 sub-requirements, the four scope columns and…
Read More
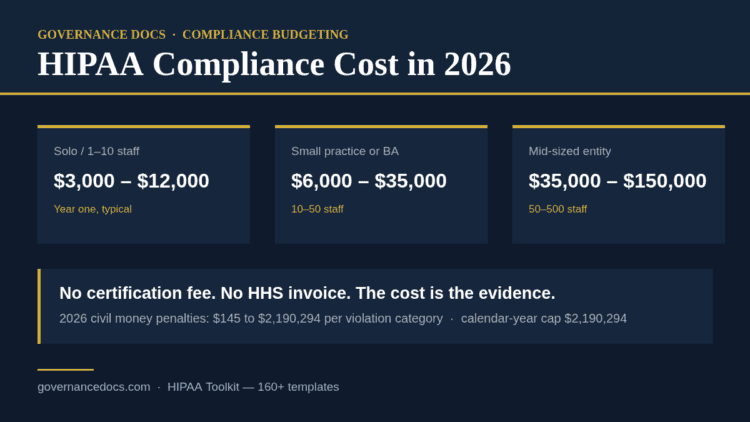
HIPAA compliance cost in 2026 broken down by organization size, with 2026 civil money penalty figures

HIPAA Compliance Cost in 2026: The Complete Breakdown

Governance Docs08th September 2026

HIPAA compliance cost in 2026 runs $3,000 to $35,000 in year one for most small organizations. A full…
Read More

Recent Posts

Vendor offboarding checklist phases: transition, access removal and close out
Vendor Offboarding Checklist: The Complete 2026 Guide to Exiting a Vendor

September 28, 2026

SaaS vendor risk assessment checks: evidence to request, SaaS-specific risks and depth by tier
SaaS Vendor Risk Assessment: The Essential 2026 Guide

September 28, 2026

Third-party risk assessment example showing the tier, due diligence and decision for a critical cloud vendor
Third-Party Risk Assessment Example: A Complete 2026 Walkthrough

September 28, 2026

Chart showing why the answer to is Cyber Essentials worth it depends on buyer demand: 3% of UK businesses, 10% of high-income charities and 26% of large businesses require suppliers to hold Cyber Essentials
Is Cyber Essentials Worth It? The Complete 2026 Cost-Benefit Case

September 28, 2026

Legitimate interests examples grouped into those that usually pass, need care or usually fail
Legitimate Interests Examples: 12 Proven Cases and Where They Fail (2026)

September 28, 2026

Categories

  • Articles
  • DORA
  • GDPR
  • HIPAA
  • ISO 27001
  • ISO 42001 & AI governance
  • ISO 9001
  • Management systems
  • NIS2
  • Security frameworks
  • SOC 2
Governance DocsGovernance Docs

Reliable ISO & compliance documentation toolkits that help your business meet regulatory standards with ease.

Governance Docs LLC
1209 Mountain Road Pl NE, Suite R
Albuquerque, NM 87110, USA
info@governancedocs.com
+1 812 227 5662

Toolkits

  • ISO 27001:2022
  • GDPR
  • SOC 2
  • PCI-DSS v4.0
  • HIPAA
  • ISO 42001
  • All toolkits →

Company

  • About Us
  • Blog
  • Contact
  • FAQ
  • Which toolkit do I need?
  • Free templates
  • SoA generator
  • Gap assessments
  • Business impact analysis
  • ISO 27001 risk assessment
  • Privacy risk assessment
  • Continuity risk assessment
  • Enterprise risk assessment
  • AI risk assessment
  • DPIA template
  • Transfer impact assessment
  • AI impact assessment
  • RSS feeds

Policies

  • Privacy Policy
  • Terms & Conditions
  • Refund & Return Policy
  • Delivery Policy
  • Manage cookies
Browse by topicISO 27001ISO 42001 & AI governanceGDPRSOC 2HIPAANIS2DORAISO 9001Management systemsSecurity frameworks
© 2026 Governance Docs LLC. All rights reserved.
Secure checkoutstripeVISA