
About Us Contact Blog
Governance DocsGovernance Docs
Which Toolkit?SoA GeneratorFree TemplatesAboutBlogContactMy AccountCart
FOX v.2.4.9
Browse Toolkits
Governance Docs
  • Browse All Toolkits
  • Information Security & Cybersecurity
  • Data Privacy & Protection
  • Governance, Risk & Compliance
  • Quality Management
  • Health, Safety & Environment
  • AI Governance

My Account
CART

No products in the cart.

ISO 27001

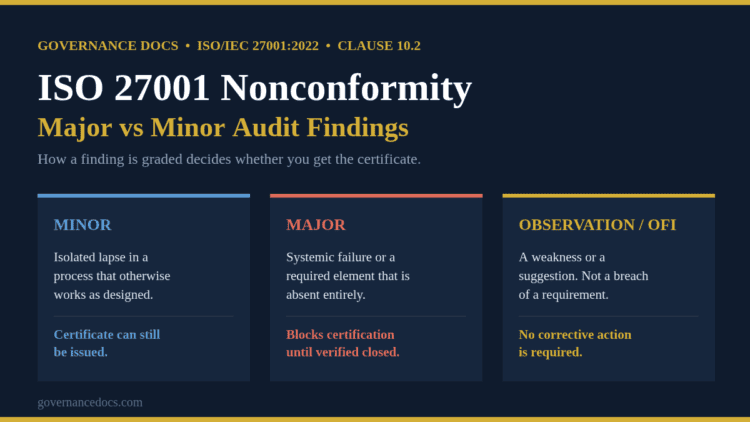
ISO 27001 nonconformity classification chart comparing major and minor audit findings

ISO 27001 Nonconformity: The Complete 2026 Guide to Major vs Minor Findings

Governance Docs22nd August 2026

How ISO 27001 nonconformity findings are classified as major or minor, the deadlines that follow, the six most common findings, and how to close corrective actions first time.
Read More
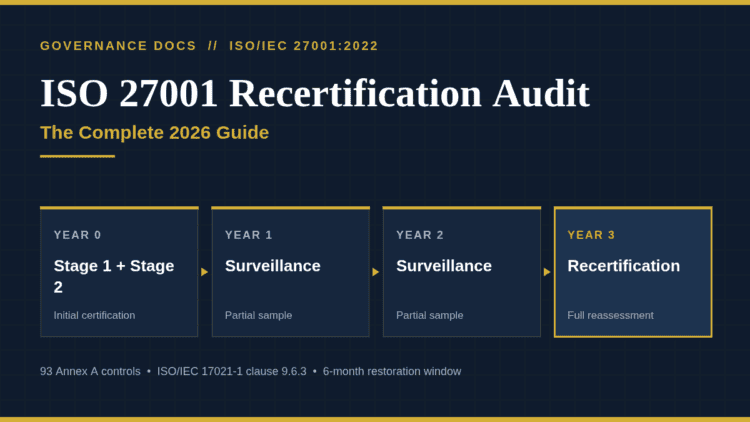
ISO 27001 recertification audit timeline showing the three-year certification cycle from Stage 1 and Stage 2 through surveillance audits to year three reassessment

ISO 27001 Recertification Audit: The Complete 2026 Guide

Governance Docs21st August 2026

What happens at the year-three ISO 27001 recertification audit: the ISO/IEC 17021-1 timing rules, what auditors sample, typical duration and cost ranges, and the six-month restoration window if your certificate...
Read More
BYOD policy requirements mapped to ISO 27001:2022 Annex A controls

BYOD Policy: The Essential 2026 Guide for ISO 27001

Governance Docs20th August 2026

A BYOD policy that survives an ISO 27001 audit: the 7 Annex A controls it satisfies, the 9 clauses it needs, and the MDM decision that shapes all of them.
Read More
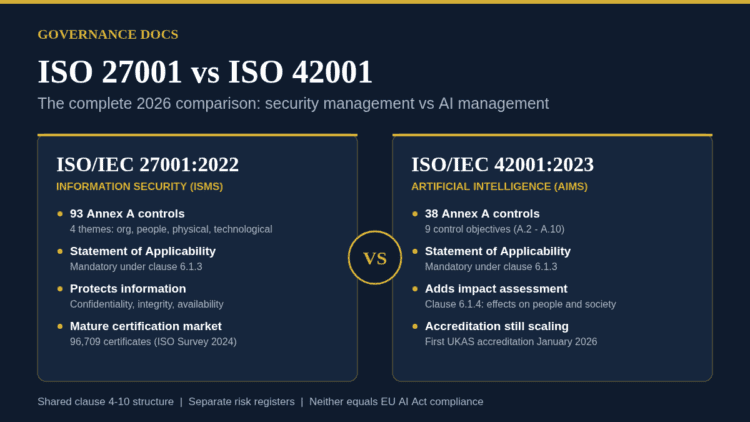
ISO 27001 vs ISO 42001 comparison chart showing 93 security controls against 38 AI controls

ISO 27001 vs ISO 42001: The Complete 2026 Comparison Guide

Governance Docs20th August 2026

ISO 27001 vs ISO 42001 compared for 2026: 93 security controls versus 38 AI controls, the shared clause structure, what the EU AI Act omnibus changed, and which one to...
Read More
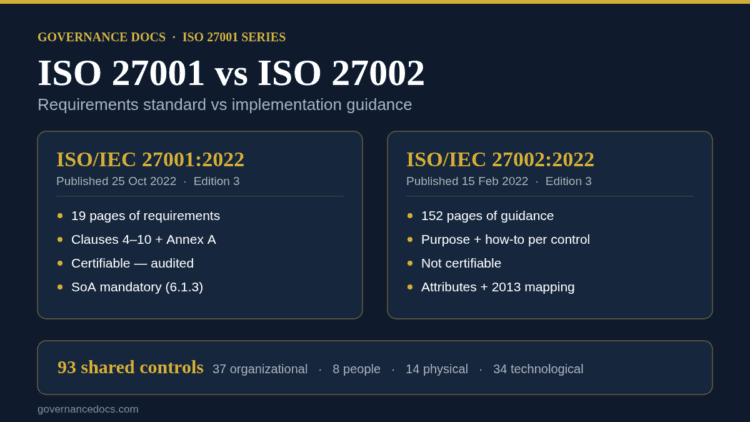
ISO 27001 vs ISO 27002 comparison chart showing the 19-page requirements standard against the 152-page implementation guidance

ISO 27001 vs ISO 27002: The Complete 2026 Guide to Which One You Need

Governance Docs19th August 2026

ISO 27001 vs ISO 27002 explained: one is a 19-page certifiable requirements standard, the other 152 pages of implementation guidance. Both cover the same 93 controls. Here is which one...
Read More
ISO 27001 scope diagram showing organizational, physical and logical ISMS boundaries under Clause 4.3

ISO 27001 Scope: The Complete 2026 Guide to Defining Your ISMS

Governance Docs18th August 2026

Your ISO 27001 scope decides your audit days, your workload and what your certificate says. Clause 4.3 rules, three scoping models, a worked example and the exclusions auditors reject.
Read More
ISO 27001 surveillance audit timeline showing the three-year certification cycle

ISO 27001 Surveillance Audit: The Complete 2026 Guide

Governance Docs17th August 2026

What an ISO 27001 surveillance audit covers, when it is due, what it costs in 2026, and how to prepare — with the exact clauses your certification body follows.
Read More
What each ISO 27001 certification audit stage tests in a readiness assessment

ISO 27001 Readiness Assessment: 6 Proven Checks

Governance Docs16th August 2026

A gap analysis asks what is missing. A readiness assessment asks whether you would pass Stage 2 — and three clauses cannot be closed by working harder.
Read More
The three levels at which segregation of duties has to be established

Segregation of Duties: 6 Proven Steps for SOX and ISO 27001

Governance Docs16th August 2026

One term covers three problems: transaction level, entitlement level and function level. What SOX 404, DORA Article 6(4) and ISO 27001 A.5.3 each demand.
Read More
The FIPS 199 impact levels and the high water mark rule for data classification

Data Classification: 6 Proven Steps for ISO 27001

Governance Docs16th August 2026

Most schemes classify confidentiality only and have no rule for mixed data. What FIPS 199 and ISO 27001 Annex A 5.12 and 5.13 actually establish.
Read More
    ←
  • 1
  • 2
  • 3
  • 4
  • 5
  • 6
  • …
  • 33
  • →

Recent Posts

ISO 9001 certification timeline 2026: six stages from gap analysis to certificate, with the ISO 9001:2026 transition dates
ISO 9001 Certification Timeline: The Complete 2026 Guide

September 21, 2026

ISO 13485 certification timeline infographic: 6–18 months from kickoff to certificate, phase by phase
ISO 13485 Certification Timeline: The Complete 2026 Guide

September 20, 2026

ISO 27001 vs HIPAA infographic comparing the voluntary ISO/IEC 27001:2022 standard with the HIPAA federal law on scope, controls, proof and consequences
ISO 27001 vs HIPAA: 7 Essential Differences Explained (2026)

September 20, 2026

HITRUST vs ISO 27001 comparison: issuer, controls, scoring, validity and recognition side by side
HITRUST vs ISO 27001: 7 Essential Differences Explained (2026)

September 19, 2026

compliance consultant certifications explained
Compliance Consultant Certifications: 6 Essential Credentials

September 19, 2026

Categories

  • Articles
  • DORA
  • GDPR
  • HIPAA
  • ISO 27001
  • ISO 42001 & AI governance
  • ISO 9001
  • Management systems
  • NIS2
  • Security frameworks
  • SOC 2
Governance DocsGovernance Docs

Reliable ISO & compliance documentation toolkits that help your business meet regulatory standards with ease.

Governance Docs LLC
1209 Mountain Road Pl NE, Suite R
Albuquerque, NM 87110, USA
info@governancedocs.com
+1 812 227 5662

Toolkits

  • ISO 27001:2022
  • GDPR
  • SOC 2
  • PCI-DSS v4.0
  • HIPAA
  • ISO 42001
  • All toolkits →

Company

  • About Us
  • Blog
  • Contact
  • FAQ
  • Which toolkit do I need?
  • Free templates
  • SoA generator
  • RSS feeds

Policies

  • Privacy Policy
  • Terms & Conditions
  • Refund & Return Policy
  • Delivery Policy
  • Manage cookies
Browse by topicISO 27001ISO 42001 & AI governanceGDPRSOC 2HIPAANIS2DORAISO 9001Management systemsSecurity frameworks
© 2026 Governance Docs LLC. All rights reserved.
Secure checkoutstripeVISA