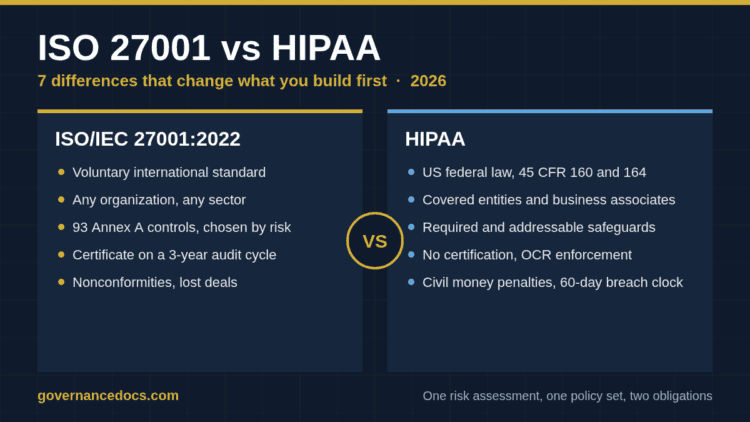
ISO 27001 vs HIPAA compared: law vs standard, 93 Annex A controls vs Security Rule safeguards, audits, breach rules, cost, and when a health-tech vendor needs both.
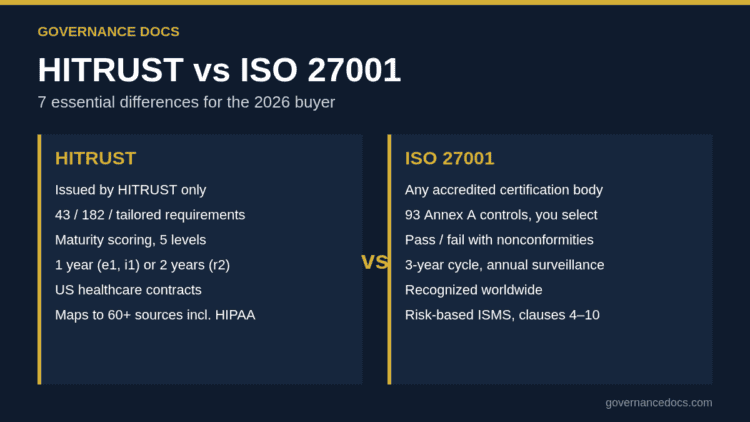
HITRUST vs ISO 27001 compared on issuer, controls (43/182/tailored vs 93), scoring, validity (1–2 vs 3 years), cost and recognition, plus when to pursue each.
NIST CSF vs ISO 27001 on 5 differences: outcome framework vs certifiable system, Profiles vs certificate, scope, prescription, demand — with the mapping.
CIS Controls ISO 27001 mapping: all 18 Controls to the 93 Annex A controls of ISO 27001:2022, where CIS goes deeper, what ISO adds, and how to use it both...
NIST 800-53 vs ISO 27001 on 5 differences: catalogue vs certifiable system, baseline vs risk assessment, granularity, assessment vs certification, demand.
ISO 20000 vs ISO 27001 on 5 differences: purpose, what the audit tests, who asks, overlap, and which to certify first — plus how to run both from one system.
The ISO 27001 assessment report in 6 sections — summary, method, clause results, Annex A results, findings, action plan — and the traps that make one weak.
A supplier security assessment under ISO 27001 controls A.5.19–A.5.22: tier suppliers, what to ask, what evidence to accept, and how to keep the review alive.
The ISO 27001 control assessment: scoring all 93 Annex A controls for applicability, implementation and evidence, with the 5 ISO 27002 attributes for reporting.