

ISO 55001 vs ISO 41001 vs ISO 50001: Which One Do You Need?
ISO 55001, ISO 41001 and ISO 50001 manage different things about the same estate. What each one actually…
CART
ISO 55001, ISO 41001 and ISO 50001 manage different things about the same estate. What each one actually…
Teams adopting COBIT, ISO 31000 and the CIS Controls often assume they are choosing between them. They are not. Each occupies a different layer of the same problem, and an
A practical 2026 guide to choosing an accredited ISO 27001 certification body: what changed on 1 January 2026,…
If your institution is on the SWIFT network, security is not a matter of internal policy. SWIFT CSP attestation is an annual obligation: every member must attest against the Customer
There is no single rulebook for finance. Financial services compliance is a patchwork determined by what you do and where you do it — a bank in Riyadh, a European
Most organisations arrive at quality, health and safety, and environment separately — three managers, three manuals, three audit schedules, three sets of paperwork that say much the same thing. A
Sarbanes-Oxley made internal control a named personal responsibility: under Sections 302 and 404, executives sign to say the controls over financial reporting work, and auditors test whether that signature is
Healthcare vendors get asked for HIPAA compliance constantly, and increasingly for HITRUST certification as well. The two are often spoken of as if they were alternatives, which they are not.
Sooner or later a prospect asks a cloud provider to prove its security, and the honest first answer is a question: prove it to whom? There is no single cloud
A NIST SP 800-30 risk assessment is how you work out which risks actually matter to your organisation. The NIST Cybersecurity Framework tells you what good security looks like. It
Every security team is asked the same question by its board sooner or later: are we getting safer? Answering it means reporting numbers — and that is where cybersecurity KRIs
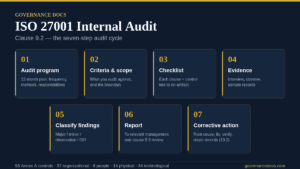
What ISO 27001 clause 9.2 requires from an internal audit, who can run it, a seven-step method, and…
October 24, 2026
October 23, 2026
October 23, 2026

October 22, 2026

October 22, 2026