

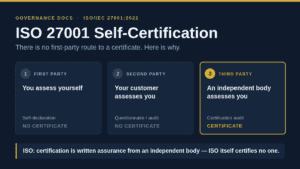
ISO 27001 Self-Certification: The Complete 2026 Guide
ISO 27001 self-certification does not exist: certification needs an independent body. What you can legitimately claim, and the…
CART
ISO 27001 self-certification does not exist: certification needs an independent body. What you can legitimately claim, and the…
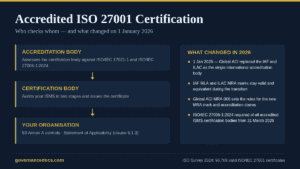
Accredited ISO 27001 certification in 2026: what Global ACI changed on 1 January, how to verify a certificate…
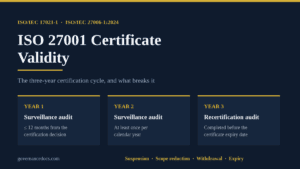
ISO 27001 certificate validity runs three years from the certification decision: two surveillance audits, one recertification, and four…
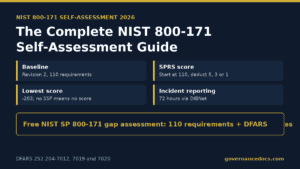
How to run a NIST 800-171 self-assessment that stands up after the CMMC suspension: scope, SSP, evidence, the…
What a covered business needs in place under the CCPA in 2026, with the deadlines, the evidence and…
What a UK GDPR programme needs in 2026, area by area, with the evidence for each item and…
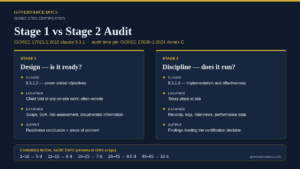
Stage 1 vs stage 2 audit, explained by an auditor: what each stage checks, why stage 2 is…
NERC CIP-010 guide: R1 baselines and change control, R2 monitoring, R3 vulnerability assessments, R4 transient assets and audit…
NIS2 supply chain security under Article 21: what the directive requires, how to assess suppliers, contract clauses and…
CMMC POA&M rules for Level 2: minimum score, 180-day closeout, which requirements cannot be deferred and what the…
How to write a NIST 800-171 SSP: scope, boundary, control implementation statements, Rev 2 vs Rev 3 and…
DPDP data principal rights under India’s DPDP Act and Rules: what individuals can request, how fiduciaries must respond…
October 18, 2026
October 18, 2026
October 15, 2026
October 15, 2026
October 14, 2026