About Us Contact Blog
Governance DocsGovernance Docs
Which Toolkit?SoA GeneratorFree TemplatesSample ReportsRecords of Processing (ROPA)Data Privacy Impact AssessmentLegitimate Interests AssessmentTransfer Impact AssessmentPrivacy Risk AssessmentGDPR Gap AssessmentISO 27701 Gap AssessmentHIPAA Gap AssessmentGap AssessmentsBusiness Impact AnalysisISO 27001 Risk AssessmentContinuity Risk AssessmentEnterprise Risk AssessmentAI Risk AssessmentAI Impact AssessmentThird-Party Risk AssessmentAboutBlogContactMy AccountCart
FOX v.2.4.9
Browse Toolkits
Governance Docs
  • Browse All Toolkits
  • Information Security & Cybersecurity
  • Data Privacy & Protection
  • Governance, Risk & Compliance
  • Quality Management
  • Health, Safety & Environment
  • AI Governance

My Account

CART

No products in the cart.

Day: September 29, 2026

SOX for newly public companies IPO compliance timeline

SOX for Newly Public Companies: IPO Timeline 2026

Governance Docs29th September 2026

A practical guide to SOX after an IPO: what applies immediately, what the SEC transition period defers and…
Read More
SOC 1 subservice organization carve-out vs inclusive method

SOC 1 Subservice Organization: Carve-Out vs Inclusive 2026

Governance Docs29th September 2026

Understand how SOC 1 treats subservice organizations: carve-out versus inclusive, CSOCs and the monitoring evidence auditors expect.
Read More
Saudi PDPL privacy policy Article 12 checklist

Saudi PDPL Privacy Policy: What Article 12 Requires in 2026

Governance Docs29th September 2026

Article 12 of the Saudi PDPL requires a privacy policy before collection. See the eight required elements, timing…
Read More
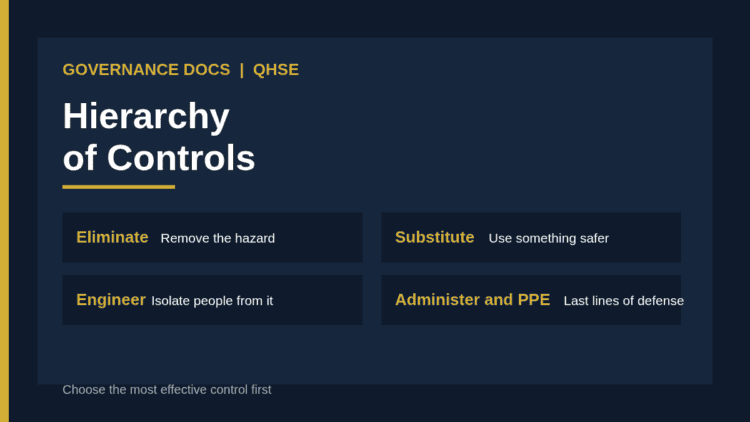
Hierarchy of controls: elimination, substitution, engineering controls, administrative controls and PPE

Hierarchy of Controls: The Essential 2026 Guide to Choosing Safer Risk Controls

Governance Docs29th September 2026

How to use the hierarchy of controls: the five levels from elimination to PPE, how ISO 45001 applies…
Read More
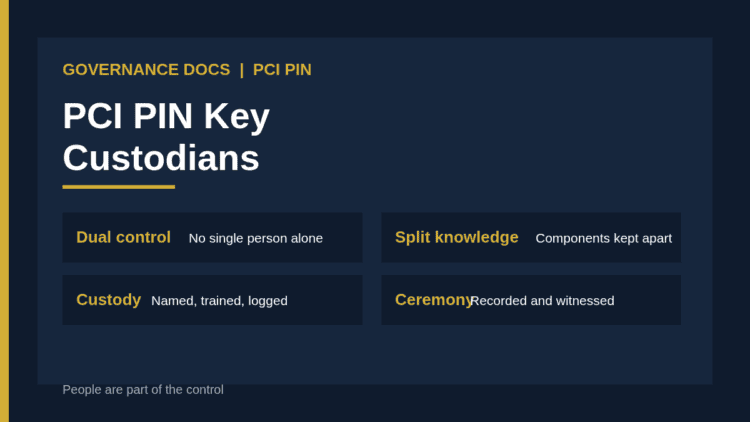
PCI PIN key custodians applying dual control and split knowledge to key components and shares

PCI PIN Key Custodians: The Essential 2026 Guide to Dual Control and Split Knowledge

Governance Docs29th September 2026

A guide to PCI PIN key custodians: their role, dual control and split knowledge in key components, key…
Read More
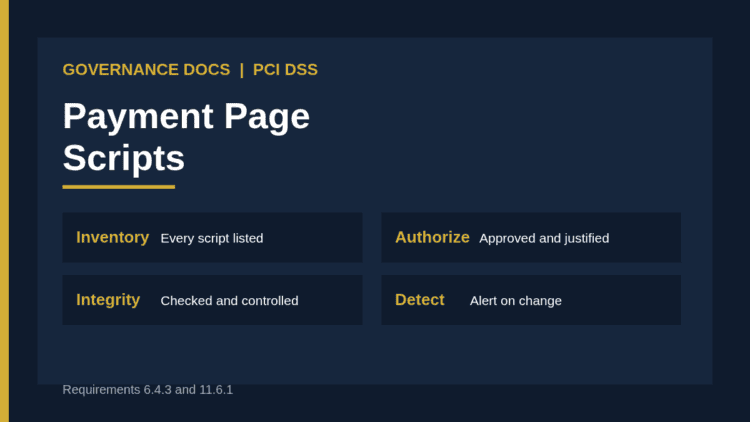
PCI DSS payment page scripts: inventory, authorization, integrity and change detection under requirements 6.4.3 and 11.6.1

PCI DSS Payment Page Scripts: The Essential 2026 Guide to Requirements 6.4.3 and 11.6.1

Governance Docs29th September 2026

How to meet PCI DSS payment page script requirements 6.4.3 and 11.6.1: script inventory, authorization, integrity, change detection,…
Read More
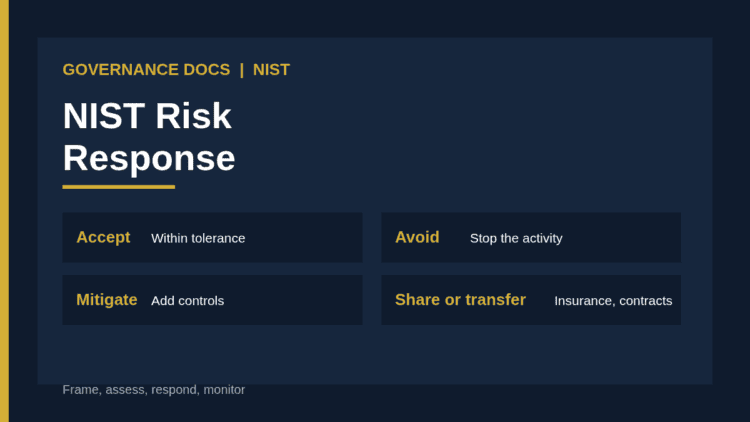
NIST risk response options: accept, avoid, mitigate, share and transfer, chosen against risk tolerance

NIST Risk Response: The Essential 2026 Guide to Accept, Avoid, Mitigate, Share or Transfer

Governance Docs29th September 2026

How NIST risk response works: the five response options in SP 800-39, how to choose between them using…
Read More
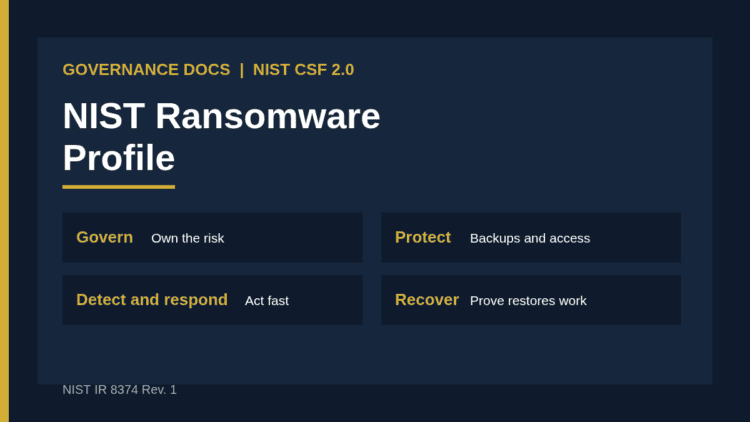
NIST ransomware profile mapping CSF 2.0 functions govern, identify, protect, detect, respond and recover to ransomware

NIST Ransomware Profile: The Essential 2026 Guide to NIST IR 8374 Rev. 1

Governance Docs29th September 2026

A practical guide to the NIST ransomware profile (IR 8374 Rev. 1): how it maps CSF 2.0 to…
Read More
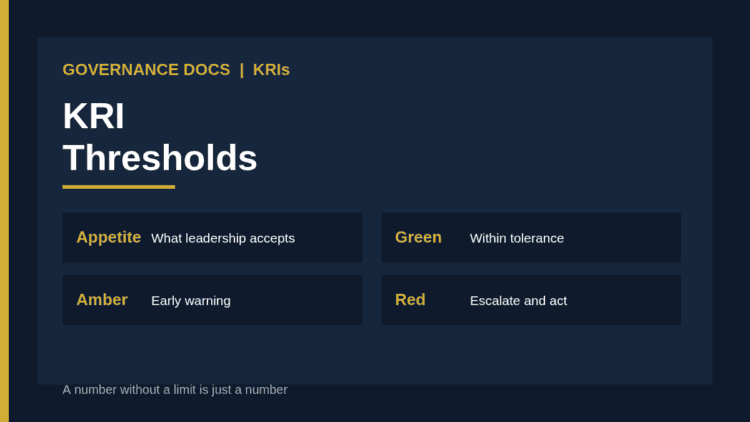
KRI thresholds: green, amber and red limits derived from risk appetite with escalation rules

KRI Thresholds: The Essential 2026 Guide to Setting Amber and Red Limits for Cyber Risk

Governance Docs29th September 2026

How to set KRI thresholds for IT and cybersecurity indicators: translating risk appetite into amber and red limits,…
Read More
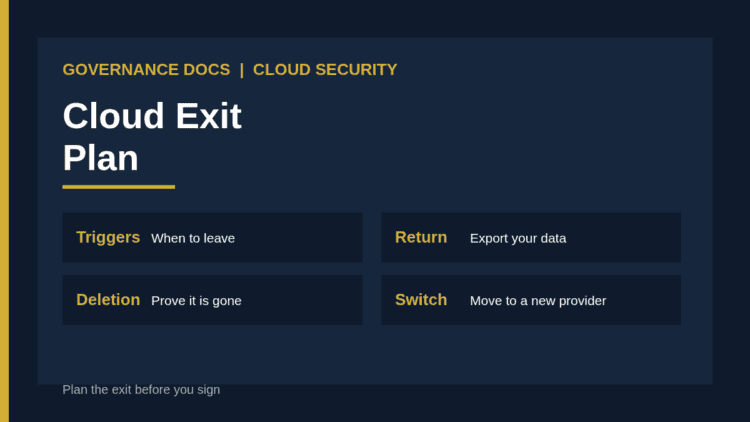
Cloud exit plan: termination triggers, data export, deletion evidence and migration to a new provider

Cloud Exit Plan: The Essential 2026 Guide to Termination, Data Return and Deletion

Governance Docs29th September 2026

How to write a cloud exit plan: termination triggers, data return and deletion, portability, EU Data Act switching…
Read More
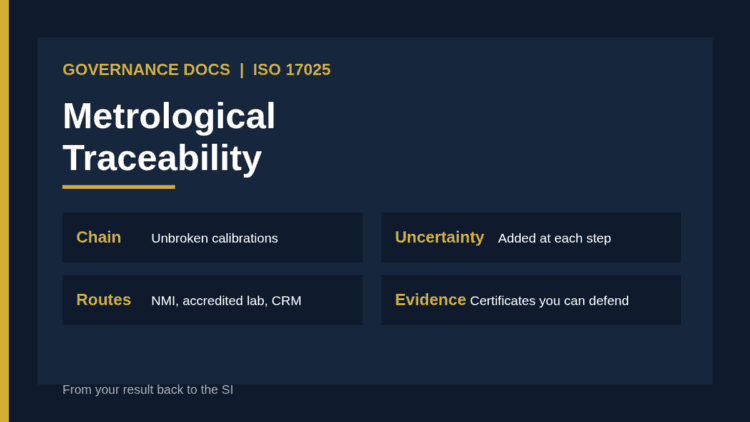
ISO 17025 metrological traceability: unbroken chain of calibrations from laboratory measurement to SI units

ISO 17025 Metrological Traceability: The Essential 2026 Guide to Clause 6.5

Governance Docs29th September 2026

How to meet ISO 17025 metrological traceability: the clause 6.5 requirements, ILAC P10 traceability routes, calibration certificate checks…
Read More
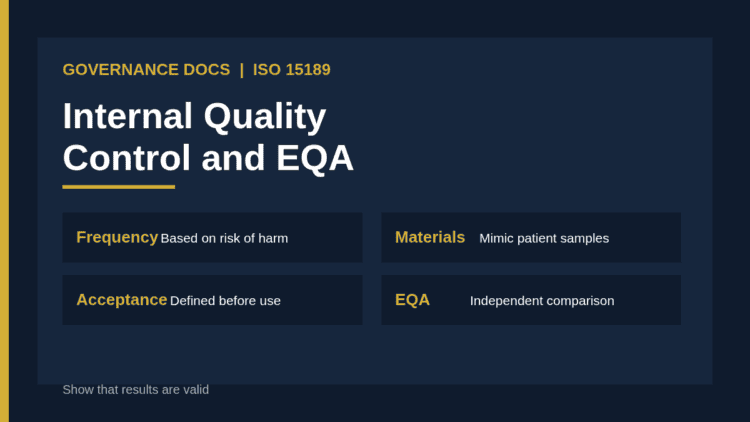
ISO 15189 internal quality control: control materials, frequency, acceptance rules and external quality assessment

ISO 15189 Internal Quality Control: The Essential 2026 Guide to IQC and EQA

Governance Docs29th September 2026

How ISO 15189 internal quality control and external quality assessment work in medical laboratories: risk-based frequency, control materials,…
Read More

    ←
  • 1
  • …
  • 5
  • 6
  • 7
  • 8
  • 9
  • 10
  • →

Recent Posts

Gap assessment reassessment progress comparison diagram
Gap Assessment Reassessment: The Essential 2026 Guide to Measuring Progress

September 30, 2026

Business continuity supply chain risk map diagram
Business Continuity Supply Chain Risk: The Essential 2026 Guide to Resilient Suppliers

September 30, 2026

Business continuity risk appetite statement diagram
Business Continuity Risk Appetite: The Essential 2026 Guide to Setting Tolerance for Disruption

September 30, 2026

Business continuity risk monitoring indicators diagram
Business Continuity Risk Monitoring: The Essential 2026 Guide to Indicators and Reviews

September 30, 2026

Business continuity scenario planning steps diagram
Business Continuity Scenario Planning: The Essential 2026 Guide to Testing Your Plans

September 30, 2026

Categories

  • Articles
  • DORA
  • GDPR
  • HIPAA
  • ISO 27001
  • ISO 42001 & AI governance
  • ISO 9001
  • Management systems
  • NIS2
  • Security frameworks
  • SOC 2
Governance DocsGovernance Docs

Reliable ISO & compliance documentation toolkits that help your business meet regulatory standards with ease.

Governance Docs LLC
1209 Mountain Road Pl NE, Suite R
Albuquerque, NM 87110, USA
info@governancedocs.com
+1 812 227 5662

Toolkits

  • ISO 27001:2022
  • GDPR
  • SOC 2
  • PCI-DSS v4.0
  • HIPAA
  • ISO 42001
  • All toolkits →

Company

  • About Us
  • Blog
  • Contact
  • FAQ
  • Which toolkit do I need?
  • Free templates
  • SoA generator
  • Assessments
  • Sample reports
  • RSS feeds

Policies

  • Privacy Policy
  • Terms & Conditions
  • Refund & Return Policy
  • Delivery Policy
  • Manage cookies
Browse by topicISO 27001ISO 42001 & AI governanceGDPRSOC 2HIPAANIS2DORAISO 9001Management systemsSecurity frameworks
© 2026 Governance Docs LLC. All rights reserved.
Secure checkoutstripeVISA