About Us Contact Blog
Governance DocsGovernance Docs
Which Toolkit?SoA GeneratorFree TemplatesSample ReportsFind the Right AssessmentRecords of Processing (ROPA)Data Privacy Impact AssessmentLegitimate Interests AssessmentTransfer Impact AssessmentPrivacy Risk AssessmentGDPR Gap AssessmentUK GDPR Gap AssessmentCCPA/CPRA Gap AssessmentISO 27701 Gap AssessmentHIPAA Gap AssessmentISO 27001 Risk AssessmentThird-Party Risk AssessmentSoA GeneratorISO 27001 Assessment Tool (Excel)ISO 27001 Gap AssessmentSOC 2 Gap AssessmentNIST CSF 2.0 Gap AssessmentNIST SP 800-53 Gap AssessmentNIST RMF Gap AssessmentCIS Controls Gap AssessmentPCI DSS 4.0 Gap AssessmentNIS2 Gap AssessmentCMMC 2.0 Gap AssessmentNIST SP 800-171 Gap AssessmentFedRAMP Gap AssessmentBSI C5 Gap AssessmentIEC 62443 Gap AssessmentSAMA CSF Gap AssessmentNCA ECC Gap AssessmentISO 20000 Gap AssessmentAI Risk AssessmentAI Impact AssessmentISO 42001 Gap AssessmentEU AI Act Gap AssessmentBusiness Impact AnalysisContinuity Risk AssessmentISO 22301 Assessment Tool (Excel)ISO 22301 Gap AssessmentDORA Gap AssessmentISO 9001 Gap AssessmentISO 13485 Gap AssessmentIATF 16949 Gap AssessmentISO 14001 Gap AssessmentISO 45001 Gap AssessmentISO 45001 Assessment Tool (Excel)HACCP Gap AssessmentEnterprise Risk AssessmentISO 31000 Gap AssessmentData Governance Gap AssessmentProject Management Gap AssessmentAll Gap AssessmentsISO 27001 Internal AuditISO 42001 Internal AuditAboutBlogContactMy AccountCart
Browse Toolkits
Governance Docs
  • Browse All Toolkits
  • Information Security & Cybersecurity
  • Data Privacy & Protection
  • Governance, Risk & Compliance
  • Quality Management
  • Health, Safety & Environment
  • AI Governance

My Account

CART

No products in the cart.

Day: September 29, 2026

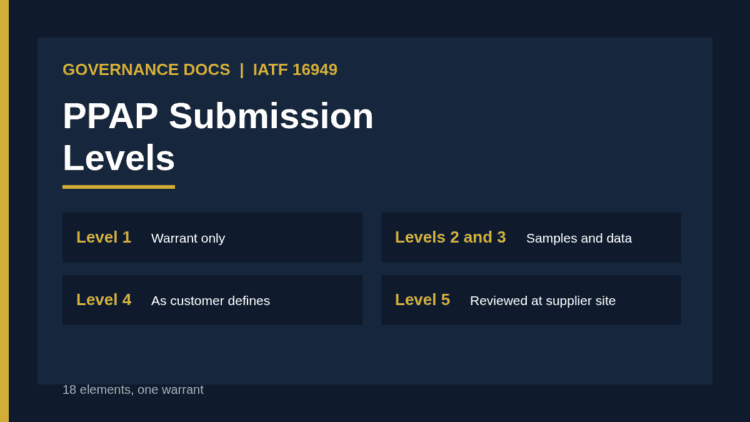
PPAP submission levels 1 to 5 and the 18 elements of the production part approval process

PPAP Submission Levels: The Essential 2026 Guide to the 18 Elements and Approval

Governance Docs29th September 2026

A guide to PPAP submission levels 1 to 5, the 18 PPAP elements, the part submission warrant, approval…
Read More
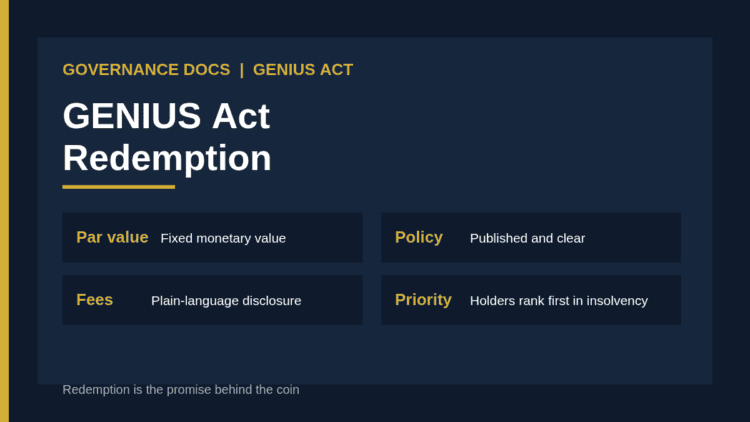
GENIUS Act redemption: par redemption, public redemption policy, fee disclosure and proposed timing rules

GENIUS Act Redemption: The Essential 2026 Guide to Par Redemption and Policy Rules

Governance Docs29th September 2026

What the GENIUS Act requires on stablecoin redemption: par value, a public redemption policy, fee disclosure, insolvency priority…
Read More
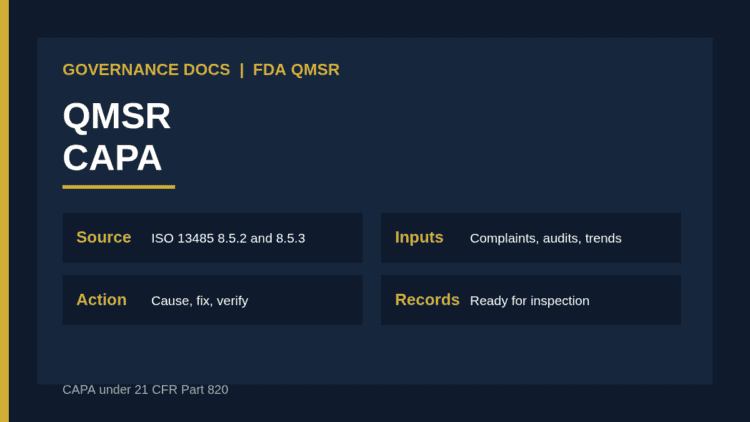
QMSR CAPA: corrective and preventive action under ISO 13485 as incorporated into 21 CFR Part 820

QMSR CAPA: The Essential 2026 Guide to Corrective and Preventive Action Under 21 CFR Part 820

Governance Docs29th September 2026

How CAPA works under the FDA QMSR: the ISO 13485 requirements now incorporated into Part 820, what inspectors…
Read More
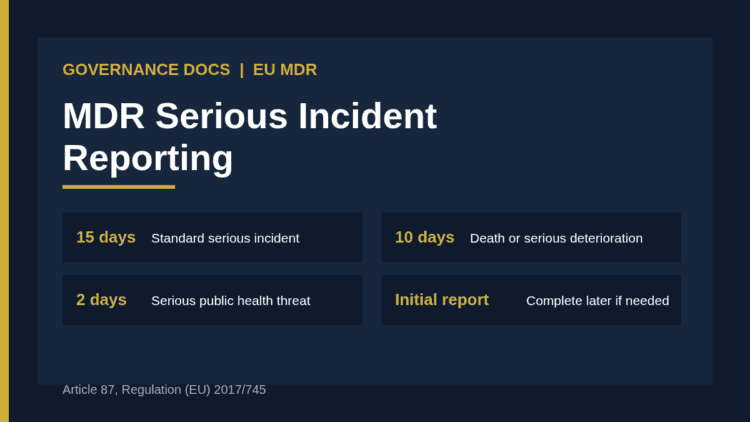
MDR serious incident reporting: Article 87 deadlines of 15, 10 and 2 days from awareness

MDR Serious Incident Reporting: The Essential 2026 Guide to Article 87 Deadlines

Governance Docs29th September 2026

How MDR serious incident reporting works under Article 87: what counts as a serious incident, the 15, 10…
Read More
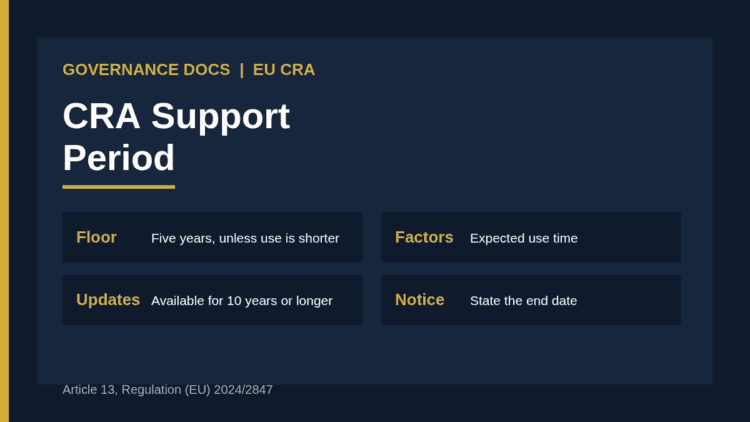
CRA support period: five-year minimum, security updates and end-of-support date under Article 13 of the Cyber Resilience Act

CRA Support Period: The Essential 2026 Guide to Five Years, Updates and End-of-Support Dates

Governance Docs29th September 2026

How to set and document the Cyber Resilience Act support period: the five-year floor, factors that set it,…
Read More
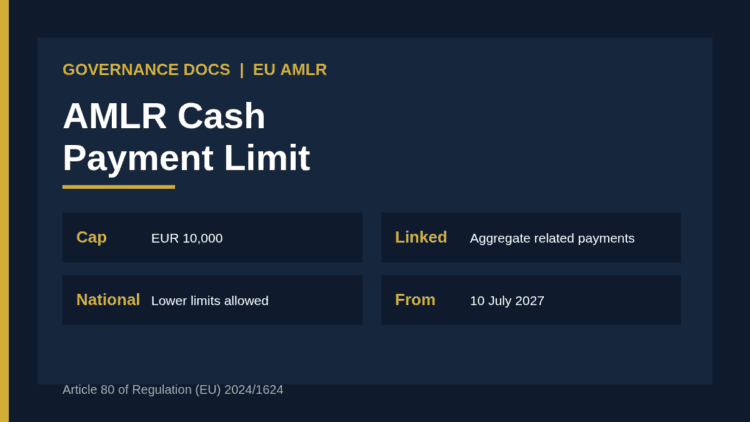
AMLR cash payment limit: EUR 10,000 cap on cash payments for goods and services under Article 80

AMLR Cash Payment Limit: The Essential 2026 Guide to the EUR 10,000 Rule

Governance Docs29th September 2026

What the AMLR cash payment limit in Article 80 requires: the EUR 10,000 cap, linked transactions, lower national…
Read More
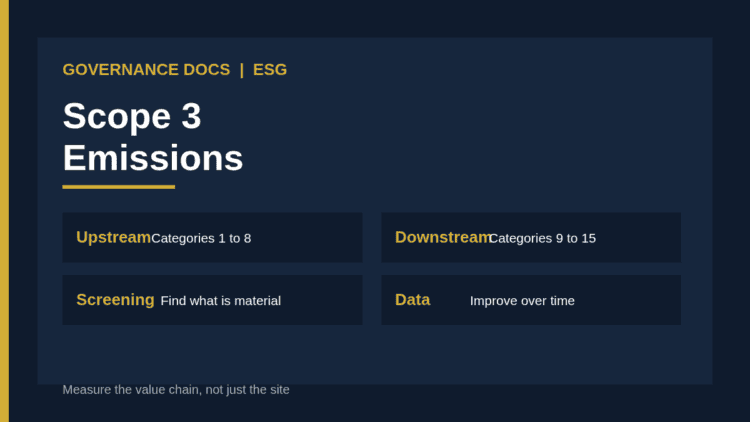
Scope 3 emissions: 15 GHG Protocol categories split into upstream and downstream value chain sources

Scope 3 Emissions: The Essential 2026 Guide to the 15 Categories and How to Start

Governance Docs29th September 2026

A practical guide to scope 3 emissions: the 15 GHG Protocol categories, screening for materiality, data sources, a…
Read More
Data governance council: purpose, members, decision rights, escalation and cadence

Data Governance Council: The Essential 2026 Guide to Charter, Members and Decision Rights

Governance Docs29th September 2026

How to set up a data governance council: purpose, membership, decision rights, escalation, meeting cadence and a charter…
Read More
Compliance consulting statement of work: scope, deliverables, assumptions, client duties and change control

Compliance Consulting Statement of Work: The Essential 2026 Guide for Consultants

Governance Docs29th September 2026

How to write a compliance consulting statement of work: scope, deliverables, assumptions, client responsibilities, change control, fees and…
Read More
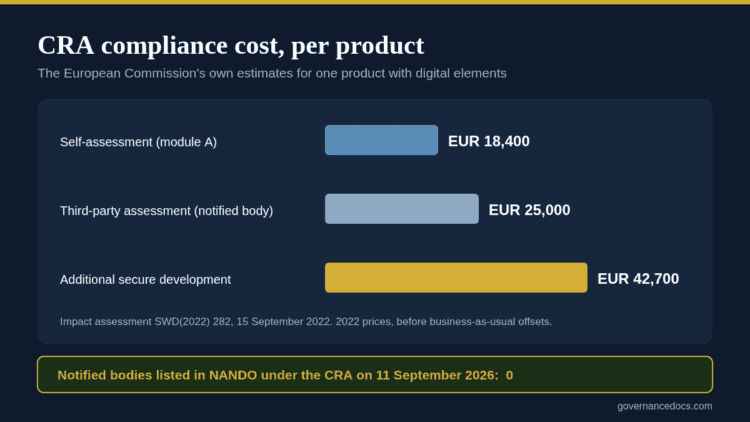
CRA compliance cost per product: EUR 18,400 self-assessment, EUR 25,000 third-party assessment, EUR 42,700 additional secure development

CRA Compliance Cost: The Complete 2026 Budget Breakdown

Governance Docs29th September 2026

CRA compliance cost priced off the European Commission's own impact assessment: EUR 18,400 self-assessed, EUR 25,000 third-party, zero…
Read More
COBIT goals cascade: enterprise goals lead to alignment goals and then to governance and management objectives

COBIT Goals Cascade: The Essential 2026 Guide to Turning Strategy into IT Priorities

Governance Docs29th September 2026

How the COBIT 2019 goals cascade links enterprise goals to alignment goals and to the 40 governance and…
Read More
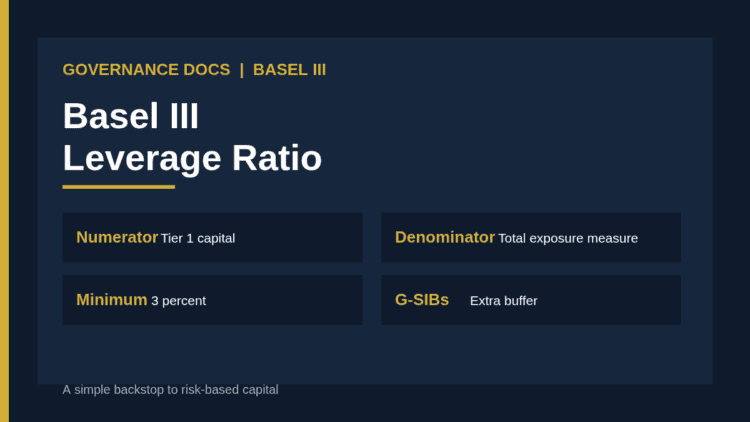
Basel III leverage ratio: Tier 1 capital divided by total exposure measure, with a 3 percent minimum

Basel III Leverage Ratio: The Essential 2026 Guide to the Non-Risk-Based Backstop

Governance Docs29th September 2026

How the Basel III leverage ratio works: the 3% minimum, the exposure measure, the G-SIB buffer, a worked…
Read More
    ←
  • 1
  • …
  • 6
  • 7
  • 8
  • 9
  • 10
  • →

Recent Posts

ISO 22301 surveillance audit cycle: stage 1 and 2, two annual surveillance audits, recertification, and what BCMS auditors test
ISO 22301 Surveillance Audit: The Complete 2026 Guide

November 11, 2026

ISO 42001 recertification audit: full-system review, major nonconformities closed before expiry, 6-month restore window and ISO/IEC 42006
ISO 42001 Recertification Audit: The Complete 2026 Guide

November 10, 2026

ISO 45001 toolkit: what a complete one contains, mapped to clauses 4 to 10
ISO 45001 Toolkit: What a Complete One Contains (2026)

November 9, 2026

ISO 13485 recertification audit 2026: audit time, expiry rules and MDSAP re-audit
ISO 13485 Recertification Audit: The Complete 2026 Guide

November 8, 2026

ISO 13485 surveillance audit infographic: first audit within 12 months of the certification decision, about one third of initial days, 8 plus 1 review areas, Global ACI-TECH-3-007
ISO 13485 Surveillance Audit: The Complete 2026 Guide

November 7, 2026

Categories

  • Articles
  • DORA
  • GDPR
  • HIPAA
  • ISO 27001
  • ISO 42001 & AI governance
  • ISO 9001
  • Management systems
  • NIS2
  • Security frameworks
  • SOC 2
Governance DocsGovernance Docs

Reliable ISO & compliance documentation toolkits that help your business meet regulatory standards with ease.

Governance Docs LLC
1209 Mountain Road Pl NE, Suite R
Albuquerque, NM 87110, USA
[email protected]
+1 505 289 2455

Toolkits

  • ISO 27001:2022
  • GDPR
  • SOC 2
  • PCI-DSS v4.0
  • HIPAA
  • ISO 42001
  • All toolkits →

Company

  • About Us
  • Blog
  • Contact
  • FAQ
  • Which toolkit do I need?
  • Request a custom toolkit
  • Free templates
  • SoA generator
  • Assessments
  • Sample reports
  • RSS feeds

Policies

  • Privacy Policy
  • Terms & Conditions
  • Refund & Return Policy
  • Delivery Policy
  • Manage cookies
Browse by topicISO 27001ISO 42001 & AI governanceGDPRSOC 2HIPAANIS2DORAISO 9001Management systemsSecurity frameworks
© 2026 Governance Docs LLC. All rights reserved.
Secure checkoutstripeVISA