About Us Contact Blog
Governance DocsGovernance Docs
Which Toolkit?SoA GeneratorFree TemplatesSample ReportsFind the Right AssessmentRecords of Processing (ROPA)Data Privacy Impact AssessmentLegitimate Interests AssessmentTransfer Impact AssessmentPrivacy Risk AssessmentGDPR Gap AssessmentUK GDPR Gap AssessmentCCPA/CPRA Gap AssessmentISO 27701 Gap AssessmentHIPAA Gap AssessmentISO 27001 Risk AssessmentThird-Party Risk AssessmentSoA GeneratorISO 27001 Assessment Tool (Excel)ISO 27001 Gap AssessmentSOC 2 Gap AssessmentNIST CSF 2.0 Gap AssessmentNIST SP 800-53 Gap AssessmentNIST RMF Gap AssessmentCIS Controls Gap AssessmentPCI DSS 4.0 Gap AssessmentNIS2 Gap AssessmentCMMC 2.0 Gap AssessmentNIST SP 800-171 Gap AssessmentFedRAMP Gap AssessmentBSI C5 Gap AssessmentIEC 62443 Gap AssessmentSAMA CSF Gap AssessmentNCA ECC Gap AssessmentISO 20000 Gap AssessmentAI Risk AssessmentAI Impact AssessmentISO 42001 Gap AssessmentEU AI Act Gap AssessmentBusiness Impact AnalysisContinuity Risk AssessmentISO 22301 Assessment Tool (Excel)ISO 22301 Gap AssessmentDORA Gap AssessmentISO 9001 Gap AssessmentISO 13485 Gap AssessmentIATF 16949 Gap AssessmentISO 14001 Gap AssessmentISO 45001 Gap AssessmentISO 45001 Assessment Tool (Excel)HACCP Gap AssessmentEnterprise Risk AssessmentISO 31000 Gap AssessmentData Governance Gap AssessmentProject Management Gap AssessmentAll Gap AssessmentsISO 27001 Internal AuditISO 42001 Internal AuditAboutBlogContactMy AccountCart
FOX v.2.4.9
Browse Toolkits
Governance Docs
  • Browse All Toolkits
  • Information Security & Cybersecurity
  • Data Privacy & Protection
  • Governance, Risk & Compliance
  • Quality Management
  • Health, Safety & Environment
  • AI Governance

My Account

CART

No products in the cart.

Day: September 29, 2026

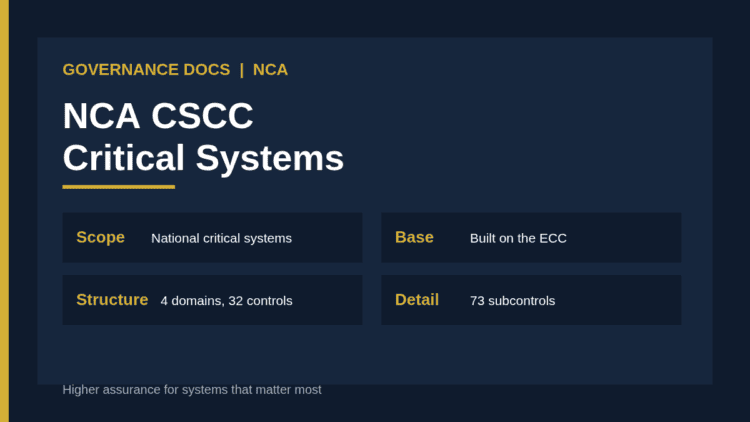
NCA CSCC critical systems cybersecurity controls: 4 domains, 32 controls and 73 subcontrols, built on the ECC

NCA CSCC: The Essential 2026 Guide to the Critical Systems Cybersecurity Controls

Governance Docs29th September 2026

A guide to the NCA Critical Systems Cybersecurity Controls (CSCC-1:2019): who it applies to, how it extends the…
Read More
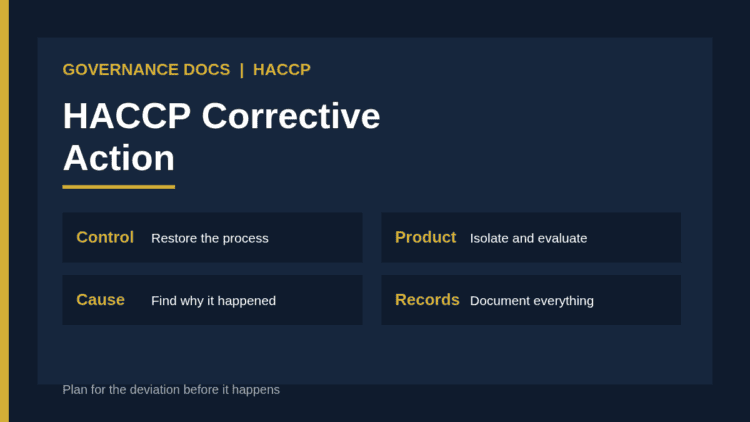
HACCP corrective action: restore control, isolate product, find the cause, prevent recurrence and keep records

HACCP Corrective Action: The Essential 2026 Guide to Handling CCP Deviations

Governance Docs29th September 2026

What a HACCP corrective action must cover when a critical limit is breached: restoring control, product disposition, root…
Read More
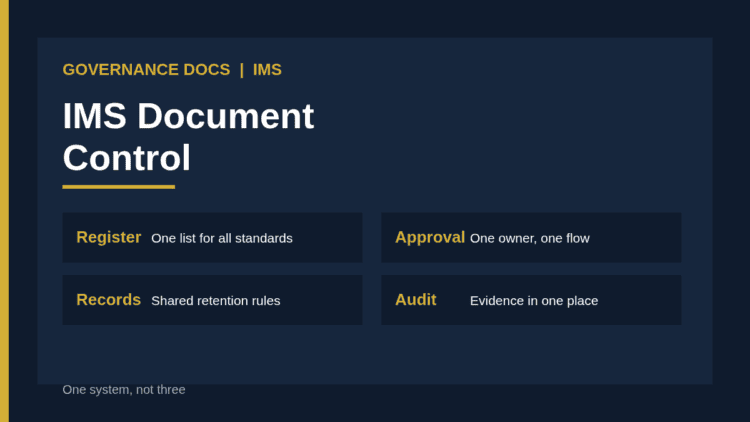
IMS document control: one register, approval flow and retention rule shared across management system standards

IMS Document Control: The Essential 2026 Guide to One System for Every Standard

Governance Docs29th September 2026

How to run IMS document control once for ISO 9001, ISO 14001 and ISO 45001: one register, one…
Read More
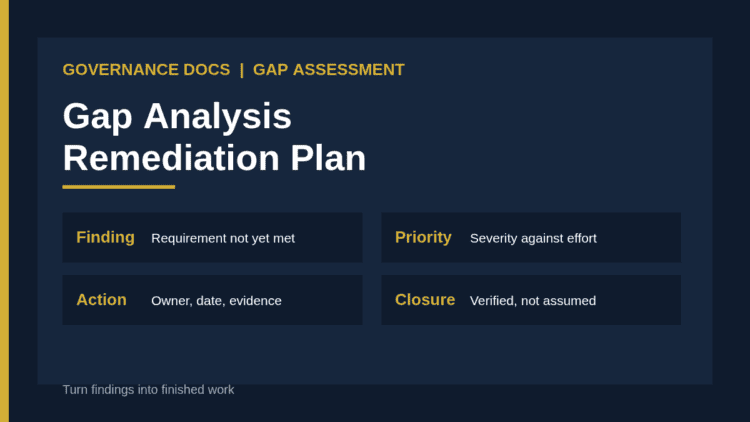
Gap analysis remediation plan: from finding to prioritized action, owner, date and closure evidence

Gap Analysis Remediation Plan: The Essential 2026 Guide to Closing Findings

Governance Docs29th September 2026

How to turn gap assessment findings into a remediation plan: the ten fields, prioritization by severity and effort,…
Read More
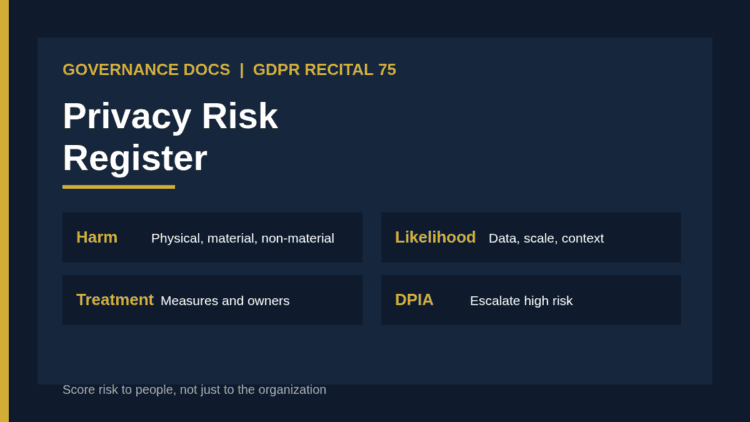
Privacy risk register: 12 fields scoring harm to individuals from source to residual rating

Privacy Risk Register: The Essential 2026 Guide with 12 Fields for Harm to Individuals

Governance Docs29th September 2026

How to build a privacy risk register: 12 fields, scoring harm to individuals using GDPR Recital 75, links…
Read More
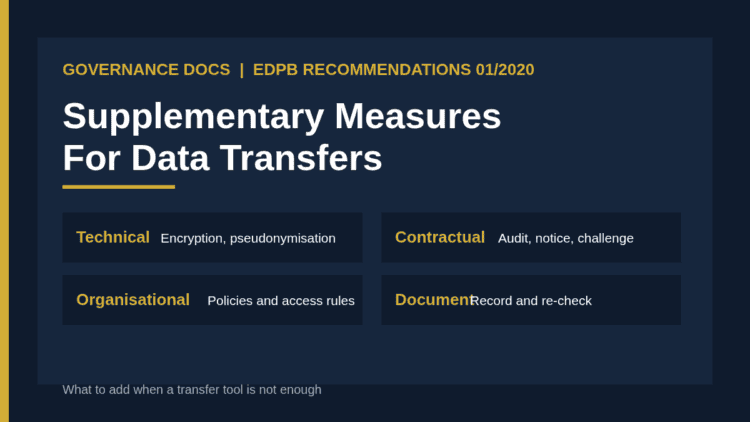
Supplementary measures for data transfers: technical, contractual and organisational measures after a transfer impact assessment

Supplementary Measures for Data Transfers: The Essential 2026 Guide to the EDPB Six Steps

Governance Docs29th September 2026

When a transfer tool is not enough, supplementary measures may be needed. The EDPB six steps, the three…
Read More
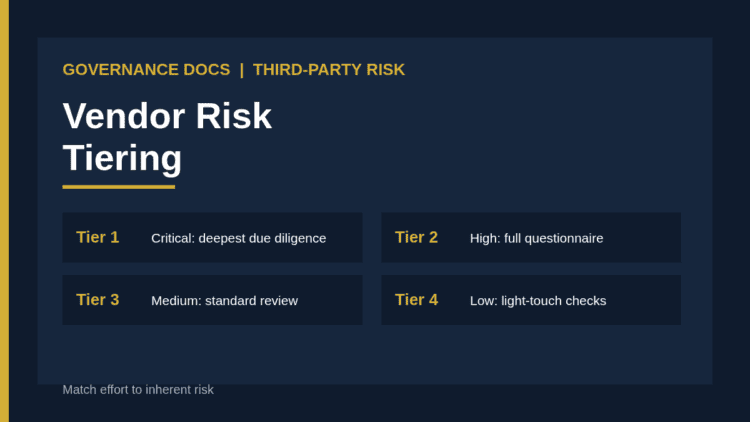
Vendor risk tiering: four tiers from critical to low with due diligence depth for each

Vendor Risk Tiering: The Essential 2026 Guide to 4 Tiers, Criteria and Review Cycles

Governance Docs29th September 2026

How to tier vendors by risk: four tiers, weighted scoring criteria, override rules and how each tier drives…
Read More
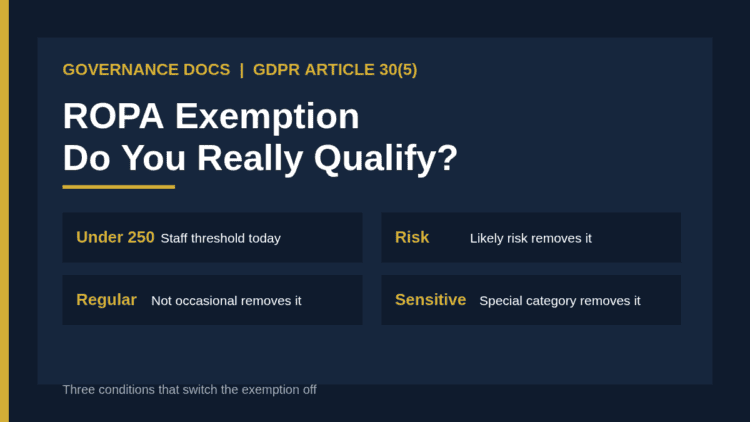
ROPA exemption: the GDPR Article 30(5) decision for organizations with fewer than 250 employees

ROPA Exemption: The Essential 2026 Guide to GDPR Article 30(5) for Small Organizations

Governance Docs29th September 2026

Does a small organization need a record of processing activities? The ROPA exemption in GDPR Article 30(5), the…
Read More
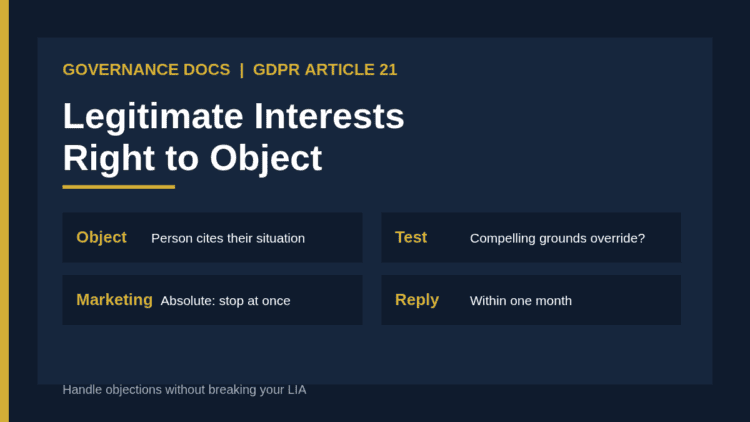
Legitimate interests right to object: the GDPR Article 21 decision flow

Legitimate Interests Right to Object: The Essential 2026 Guide to GDPR Article 21

Governance Docs29th September 2026

What happens when someone objects to processing based on legitimate interests: the Article 21 test, the absolute marketing…
Read More
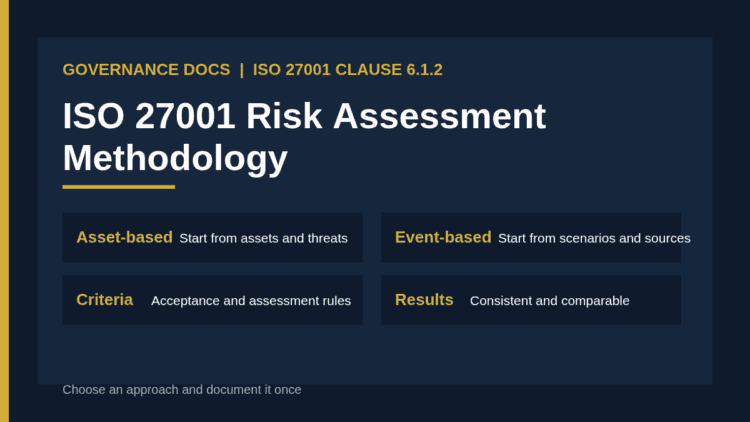
ISO 27001 risk assessment methodology: asset-based and event-based approaches compared

ISO 27001 Risk Assessment Methodology: The Essential 2026 Guide to Choosing an Approach

Governance Docs29th September 2026

How to define an ISO 27001 risk assessment methodology: what clause 6.1.2 requires, asset-based versus event-based approaches and…
Read More
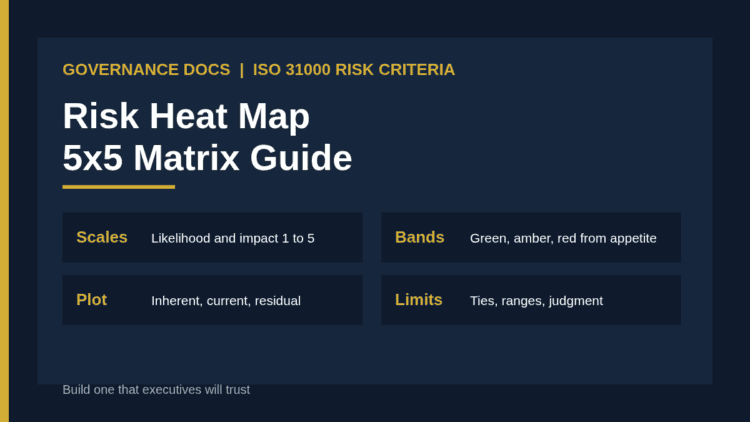
Risk heat map: a 5x5 likelihood and impact matrix with green, amber and red bands

Risk Heat Map: The Essential 2026 Guide to Building a 5×5 Matrix Executives Trust

Governance Docs29th September 2026

How to build a risk heat map: define 5x5 likelihood and impact scales, set colour bands from risk…
Read More
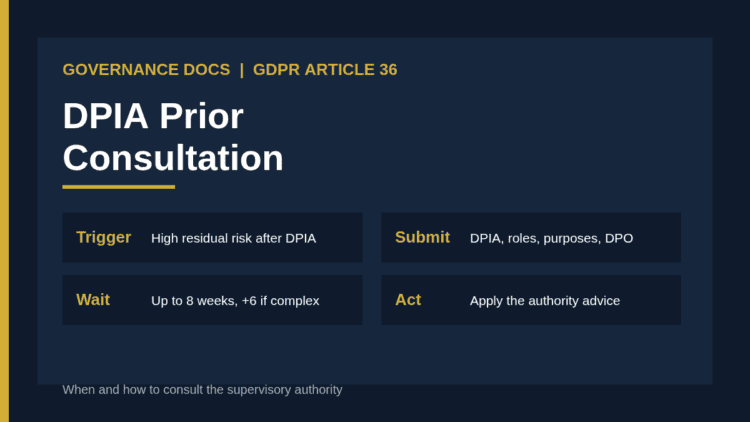
DPIA prior consultation: the GDPR Article 36 steps from high residual risk to regulator advice

DPIA Prior Consultation: The Essential 2026 Guide to GDPR Article 36

Governance Docs29th September 2026

When a DPIA leaves high residual risk, GDPR Article 36 requires prior consultation. Learn the trigger, the submission…
Read More

    ←
  • 1
  • …
  • 7
  • 8
  • 9
  • 10
  • →

Recent Posts

ISO 27001 password policy requirements under Annex A 5.17 and A.8.5, with NIST, PCI DSS and Cyber Essentials length baselines compared
ISO 27001 Password Policy: Complete 2026 Requirements Guide

October 20, 2026

ISO 27001 intellectual property rights: the six categories in Annex A control 5.32
ISO 27001 Intellectual Property Rights: Complete 2026 Guide

October 20, 2026

ISO 27001 independent review under Annex A 5.35 compared with the clause 9.2 internal audit and clause 9.3 management review
ISO 27001 Independent Review: Complete A.5.35 Guide 2026

October 19, 2026

ISO 27001 acceptable use policy requirements under Annex A control A.5.10
ISO 27001 Acceptable Use Policy: Complete 2026 Guide

October 19, 2026

ISO 27001 network security controls A.8.20, A.8.21 and A.8.22 compared
ISO 27001 Network Security: Complete A.8.20–8.22 Guide 2026

October 18, 2026

Categories

  • Articles
  • DORA
  • GDPR
  • HIPAA
  • ISO 27001
  • ISO 42001 & AI governance
  • ISO 9001
  • Management systems
  • NIS2
  • Security frameworks
  • SOC 2
Governance DocsGovernance Docs

Reliable ISO & compliance documentation toolkits that help your business meet regulatory standards with ease.

Governance Docs LLC
1209 Mountain Road Pl NE, Suite R
Albuquerque, NM 87110, USA
[email protected]
+1 505 289 2455

Toolkits

  • ISO 27001:2022
  • GDPR
  • SOC 2
  • PCI-DSS v4.0
  • HIPAA
  • ISO 42001
  • All toolkits →

Company

  • About Us
  • Blog
  • Contact
  • FAQ
  • Which toolkit do I need?
  • Free templates
  • SoA generator
  • Assessments
  • Sample reports
  • RSS feeds

Policies

  • Privacy Policy
  • Terms & Conditions
  • Refund & Return Policy
  • Delivery Policy
  • Manage cookies
Browse by topicISO 27001ISO 42001 & AI governanceGDPRSOC 2HIPAANIS2DORAISO 9001Management systemsSecurity frameworks
© 2026 Governance Docs LLC. All rights reserved.
Secure checkoutstripeVISA