About Us Contact Blog
Governance DocsGovernance Docs
Which Toolkit?SoA GeneratorFree TemplatesSample ReportsFind the Right AssessmentRecords of Processing (ROPA)Data Privacy Impact AssessmentLegitimate Interests AssessmentTransfer Impact AssessmentPrivacy Risk AssessmentGDPR Gap AssessmentUK GDPR Gap AssessmentCCPA/CPRA Gap AssessmentISO 27701 Gap AssessmentHIPAA Gap AssessmentISO 27001 Risk AssessmentThird-Party Risk AssessmentSoA GeneratorISO 27001 Assessment Tool (Excel)ISO 27001 Gap AssessmentSOC 2 Gap AssessmentNIST CSF 2.0 Gap AssessmentNIST SP 800-53 Gap AssessmentNIST RMF Gap AssessmentCIS Controls Gap AssessmentPCI DSS 4.0 Gap AssessmentNIS2 Gap AssessmentCMMC 2.0 Gap AssessmentNIST SP 800-171 Gap AssessmentFedRAMP Gap AssessmentBSI C5 Gap AssessmentIEC 62443 Gap AssessmentSAMA CSF Gap AssessmentNCA ECC Gap AssessmentISO 20000 Gap AssessmentAI Risk AssessmentAI Impact AssessmentISO 42001 Gap AssessmentEU AI Act Gap AssessmentBusiness Impact AnalysisContinuity Risk AssessmentISO 22301 Assessment Tool (Excel)ISO 22301 Gap AssessmentDORA Gap AssessmentISO 9001 Gap AssessmentISO 13485 Gap AssessmentIATF 16949 Gap AssessmentISO 14001 Gap AssessmentISO 45001 Gap AssessmentISO 45001 Assessment Tool (Excel)HACCP Gap AssessmentEnterprise Risk AssessmentISO 31000 Gap AssessmentData Governance Gap AssessmentProject Management Gap AssessmentAll Gap AssessmentsISO 27001 Internal AuditISO 42001 Internal AuditAboutBlogContactMy AccountCart
Browse Toolkits
Governance Docs
  • Browse All Toolkits
  • Information Security & Cybersecurity
  • Data Privacy & Protection
  • Governance, Risk & Compliance
  • Quality Management
  • Health, Safety & Environment
  • AI Governance

My Account

CART

No products in the cart.

Category: Articles

NERC CIP patch management — NERC CIP Patch Management: The Complete 2026 Guide

NERC CIP Patch Management: The Complete 2026 Guide

Governance Docs03rd September 2026

NERC CIP patch management under CIP-007 R2: the two separate 35-calendar-day clocks, named patch sources, and mitigation plans…
Read More
NERC CIP low impact — NERC CIP Low Impact: The Complete 2026 Guide

NERC CIP Low Impact: The Complete 2026 Guide

Governance Docs03rd September 2026

NERC CIP low impact explained: the seven CIP-003 Attachment 1 topics, the vendor remote access control added in…
Read More
BES Cyber System categorization — BES Cyber System Categorization: A Complete CIP-002 Guide

BES Cyber System Categorization: A Complete CIP-002 Guide

Governance Docs03rd September 2026

BES Cyber System categorization under CIP-002: the high, medium and low criteria, the process auditors test, and the…
Read More
NERC CIP compliance — NERC CIP Compliance: The Complete 2026 Guide

NERC CIP Compliance: The Complete 2026 Guide

Governance Docs03rd September 2026

NERC CIP compliance explained: how RSAW audits work, the three evidence rules, the compliance calendar, and where programmes…
Read More
NERC CIP standards — NERC CIP Standards: The Complete 2026 Guide to All 13

NERC CIP Standards: The Complete 2026 Guide to All 13

Governance Docs03rd September 2026

NERC CIP standards explained: all 13 enforceable standards, 46 requirements, the 2028 cutover, and why CIP-015 is not…
Read More
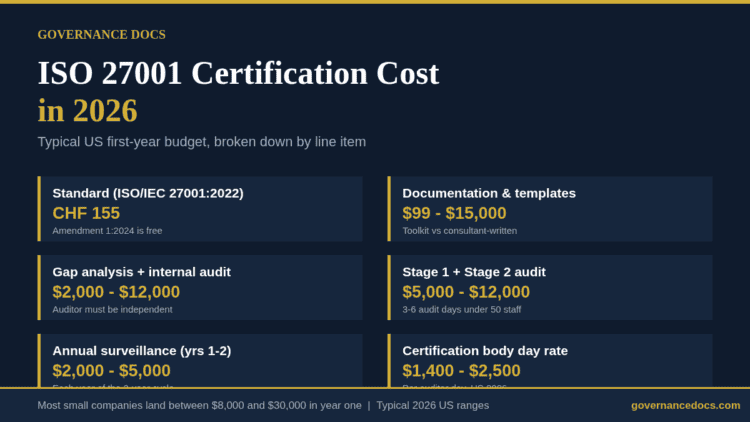
ISO 27001 certification cost breakdown for 2026 showing audit fees, day rates and surveillance costs

ISO 27001 Certification Cost in 2026: The Complete Breakdown

Governance Docs03rd September 2026

ISO 27001 certification cost in 2026 runs $8,000 to $30,000 for most small US companies. A full line-item…
Read More
The gifts and hospitality policy explained

Gifts and Hospitality: A Clear ISO 37001 Guide for 2026

Governance Docs02nd September 2026

A gifts and hospitality policy has to fix 5 things a salesperson can apply at dinner. What ISO…
Read More
ISO 27018 cloud privacy explained

ISO 27018: A Clear Guide to the 2025 Cloud Privacy Rules

Governance Docs02nd September 2026

ISO 27018 applies in one narrow case: public cloud, personal data, acting as processor. The 6 obligations that…
Read More
The ISO 21001 internal audit checklist

ISO 21001 Internal Audit: A Clear Checklist for 2026

Governance Docs02nd September 2026

An ISO 21001 internal audit has to test whether learning happened. What to check clause by clause, the…
Read More
Authorised Economic Operator status explained

Authorised Economic Operator: A Clear Guide to the 4 Tests

Governance Docs02nd September 2026

Authorised Economic Operator status comes as AEOC or AEOS, against 4 cumulative criteria. What the audit examines, and…
Read More
CSA STAR Level 2 explained

STAR Level 2: A Clear Guide to Certification vs Attestation

Governance Docs02nd September 2026

STAR Level 2 comes in 2 forms: certification built on ISO 27001, attestation built on SOC 2. Which…
Read More
The ICAAP explained

ICAAP: A Clear Guide to the 6 Building Blocks in 2026

Governance Docs02nd September 2026

The ICAAP is the bank's own capital argument. The 6 building blocks, the 2 perspectives, what the 2026…
Read More

    ←
  • 1
  • …
  • 70
  • 71
  • 72
  • 73
  • 74
  • …
  • 106
  • →

Recent Posts

ISO 14001 surveillance audit infographic showing the cycle years, audit time, eight review areas and the 2029 transition deadline
ISO 14001 Surveillance Audit: The Complete 2026 Guide

November 3, 2026

ISO 27001 toolkit contents shown as three layers: clause 4 to 10 records, 93 Annex A controls and supporting registers
ISO 27001 Toolkit: What a Complete One Contains (2026)

November 2, 2026

ISO 9001 recertification audit three-year cycle showing surveillance in years 1 and 2 and recertification in year 3
ISO 9001 Recertification Audit: The Complete 2026 Guide

November 1, 2026

ISO 9001 surveillance audit: eight required review areas, the 12-month window and the 2029 transition deadline
ISO 9001 Surveillance Audit: The Complete 2026 Guide

October 31, 2026

ISO 27001 software installation under Annex A 8.19: production systems and end-user endpoints
ISO 27001 Software Installation: Essential A.8.19 Guide 2026

October 31, 2026

Categories

  • Articles
  • DORA
  • GDPR
  • HIPAA
  • ISO 27001
  • ISO 42001 & AI governance
  • ISO 9001
  • Management systems
  • NIS2
  • Security frameworks
  • SOC 2
Governance DocsGovernance Docs

Reliable ISO & compliance documentation toolkits that help your business meet regulatory standards with ease.

Governance Docs LLC
1209 Mountain Road Pl NE, Suite R
Albuquerque, NM 87110, USA
[email protected]
+1 505 289 2455

Toolkits

  • ISO 27001:2022
  • GDPR
  • SOC 2
  • PCI-DSS v4.0
  • HIPAA
  • ISO 42001
  • All toolkits →

Company

  • About Us
  • Blog
  • Contact
  • FAQ
  • Which toolkit do I need?
  • Request a custom toolkit
  • Free templates
  • SoA generator
  • Assessments
  • Sample reports
  • RSS feeds

Policies

  • Privacy Policy
  • Terms & Conditions
  • Refund & Return Policy
  • Delivery Policy
  • Manage cookies
Browse by topicISO 27001ISO 42001 & AI governanceGDPRSOC 2HIPAANIS2DORAISO 9001Management systemsSecurity frameworks
© 2026 Governance Docs LLC. All rights reserved.
Secure checkoutstripeVISA