Is ISO 45001 a Legal Requirement? The Clear Answer for 2026 Governance Docs06th September 2026 Is ISO 45001 a legal requirement? No, in any country. But the OH&S law underneath it is mandatory.… Read More
ISO Climate Change Amendment: 2 Sentences, 31 Standards, 1 Trap Governance Docs06th September 2026 The ISO climate change amendment added 2 sentences to clauses 4.1 and 4.2 across 31 standards. What auditors… Read More
Annex SL Explained: The Best Guide to 10 ISO Clauses Governance Docs06th September 2026 Annex SL is the harmonized structure behind ISO 9001, 14001, 27001 and 45001. The 10 clauses explained, the… Read More
CertiKit Alternative: The Best Options Before It Closes in 2026 Governance Docs06th September 2026 CertiKit closes on 18 December 2026. A CertiKit alternative covering all nine of their frameworks plus 66 more,… Read More
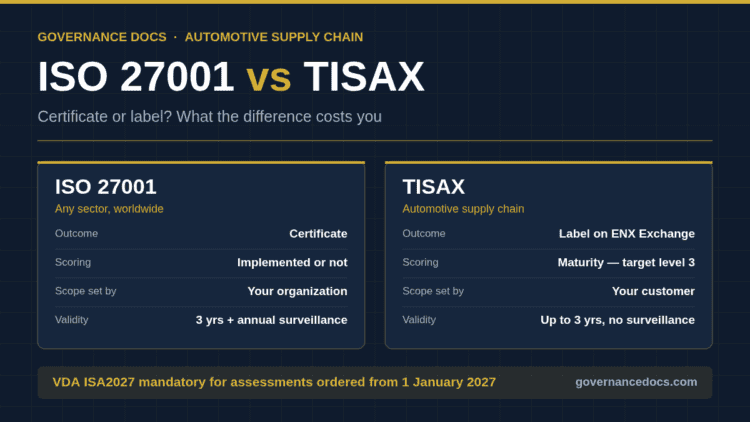
ISO 27001 vs TISAX: The Complete 2026 Supplier Guide Governance Docs06th September 2026 ISO 27001 vs TISAX compared for automotive suppliers: certificate versus ENX label, maturity level 3 scoring, AL2 vs… Read More
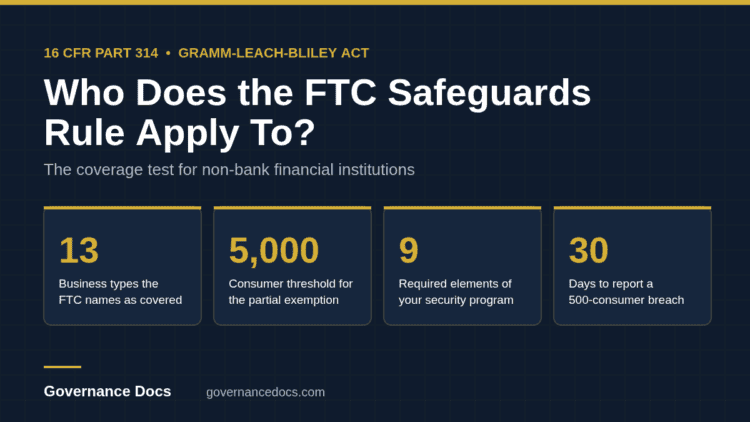
Who Does the FTC Safeguards Rule Apply To? The Complete 2026 Guide Governance Docs05th September 2026 The FTC Safeguards Rule covers 13 types of non-bank financial institution, not just banks. Here is the two-part… Read More
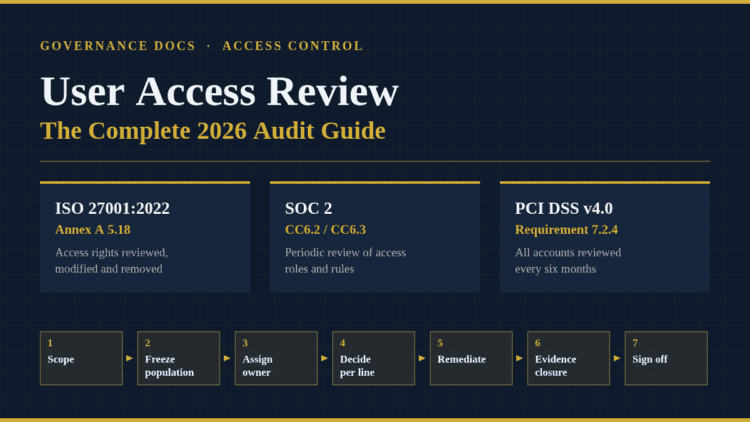
User Access Review: A Complete 2026 Guide for ISO 27001 and SOC 2 Governance Docs04th September 2026 A user access review is the control auditors test hardest. Here is the seven-step process, the ISO 27001… Read More
NIST Privacy Framework Data Map: How to Build One (ID.IM-P8) Governance Docs03rd September 2026 A NIST Privacy Framework data map shows every data action, store and party. What to include, how much… Read More
NIST Privacy Framework vs ISO 27701: Which One in 2026? Governance Docs03rd September 2026 NIST Privacy Framework vs ISO 27701: a free risk model against a certifiable management system. Which to start… Read More
NIST Privacy Framework vs GDPR: How They Fit Together Governance Docs03rd September 2026 NIST Privacy Framework vs GDPR: one is a voluntary risk model, one is law. Where they overlap, where… Read More
NIST Privacy Framework Implementation Tiers: Not a Maturity Model Governance Docs03rd September 2026 NIST Privacy Framework Implementation Tiers: Partial, Risk Informed, Repeatable and Adaptive — and why Tier 4 is not… Read More
NIST Privacy Framework Profiles: Current vs Target in 2026 Governance Docs03rd September 2026 A NIST Privacy Framework Profile records what you achieve and what you need. How to build an honest… Read More