About Us Contact Blog
Governance DocsGovernance Docs
Which Toolkit?SoA GeneratorFree TemplatesSample ReportsFind the Right AssessmentRecords of Processing (ROPA)Data Privacy Impact AssessmentLegitimate Interests AssessmentTransfer Impact AssessmentPrivacy Risk AssessmentGDPR Gap AssessmentUK GDPR Gap AssessmentCCPA/CPRA Gap AssessmentISO 27701 Gap AssessmentHIPAA Gap AssessmentISO 27001 Risk AssessmentThird-Party Risk AssessmentSoA GeneratorISO 27001 Assessment Tool (Excel)ISO 27001 Gap AssessmentSOC 2 Gap AssessmentNIST CSF 2.0 Gap AssessmentNIST SP 800-53 Gap AssessmentNIST RMF Gap AssessmentCIS Controls Gap AssessmentPCI DSS 4.0 Gap AssessmentNIS2 Gap AssessmentCMMC 2.0 Gap AssessmentNIST SP 800-171 Gap AssessmentFedRAMP Gap AssessmentBSI C5 Gap AssessmentIEC 62443 Gap AssessmentSAMA CSF Gap AssessmentNCA ECC Gap AssessmentISO 20000 Gap AssessmentAI Risk AssessmentAI Impact AssessmentISO 42001 Gap AssessmentEU AI Act Gap AssessmentBusiness Impact AnalysisContinuity Risk AssessmentISO 22301 Assessment Tool (Excel)ISO 22301 Gap AssessmentDORA Gap AssessmentISO 9001 Gap AssessmentISO 13485 Gap AssessmentIATF 16949 Gap AssessmentISO 14001 Gap AssessmentISO 45001 Gap AssessmentISO 45001 Assessment Tool (Excel)HACCP Gap AssessmentEnterprise Risk AssessmentISO 31000 Gap AssessmentData Governance Gap AssessmentProject Management Gap AssessmentAll Gap AssessmentsISO 27001 Internal AuditISO 42001 Internal AuditAboutBlogContactMy AccountCart
Browse Toolkits
Governance Docs
  • Browse All Toolkits
  • Information Security & Cybersecurity
  • Data Privacy & Protection
  • Governance, Risk & Compliance
  • Quality Management
  • Health, Safety & Environment
  • AI Governance

My Account

CART

No products in the cart.

Category: Articles

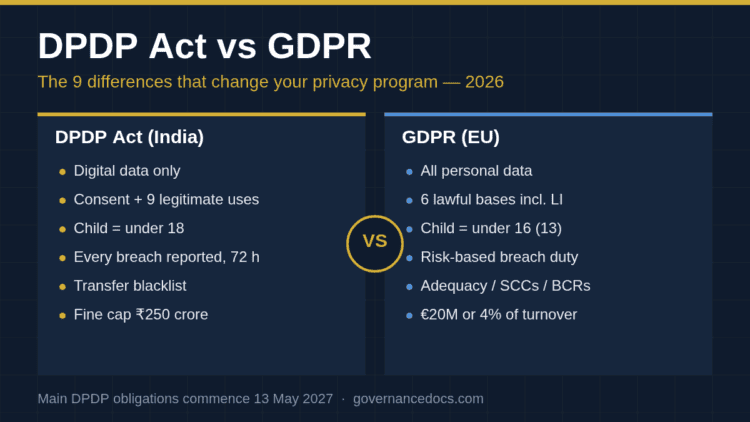
DPDP Act vs GDPR: the 9 differences compared side by side

DPDP Act vs GDPR: The Complete 2026 Guide to 9 Differences

Governance Docs18th September 2026

DPDP Act vs GDPR compared on 9 points: consent, a ₹250 crore fine cap vs 4% of turnover,…
Read More
ISO 50001 mandatory documents explained

ISO 50001 Mandatory Documents: The Complete List of 20 (2026)

Governance Docs18th September 2026

ISO 50001 mandatory documents: all 20 by clause with maintain vs retain, the energy-specific set no other standard…
Read More
significant energy uses explained

Significant Energy Uses: A Complete ISO 50001 Guide (2026)

Governance Docs18th September 2026

Significant energy uses in ISO 50001: the definition, the 2 criteria with a worked 8-use selection, what the…
Read More
energy baseline explained

Energy Baseline: A Complete ISO 50001 Guide to Clause 6.5 (2026)

Governance Docs18th September 2026

The energy baseline under ISO 50001 clause 6.5: the period, the 3 forms, normalisation with a worked regression…
Read More
ISO 50001 vs ISO 14001 explained

ISO 50001 vs ISO 14001: 5 Clear Differences Explained (2026)

Governance Docs18th September 2026

ISO 50001 vs ISO 14001: shared clauses, different demands — 10 points compared, the 5 differences that decide…
Read More
ISO 50001 certification cost explained

ISO 50001 Certification Cost: A Realistic 2026 Breakdown

Governance Docs18th September 2026

ISO 50001 certification cost: audit days set by ISO 50003 from energy complexity × $1,200–2,500/day, $8,000–78,000 over 3…
Read More
complementary customer controls explained

Complementary Customer Controls: A Complete C5 Guide (2026)

Governance Docs18th September 2026

Complementary customer controls in C5:2026: what CUEC are, the 3 audiences, where they cluster by area, the customer's…
Read More
who needs BSI C5 explained

Who Needs BSI C5? Healthcare, Federal Government and 3 More (2026)

Governance Docs18th September 2026

Who needs BSI C5: the 5 customer groups — healthcare under § 393 SGB V (type 2 since…
Read More
BSI C5 attestation cost explained

BSI C5 Attestation Cost: A Realistic 2026 Estimate by Profile

Governance Docs18th September 2026

BSI C5 attestation cost estimated by provider profile: assessor days × €1,500–2,500, type 1 vs type 2, the…
Read More
C5 criteria explained

C5 Criteria: All 17 Objectives and 168 Criteria Explained (2026)

Governance Docs18th September 2026

The C5 criteria in C5:2026: 17 objectives, 168 criteria, basic and additional subcriteria, 6 general conditions, complementary customer…
Read More
BSI C5 vs SOC 2 explained

BSI C5 vs SOC 2: 5 Clear Differences and the Mapping (2026)

Governance Docs18th September 2026

BSI C5 vs SOC 2: same report shape, different content — 10 points compared, the 5 differences that…
Read More
QHSE management review explained

QHSE Management Review: The 3-Standard Agenda in 10 Items (2026)

Governance Docs18th September 2026

The QHSE management review: the union of the three clause 9.3 input lists, the required outputs, a 10-item…
Read More

    ←
  • 1
  • …
  • 51
  • 52
  • 53
  • 54
  • 55
  • …
  • 106
  • →

Recent Posts

ISO 45001 surveillance audit requirements for 2026: annual frequency, the 12-month deadline, one third of initial audit time, and the on-site rule
ISO 45001 Surveillance Audit: The Complete 2026 Guide

November 4, 2026

ISO 14001 surveillance audit infographic showing the cycle years, audit time, eight review areas and the 2029 transition deadline
ISO 14001 Surveillance Audit: The Complete 2026 Guide

November 3, 2026

ISO 27001 toolkit contents shown as three layers: clause 4 to 10 records, 93 Annex A controls and supporting registers
ISO 27001 Toolkit: What a Complete One Contains (2026)

November 2, 2026

ISO 9001 recertification audit three-year cycle showing surveillance in years 1 and 2 and recertification in year 3
ISO 9001 Recertification Audit: The Complete 2026 Guide

November 1, 2026

ISO 9001 surveillance audit: eight required review areas, the 12-month window and the 2029 transition deadline
ISO 9001 Surveillance Audit: The Complete 2026 Guide

October 31, 2026

Categories

  • Articles
  • DORA
  • GDPR
  • HIPAA
  • ISO 27001
  • ISO 42001 & AI governance
  • ISO 9001
  • Management systems
  • NIS2
  • Security frameworks
  • SOC 2
Governance DocsGovernance Docs

Reliable ISO & compliance documentation toolkits that help your business meet regulatory standards with ease.

Governance Docs LLC
1209 Mountain Road Pl NE, Suite R
Albuquerque, NM 87110, USA
[email protected]
+1 505 289 2455

Toolkits

  • ISO 27001:2022
  • GDPR
  • SOC 2
  • PCI-DSS v4.0
  • HIPAA
  • ISO 42001
  • All toolkits →

Company

  • About Us
  • Blog
  • Contact
  • FAQ
  • Which toolkit do I need?
  • Request a custom toolkit
  • Free templates
  • SoA generator
  • Assessments
  • Sample reports
  • RSS feeds

Policies

  • Privacy Policy
  • Terms & Conditions
  • Refund & Return Policy
  • Delivery Policy
  • Manage cookies
Browse by topicISO 27001ISO 42001 & AI governanceGDPRSOC 2HIPAANIS2DORAISO 9001Management systemsSecurity frameworks
© 2026 Governance Docs LLC. All rights reserved.
Secure checkoutstripeVISA