PRRC: The 5 Essential Duties of the MDR Article 15 Role Governance Docs19th September 2026 PRRC under MDR Article 15: the 2 qualification routes, the 5 duties, where the person must sit, micro… Read More
MDR Technical Documentation: 8 Essential Annex II and III Parts Governance Docs19th September 2026 MDR technical documentation under Article 10(4): the 6 Annex II sections and 2 Annex III parts, what the… Read More
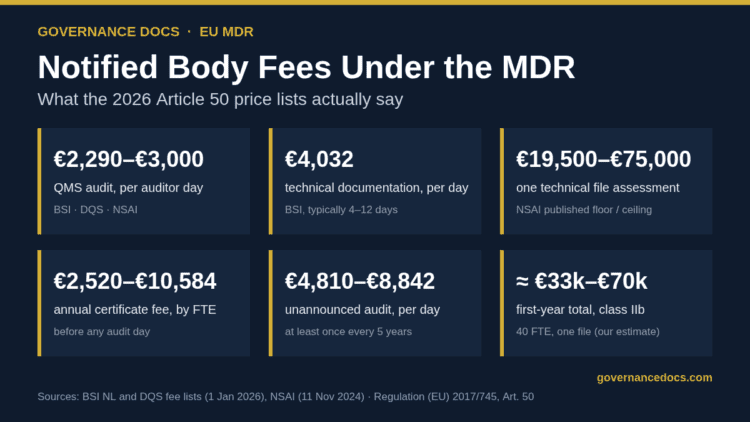
Notified Body Fees Under the MDR: A Clear 2026 Breakdown Governance Docs19th September 2026 Notified body fees under the MDR from the 2026 price lists: €2,290–€3,000 audit days, €4,032 technical file days,… Read More
Saudi PDPL Penalties: The 2 Tiers up to SAR 5 Million Explained Governance Docs18th September 2026 Saudi PDPL penalties: Article 35 criminal tier (2 years, SAR 3m) for sensitive-data disclosure, Article 36 fines up… Read More
Saudi PDPL Breach Notification: The Complete 72-Hour SDAIA Guide Governance Docs18th September 2026 Saudi PDPL breach notification: 72 hours to SDAIA through the platform with 5 items, data subjects without undue… Read More
201 CMR 17.00: The Complete Massachusetts WISP Guide (2026) Governance Docs18th September 2026 201 CMR 17.00 explained: who it binds, personal information defined, the 10 WISP elements of 17.03, the 8… Read More
FTC Safeguards Rule Breach Notification: The 30-Day WISP Rule Governance Docs18th September 2026 FTC Safeguards Rule breach notification under 314.4(j): the notification-event definition, deemed discovery, 500 consumers, 30 days, the 6… Read More
FTC Safeguards Rule Penalties: The Complete WISP Enforcement Guide Governance Docs18th September 2026 FTC Safeguards Rule penalties: no fine in the Rule, section 5 orders with 20-year obligations, $53,088 per violation… Read More
Qualified Individual: The Complete WISP and Safeguards Rule Guide Governance Docs18th September 2026 The Qualified Individual under 16 CFR 314.4(a): what the Rule requires, what qualified means, 3 ways to fill… Read More
NIST CSF vs ISO 27001: 5 Clear Differences Explained (2026) Governance Docs18th September 2026 NIST CSF vs ISO 27001 on 5 differences: outcome framework vs certifiable system, Profiles vs certificate, scope, prescription,… Read More
SOX Scoping and Materiality: A Clear Top-Down Guide (2026) Governance Docs18th September 2026 SOX scoping and materiality under AS 2201: the top-down sequence, overall and performance materiality, qualitative factors, locations, service… Read More
SOX Control Testing: The Clear Guide to Sample Sizes (2026) Governance Docs18th September 2026 SOX control testing under AS 2201: the principles, conventional sample sizes by frequency (annual 1 to daily 20–40),… Read More