About Us Contact Blog
Governance DocsGovernance Docs
Which Toolkit?SoA GeneratorFree TemplatesSample ReportsFind the Right AssessmentRecords of Processing (ROPA)Data Privacy Impact AssessmentLegitimate Interests AssessmentTransfer Impact AssessmentPrivacy Risk AssessmentGDPR Gap AssessmentUK GDPR Gap AssessmentCCPA/CPRA Gap AssessmentISO 27701 Gap AssessmentHIPAA Gap AssessmentISO 27001 Risk AssessmentThird-Party Risk AssessmentSoA GeneratorISO 27001 Assessment Tool (Excel)ISO 27001 Gap AssessmentSOC 2 Gap AssessmentNIST CSF 2.0 Gap AssessmentNIST SP 800-53 Gap AssessmentNIST RMF Gap AssessmentCIS Controls Gap AssessmentPCI DSS 4.0 Gap AssessmentNIS2 Gap AssessmentCMMC 2.0 Gap AssessmentNIST SP 800-171 Gap AssessmentFedRAMP Gap AssessmentBSI C5 Gap AssessmentIEC 62443 Gap AssessmentSAMA CSF Gap AssessmentNCA ECC Gap AssessmentISO 20000 Gap AssessmentAI Risk AssessmentAI Impact AssessmentISO 42001 Gap AssessmentEU AI Act Gap AssessmentBusiness Impact AnalysisContinuity Risk AssessmentISO 22301 Assessment Tool (Excel)ISO 22301 Gap AssessmentDORA Gap AssessmentISO 9001 Gap AssessmentISO 13485 Gap AssessmentIATF 16949 Gap AssessmentISO 14001 Gap AssessmentISO 45001 Gap AssessmentISO 45001 Assessment Tool (Excel)HACCP Gap AssessmentEnterprise Risk AssessmentISO 31000 Gap AssessmentData Governance Gap AssessmentProject Management Gap AssessmentAll Gap AssessmentsAboutBlogContactMy AccountCart
FOX v.2.4.9
Browse Toolkits
Governance Docs
  • Browse All Toolkits
  • Information Security & Cybersecurity
  • Data Privacy & Protection
  • Governance, Risk & Compliance
  • Quality Management
  • Health, Safety & Environment
  • AI Governance

My Account

CART

No products in the cart.

Category: Articles

Vendor exit strategy showing triggers, exit options, data return, transition and testing steps

Vendor Exit Strategy: How to Plan One in 2026

Governance Docs30th September 2026

How to build a vendor exit strategy: triggers, stressed and planned exit options, data return, transition steps, contract…
Read More
Vendor risk register table with vendor, risk description, rating, owner, treatment and review date columns

Vendor Risk Register: How to Build One in 2026

Governance Docs30th September 2026

How to build a vendor risk register: the fields to include, how to score risks, assign owners, link…
Read More
TPRM metrics dashboard showing coverage, assessment timeliness, open findings, incidents and concentration

TPRM Metrics and KPIs: A Practical 2026 Guide

Governance Docs30th September 2026

Which TPRM metrics matter: coverage, timeliness, findings, incidents and concentration, how to set thresholds and how to report…
Read More
Third-party contract clauses grouped into security, data, audit, incident, subcontractor and exit protections

Third-Party Contract Clauses for Risk Management: 2026

Governance Docs30th September 2026

The third-party contract clauses that matter for risk management: security, data protection, audit rights, incident notification, subcontractors, resilience…
Read More
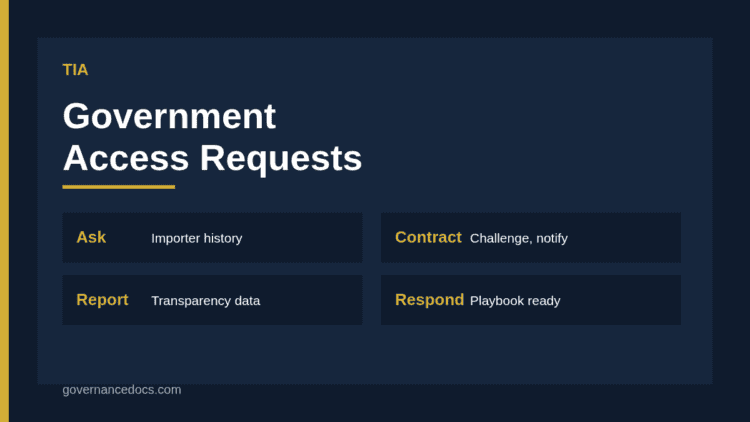
Government access requests in a TIA showing assessment, contract clauses, transparency reports and response steps

Government Access Requests in a TIA: 2026 Guide

Governance Docs30th September 2026

How to handle government access requests in a TIA: assessing importer track record, contract commitments, transparency reports and…
Read More
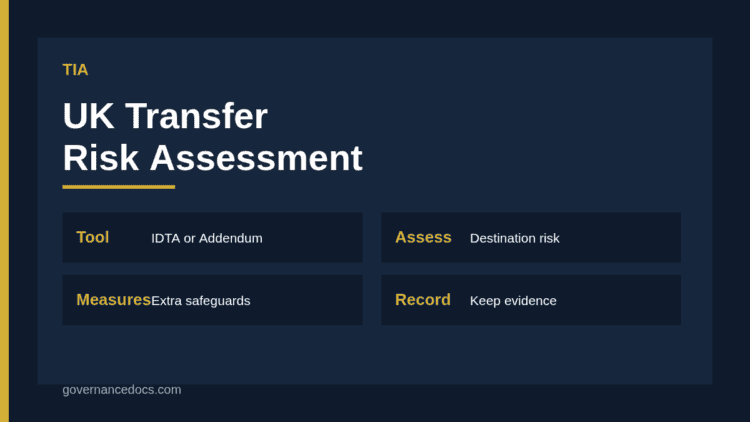
UK transfer risk assessment steps covering transfer description, tool, destination laws, risk rating and safeguards

UK Transfer Risk Assessment: A Practical 2026 Guide

Governance Docs30th September 2026

How to do a UK transfer risk assessment: when the IDTA or UK Addendum needs one, the ICO…
Read More
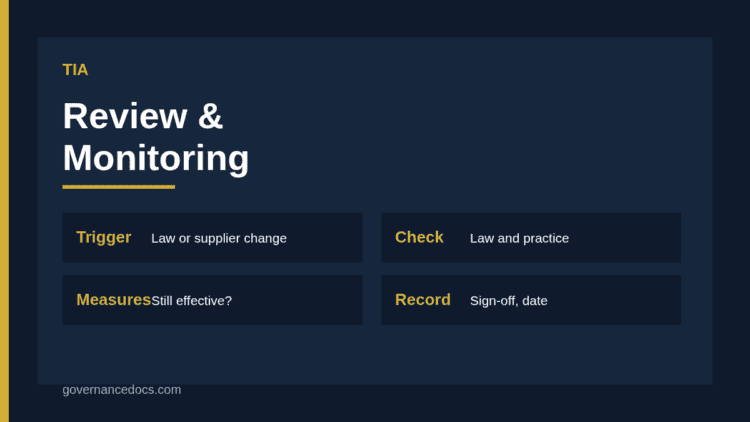
TIA review and monitoring cycle showing triggers, legal check, supplier check, measures review and sign-off

TIA Review and Monitoring: A Practical 2026 Guide

Governance Docs30th September 2026

How to run TIA review and monitoring: review triggers, schedules, what to check about laws and suppliers, ownership…
Read More
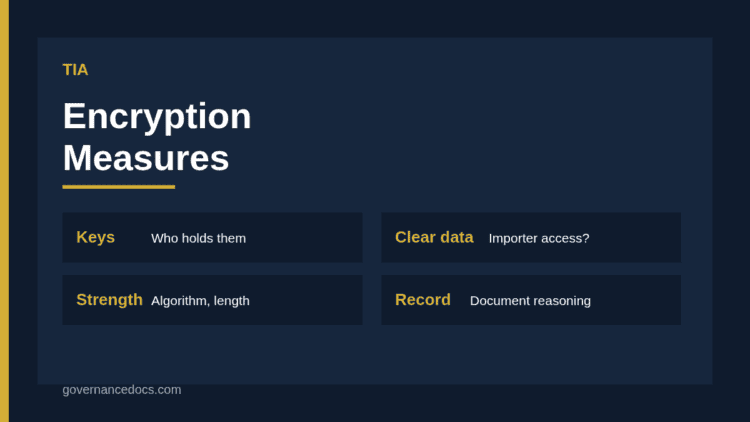
Encryption in a TIA decision flow showing key control, data in the clear and residual risk for a transfer

Encryption as a Supplementary Measure in a TIA: 2026

Governance Docs30th September 2026

How to assess encryption in a TIA: when it works as a supplementary measure, who must hold the…
Read More
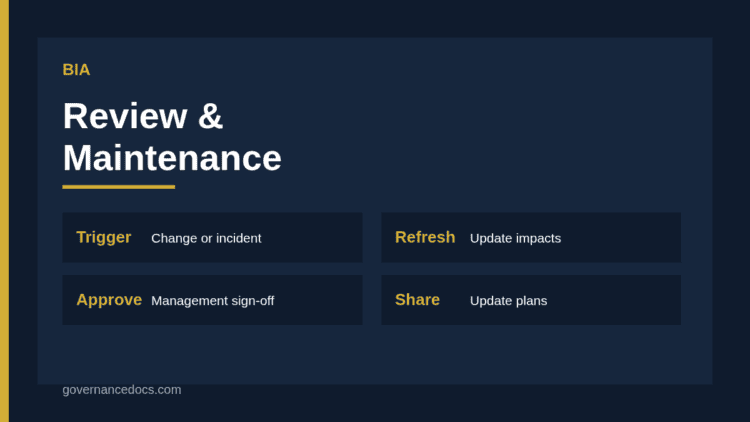
BIA review and maintenance cycle showing triggers, refresh, approval and communication of updated recovery priorities

BIA Review and Maintenance: A 2026 Guide

Governance Docs30th September 2026

How to handle BIA review and maintenance: refresh cycles, review triggers, ownership, what to check and how to…
Read More
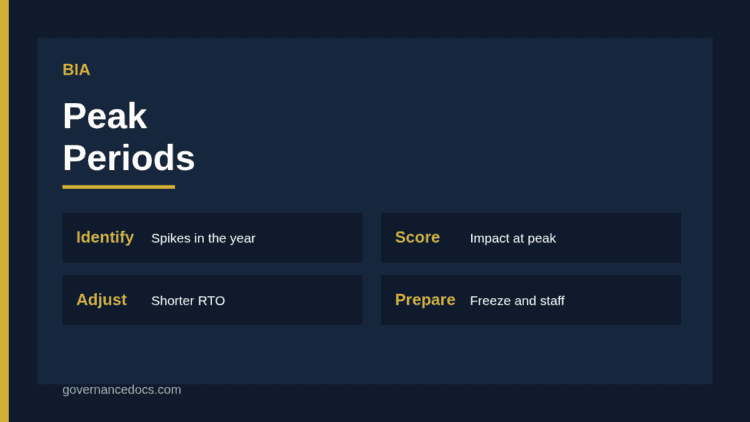
BIA peak periods calendar showing month-end, seasonal and event-driven spikes that raise disruption impact

BIA Peak Periods and Seasonality: 2026 Guide

Governance Docs30th September 2026

How to handle BIA peak periods: capturing seasonal, month-end and event-driven spikes, adjusting recovery targets and planning for…
Read More
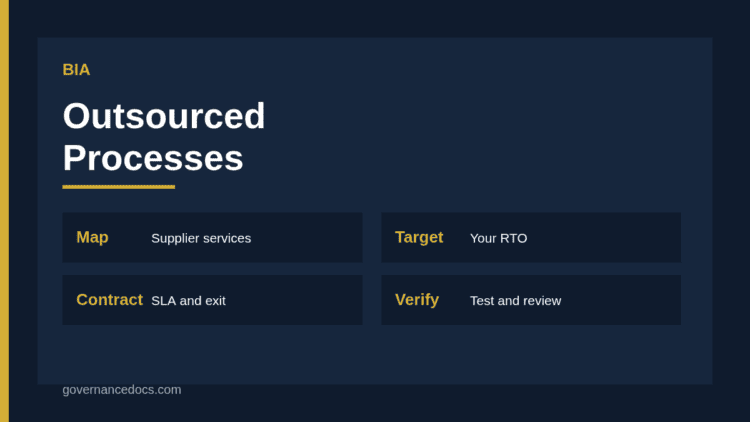
BIA for outsourced processes linking internal activities to supplier services, contract terms and recovery targets

BIA for Outsourced Processes: A 2026 Guide

Governance Docs30th September 2026

How to run a BIA for outsourced processes: mapping supplier-run activities, setting recovery expectations, reviewing contracts and verifying…
Read More
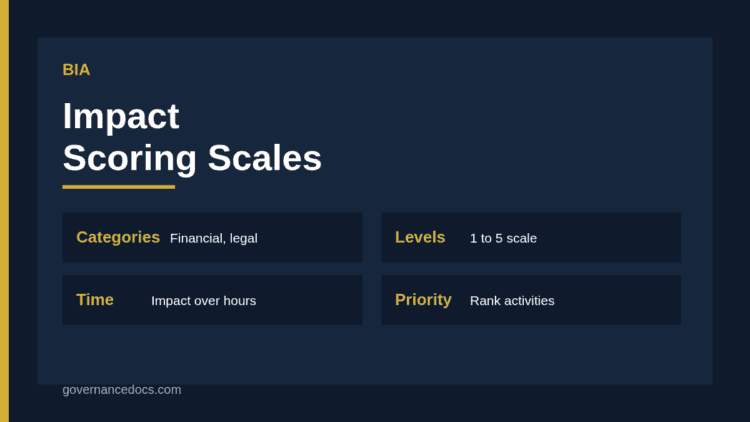
BIA impact scoring scales matrix showing impact categories and severity levels over time

BIA Impact Scoring Scales: A Practical 2026 Guide

Governance Docs30th September 2026

How to build BIA impact scoring scales: choosing impact categories, defining thresholds over time, calibrating ratings and linking…
Read More

    ←
  • 1
  • …
  • 13
  • 14
  • 15
  • 16
  • 17
  • …
  • 99
  • →

Recent Posts

ISO 27001 configuration management requirements under Annex A 8.9 - established, documented, implemented, monitored, reviewed
ISO 27001 Configuration Management: Complete 2026 Guide

October 11, 2026

internal audit findings rating scale — Internal Audit Findings Rating Scale: Examples and Template
Internal Audit Findings Rating Scale: Examples and Template

October 11, 2026

third party topical requirement — Third Party Topical Requirement: The 2026 Audit Guide
Third Party Topical Requirement: The 2026 Audit Guide

October 11, 2026

cybersecurity topical requirement — Cybersecurity Topical Requirement: How to Audit It in 2026
Cybersecurity Topical Requirement: How to Audit It in 2026

October 11, 2026

quality assurance and improvement program — Quality Assurance and Improvement Program (QAIP): 2026 Guide
Quality Assurance and Improvement Program (QAIP): 2026 Guide

October 11, 2026

Categories

  • Articles
  • DORA
  • GDPR
  • HIPAA
  • ISO 27001
  • ISO 42001 & AI governance
  • ISO 9001
  • Management systems
  • NIS2
  • Security frameworks
  • SOC 2
Governance DocsGovernance Docs

Reliable ISO & compliance documentation toolkits that help your business meet regulatory standards with ease.

Governance Docs LLC
1209 Mountain Road Pl NE, Suite R
Albuquerque, NM 87110, USA
info@governancedocs.com
+1 505 289 2455

Toolkits

  • ISO 27001:2022
  • GDPR
  • SOC 2
  • PCI-DSS v4.0
  • HIPAA
  • ISO 42001
  • All toolkits →

Company

  • About Us
  • Blog
  • Contact
  • FAQ
  • Which toolkit do I need?
  • Free templates
  • SoA generator
  • Assessments
  • Sample reports
  • RSS feeds

Policies

  • Privacy Policy
  • Terms & Conditions
  • Refund & Return Policy
  • Delivery Policy
  • Manage cookies
Browse by topicISO 27001ISO 42001 & AI governanceGDPRSOC 2HIPAANIS2DORAISO 9001Management systemsSecurity frameworks
© 2026 Governance Docs LLC. All rights reserved.
Secure checkoutstripeVISA