About Us Contact Blog
Governance DocsGovernance Docs
Which Toolkit?SoA GeneratorFree TemplatesSample ReportsFind the Right AssessmentRecords of Processing (ROPA)Data Privacy Impact AssessmentLegitimate Interests AssessmentTransfer Impact AssessmentPrivacy Risk AssessmentGDPR Gap AssessmentUK GDPR Gap AssessmentCCPA/CPRA Gap AssessmentISO 27701 Gap AssessmentHIPAA Gap AssessmentISO 27001 Risk AssessmentThird-Party Risk AssessmentSoA GeneratorISO 27001 Assessment Tool (Excel)ISO 27001 Gap AssessmentSOC 2 Gap AssessmentNIST CSF 2.0 Gap AssessmentNIST SP 800-53 Gap AssessmentNIST RMF Gap AssessmentCIS Controls Gap AssessmentPCI DSS 4.0 Gap AssessmentNIS2 Gap AssessmentCMMC 2.0 Gap AssessmentNIST SP 800-171 Gap AssessmentFedRAMP Gap AssessmentBSI C5 Gap AssessmentIEC 62443 Gap AssessmentSAMA CSF Gap AssessmentNCA ECC Gap AssessmentISO 20000 Gap AssessmentAI Risk AssessmentAI Impact AssessmentISO 42001 Gap AssessmentEU AI Act Gap AssessmentBusiness Impact AnalysisContinuity Risk AssessmentISO 22301 Assessment Tool (Excel)ISO 22301 Gap AssessmentDORA Gap AssessmentISO 9001 Gap AssessmentISO 13485 Gap AssessmentIATF 16949 Gap AssessmentISO 14001 Gap AssessmentISO 45001 Gap AssessmentISO 45001 Assessment Tool (Excel)HACCP Gap AssessmentEnterprise Risk AssessmentISO 31000 Gap AssessmentData Governance Gap AssessmentProject Management Gap AssessmentAll Gap AssessmentsAboutBlogContactMy AccountCart
FOX v.2.4.9
Browse Toolkits
Governance Docs
  • Browse All Toolkits
  • Information Security & Cybersecurity
  • Data Privacy & Protection
  • Governance, Risk & Compliance
  • Quality Management
  • Health, Safety & Environment
  • AI Governance

My Account

CART

No products in the cart.

Category: Articles

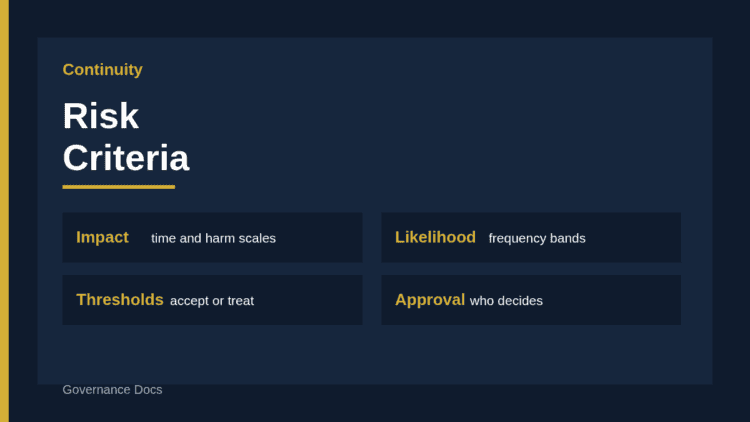
Business continuity risk criteria scales diagram

Business Continuity Risk Criteria: The Essential 2026 Guide to Setting Scales and Thresholds

Governance Docs30th September 2026

How to define business continuity risk criteria so continuity risks are scored consistently and escalated at the right…
Read More
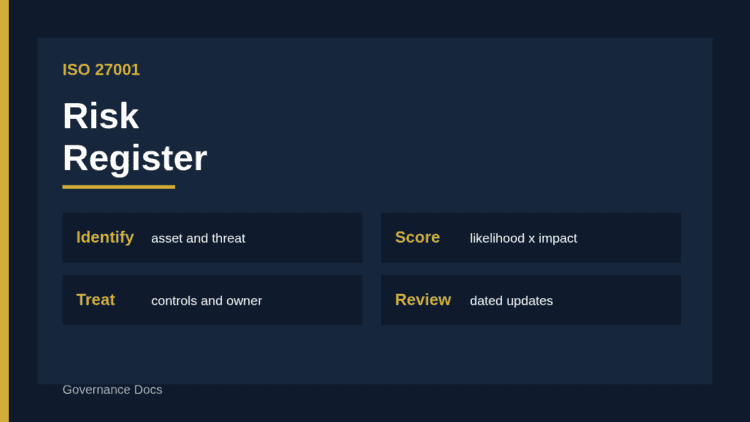
ISO 27001 risk register fields diagram

ISO 27001 Risk Register: The Essential 2026 Guide to Fields, Scoring and Evidence

Governance Docs30th September 2026

What an ISO 27001 risk register should contain, how to keep it current and what auditors sample.
Read More
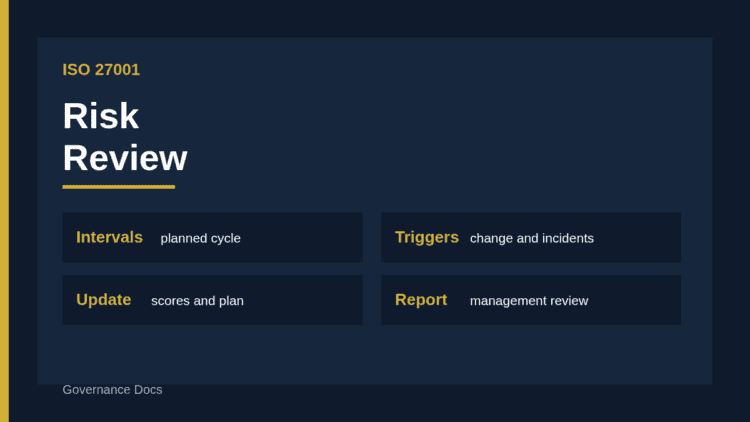
ISO 27001 risk review cycle diagram

ISO 27001 Risk Review: The Essential 2026 Guide to Keeping Assessments Current

Governance Docs30th September 2026

How to run an ISO 27001 risk review with planned intervals, change triggers and evidence that satisfies auditors.
Read More
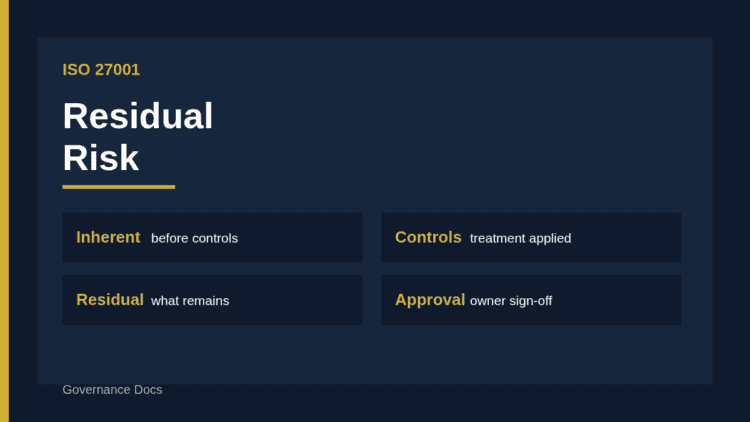
ISO 27001 residual risk lifecycle diagram

ISO 27001 Residual Risk: The Essential 2026 Guide to Evaluating What Remains

Governance Docs30th September 2026

How to calculate, approve, record and review ISO 27001 residual risk so your treatment plan and audit evidence…
Read More
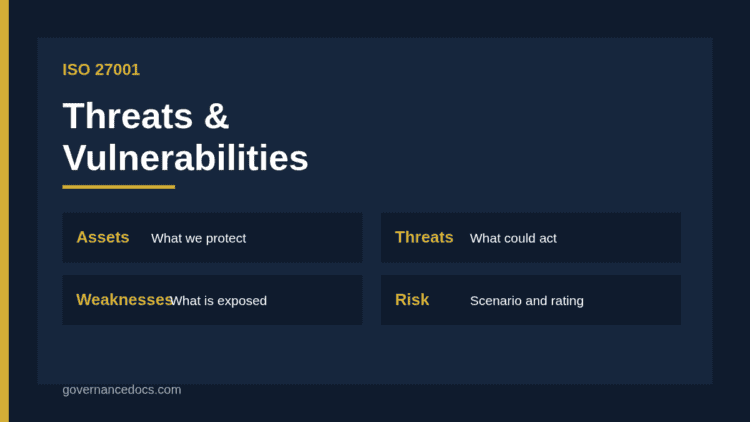
ISO 27001 threats and vulnerabilities linked to assets, existing controls and resulting risk scenarios

ISO 27001 Threats and Vulnerabilities: 2026 Guide

Governance Docs30th September 2026

How to identify ISO 27001 threats and vulnerabilities: threat sources, vulnerability types, linking them to assets and controls,…
Read More
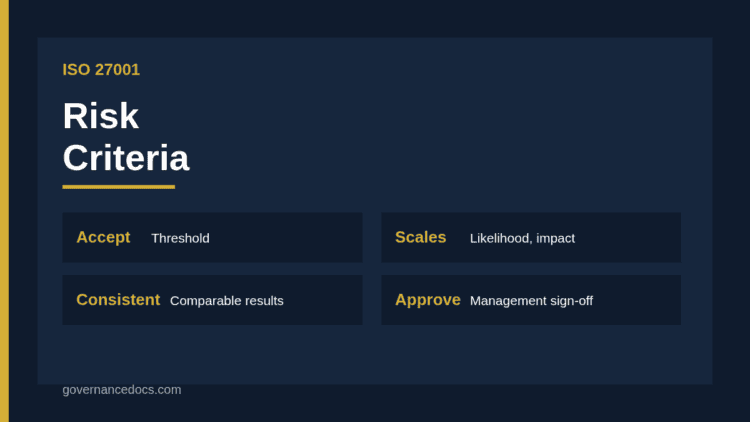
ISO 27001 risk criteria showing acceptance criteria, likelihood and impact scales, and consistent scoring for audit

ISO 27001 Risk Criteria: A Practical 2026 Guide

Governance Docs30th September 2026

How to define ISO 27001 risk criteria: risk acceptance criteria and assessment criteria, likelihood and impact scales, approval…
Read More
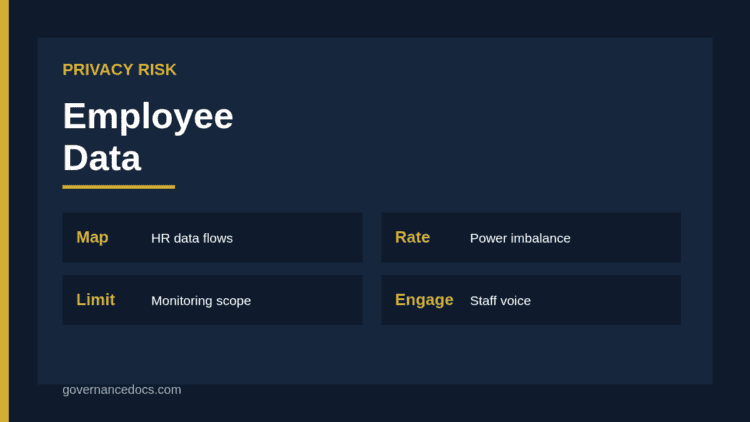
Privacy risk assessment for employee data covering HR records, monitoring, profiling, retention and staff involvement

Privacy Risk Assessment for Employee Data: 2026 Guide

Governance Docs30th September 2026

How to run a privacy risk assessment for employee data: mapping HR data, rating risks from monitoring and…
Read More
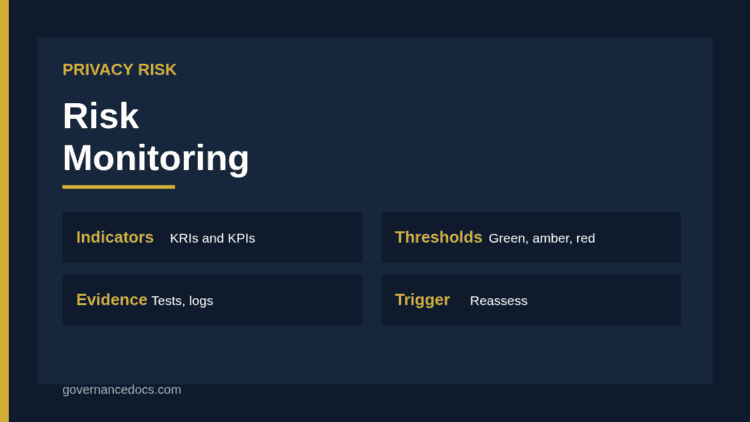
Privacy risk monitoring loop with indicators, thresholds, evidence, reporting and reassessment triggers

Privacy Risk Monitoring: A Practical 2026 Guide

Governance Docs30th September 2026

How to run privacy risk monitoring: choosing indicators, setting thresholds, gathering evidence, reporting to leaders and triggering reassessment…
Read More
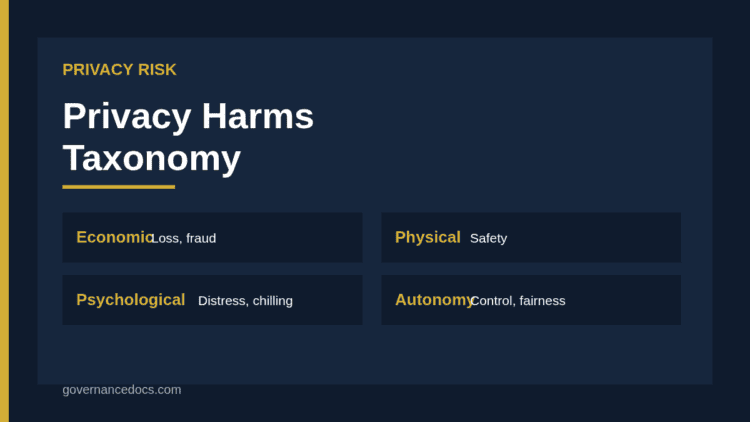
Privacy harms taxonomy grouping harms into physical, economic, psychological, reputational and autonomy categories

Privacy Harms Taxonomy: A Practical 2026 Guide

Governance Docs30th September 2026

How to use a privacy harms taxonomy: categories of harm to individuals, problematic data actions, how to apply…
Read More
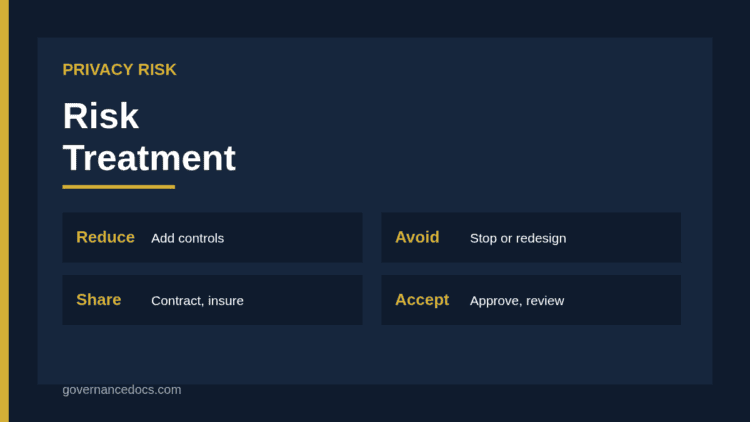
Privacy risk treatment options of reduce, avoid, share and accept with owners, dates and residual risk approval

Privacy Risk Treatment: Options and Plans for 2026

Governance Docs30th September 2026

How to plan privacy risk treatment: options to reduce, avoid, share or accept risk, writing an actionable plan…
Read More
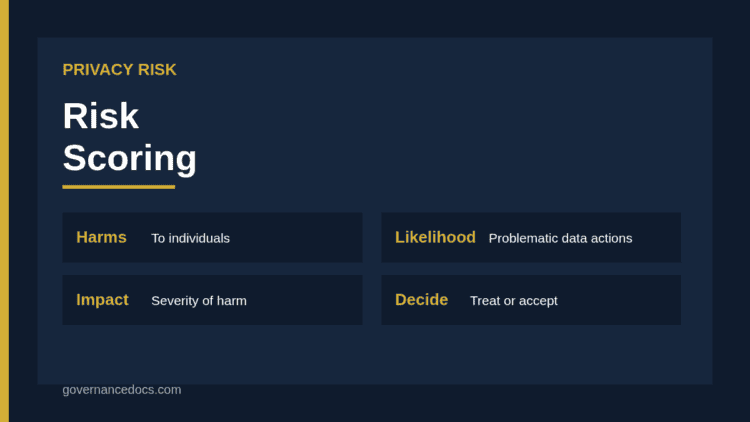
Privacy risk scoring matrix combining likelihood and impact of privacy harms to individuals into risk levels

Privacy Risk Scoring: A Practical 2026 Guide

Governance Docs30th September 2026

How to approach privacy risk scoring: rating likelihood and impact of harm to individuals, building a matrix, scoring…
Read More
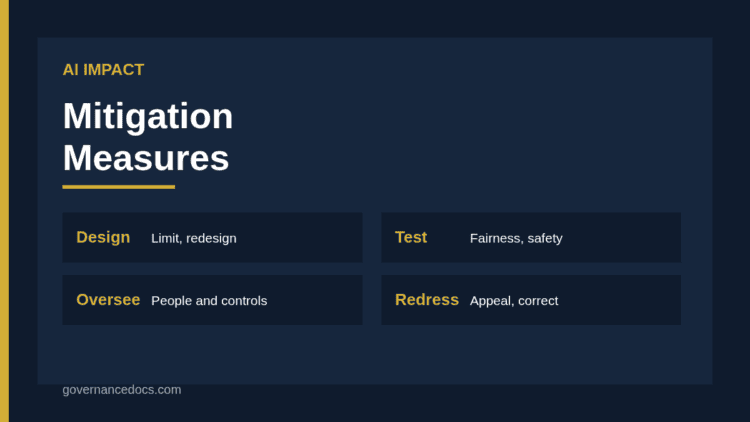
AI impact assessment mitigation measures grouped into design, testing, oversight, transparency and redress controls

AI Impact Assessment Mitigation Measures: 2026 Guide

Governance Docs30th September 2026

How to plan AI impact assessment mitigation: technical, organizational and procedural safeguards, owners and dates, evidence and residual…
Read More

    ←
  • 1
  • …
  • 11
  • 12
  • 13
  • 14
  • 15
  • …
  • 99
  • →

Recent Posts

ISO 27001 configuration management requirements under Annex A 8.9 - established, documented, implemented, monitored, reviewed
ISO 27001 Configuration Management: Complete 2026 Guide

October 11, 2026

internal audit findings rating scale — Internal Audit Findings Rating Scale: Examples and Template
Internal Audit Findings Rating Scale: Examples and Template

October 11, 2026

third party topical requirement — Third Party Topical Requirement: The 2026 Audit Guide
Third Party Topical Requirement: The 2026 Audit Guide

October 11, 2026

cybersecurity topical requirement — Cybersecurity Topical Requirement: How to Audit It in 2026
Cybersecurity Topical Requirement: How to Audit It in 2026

October 11, 2026

quality assurance and improvement program — Quality Assurance and Improvement Program (QAIP): 2026 Guide
Quality Assurance and Improvement Program (QAIP): 2026 Guide

October 11, 2026

Categories

  • Articles
  • DORA
  • GDPR
  • HIPAA
  • ISO 27001
  • ISO 42001 & AI governance
  • ISO 9001
  • Management systems
  • NIS2
  • Security frameworks
  • SOC 2
Governance DocsGovernance Docs

Reliable ISO & compliance documentation toolkits that help your business meet regulatory standards with ease.

Governance Docs LLC
1209 Mountain Road Pl NE, Suite R
Albuquerque, NM 87110, USA
info@governancedocs.com
+1 505 289 2455

Toolkits

  • ISO 27001:2022
  • GDPR
  • SOC 2
  • PCI-DSS v4.0
  • HIPAA
  • ISO 42001
  • All toolkits →

Company

  • About Us
  • Blog
  • Contact
  • FAQ
  • Which toolkit do I need?
  • Free templates
  • SoA generator
  • Assessments
  • Sample reports
  • RSS feeds

Policies

  • Privacy Policy
  • Terms & Conditions
  • Refund & Return Policy
  • Delivery Policy
  • Manage cookies
Browse by topicISO 27001ISO 42001 & AI governanceGDPRSOC 2HIPAANIS2DORAISO 9001Management systemsSecurity frameworks
© 2026 Governance Docs LLC. All rights reserved.
Secure checkoutstripeVISA